
 Middle East Cybersecurity Market | 2026-2036
Middle East Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Middle East Cybersecurity Market Insights
Project finance for sovereign digital infrastructure is tilting competitive dynamics toward vendors capable of multi-year managed service contracts. Palo Alto Networks leverages its platform consolidation strategy to capture enterprise firewall refresh cycles across Gulf banking groups. DarkMatter anchors its position through deep integration with UAE federal security architecture and cleared personnel pools. Fortinet competes aggressively on appliance density and SD-WAN attach rates in mid-market energy services firms.
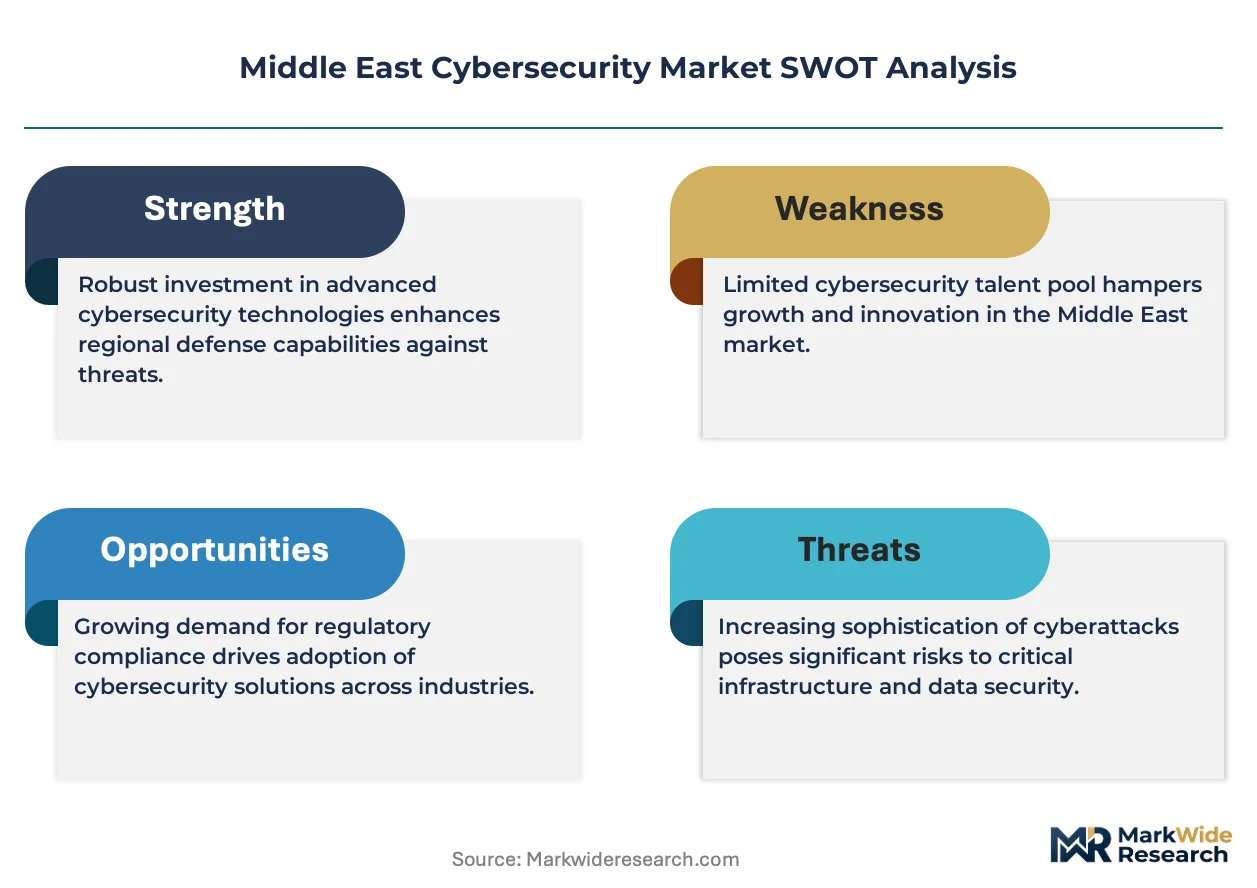
Middle East cybersecurity encompasses hardware, software, and services engineered to protect digital assets against unauthorized access, disruption, or exfiltration across on-premises, cloud, and operational technology environments, with next-generation firewalls typically processing traffic at 100 Gbps throughput thresholds and zero-trust architectures enforcing continuous identity verification. The primary commercial purpose is risk transfer and operational continuity for organizations managing critical infrastructure, financial transactions, or citizen data. Network Security dominates current procurement volumes as Gulf utilities and oil operators harden SCADA perimeter defenses against targeted intrusions. Cloud Security represents the fastest-expanding segment as Saudi and Emirati government cloud migrations accelerate and shared responsibility models create advisory service pull-through for consulting and implementation engagements.
NESA in the UAE, SDAIA in Saudi Arabia, and Qatar's NCSA collectively mandate baseline controls, incident reporting timelines, and certified product lists that filter vendor eligibility and inflate compliance service attach rates. SAMR-aligned GB standards and ISO 27001 certification requirements further segment the supplier base between accredited integrators and uncertified challengers. Stakeholders must monitor how sovereign data localization edicts reshape cloud architecture decisions and whether national cybersecurity funds redirect procurement toward domestic capability builds.
Market Dynamics
Sovereign data governance mandates from SDAIA and NESA are compressing procurement timelines and forcing security architecture redesigns across Gulf energy and banking operators. These regulations eliminate vendor flexibility and mandate certified implementation partners.
Growth Catalysts
- SCADA perimeter hardening:Saudi Aramco and ADNOC are mandating air-gapped network segmentation for operational technology environments, creating dedicated procurement streams for industrial firewall appliances.
- NESA compliance deadlines:UAE federal entities must complete baseline control implementation by mandated phases, accelerating advisory and managed security service contracts.
- Sovereign cloud migration:Saudi government cloud (SCCC) and UAE's Federal Network (FAN) expansion is driving demand for cloud-native security posture management and encryption key escrow services.
Market Restraints
- Cleared personnel scarcity:UAE and Saudi security clearance processes for foreign technicians create 6-12 month onboarding bottlenecks for complex integration projects.
- Hardware import dependencies:Specialized cryptographic modules and tamper-resistant hardware security modules concentrate sourcing from limited certified foundries in Asia-Pacific and Europe.
- Localization requirements:SDAIA data residency rules fragment cloud architectures, forcing redundant infrastructure deployment that inflates total cost of ownership for multinational operators.
Strategic Opportunities
- Qatar NCSA maturation:The national cybersecurity agency's expanding certification framework creates first-mover advantage for integrators establishing cleared delivery centers in Doha.
- Zero-trust network access convergence:Software-defined perimeter technology combined with identity-aware proxy architectures opens new service attach rates for mid-market professional services firms.
- Kuwaiti banking digitization:Central Bank of Kuwait's open banking directives are accelerating API security and customer identity verification procurement among tier-2 financial institutions.
Industry Challenges
- OT security skill scarcity:Industrial control system vulnerability assessment and incident response capabilities remain concentrated among a handful of specialized practitioners across the Gulf.
- Multi-framework compliance burden:Organizations operating across Saudi, UAE, and Qatar must maintain parallel ISO 27001, NESA, SDAIA, and NCSA audit cycles with divergent control mappings.
- Legacy mainframe integration:Core banking systems in established Gulf financial institutions require custom API gateway development to interface with modern zero-trust enforcement points.
Report Scope
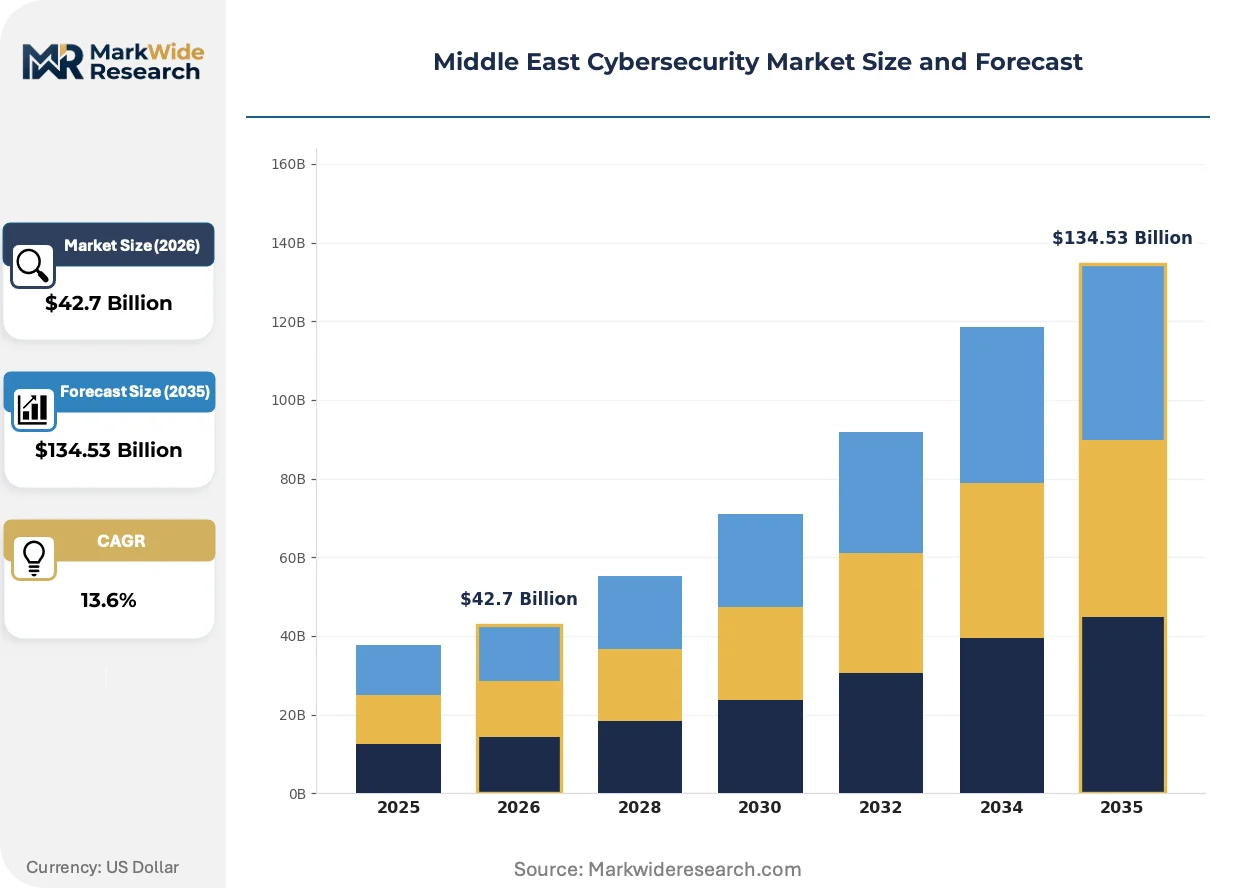
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Middle East Cybersecurity Market |
| Market Size in 2026 | $42.7 Billion |
| Market Size in 2035 | $134.53 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Security, Network Security, Cloud Security, Application Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed End User: Government, BFSI, Healthcare, Retail Service Type: Consulting, Implementation, Maintenance, Training |
| Companies Covered | Fortinet, DarkMatter, Palo Alto Networks, Trend Micro, Help AG, Cisco Systems, IBM Corporation, Zscaler, Microsoft Corporation, Others |
| Regions Covered | Middle East: Saudi Arabia, UAE, Qatar, Israel, Kuwait, Oman, Bahrain, Iran, Iraq, Rest of Middle East |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Middle East Cybersecurity Market Trends and Innovations
Security delivery models are pivoting from appliance-centric sales toward continuous monitoring subscriptions, with vendor economics increasingly tied to outcome metrics rather than upfront hardware recognition. This shift reconfigures channel relationships and professional services staffing across the Gulf.
Secure access service edge (SASE) architecture is virtualizing branch office security stacks by converging SD-WAN, cloud-delivered firewall, and zero-trust network access into unified policy enforcement. Saudi petrochemical distributors and UAE retail banking networks are adopting this model to eliminate appliance sprawl at remote sites. The technology is virtualizing traditional perimeter security capital expenditure into operationalized subscription flows.
SDAIA's Personal Data Protection Law and accompanying executive regulations are mandating privacy impact assessments and breach notification timelines that exceed baseline GDPR alignment. Data processors serving Saudi government entities must now maintain localized incident response capabilities with 72-hour reporting windows. Financial services and healthcare verticals are responding by embedding privacy engineers into product development cycles.
Long-term managed detection and response contracts are displacing traditional annual license renewals among Gulf sovereign wealth funds and national oil companies. These agreements bundle threat hunting, forensic retainer, and compliance reporting into single-vendor relationships. The shift is most visible in Saudi Arabia where procurement officers favor multi-year commitments that transfer operational risk to service providers.
Middle East Cybersecurity Market Segmentation
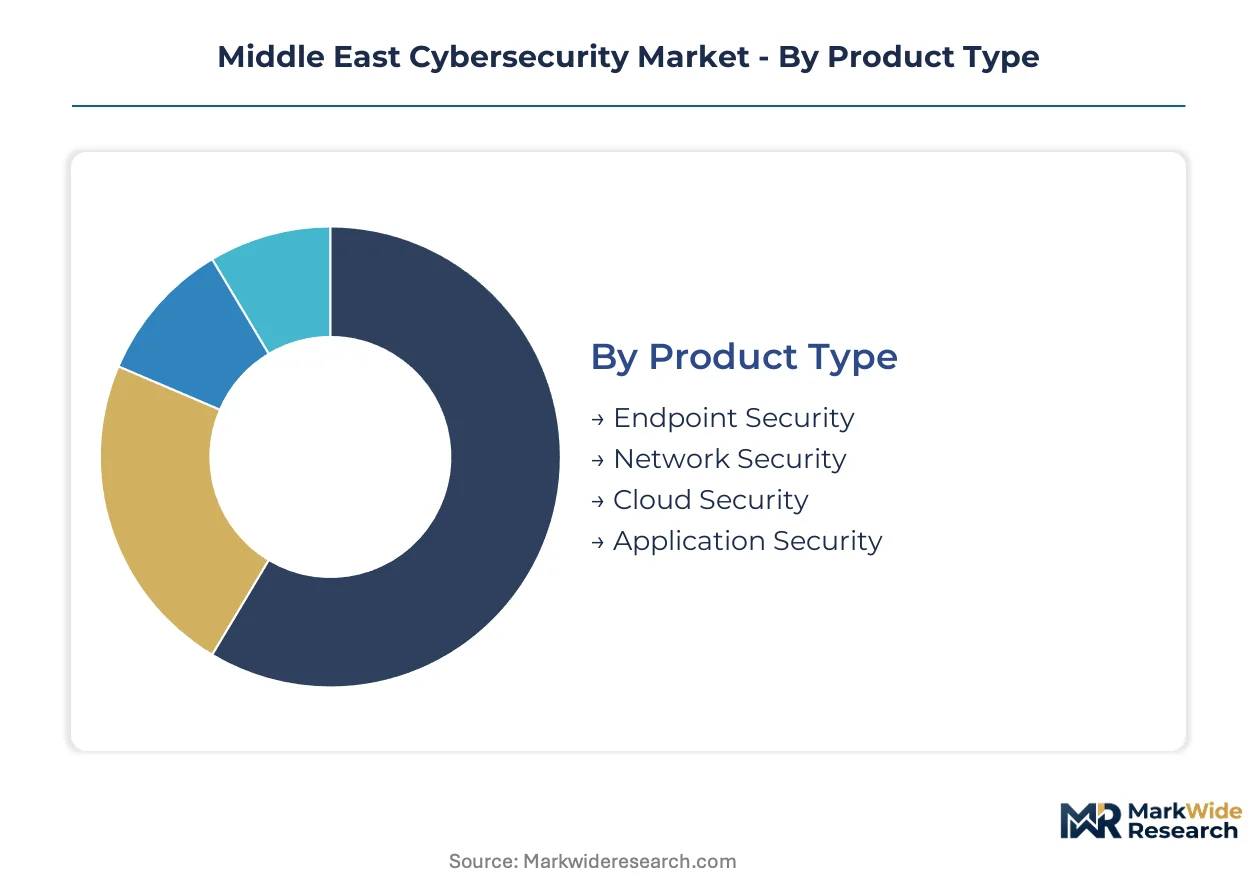
Procurement patterns across the Middle East diverge sharply by infrastructure maturity and regulatory exposure. Government cloud mandates and SCADA hardening requirements create distinct purchasing profiles that reshape how vendors configure product portfolios and service delivery models.
Product Type:
Use cases span from industrial control perimeter defense to SaaS-native data protection, with each segment commanding different technical specifications and compliance certifications.
- Network Security:Next-generation firewalls and intrusion prevention systems process traffic at 100 Gbps thresholds for Saudi Aramco and ADNOC operational technology environments. Gulf utilities mandate air-gapped segmentation, creating dedicated procurement streams for industrial-rated appliances with IEC 62443 certification.
- Cloud Security:Cloud-native posture management and encryption key escrow services address SCCC and FAN expansion requirements. Saudi government entities drive demand for sovereign cloud data loss prevention and identity governance admin consoles.
- Endpoint Security:Extended detection and response platforms with behavioral analytics protect distributed workforces in UAE banking groups.
- Application Security:API gateways and runtime application self-protection secure open banking interfaces and healthcare data exchanges.
The dominant share belongs to Network Security, while Cloud Security is closing the gap fastest.
Deployment Model:
Cost structures and operational control requirements segment buyers between capital-intensive appliance ownership and operationalized service consumption.
- Managed:Multi-year contracts bundle threat hunting, forensic retainer, and compliance reporting for Saudi sovereign wealth funds and national oil companies. Procurement officers favor risk transfer arrangements that offload 24/7 security operations to specialized providers.
- Cloud-Based:SASE architectures virtualize branch office stacks across Saudi petrochemical distributors and UAE retail banking networks. Subscription economics eliminate appliance refresh cycles while centralizing policy enforcement.
- On-Premises:Air-gapped deployments satisfy NESA and SDAIA data residency mandates for critical infrastructure operators.
- Hybrid:Split architectures accommodate workload portability between sovereign cloud instances and private data centers.
Managed deployments capture the largest contract value, though Cloud-Based adoption is expanding most quickly among mid-market enterprises.
End User:
Customer type determines procurement sophistication, with sovereign entities imposing certification requirements that filter vendor eligibility.
- Government:Federal entities across Saudi Arabia, UAE, and Qatar mandate cleared personnel and certified implementation partners. NESA compliance deadlines accelerate advisory and managed security service contracts with strict audit trail requirements.
- BFSI:Central Bank of Kuwait open banking directives and Saudi Arabian Monetary Authority cybersecurity frameworks drive API security and customer identity verification procurement. Tier-1 institutions maintain parallel ISO 27001 and national regulatory audit cycles.
- Healthcare:Patient data protection mandates spur investment in medical device security and encrypted health information exchanges.
- Retail:Payment card industry compliance and e-commerce platform protection dominate purchasing criteria.
Government verticals command the highest service attach rates, while BFSI demonstrates the steepest expansion trajectory as open banking regulations proliferate.
Service Type:
Margin concentration shifts toward advisory and ongoing operational support as hardware commoditization pressures appliance-centric revenue models.
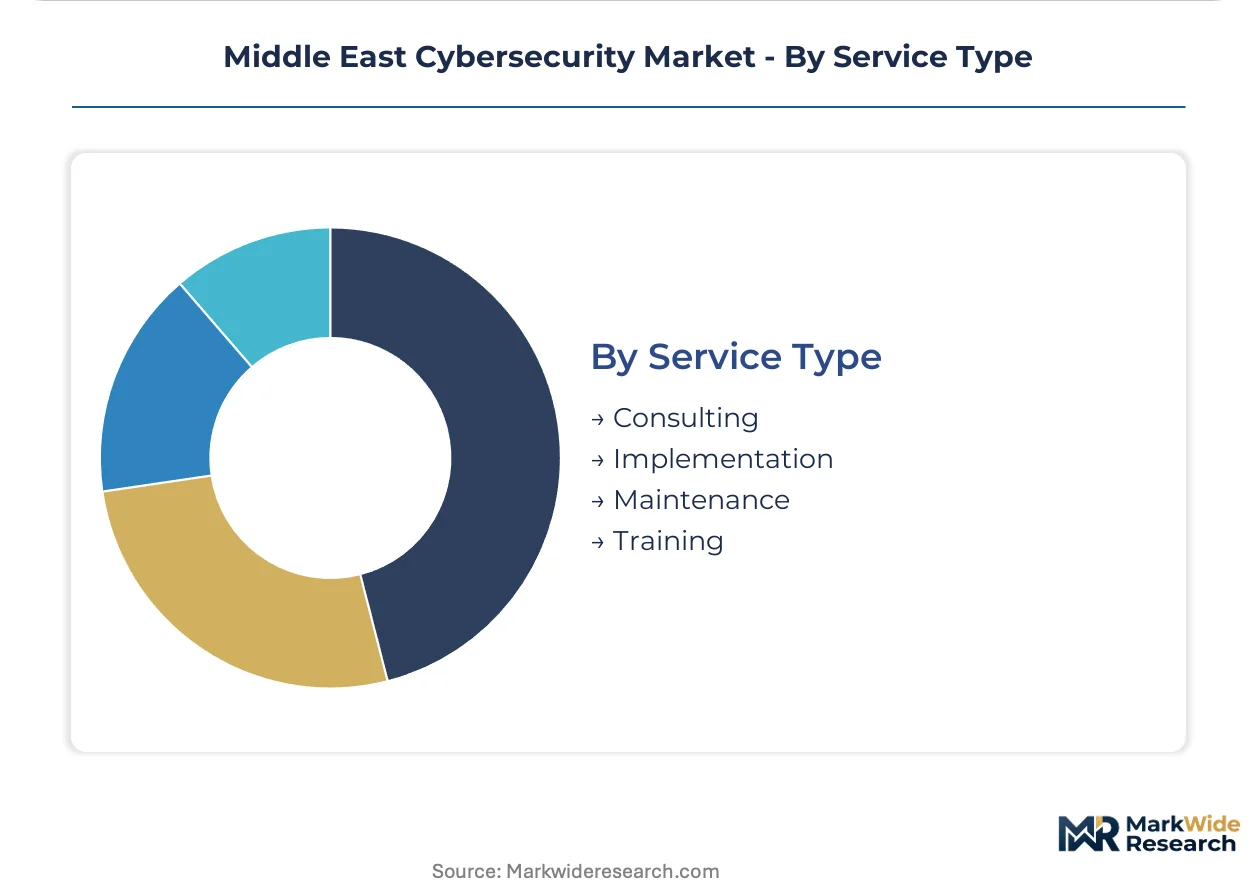
- Consulting:Privacy impact assessments and control gap analyses address SDAIA Personal Data Protection Law requirements exceeding baseline GDPR alignment. Data processors serving Saudi government entities require localized incident response capabilities with 72-hour reporting windows.
- Implementation:Certified deployment of NESA and SDAIA-compliant architectures commands premium pricing due to cleared personnel scarcity creating 6-12 month onboarding bottlenecks.
- Maintenance:Hardware refresh and signature update subscriptions sustain recurring revenue from installed firewall and endpoint protection bases.
- Training:OT security skill development addresses industrial control system vulnerability assessment capability gaps concentrated among specialized Gulf practitioners.
Consulting services generate the highest margins, with Implementation climbing fastest as compliance deadlines compress project timelines.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
NESA compliance mandates and SDAIA data governance rules are compressing procurement timelines across Gulf sovereign entities. Saudi Arabia and the UAE channel sovereign wealth capital into national digital transformation programs. Qatar and Kuwait are maturing their cybersecurity agency frameworks to match regional standards.
Saudi Arabia
Saudi Aramco and ADNOC are mandating air-gapped network segmentation for operational technology environments. SDAIA data residency rules fragment cloud architectures and force redundant infrastructure deployment. Riyadh-based banking groups and Eastern Province oil operators are driving dedicated procurement streams for industrial-rated appliances with IEC 62443 certification.
United Arab Emirates
UAE federal entities must complete NESA baseline control implementation by mandated phases, accelerating advisory contracts. The Federal Network (FAN) expansion drives demand for cloud-native security posture management. Dubai and Abu Dhabi financial institutions maintain parallel ISO 27001 and national regulatory audit cycles with strict audit trail requirements.
Qatar
The national cybersecurity agency's expanding certification framework creates first-mover advantage for integrators. NCSA maturation mandates cleared personnel and certified implementation partners for government contracts. Doha-based delivery centers are attracting regional security providers seeking Qatar-specific accreditation status.
Kuwait
Central Bank of Kuwait open banking directives accelerate API security procurement among tier-2 financial institutions. Customer identity verification mandates are reshaping retail banking technology budgets. Kuwait City financial services firms are embedding privacy engineers into product development cycles to meet tightened breach notification timelines.
Middle East Cybersecurity Market Competitive Landscape
On the supply side, the industry is consolidating around platform vendors capable of multi-year managed service contracts and regional system integrators with cleared personnel pools. Three strategic archetypes dominate: global platform consolidators with Gulf banking relationships, federally-integrated local champions with security clearance access, and appliance specialists competing on density metrics. M&A activity targets mid-market professional services firms, while strategic partnerships between global vendors and local integrators address personnel scarcity bottlenecks.
Within the federally-integrated tier, DarkMatter anchors its position through deep integration with UAE federal security architecture. Fortinet and Palo Alto Networks occupy positions at opposite ends of the appliance-versus-platform spectrum, with the former competing aggressively on appliance density and SD-WAN attach rates while the latter leverages platform consolidation to capture enterprise firewall refresh cycles. These three exemplify how vendor economics increasingly tie to outcome metrics rather than upfront hardware recognition.
| Leading Market Players |
|---|
| Fortinet |
| DarkMatter |
| Palo Alto Networks |
| Trend Micro |
| Help AG |
| Cisco Systems |
| IBM Corporation |
| Zscaler |
| Microsoft Corporation |
| Others |
Pricing and Supply Chain Analysis
Overcapacity in Asia-Pacific cryptographic module foundries is compressing hardware margins while concentrating bargaining power among cleared integrators in Saudi Arabia and the UAE. This utilization asymmetry forces multinational vendors to absorb certification costs or cede procurement cycles to federally-embedded local champions.
Pricing Analysis
Certification level creates the primary spread across the Middle East cybersecurity market, with NESA and SDAIA-accredited implementations commanding substantial premiums over uncertified alternatives. Pricing stratifies across sovereign-grade, enterprise-compliant, and commercial-off-the-shelf tiers, with hardware import dependencies and cleared personnel scarcity inflating implementation quotes. Cost compression in mid-market appliance sales is intensifying because Fortinet and Palo Alto Networks are competing aggressively on SD-WAN attach rates. Government verticals demonstrate the least price sensitivity due to mandated compliance deadlines, while retail and tier-2 healthcare providers remain highly cost-conscious.
Supply Chain Analysis
Upstream feedstock for cryptographic processors and tamper-resistant hardware security modules draws from concentrated foundry capacity in Taiwan, South Korea, and select European facilities. Specialized ASIC fabrication, FIPS 140-2 validated components, and industrial-rated firewall chassis rest on limited certified suppliers. Single-source vulnerability in advanced semiconductor lithography creates structural exposure for Gulf critical infrastructure operators. Distribution runs through cleared regional integrators with security personnel pools, bypassing direct vendor relationships for sovereign entity procurement.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is consolidating around Saudi sovereign wealth funds and UAE federal entities capable of dictating multi-year managed service terms. This concentration fragments pricing leverage for unaccredited vendors.
For Market Incumbents: Entrench platform consolidation advantages by embedding zero-trust architectures into SCCC and FAN sovereign cloud migrations before compliance deadlines harden procurement standards. Vertical integration into cleared personnel development in Riyadh and Abu Dhabi addresses the 6-12 month onboarding bottleneck threatening project delivery timelines. Prioritize IEC 62443 certification investments to capture Saudi Aramco and ADNOC OT segmentation mandates. For New Entrants and Emerging Players: Mid-market Kuwaiti tier-2 banks and Qatar NCSA early-phase certification represent the most penetrable entry points for API security and identity governance specialization. These segments lack incumbent saturation while regulatory pressure is accelerating procurement velocity. A channel partnership strategy with established UAE integrators bypasses direct security clearance requirements. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among managed detection and response providers serving Saudi national oil companies and sovereign wealth funds. Long-term viability across the projection horizon favors acquisition targets with cleared delivery centers in multiple Gulf jurisdictions. Monitor SDAIA enforcement actions against non-compliant data processors as an inflection indicator for compliance service demand spikes.| Strategic Initiative | Industry Significance |
|---|---|
| Cleared Personnel Center Establishment | Riyadh-based security operations centers capture Saudi Aramco and SDAIA-mandated contracts before competitors complete accreditation. |
| Sovereign Cloud Security Integration | Native posture management tools embedded in SCCC and FAN architectures create switching costs for federal procurement officers. |
| OT Security Specialist Acquisition | Industrial control system vulnerability capabilities address concentrated skill scarcity across Saudi Eastern Province oil operators. |
| Multi-Framework Compliance Automation | Parallel NESA, SDAIA, and NCSA audit tooling reduces operational burden for banking groups operating across Gulf jurisdictions. |
| Zero-Trust Network Access Platform Launch | Software-defined perimeter convergence with SASE architectures virtualizes branch security stacks for UAE retail banking networks. |
Research Methodology
Two parallel data streams informed the analysis: structured interviews with CISOs at Saudi banking groups, UAE federal procurement officers, Qatar NCSA certification leads, and OT security directors at national oil companies, combined with secondary validation against NESA control documentation, SDAIA executive regulations, SEC filings from Palo Alto Networks and Fortinet, and hyperscaler sovereign cloud expansion disclosures. Bottom-up segmentation modeling triangulated against top-down macroeconomic indicators derived from sovereign wealth fund capital allocation patterns.
Forecast inputs considered deployment model transitions, vertical regulatory exposure, and cleared personnel availability across the projection horizon. Segmentation dimensions modeled include product type, deployment architecture, end-user vertical, and certification tier. CAGRs were synthesized from historical procurement cycle analysis and forward-looking compliance deadline impacts. Industry-specific inputs incorporated NESA phase implementation schedules and SDAIA data residency enforcement intensity.
Practitioners should monitor NESA audit failure rates and SDAIA breach notification compliance for early signals of regulatory tightening that could accelerate procurement timelines. Cross-checking against hyperscaler sovereign cloud capex disclosures and national cybersecurity agency staffing budgets is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Europe Mobile Security Market
Cybersecurity
Europe Cybersecurity Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
India Ransomware Protection Market
Cybersecurity
Cyber Security As a Service Market
Cybersecurity
United Arab Emirates Cybersecurity Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
DNS Firewall Market
Cybersecurity
North America IoT Security Market
Cybersecurity
Europe IoT Security Market
Cybersecurity
Data Security Market
Cybersecurity
Internet of Things (IoT) Security Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Hong Kong Cybersecurity Market
Cybersecurity
Austria Cybersecurity Market