
 Italy Cybersecurity Market | 2026-2036
Italy Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Italy Cybersecurity Market Foresight
Italian banking is expanding its cybersecurity procurement faster than any other end-use vertical, driven by open banking APIs and instant payment rails that multiply attack surfaces. Leonardo S.p.A. anchors defense-grade solutions through its long-standing relationships with government and aerospace clients. IBM Corporation leverages its hybrid cloud security portfolio to compete for large financial institution contracts. Reply S.p.A. differentiates through managed detection and response services tailored to mid-market enterprises.
Cybersecurity encompasses technologies, processes, and practices designed to protect networks, devices, programs, and data from attack, damage, or unauthorized access through mechanisms such as encryption protocols, intrusion detection systems, and zero-trust architecture frameworks. Its primary commercial purpose is to ensure confidentiality, integrity, and availability of digital assets across interconnected business environments. Network Security solutions dominate spending among Italian utilities and transport operators managing legacy SCADA integrations, while Cloud Security represents the fastest-expanding solution category as enterprises migrate workloads to multi-tenant environments. The Maintenance service type captures recurring revenue streams as organizations shift from capital-intensive hardware refresh cycles toward subscription-based security operations.
Italy's national cybersecurity agency, ACN, coordinates incident response and critical infrastructure protection under the EU NIS2 Directive, while the GDPR enforcement by Italy's Garante per la Protezione dei Dati Personali shapes data breach notification and privacy-by-design requirements for security vendors. The EU Cybersecurity Act's certification schemes for ICT products create compliance gateways that filter market access for non-EU suppliers. Stakeholders must monitor how ACN's forthcoming sector-specific security mandates for energy and healthcare reshape procurement specifications and vendor qualification criteria.
Market Dynamics
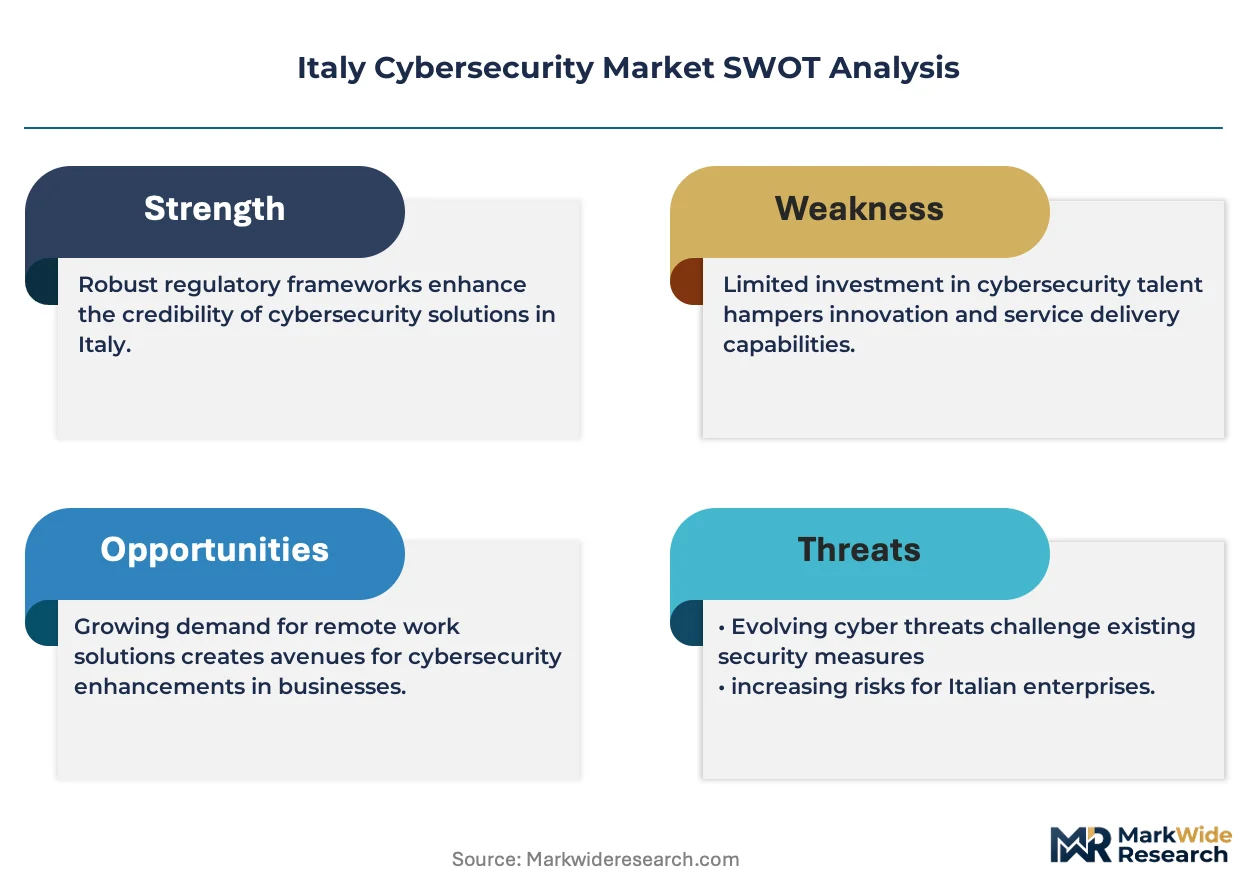
Italian cybersecurity procurement is reconfiguring around the EU NIS2 Directive's mandatory incident reporting windows and supply chain audit requirements, forcing critical infrastructure operators to consolidate vendor relationships and accelerate cloud security migration.
Growth Catalysts
- Instant payment rails:Open banking APIs and real-time transaction systems multiply attack surfaces across Italian financial institutions, expanding security procurement budgets.
- EU NIS2 Directive:Mandatory 24-hour incident reporting and supply chain risk management obligations create compliance-driven demand across energy, transport, and healthcare operators.
- Lombardy cluster density:Milan's financial district concentrates enterprise security buyers and service providers, generating network effects that accelerate technology adoption.
Market Restraints
- Certification bottlenecks:EU Cybersecurity Act's ICT product certification schemes filter market access for non-EU suppliers, extending vendor qualification timelines.
- Legacy SCADA integration costs:Italian utilities and transport operators face capital-intensive retrofitting of decades-old industrial control systems with modern security architectures.
- Talent scarcity:Domestic supply of zero-trust architects and threat intelligence analysts lags behind enterprise demand, inflating implementation costs.
Strategic Opportunities
- Managed detection and response:Mid-market enterprises seek outsourced security operations, creating white space for service providers between self-managed and fully outsourced models.
- Healthcare sector mandates:ACN's forthcoming sector-specific security requirements for healthcare operators will reshape procurement specifications and vendor qualification criteria.
- Multi-tenant cloud migration:Enterprises shifting workloads to hybrid environments drive fastest-expanding demand for cloud-native security solutions.
Industry Challenges
- Zero-trust skill gaps:Organizations struggle to recruit and retain architects capable of implementing identity-centric security frameworks across distributed environments.
- GDPR-Garante coordination:Italy's data protection authority enforces privacy-by-design requirements that complicate security vendor product development cycles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Italy Cybersecurity Market |
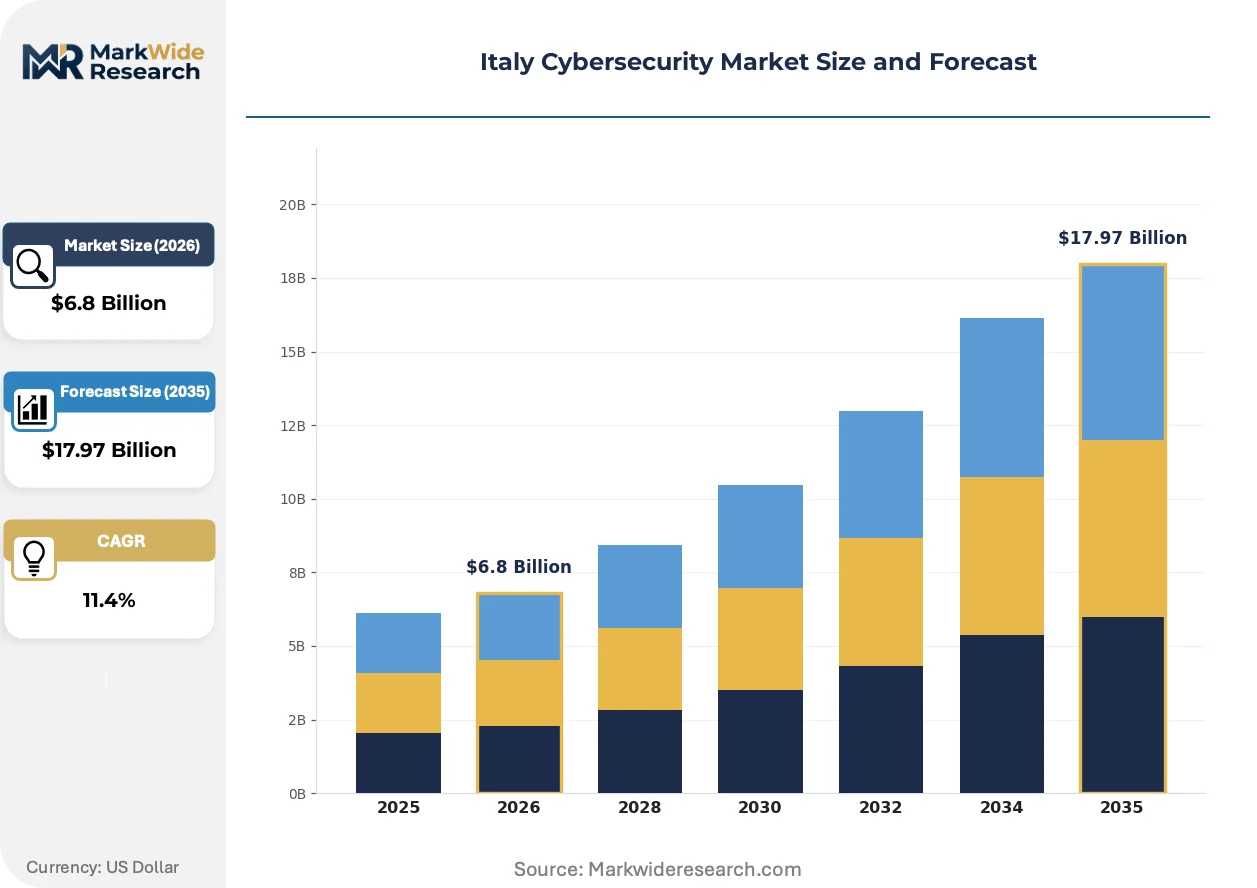
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $17.97 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Endpoint Security, Network Security, Application Security, Cloud Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed End User: Government, Banking, Retail, Healthcare Service Type: Consulting, Implementation, Maintenance, Training |
| Companies Covered | Dell Technologies Inc., Leonardo S.p.A., IBM Corporation, Reply S.p.A., Tinexta, Cisco Systems Inc, Broadcom Inc., Certego Srl, Trend Micro Incorporated, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Italy Cybersecurity Market Shifts & Advancements
Security architecture is pivoting from perimeter defense to identity-centric models, while regulatory compliance and procurement patterns reshape how Italian enterprises acquire and deploy protective technologies.
Zero-trust architecture is decentralizing access control across Italian banking and utility networks. Financial institutions migrating to open banking APIs are adopting identity-verification systems that authenticate every transaction request regardless of network origin. This shift compresses traditional network perimeter spending while expanding identity and access management procurement.
EU NIS2 Directive mandates are compressing vendor consolidation cycles across critical infrastructure operators. The directive's supply chain audit requirements force energy and transport companies to reduce supplier counts and demand deeper transparency from remaining partners. Healthcare operators anticipate similar obligations under ACN's forthcoming sector mandates, preemptively restructuring procurement frameworks.
Subscription-based security operations are displacing capital-intensive hardware refresh cycles among Italian mid-market enterprises. Organizations previously purchasing on-premise intrusion detection systems now favor managed detection and response services with predictable recurring costs. This behavioral shift concentrates demand in Lombardy's service provider corridor, where Reply and similar firms tailor offerings to buyers seeking outsourced threat monitoring without internal security operations center investment.
Italy Cybersecurity Market Segmentation
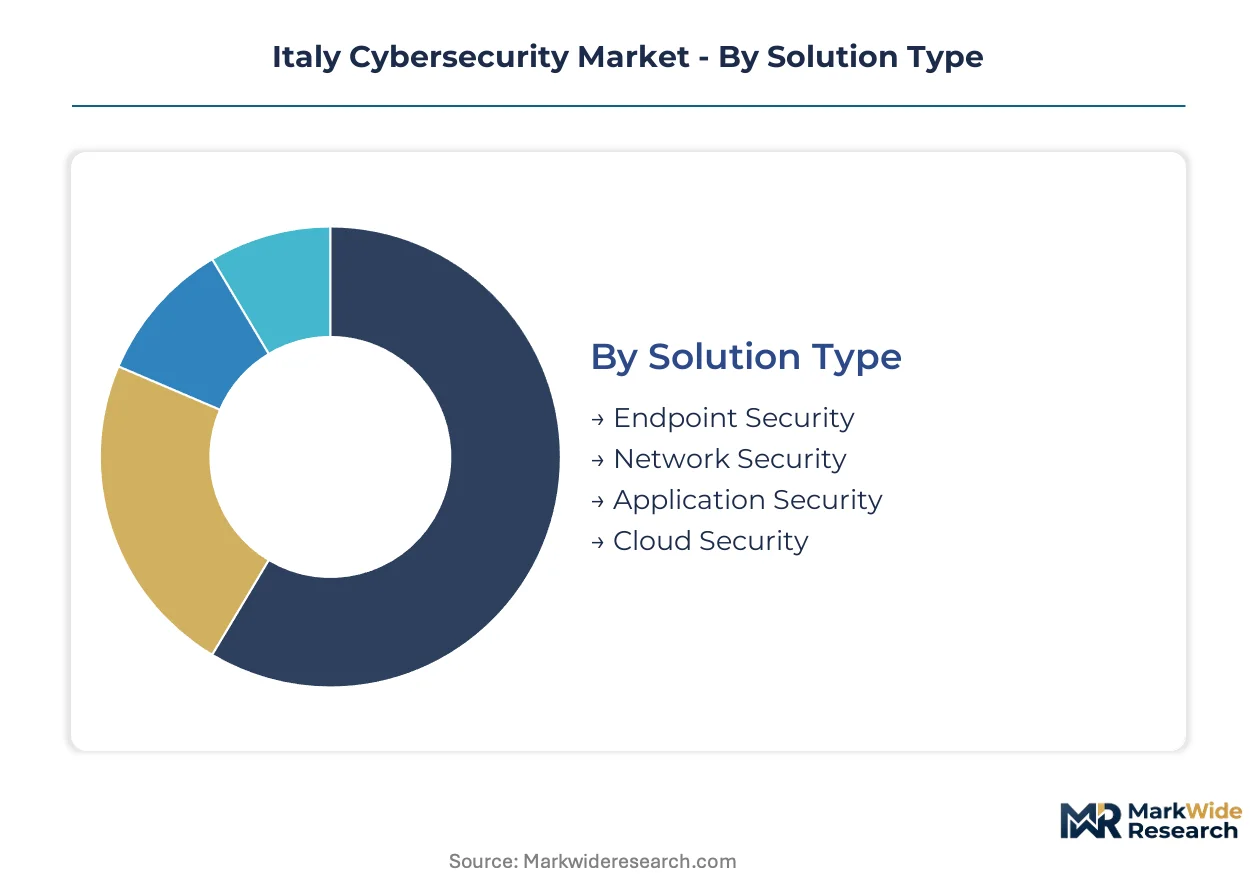
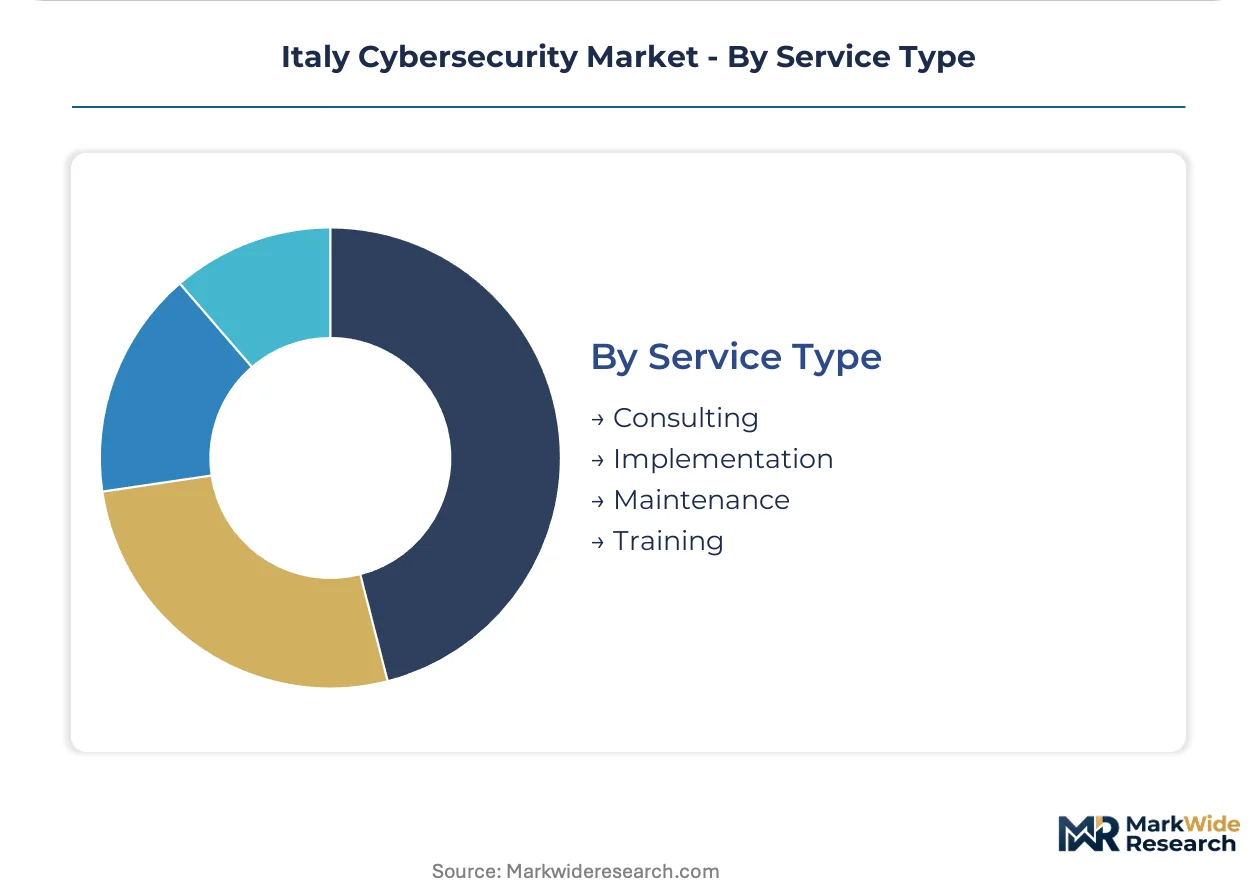
Italian cybersecurity procurement splits across four distinct taxonomies that reveal how organizations balance capital expenditure against operational flexibility. Each segmentation axis exposes different buyer priorities: solution type indicates technical maturity, deployment model signals risk tolerance, end user reflects regulatory exposure, and service type captures outsourcing appetite.
Solution Type:
Capital intensity varies sharply across protective technologies, with some requiring dedicated hardware appliances and others deploying through software licenses.
- Network Security:Firewalls, intrusion detection systems, and secure access service edge platforms protect traffic flows across enterprise infrastructure. Italian utilities and transport operators in Lombardy drive concentrated demand as they retrofit legacy SCADA systems with modern segmentation controls. The EU NIS2 Directive's mandatory incident reporting compresses procurement timelines for these operators.
- Cloud Security:Cloud-native workload protection, container security, and multi-tenant access controls secure distributed computing environments. Milan's financial district institutions expanding open banking APIs represent the densest demand cluster, with migration to hybrid architectures accelerating faster than on-premise refresh cycles.
- Endpoint Security:Antivirus, endpoint detection and response, and device control solutions protect individual workstations and mobile assets.
- Application Security:Static and dynamic testing tools, runtime application self-protection, and software composition analysis secure code repositories and production applications.
Most installed capacity flows through Network Security. Expansion is steepest in Cloud Security.
Deployment Model:
Procurement patterns reveal organizational preferences for control retention versus operational delegation, shaped heavily by ACN compliance obligations and data residency requirements.
- Managed:Fully outsourced security operations delivered through service level agreements with specialized providers. Mid-market enterprises across Italy's northern industrial belt favor this model to bypass zero-trust architect recruitment challenges while satisfying EU NIS2 supply chain audit demands.
- Hybrid:Split architectures combining on-premise control planes with cloud-delivered enforcement points. Banking institutions navigating GDPR-Garante coordination requirements adopt hybrid deployments to maintain sensitive data on-premise while leveraging cloud analytics for threat intelligence.
- On-Premises:Self-managed hardware and software deployed within organizational data centers.
- Cloud-Based:Fully SaaS-delivered security controls with no local infrastructure footprint.
Revenue concentration tilts toward Managed deployments. Hybrid architectures are gaining share fastest among regulated sectors.
End User:
Sector-specific regulatory exposure determines procurement sophistication and vendor qualification stringency.
- Banking:Payment processors, retail banks, and investment institutions managing instant payment rails and open banking APIs. This vertical commands the steepest security spending growth as transaction volumes surge and attack surfaces multiply across interconnected financial infrastructure.
- Government:National ministries, regional administrations, and defense agencies subject to ACN coordination mandates. Leonardo S.p.A.'s defense-grade relationships anchor procurement preferences for domestically controlled supply chains.
- Healthcare:Hospitals, pharmaceutical distributors, and medical device operators anticipating ACN sector-specific security mandates.
- Retail:E-commerce platforms, point-of-sale networks, and supply chain operators managing customer payment data.
Banking absorbs the largest procurement volume. Healthcare is climbing the fastest as forthcoming ACN requirements reshape specifications.
Service Type:
Revenue model preferences are shifting from project-based implementation toward recurring operational relationships.
- Maintenance:Ongoing monitoring, patch management, and threat response delivered through subscription agreements. Italian mid-market enterprises favor this predictable cost structure over capital-intensive hardware refresh cycles, concentrating demand among Lombardy's managed service provider corridor.
- Consulting:Risk assessments, compliance gap analyses, and security architecture design delivered through professional services engagements.
- Implementation:Deployment and integration of security technologies within existing infrastructure.
- Training:Workforce certification programs and security awareness education for technical and non-technical staff.
Maintenance captures the recurring revenue base. Consulting engagements are expanding most quickly as NIS2 readiness assessments proliferate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Lombardy's technology corridor concentrates Italy's densest cluster of enterprise security buyers and service providers, generating network effects that accelerate adoption across the national market.
Lombardy
Milan's financial district hosts the headquarters of major banking institutions expanding open banking API security and instant payment rail protections. The EU NIS2 Directive's mandatory incident reporting obligations compress procurement timelines for energy and transport operators headquartered here. ACN coordinates critical infrastructure protection mandates from offices in the regional capital, shaping vendor qualification criteria for domestic and international suppliers.
Piedmont
Turin's automotive and aerospace manufacturing base drives demand for industrial control system security and supply chain risk management solutions. The EU Cybersecurity Act's ICT product certification schemes filter market access for component suppliers serving defense-grade contractors. Leonardo S.p.A. maintains significant operational presence in the region, anchoring procurement preferences for domestically controlled security architectures.
Veneto
Padua and Verona host pharmaceutical and medical device manufacturers anticipating ACN's forthcoming sector-specific security mandates for healthcare operators. GDPR enforcement by Italy's Garante per la Protezione dei Dati Personali shapes privacy-by-design requirements for security vendors serving this vertical. The region's logistics hubs concentrate demand for endpoint protection across distributed supply chain networks.
Emilia-Romagna
Bologna's machinery and packaging equipment manufacturers retrofit legacy SCADA systems with modern segmentation controls to satisfy EU NIS2 supply chain audit requirements. The region's industrial automation density creates concentrated demand for network security solutions managing legacy industrial control system integrations. Mid-market enterprises here favor managed detection and response services to bypass zero-trust architect recruitment challenges.
Lazio
Rome's government and defense agencies subject to ACN coordination mandates drive procurement for nationally controlled security supply chains. The national cybersecurity agency's headquarters location shapes regulatory interpretation and enforcement patterns across critical infrastructure sectors. Public administration digitalization programs expand demand for cloud security solutions with data residency guarantees.
Italy Cybersecurity Market Competitive Landscape
Strategic partnerships dominate the current landscape as vendors consolidate capabilities to address EU NIS2 compliance requirements and supply chain audit demands. The market exhibits tiered concentration with defense-grade specialists, global technology conglomerates, and regional managed service providers occupying distinct competitive positions. Three archetypes define the structure: domestically anchored contractors serving government and aerospace clients, multinational platforms competing for financial institution contracts, and mid-market service specialists delivering outsourced operations. Portfolio diversification and geographic expansion through channel partnerships represent the dominant competitive vectors.
Among Italy-based specialists, Leonardo S.p.A. exemplifies the defense-grade contractor archetype through its long-standing government relationships, while Reply S.p.A. occupies a position within the managed service provider tier tailored to mid-market outsourcing demand. IBM Corporation represents the multinational platform archetype competing for large financial institution contracts with hybrid cloud security portfolios. These three anchors illustrate how vendor selection criteria diverge across regulated sectors, procurement sophistication levels, and risk tolerance profiles.
| Leading Market Players |
|---|
| Dell Technologies Inc. |
| Leonardo S.p.A. |
| IBM Corporation |
| Reply S.p.A. |
| Tinexta |
| Cisco Systems Inc |
| Broadcom Inc. |
| Certego Srl |
| Trend Micro Incorporated |
| Others |
Supply & Pricing Matrix
Private-equity-rolled-up managed security service providers across Lombardy and Lazio anchor pricing discipline through recurring revenue lock-in, while their concentrated ownership structures compress channel margins and enforce standardized service tiers across the Italian cybersecurity market.
Pricing Analysis
Distributor margins on security hardware appliances range from 15 to 25 percent, while managed service providers capture 40 to 60 percent gross margins on recurring detection and response contracts. Three-tier pricing structure across premium defense-grade, standard enterprise, and economy mid-market levels differentiates Leonardo S.p.A.'s government-facing offerings from Reply S.p.A.'s outsourced operations. Pricing pressure stems from EU Cybersecurity Act certification costs that non-EU vendors pass through to Italian buyers. Mid-market enterprises show highest price sensitivity, deferring capital expenditure in favor of subscription-based security operations with predictable monthly outlays.
Supply Chain Analysis
Zero-trust architect and threat intelligence analyst shortages across Milan, Turin, and Rome constrain service provider capacity expansion and inflate implementation timelines for complex security transformations. Hardware component sourcing draws from Taiwan for semiconductor-based encryption modules, Israel for advanced threat detection sensors, and Germany for industrial control system gateways. Single-source vulnerability around specialized cryptographic processors creates procurement risk for defense-grade contractors serving ACN-coordinated agencies. Distribution runs through value-added resellers concentrated in Lombardy's technology corridor, with direct OEM relationships dominating government and banking procurement.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Italy cybersecurity market functions as a stable compounder, with EU NIS2 Directive compliance obligations generating recurring procurement cycles that insulate revenue streams from discretionary budget cuts.
For Market Incumbents: Extend managed detection and response capabilities into healthcare and pharmaceutical verticals before ACN sector-specific mandates crystallize procurement specifications. Consolidate vendor partnerships to satisfy supply chain audit requirements, reducing supplier counts from fragmented portfolios to three to five strategic relationships. Deepen backward integration into threat intelligence data feeds to differentiate from commodity security operations.
For New Entrants and Emerging Players: Enter via cloud-native workload protection tools targeting Milan's financial district institutions migrating open banking APIs to hybrid architectures. White space concentrates in mid-market enterprises across Emilia-Romagna's industrial automation belt seeking outsourced security operations without internal SOC investment. Partner with established Lombardy service providers for channel access rather than building direct sales infrastructure.
For Investors and Strategic Acquirers: Valuations sit cheapest among regional managed security specialists with concentrated healthcare or utility client bases and limited geographic diversification. Long-term viability rests on recurring revenue visibility from multi-year managed service contracts rather than project-based implementation fees. Monitor ACN enforcement patterns and NIS2 penalty structures as inflection indicators for compliance-driven procurement acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Managed Detection and Response Expansion | Captures recurring revenue from mid-market enterprises bypassing internal SOC construction in Lombardy. |
| EU Cybersecurity Act Certification Investment | Unlocks government and critical infrastructure procurement channels requiring ICT product assurance schemes. |
| Healthcare Sector Pre-positioning | Establishes vendor relationships before ACN sector-specific security mandates reshape procurement specifications. |
| Threat Intelligence Platform Integration | Differentiates service offerings through proprietary data feeds sourced from banking and government incident response. |
| Hybrid Cloud Security Partnership | Addresses Milan financial institutions' GDPR-Garante data residency requirements while leveraging cloud analytics. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with CISOs at banking and utility institutions, ACN policy officials, procurement managers at Leonardo S.p.A. and Reply S.p.A., and channel partners across Lombardy's technology corridor with secondary validation through ENISA threat landscape reports, EU NIS2 implementation guidance, Garante enforcement case databases, and ACN sector security directives. Bottom-up service provider revenue aggregation and top-down critical infrastructure spending estimates were triangulated against regulatory compliance timeline assumptions.
Segment-weighting approaches applied differential growth rates across solution types, deployment models, end-user verticals, and service categories, with network security and cloud security receiving distinct trajectory assumptions based on legacy SCADA retrofit cycles versus hybrid migration patterns. CAGRs were derived from historical spending correlations with digital payment volume growth, regulatory enforcement intensity, and managed service adoption curves. Forecast inputs incorporated EU NIS2 implementation phase transitions and ACN sector mandate rollout sequencing without specifying calendar years.
Inputs from primary stakeholder interviews and published regulatory guidance were available through the study window; gaps in real-time breach cost data and vendor-specific contract terms introduce uncertainty bands around enterprise spending estimates. Forecasts reflect assumptions regarding steady EU NIS2 enforcement and ACN coordination capacity expansion. Material deviation in penalty structures, certification timeline delays, or sovereign cyber incident response funding warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Indonesia Cybersecurity Market
Cybersecurity
Europe SOC As a Service Market
Cybersecurity
Cloud Authentication Market
Cybersecurity
India Cybersecurity Market
Cybersecurity
Next-Gen Firewall Market
Cybersecurity
Japan Ransomware Protection Market
Cybersecurity
Global Bug Bounty Platforms Market
Cybersecurity
Firewall-As-A-Service (Fwaas) Market
Cybersecurity
Industrial Cybersecurity Market
Cybersecurity
Network Traffic Analysis Solutions Market
Cybersecurity
Cyber Deception Market
Cybersecurity
Information Security Products and Services Market
Cybersecurity
Network Security Market
Cybersecurity
Cloud-Based Database Security Market
Cybersecurity
5G Security Market
Cybersecurity
Thailand Cybersecurity Market