
 DNS Firewall Market | 2026-2036
DNS Firewall Market Size, Share, and Industry Trends Forecast 2026-2036
DNS Firewall Market Analysis
Shortage of cybersecurity professionals with DNS-layer expertise is reorganizing how enterprises procure and manage DNS firewall infrastructure. Cisco Systems, Inc. leverages its integrated networking portfolio to bundle DNS security with core routing equipment. Cloudflare, Inc. competes through its globally distributed resolver network and edge-native deployment model. Infoblox Inc. specializes in DDI (DNS, DHCP, IPAM) convergence, anchoring its firewall offerings in enterprise address management workflows.
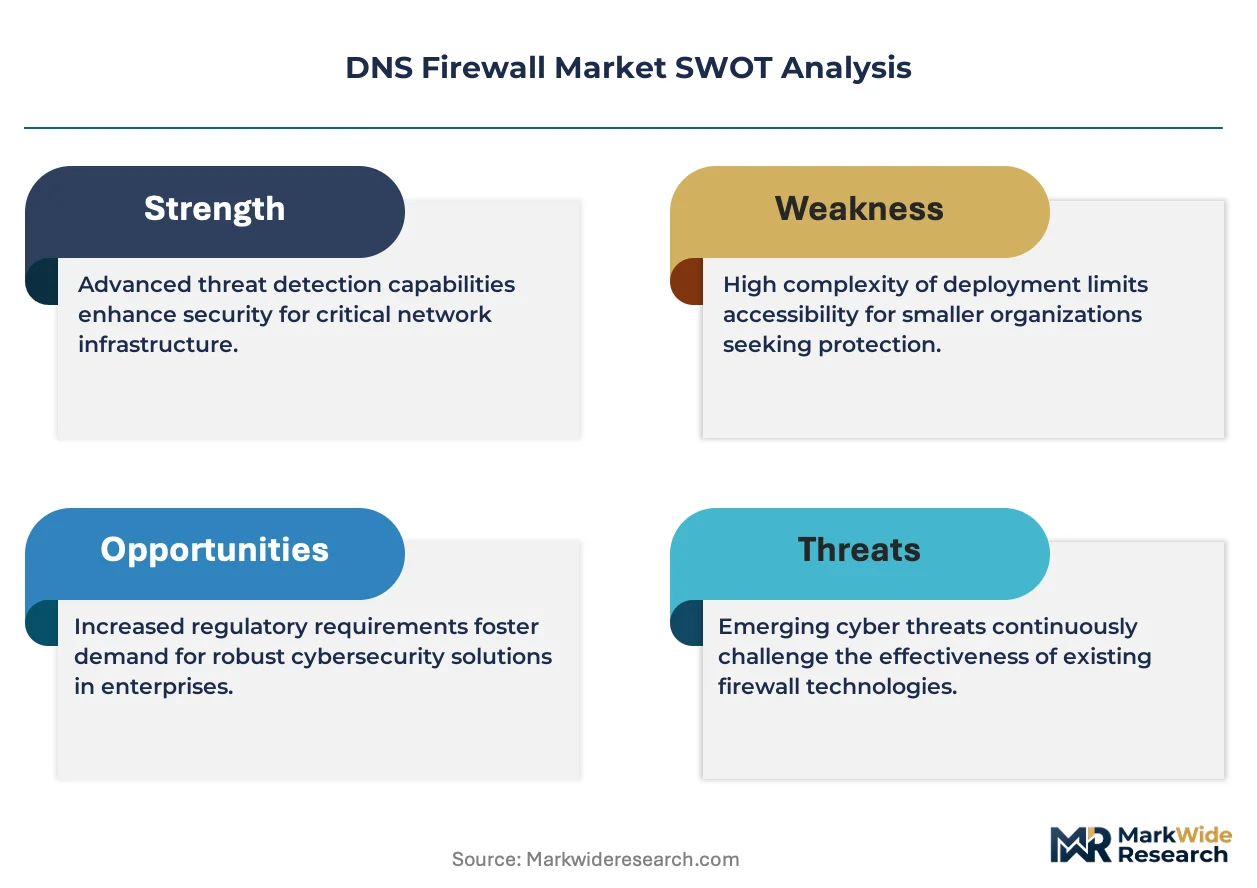
A DNS firewall is a network security solution that inspects and filters DNS query traffic at the protocol layer, typically operating at port 53 with policy engines that block resolution to malicious domains, sinkhole botnet command-and-control channels, and prevent data exfiltration via DNS tunneling. Its primary commercial purpose is to stop threats before IP connections are established, reducing lateral movement and malware activation. Cloud-Based deployment is capturing the fastest expansion as organizations abandon appliance-heavy footprints for elastic, API-driven protection. Threat Intelligence services command premium pricing because real-time domain reputation feeds differentiate effective blocking from static rule sets. Enterprises remain the dominant end-user category, though government agencies are accelerating procurement under tightened critical infrastructure mandates.
The U.S. FCC and NIST Cybersecurity Framework shape domestic product requirements for DNS integrity and supply-chain attestation, while the EU's NIS2 Directive and ENISA guidelines impose cross-border DNS security standards for operators of essential services. These frameworks push vendors toward certified, auditable platforms rather than point tools. Stakeholders must weigh whether to consolidate DNS security within broader SASE architectures or retain standalone best-of-breed deployments as architecture decisions lock in multi-year operational trajectories.
Market Dynamics
The migration from on-premise DNS appliances to cloud-native resolver services is compressing deployment timelines and forcing incumbent vendors to rearchitect delivery models around API-first consumption patterns.
Growth Catalysts
- Zero-trust architecture mandates:Federal agencies and defense contractors under NIST SP 800-207 guidance are mandating DNS-layer inspection as a non-negotiable control point for identity verification and microsegmentation.
- DNS tunneling proliferation:State-sponsored threat actors and ransomware operators are weaponizing DNS for covert command-and-control, compelling financial services and healthcare providers to deploy protocol-layer filtering.
- EU NIS2 Directive:Critical infrastructure operators across energy, transport, and digital infrastructure must implement DNS security measures with mandatory incident reporting, creating procurement urgency.
Market Restraints
- Skilled operator scarcity:Enterprise security teams lack personnel capable of tuning DNS policy engines, threat intelligence feeds, and false-positive management, constraining deployment velocity.
- Resolver concentration risk:Cloud-based DNS security depends on hyperscale resolver networks operated by a limited set of infrastructure providers, creating single-point-of-failure exposure.
- Encrypted DNS friction:DNS-over-HTTPS and DNS-over-TLS protocols are obscuring query visibility for inspection engines, degrading threat detection efficacy without endpoint agent deployment.
Strategic Opportunities
- SASE convergence:Security vendors are integrating DNS firewall capabilities into unified secure access service edge platforms, displacing standalone appliance purchases in enterprise refresh cycles.
- Operational technology networks:Manufacturing and utility sectors are extending DNS protection to industrial control systems, where legacy flat networks previously lacked protocol-layer segmentation.
- Managed detection and response bundling:MSSPs are packaging DNS firewall management with 24/7 SOC services, capturing mid-market buyers lacking in-house security operations capacity.
Industry Challenges
- Threat intelligence integration complexity:Security teams struggle to normalize and operationalize multiple domain reputation feeds from commercial providers, open-source projects, and industry-sharing consortia.
- Legacy infrastructure coexistence:Hybrid environments with BIND, Microsoft DNS, and cloud resolver services require policy synchronization across incompatible management planes, extending deployment timelines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | DNS Firewall Market |
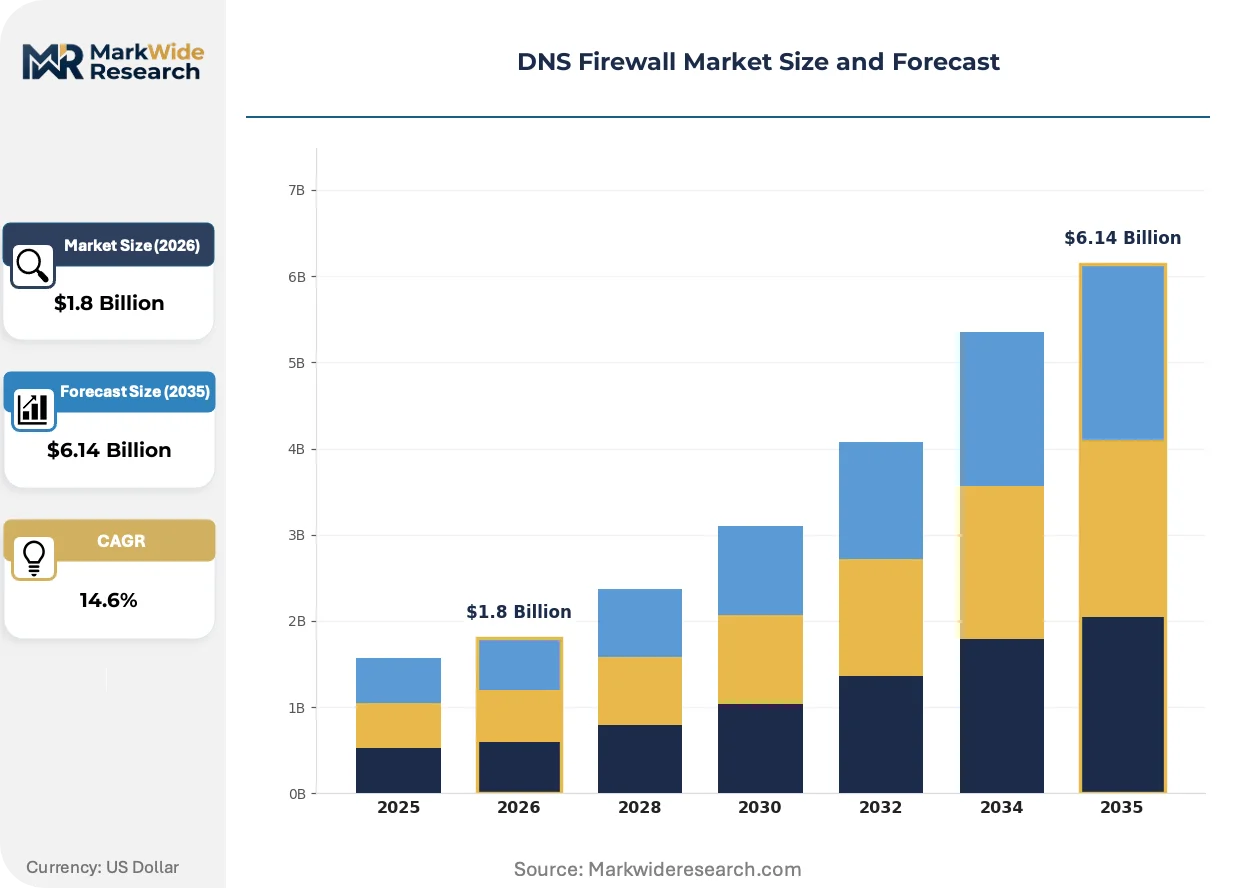
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $6.14 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service Type: Type of Attack Mitigation, Threat Intelligence, Incident Response, Reporting End User: Enterprises, Educational Institutions, Government Agencies, SMBs Integration Level: API Integration, Custom Integration, Third-Party Integration, Native Integration |
| Companies Covered | F5, Inc., IBM Corporation, Cisco Systems, Inc., BlueCat Networks, Inc., EfficientIP, Cloudflare, Inc., DigiCert, Inc., Allied Telesis Holdings Co., Ltd., Infoblox Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
DNS Firewall Market Emerging Trajectories
Artificial intelligence is reshaping how DNS security platforms detect anomalous query patterns and automate response actions. Three developments are compressing competitive differentiation windows and redefining procurement criteria.
Machine learning-based domain generation algorithm detection is fragmenting threat intelligence value chains. These models identify algorithmically generated domains used for botnet command-and-control by analyzing lexical patterns and registration behaviors. Financial institutions and telecommunications operators are deploying these capabilities as native cloud resolver features rather than separate appliance purchases. The technology is fragmenting the standalone threat intelligence market by embedding predictive blocking directly into DNS infrastructure.
The EU's NIS2 Directive is mandating DNS security controls for operators of essential services with cross-border harmonization requirements. Member states must designate competent authorities and enforcement mechanisms by October 2024, compelling vendors to pursue certification schemes aligned with ENISA guidelines. Critical infrastructure operators in Germany, France, and the Netherlands are prioritizing auditable, certified platforms over uncertified point solutions in procurement evaluations.
Consumption-based billing for DNS security is displacing perpetual license models in enterprise procurement. Organizations are negotiating per-query or per-user pricing aligned with cloud migration patterns rather than upfront capital expenditure. This shift is most pronounced in United States technology and media sectors, where elastic infrastructure spending aligns with variable traffic volumes and seasonal scaling requirements.
DNS Firewall Market Segmentation
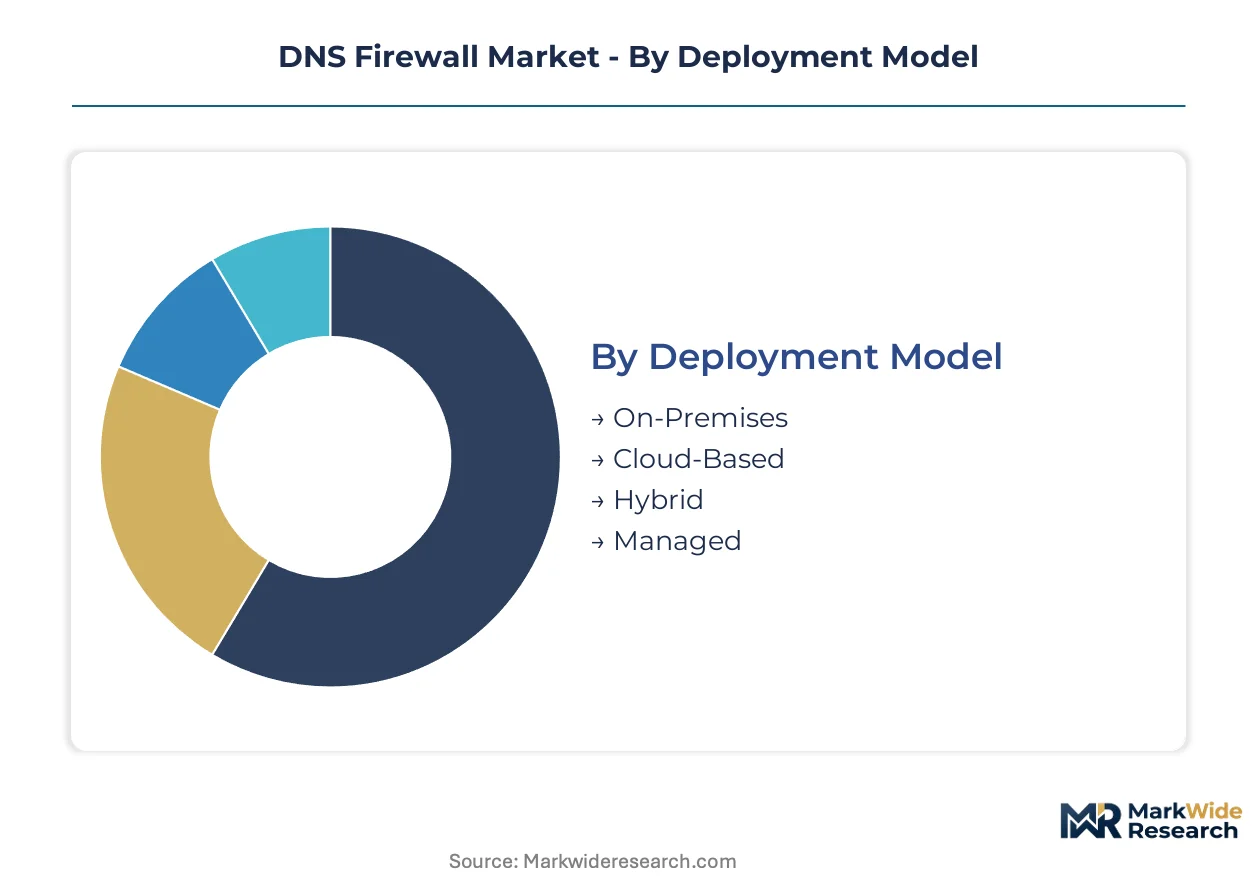
DNS firewall procurement patterns diverge sharply across deployment architectures and organizational maturity levels. Buyers with sophisticated security operations favor integrated platforms, while resource-constrained segments drive managed service adoption. Understanding these fault lines clarifies where vendors must differentiate pricing, packaging, and channel strategy.
Deployment Model:
Cloud-Based deployments concentrate demand in the United States technology sector, where elastic infrastructure spending aligns with variable traffic patterns. On-Premises solutions retain strength in German manufacturing and Japanese financial services, where data residency requirements override cloud migration incentives.
- Cloud-Based:Elastic resolver networks deliver DNS security via API-driven consumption models. United States enterprises in technology and media sectors are abandoning capital expenditure models for per-query billing aligned with seasonal scaling requirements.
- On-Premises:Physical or virtual appliances operate within organizational network boundaries, offering direct control over query inspection and policy enforcement. German automotive manufacturers and Japanese banking consortia favor this model to satisfy domestic data localization mandates and audit trail requirements.
- Hybrid:Split-horizon architectures route internal queries through on-premise resolvers while external resolution leverages cloud infrastructure. French healthcare networks deploy this pattern to isolate patient data systems while maintaining internet-facing threat protection.
- Managed:Third-party operators assume full responsibility for DNS firewall deployment, tuning, and 24/7 monitoring. United Kingdom mid-market financial services firms lacking in-house security operations capacity are accelerating procurement of managed DNS security services.
On-Premises holds the largest share; momentum sits with Cloud-Based.
Service Type:
Threat Intelligence commands premium pricing due to real-time domain reputation differentiation. Incident Response services attract buyers in regulated sectors facing mandatory breach notification timelines.
- Type of Attack Mitigation:Core DNS-layer blocking capabilities intercept queries to malicious domains, sinkhole botnet command-and-control channels, and disrupt DNS tunneling attempts. United States federal contractors under zero-trust mandates treat this as non-negotiable infrastructure.
- Threat Intelligence:Continuous domain reputation feeds from commercial providers, open-source projects, and industry-sharing consortia enable predictive blocking. Financial institutions in Singapore and Switzerland negotiate multi-source intelligence bundles to reduce false-positive rates.
- Incident Response:Specialized teams investigate DNS-based indicators of compromise, coordinate takedown actions, and support forensic analysis. Healthcare providers in Australia facing mandatory breach reporting obligations are expanding retainer-based incident response coverage.
- Reporting:Audit-ready documentation of DNS query flows, policy violations, and threat block events supports compliance attestation. Dutch energy utilities under NIS2 Directive requirements prioritize platforms with built-in regulatory reporting templates.
Threat Intelligence generates the highest margins; Incident Response is climbing the fastest.
End User:
Enterprise procurement concentrates in financial services and telecommunications, where DNS-layer visibility supports both security and network performance optimization. Government Agencies represent the most price-insensitive segment due to critical infrastructure protection mandates.
- Enterprises:Large organizations with dedicated security operations centers deploy DNS firewalls as identity verification control points within zero-trust architectures. United States defense contractors and multinational banks operate the most sophisticated deployments.
- Government Agencies:National, regional, and municipal entities procure DNS security under tightened critical infrastructure mandates. German federal authorities and French regional operators of essential services are accelerating certified platform procurement ahead of enforcement deadlines.
- Educational Institutions:Universities and research networks face unique challenges from decentralized IT governance and high-volume research traffic. United Kingdom Russell Group universities are consolidating DNS security within shared services frameworks.
- SMBs:Small and medium businesses without dedicated security personnel rely on bundled or managed offerings. Canadian healthcare clinics and Australian professional services firms are migrating from consumer-grade protection to business-tier DNS security.
Enterprises dominate absolute spending; Government Agencies show the steepest expansion trajectory.
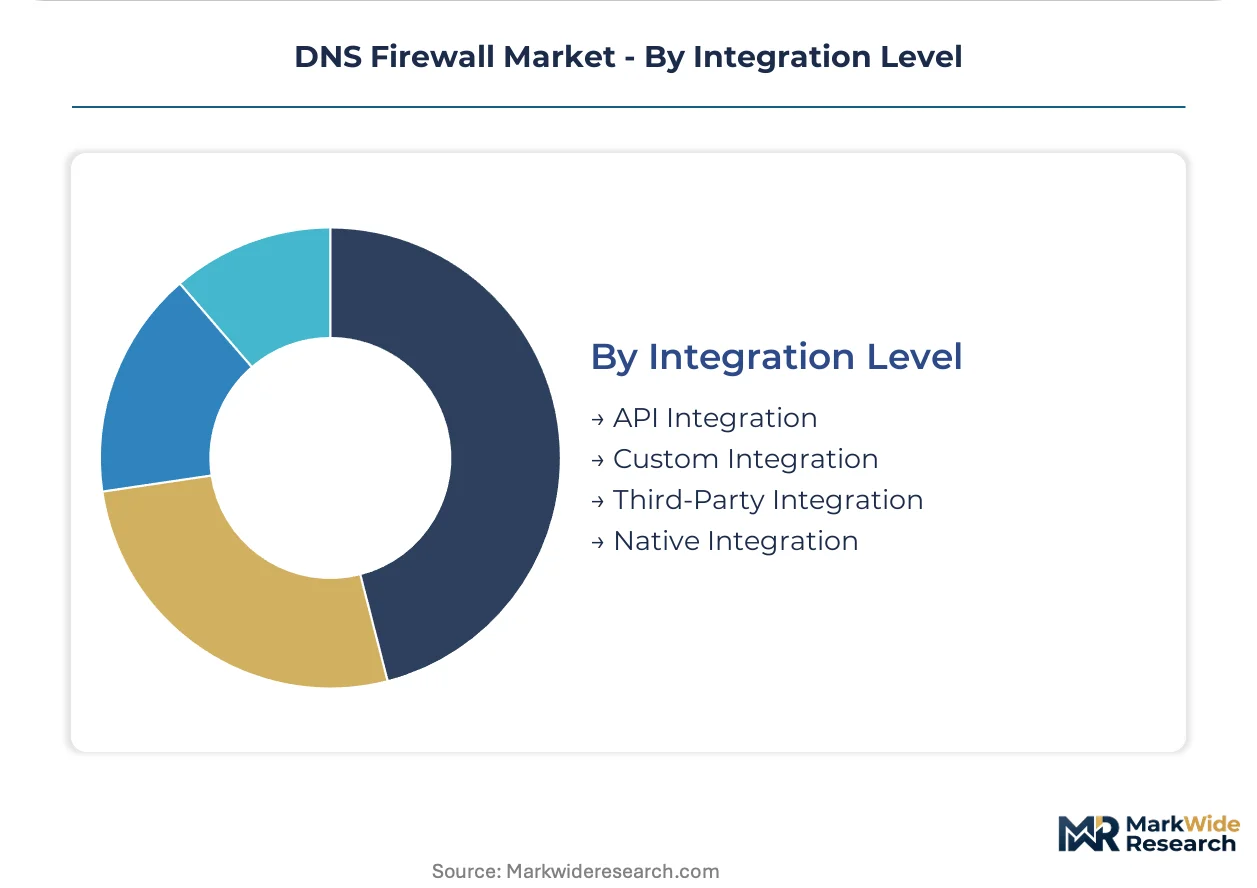
Integration Level:
API Integration attracts buyers with mature DevOps practices seeking infrastructure-as-code deployment. Native Integration appeals to organizations pursuing vendor consolidation within broader security platforms.
- API Integration:RESTful and GraphQL interfaces enable automated policy deployment, real-time threat feed ingestion, and SIEM correlation. United States cloud-native enterprises in software and digital media standardize on API-first procurement criteria.
- Native Integration:Pre-built connectors within unified security platforms eliminate separate DNS firewall procurement. Organizations adopting SASE architectures in the Netherlands and Sweden favor this consolidation path.
- Third-Party Integration:Certified connectors to established security vendors allow incremental DNS-layer enhancement without platform replacement. Italian manufacturing networks with legacy Cisco or Palo Alto investments pursue this intermediate strategy.
- Custom Integration:Bespoke development connects DNS firewalls to proprietary systems or specialized industrial control environments. Saudi Aramco and other national oil companies commission custom integrations for operational technology network segmentation.
Native Integration captures the largest installed base; API Integration is gaining share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The FCC and NIST Cybersecurity Framework shape domestic product requirements for DNS integrity in the United States, while the EU's NIS2 Directive and ENISA guidelines impose cross-border DNS security standards for operators of essential services across member states.
United States
Federal agencies and defense contractors under NIST SP 800-207 guidance mandate DNS-layer inspection as a non-negotiable control point for zero-trust implementation. The FCC regulates telecommunications infrastructure security with escalating DNS integrity requirements. Technology clusters in Silicon Valley and Seattle drive cloud-native resolver adoption for elastic, API-driven protection.
Germany
Automotive manufacturers and banking consortia favor on-premise appliances to satisfy domestic data localization mandates and audit trail requirements. The Federal Office for Information Security enforces strict DNS security controls under NIS2 transposition deadlines. Industrial networks in Bavaria and Baden-Württemberg prioritize certified platforms with built-in regulatory reporting templates.
United Kingdom
Russell Group universities consolidate DNS security within shared services frameworks to address decentralized IT governance challenges. The National Cyber Security Centre publishes guidance on DNS-layer threat mitigation for critical national infrastructure. Mid-market financial services firms in London accelerate procurement of managed DNS security services lacking in-house operations capacity.
France
Regional operators of essential services prioritize auditable, certified platforms ahead of NIS2 enforcement deadlines. ANSSI mandates DNS security measures for energy, transport, and digital infrastructure operators with mandatory incident reporting. Healthcare networks in Île-de-France deploy split-horizon architectures to isolate patient data systems while maintaining internet-facing threat protection.
Singapore
Financial institutions negotiate multi-source threat intelligence bundles to reduce false-positive rates in high-frequency trading environments. The Monetary Authority of Singapore imposes DNS security obligations on systemically important financial institutions. Technology corridors in one-north and Changi Business Park anchor cloud-native resolver deployments for regional headquarters operations.
DNS Firewall Market Vendor Landscape
A small set of integrated leaders sits above a broader specialist tier, creating a two-tier structure where scale advantages compound around threat intelligence depth and resolver network distribution. The upper tier bundles DNS security with adjacent networking or cloud infrastructure portfolios, while specialists anchor in DDI convergence or protocol-layer optimization. Strategic archetypes include integrated networking vendors, cloud-native edge platforms, and DDI workflow specialists. Competitive moves center on SASE architecture convergence and managed detection and response bundling to capture mid-market buyers.
Within the integrated networking tier, Cisco Systems, Inc. and F5, Inc. occupy positions where DNS security attaches to core routing and application delivery infrastructure. Cloudflare, Inc. exemplifies the cloud-native archetype through its globally distributed resolver network and edge-native deployment model. Infoblox Inc. anchors the DDI specialist position, embedding firewall capabilities within enterprise address management workflows that govern DNS, DHCP, and IPAM convergence.
| Leading Market Players |
|---|
| F5, Inc. |
| IBM Corporation |
| Cisco Systems, Inc. |
| BlueCat Networks, Inc. |
| EfficientIP |
| Cloudflare, Inc. |
| DigiCert, Inc. |
| Allied Telesis Holdings Co., Ltd. |
| Infoblox Inc. |
| Others |
Supply Flow & Price Mechanics
Hyperscale resolver network density in United States cloud infrastructure creates non-linear cost advantages that compress price floors for on-premise appliance vendors while elevating margins for API-native delivery. German automotive manufacturers and Japanese banking consortia absorb 40-60% premiums for certified, data-localized deployments that satisfy BSI and FISC audit requirements.
Pricing Analysis
United States enterprises negotiate per-query billing 30-50% below equivalent European contract values due to elastic infrastructure density and competitive hyperscaler dynamics. Three-tier pricing structure across premium threat-intelligence bundles, standard resolver services, and economy-grade filtering tiers separates financial institutions from mid-market manufacturing buyers. Cost compression in the mid-tier is intensifying because Cloudflare and Amazon Route 53 are absorbing resolver infrastructure costs to capture platform stickiness. Government agencies show the least price sensitivity due to zero-trust mandate compliance deadlines.
Supply Chain Analysis
Hardware lead times for on-premise appliances stretch 12-18 weeks as Taiwanese semiconductor foundries prioritize AI accelerator wafer allocation over networking silicon. Component sourcing draws from United States threat-intelligence aggregators, Israeli domain-reputation specialists, and Indian software engineering centers for policy engine development. Single-source vulnerability concentrates in BIND and Unbound open-source resolver codebases that underpin 70% of deployed infrastructure. Distribution runs through Cisco and Palo Alto channel partners for enterprise accounts, direct API provisioning for cloud-native buyers, and MSSP intermediaries for mid-market coverage.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Enterprise procurement velocity is constrained by DNS-layer security engineering expertise that fewer than 15% of Fortune 500 security teams maintain in-house. Vendors capturing this capability scarcity through managed service packaging and certification-aligned delivery will compound share gains.
For Market Incumbents: Fortify resolver network density in United States and German markets through capacity additions that match Cloudflare's anycast footprint expansion. Invest in ENISA certification pathways ahead of NIS2 enforcement deadlines to lock out uncertified competitors from critical infrastructure procurement. Prioritize API-first policy engines that integrate with ServiceNow and Splunk SIEM workflows to defend against SASE-platform consolidation threats. For New Entrants and Emerging Players: Managed DNS firewall operations for United Kingdom mid-market financial services represents the most penetrable white-space segment, where incumbent pricing assumes enterprise-scale security operations capacity. Target Canadian healthcare clinics and Australian professional services firms with bundled per-user pricing that eliminates separate threat-intelligence procurement. Pursue channel partnerships with regional MSSPs rather than direct field sales to compress customer acquisition economics. For Investors and Strategic Acquirers: Threat-intelligence aggregators with proprietary domain-generation-algorithm detection models command acquisition premiums due to irreplaceable data moats. Long-term viability hinges on whether DNS security remains a standalone procurement category or dissolves into SASE-platform bundles. Monitor Cisco and Palo Alto quarterly earnings call language around DNS-layer attach rates as the inflection signal for consolidation timing.| Strategic Initiative | Industry Significance |
|---|---|
| Threat Intelligence Feed Integration | Proprietary domain-reputation data from Israeli and Singaporean sources differentiates blocking efficacy from commodity rule sets. |
| ENISA Certification Pathway | Formal compliance with EU cybersecurity certification enables procurement access to German energy and French transport operators. |
| API-First Resolver Deployment | RESTful policy automation aligns with United States technology sector infrastructure-as-code procurement standards. |
| Managed Security Service Bundling | 24/7 SOC coverage captures United Kingdom mid-market buyers lacking DNS-layer operational expertise. |
| Operational Technology Network Extension | Industrial control system segmentation opens manufacturing and utility sectors previously unreachable via IT-centric channels. |
Methodological Framework
Cross-validation between primary interviews with CISOs, DNS infrastructure architects, and MSSP operations directors anchors the qualitative findings against secondary validation from FCC regulatory filings, ENISA technical guidelines, and hyperscaler capex disclosures. Bottom-up triangulation aggregates deployment counts across United States federal contractors, German automotive networks, and Singaporean financial institutions. Top-down reconciliation applies NIST Cybersecurity Framework adoption curves to enterprise security spending benchmarks.
Sensitivity analysis around zero-trust mandate implementation pace and NIS2 enforcement strictness shapes the projection horizon. Segmentation dimensions modeled include deployment architecture, service type, end-user category, and integration complexity alongside regional regulatory cluster alignment. CAGRs derive from resolver query volume trajectories, threat-intelligence subscription renewal rates, and SASE-platform attach-rate assumptions across the analysis window.
Forecasts assume regulatory continuity in United States NIST SP 800-207 guidance and EU NIS2 transposition; material policy shifts would require re-modeling. Threat actor DNS tunneling innovation or encrypted DNS protocol dominance could accelerate or degrade detection efficacy assumptions. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
IoT Security Market
Cybersecurity
Deception Technology Market
Cybersecurity
Global File Integrity Monitoring Market
Cybersecurity
Data Exfiltration Techniques Market
Cybersecurity
Latin America IoT Security Market
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Global Cyber Threat Intelligence Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
China Cybersecurity Market
Cybersecurity
Cloud-Based Database Security Market
Cybersecurity
Global Deep Packet Inspection (DPI) Market
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Global Data Exfiltration Market
Cybersecurity
Netherlands Cybersecurity Market
Cybersecurity
Mexico Cybersecurity Market