
 Europe IoT Security Market | 2026-2036
Europe IoT Security Market Size, Share, and Industry Trends Forecast 2026-2036
Europe IoT Security Market Foresight
The gap between premium hardware-backed security and commodity software-only offerings is repositioning competitive dynamics across the European landscape. Thales Group leverages chip-level encryption to anchor its position in aerospace and defense IoT channels. Palo Alto Networks competes through cloud-native platform consolidation, while Infineon Technologies AG dominates embedded secure element manufacturing for automotive and industrial endpoints.
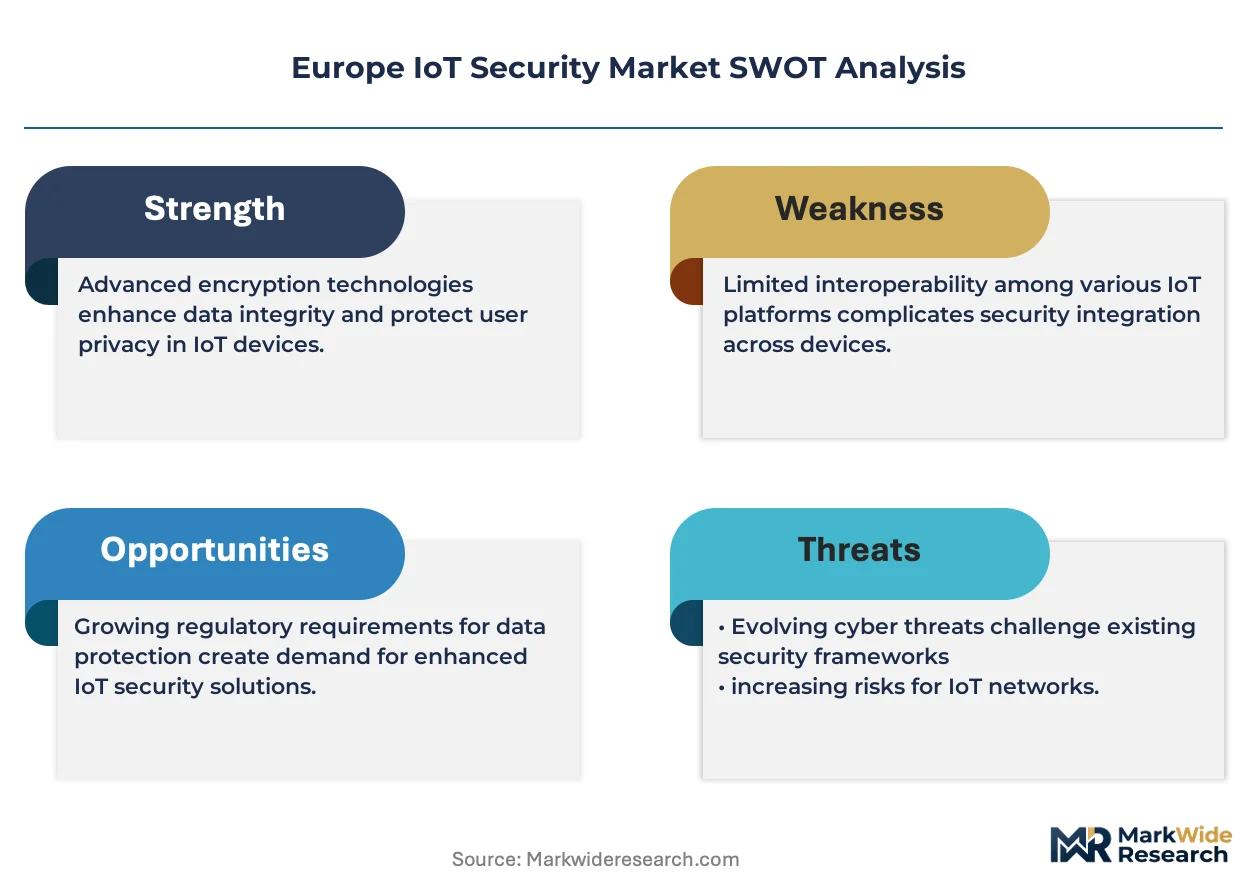
Europe IoT Security encompasses cryptographic protocols, device identity frameworks, and network segmentation mechanisms engineered to protect connected endpoints from unauthorized access, data exfiltration, and lateral movement attacks. The architecture typically integrates hardware roots of trust, certificate lifecycle management, and zero-trust network access operating at sub-100-millisecond latency thresholds for real-time industrial control systems. Identity Management and Intrusion Detection Systems command premium pricing due to regulatory mandates, while Edge deployment configurations represent the fastest-expanding segment as factories and energy grids localize threat response. Managed Services capture recurring revenue streams by embedding compliance monitoring directly into operational technology environments.
The EU Cybersecurity Act, GDPR, and the NIS2 Directive collectively mandate baseline encryption standards and incident reporting timelines that reshape product certification requirements across member states. ETSI standards and CE marking for connected devices further tighten market access for non-compliant vendors. Stakeholders must monitor the interplay between sovereign cloud requirements in Germany and France and the emerging EU Cyber Resilience Act's hardware certification scope.
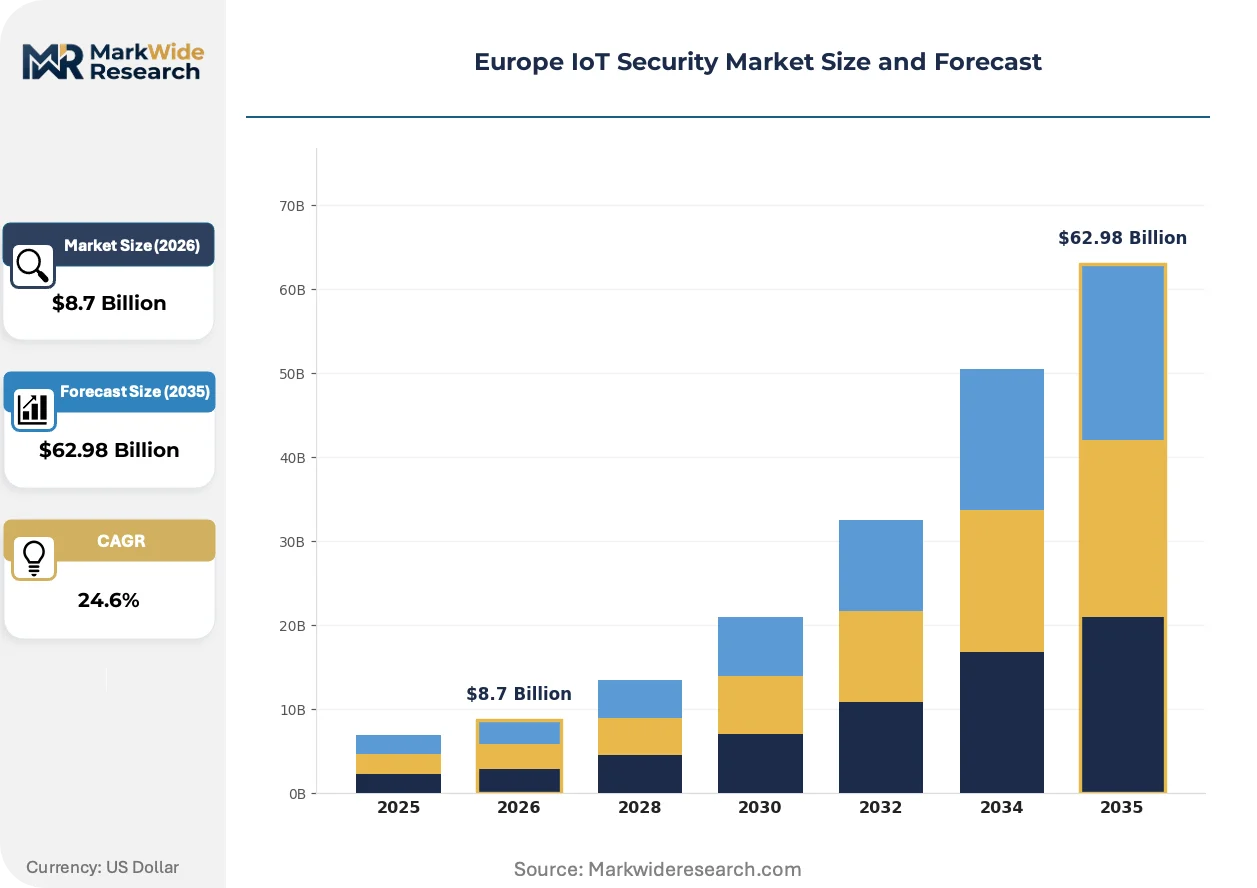
Market Dynamics
Hardware-backed trust anchors are displacing software-only security stacks across European industrial corridors, compressing procurement cycles and elevating certification requirements for vendors serving automotive and energy grid deployments.
Growth Catalysts
- EU Cyber Resilience Act:Mandatory hardware certification for connected devices creates a compliance-driven replacement cycle across industrial manufacturing corridors in Northern Italy and the Netherlands.
- Automotive OEM demand:Software-defined vehicle architectures require embedded secure elements for over-the-air update verification, pulling semiconductor security capabilities into tier-1 supplier specifications.
- Edge localization:Factory operators in Germany's Ruhr region are deploying localized threat response systems to meet GDPR data residency requirements while maintaining sub-100-millisecond industrial control latency.
Market Restraints
- Semiconductor supply concentration:Secure element manufacturing capacity concentrates among a limited set of European foundries, creating allocation risk for automotive and aerospace certification programs.
- Certification timeline friction:ETSI standards compliance and CE marking processes extend product launch cycles by 8-14 months for non-established vendors entering EU member state markets.
- Legacy system integration costs:Brownfield industrial sites face capital-intensive retrofit requirements to embed hardware roots of trust into pre-2015 operational technology infrastructure.
Strategic Opportunities
- French sovereign cloud mandates:Public sector procurement criteria under the Cloud de Confiance framework create captive demand for EU-hosted security operations centers serving critical infrastructure operators.
- Post-quantum cryptography convergence:NIST standardization of quantum-resistant algorithms intersects with ETSI roadmap requirements, enabling first-mover positioning for cryptographic hardware vendors.
- Energy grid modernization:Distribution system operators in Spain and Poland are unbundling security monitoring from equipment procurement, opening recurring revenue streams for managed detection and response providers.
Industry Challenges
- Embedded systems security engineering scarcity:The intersection of cryptography, hardware design, and industrial protocol knowledge concentrates among a limited talent pool in Munich, Eindhoven, and Grenoble technology clusters.
- Cross-border certification fragmentation:Divergent national implementation timelines for NIS2 Directive incident reporting requirements create operational complexity for vendors serving multiple EU member states simultaneously.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe IoT Security Market |
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $62.98 Billion |
| CAGR (2026 – 2036) | 24.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewalls, Antivirus, Identity Management, Intrusion Detection Systems End User: Manufacturing, Smart Home, Healthcare, Retail Deployment: On-premises, Cloud, Hybrid, Edge Service Type: Managed Services, Professional Services, Consulting, Training |
| Companies Covered | Symantec Corporation, Sophos Ltd., IBM Corporation, Intel Corporation, Hewlett Packard Enterprise Company, Fortinet Inc., Infineon Technologies AG, Palo Alto Networks Inc., Thales Group, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe IoT Security Market Shifts & Advancements
Convergence between operational technology and information security architectures is compressing vendor consolidation timelines while elevating platform-level purchasing criteria over point-product procurement across European industrial buyers.
Confidential computing hardware extensions are unifying memory encryption and remote attestation capabilities into single-socket solutions. Automotive tier-1 suppliers in Stuttgart and Wolfsburg are qualifying these architectures for autonomous driving platform security. The technology is unifying previously separate hardware security module and trusted execution environment procurement categories into consolidated silicon decisions.
GDPR Article 32 enforcement actions against industrial operators are mandating encryption-by-default for connected device data flows. Manufacturing facilities in Bavaria and Baden-Württemberg are retrofitting certificate lifecycle management systems to demonstrate technical and organizational measures compliance. Energy utilities face the most acute compliance pressure, with grid operators deploying automated key rotation to satisfy regulatory audit requirements.
Outcome-based security service contracts are displacing perpetual license models among mid-market manufacturing enterprises. System integrators in the Netherlands are bundling device identity provisioning with ongoing threat monitoring under fixed-fee arrangements. This shift is most visible among food processing and pharmaceutical packaging equipment buyers seeking to transfer operational risk to specialized managed security providers.
Europe IoT Security Market Segmentation
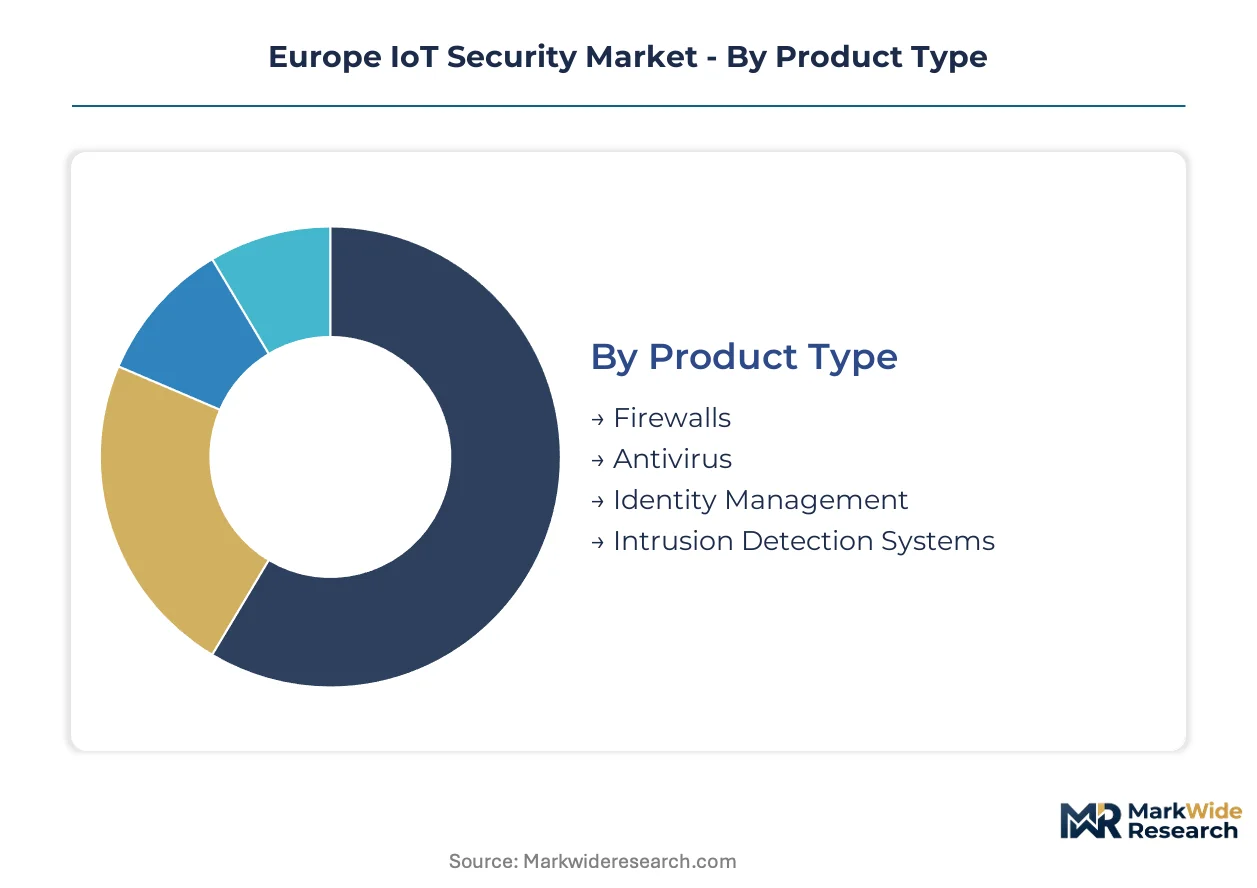
European IoT security procurement diverges sharply between regulated critical infrastructure operators seeking certified hardware stacks and mid-market enterprises prioritizing subscription flexibility. Segmentation patterns reveal how GDPR enforcement and NIS2 compliance timelines reshape purchasing criteria across member states.
Product Type:
Customization intensity spans from commodity software licensing to silicon-anchored trust architectures requiring ETSI certification.
- Identity Management:Certificate lifecycle management platforms with hardware-backed key storage dominate automotive and energy sector procurement. German distribution system operators mandate FIPS 140-2 Level 3 equivalent certification for grid-connected device onboarding. Premium pricing reflects embedded secure element integration and automated compliance audit trails.
- Intrusion Detection Systems:Network behavioral analytics engines operating at sub-100-millisecond latency for industrial control environments. Northern Italian manufacturing corridors concentrate demand as factory operators retrofit brownfield OT infrastructure to satisfy EU Cyber Resilience Act hardware certification timelines.
- Firewalls:Segment-specific protocol filtering for Modbus and OPC-UA traffic in operational technology deployments.
- Antivirus:Lightweight endpoint agents optimized for resource-constrained embedded systems in smart home gateways.
Most installed capacity flows through Identity Management. Expansion is steepest in Intrusion Detection Systems.
End User:
Application risk profiles separate capital-intensive industrial certification programs from consumer-scale deployment velocity.
- Manufacturing:Operational technology security spanning programmable logic controllers, human-machine interfaces, and robotic workcells. Bavarian automotive suppliers and Dutch food processing operators drive hardware root-of-trust adoption to satisfy GDPR Article 32 technical measures requirements. Brownfield retrofit costs concentrate procurement decisions among enterprises with pre-2015 installed base.
- Smart Home:Consumer gateway and device security with escalating French and German regulatory pressure on default credential policies. CE marking requirements for connected devices under the Radio Equipment Directive reshape vendor market access timelines. Mass-market price compression favors software-only solutions despite inferior breach resistance.
- Healthcare:Medical device cybersecurity for connected diagnostic and patient monitoring equipment under MDR and GDPR joint compliance.
- Retail:Point-of-sale terminal protection and supply chain IoT tracking across warehouse automation networks.
Manufacturing commands the highest average contract value. Smart Home delivers the steepest volume expansion trajectory.
Deployment:
Infrastructure location decisions trade latency sensitivity against data residency compliance across member state regulatory environments.
- Edge:Localized threat response architectures processing telemetry within factory premises or substation perimeters. Ruhr region industrial clusters and Eindhoven manufacturing hubs prioritize GDPR-compliant data localization while maintaining deterministic control loop performance. Hardware cost premiums compress against cloud egress fee avoidance.
- Cloud:Centralized security operations center platforms with French sovereign cloud mandates under Cloud de Confiance frameworks creating captive demand for EU-hosted infrastructure.
- On-premises:Air-gapped or private data center deployments for defense and classified infrastructure operators.
- Hybrid:Orchestrated policy enforcement spanning edge, on-premises, and cloud control planes with unified identity fabric.
Edge deployment carries the highest growth slope. Cloud retains the largest installed base among mid-market enterprises.
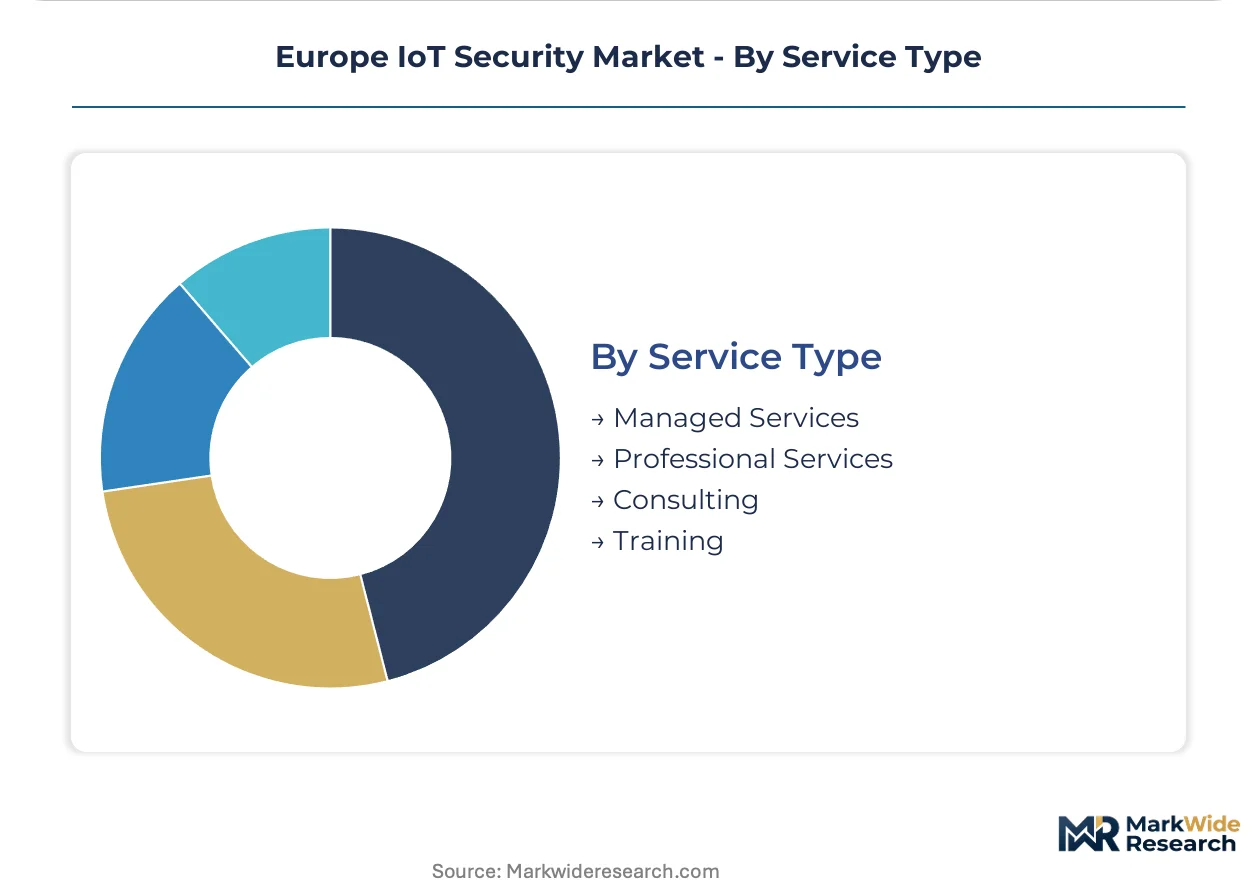
Service Type:
Commercial model preferences separate perpetual license buyers from risk-transfer seeking subscription adopters.
- Managed Services:Recurring security operations center engagement embedding compliance monitoring directly into operational technology environments. Dutch system integrators bundle device identity provisioning with threat detection under fixed-fee arrangements. Outcome-based contracts displace time-and-materials pricing among pharmaceutical packaging and food processing equipment buyers.
- Professional Services:Implementation, integration, and certification support for ETSI standards compliance and CE marking preparation.
- Consulting:NIS2 Directive readiness assessments and GDPR technical measures gap analysis for multi-jurisdictional operators.
- Training:Embedded systems security engineering skill development addressing talent scarcity in Munich, Eindhoven, and Grenoble clusters.
Managed Services capture the fastest-expanding revenue pool. Professional Services dominate initial deployment phases.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Cryptography and embedded systems engineering talent clusters in Munich, Eindhoven, and Grenoble anchor European IoT security development. These technical concentrations feed directly into industrial manufacturing corridors and automotive engineering centers across the continent.
Germany
Automotive OEM demand for software-defined vehicle architectures pulls semiconductor security capabilities into tier-1 supplier specifications. The EU Cyber Resilience Act and GDPR Article 32 enforcement reshape procurement criteria for Bavarian automotive suppliers and Ruhr region factory operators. Munich-based engineering clusters drive hardware root-of-trust adoption for brownfield industrial retrofit programs.
France
Cloud de Confiance sovereign cloud mandates create captive demand for EU-hosted security operations centers serving critical infrastructure operators. ANSM and CNIL regulatory guidance tightens medical device cybersecurity requirements for connected diagnostic equipment. Grenoble technology clusters concentrate embedded secure element design expertise feeding aerospace and defense channels.
Netherlands
Food processing and pharmaceutical packaging equipment buyers seek risk transfer to specialized managed security providers under outcome-based contracts. Eindhoven manufacturing hubs prioritize GDPR-compliant data localization while maintaining deterministic control loop performance. Dutch system integrators bundle device identity provisioning with threat detection under fixed-fee arrangements.
Italy
Northern Italian manufacturing corridors concentrate demand for intrusion detection systems as factory operators retrofit brownfield OT infrastructure. CE marking requirements under the Radio Equipment Directive reshape vendor market access timelines for connected industrial equipment. Milan-Turin industrial clusters drive hardware certification programs to satisfy EU Cyber Resilience Act timelines.
United Kingdom
Post-Brexit regulatory divergence creates parallel certification tracks for vendors serving UK and EU markets simultaneously. London financial services demand for operational resilience drives IoT security spending in critical infrastructure adjacent sectors. Cambridge-Oxford technology corridors concentrate quantum-resistant cryptography research intersecting with NIST standardization timelines.
Europe IoT Security Market Competitive Landscape
Capital-heavy producers compete with asset-light designers across the European IoT security landscape. Hardware-backed trust anchor vendors with captive foundry relationships face pressure from cloud-native platform consolidators with minimal fixed asset exposure. Three archetypes dominate: silicon-anchored security element manufacturers, cloud-native platform consolidators, and managed security service operators. M&A activity concentrates among mid-cap specialists seeking ETSI certification capabilities, while strategic partnerships between automotive tier-1 suppliers and semiconductor vendors accelerate.
Within the hardware-anchored tier, Infineon Technologies AG and Thales Group exemplify European-headquartered producers with deep embedded security heritage. Palo Alto Networks Inc. occupies a position representing cloud-native platform consolidation strategies competing for factory and energy grid deployments. These three anchors illustrate the competitive tension between silicon-level trust architectures and software-defined security delivery models reshaping procurement decisions across German automotive corridors and Dutch industrial clusters.
| Leading Market Players |
|---|
| Symantec Corporation |
| Sophos Ltd. |
| IBM Corporation |
| Intel Corporation |
| Hewlett Packard Enterprise Company |
| Fortinet Inc. |
| Infineon Technologies AG |
| Palo Alto Networks Inc. |
| Thales Group |
| Others |
Supply & Pricing Matrix
Hardware certification tiers under the EU Cyber Resilience Act bifurcate vendor economics between ETSI-qualified silicon suppliers and software-only commodity providers, compressing margins in the latter while anchoring premium pricing to foundry capacity allocation in Germany and France.
Pricing Analysis
Bundled managed security services with embedded compliance monitoring command recurring revenue premiums from Dutch food processing operators, while unbundled perpetual licenses face price erosion among mid-market smart home gateway manufacturers. Three-tier pricing structure across FIPS 140-2 Level 3 certified hardware, CE-marked standard modules, and uncertified economy software separates automotive tier-1 procurement from consumer electronics. Pricing pressure stems from semiconductor foundry allocation constraints for secure element manufacturing. Smart home OEMs exhibit acute price sensitivity; aerospace and defense channels show inelastic demand for hardware-backed trust anchors.
Supply Chain Analysis
French and German domestic-content mandates under Cloud de Confiance and sovereign cloud frameworks reshape sourcing toward EU-hosted security operations centers and local foundry partnerships. Secure element manufacturing concentrates in Germany, the Netherlands, and France, drawing from silicon wafer feedstock anchored in East Asian fabrication networks. Supply chain risk centers on single-source vulnerability for automotive-grade embedded security modules. Distribution runs through specialized system integrators in Eindhoven and Munich clusters serving brownfield industrial retrofit programs.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
European IoT security has entered a late-cycle quality phase where GDPR Article 32 enforcement and NIS2 compliance timelines concentrate procurement among certified hardware vendors, displacing commodity software alternatives.
For Market Incumbents: To counter cloud-native platform consolidation from Palo Alto Networks and asset-light competitors, Thales Group and Infineon Technologies AG must deepen captive foundry relationships for secure element allocation priority. Certification investment in post-quantum cryptographic hardware represents the critical defensive lever against NIST-standardized algorithm disruption.
For New Entrants and Emerging Players: The mid-market manufacturing gap between premium FIPS-certified stacks and economy software-only offerings offers white-space entry for hybrid edge-cloud solutions targeting Northern Italian brownfield retrofits. Dutch pharmaceutical packaging equipment buyers present the most penetrable segment for outcome-based managed service contracts with fixed-fee risk transfer.
For Investors and Strategic Acquirers: Consolidation pressure builds where ETSI certification capabilities concentrate among mid-cap specialists lacking automotive OEM channel access. The five-to-ten-year viability window favors acquisition targets with embedded secure element design expertise feeding Munich and Grenoble engineering clusters. The signal to watch is unbundling of security monitoring from equipment procurement among Spanish and Polish distribution system operators.
| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptography Certification | NIST-standardized algorithm integration enables first-mover positioning against ETSI roadmap requirements. |
| Managed Security Service Bundling | Dutch system integrators embed device identity provisioning with fixed-fee threat detection for food processing operators. |
| Sovereign Cloud Infrastructure Expansion | French Cloud de Confiance mandates create captive demand for EU-hosted security operations centers. |
| Automotive Tier-1 Supplier Partnership | Software-defined vehicle architectures pull semiconductor security capabilities into Stuttgart and Wolfsburg procurement specifications. |
| Brownfield OT Retrofit Specialization | Ruhr region factories deploy localized threat response to satisfy GDPR data residency with sub-100-millisecond latency. |
Research Methodology
Direct dialogue with IoT security engineering directors, automotive procurement leads at tier-1 suppliers, Dutch system integrators, and ETSI certification officers grounded qualitative findings in operational technology deployment realities. Secondary validation drew from EU Cyber Resilience Act draft texts, GDPR enforcement action databases, NIST post-quantum cryptography standardization documents, and automotive OEM supplier qualification records. Bottom-up demand modeling across edge, cloud, and on-premises deployment configurations triangulated against top-down semiconductor secure element production capacity estimates.
Bottom-up segment analysis modeled identity management, intrusion detection, and firewall product categories across manufacturing, smart home, healthcare, and retail end-use verticals. The analytical framework projected hardware-backed versus software-only solution mix, deployment latency requirements, and managed service attachment rates across the analysis window. CAGR derivation incorporated EU Cyber Resilience Act compliance timeline phasing, NIS2 Directive national implementation schedules, and automotive software-defined vehicle platform rollout sequencing.
Caveats apply where NIS2 Directive national implementation divergence, post-quantum cryptography standardization delays, or automotive semiconductor allocation shocks could materially shift the outlook. Forecasts reflect assumptions on regulatory enforcement intensity and brownfield retrofit capital availability. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
DNS Security Market
Cybersecurity
United States Virtualization Security Market
Cybersecurity
Hungary Cybersecurity Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Philippines Cybersecurity Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Spear Phishing Solution Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
North America Software Defined Perimeter Market
Cybersecurity
Switzerland Cybersecurity Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Botnet Detection Market
Cybersecurity
Global Container and Kubernetes Security Market
Cybersecurity
Data Protection Market
Cybersecurity
Global API Security Market