
 Data Security Market | 2026-2036
Data Security Market Size, Share, and Industry Trends Forecast 2026-2036
Data Security Market Analysis
Quantum-resistant cryptography is broadening the addressable market for encryption vendors as post-quantum algorithm standards from NIST render legacy RSA and elliptic curve protocols obsolete. IBM leverages its lattice-based cryptography research to anchor enterprise migration roadmaps. Palo Alto Networks competes through integrated zero-trust architectures that bundle data loss prevention with network segmentation. Thales Group specializes in hardware security modules that sustain high-assurance key management for financial and government clients.
Data security encompasses technologies, processes, and controls that protect digital information from unauthorized access, corruption, or exfiltration through encryption algorithms, identity verification protocols, and continuous monitoring systems. Its primary commercial purpose is ensuring confidentiality, integrity, and availability of structured and unstructured data across on-premises, cloud, and edge environments. Encryption products command the deepest margin pools due to regulatory mandates for data-at-rest and data-in-transit protection, while cloud-based deployment models are expanding fastest as multi-tenant architectures drive consumption-based pricing. AI-based security technology is gaining share through behavioral analytics that detect anomalous data access patterns in real time.
The US Federal Trade Commission enforces data breach notification requirements and consumer privacy standards that shape enterprise security spending priorities. The European Medicines Agency and EU AI Act impose algorithmic transparency and training data governance rules on life sciences and AI application vendors. The Securities and Exchange Commission's cybersecurity disclosure rules mandate incident reporting timelines that compress procurement cycles for incident response capabilities. Stakeholders must monitor the divergence between US sectoral approaches and EU comprehensive frameworks when architecting cross-border data protection strategies.
Market Dynamics
Post-quantum cryptography migration is compressing procurement timelines as enterprises face cryptographic obsolescence risk from NIST's algorithm standardization timeline, forcing security architecture overhauls before quantum computing renders current encryption vulnerable.
Growth Catalysts
- EU AI Act enforcement:Algorithmic transparency mandates for high-risk AI systems are compelling enterprises to deploy data lineage and governance tooling that embeds security-by-design principles.
- Healthcare digitization:Electronic health record expansion and telemedicine platforms are accelerating encryption and access control procurement to satisfy HIPAA breach notification thresholds.
- Manufacturing IoT proliferation:Industrial data protection requirements for connected production networks in Germany are tightening, driving hardware security module adoption for operational technology environments.
Market Restraints
- Specialized talent scarcity:Shortages of cryptographers and zero-trust architects are elongating deployment timelines and inflating professional services costs for complex implementations.
- Supply concentration in HSM manufacturing:Dependence on limited semiconductor foundry capacity for tamper-resistant hardware creates procurement bottlenecks for financial and government clients.
- Legacy infrastructure drag:Decades-old mainframe and on-premise data warehouse architectures resist API-native security integration without expensive middleware layers.
Strategic Opportunities
- SEC cybersecurity disclosure rules:Compressed incident reporting timelines for publicly traded companies are expanding managed detection and response service contracts.
- Edge computing security:Distributed IoT and 5G deployments are creating demand for lightweight encryption agents that operate under constrained compute and power budgets.
- France and Netherlands:CNIL guidance on data retention minimization and cross-border transfer mechanisms is opening consulting and technical implementation revenue pools.
Industry Challenges
- FIPS 140-3 certification complexity:Extended validation timelines for cryptographic modules are delaying product launches and freezing R&D roadmaps.
- Multi-cloud key management fragmentation:Inconsistent native encryption APIs across AWS, Azure, and Google Cloud are forcing customers to maintain parallel key governance frameworks.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Data Security Market |
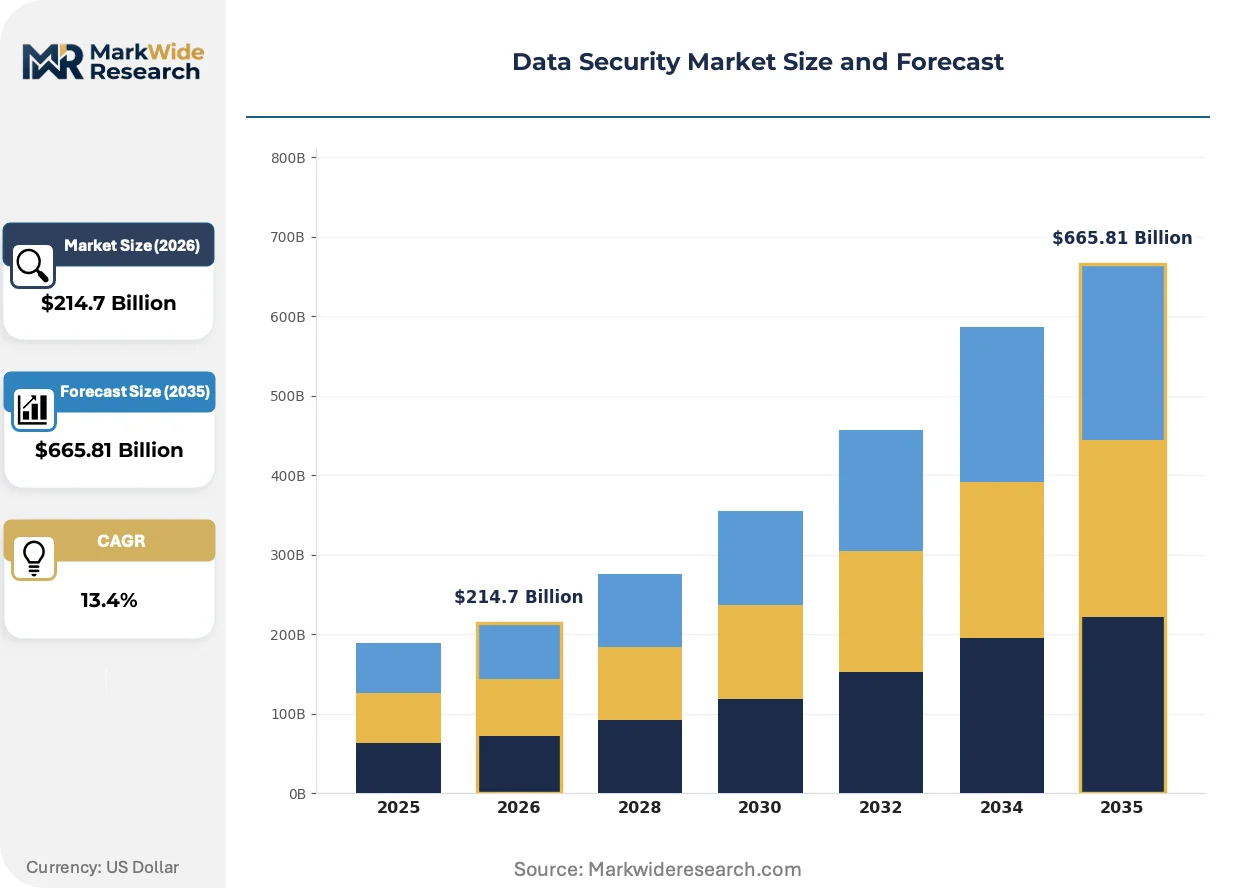
| Market Size in 2026 | $214.7 Billion |
| Market Size in 2035 | $665.81 Billion |
| CAGR (2026 – 2036) | 13.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Encryption, Authentication, Access Control, Data Loss Prevention Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed End User: Healthcare Providers, Financial Institutions, Government Agencies, Educational Institutions Technology: Blockchain, AI-Based Security, Endpoint Protection, Network Security |
| Companies Covered | IBM, Microsoft, Cisco Systems, Palo Alto Networks, Forcepoint, Imperva, Varonis Systems, McAfee, Thales Group, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Data Security Market Emerging Trajectories
Security architecture convergence is collapsing point-product silos as buyers demand integrated platforms that reduce operational overhead and eliminate coverage gaps between adjacent control categories.
Confidential computing is unifying hardware-based memory encryption with cloud-native workload isolation. Financial services firms and healthcare providers are deploying Intel SGX and AMD SEV enclaves for sensitive data processing. This technology is unifying previously separate infrastructure security and application security procurement decisions into single platform evaluations.
GDPR's Article 35 data protection impact assessment requirements are mandating systematic risk documentation before AI system deployment. Life sciences companies must now map training data provenance and model decision logic prior to regulatory submission. Pharmaceutical manufacturers in Germany and France are restructuring data governance committees to satisfy EMA parallel inspection protocols.
Subscription-based consumption is displacing perpetual licensing for encryption and key management platforms. Mid-market enterprises prefer OpEx-aligned contracts that bundle software, hardware, and managed services. This pattern is most pronounced in UK and Nordic markets where CFOs prioritize balance sheet flexibility over capital ownership.
Data Security Market Segmentation
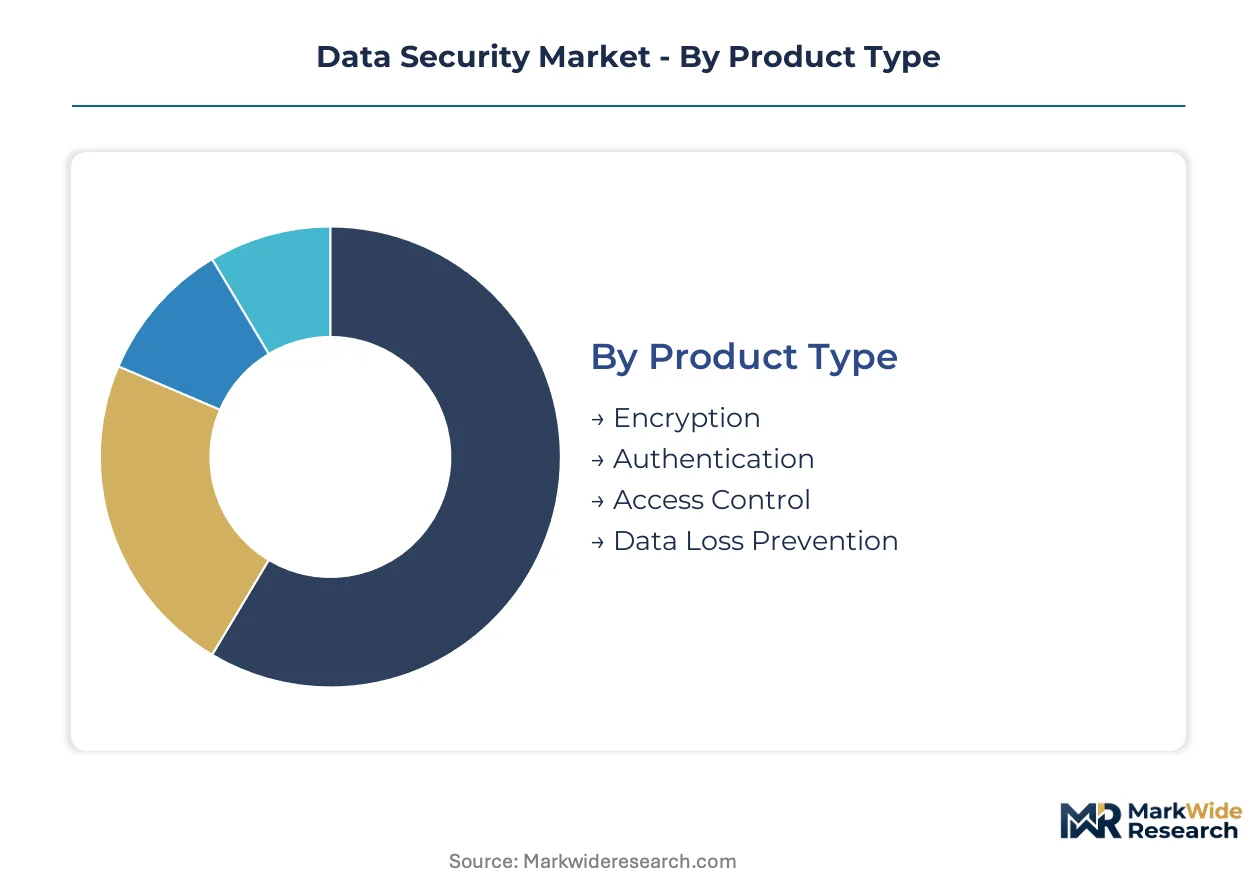
Data security procurement patterns diverge sharply across technology stacks and operational contexts. Encryption specifications, deployment architectures, and sector-specific compliance obligations create distinct purchasing workflows that vendors must navigate.
Product Type:
Technical specifications define competitive positioning across the protection stack, with algorithm standards and certification levels determining enterprise eligibility.
- Encryption:Lattice-based and elliptic curve implementations dominate enterprise roadmaps as NIST post-quantum standards displace legacy RSA. Healthcare providers in Germany and France are accelerating procurement to satisfy EMA data integrity requirements for clinical trial submissions.
- Authentication:Multi-factor and biometric verification systems integrate with identity governance platforms to enforce zero-trust access policies. Financial institutions across the US and EU mandate hardware-backed FIDO2 keys for privileged administrator accounts under SEC and ECB guidance.
- Access Control:Attribute-based policies enforce least-privilege data access across hybrid cloud environments.
- Data Loss Prevention:Content inspection engines monitor structured and unstructured data flows for regulatory pattern matching.
Mature deployment sits with Encryption. Newer deployment is concentrated in Authentication.
Deployment Model:
Cost structures and operational control requirements shape infrastructure decisions, with OpEx alignment driving mid-market preferences.
- Cloud-Based:Consumption-priced key management and encryption services eliminate capital expenditure for scaling enterprises. Nordic and UK CFOs prioritize subscription contracts that bundle software, hardware, and managed services for balance sheet flexibility.
- Hybrid:Split architectures maintain sensitive data on-premises while leveraging cloud analytics for non-critical workloads. German manufacturing IoT networks deploy hardware security modules locally while routing telemetry to cloud dashboards under tightened industrial data protection rules.
- On-Premises:Air-gapped installations serve classified government and defense environments with strict data sovereignty mandates.
- Managed:Outsourced security operations centers compress incident response timelines for resource-constrained organizations.
Established procurement favors On-Premises. Fastest expansion is occurring in Cloud-Based.
End User:
Sector-specific regulatory frameworks create divergent technology requirements and purchasing authority structures.
- Healthcare Providers:HIPAA breach notification thresholds and EMA inspection protocols mandate encryption for electronic health records and telemedicine platforms. US hospital systems and EU pharmaceutical manufacturers are restructuring data governance committees to satisfy parallel regulatory demands.
- Financial Institutions:SEC cybersecurity disclosure rules and ECB operational resilience mandates compress procurement cycles for incident response and cryptographic key rotation capabilities.
- Government Agencies:FIPS 140-3 certification requirements and classified handling procedures restrict vendor eligibility to pre-approved cryptographic modules.
- Educational Institutions:Limited IT budgets and distributed campus networks drive demand for consolidated security platforms with simplified management interfaces.
Deep compliance investment characterizes Healthcare Providers. Emerging procurement volume is shifting toward Educational Institutions.
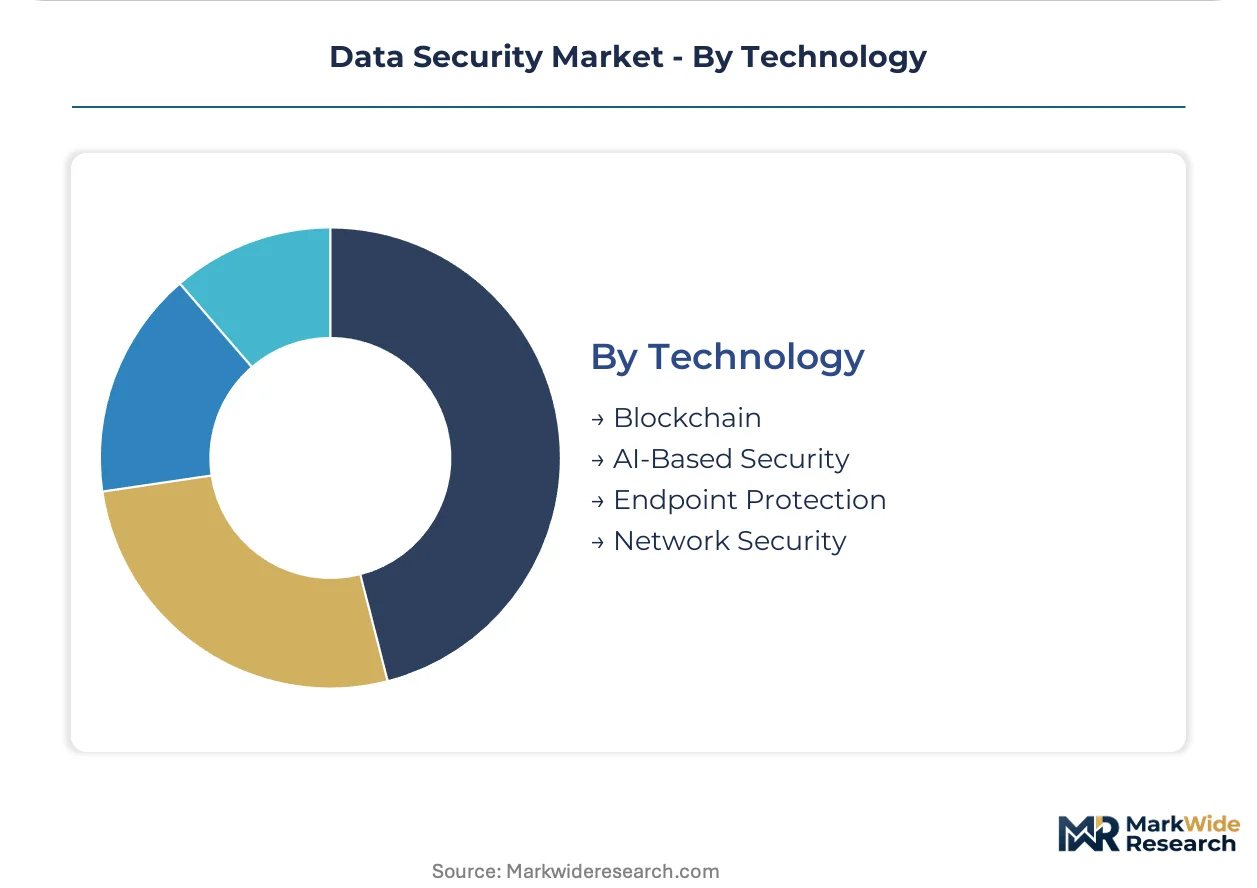
Technology:
Innovation trajectories and integration complexity determine adoption velocity across emerging protection mechanisms.
- AI-Based Security:Behavioral analytics engines detect anomalous data access patterns in real time, unifying previously separate infrastructure and application security decisions. Life sciences companies deploy these systems to map training data provenance and model decision logic prior to EU AI Act submission.
- Endpoint Protection:Lightweight encryption agents operate under constrained compute and power budgets for distributed IoT and 5G deployments at the network edge.
- Blockchain:Immutable audit trails support supply chain provenance and cross-border data integrity verification for high-assurance environments.
- Network Security:Segmentation and micro-segmentation policies isolate sensitive data flows within zero-trust architectures.
Production deployment centers on Network Security. Steepest expansion trajectory belongs to AI-Based Security.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Healthcare providers in Germany and manufacturing IoT networks across industrial clusters are compressing procurement timelines for encryption and hardware security modules. EU AI Act enforcement and GDPR compliance deadlines are compelling enterprises in France and the Netherlands to overhaul data governance frameworks. Financial institutions in the United States face SEC cybersecurity disclosure mandates that accelerate incident response contracting.
United States
SEC cybersecurity disclosure rules mandate compressed incident reporting timelines for publicly traded companies. The FTC enforces data breach notification requirements that shape enterprise security spending priorities. Hospital systems in Texas and California are restructuring data governance committees to satisfy HIPAA breach notification thresholds for electronic health records.
Germany
Industrial data protection requirements for manufacturing IoT networks are tightening rapidly across automotive and machinery sectors. KBA and BSI guidance on operational technology security drives hardware security module adoption for connected production environments. Bavarian industrial clusters around Munich and Stuttgart anchor procurement concentration for high-assurance encryption.
France
CNIL guidance on data retention minimization and cross-border transfer mechanisms opens consulting revenue pools for compliance implementation. EMA inspection protocols mandate systematic risk documentation for pharmaceutical training data provenance. Paris and Lyon pharmaceutical manufacturers are restructuring governance committees to satisfy parallel regulatory demands.
United Kingdom
NHS digitization programs accelerate encryption procurement for electronic health record platforms and telemedicine infrastructure. Mid-market CFOs prioritize subscription contracts that bundle software, hardware, and managed services for balance sheet flexibility. London financial services firms anchor demand for zero-trust architectures under FCA operational resilience mandates.
Netherlands
CNIL-aligned data protection impact assessment requirements mandate systematic risk documentation before AI system deployment. Amsterdam and Rotterdam data center clusters drive demand for cloud-based key management with consumption-based pricing. Financial institutions prioritize OpEx-aligned contracts that eliminate capital expenditure for scaling encryption services.
Data Security Market Vendor Landscape
Branded specialists and contract manufacturers split share differently across segments, with integrated platform vendors capturing premium pricing while point-product vendors face consolidation pressure. The vendor base organizes around three strategic archetypes: lattice-based cryptography researchers anchoring post-quantum migration roadmaps, zero-trust architecture bundlers collapsing network and data security silos, and hardware security module specialists serving high-assurance government and financial clients. Dominant competitive moves include strategic partnerships for multi-cloud key management integration and technology licensing for FIPS 140-3 certification acceleration.
Within the integrated platform tier, IBM and Microsoft exemplify vendors anchoring enterprise migration roadmaps through research-backed cryptographic standards. Palo Alto Networks occupies a position among architecture bundlers that collapse previously separate infrastructure and application security procurement decisions. Thales Group represents the hardware security module specialist archetype, serving financial and government clients with tamper-resistant key management requirements.
| Leading Market Players |
|---|
| IBM |
| Microsoft |
| Cisco Systems |
| Palo Alto Networks |
| Forcepoint |
| Imperva |
| Varonis Systems |
| McAfee |
| Thales Group |
| Others |
Supply Flow & Price Mechanics
Cryptographer concentration in Israel, Germany, and the United States creates labor-cost differentials that widen pricing-tier spreads between boutique quantum-cryptography consultancies and volume-oriented encryption vendors.
Pricing Analysis
Volume-heavy cloud encryption services compete on per-seat subscription rates while specialized hardware security modules command premium margins. Pricing stratifies across FIPS 140-3 certified modules, enterprise-grade key management platforms, and commodity SaaS encryption tiers. Cost compression in cloud-based tiers is intensifying because hyperscalers bundle encryption into base infrastructure pricing. Mid-market healthcare providers exhibit highest price sensitivity, while defense contractors and central banks demonstrate minimal elasticity for tamper-resistant hardware.
Supply Chain Analysis
Semiconductor foundry workforce constraints in Taiwan, South Korea, and the United States limit tamper-resistant chip output for hardware security modules. Supply chains draw from silicon wafer suppliers, cryptographic co-processor IP licensors, and certified packaging facilities. Single-source vulnerability concentrates in advanced node fabrication for high-assurance government-grade components. Distribution runs through authorized security resellers and direct federal procurement channels with extended validation timelines.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
FIPS 140-3 certification backlog creates a supply-constrained environment that props pricing for validated cryptographic modules and compresses delivery timelines for enterprise buyers.
For Market Incumbents: Anticipate post-quantum migration demand surges by pre-positioning lattice-based cryptography roadmaps and securing NIST algorithm validation slots ahead of competitor filings. Consolidation pressure from integrated zero-trust platforms threatens point-product encryption vendors; vertical integration into managed detection and response services provides defensive moat expansion.
For New Entrants and Emerging Players: Launch via channel partnerships with NHS trusts and German hospital systems where procurement cycles for clinical data protection are accelerating. Edge computing security for manufacturing IoT networks represents the most penetrable white space, with lightweight encryption agents addressing constrained compute environments underserved by incumbent hardware modules.
For Investors and Strategic Acquirers: The window for entry favors hardware security module specialists with existing FIPS 140-3 certifications and established government procurement relationships. Long-term viability hinges on post-quantum algorithm agility and multi-cloud key management integration capabilities. Watch NIST standardization timeline acceleration as the critical inflection signal for cryptographic obsolescence risk repricing.
| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptography Migration | NIST algorithm validation secures enterprise roadmap anchoring against RSA obsolescence. |
| Confidential Computing Platform Integration | Intel SGX and AMD SEV enclaves unify infrastructure and application security procurement decisions. |
| Multi-Cloud Key Management Partnership | AWS, Azure, and Google Cloud API harmonization reduces customer governance framework fragmentation. |
| Hardware Security Module Certification Acceleration | FIPS 140-3 validation compression unlocks federal and financial services market eligibility. |
| Managed Detection and Response Service Expansion | SEC disclosure rule compliance compresses incident response contracting timelines for public companies. |
Methodological Framework
SEC 10-K cybersecurity disclosures, EMA inspection protocol documentation, and NIST post-quantum cryptography standardization records formed the secondary backbone for this analysis. Primary interviews with CISOs at Fortune 500 healthcare systems, cryptographic architects at financial institutions, federal procurement officers, and hardware security module manufacturing executives combined with secondary validation through trade association filings and regulatory guidance documents. Bottom-up vendor revenue aggregation and top-down enterprise IT spending allocation were triangulated against documented contract values.
Bottom-up modeling tracked encryption, authentication, and access control procurement across deployment models and end-user sectors. Segmentation dimensions included product type, deployment architecture, organization size tier, vertical regulatory cluster, and geographic adoption pattern. CAGRs were derived from weighted average growth rates across these segments, with inputs from documented EMA compliance deadlines, SEC enforcement timelines, and German industrial data protection rule implementations.
Regulatory enforcement delays, quantum computing capability acceleration, and semiconductor foundry capacity constraints are the dominant revision risks to these projections. Forecasts reflect assumptions regarding NIST standardization adherence and EU AI Act implementation timelines. Material deviation in named triggers warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
UK Cybersecurity Market
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
Cloud Firewalls Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Endpoint Security Market
Cybersecurity
China Cybersecurity Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Container-based Firewall Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Cyber Warfare Market
Cybersecurity
Cloud Authentication Market
Cybersecurity
Data Center Logical Security Market
Cybersecurity
Europe Data Protection-As-A-Service Market
Cybersecurity
IT and Telecom Cyber Security Market
Cybersecurity
Global Deep Packet Inspection (DPI) Market