
 Cyber Security As a Service Market | 2026-2036
Cyber Security As a Service Market Size, Share, and Industry Trends Forecast 2026-2036
Cyber Security As a Service Market Analysis
Zero-trust architecture is rewriting enterprise security delivery models by decoupling perimeter defenses from identity verification layers. Microsoft leverages its cloud-native Sentinel platform to anchor extended detection and response workflows across hybrid environments. Palo Alto Networks competes through Prisma Cloud's container security specialization, while CrowdStrike Holdings dominates endpoint protection with its threat graph intelligence engine.
Cyber Security As a Service encompasses externally managed threat monitoring, incident response orchestration, and continuous vulnerability management delivered through subscription-based operational models. Providers deploy automated SOAR playbooks with sub-15-minute mean-time-to-detect thresholds to contain lateral movement before data exfiltration occurs. Managed Security Services occupies the largest revenue pool as enterprises outsource 24/7 SOC operations, while Cloud-Based deployment is expanding fastest as organizations retire legacy on-premises security stacks. The Government Sector end-user category demands FedRAMP-authorized offerings with sovereign data residency controls.
FCC cybersecurity labeling rules for IoT devices and SEC disclosure mandates for material cyber incidents are reshaping procurement specifications across regulated industries. NIST SP 800-53 revision requirements and ISO 27001 certification standards further constrain vendor eligibility for federal and enterprise contracts. Stakeholders must evaluate provider resilience against evolving quantum-computing threats and sovereign cloud fragmentation before committing to long-term managed security partnerships.
Market Dynamics
Zero-trust architecture is fragmenting traditional perimeter-based security procurement, forcing enterprises to unbundle identity verification from network controls and source each layer from specialized managed service providers.
Growth Catalysts
- EU AI Act compliance mandates:Organizations deploying high-risk AI systems must implement continuous security monitoring, creating mandatory demand for outsourced SOC operations with audit-ready documentation trails.
- Financial services operational resilience requirements:Basel Committee guidelines and DORA obligations are compelling banks to externalize 24/7 threat detection rather than build captive capabilities.
- Quantum-resistant cryptography migration:NIST post-quantum standards are accelerating hardware security module refresh cycles, with managed services providers capturing deployment complexity.
Market Restraints
- Skilled analyst scarcity:The global shortfall of certified SOC analysts exceeds available training pipeline capacity, inflating personnel costs for managed detection and response contracts.
- Cloud sovereignty fragmentation:Divergent data localization requirements across Germany, Japan, and the United States prevent providers from achieving true economies of scale in multi-tenant security platforms.
- Legacy SIEM sunk costs:Enterprises with substantial on-premises Splunk or IBM QRadar deployments face high switching friction despite superior cloud-native alternatives.
Strategic Opportunities
- Operational technology convergence:Industrial control system security for manufacturing and energy infrastructure remains underserved, with managed services penetrating less than 15 percent of addressable accounts.
- SEC cyber disclosure mandates:Material incident reporting requirements are creating retainer-based incident response services as a distinct revenue stream separate from ongoing monitoring.
- Identity fabric integration:Convergence of zero-trust network access with privileged access management enables unified per-user security subscriptions across hybrid workforces.
Industry Challenges
- FedRAMP authorization timelines:Government contractors face 12-18 month certification delays that constrain speed-to-market for sovereign cloud security offerings.
- Multi-cloud orchestration complexity:Security teams struggle to normalize threat telemetry across AWS, Azure, and Google Cloud native tooling without creating visibility gaps.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cyber Security As a Service Market |
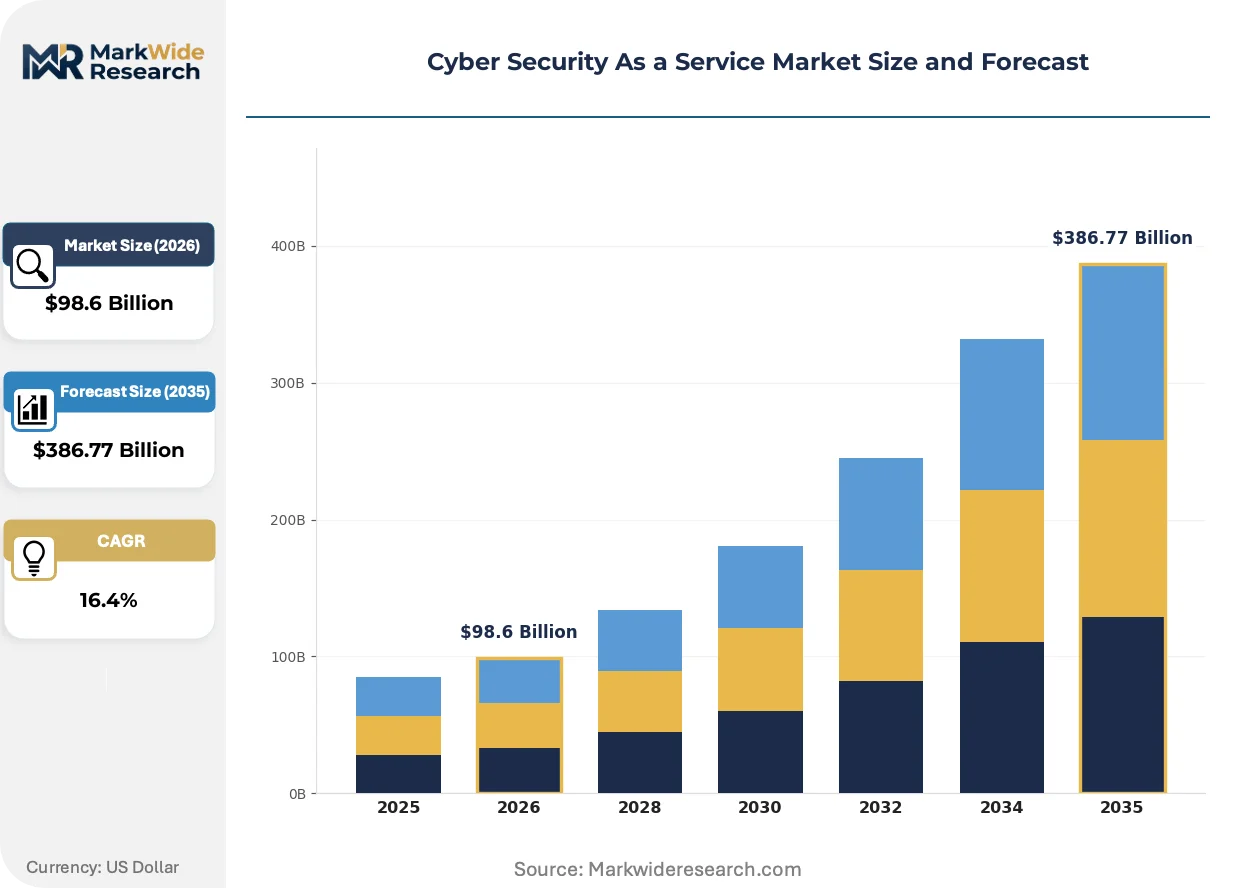
| Market Size in 2026 | $98.6 Billion |
| Market Size in 2035 | $386.77 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Security Services, Incident Response, Security Information and Event Management, Vulnerability Assessment Deployment Model: Cloud-Based, On-Premises, Hybrid, Multi-Tenant End User: Enterprise, SMBs, Government Sector, Educational Institutions Industry Vertical: Healthcare, Financial Services, Information Technology, Retail |
| Companies Covered | Microsoft, Cisco Systems, Palo Alto Networks, IBM Corporation, Fortinet, CrowdStrike Holdings, Check Point Software Technologies, Trend Micro, AWS, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cyber Security As a Service Market Emerging Trajectories
Attack surface management is converging with continuous compliance validation, collapsing the traditional separation between vulnerability discovery and regulatory evidence collection into unified SaaS delivery models.
Extended detection and response platforms are digitizing threat hunting workflows by automating indicator-of-compromise correlation across endpoint, network, and identity telemetry. Mid-market enterprises without dedicated threat intelligence teams are adopting these capabilities fastest, compressing the mean-time-to-response from hours to minutes without proportional headcount expansion.
The EU NIS2 Directive is mandating incident notification thresholds and supply chain security requirements for critical infrastructure operators. Managed security providers must now maintain 24/7 French-language support for ANSSI coordination and document subprocessor chains to German BSI standards, reshaping service delivery footprints across the European Union.
Consumption-based pricing models are displacing traditional seat-based subscriptions in enterprise procurement. CISOs in United States healthcare and German automotive verticals now prefer outcome metrics tied to mean-time-to-detect improvements rather than per-endpoint fees, compressing provider margins while locking in longer contract durations.
Cyber Security As a Service Market Segmentation
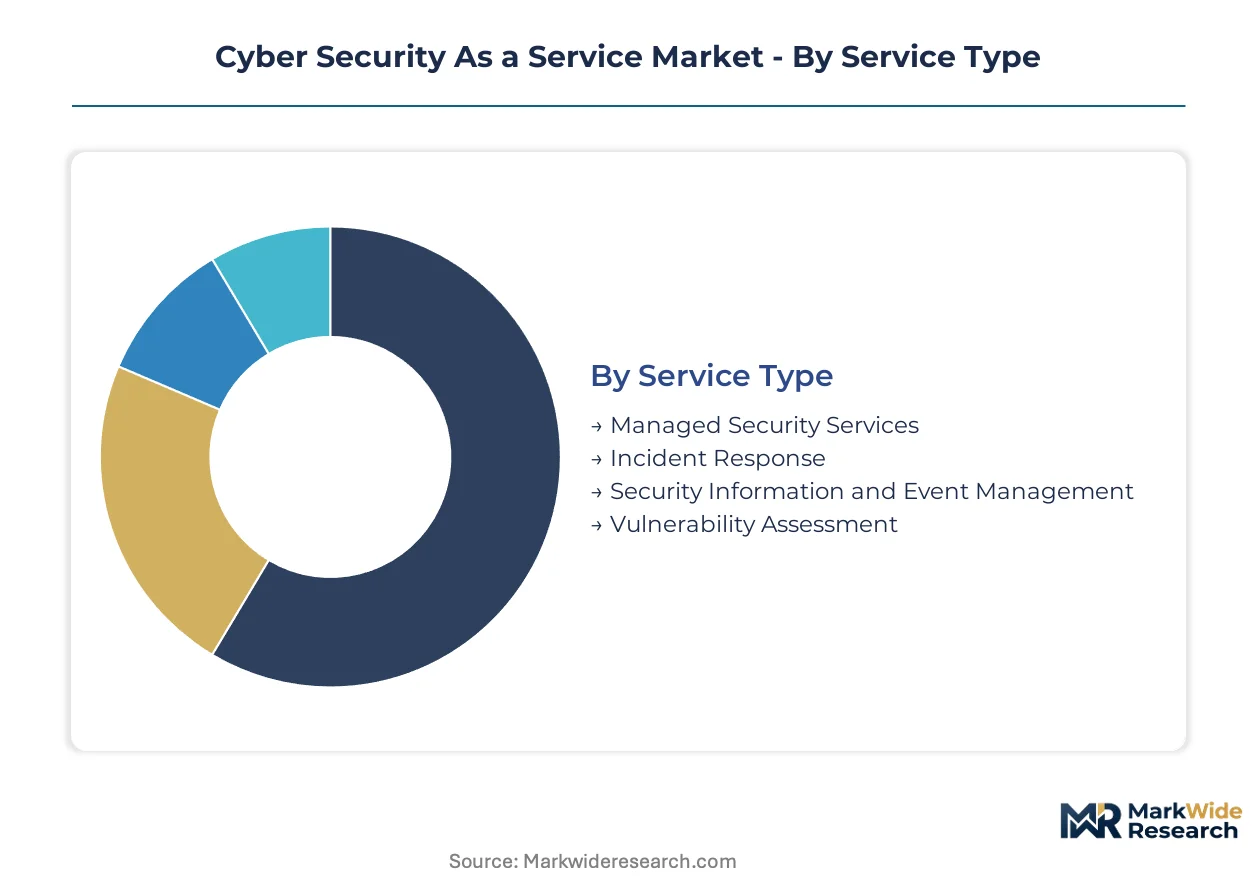
Cyber Security As a Service providers must architect delivery models around distinct operational intensities, as managed SOC operations demand fundamentally different staffing ratios than automated vulnerability scanning. Segmentation reveals where subscription economics concentrate and which deployment configurations justify premium pricing tiers.
Service Type:
After-sales service intensity varies dramatically across service categories, with 24/7 SOC operations requiring sustained engineering engagement compared to project-based assessment deliverables.
- Managed Security Services:Continuous threat monitoring delivered through dedicated analyst teams with sub-15-minute response SLAs. United States financial institutions drive demand as Basel Committee operational resilience guidelines compel externalization of round-the-clock capabilities.
- Incident Response:Retainer-based breach containment and forensic investigation services activated upon compromise detection. German automotive manufacturers are expanding procurement following BSI supply chain security mandates that require documented response playbooks.
- Security Information and Event Management:Centralized log aggregation and correlation delivered as cloud-native SaaS with automated alerting workflows.
- Vulnerability Assessment:Periodic scanning and penetration testing services with compliance-ready reporting for audit cycles.
By volume, Managed Security Services leads. By growth pace, Incident Response is ahead.
Deployment Model:
Cost tier differentiation separates enterprise-grade sovereign deployments from standardized multi-tenant offerings accessible to mid-market buyers.
- Cloud-Based:Fully managed SaaS delivery eliminating customer infrastructure burden with elastic compute scaling for telemetry processing. United States healthcare providers under HIPAA security rule obligations are retiring on-premises SIEM stacks fastest.
- Hybrid:Split architecture preserving sensitive data processing on-premises while leveraging cloud analytics for correlation. Japanese manufacturing conglomerates prefer this model to satisfy METI data localization guidance without sacrificing threat intelligence scale.
- On-Premises:Customer-controlled hardware and software deployment with provider-managed configuration and tuning services.
- Multi-Tenant:Shared infrastructure platforms achieving cost efficiency through pooled resource utilization across customer bases.
Cloud-Based deployments dominate new contract value. Hybrid configurations are climbing fastest as sovereignty requirements harden.
End User:
Customer type determines contract structure complexity, with government procurement mandating FedRAMP authorization timelines that extend sales cycles substantially.
- Enterprise:Large organizations with dedicated CISO functions purchasing integrated security stacks across identity, endpoint, and network layers. German DAX-listed corporations are consolidating vendor relationships under EU NIS2 Directive supply chain security requirements.
- Government Sector:Federal and state agencies requiring FedRAMP-authorized or equivalent sovereign certification with documented data residency controls. United States civilian agencies face SEC cyber disclosure mandates that elevate incident response retainer priority.
- SMBs:Small and medium businesses accessing standardized service tiers through channel partners without dedicated security personnel.
- Educational Institutions:Universities and school districts with constrained budgets prioritizing grant-funded security awareness and basic monitoring capabilities.
Enterprise accounts generate the highest per-customer revenue. Government Sector contracts are expanding most quickly as sovereign cyber defense investments accelerate.
Industry Vertical:
Application-specific compliance burdens create vertical specialization opportunities, with healthcare and financial services presenting the most stringent regulatory environments.
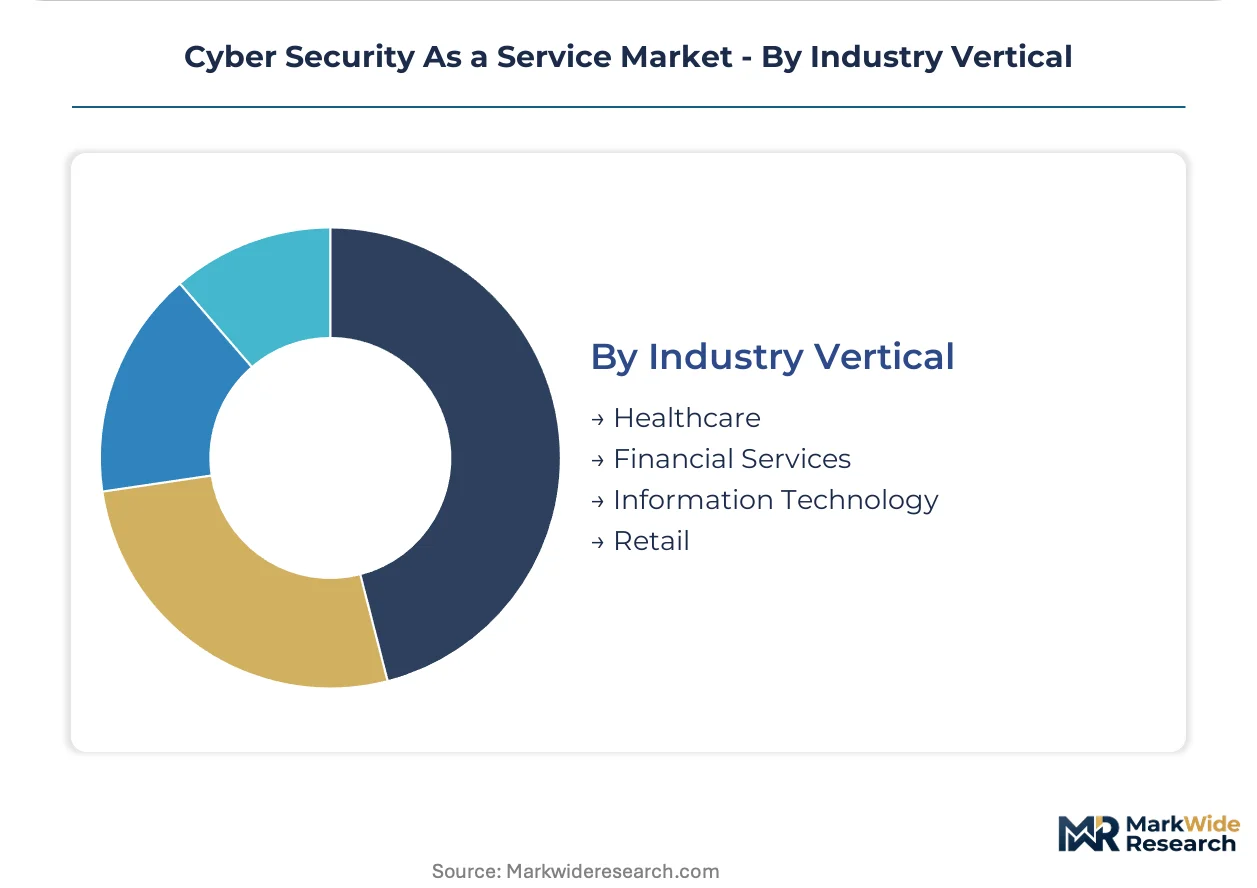
- Financial Services:Banks, insurers, and payment processors subject to DORA operational resilience requirements and SEC cyber risk disclosure rules. United States regional banks are externalizing SOC operations fastest as qualified analyst hiring fails to keep pace with regulatory expectations.
- Healthcare:Hospitals and health systems navigating HIPAA security rule enforcement and FDA medical device cybersecurity guidance. German university hospitals are prioritizing vulnerability management for connected clinical equipment under BSI healthcare sector advisories.
- Information Technology:Software vendors and cloud service providers managing their own supply chain security attestations and customer trust programs.
- Retail:Merchants and e-commerce platforms defending payment card environments and customer databases against credential stuffing and POS intrusion campaigns.
Financial Services commands the largest addressable spend. Healthcare is gaining share fastest as medical device connectivity expands attack surfaces.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States-based managed security providers export SOC-as-a-service capabilities to European financial institutions and Japanese manufacturers seeking FedRAMP-equivalent operational standards. Cross-border data flows concentrate through Frankfurt, Tokyo, and Singapore hubs as sovereign cloud requirements fragment delivery architectures.
United States
Financial institutions and federal agencies drive demand for 24/7 outsourced threat detection. SEC cyber disclosure mandates and FedRAMP authorization requirements compel providers to maintain sovereign data residency controls. The Washington DC-to-Boston corridor hosts the densest concentration of government-contracted security operations centers.
Germany
Automotive manufacturers and critical infrastructure operators externalize security operations under BSI supply chain mandates. EU NIS2 Directive incident notification thresholds require documented response playbooks with German-language ANSSI coordination capabilities. Bavaria's industrial corridor around Munich leads procurement of OT-security managed services for manufacturing plants.
Japan
Manufacturing conglomerates and healthcare systems adopt hybrid deployment models to satisfy METI data localization guidance. The country's national cybersecurity regulator enforces strict subprocessor documentation requirements for foreign-managed service providers. Tokyo-Osaka corridor enterprises prioritize cloud-native SIEM migration while retaining sensitive data processing on-premises.
United Kingdom
Financial services firms under Bank of England operational resilience expectations externalize SOC capabilities faster than continental peers. The UK national cybersecurity center mandates incident reporting thresholds that elevate retainer-based incident response procurement. London's fintech cluster drives consumption-based pricing adoption for mid-market security subscriptions.
India
IT service providers and banking sector entities expand managed security procurement under RBI cybersecurity framework obligations. The country's national cybersecurity regulator enforces strict data localization for critical infrastructure operators. Bangalore and Hyderabad technology corridors concentrate delivery centers for global MSSP operations serving North American and European clients.
Cyber Security As a Service Market Vendor Landscape
Channel-controlling players compete with product-specialist players across tiered procurement segments, with hyperscale cloud platforms capturing enterprise consolidations while boutique providers defend mid-market relationships. The vendor base organizes around three strategic archetypes: platform-native integrators bundling identity and endpoint layers, standalone threat intelligence specialists, and vertical-focused compliance enablers. Dominant competitive moves include M&A to acquire SOAR automation capabilities and strategic partnerships to embed managed detection into broader IT outsourcing contracts.
Within the platform-native tier, Microsoft and Palo Alto Networks exemplify cloud-anchored delivery models, while CrowdStrike Holdings occupies a position as an endpoint-centric specialist. These three entities represent divergent architectural bets: unified security stacks versus best-of-breed integration, with each archetype capturing distinct procurement preferences across regulated industries.
| Leading Market Players |
|---|
| Microsoft |
| Cisco Systems |
| Palo Alto Networks |
| IBM Corporation |
| Fortinet |
| CrowdStrike Holdings |
| Check Point Software Technologies |
| Trend Micro |
| AWS |
| Others |
Supply Flow & Price Mechanics
Single-source dependency on hyperscale cloud infrastructure in the United States determines both the three-tier pricing spread across FedRAMP-authorized, enterprise-grade, and mid-market service tiers and the geographic footprint of security operations center delivery. Cloud sovereignty mandates in Germany and Japan fragment what would otherwise be unified multi-tenant platforms, forcing providers to replicate infrastructure across jurisdictions and compressing margins at the standard tier.
Pricing Analysis
Next-generation cloud-native SIEM platforms command premium positioning over legacy on-premises deployments and emerging quantum-resistant cryptography bundles, creating a technology-generation pricing gap that stratifies the market. Subscription-based SaaS tiers dominate, with price differentiation driven by FedRAMP authorization status and mean-time-to-detect SLA guarantees. Cost compression in the mid-market tier intensifies as channel partners consolidate procurement volume, while government sector buyers exhibit the lowest price sensitivity due to sovereign compliance mandates.
Supply Chain Analysis
Tariff exposure between the United States and China dominates supply chain risk for hardware security modules and specialized SOC analyst training pipelines. The industry draws from talent pools concentrated in India, Poland, and the United States, with component dependencies spanning cloud compute from AWS, Azure, and Google Cloud. Single-source vulnerability in FedRAMP-authorized data centers creates chokepoint risk. Distribution runs through direct enterprise sales teams and managed service provider channel partners.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The market sits at a platform-economics inflection where Microsoft Sentinel's ecosystem integration is collapsing the standalone best-of-breed vendor model, rewarding interoperability-first architectural bets.
For Market Incumbents: Harden FedRAMP authorization pipelines against 12-18 month certification delays that constrain speed-to-market for sovereign cloud offerings. Deepen vertical integration into OT-security capabilities for manufacturing and energy infrastructure, where managed services penetration remains below 15 percent of addressable accounts and specialized compliance expertise commands pricing power. For New Entrants and Emerging Players: Build out retainer-based incident response services as a distinct revenue stream separate from ongoing monitoring, capitalizing on SEC cyber disclosure mandates that elevate procurement priority among United States regional banks. Target German automotive manufacturers under BSI supply chain security mandates with German-language ANSSI coordination capabilities as the go-to-market wedge. For Investors and Strategic Acquirers: Boutique SOAR automation specialists with pre-built playbooks for NIS2 Directive compliance represent the most attractive acquisition archetype for platform-native integrators seeking to compress mean-time-to-response metrics. The signal to watch is consolidation velocity among mid-market MSSPs serving United States healthcare providers, where HIPAA security rule enforcement is accelerating vendor rationalization.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies identity, endpoint, and network telemetry through Microsoft Sentinel or equivalent cloud-native stacks. |
| Acquisition of Specialist Firm | Captures SOAR automation capabilities and pre-built compliance playbooks for EU NIS2 Directive obligations. |
| Geographic Expansion | Establishes sovereign data residency in Germany, Japan, and United States to satisfy divergent localization requirements. |
| Strategic Partnership | Embeds managed detection into broader IT outsourcing contracts with channel-controlling systems integrators. |
| Product Launch | Introduces quantum-resistant cryptography migration services aligned with NIST post-quantum standards. |
Methodological Framework
Cross-validation between primary interviews with CISOs, SOC directors, and managed security provider executives and secondary sources including SEC cyber disclosure filings, FedRAMP authorization databases, and EU NIS2 Directive implementation guidance anchors the qualitative findings. Bottom-up and top-down triangulation reconciles contract value data from government procurement portals with hyperscaler security revenue disclosures.
Calibration against historical adoption curves for cloud-native SIEM migration and operational technology security penetration shapes the analytical framework across the analysis window. Segmentation dimensions include service type, deployment model, end-user category, and industry vertical, with CAGRs derived from elasticity modeling of regulatory compliance spending and analyst staffing ratios.
The forecast holds incumbent behavior within observed patterns; aggressive ecosystem bundling moves by hyperscale cloud platforms or sovereign cloud fragmentation beyond current trajectories would shift outcomes. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Data Center Security Market
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Global API Security Market
Cybersecurity
Domain Name System (DNS) Firewall Market
Cybersecurity
Wireless Lan Security Market
Cybersecurity
Europe IoT Security Market
Cybersecurity
Global Sensitive Data Discovery Market
Cybersecurity
Saudi Arabia Cybersecurity Market
Cybersecurity
India Network Security and Cyber Risk Management Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Global Zero-Trust Security Market
Cybersecurity
Cloud Application Security Market
Cybersecurity
Cloud Access Security Broker Market
Cybersecurity
New Zealand Cybersecurity Market