
 Austria Cybersecurity Market | 2026-2036
Austria Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Austria Cybersecurity Market Analysis
Legacy signature-based detection is consolidating toward AI-native behavioral analytics, compressing incumbent tool refresh cycles. Palo Alto Networks leverages cloud-native platform architecture to anchor enterprise accounts across Vienna and Linz. IBM Corporation sustains consulting-led deployment models that integrate managed security with incident response workflows. SEC Consult differentiates through offensive security testing rooted in Central European regulatory familiarity.
Austria cybersecurity encompasses hardware, software, and service layers engineered to protect digital assets through encryption protocols, intrusion detection systems, and zero-trust access frameworks operating at sub-100-millisecond threat response thresholds. Its primary purpose spans safeguarding critical infrastructure, financial transaction integrity, and citizen data sovereignty against state-sponsored and criminal adversaries. Managed Security services capture recurring revenue pools as Austrian enterprises outsource Security Operations Center staffing. Cloud-Based deployment models expand fastest among mid-market manufacturers adopting hybrid infrastructure. Finance and Healthcare verticals absorb disproportionate compliance investment under tightening EU supervisory expectations.
The EU NIS2 Directive, enforced through Austria's national transposition, mandates incident reporting timelines and supply-chain security audits that reshape procurement criteria. BSI Austria aligns federal agency standards with ENISA guidelines, while GDPR residual provisions enforce cross-border data breach penalties that elevate liability-aware spending. Stakeholders must weigh sovereign cloud certifications against interoperability with NATO-aligned threat intelligence sharing frameworks.
Market Dynamics
The EU NIS2 Directive's transposition into Austrian federal law is compressing procurement timelines and mandating supply-chain security audits that reshape how enterprises evaluate vendors.
Growth Catalysts
- EU NIS2 Directive:Incident reporting mandates and supply-chain audit requirements are forcing Austrian critical infrastructure operators to accelerate security spending and consolidate vendor relationships.
- Digital banking expansion:Austrian financial institutions are deploying zero-trust architectures and behavioral analytics to protect real-time payment rails and customer data vaults.
- Vienna enterprise corridor:Concentrated demand from federal government clusters and headquarters of major industrial groups creates scalable deployment opportunities for integrated security platforms.
Market Restraints
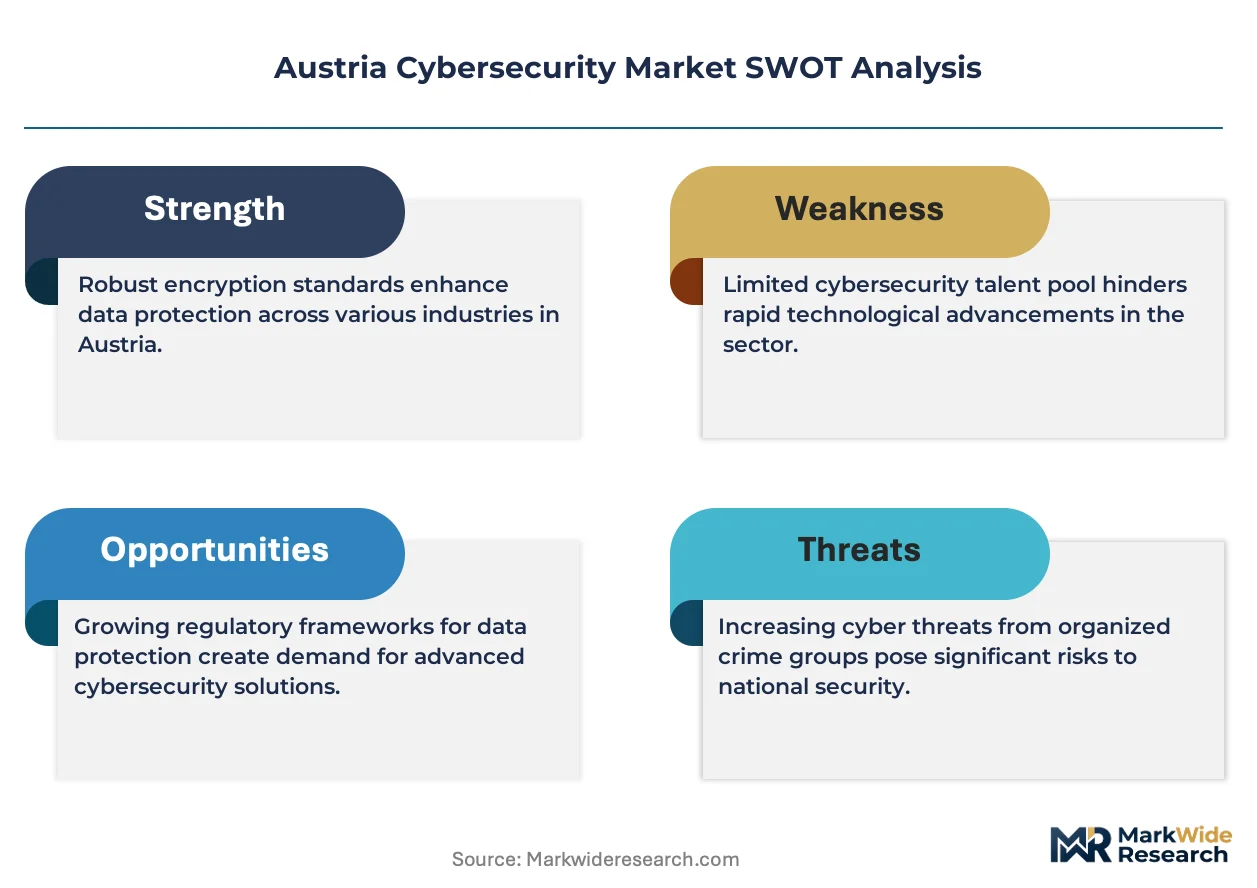
- Specialized talent scarcity:Austria's domestic pool of certified incident responders and threat intelligence analysts remains insufficient relative to NIS2-mandated staffing requirements.
- Legacy infrastructure drag:Manufacturing and public sector entities operate hybrid environments where decades-old operational technology resists seamless integration with modern security stacks.
- Compliance cost concentration:GDPR residual provisions and sector-specific supervisory expectations impose disproportionate liability burdens on mid-market enterprises with limited security budgets.
Strategic Opportunities
- Managed Security Services:Austrian enterprises are outsourcing Security Operations Center staffing to specialized providers, creating recurring revenue pools and long-term contract visibility.
- Cloud-native convergence:Mid-market manufacturers adopting hybrid infrastructure present openings for platforms integrating endpoint detection with cloud workload protection.
- ENISA alignment:BSI Austria's harmonization with EU agency standards enables vendors to leverage certifications across neighboring member states without redundant audit cycles.
Industry Challenges
- Operational technology integration:Industrial control systems in Austrian energy and manufacturing sectors require specialized segmentation architectures that generalist security vendors struggle to deliver.
- Cross-border data sovereignty:Enterprises must reconcile GDPR breach notification timelines with NATO-aligned threat intelligence sharing frameworks, creating compliance architecture complexity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Austria Cybersecurity Market |
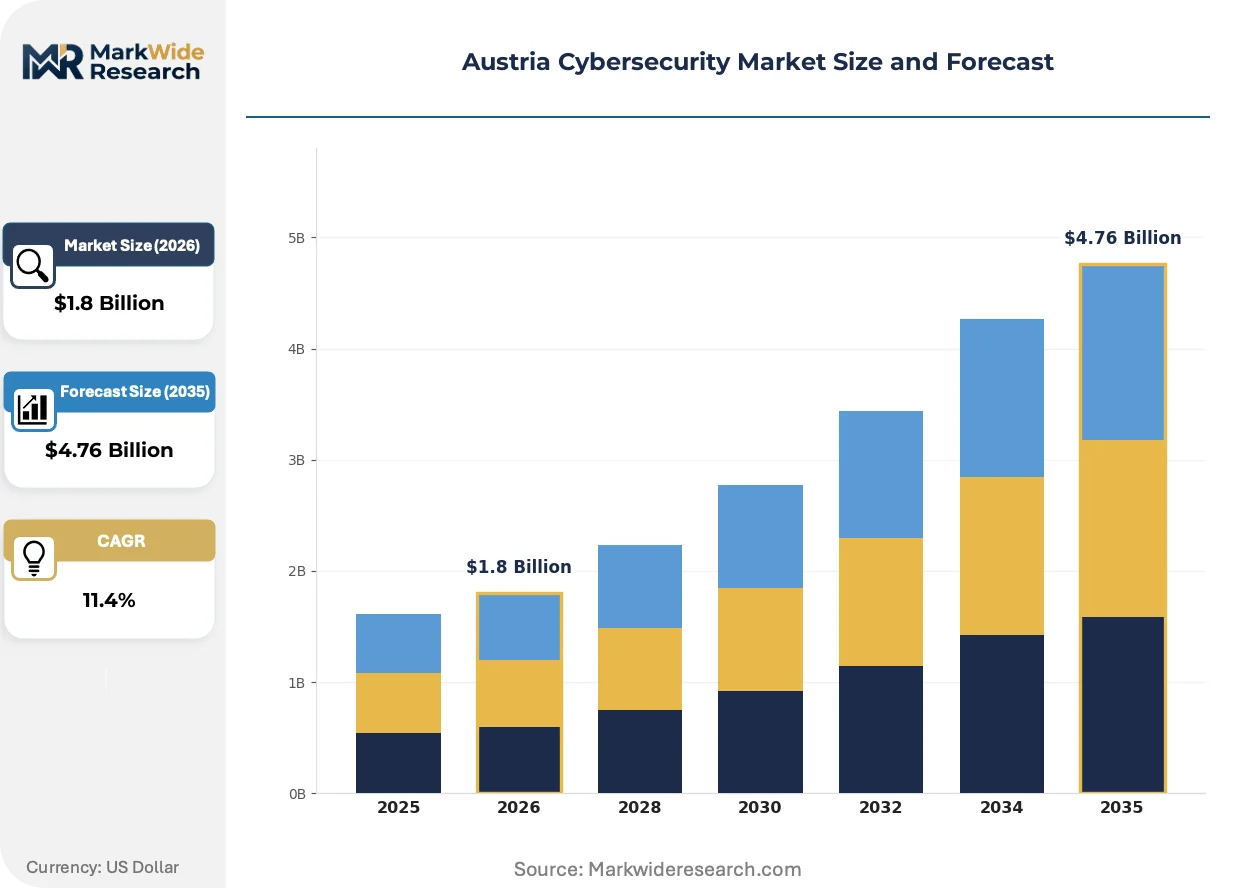
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $4.76 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Security, Incident Response, Threat Intelligence, Compliance Management Industry Vertical: Finance, Healthcare, Retail, Manufacturing Deployment Model: On-Premise, Cloud-Based, Hybrid, Endpoint Security Customer Type: Small Businesses, Enterprises, Government Agencies, Non-Profits |
| Companies Covered | IBM Corporation, Check Point Software Technologies, Palo Alto Networks, DeepStrike, CyberArk Software, Cisco Systems, SEC Consult, CRYPTAS, Fortinet, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Austria Cybersecurity Market Emerging Trajectories
Behavioral analytics and autonomous response capabilities are displacing signature-based detection across Austrian enterprise deployments, compressing refresh cycles for incumbent tool vendors.
Extended detection and response platforms are automating threat correlation across endpoints, networks, and cloud workloads. Austrian financial institutions and federal agencies are adopting these systems at accelerated pace to meet NIS2-mandated response timelines. The technology is automating tier-1 analyst workflows and reducing mean-time-to-containment below the 100-millisecond threshold specified in critical infrastructure guidelines.
The EU NIS2 Directive, transposed through Austria's national implementation act, mandates 24-hour incident reporting and supply-chain security attestations. Industrial consequence includes procurement teams rewriting vendor evaluation scorecards to prioritize certified security postures over price. Energy and transport operators are most affected, responding by pre-qualifying fewer suppliers and demanding continuous compliance monitoring.
Austrian enterprises are unbundling managed detection from incident response retainers, treating these as separate procurement categories with distinct performance metrics. System integrators and consultancies are capturing the response workflow layer while pure-play technology vendors compete on detection efficacy. This pattern is most visible among Vienna-headquartered industrial conglomerates with complex multi-site environments.
Austria Cybersecurity Market Segmentation
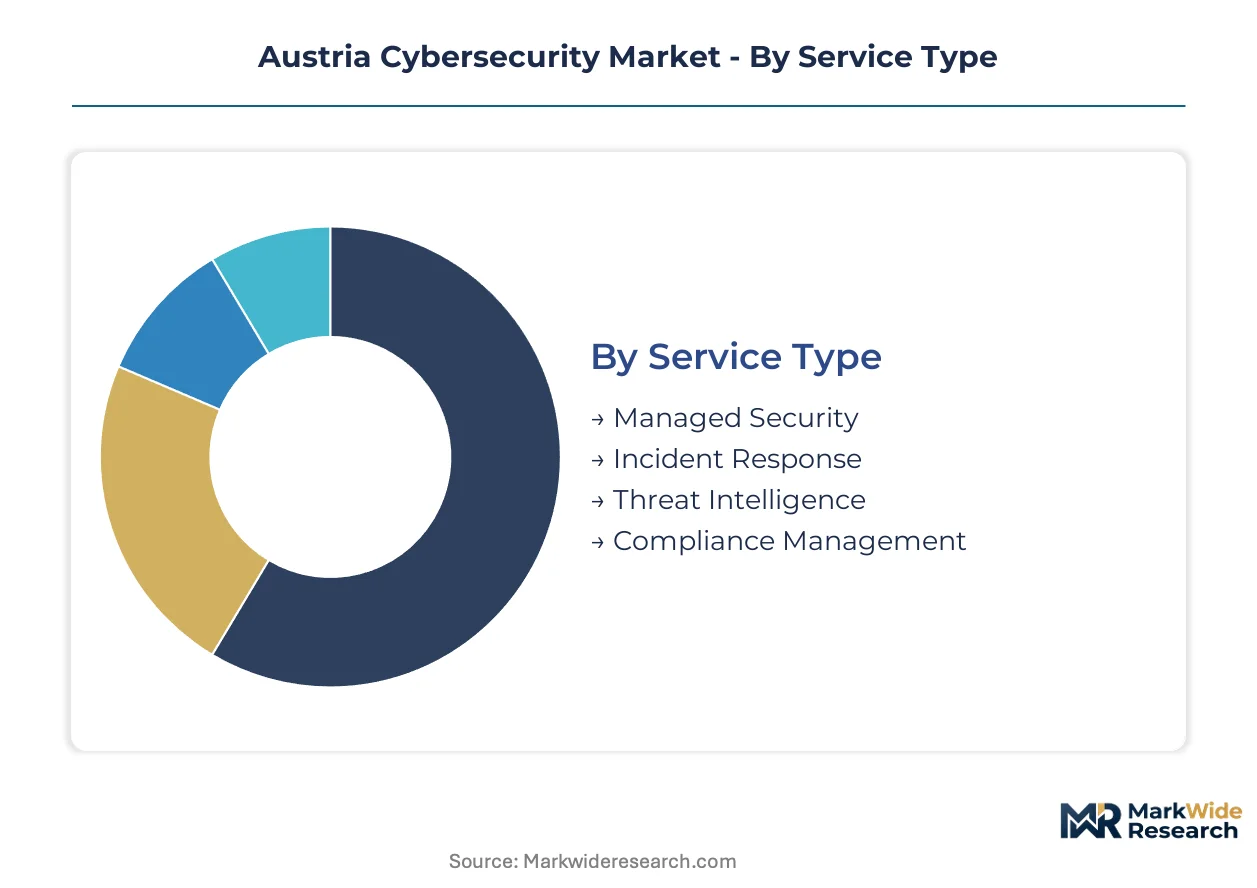
Segmentation reveals how procurement patterns split across Austrian cybersecurity demand. NIS2 compliance timelines and hybrid infrastructure adoption create divergent spending profiles that vendors must navigate.
Service Type:
Supply concentration clusters around recurring revenue models that address Austria's persistent talent scarcity.
- Managed Security:Continuous Security Operations Center monitoring and threat detection delivered through subscription contracts. Vienna-headquartered financial institutions and federal agencies outsource tier-1 analyst staffing to meet NIS2-mandated coverage requirements without expanding internal headcount.
- Incident Response:Retainer-based breach containment and forensic investigation services activated upon detection. Austrian critical infrastructure operators pre-negotiate response SLAs to satisfy the directive's compressed reporting timelines.
- Threat Intelligence:Curated adversary indicators and attack pattern feeds tailored to Central European threat actor profiles.
- Compliance Management:Audit preparation and documentation services mapping technical controls to BSI Austria and ENISA frameworks.
Managed Security absorbs the bulk of installed capacity; Incident Response is expanding most quickly.
Industry Vertical:
Cost tier stratification separates compliance-heavy sectors from price-sensitive adopters.
- Finance:Real-time payment rail protection and customer data vault security consuming premium-tier solutions. Austrian banks deploy behavioral analytics and zero-trust architectures as digital transaction volumes accelerate.
- Healthcare:Patient record encryption and medical device network segmentation under GDPR residual enforcement. University hospitals in Graz and Innsbruck invest disproportionately in endpoint detection for connected clinical equipment.
- Retail:POS system hardening and e-commerce fraud prevention targeting mid-market budget constraints.
- Manufacturing:Operational technology segmentation for industrial control systems resisting cloud-native integration.
Finance absorbs the bulk of installed capacity; Healthcare is expanding most quickly.
Deployment Model:
Application context dictates architecture choice across Austria's hybrid infrastructure landscape.
- Cloud-Based:Scalable workload protection and SaaS-delivered security services requiring no on-site hardware. Mid-market manufacturers in Upper Austria adopt these models fastest as they migrate ERP systems to hybrid environments.
- Hybrid:Coordinated on-premise and cloud security controls with unified policy management. Federal government clusters in Vienna demand this architecture to retain sovereign data custody while accessing elastic compute.
- On-Premise:Air-gapped appliance deployments for classified networks and legacy system dependencies.
- Endpoint Security:Device-level detection agents protecting distributed workforces and remote operational technology interfaces.
Hybrid deployments absorb the bulk of installed capacity; Cloud-Based is expanding most quickly.
Customer Type:
Volume concentration maps to procurement sophistication and compliance exposure.
- Enterprises:Multi-site integrated platforms with dedicated security architecture teams. Industrial conglomerates headquartered in Vienna's enterprise corridor consolidate vendor relationships to simplify NIS2 audit trails.
- Government Agencies:Federal and state entities procuring through BSI Austria-certified frameworks with sovereign cloud requirements.
- Small Businesses:Bundled security packages distributed through managed service provider channels.
- Non-Profits:Grant-subsidized basic protection for research institutions and cultural organizations.
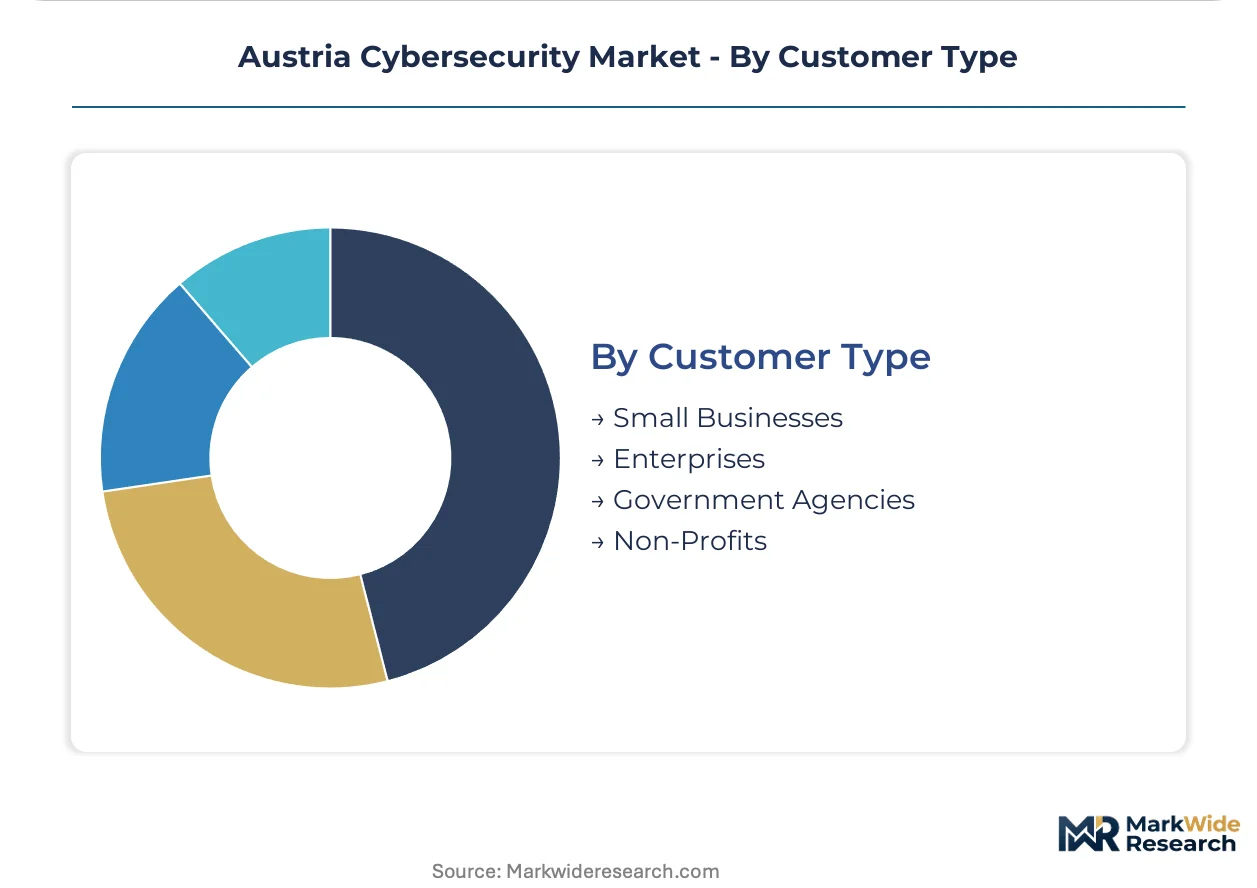
Enterprises absorb the bulk of installed capacity; Government Agencies are expanding most quickly.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Demand concentrates in Vienna's enterprise corridor and federal government clusters, with procurement patterns radiating outward to industrial centers in Upper Austria and Styria. The EU NIS2 Directive's national transposition creates uniform compliance pressure across all sub-regions while local infrastructure conditions shape deployment preferences.
Vienna
Financial institutions and federal agencies anchor procurement volume in the capital region. BSI Austria certification requirements govern sovereign cloud deployments for government clusters. Headquarters of major industrial conglomerates consolidate vendor relationships to simplify NIS2 audit trails across multi-site environments.
Upper Austria
Mid-market manufacturers drive cloud-native security adoption as ERP migration accelerates. The regional government's digitalization programs subsidize hybrid infrastructure investments. Linz industrial parks host concentrated demand for operational technology segmentation solutions.
Styria
Automotive and machinery producers require specialized industrial control system protection. Graz university hospitals invest disproportionately in medical device network security under GDPR enforcement. The region's research institutions generate grant-subsidized demand for basic protection packages.
Tyrol
Tourism-dependent enterprises prioritize POS system hardening and e-commerce fraud prevention. Innsbruck healthcare clusters expand endpoint detection for connected clinical equipment. Alpine logistics operators demand supply-chain security attestations to maintain EU market access.
Austria Cybersecurity Market Vendor Landscape
Platform consolidation dominates the current landscape as enterprises reduce vendor sprawl to meet NIS2 audit requirements. The market structure tilts toward integrated solution providers with consulting capabilities, compressing pure-play tool vendors into niche positions. Three archetypes occupy distinct competitive terrain: cloud-native platform vendors, consulting-led systems integrators, and offensive security specialists. M&A activity accelerates as incumbents acquire behavioral analytics capabilities, while strategic partnerships between technology vendors and regional consultancies expand local delivery footprints.
Among the integrated platform tier, Palo Alto Networks and IBM Corporation exemplify divergent go-to-market approaches. Palo Alto Networks anchors enterprise accounts through cloud-native architecture deployed across Vienna and Linz corridors. IBM Corporation sustains consulting-led deployment models that weave managed security services with incident response workflows. SEC Consult occupies a specialist position rooted in Central European regulatory familiarity and offensive security testing methodologies. These three patterns—platform-centric, services-anchored, and compliance-specialized—structure competitive positioning across Austrian procurement cycles.
| Leading Market Players |
|---|
| IBM Corporation |
| Check Point Software Technologies |
| Palo Alto Networks |
| DeepStrike |
| CyberArk Software |
| Cisco Systems |
| SEC Consult |
| CRYPTAS |
| Fortinet |
| Others |
Supply Flow & Price Mechanics
Private-equity-rolled-up managed security providers anchor supply concentration in Vienna's enterprise corridor, translating recurring revenue visibility into pricing discipline that resists commoditization pressure from cloud-native entrants. Their subscription-based contracts with federal agencies and financial institutions create captive demand pools that insulate margin structures from transactional pricing erosion.
Pricing Analysis
Volume concentrates in standardized SaaS-tiered subscriptions while margin pools in customized incident response retainers and compliance management bundles. Price differentiation hinges on ENISA certification tier and sovereign cloud custody level, with BSI Austria-certified deployments commanding substantial premiums over uncertified alternatives. Pricing pressure stems from mid-market manufacturers demanding cloud-native solutions at compressed per-seat rates. Government agencies exhibit lowest price sensitivity due to NIS2-mandated coverage requirements, while retail and small business segments drive hardest bargain through managed service provider channels.
Supply Chain Analysis
Single-source vulnerability sits with specialized threat intelligence feeds originating from NATO-aligned sharing frameworks concentrated in Germany and the Netherlands. Hardware dependencies draw from Taiwan for semiconductor components, Ireland for data center infrastructure, and Germany for industrial control system modules. Supply chain risk centers on regulatory restriction disrupting cross-border data flows under GDPR enforcement. Distribution runs through Vienna-headquartered systems integrators with BSI Austria certification, supplemented by direct vendor relationships with federal procurement frameworks.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Austria cybersecurity market sits in a technology-transition phase where AI-native behavioral analytics displaces legacy signature-based detection, compressing refresh cycles and redistributing value capture toward platforms with autonomous response capabilities.
For Market Incumbents: Deploy vertical integration into sovereign cloud infrastructure to defend against hyperscaler encroachment on federal accounts. Consolidate tier-2 incident response capabilities through targeted capability acquisition, addressing the talent scarcity that constrains NIS2 compliance scaling. Anchor enterprise relationships with Vienna-headquartered industrial conglomerates through multi-year managed security contracts that embed compliance documentation into service delivery. For New Entrants and Emerging Players: Capture white-space in operational technology segmentation for Styrian automotive and Upper Austrian manufacturing facilities, where generalist security vendors struggle with legacy industrial control integration. Target Graz and Innsbruck healthcare clusters with medical device network security offerings, exploiting GDPR enforcement pressure on university hospitals. Lead with ENISA-aligned certification to bypass redundant audit cycles and accelerate procurement timelines. For Investors and Strategic Acquirers: Distressed-cycle entries favor offensive security specialists with Central European regulatory familiarity in Vienna and Linz corridors, where compliance complexity creates durable moats. Long-term viability hinges on recurring revenue visibility from managed security contracts rather than transactional tool sales. Watch NIS2 enforcement intensity as the inflection signal determining whether compliance spending accelerates or plateaus.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint detection with cloud workload protection for hybrid Austrian manufacturers. |
| Acquisition of Specialist Firm | Adds operational technology segmentation capabilities for energy and transport operators. |
| Strategic Partnership | Aligns vendor certifications with BSI Austria and ENISA frameworks to reduce audit friction. |
| Geographic Expansion | Establishes Linz delivery presence to capture Upper Austrian mid-market ERP migration demand. |
| Product Launch | Introduces autonomous response modules that compress mean-time-to-containment below NIS2 thresholds. |
Methodological Framework
Multi-period observation of NIS2 compliance timelines and cloud-native adoption rates anchored the trend analysis, supplemented by interviews with CISOs at Vienna-headquartered financial institutions, federal procurement officers, managed security service provider executives, and industrial control system engineers. Secondary validation drew from ENISA threat landscape reports, BSI Austria certification databases, EU directive transposition documents, and hyperscaler security service disclosures. Bottom-up segmentation sizing triangulated against top-down market aggregation to constrain estimate variance.
Input-output matrices mapped service type, vertical, and deployment model dimensions across the projection horizon, with CAGRs derived from segment-level growth rate reconciliation against aggregate market expansion. Modeled variables included NIS2 enforcement intensity, hybrid infrastructure penetration curves, and sovereign cloud certification velocity as Austria-specific forecast inputs.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to EU regulatory amendment cycles and NATO threat intelligence sharing continuity. Forecasts reflect documented assumptions about compliance timeline adherence and talent supply elasticity. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Canada Cybersecurity Market
Cybersecurity
Cloud Security Market
Cybersecurity
North America Data Exfiltration Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Deception Technology Market
Cybersecurity
United States Cybersecurity Market
Cybersecurity
CDN Security Market
Cybersecurity
Norway Cybersecurity Market
Cybersecurity
Data Protection Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Belgium Cybersecurity Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Retail Cybersecurity Market
Cybersecurity
Global Quantum Cryptography Solutions Market