
 India Ransomware Protection Market | 2026-2036
India Ransomware Protection Market Size, Share, and Industry Trends Forecast 2026-2036
India Ransomware Protection Market Insights
Managed detection and response revenue is tilting from pure software licensing toward continuous monitoring contracts. Palo Alto Networks leverages its Cortex platform to anchor enterprise accounts across India's banking sector. CrowdStrike competes through cloud-native endpoint specialization, while K7 Computing dominates domestic mid-market channels with localized threat signatures.
Ransomware protection encompasses endpoint security architectures, network segmentation protocols, and encrypted backup systems engineered to detect cryptographic lockdown attempts and restore operational continuity without attacker payment. Solutions deploy through on-premises appliances, cloud-native agents, or hybrid configurations with managed services overlay, with AI-based behavioral analysis now superseding signature-dependent detection in enterprise procurement. Cloud-based deployment captures the fastest expansion as SaaS delivery reduces capital intensity for mid-tier buyers, while BFSI end users sustain premium pricing for hybrid architectures that preserve data sovereignty. Backup solutions and endpoint protection command the deepest margin pools where ransomware recovery guarantees differentiate vendor positioning.
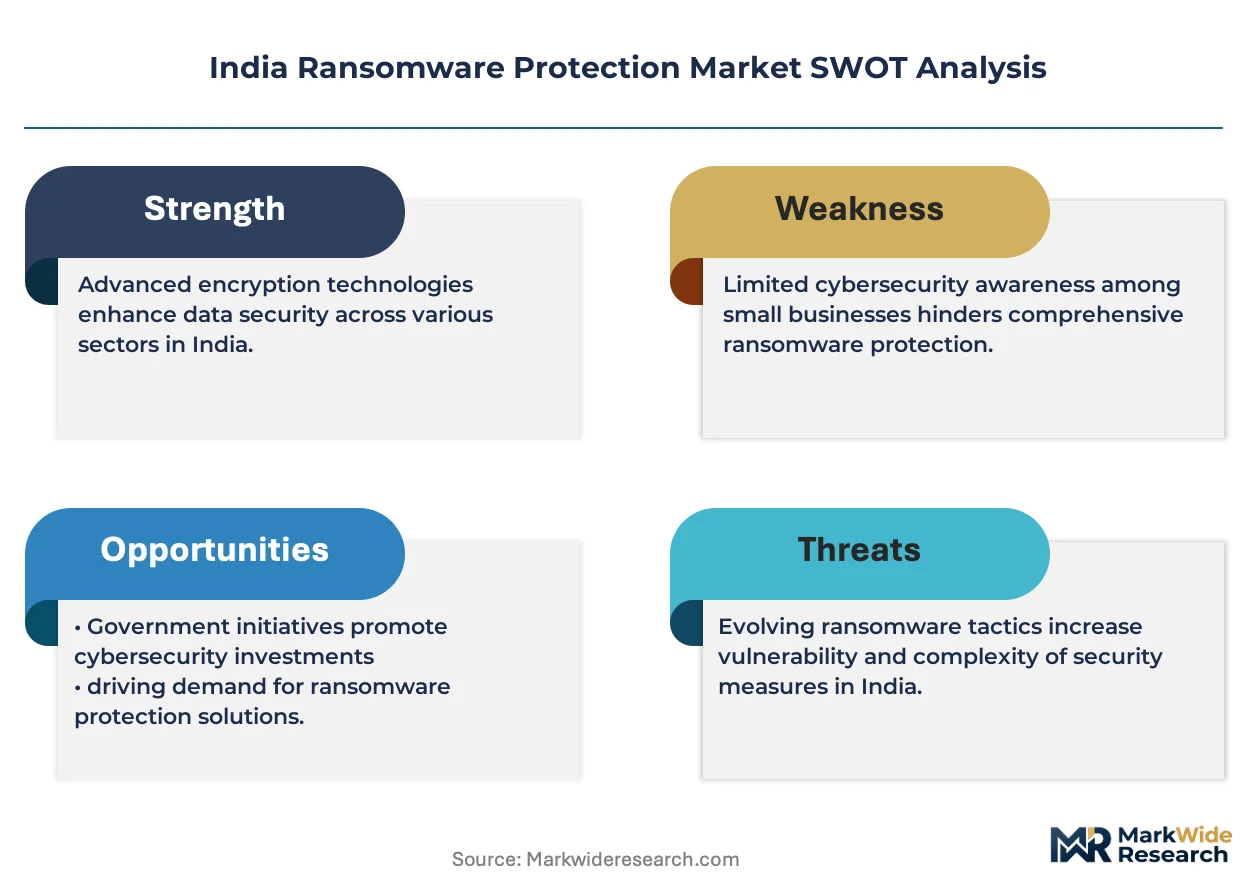
CERT-In mandates incident reporting within six hours, compelling organizations to upgrade from passive antivirus to active threat-hunting platforms. The Digital Personal Data Protection Act imposes breach notification penalties that reshape procurement criteria toward vendors with demonstrable forensic response capabilities. BIS cybersecurity standards for critical infrastructure further tighten product certification requirements. Stakeholders must evaluate whether their vendor's India-specific threat intelligence feeds match the velocity of regional ransomware variants before committing to multi-year enterprise agreements.
Market Dynamics
The CERT-In six-hour incident reporting mandate is compressing procurement cycles across Indian enterprises, forcing organizations to replace passive antivirus with active threat-hunting platforms before contract renewals expire.
Growth Catalysts
- Digital Payment Surge:UPI transaction volumes exceeding 10 billion monthly transactions are expanding BFSI attack surfaces and mandating real-time endpoint monitoring investments.
- DPDP Act Penalties:The Digital Personal Data Protection Act's breach notification fines are redirecting procurement budgets toward vendors with demonstrable forensic response capabilities.
- AI Behavioral Detection:Machine learning models analyzing endpoint behavior patterns are displacing signature-dependent detection in enterprise security architectures.
Market Restraints
- Skilled Analyst Scarcity:India's shortage of certified SOC analysts is inflating managed detection and response service costs beyond mid-market budget thresholds.
- Legacy Infrastructure Debt:State-owned banks running Windows 7 and unpatched server stacks face integration friction with cloud-native protection agents.
- Input Cost Volatility:GPU and specialized hardware for on-premises AI inference engines are subject to import duty fluctuations and supply chain disruptions.
Strategic Opportunities
- Tier-2 City Expansion:Manufacturing hubs in Coimbatore, Vadodara, and Chandigarh remain underpenetrated for ransomware protection relative to Mumbai-Pune data center concentration.
- Critical Infrastructure Mandate:BIS cybersecurity standards for power grids and telecommunications are creating certified-product procurement pipelines for domestic vendors.
- Zero Trust Convergence:The integration of network segmentation with identity-aware access controls is opening unified platform opportunities beyond point endpoint solutions.
Industry Challenges
- Forensic Certification Timelines:CERT-In empanelment for incident response providers requires 18-24 month validation cycles that delay market entry for new entrants.
- Interoperability Complexity:SIEM integration with existing SOAR platforms demands custom API development that stretches deployment timelines for hybrid cloud environments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | India Ransomware Protection Market |
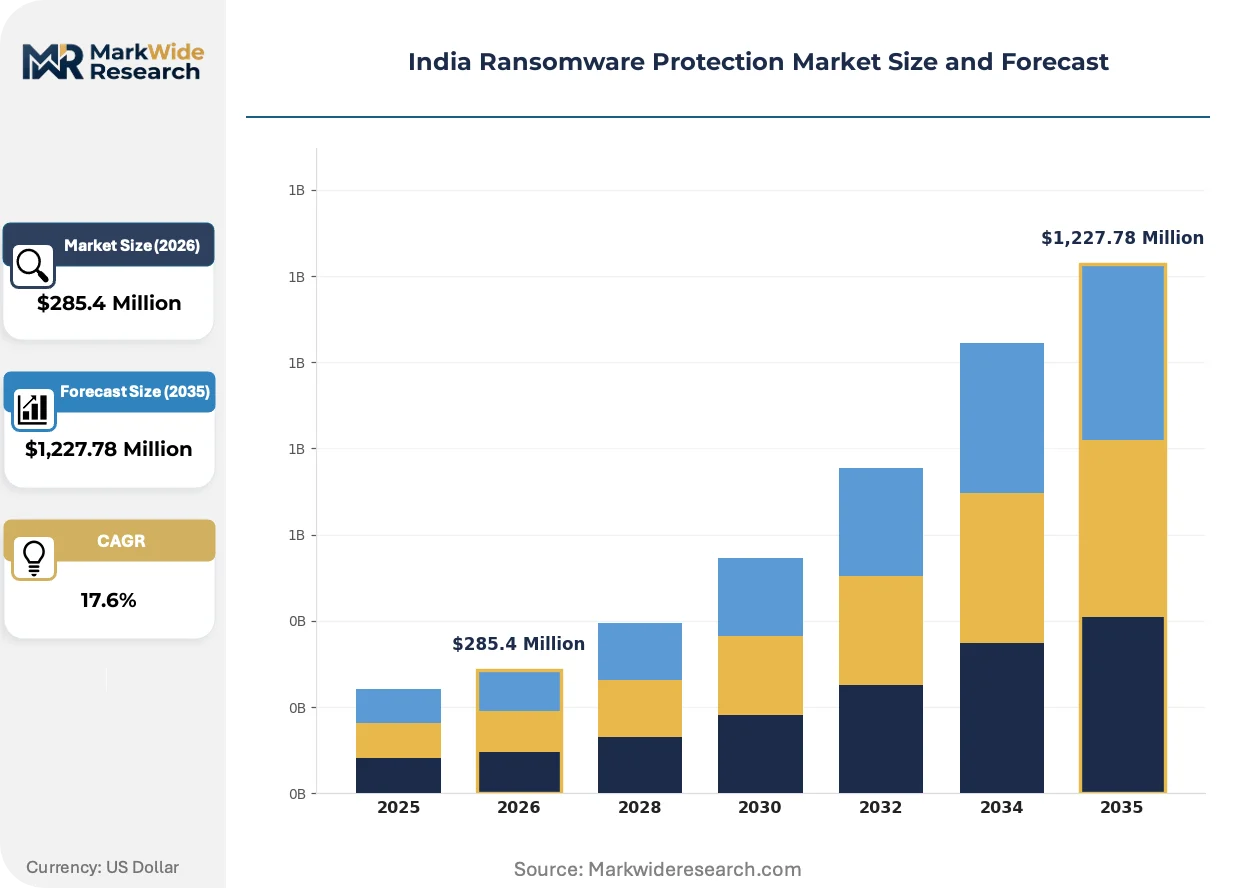
| Market Size in 2026 | $285.4 Million |
| Market Size in 2035 | $1,227.78 Million |
| CAGR (2026 – 2036) | 17.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Government, BFSI, Healthcare, Education Solution: Backup Solutions, Endpoint Protection, Encryption Services, Threat Intelligence Technology: AI-Based, Machine Learning, Behavioral Analysis, Signature-Based |
| Companies Covered | CrowdStrike, Palo Alto Networks, Fortinet, Cisco, Check Point Software, Sophos, SentinelOne, Microsoft, K7 Computing, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
India Ransomware Protection Market Trends and Innovations
Indian ransomware protection architectures are pivoting from perimeter defense to identity-centric resilience models, with deployment patterns splitting between sovereign data requirements and cloud-native agility demands.
Extended detection and response platforms are hybridizing endpoint telemetry with network flow analysis and identity threat signals into unified data lakes. Large BFSI institutions are piloting these consolidated stacks to reduce alert fatigue and consolidate vendor relationships. This convergence is compressing standalone EDR vendor margins while rewarding platform players with cross-sell expansion.
The Digital Personal Data Protection Act's breach notification requirements are compelling organizations to deploy automated forensic evidence collection before regulatory deadlines expire. Compliance teams are now co-approving security procurement alongside CISOs, shifting evaluation criteria toward audit-ready documentation. BFSI and healthcare verticals are most affected, with both sectors accelerating replacement of legacy logging systems.
Mid-market buyers are unbundling ransomware protection from bundled IT security contracts and selecting specialized vendors for backup recovery guarantees. Channel partners in Ahmedabad and Hyderabad are building managed service practices around these discrete recovery SLAs. This fragmentation is most visible among pharmaceutical manufacturers and educational institutions seeking operational continuity commitments distinct from detection capabilities.
India Ransomware Protection Market Segmentation
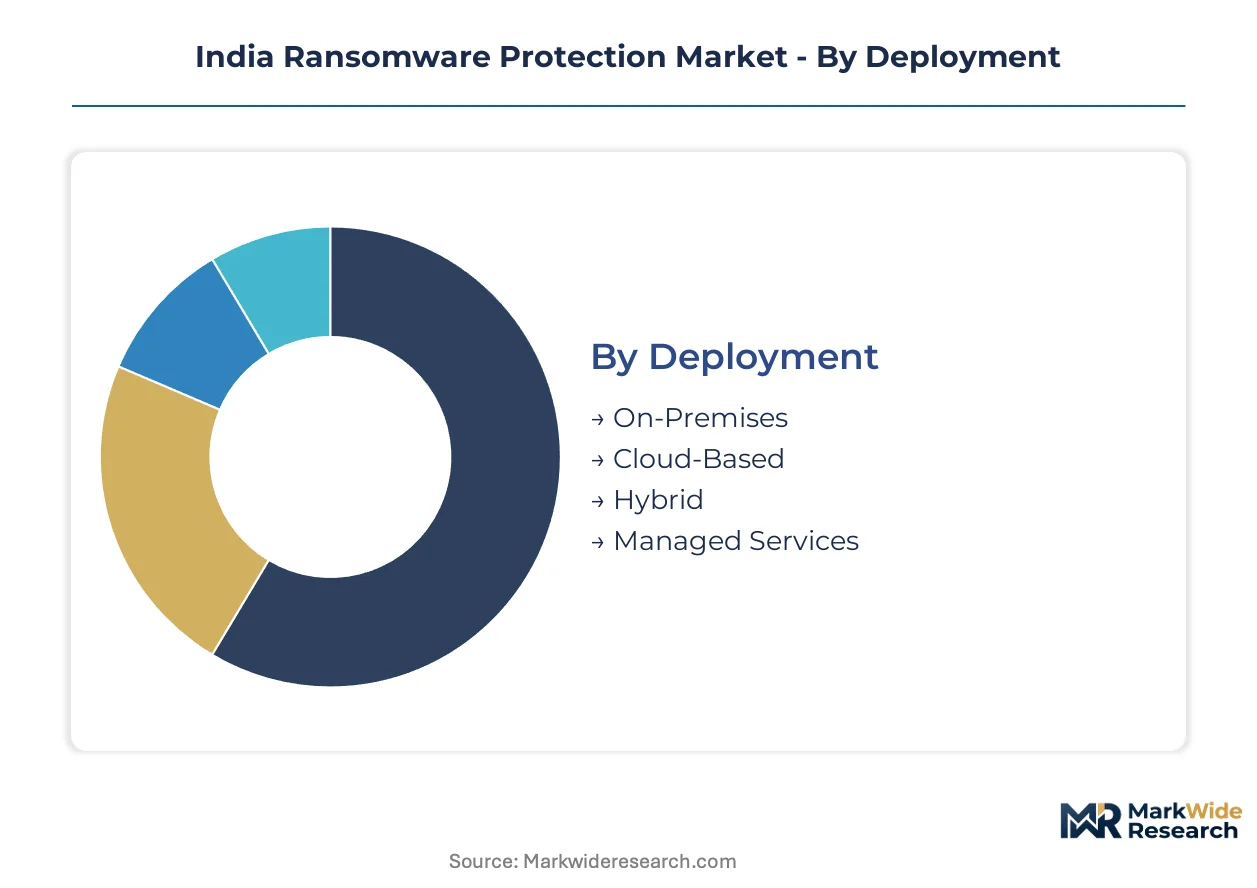
Segmentation in India's ransomware protection market reveals how procurement criteria diverge between compliance-driven BFSI institutions and cost-conscious mid-market buyers. Understanding these fault lines enables vendors to align pricing architectures with distinct technical requirements and deployment constraints across the country's heterogeneous enterprise base.
Deployment:
Cost tier differentiation shapes deployment preferences, with capital intensity thresholds separating sovereign data requirements from SaaS agility demands.
- On-Premises:Hardware appliances and localized software stacks processing sensitive data within organizational firewalls. Large BFSI institutions in Mumbai's Bandra-Kurla Complex mandate these configurations to satisfy RBI data localization directives and preserve forensic chain-of-custody.
- Cloud-Based:Agentless or lightweight agent architectures delivering protection through browser-accessible dashboards without infrastructure ownership. Mid-market pharmaceutical manufacturers in Hyderabad's Genome Valley are adopting these to bypass capital expenditure approval cycles.
- Hybrid:Split architectures retaining critical workloads on-premises while offloading telemetry processing to cloud analytics engines. This configuration dominates among Maharashtra-based enterprises navigating CERT-In's six-hour reporting mandate.
- Managed Services:Outsourced security operations where vendors assume full responsibility for threat detection, incident response, and compliance documentation. Tier-2 city hospitals in Kochi and Jaipur favor these to compensate for internal SOC analyst shortages.
On-Premises holds installed capacity. Cloud-Based is rotating up the share rankings.
End User:
Application-specific risk profiles drive divergent procurement patterns, with regulatory exposure determining budget allocation intensity.
- BFSI:Banks, insurance carriers, and payment processors facing UPI transaction surge exposure and RBI cybersecurity framework obligations. These institutions command premium pricing for solutions with demonstrable forensic certification and automated breach notification workflows.
- Government:Central ministries, state departments, and public sector undertakings bound by CERT-In directives and BIS critical infrastructure standards. Procurement cycles here stretch 18-24 months through empanelment requirements.
- Healthcare:Hospital networks, diagnostic chains, and telemedicine platforms managing patient records under DPDP Act breach notification penalties. This vertical is accelerating replacement of legacy logging systems with automated evidence collection.
- Education:Universities, research institutions, and K-12 technology adopters with dispersed endpoint populations and limited security staffing. Channel partners in Ahmedabad are building managed service practices around discrete recovery SLAs for this segment.
BFSI commands pricing premiums. Healthcare is climbing the fastest as DPDP enforcement tightens.
Solution:
Customer type sophistication determines solution bundling preferences, with enterprise buyers unbundling detection from recovery capabilities.
- Endpoint Protection:Agent-based or agentless software monitoring workstations, servers, and mobile devices for ransomware execution indicators. Large institutions are consolidating standalone EDR vendors into extended detection and response platforms.
- Backup Solutions:Immutable storage architectures with air-gapped recovery capabilities engineered to restore operational continuity without attacker payment. Mid-market buyers in Coimbatore's manufacturing belt unbundle these from bundled IT security contracts.
- Threat Intelligence:Feeds of Indications of Compromise and attacker infrastructure patterns enabling proactive threat hunting. Domestic vendors compete here through India-specific signature development.
- Encryption Services:Data-at-rest and data-in-transit cryptographic protection preventing unauthorized access even during successful breaches. Demand concentrates among healthcare providers managing DPDP-covered personal data.
Endpoint Protection anchors enterprise deployments. Backup Solutions is expanding most quickly among mid-market continuity planners.
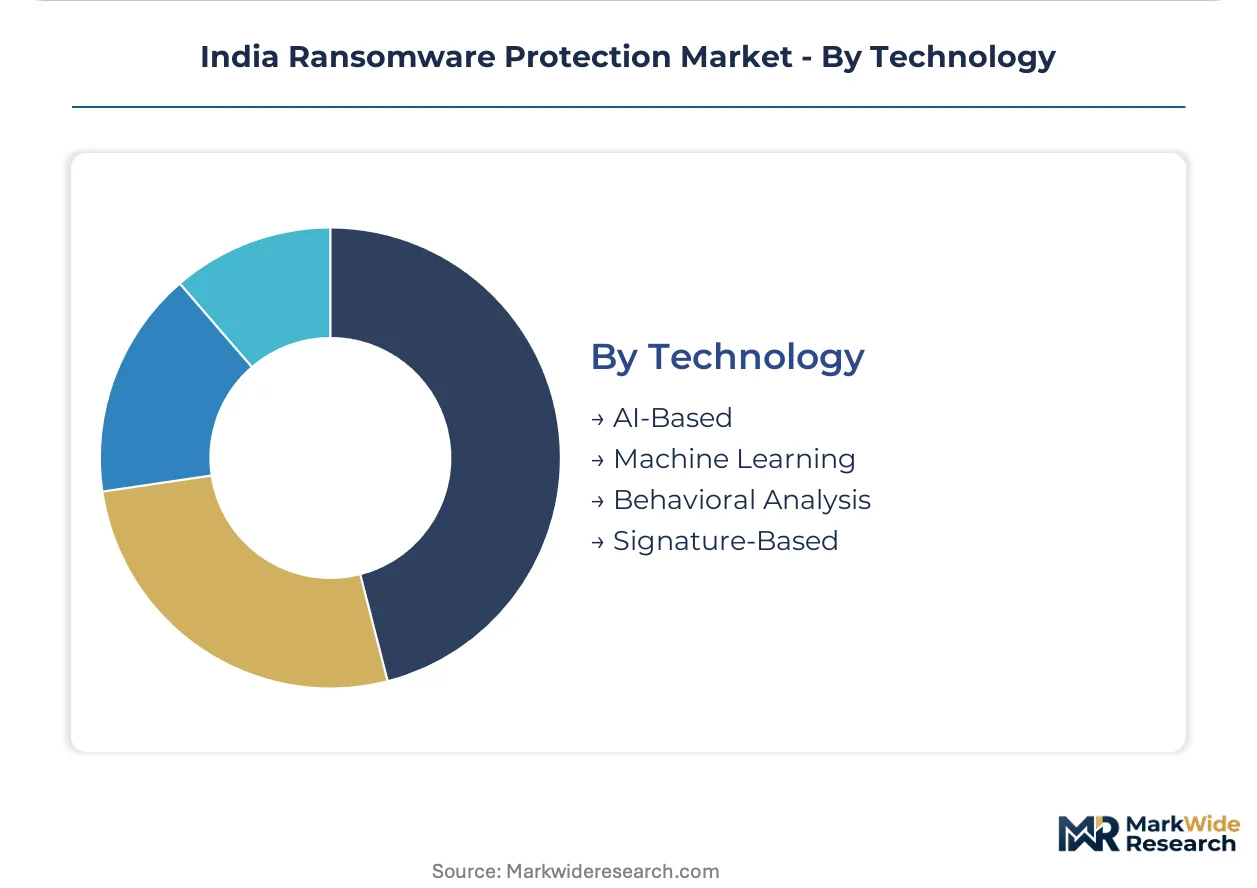
Technology:
Maturity gradients separate legacy detection architectures from behavioral models displacing signature-dependent approaches.
- AI-Based:Neural network architectures trained on ransomware behavioral patterns to identify novel variants without prior signature exposure. BFSI pilot programs are validating these against regulatory audit requirements.
- Behavioral Analysis:Rule engines and statistical models detecting anomalous process execution, file system modifications, and network lateral movement. These supersede signature detection in enterprise procurement evaluations.
- Machine Learning:Supervised and unsupervised algorithms classifying endpoint telemetry into threat severity tiers. GPU hardware requirements for on-premises inference face import duty volatility.
- Signature-Based:Pattern-matching engines comparing file hashes and code sequences against known ransomware databases. Legacy infrastructure in state-owned banks retains these for compatibility with unpatched Windows 7 stacks.
Signature-Based retains legacy footprint. AI-Based is gaining share fastest as CERT-In mandates compress response windows.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Demand elasticity varies sharply across Indian states. BFSI-heavy metros absorb premium pricing for hybrid architectures, while tier-2 manufacturing belts prioritize cost-efficient SaaS delivery over sovereign data controls.
Maharashtra
Mumbai's Bandra-Kurla Complex houses the densest concentration of banking headquarters requiring RBI-mandated data localization. CERT-In's six-hour reporting window compresses procurement cycles for threat-hunting platforms across Pune's software parks. The Mumbai-Pune corridor anchors hybrid deployment demand as enterprises balance cloud agility with forensic chain-of-custody requirements.
Karnataka
Bengaluru's fintech startup density and UPI transaction surge expand endpoint attack surfaces for real-time monitoring investments. The state's IT department enforces BIS cybersecurity standards for government data centers. Whitefield and Electronic City clusters drive cloud-native agent adoption among mid-market SaaS exporters seeking capital expenditure avoidance.
Telangana
Hyderabad's Genome Valley pharmaceutical manufacturers unbundle backup recovery SLAs from bundled IT security contracts. The Telangana State Innovation Cell promotes cyber resilience grants for life sciences exporters facing DPDP Act breach notification penalties. Cyberabad's data center expansion attracts managed detection and response providers targeting SOC analyst shortages.
Gujarat
Ahmedabad's diamond trading houses and chemical processors exhibit acute price sensitivity favoring channel-delivered managed services. The Gujarat International Finance Tec-City regulatory sandbox experiments with zero-trust network segmentation for commodity trading platforms. Surat's textile automation clusters remain underpenetrated relative to Mumbai-tier protection deployment.
Tamil Nadu
Coimbatore's precision manufacturing belt and Chennai's automotive electronics hubs face ransomware targeting operational technology-IT convergence. The Tamil Nadu Cyber Security Policy mandates critical infrastructure reporting to the state CERT. Sriperumbudur's electronics manufacturing zones drive air-gapped backup demand for semiconductor fabrication continuity guarantees.
India Ransomware Protection Market Competitive Landscape
Capability concentration sits with global platform vendors; scale advantage sits with domestic channel specialists. The vendor base stratifies into three tiers: multinational security platforms with integrated XDR stacks, regional specialists with India-specific threat intelligence, and channel-centric providers with localized support density. Consolidation pressure intensifies as BFSI procurement committees favor unified platforms over point solutions. Dominant competitive moves include strategic partnerships with domestic system integrators and portfolio expansion into managed detection and response services.
Within the global platform tier, Palo Alto Networks and CrowdStrike occupy positions anchoring enterprise banking accounts through cloud-native specialization. K7 Computing exemplifies the domestic mid-market archetype with localized signature development and state-level channel penetration. These three vendors illustrate the competitive tension between scale-driven platform consolidation and geography-specific threat responsiveness.
| Leading Market Players |
|---|
| CrowdStrike |
| Palo Alto Networks |
| Fortinet |
| Cisco |
| Check Point Software |
| Sophos |
| SentinelOne |
| Microsoft |
| K7 Computing |
| Others |
Pricing and Supply Chain Analysis
GPU fabrication concentration in Taiwan and South Korea feeds directly into margin pools for on-premises AI inference engines serving Maharashtra's BFSI institutions. Import duty volatility on specialized hardware reshapes procurement trade-offs between capital-intensive sovereign deployments and SaaS-delivered alternatives.
Pricing Analysis
Managed detection and response contracts now generate lifetime value exceeding pure software licensing through continuous monitoring revenue streams. Three-tier pricing structure across premium, standard, and economy levels separates BFSI institutions demanding forensic certification from mid-market buyers prioritizing operational continuity guarantees. Cost compression in cloud-native tiers is intensifying because hyperscaler infrastructure commoditizes telemetry processing. State-owned banks exhibit acute price sensitivity due to legacy integration burdens, while private sector BFSI commands premium positioning for hybrid architectures preserving data sovereignty.
Supply Chain Analysis
US export controls on advanced GPU and AI accelerator technologies constrain hardware availability for on-premises behavioral analysis engines. Supply chains for endpoint protection hardware draw from Taiwan, South Korea, and China for semiconductor components, with specialized storage arrays sourced from Japan and Germany. Single-source vulnerability concentrates in GPU supply for machine learning inference. Distribution runs through domestic system integrators with CERT-In empanelment and channel partners building managed service practices in Ahmedabad and Hyderabad.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Managed security service contracts represent the fastest-expanding recurring-revenue layer as continuous monitoring displaces perpetual licensing. Hardware-centric vendors must attach service capabilities to capture margin migration toward operational expenditure models.
For Market Incumbents: Harden platform consolidation around extended detection and response stacks to counter standalone EDR vendor margin compression. Deepen CERT-In empanelment investments to defend against 18-24 month validation delays threatening competitive positioning. Acquire domestic threat intelligence specialists to anchor India-specific signature development against regional ransomware variant velocity.
For New Entrants and Emerging Players: Tier-2 city manufacturing belts in Coimbatore and Vadodara represent the most penetrable entry point given underpenetrated ransomware protection relative to Mumbai-Pune data center density. Channel-delivered managed services with discrete recovery SLAs bypass direct enterprise sales friction. Partner with state-level system integrators possessing existing BIS critical infrastructure certification relationships.
For Investors and Strategic Acquirers: Secondary-cycle assets sit with PE-backed domestic mid-market specialists holding localized channel density but lacking platform breadth. Long-term viability hinges on convergence toward unified XDR architectures displacing point solutions. Watch for DPDP Act enforcement acceleration as inflection indicator compressing replacement cycles for legacy logging systems.
| Strategic Initiative | Industry Significance |
|---|---|
| Managed Detection and Response Service Launch | Captures recurring revenue migration from perpetual licensing in BFSI procurement cycles. |
| CERT-In Empanelment Investment | Validates forensic response capabilities required for six-hour incident reporting mandates. |
| Domestic Threat Intelligence Acquisition | Accelerates India-specific signature velocity against regional ransomware variant evolution. |
| Tier-2 City Channel Expansion | Penetrates underexposed manufacturing belts in Coimbatore and Vadodara through partner density. |
| Zero Trust Platform Integration | Converges network segmentation with identity-aware controls beyond point endpoint solutions. |
Research Methodology
Desk research of CERT-In directive filings, BIS cybersecurity standards documentation, and RBI cybersecurity framework circulars preceded structured interviews with CISOs at BFSI institutions, SOC operations directors, channel partner principals, and managed security service providers. Primary fieldwork validated deployment preference shifts across on-premises, cloud-native, and hybrid architectures. Secondary sources included vendor SEC filings, hyperscaler capex disclosures, and customs data on GPU import volumes. Bottom-up endpoint installation estimates triangulated against top-down IT security spending allocations from enterprise budget disclosures.
Assumptions held CERT-In reporting mandates and DPDP Act enforcement intensity fixed across the analysis window, with UPI transaction growth and AI detection adoption varied through sensitivity bands. Segmentation modeling incorporated deployment model, end-user vertical, solution type, and technology maturity tier. CAGR derivation applied logistic diffusion curves for behavioral analysis adoption and linear extrapolation for backup solution growth. Industry-specific inputs included SOC analyst wage inflation and GPU import duty rate volatility.
Stress conditions across regulatory enforcement intensity, skilled labor availability, and hardware import restriction severity were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect these documented assumptions and risk factor calibrations. Material shifts in CERT-In empanelment timelines or DPDP penalty enforcement would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
Hong Kong Cybersecurity Market
Cybersecurity
Benelux Cybersecurity Market
Cybersecurity
Canada Cybersecurity Market
Cybersecurity
SOC As a Service Market
Cybersecurity
North America Software Defined Perimeter Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
United States Cybersecurity Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Content Delivery Network (CDN) Security Market
Cybersecurity
Web Filtering Market
Cybersecurity
Dark Web Intelligence Market