
 Global Healthcare IoT Security Market | 2026-2036
Global Healthcare IoT Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Healthcare IoT Security Market Analysis
The EU AI Act is rebalancing the cost-of-entry calculus for medical device vendors selling into European health systems by mandating conformity assessments for AI-enabled diagnostic tools. Cisco Systems leverages its networking heritage to anchor healthcare IoT security deployments across integrated delivery networks. IBM Corporation competes through Watson Health's specialized threat intelligence services for clinical environments. Fortinet sustains its position with consolidated security fabric architectures that unify network and endpoint protection for hospital IT teams.
Healthcare IoT security encompasses the technologies, protocols, and governance frameworks that protect connected medical devices, patient data streams, and clinical network infrastructure from unauthorized access, manipulation, or disruption; core functional parameters include real-time anomaly detection with sub-100-millisecond response thresholds, end-to-end encryption for PHI transmission, and zero-trust segmentation isolating infusion pumps from electronic health record systems. The software segment dominates current spending as health systems prioritize agentless network detection and response platforms over hardware appliance refreshes. Services growth outpaces product sales as hospitals outsource security operations center staffing and medical device risk assessments to specialized vendors. Platform offerings are consolidating encryption, authentication, and intrusion detection modules into unified clinical security operations dashboards that reduce tool sprawl for resource-constrained biomedical engineering departments.
FDA cybersecurity guidance, the EU AI Act, and HIPAA Security Rule enforcement collectively elevate baseline security spending by treating legacy medical devices as persistent vulnerabilities requiring compensating network controls. Japan's PMDA has aligned its software-as-medical-device framework with international cybersecurity standards, creating export pathway clarity for vendors seeking multi-regional approval. Stakeholders must monitor how NIST's forthcoming healthcare sector cybersecurity framework update reconciles zero-trust mandates with the operational realities of life-sustaining device uptime requirements.
Market Dynamics
Ransomware attacks on hospital networks are compressing procurement cycles for zero-trust segmentation tools as health systems confront FDA cybersecurity guidance mandates for legacy device hardening.
Growth Catalysts
- FDA Cybersecurity Guidance:Post-market management requirements for connected devices are compelling hospitals to deploy compensating network controls for infusion pumps and patient monitors.
- EU AI Act Conformity Assessments:AI-enabled diagnostic tools now require documented risk management systems, creating sustained demand for validation services across European health systems.
- Agentless Network Detection:Biomedical engineering departments prioritize passive monitoring platforms that discover medical devices without endpoint software installation.
Market Restraints
- Legacy Device Obsolescence:Unpatchable Windows-embedded systems in MRI machines and CT scanners require expensive network isolation architectures.
- Specialized Talent Scarcity:Hospital IT departments face acute shortages of professionals cross-trained in clinical workflows and OT security protocols.
- Fragmented Vendor Ecosystem:Point solutions for medical device inventory, network segmentation, and threat detection create integration complexity and procurement paralysis.
Strategic Opportunities
- Japan PMDA Software-as-Medical-Device Framework:Aligned cybersecurity standards create export pathway clarity for vendors seeking multi-regional approval.
- Consolidated Security Fabric Architectures:Unified platforms integrating encryption, authentication, and intrusion detection reduce tool sprawl for resource-constrained hospitals.
- Outsourced Security Operations:Health systems are transferring SOC staffing and medical device risk assessments to specialized managed security providers.
Industry Challenges
- Sub-100-Millisecond Response Thresholds:Real-time anomaly detection for life-sustaining devices demands specialized edge computing infrastructure that strains hospital capex budgets.
- Zero-Trust Segmentation Complexity:Isolating infusion pumps from EHR systems while maintaining clinical workflow continuity requires extensive network reconfiguration.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Healthcare IoT Security Market |
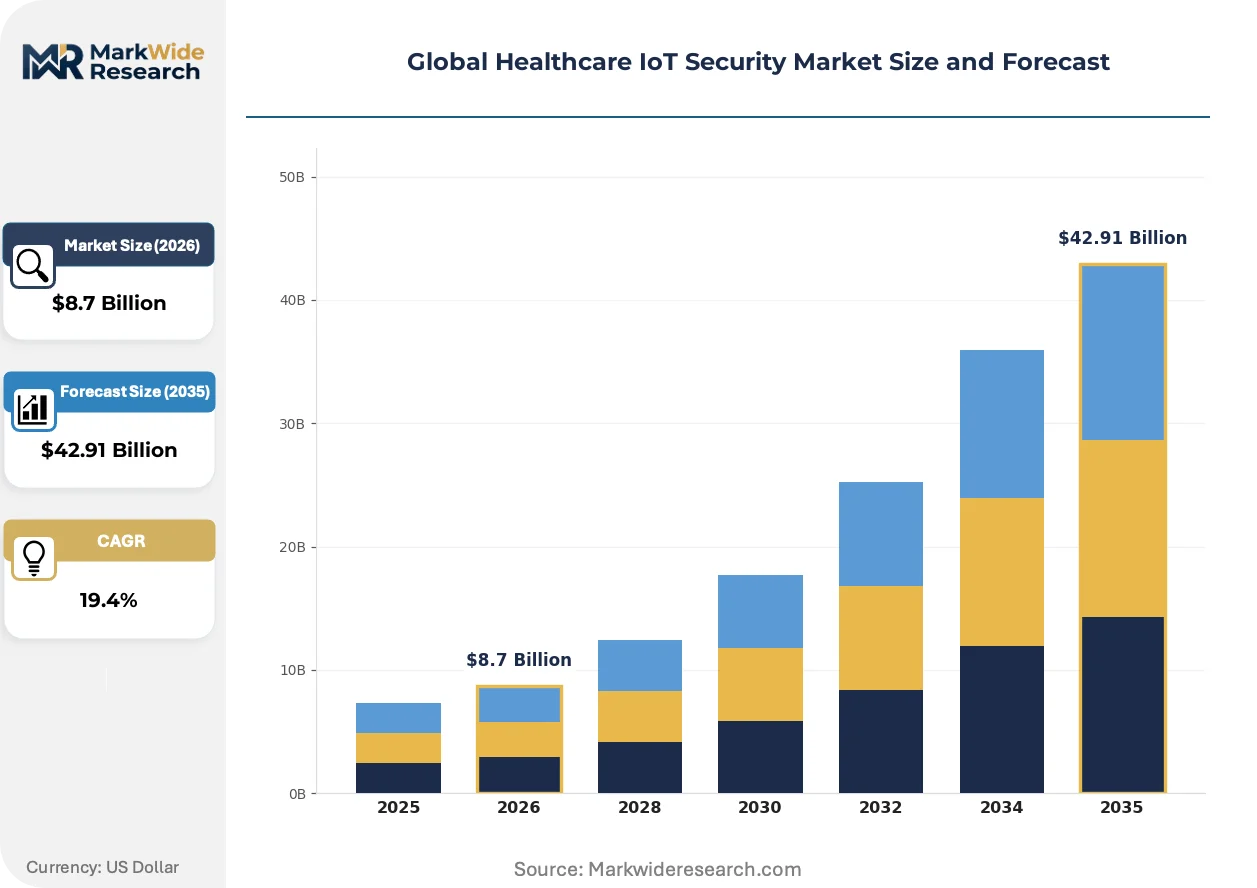
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $42.91 Billion |
| CAGR (2026 – 2036) | 19.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Software, Hardware, Services, Platform Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, On-premises End User: Hospitals, Clinics, Home Healthcare, Pharmaceutical Companies Technology: Encryption, Authentication, Intrusion Detection, Malware Protection |
| Companies Covered | Cisco Systems, IBM Corporation, Intel Corporation, Oracle Corporation, Microsoft Corporation, Fortinet, GE Healthcare, Deutsche Telekom AG, Inside Secure SA, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Healthcare IoT Security Market Emerging Trajectories
Clinical security operations dashboards are consolidating previously siloed functions as health systems confront device sprawl and regulatory documentation burdens.
Agentless network detection and response platforms are unifying device discovery, behavioral profiling, and threat containment without endpoint agents. Hospital IT teams are adopting these platforms at accelerated pace to avoid software conflicts with FDA-validated medical devices. This unification is compressing vendor consolidation timelines as standalone inventory tools lose procurement viability.
EU AI Act high-risk system requirements are mandating conformity assessments for AI-enabled diagnostic tools before European market entry. Device manufacturers must now document risk management systems and post-market monitoring protocols. Germany and France are seeing the earliest enforcement waves as notified bodies establish assessment capacity.
Hospital procurement committees are elevating biomedical engineering representation in security technology selection. Traditional IT-centric purchasing is yielding to cross-functional evaluation involving clinical engineering, compliance, and nursing leadership. United States integrated delivery networks are pioneering this governance shift to align security investments with patient safety priorities.
Global Healthcare IoT Security Market Segmentation
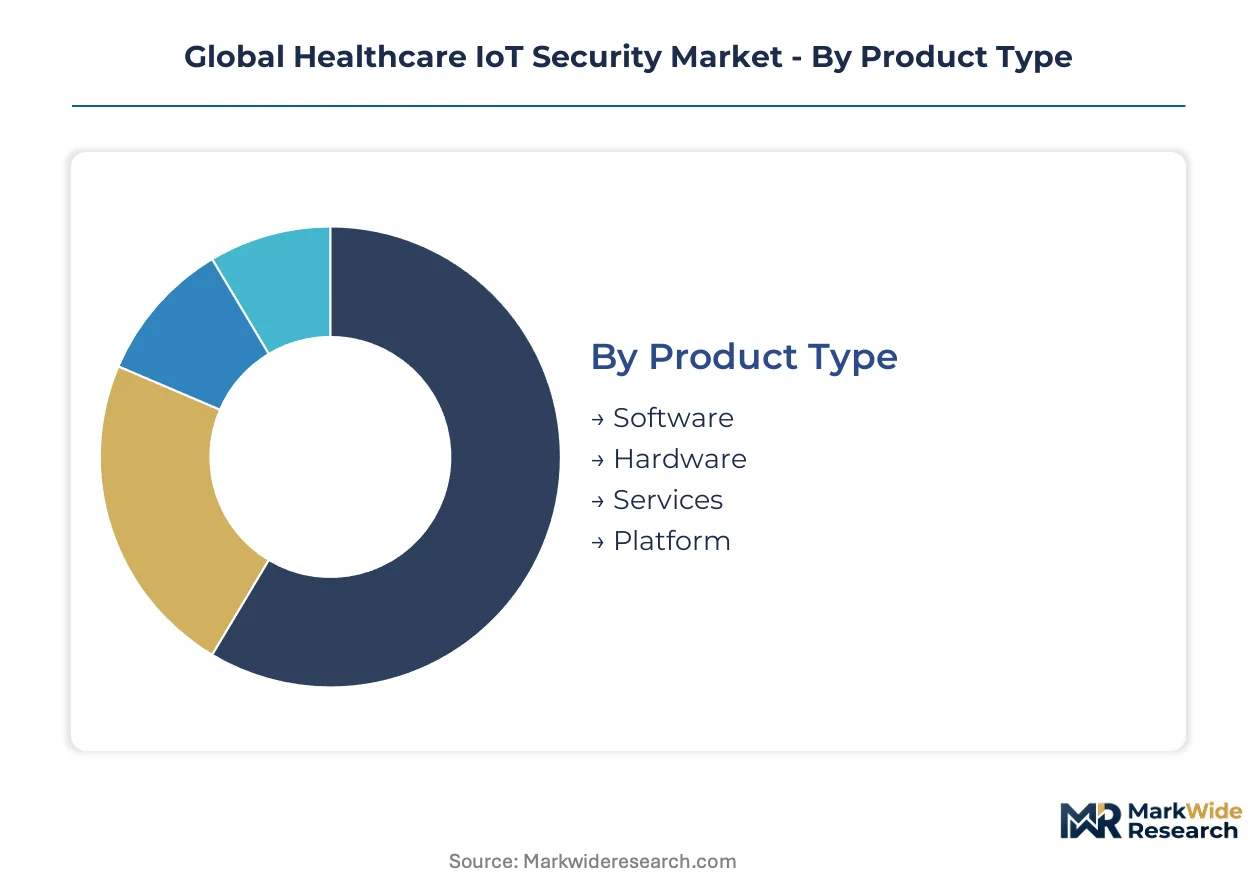
Healthcare IoT security procurement patterns diverge sharply across product architectures, cloud postures, and clinical settings. Understanding these fault lines reveals where security spending concentrates and which segments command pricing premiums.
Product Type:
Upgrade cycles vary by product category, with software refresh timelines compressing faster than hardware replacement schedules.
- Software:Agentless network detection platforms dominate current procurement as hospitals prioritize passive monitoring without endpoint installation conflicts. United States integrated delivery networks favor these tools for legacy device visibility. FDA cybersecurity guidance on post-market management accelerates replacement of signature-based systems.
- Services:Outsourced security operations center staffing and medical device risk assessments expand fastest as biomedical engineering departments face specialized talent scarcity. German hospital networks lead European adoption of managed detection and response contracts.
- Hardware:Dedicated encryption appliances and network segmentation gateways serve environments with strict data residency requirements.
- Platform:Consolidated clinical security operations dashboards unify previously siloed encryption, authentication, and intrusion detection modules.
Software sits at the top of the volume ranking, with Services climbing the fastest.
Deployment Model:
Cloud posture selection tracks directly to patient data sovereignty requirements and clinical workflow latency tolerances.
- Hybrid Cloud:Architectures splitting sensitive PHI processing on-premises while leveraging cloud analytics for threat intelligence gain traction among multi-site United States health systems. Japan's PMDA software-as-medical-device framework provides regulatory clarity for hybrid deployments spanning domestic and international data centers.
- Private Cloud:Single-tenant environments satisfy German hospital requirements under GDPR and national healthcare data protection laws.
- Public Cloud:Shared infrastructure appeals to smaller clinics with limited IT staffing for security operations.
- On-premises:Air-gapped deployments persist for military medical facilities and critical infrastructure-designated hospitals.
Hybrid Cloud captures the largest deployment share, with Private Cloud expanding most quickly among European compliance-sensitive buyers.
End User:
Customer type determines solution complexity thresholds and procurement committee composition.
- Hospitals:Acute care facilities deploy the most comprehensive security fabrics, integrating network segmentation with electronic health record isolation. United States integrated delivery networks with 10+ facilities standardize on unified platforms to reduce tool sprawl across biomedical engineering teams.
- Home Healthcare:Remote patient monitoring devices drive demand for lightweight encryption and over-the-air update capabilities. Japanese insurers now mandate minimum security baselines for reimbursed connected devices.
- Clinics:Ambulatory settings prioritize cost-constrained solutions with simplified deployment.
- Pharmaceutical Companies:Clinical trial data protection and manufacturing OT security create specialized requirements distinct from provider settings.
Hospitals anchor the end-user hierarchy, with Home Healthcare gaining share fastest on remote care expansion.
Technology:
Technology selection prioritizes real-time response capabilities for life-sustaining device protection.
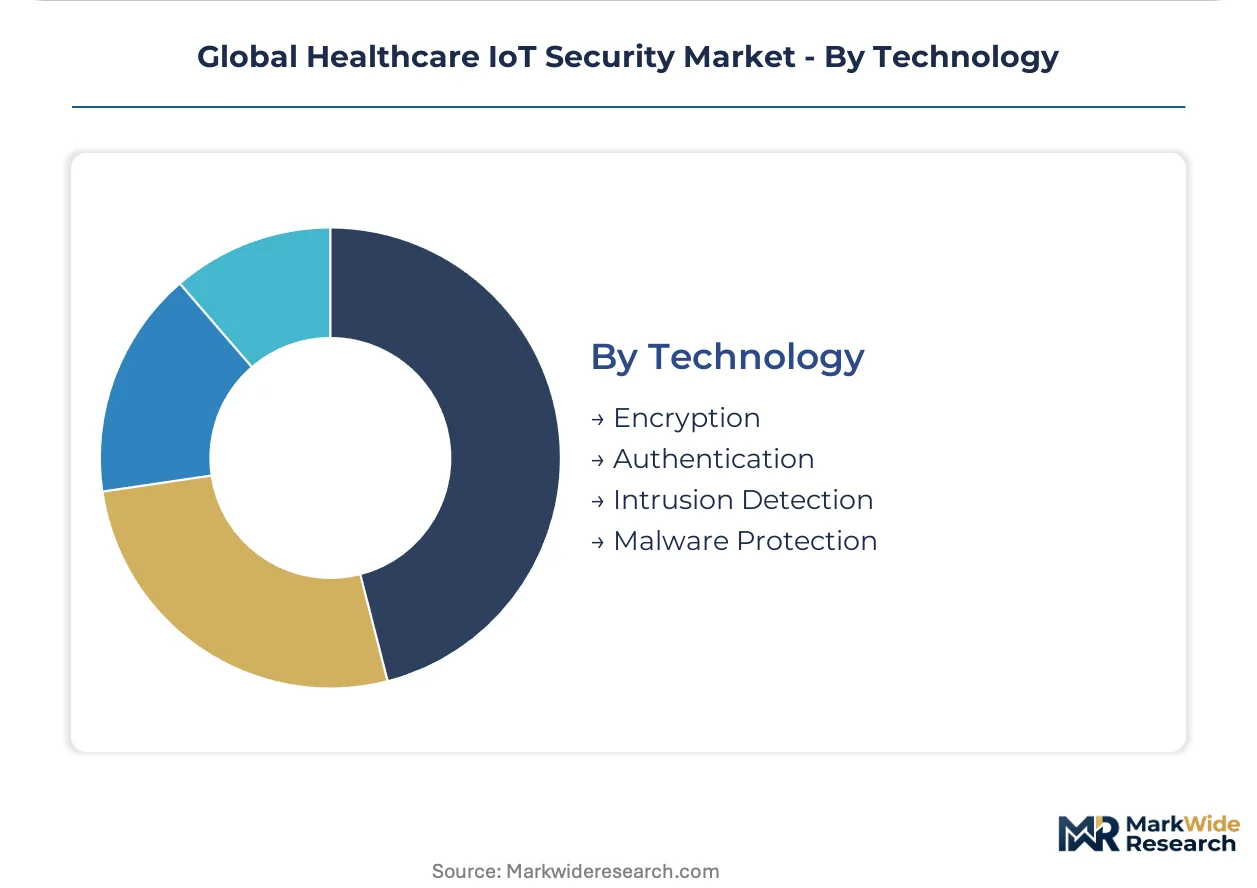
- Encryption:End-to-end PHI transmission protection with FIPS 140-2 validation serves as the baseline procurement requirement. German health systems enforce additional national cryptographic standards for cross-border data flows.
- Intrusion Detection:Behavioral analytics platforms achieving sub-100-millisecond anomaly response command premium positioning. United States trauma centers prioritize these capabilities for infusion pump networks.
- Authentication:Multi-factor and certificate-based identity verification for clinical staff and device-to-device communication.
- Malware Protection:Specialized threat signatures for medical device operating systems and embedded controllers.
Encryption holds the highest technology penetration, with Intrusion Detection showing the steepest expansion trajectory on ransomware defense urgency.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The United States pioneered large-scale hospital network digitization during the 2000s HITECH Act implementation, establishing the regulatory and technical foundations that European and Asian health systems later adapted for their own connected medical device deployments.
United States
Integrated delivery networks with 10-plus facilities drive concentrated demand for unified security fabrics that reduce biomedical engineering tool sprawl. FDA cybersecurity guidance on post-market management for connected devices compels hospitals to deploy compensating network controls for legacy infusion pumps and patient monitors. The Boston-Cambridge corridor anchors specialized managed security providers serving academic medical centers with advanced threat intelligence requirements.
Germany
University hospital networks prioritize private cloud deployments satisfying GDPR and national healthcare data protection law requirements for patient data sovereignty. The EU AI Act conformity assessment mandates for AI-enabled diagnostic tools create sustained validation service demand across German health systems. The Rhine-Ruhr metropolitan region concentrates medical device cybersecurity consulting firms serving both domestic hospitals and cross-border European clients.
Japan
Insurer-mandated security baselines for reimbursed connected home healthcare devices accelerate lightweight encryption and over-the-air update capability procurement. PMDA alignment of its software-as-medical-device framework with international cybersecurity standards creates export pathway clarity for domestic vendors seeking multi-regional approval. The Tokyo-Osaka corridor hosts specialized security operations centers serving both domestic health systems and regional expansion into Southeast Asian markets.
United Kingdom
NHS integrated care systems consolidate procurement for zero-trust segmentation tools across formerly autonomous hospital trusts facing unified ransomware defense mandates. National Health Service Digital cybersecurity standards for connected medical devices elevate baseline network hardening requirements throughout English health systems. The Cambridge-London health tech cluster concentrates vendors developing agentless detection platforms specifically for legacy device environments.
India
Private hospital chains in metropolitan centers deploy hybrid cloud security architectures splitting PHI processing on-premises while leveraging cloud analytics for threat intelligence. CDSCO draft guidance on cybersecurity for connected medical devices signals impending regulatory alignment with FDA and EU frameworks. The Bengaluru-Hyderabad corridor anchors domestic security software development targeting cost-constrained clinic and mid-tier hospital segments.
Global Healthcare IoT Security Market Vendor Landscape
The competitive structure tilts toward diversified technology conglomerates with established healthcare verticals rather than pure-play cybersecurity specialists. Network infrastructure heritage and enterprise software platforms provide incumbents with pre-existing hospital relationships and integration credibility that specialized entrants struggle to replicate. Two strategic archetypes dominate: networking vendors extending security fabric architectures into clinical environments, and enterprise software providers layering healthcare-specific threat intelligence atop general-purpose platforms. Competitive moves concentrate on portfolio consolidation through targeted acquisitions of medical device inventory and risk assessment specialists, plus strategic partnerships with biomedical engineering service firms to embed security operations within clinical workflow teams.
Among diversified technology conglomerates, Cisco Systems, IBM Corporation, and Fortinet occupy distinct positioning vectors within hospital procurement committees. Cisco Systems exemplifies the network-centric archetype, leveraging routing and switching heritage to anchor integrated delivery network deployments. IBM Corporation represents the enterprise software pathway, with Watson Health branding signaling specialized clinical environment expertise. Fortinet sits within the consolidated security fabric tier, unifying network and endpoint protection modules to reduce tool sprawl for resource-constrained hospital IT departments. Each anchors a distinct procurement evaluation criteria set: infrastructure integration, artificial intelligence-enabled analytics, or unified platform consolidation.
| Leading Market Players |
|---|
| Cisco Systems |
| IBM Corporation |
| Intel Corporation |
| Oracle Corporation |
| Microsoft Corporation |
| Fortinet |
| GE Healthcare |
| Deutsche Telekom AG |
| Inside Secure SA |
| Others |
Supply Flow & Price Mechanics
Specialized cybersecurity talent compensation in the United States and Germany cascades through subscription pricing tiers for healthcare IoT security platforms, compressing margins for vendors serving mid-tier hospital networks while sustaining premium positioning for academic medical center deployments.
Pricing Analysis
Subscription-based SaaS tiers with annual recurring revenue models dominate healthcare IoT security procurement, separating enterprise-grade agentless detection platforms from mid-market network monitoring bundles. Price differentiation rests on FDA cybersecurity validation tier and real-time response latency guarantees, with sub-100-millisecond anomaly detection commanding substantial premiums. Pricing pressure stems from open-source network detection tools encroaching on lower-tier clinic segments. United States integrated delivery networks show least price sensitivity due to bundled GPO contracting, while independent rural hospitals face acute budget constraints.
Supply Chain Analysis
Freight costs for hardware encryption appliances and network segmentation gateways from manufacturing centers in Taiwan, South Korea, and China inflate landed costs for European and North American hospital procurement committees. Semiconductor components for edge computing nodes and specialized cryptographic processors draw from concentrated foundry capacity in Taiwan and South Korea. Single-source vulnerability in advanced FPGA supply creates exposure for intrusion detection hardware vendors. Distribution runs through authorized medical device distributors with FDA establishment registration, bypassing generic IT channel partners.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Healthcare IoT security vendors can exploit geographic arbitrage between United States talent costs and Eastern European security operations center staffing, capturing margin expansion while maintaining HIPAA-compliant data handling.
For Market Incumbents: Anchor platform consolidation strategies through targeted acquisition of medical device inventory specialists and biomedical engineering service firms. Cisco Systems and Fortinet face substitution threat from cloud-native entrants offering API-first security fabrics. Priority lever: deepen backward integration into clinical workflow analytics to embed threat detection within nursing station dashboards. For New Entrants and Emerging Players: Rural United States critical access hospitals represent an underserved buyer archetype with unmet demand for lightweight, agentless monitoring solutions. Home healthcare device manufacturers in Japan offer secondary penetration vector through insurer-mandated security baselines. Go-to-market angle: partner with regional health information exchanges for co-branded security assessments. For Investors and Strategic Acquirers: Consolidation pressure builds where standalone medical device inventory tools lose procurement viability to unified clinical security operations platforms. Five-to-ten-year viability favors vendors with FDA cybersecurity guidance validation and EU AI Act conformity assessment capabilities. Acquisition target archetype: agentless network detection specialists with behavioral analytics IP. Signal to watch: hospital procurement committee elevation of biomedical engineering representation in security technology selection.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Consolidation | Unifies encryption, authentication, and intrusion detection modules to reduce tool sprawl for resource-constrained hospital IT departments. |
| FDA Cybersecurity Validation | Accelerates hospital procurement cycles by satisfying post-market management requirements for connected infusion pumps and patient monitors. |
| EU AI Act Conformity Assessment | Creates sustained validation service demand across German and French health systems for AI-enabled diagnostic tools. |
| Biomedical Engineering Partnership | Embeds security operations within clinical workflow teams to align threat response with patient safety priorities. |
| Hybrid Cloud Architecture | Splits sensitive PHI processing on-premises while leveraging cloud analytics for threat intelligence across multi-site United States health systems. |
Methodological Framework
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with hospital CISOs, biomedical engineering directors, GPO contracts managers, and medical device cybersecurity consultants with secondary validation against FDA guidance documents, EU AI Act implementing acts, hospital procurement databases, and CMS Medicare reimbursement filings. Bottom-up segmentation modeling and top-down market sizing triangulated demand estimates.
Segment-weighting approaches applied differential growth assumptions across software, services, hardware, and platform product categories, with deployment model splits across hybrid cloud, private cloud, public cloud, and on-premises architectures. End-user segmentation distinguished hospitals, home healthcare, clinics, and pharmaceutical companies. CAGRs derived from regression analysis against healthcare IT spending elasticity and regulatory enforcement intensity metrics, incorporating ransomware incident frequency and medical device recall data as industry-specific forecast inputs.
Inputs from hospital procurement databases and GPO contract repositories were available through the study window; gaps in real-time pricing transparency for managed security service contracts introduce uncertainty bands around services segment estimates. Forecasts reflect documented assumptions regarding FDA cybersecurity guidance enforcement timelines and EU AI Act notified body capacity expansion. Stakeholders should weight assumptions against their own operating context.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
DNS Firewall Market
Cybersecurity
Digital Security Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
Enterprise Network Firewall Market
Cybersecurity
North America Cyber Security Market
Cybersecurity
Global Sensitive Data Discovery Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Thailand Cybersecurity Market
Cybersecurity
Global Digital Forensic Laboratory As a Service Market
Cybersecurity
Cyber Security in Energy Market
Cybersecurity
5G Security Market
Cybersecurity
Qatar Cybersecurity Market
Cybersecurity
Taiwan Cybersecurity Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Cognitive Security Market