
 Firewall-As-A-Service (Fwaas) Market | 2026-2036
Firewall-As-A-Service (Fwaas) Market Size, Share, and Industry Trends Forecast 2026-2036
Firewall-As-A-Service (Fwaas) Market Insights
Software-defined perimeter architectures are decoupling firewall functionality from dedicated hardware appliances, collapsing capital expenditure models into subscription economics. Palo Alto Networks leverages its Prisma Access platform to anchor enterprise-grade cloud firewall deployments across distributed workforces. Fortinet sustains competitive pressure through integrated SD-WAN and FWaaS bundles that reduce vendor sprawl for mid-market buyers. Zscaler dominates proxy-based cloud security lanes, competing directly with traditional firewall vendors by intercepting traffic closer to the user endpoint.
Firewall-as-a-Service delivers network security policy enforcement through cloud-hosted infrastructure, inspecting traffic flows via distributed points of presence rather than on-premises appliances. The architecture scales throughput elastically while maintaining stateful packet inspection, application-layer filtering, and intrusion prevention across hybrid IT estates. Public cloud deployments absorb the majority of new subscription volume as organizations consolidate security stacks around AWS, Azure, and Google Cloud native integrations. Multi-cloud configurations represent the fastest-expanding deployment model, though on-premises retention persists in regulated verticals where data sovereignty requirements constrain full cloud migration. Managed firewall services capture disproportionate margin pools by bundling 24/7 security operations center oversight with policy tuning and threat response.
NIST zero-trust architecture guidance shapes federal procurement specifications, while FedRAMP authorization gates vendor participation in US government cloud contracts. The SEC's cybersecurity disclosure rules for publicly traded companies accelerate board-level investment in demonstrable network security controls. Stakeholders must monitor evolving encryption standards and quantum-resistant algorithm timelines to ensure long-term traffic inspection viability without performance degradation.
Market Dynamics
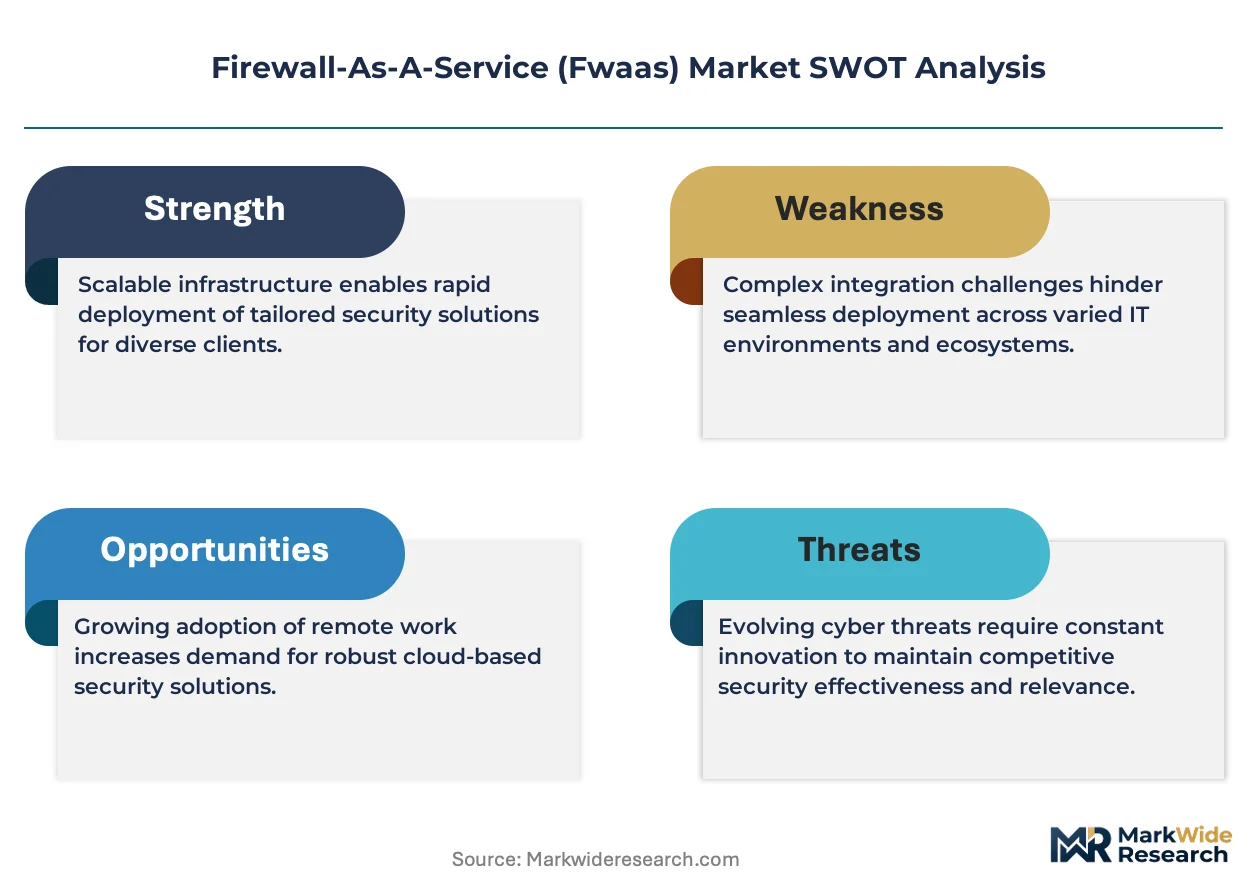
Cloud-first mandates from federal agencies and financial regulators are collapsing traditional perimeter security architectures into distributed, identity-centric enforcement models. This structural shift reconfigures procurement patterns away from capital-intensive appliance refresh cycles toward elastic, consumption-based security subscriptions.
Growth Catalysts
- Zero-trust architecture mandates:NIST SP 800-207 guidance and sector-specific directives from banking regulators in the United States are compelling enterprises to replace static network perimeters with dynamic, identity-aware access controls.
- Financial services cloud migration:Branch network consolidation and core banking platform modernization are driving tier-one banks to retire on-premises firewall appliances in favor of cloud-delivered policy enforcement.
- SD-WAN integration:The fusion of software-defined wide area networking with security service edge architectures is collapsing separate networking and security procurement decisions into unified vendor selections.
Market Restraints
- Data sovereignty constraints:European GDPR localization requirements and China's cybersecurity law mandate in-country data processing, fragmenting cloud firewall architectures and inflating operational complexity.
- Encryption visibility limitations:Widespread TLS 1.3 adoption and emerging post-quantum cryptography standards are degrading deep packet inspection capabilities without costly certificate management infrastructure.
- Skilled security operations scarcity:The shortage of cloud-native security architects and SecDevOps practitioners is elongating deployment timelines and forcing reliance on managed service intermediaries.
Strategic Opportunities
- Operational technology convergence:Manufacturing and critical infrastructure operators are extending cloud firewall policies to industrial control systems, creating demand for specialized protocol-aware inspection engines.
- India's digital public infrastructure:The country's cloud-first government initiatives and data center localization incentives are opening greenfield deployment opportunities for regionally compliant service providers.
- 5G network slicing security:Telecommunications carriers require granular, slice-isolated firewall policies for enterprise private networks, enabling premium service tiering beyond commodity internet protection.
Industry Challenges
- FedRAMP authorization timelines:The protracted certification process for cloud service providers seeking federal contract eligibility is compressing vendor revenue recognition and inflating compliance engineering costs.
- Multi-cloud policy orchestration:Enterprises operating across AWS, Azure, and Google Cloud environments face inconsistent native firewall APIs, forcing expensive abstraction layer development or vendor lock-in acceptance.
- Threat intelligence integration latency:Real-time indicator-of-compromise sharing between cloud firewall platforms and endpoint detection systems remains technically fragmented, creating exploitable detection gaps.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Firewall-As-A-Service (Fwaas) Market |
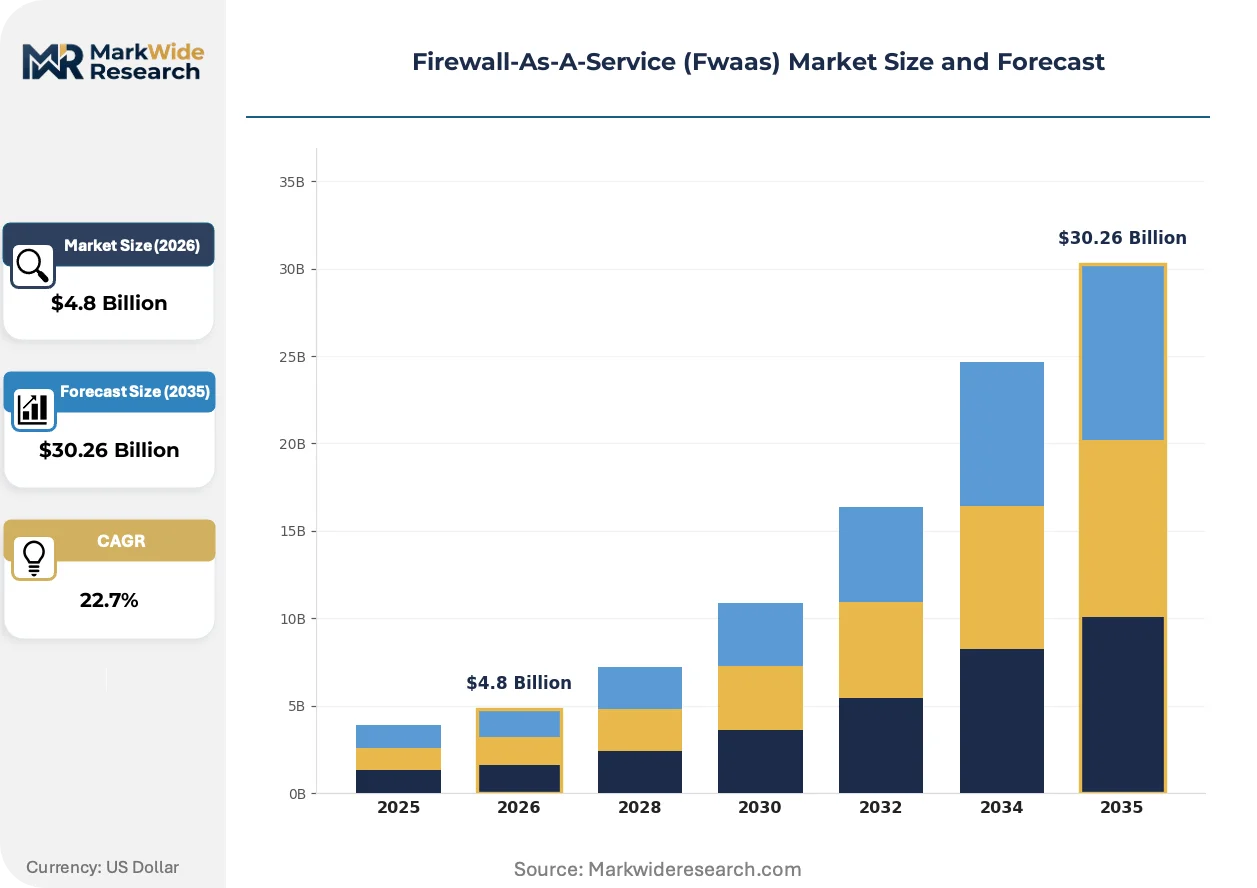
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $30.26 Billion |
| CAGR (2026 – 2036) | 22.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Firewall, Intelligent Firewall, Cloud Firewall, Hybrid Firewall Deployment Model: Public Cloud, Private Cloud, Multi-Cloud, On-Premises End User: SMEs, Large Enterprises, Government, Educational Institutions Compliance Standard: GDPR, HIPAA, PCI-DSS, ISO 27001 |
| Companies Covered | Palo Alto Networks, Fortinet, Cisco Systems, Zscaler, Check Point Software Technologies, Barracuda Networks, Cato Networks, Cloudflare, Juniper Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Firewall-As-A-Service (Fwaas) Market Trends and Innovations
Distributed workforce permanence and edge computing proliferation are dissolving traditional network boundaries, forcing security architectures to embed policy enforcement directly into user sessions and application workloads rather than infrastructure chokepoints.
Secure access service edge frameworks are converging with zero-trust network access to unify remote user protection and branch security under single-vendor consoles. Mid-market enterprises with limited security operations staff are adopting these consolidated platforms fastest, compressing the addressable market for standalone firewall vendors and privileging providers with broad cloud-native portfolios.
European NIS2 Directive implementation is mandating incident reporting timelines and supply chain security attestations for critical infrastructure operators. The regulation is accelerating procurement of managed detection and response capabilities bundled with cloud firewall services, particularly among energy and transport sector operators in Germany and France who face the earliest compliance deadlines.
Consumption-based pricing models are displacing per-seat or per-site licensing as the dominant commercial structure. Enterprise buyers in the United States are negotiating throughput-tiered subscriptions aligned with cloud egress volumes rather than user counts, while managed service providers in the United Kingdom are unbundling professional services from platform fees to compete on operational efficiency metrics.
Firewall-As-A-Service (Fwaas) Market Segmentation
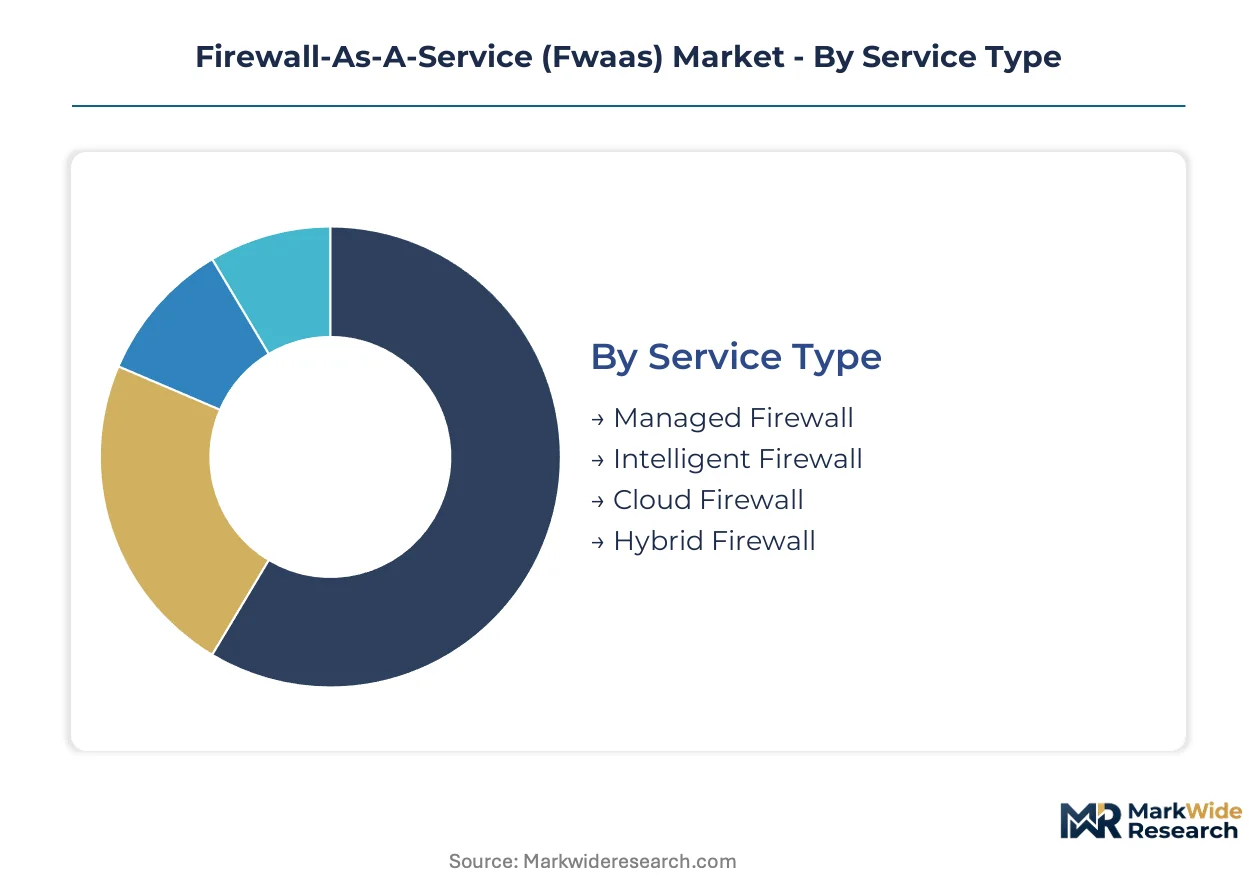
FWaaS procurement patterns fragment sharply across service delivery models, deployment architectures, and regulatory compliance tiers. Vendor positioning and margin capture depend on matching specific technical configurations to buyer security maturity and cloud-native readiness.
Service Type:
Supply concentration clusters around platforms that bundle policy orchestration with continuous threat intelligence feeds, favoring providers with distributed points of presence.
- Managed Firewall:Third-party security operations centers handle 24/7 monitoring, policy tuning, and incident response through dedicated service level agreements. Financial services firms in the United States contract these services to satisfy SEC cybersecurity disclosure obligations without building internal SecDevOps teams. Managed Firewall absorbs the bulk of installed capacity; Cloud Firewall is expanding most quickly.
- Intelligent Firewall:Machine learning engines analyze traffic patterns to autonomously adjust blocking rules and reduce false positives in dynamic cloud environments. Large enterprises deploy these systems where application workloads shift hourly across Kubernetes clusters.
- Cloud Firewall:Native policy enforcement delivered through hyperscaler marketplaces or independent software vendor platforms, scaling throughput elastically with cloud egress volumes.
- Hybrid Firewall:Unified policy management spanning on-premises appliances and cloud-hosted instances, preserving existing capital investments during gradual migration.
Intelligent Firewall commands premium pricing for autonomous threat detection; Cloud Firewall scales subscription volumes fastest among pure-cloud adopters.
Deployment Model:
Cost tier differentiation separates commodity public cloud subscriptions from architecturally complex multi-cloud configurations requiring custom integration layers.
- Public Cloud:Single-tenant or shared firewall instances provisioned through AWS, Azure, or Google Cloud native security services, minimizing operational overhead for cloud-first organizations.
- Private Cloud:Dedicated virtual firewall appliances deployed within isolated cloud environments, satisfying data residency requirements for European GDPR-regulated workloads. Private Cloud absorbs the bulk of installed capacity; Multi-Cloud is expanding most quickly.
- Multi-Cloud:Centralized policy orchestration across heterogeneous cloud environments, addressing API inconsistency through abstraction layers or vendor-native federation tools. Enterprises operating across AWS and Azure deploy these architectures to avoid lock-in while maintaining consistent security posture.
- On-Premises:Virtualized firewall software running on customer-managed hardware, persisting in regulated verticals where air-gapped networks remain mandatory.
Private Cloud retains the largest policy enforcement footprint; Multi-Cloud configurations gain share fastest as enterprises diversify cloud provider relationships.
End User:
Customer type determines procurement channel preference, with large enterprises negotiating direct platform licenses while SMEs route through managed service provider intermediaries.
- SMEs:Resource-constrained organizations purchasing FWaaS through bundled security service packages, prioritizing simplified deployment over granular policy customization.
- Large Enterprises:Complex hybrid IT estates requiring dedicated customer success teams, custom threat intelligence integrations, and API access for security orchestration automation. Large Enterprises absorb the bulk of installed capacity; SMEs are expanding most quickly.
- Government:Federal, state, and local agencies mandating FedRAMP authorization as a gate for vendor eligibility, with procurement cycles elongated by security assessment requirements.
- Educational Institutions:Universities and K-12 districts with distributed campus networks and limited security staffing, increasingly adopting cloud-delivered models to replace aging perimeter appliances.
Large Enterprises dominate current subscription value; SME adoption accelerates fastest as packaged service bundles reduce deployment complexity.
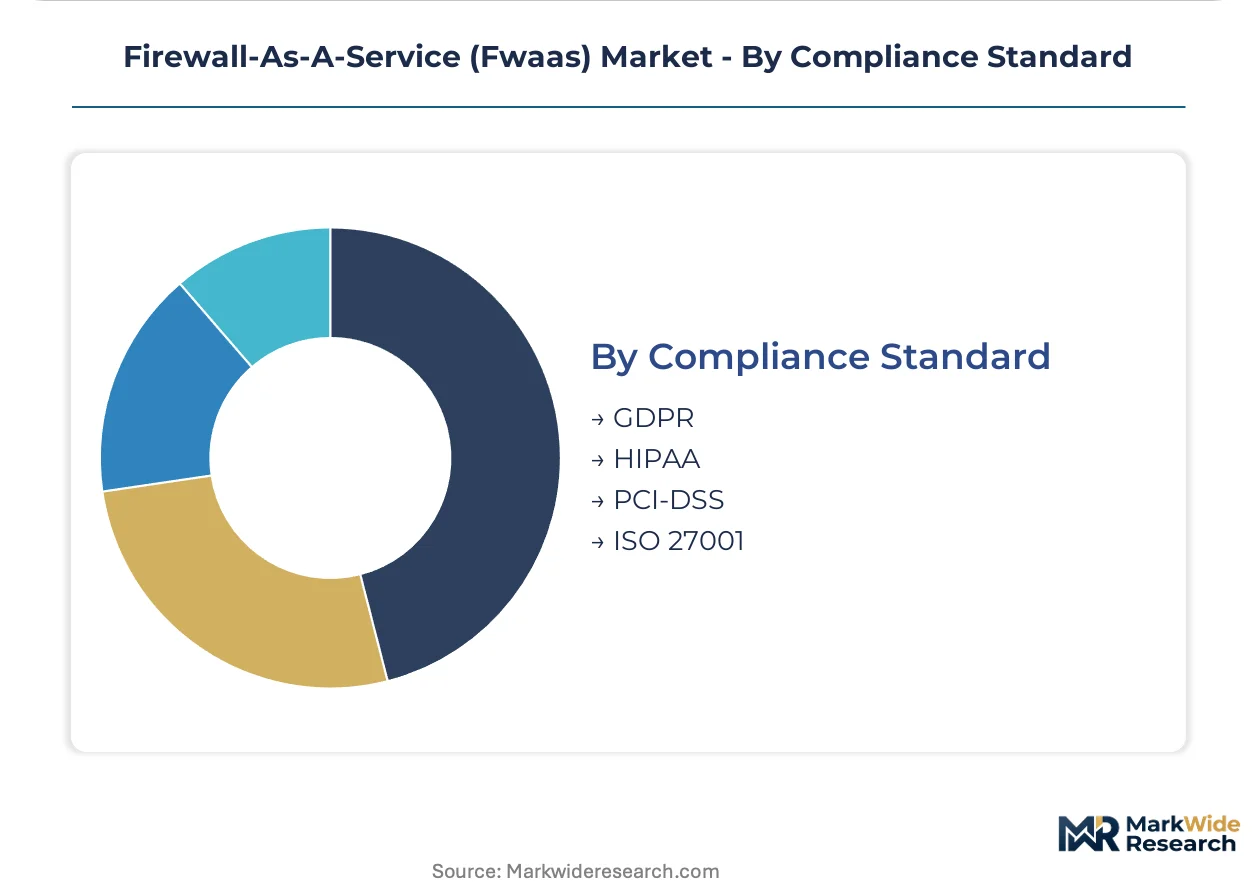
Compliance Standard:
Margin tier stratification privileges certified platforms, with HIPAA and PCI-DSS attestation commanding substantial pricing premiums over baseline ISO 27001 compliance.
- GDPR:European data protection mandates requiring in-region data processing, breach notification timelines, and privacy-by-design architecture validation for controllers and processors.
- HIPAA:United States healthcare privacy and security rules mandating administrative, physical, and technical safeguards for protected health information in transit and at rest. HIPAA-certified platforms absorb the bulk of installed capacity; GDPR-aligned services are expanding most quickly.
- PCI-DSS:Payment card industry data security standards governing firewall configuration, network segmentation, and access control for cardholder data environments.
- ISO 27001:International information security management system certification providing baseline assurance for cross-border commercial contracts and supply chain due diligence.
HIPAA-compliant deployments retain the largest certified footprint; GDPR-aligned service expansion climbs fastest as European NIS2 Directive implementation tightens incident reporting obligations.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States federal agencies and financial institutions absorb the dominant share of FWaaS procurement, driven by FedRAMP authorization requirements and SEC cybersecurity disclosure mandates. Cloud-first policies from Washington reshape how security infrastructure contracts flow through procurement channels.
United States
Financial services firms and federal agencies drive concentrated demand for FedRAMP-authorized platforms. NIST zero-trust architecture guidance shapes procurement specifications across civilian and defense contracts. Northern Virginia's data center corridor hosts the densest concentration of cloud firewall points of presence serving government and enterprise workloads.
Germany
Industrial manufacturers and automotive OEMs extend cloud security policies to operational technology environments. The NIS2 Directive mandates incident reporting timelines that accelerate managed firewall service adoption. Baden-Württemberg's automotive cluster leads private 5G network deployments requiring slice-isolated firewall policies.
United Kingdom
Financial services regulators in London mandate demonstrable network security controls for systemic institutions. The National Cyber Security Centre publishes cloud security principles that filter into bank procurement specifications. The City of London's trading infrastructure drives demand for low-latency cloud firewall deployments.
India
Digital public infrastructure initiatives and data center localization incentives open greenfield deployment opportunities. The Reserve Bank of India's cybersecurity guidelines for payment systems accelerate cloud security adoption. Karnataka's Bengaluru tech corridor concentrates enterprise security operations centers serving domestic and export markets.
Japan
Manufacturing conglomerates consolidate branch security during cloud migration of legacy systems. METI's cybersecurity framework for critical infrastructure operators shapes vendor selection criteria. The Kanto region's Tokyo-Osaka industrial belt hosts hybrid deployments spanning on-premises appliances and cloud-native enforcement.
Firewall-As-A-Service (Fwaas) Market Competitive Landscape
Platform consolidation dominates the current landscape as vendors bundle networking and security functions into unified service edges. The vendor base separates into three distinct tiers: hyperscaler-native platforms, independent cloud security specialists, and legacy appliance vendors transitioning to subscription models. Strategic imperatives center on SD-WAN integration and zero-trust architecture certification. Competitive positioning hinges on FedRAMP authorization status and multi-cloud policy orchestration capabilities.
Within the independent cloud security tier, Zscaler and Cato Networks exemplify the proxy-based and SASE-native archetypes respectively. Palo Alto Networks anchors the platform consolidation vector through its Prisma Access offering. These three companies represent contrasting bets on architectural approaches to distributed workforce protection.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Fortinet |
| Cisco Systems |
| Zscaler |
| Check Point Software Technologies |
| Barracuda Networks |
| Cato Networks |
| Cloudflare |
| Juniper Networks |
| Others |
Pricing and Supply Chain Analysis
Cloud infrastructure compute costs cascade through FWaaS pricing tiers as hyperscaler egress fees and point-of-presence operational expenditures compress margins at the service delivery layer. These input costs stratify subscription rates across managed firewall bundles, intelligent firewall premiums, and elastic cloud firewall throughput tiers.
Pricing Analysis
Volume subscriptions capture the mass-market tier while premium margins concentrate in FedRAMP-authorized and HIPAA-certified deployments. Pricing stratifies across certification-grade tiers, with compliance attestation commanding substantial premiums over baseline ISO 27001 offerings. Cost compression in mid-market segments is intensifying because hyperscaler marketplace commoditization erodes differentiation. SMEs exhibit highest price sensitivity, negotiating per-user rates, while federal agencies accept premium throughput-tiered contracts.
Supply Chain Analysis
Certification gating restricts viable vendor participation to providers with FedRAMP authorization engineering capacity concentrated in the United States, Israel, and Ireland. Hyperscaler backbone dependencies rest on AWS, Azure, and Google Cloud infrastructure, with specialized threat intelligence feeds sourcing from Israel and the United States. Single-source vulnerability concentrates in certificate management infrastructure for TLS inspection. Distribution runs through direct enterprise sales, hyperscaler marketplaces, and managed security service provider intermediaries.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
FWaaS market expansion is supply-constrained by FedRAMP authorization engineering bottlenecks that elongate vendor onboarding and sustain pricing power for certified incumbents.
For Market Incumbents: Deploy zero-trust architecture certification investments to anchor federal procurement specifications before NIST guidance hardens into mandatory requirements. Consolidate SD-WAN integration capabilities to counter emerging SASE-native entrants threatening mid-market bundles. Channel control through managed security service provider exclusivity agreements limits price erosion from hyperscaler marketplace commoditization. For New Entrants and Emerging Players: India's data center localization incentives and digital public infrastructure initiatives offer the most penetrable geography for greenfield cloud firewall deployment. Operational technology security for manufacturing and critical infrastructure represents an underserved buyer archetype with specialized protocol requirements and limited incumbent presence. A channel-native go-to-market through regional system integrators accelerates compliance navigation. For Investors and Strategic Acquirers: Distressed-cycle entries favor mid-tier managed security service providers with established SOC operations in Germany and France facing NIS2 Directive compliance cost pressures. Long-term viability hinges on multi-cloud policy orchestration intellectual property and zero-trust architecture implementation expertise. The signal to watch is hyperscaler marketplace revenue share renegotiations indicating platform dependency risk.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Investment | Unlocks federal procurement channels under NIST zero-trust mandates and compresses competitive vendor pools. |
| SD-WAN Integration | Collapses separate networking and security procurement decisions into unified vendor selections for mid-market buyers. |
| Operational Technology Security Extension | Captures manufacturing and critical infrastructure demand for protocol-aware inspection engines in industrial control environments. |
| Multi-Cloud Policy Orchestration Development | Addresses API inconsistency across AWS, Azure, and Google Cloud environments to reduce customer lock-in friction. |
| Managed Detection and Response Bundling | Aligns with European NIS2 Directive incident reporting mandates accelerating procurement among energy and transport operators. |
Research Methodology
Trade association data, regulatory filings, and customs records anchored secondary inputs, supplemented by primary interviews with CISOs, cloud security architects, federal procurement officers, and managed security service provider executives. SEC cybersecurity disclosure filings, FedRAMP authorization repositories, NIST guidance documents, and hyperscaler marketplace transaction data provided validation layers. Bottom-up subscription volume estimates triangulated against top-down IT security spending allocation surveys.
Data-stream reconciliation across deployment model segmentation, compliance tier stratification, and end-user archetype clustering shaped the analytical framework across the projection horizon. Modeled dimensions included service delivery type, cloud architecture configuration, regulatory certification level, and organization size tier. CAGRs were derived from elasticity-adjusted adoption curves and replacement cycle acceleration factors. Quantum-resistant cryptography timelines and post-TLS 1.3 inspection viability constraints informed long-horizon technology substitution assumptions.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to encryption standard evolution and federal cloud procurement policy shifts. Forecasts reflect documented assumptions regarding zero-trust mandate adoption velocity and hyperscaler marketplace fee structures. A model refresh is warranted upon material change in NIST zero-trust architecture enforcement timelines or FedRAMP authorization process duration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Cyber Situational Awareness Market
Cybersecurity
Enterprise Network Firewall Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Endpoint Protection Platforms (EPP) Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
North America Software Defined Perimeter Market
Cybersecurity
North America Digital Forensics Market
Cybersecurity
Cloud Workload Protection Market
Cybersecurity
Network Sandboxing Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
Greece Cybersecurity Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Oman Cybersecurity Market
Cybersecurity
Global Database Encryption Market
Cybersecurity
Europe Web Application Firewall Market
Cybersecurity
Threat Intelligence Market