
 Cryptojacking Solution Market | 2026-2036
Cryptojacking Solution Market Size, Share, and Industry Trends Forecast 2026-2036
Cryptojacking Solution Market Outlook
Defensive cybersecurity talent scarcity is bifurcating the competitive landscape between vendors with embedded threat-intelligence teams and those reliant on third-party feeds. Palo Alto Networks leverages its Unit 42 research division to sustain rapid signature updates against evolving miner strains. Fortinet anchors its position through tight integration of cryptojacking detection with broader SD-WAN and firewall deployments. Kaspersky competes on behavioral analytics depth, particularly in European and Asian enterprise accounts where its endpoint agents occupy substantial installed bases.
Cryptojacking solutions encompass software platforms and managed services engineered to detect unauthorized cryptocurrency mining operations executing on compromised hardware, typically identifying anomalous CPU utilization patterns, suspicious outbound mining-pool connections, and memory-resident payload signatures. Cloud-based delivery models are capturing disproportionate growth as hybrid work architectures expand the attack surface beyond traditional perimeter controls, while machine learning technology segments command premium positioning due to adaptive detection of polymorphic miner variants that evade static rule sets. Behavioral analytics deployment approaches attract mid-market buyers seeking reduced false-positive overhead compared to signature-dependent alternatives.
The U.S. Securities and Exchange Commission mandates incident disclosure protocols that expose cryptojacking breaches to shareholder litigation, while the European Union Agency for Cybersecurity publishes technical guidance under the Cybersecurity Act that shapes procurement specifications. ISO 27001 certification requirements increasingly incorporate cryptojacking risk assessments within broader information-security management audits. Stakeholders must weigh whether to consolidate detection capabilities within existing endpoint platforms or deploy specialized point solutions as mining malware grows more adept at evading general-purpose defenses.
Market Dynamics
Cloud-native detection architectures are restructuring competitive positioning as enterprises abandon perimeter-centric security models. The shift toward distributed workforce infrastructure has fragmented the attack surface, forcing vendors to reengineer monitoring capabilities for containerized and serverless environments.
Growth Catalysts
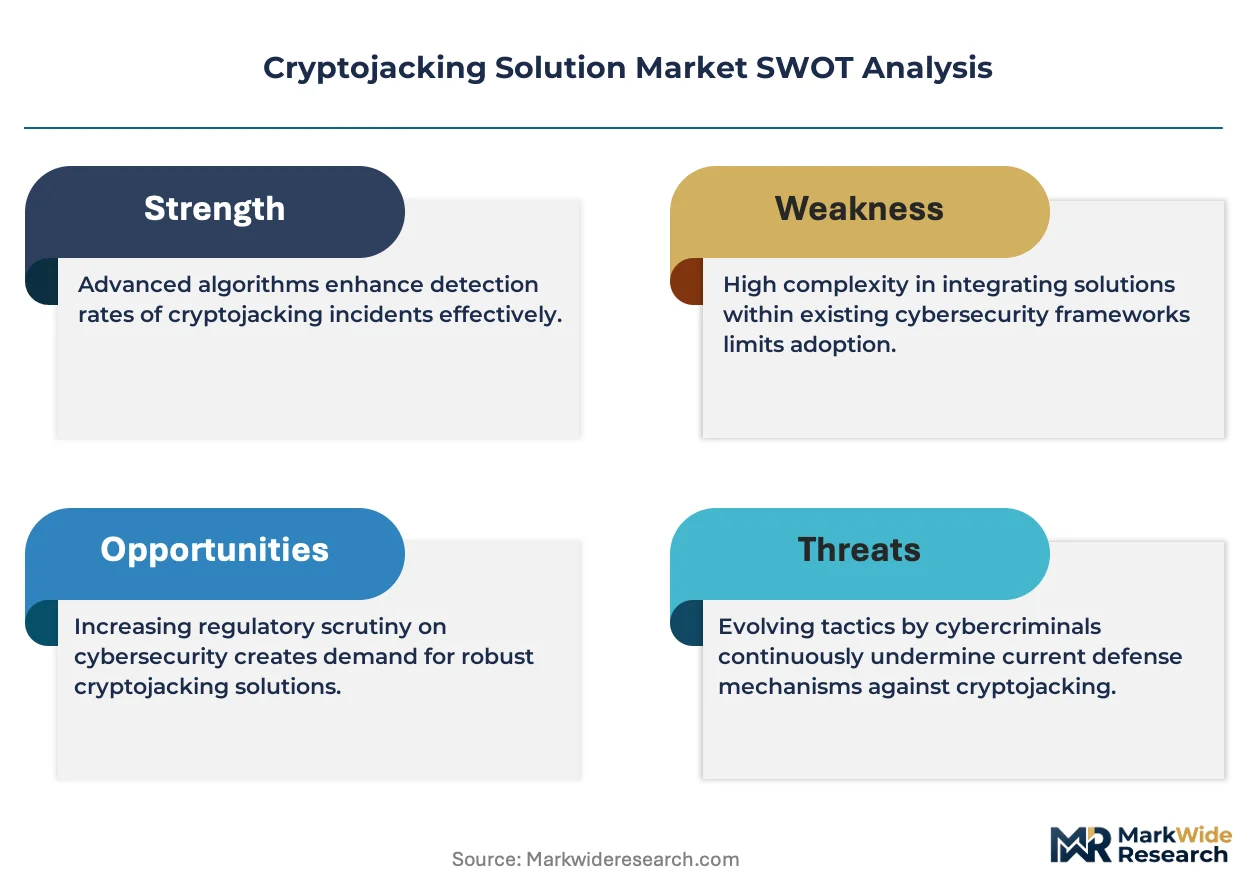
- NIS2 Directive:The European Union's expanded incident-reporting obligations for critical infrastructure operators accelerate procurement of compliant detection platforms across energy and transport sectors.
- Behavioral Analytics:Machine learning models analyzing CPU thermal patterns and memory allocation anomalies identify polymorphic miner strains that signature-based tools miss.
- Financial Services:Enterprise IT departments at banks and payment processors face sustained computational resource drains, driving enterprise-wide deployment of endpoint monitoring agents.
Market Restraints
- False Positive Overhead:Behavioral detection systems generate alert fatigue when legitimate high-performance computing workloads trigger mining-pattern signatures.
- Supply Concentration:Cloud infrastructure providers in the United States control the majority of hyperscale detection platform hosting, creating single-point-of-failure risks.
- Technical Limitation:Memory-resident miners executing exclusively in RAM evade disk-scanning detection modules, requiring continuous live-system monitoring that consumes additional processing overhead.
Strategic Opportunities
- ISO 27001 Convergence:Certification requirements increasingly incorporate cryptojacking risk assessments, creating bundled compliance service opportunities for information-security consultancies.
- Edge Computing Expansion:IoT device fleets and industrial control systems remain undermonitored for unauthorized mining operations, representing greenfield deployment territory.
- Managed Detection Services:Mid-market enterprises lacking internal security operations centers are adopting subscription-based threat-hunting services to offset talent scarcity.
Industry Challenges
- Threat Intelligence Talent Scarcity:Vendors struggle to recruit analysts capable of reverse-engineering evolving miner payloads and maintaining signature databases against obfuscation techniques.
- Legacy System Integration:Industrial control environments running outdated operating systems cannot accommodate modern endpoint agents without operational disruption.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cryptojacking Solution Market |
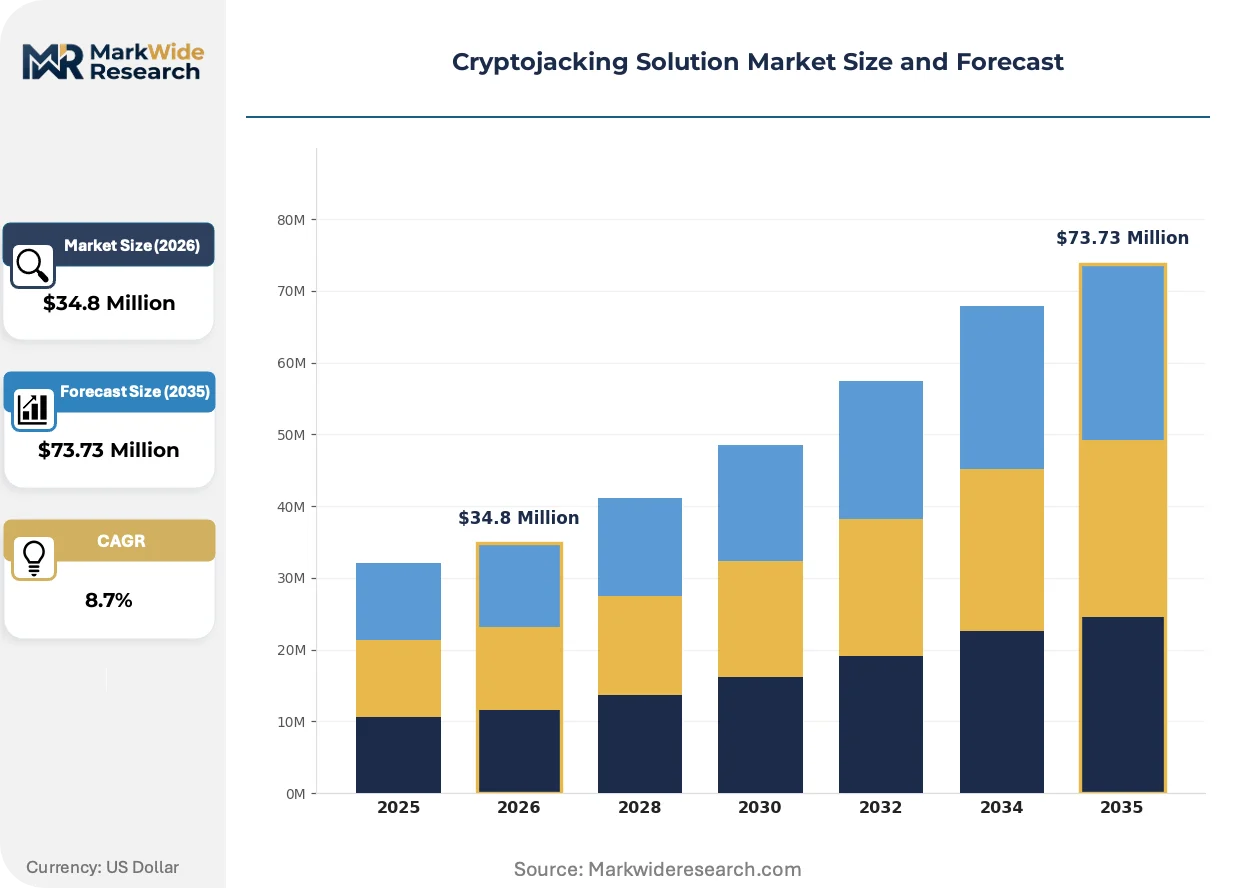
| Market Size in 2026 | $34.8 Million |
| Market Size in 2035 | $73.73 Million |
| CAGR (2026 – 2036) | 8.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: On-Premise, Cloud-Based, Hybrid, Managed Service End User: IT Companies, Financial Institutions, Telecommunications, Public Sector Deployment: Software Deployment, Vendor Deployment, Self-Hosted, Third-Party Managed Technology: Machine Learning, Behavioral Analytics, Intrusion Detection, Firewall Protection |
| Companies Covered | Cisco Systems, IBM Corporation, Palo Alto Networks, Symantec (Broadcom Inc.), McAfee (Trellix), Fortinet, Trend Micro, Kaspersky, SonicWall, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cryptojacking Solution Market Strategic Shifts
Adaptive detection methodologies are displacing static rule-based systems as attackers deploy polymorphic code that regenerates signatures between infections. The convergence of cloud workload protection with endpoint detection platforms is compressing vendor consolidation timelines.
Extended detection and response platforms with embedded cryptojacking modules are displacing standalone mining-specific tools as enterprises prioritize consolidated security stacks. Financial institutions and defense contractors in the United States are standardizing on these integrated suites. The displacement is compressing pricing power for point-solution vendors lacking broader platform integration.
The European Union Agency for Cybersecurity technical guidance under the Cybersecurity Act shapes procurement specifications for critical infrastructure operators. Member states transpose these requirements into national compliance frameworks. Energy and transport sectors in Germany and France are adapting security audits to incorporate mining-detection capability assessments.
Enterprise buyers are unbundling detection software from managed response services, creating specialized procurement channels for pure-play technology licensing. Value-added resellers and systems integrators capture this disintermediation opportunity. The United Kingdom and Netherlands show the most pronounced unbundling behavior among mid-market enterprises seeking cost optimization.
Cryptojacking Solution Market Segmentation
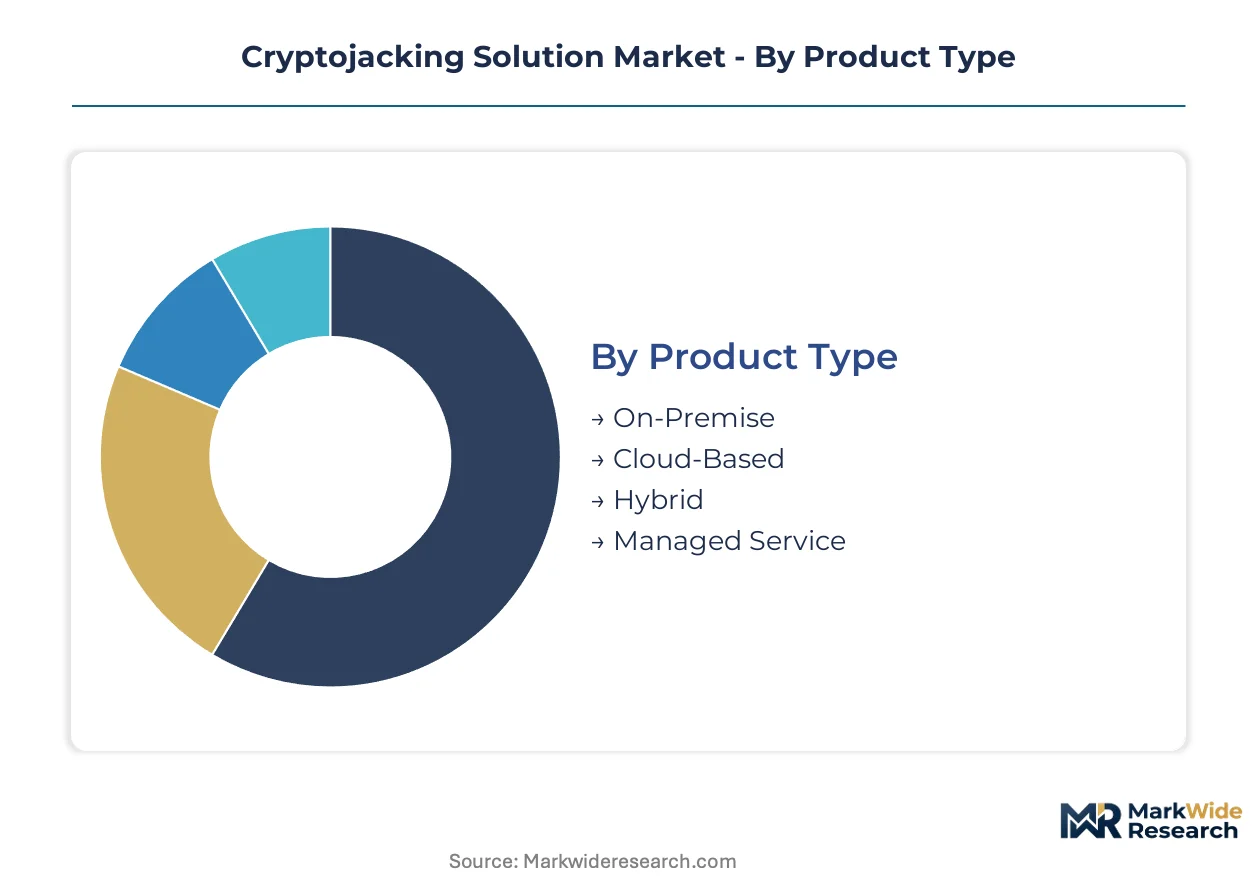
Cryptojacking solution procurement patterns diverge sharply across deployment architectures and organizational risk profiles. Regulatory mandates in the European Union and United States create asymmetric compliance burdens that reshape segment prioritization. Technology sophistication thresholds further stratify buyer segments between behavioral analytics adopters and signature-dependent legacy users.
Product Type:
EU NIS2 Directive incident-reporting obligations and U.S. SEC disclosure protocols drive divergent procurement preferences across delivery models, with cloud-native architectures gaining traction among compliance-heavy sectors.
- Cloud-Based:Elastic compute environments enable real-time threat intelligence ingestion without on-site infrastructure overhead. Financial institutions in Germany and France favor this model to satisfy ENISA technical guidance while avoiding capital expenditure approval cycles. The delivery mechanism supports continuous signature updates against polymorphic miner strains.
- Managed Service:Security operations center outsourcing addresses acute talent scarcity among mid-market enterprises lacking reverse-engineering capabilities. Dutch and British buyers show pronounced unbundling behavior, procuring pure detection technology separately from incident response retainers. Subscription pricing aligns with ISO 27001 audit cycles.
- On-Premise:Air-gapped deployments serve defense contractors and classified facilities with data sovereignty requirements.
- Hybrid:Split architectures accommodate workloads with mixed sensitivity classifications across distributed workforce infrastructure.
Established volume favors On-Premise; emerging adoption favors Cloud-Based.
End User:
Cost tier differentiation separates enterprise buyers with dedicated threat-hunting budgets from resource-constrained sectors dependent on bundled security suites.
- Financial Institutions:Basel III operational risk frameworks and SEC shareholder litigation exposure mandate enterprise-wide endpoint monitoring. U.S. banks and payment processors deploy behavioral analytics at premium price points to detect memory-resident miners evading disk scans. Computational resource drains from undetected mining operations justify dedicated procurement committees.
- Public Sector:Federal agencies and defense contractors face sustained targeting by state-affiliated threat actors seeking covert infrastructure access. NIST Cybersecurity Framework adoption drives standardized procurement specifications across civilian and military branches. Budget cycles align with fiscal year appropriations rather than quarterly business rhythms.
- IT Companies:Technology service providers integrate cryptojacking modules into multi-tenant managed security offerings.
- Telecommunications:Network operators leverage existing traffic inspection infrastructure to detect mining-pool connection anomalies.
Financial Institutions command premium pricing tiers; Public Sector shows steepest expansion trajectory under federal modernization mandates.
Deployment:
Customer type maturity separates sophisticated buyers with internal DevSecOps pipelines from organizations requiring turnkey implementation support.
- Software Deployment:Packaged agents integrate with existing endpoint detection platforms through standardized APIs. Volume concentrates among enterprise IT departments with established software asset management disciplines. Licensing models favor annual subscriptions aligned with ISO 27001 recertification schedules.
- Third-Party Managed:Value-added resellers and systems integrators capture disintermediation opportunities as buyers unbundle technology from response services. Mid-market enterprises in the United Kingdom and Netherlands leverage this channel for cost optimization without internal security operations center investment.
- Vendor Deployment:Professional services-led implementation suits industrial control environments with legacy operating system constraints.
- Self-Hosted:Containerized deployments appeal to cloud-native enterprises with Kubernetes orchestration expertise.
Software Deployment retains dominant share; Third-Party Managed is gaining share fastest among talent-constrained buyers.
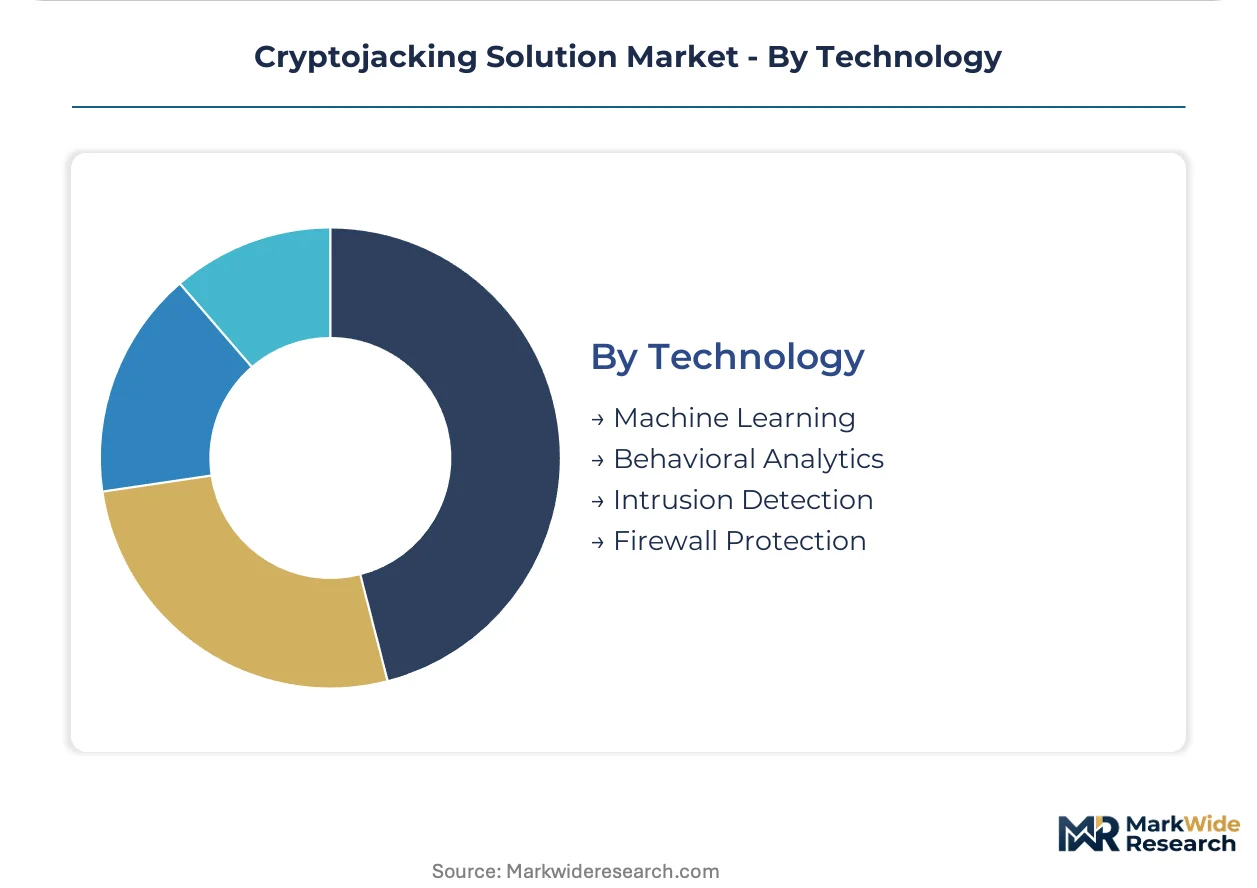
Technology:
Margin structure differentiates premium machine learning offerings from commoditized signature-based alternatives facing pricing compression.
- Behavioral Analytics:CPU thermal pattern analysis and memory allocation anomaly detection identify polymorphic miner strains that static rules miss. Palo Alto Networks and Kaspersky compete on algorithmic depth for European and Asian enterprise accounts. False-positive overhead remains the primary adoption barrier against legitimate high-performance computing workloads.
- Machine Learning:Adaptive models regenerate detection boundaries without human analyst intervention. Premium positioning commands price multiples over signature-dependent alternatives. Cloud workload protection convergence compresses standalone mining-specific tool viability.
- Intrusion Detection:Network-layer monitoring captures mining-pool connection signatures at perimeter boundaries.
- Firewall Protection:Integrated SD-WAN deployments embed cryptojacking controls within broader traffic management policies.
Behavioral Analytics anchors premium tiers; Machine Learning shows strongest pipeline growth among cloud-native adopters.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The SEC mandates incident disclosure protocols that expose cryptojacking breaches to shareholder litigation, anchoring United States demand. Federal procurement specifications and defense contractor requirements concentrate detection platform deployment across North American enterprise accounts.
United States
Financial institutions and defense contractors face sustained targeting by state-affiliated threat actors seeking covert mining access. NIST Cybersecurity Framework adoption drives standardized procurement specifications across civilian and military branches. Silicon Valley technology clusters and Washington D.C. federal procurement hubs anchor enterprise deployment volumes.
Germany
Energy and transport sectors adapt security audits to incorporate mining-detection capability assessments under transposed NIS2 requirements. The country's national cybersecurity regulator publishes technical guidance that shapes critical infrastructure operator procurement. Frankfurt financial services clusters and Munich industrial technology corridors concentrate compliance-driven platform adoption.
United Kingdom
Mid-market enterprises show pronounced unbundling behavior, procuring pure detection technology separately from incident response retainers. ISO 27001 certification requirements increasingly incorporate cryptojacking risk assessments within broader information-security management audits. London financial services districts and Manchester technology hubs drive subscription-based managed detection service adoption.
France
Critical infrastructure operators accelerate procurement of compliant detection platforms across energy and transport sectors under ENISA technical guidance. The national cybersecurity agency shapes procurement specifications through Cybersecurity Act implementation. Paris financial centers and Lyon industrial automation clusters concentrate behavioral analytics deployment for polymorphic miner detection.
Netherlands
Value-added resellers and systems integrators capture disintermediation opportunities as buyers unbundle technology from response services. Dutch enterprises leverage third-party managed channels for cost optimization without internal security operations center investment. Amsterdam data center corridors and Eindhoven high-technology campuses anchor cloud-native detection architecture deployment.
Cryptojacking Solution Market Competitive Environment
Technology leadership and cost leadership are held by different player archetypes across the cryptojacking solution market. The vendor base concentrates around network security incumbents with embedded threat intelligence capabilities and specialized endpoint protection firms with behavioral analytics depth. Strategic archetypes include platform consolidators integrating mining detection into broader security stacks, pure-play specialists commanding premium positioning through algorithmic differentiation, and managed service providers addressing mid-market talent scarcity. Dominant competitive moves encompass portfolio diversification into cloud workload protection and geographic expansion through value-added reseller channel development.
Within the platform consolidator tier, Palo Alto Networks and Fortinet exemplify archetypes anchoring competitive positioning through integrated security stack deployment. Kaspersky occupies a specialist position emphasizing behavioral analytics depth for European and Asian enterprise accounts. These three entities represent distinct strategic postures: network-centric platform integration, SD-WAN and firewall-embedded detection, and algorithmic endpoint specialization respectively.
| Leading Market Players |
|---|
| Cisco Systems |
| IBM Corporation |
| Palo Alto Networks |
| Symantec (Broadcom Inc.) |
| McAfee (Trellix) |
| Fortinet |
| Trend Micro |
| Kaspersky |
| SonicWall |
| Others |
Value Chain & Pricing Dynamics
Cloud-native delivery models displacing on-premise deployments simultaneously redistribute supply geography toward hyperscale hosting regions and compress pricing economics through subscription standardization. This substitution dynamic concentrates procurement leverage among buyers in Germany and France seeking ENISA-compliant elasticity without capital expenditure cycles.
Pricing Analysis
Geographic price spreads widen between U.S. defense contractors facing NIST Cybersecurity Framework mandates and mid-market Dutch enterprises unbundling detection from response services. The dominant pricing structure is three-tier SaaS subscription across premium behavioral analytics, standard signature-based detection, and economy firewall-embedded modules. Price differentiation hinges on machine learning sophistication and ISO 27001 audit bundling. Cost compression in the standard tier intensifies as Palo Alto Networks and Fortinet integrate mining detection into broader platform suites. Mid-market buyers in the United Kingdom show highest price sensitivity; federal agencies in the United States show least.
Supply Chain Analysis
Inbound logistics costs for specialized GPU hardware feeding behavioral analytics training clusters have risen on transpacific trade lanes serving U.S. cloud infrastructure providers. Supply concentrates in the United States for hyperscale hosting, Germany for industrial control system integration, and India for software development labor. Component dependencies include NVIDIA processing units, threat intelligence data feeds, and endpoint agent software licenses. Single-source vulnerability persists in cloud infrastructure provisioning. Distribution runs through value-added resellers capturing disintermediation opportunities in the Netherlands and United Kingdom.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Cryptojacking solutions represent a service-attach opportunity as managed detection and response retainers expand faster than standalone software licensing among talent-constrained mid-market enterprises.
For Market Incumbents: Secure threat intelligence talent pipelines against state-affiliated miner strain evolution by acquiring specialized reverse-engineering boutiques in Eastern Europe. Anchor platform stickiness through ISO 27001 compliance bundling that raises switching costs for financial institution accounts. Defend margin position by integrating mining detection into cloud workload protection suites before point-solution vendors achieve scale.
For New Entrants and Emerging Players: Differentiate on edge computing deployment architectures for IoT device fleets and industrial control systems that incumbent endpoint platforms cannot penetrate without operational disruption. Target undermonitored manufacturing corridors in Germany and France where NIS2 compliance deadlines create urgent procurement windows. Pursue value-added reseller channel partnerships rather than direct enterprise sales to bypass incumbent relationship lock-in.
For Investors and Strategic Acquirers: Secondary-cycle assets sit with private equity-backed managed security service providers lacking behavioral analytics depth. Long-term viability favors platforms converging cryptojacking detection with broader XDR capabilities over standalone mining specialists facing pricing compression. Watch for inflection in federal procurement specification language that mandates adaptive detection methodologies over signature-based alternatives.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Embedding mining detection into Palo Alto Networks and Fortinet suites displaces standalone vendors. |
| Behavioral Analytics Investment | Machine learning R&D at Kaspersky targets polymorphic miner strains evading static rules. |
| Managed Service Expansion | Subscription threat-hunting addresses mid-market talent scarcity in the United Kingdom and Netherlands. |
| Edge Computing Deployment | IoT-focused architectures penetrate industrial control environments legacy agents cannot serve. |
| Compliance Bundling | ISO 27001 audit integration raises switching costs for financial institution accounts in Germany and France. |
Study Parameters
Initial hypotheses were tested against primary input from CISOs at financial institutions, SOC managers at managed security service providers, procurement officers at defense contractors, and channel partners at value-added resellers, then refined against secondary validation from SEC disclosure filings, ENISA technical guidance documents, NIST Cybersecurity Framework implementation reports, and ISO 27001 certification databases. Bottom-up deployment volume estimates were triangulated with top-down market sizing across cloud-native, managed service, on-premise, and hybrid delivery architectures.
Variance decomposition across the projection horizon isolates growth contributions from NIS2 Directive compliance mandates, SEC litigation exposure, behavioral analytics adoption curves, and edge computing expansion trajectories. Segmentation dimensions modeled include delivery model, end-user vertical, deployment channel, and technology sophistication tier. CAGRs were derived from fitted adoption curves calibrated against historical endpoint security platform penetration patterns and cloud workload protection convergence timelines.
The analysis sits within stated boundaries; outcomes outside sustained state-affiliated threat actor targeting of federal infrastructure or accelerated NIS2 enforcement timelines would require recalibration. Forecasts reflect assumptions regarding threat intelligence talent availability, cloud infrastructure concentration stability, and polymorphic miner evolution velocity. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
India Ransomware Protection Market
Cybersecurity
Asia Pacific Digital Forensics Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Global SSH Terminal Market
Cybersecurity
Europe Mobile Security Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
Global Cyber Situational Awareness Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Global Virtualization Security Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Internet of Things (IoT) Security Market