
 Europe Web Application Firewall Market | 2026-2036
Europe Web Application Firewall Market Size, Share, and Industry Trends Forecast 2026-2036
Europe Web Application Firewall Market Insights
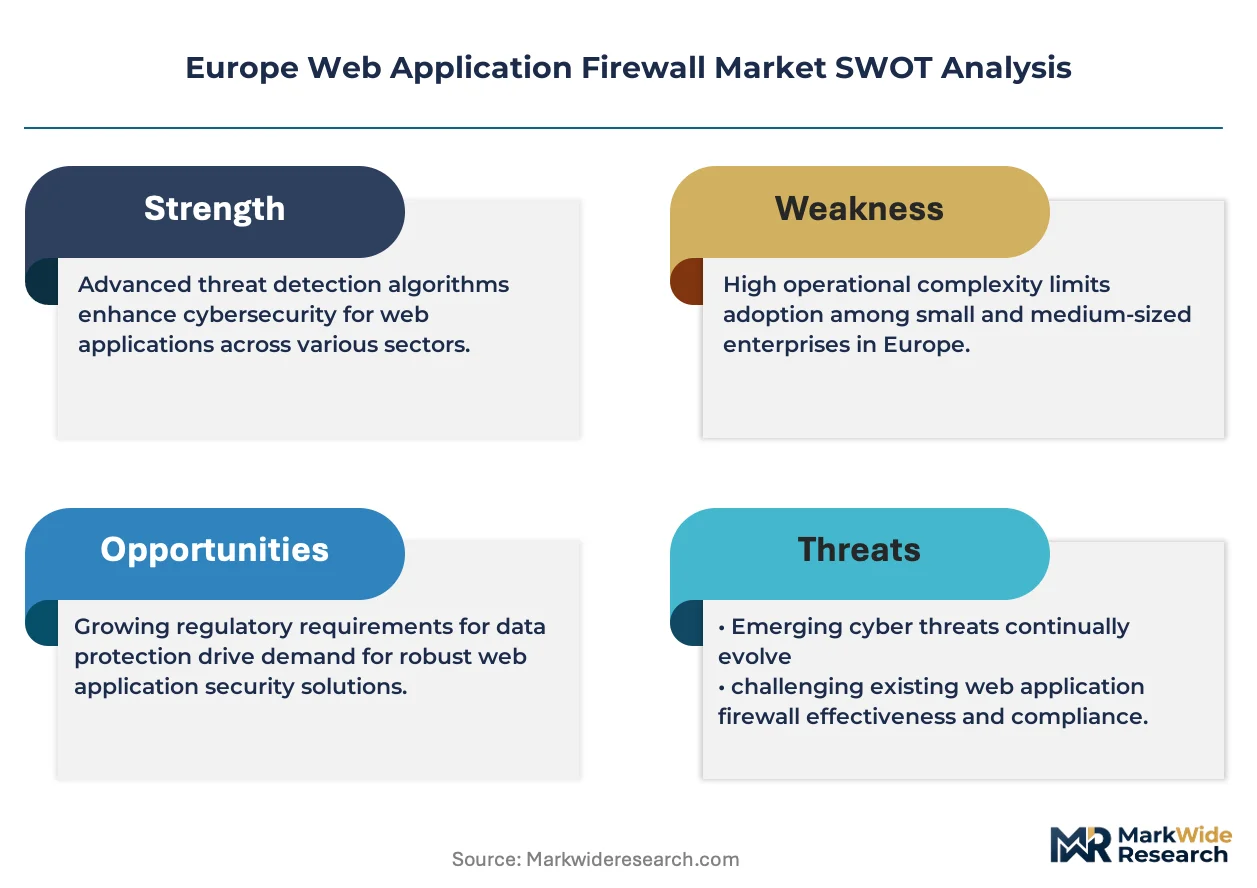
The gap between premium managed WAF offerings and commodity self-service tiers is shifting as enterprise buyers prioritize API security and bot management over basic OWASP rule sets. Cloudflare leverages its edge-network density to sustain low-latency protection across European POPs. Imperva anchors its position through deep specialization in financial services compliance workflows. Fortinet competes by bundling WAF modules into broader SASE contracts, extending its channel control across mid-market accounts.
A web application firewall filters, monitors, and blocks HTTP traffic to and from web applications through signature-based detection, behavioral analysis, and machine-learning anomaly scoring, typically operating at Layer 7 of the OSI model with sub-10-millisecond inspection latency for enterprise deployments. Cloud-based deployment models now dominate new procurement in Europe as organizations abandon hardware refresh cycles, while managed services capture expanding margin pools by offloading rule-tuning and threat-response labor from understaffed security teams. The financial services vertical leads absolute spending due to PSD2 open-banking APIs and SWIFT CSP mandates, though e-commerce is registering the fastest growth as payment fraud vectors migrate to mobile and headless checkout architectures.
The EU NIS2 Directive and GDPR enforcement by national data protection authorities are mandating application-layer logging, incident reporting, and supply-chain security assessments that directly expand WAF addressable spend. EMA guidelines for pharmacovigilance web portals and the EU AI Act's risk-classification framework for automated decision systems are creating compliance-driven procurement in healthcare and public administration. Stakeholders must monitor how ENISA's forthcoming cloud-security certification schemes reshape vendor qualification criteria before the next refresh cycle.
Market Dynamics
The NIS2 Directive and EU AI Act are compressing procurement cycles across European critical infrastructure operators, forcing security teams to consolidate point solutions into unified application-layer protection stacks before compliance deadlines.
Growth Catalysts
- PSD2 Open Banking Mandates:Financial institutions in Germany and France must harden API gateways against credential-stuffing attacks, expanding managed WAF procurement for real-time transaction monitoring.
- Automotive Software-Defined Vehicles:German OEMs are deploying edge-native WAFs to protect over-the-air update channels and connected vehicle APIs from remote exploitation.
- GDPR Article 32 Enforcement:National data protection authorities in Italy and Spain are fining organizations for inadequate application-layer logging, directly expanding WAF addressable spend for breach detection capabilities.
Market Restraints
- Certified Security Engineer Scarcity:The shortage of professionals holding ENISA-certified cybersecurity credentials limits enterprise ability to self-manage complex rule-tuning operations.
- Cloud Concentration Risk:Over-reliance on hyperscale cloud providers for WAF delivery creates single-point-of-failure exposure during regional outages or geopolitical data sovereignty disputes.
- Signature Erosion:Polymorphic attack payloads and encrypted traffic volumes degrade the efficacy of traditional signature-based detection engines against zero-day threats.
Strategic Opportunities
- Healthcare Pharmacovigilance Portals:EMA guidelines for adverse event reporting systems create compliance-driven procurement in Sweden and Denmark for WAFs with immutable audit logging.
- Bot Management Convergence:Integration of behavioral biometrics with Layer 7 inspection enables e-commerce platforms to distinguish human shoppers from automated checkout abuse without friction.
- Poland and Romania Expansion:Shared service centers and IT outsourcing hubs in these markets remain underpenetrated relative to Western European WAF adoption rates.
Industry Challenges
- Legacy Mainframe Integration:Financial services organizations struggle to route COBOL-based core banking traffic through modern cloud-native WAF architectures without latency degradation.
- ENISA Certification Timelines:Pending EUCC cloud security certification schemes delay vendor qualification for public sector procurement frameworks, freezing refresh cycles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Europe Web Application Firewall Market |
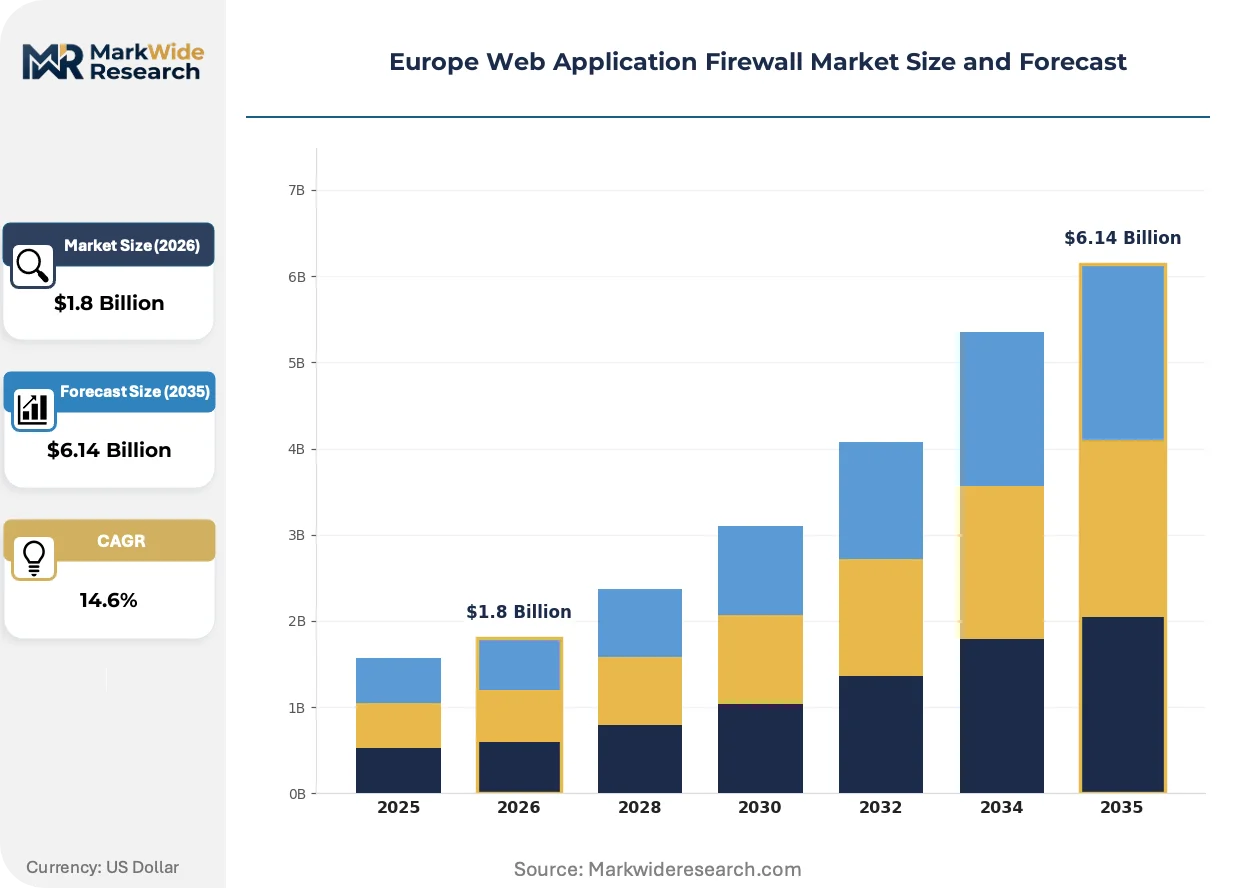
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $6.14 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Cloud-Based, On-Premises, Hybrid, Managed Services Industry Vertical: Financial Services, E-Commerce, Healthcare, Government Deployment Model: Public Cloud, Private Cloud, Multi-Cloud, Hybrid Cloud End User: Small Enterprises, Medium Enterprises, Large Enterprises, Others |
| Companies Covered | Cloudflare, Barracuda Networks, Imperva, AWS, Radware, F5 Networks, Fortinet, Microsoft, Akamai Technologies, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Europe Web Application Firewall Market Trends and Innovations
Machine-learning inference at the network edge is compressing detection latency thresholds while regulatory pressure on automated decision systems forces transparency into algorithmic blocking logic.
Edge-deployed neural inference engines for anomaly scoring are rewriting how application-layer threats are identified. German automotive suppliers and Dutch payment processors are piloting sub-millisecond behavioral models that flag API abuse without decrypting TLS traffic. This compression of inspection latency is collapsing the performance gap between cloud-native and hardware-appliance deployments.
The EU AI Act's risk-classification framework for automated decision systems imposes documentation and human-oversight requirements on security tools that autonomously block traffic. Financial services institutions in France must now maintain explainable audit trails for WAF blocking decisions affecting customer access. Healthcare operators in Belgium are retrofitting existing deployments with interpretability modules to satisfy conformity assessment obligations.
Enterprise buyers are unbundling managed detection and response labor from core WAF licensing. Mid-market organizations in the UK are engaging specialized European MSSPs for 24/7 rule-tuning rather than purchasing premium vendor-managed tiers. This disintermediation of professional services from product subscriptions is visible most acutely in the Nordics, where regional security consultancies compete on GDPR-specific incident response expertise.
Europe Web Application Firewall Market Segmentation
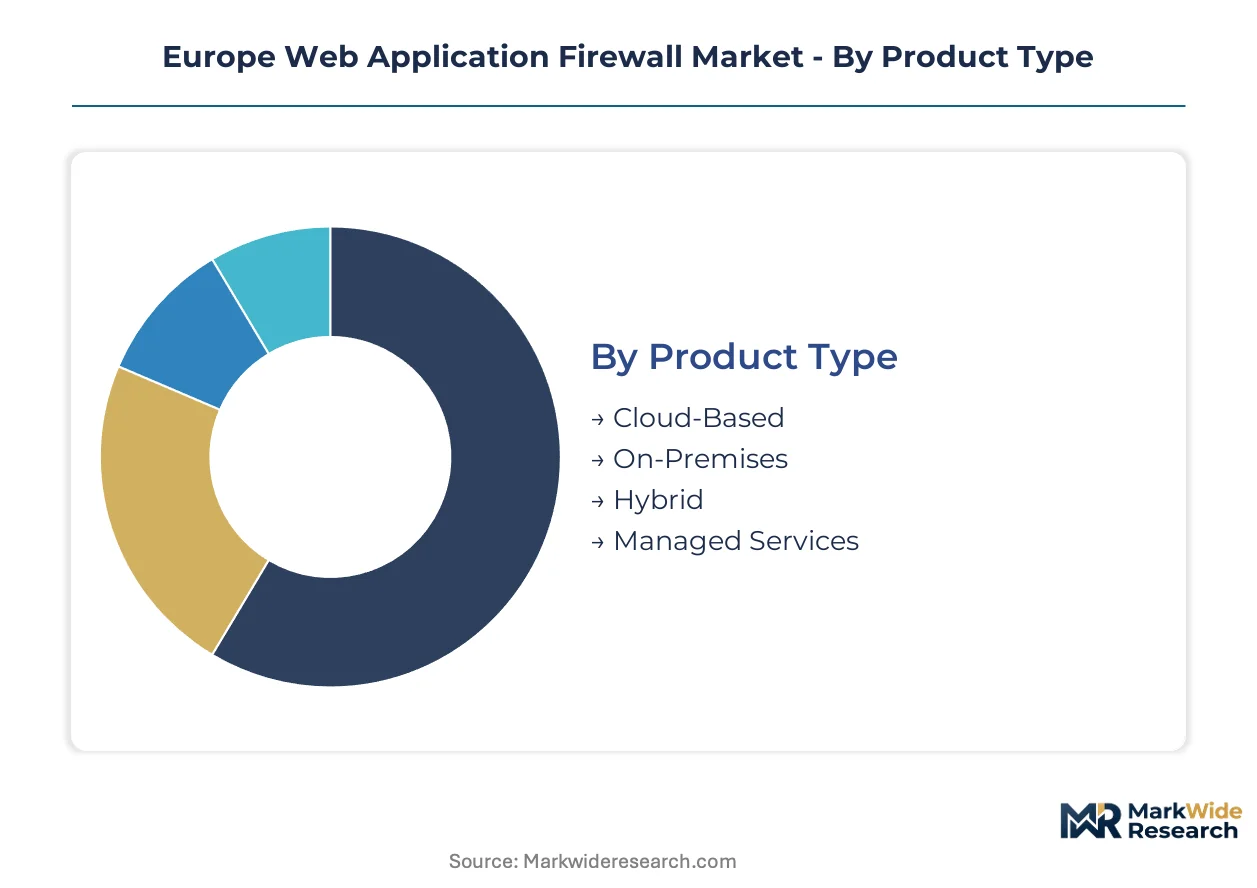
Segmentation in the Europe Web Application Firewall Market reveals how procurement priorities diverge across infrastructure maturity and regulatory exposure. Buyers select deployment architectures based on legacy system constraints, while vertical-specific compliance mandates reshape feature requirements.
Product Type:
Capital intensity varies sharply across product categories, with managed services and hybrid deployments demanding sustained operational expenditure while cloud-native offerings minimize upfront infrastructure investment.
- Cloud-Based:Fully hosted Layer 7 inspection delivered through hyperscale edge networks eliminates data center provisioning. German automotive suppliers and Dutch payment processors favor this model for sub-millisecond latency across distributed API gateways. The shift away from hardware refresh cycles concentrates demand here.
- Managed Services:24/7 rule-tuning, threat response, and compliance reporting offloaded to specialized security operations centers. French financial institutions under EU AI Act documentation requirements drive procurement for explainable audit trails and human-in-the-loop oversight.
- On-Premises:Hardware appliances deployed within customer-controlled facilities for air-gapped environments.
- Hybrid:Split traffic processing combining local inspection for sensitive workloads with cloud scale for distributed attacks.
Cloud-Based absorbs the bulk of installed capacity; Managed Services is expanding most quickly.
Industry Vertical:
Application complexity and regulatory burden determine vertical adoption patterns, with financial services and healthcare facing the steepest compliance-driven procurement cycles.
- Financial Services:PSD2 open-banking APIs and SWIFT CSP mandates require hardened transaction monitoring. Banks across Germany, France, and the UK deploy WAFs for real-time credential-stuffing defense and bot-managed checkout protection. Regulatory pressure from national data protection authorities accelerates refresh timelines.
- Healthcare:EMA pharmacovigilance guidelines for adverse event reporting systems mandate immutable audit logging. Belgian hospitals and Swedish regional health authorities retrofit existing infrastructure with interpretability modules to satisfy EU AI Act conformity assessments for automated blocking decisions.
- E-Commerce:Mobile and headless checkout architectures face payment fraud migration.
- Government:Critical infrastructure operators under NIS2 Directive consolidate point solutions into unified protection stacks.
Financial Services commands the largest absolute spend; E-Commerce climbs the fastest as fraud vectors fragment across channels.
Deployment Model:
Architectural choices reflect data sovereignty requirements and resilience planning, with multi-cloud strategies gaining traction among organizations hedging against regional outages.
- Public Cloud:Shared infrastructure delivering elastic scale for unpredictable attack volumes. UK mid-market organizations favor this model for rapid deployment without capital commitment, though Italian regulators warn of concentration risk during geopolitical disputes.
- Multi-Cloud:Distributed protection across two or more hyperscale providers to eliminate single-point-of-failure exposure. German critical infrastructure operators under NIS2 resilience mandates lead adoption, routing traffic through redundant European points of presence.
- Private Cloud:Dedicated tenant environments for regulated workloads with strict data residency requirements.
- Hybrid Cloud:Orchestrated policies spanning on-premises appliances and cloud-native inspection.
Public Cloud holds the dominant share; Multi-Cloud is gaining share fastest among risk-averse enterprises.
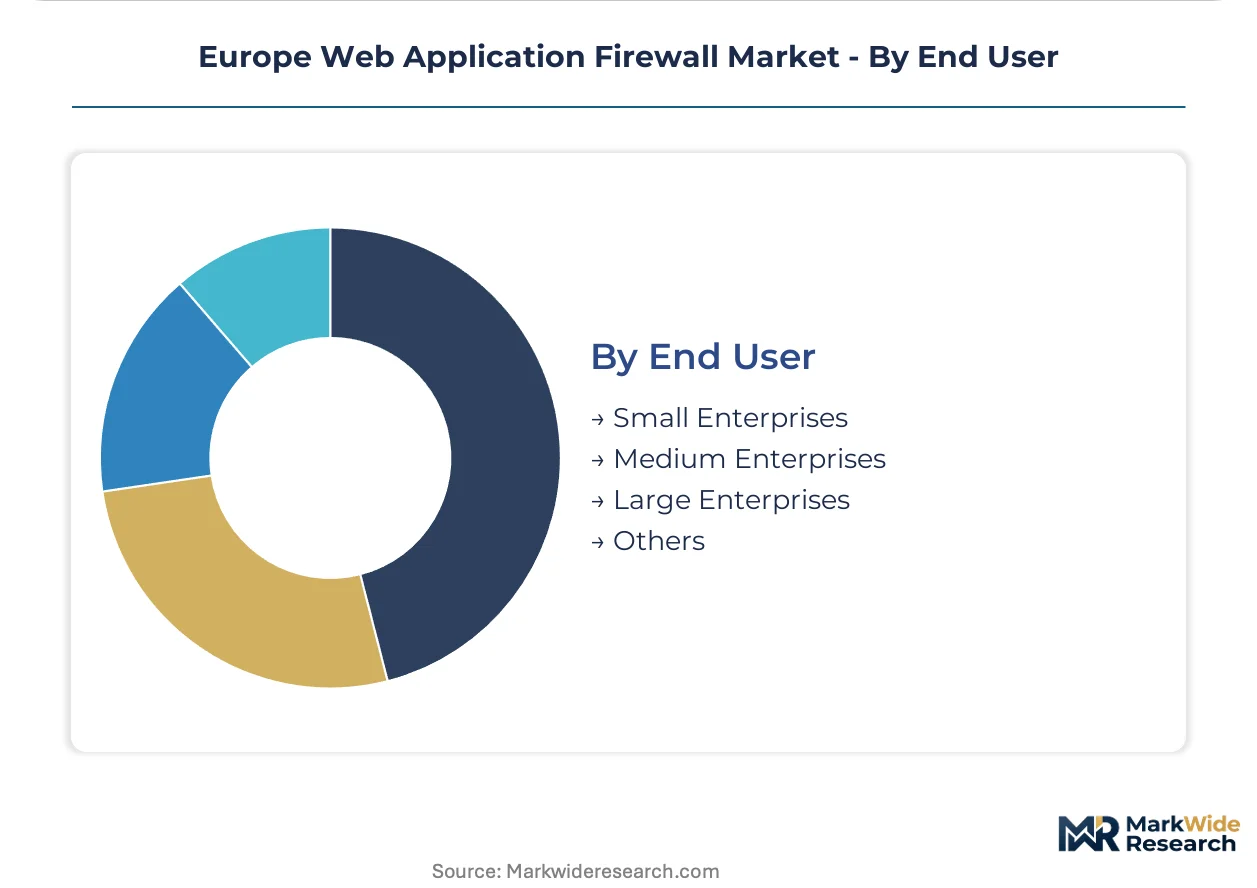
End User:
Organizational scale dictates whether buyers self-manage complex rule-tuning or outsource to specialized providers, with talent scarcity driving divergent procurement strategies.
- Large Enterprises:In-house security engineering teams with ENISA-certified credentials manage sophisticated multi-layer deployments. German banking conglomerates and French automotive groups maintain dedicated WAF operations centers for 24/7 threat response across global application portfolios.
- Small Enterprises:Limited security staffing forces reliance on vendor-managed tiers or regional MSSPs. Nordic security consultancies compete aggressively here on GDPR-specific incident response expertise and fixed-fee rule-tuning packages.
- Medium Enterprises:Hybrid approaches combining core licensing with outsourced professional services.
- Others:Non-profit and educational institutions with specialized funding constraints.
Large Enterprises deploy the greatest installed base; Small Enterprises show the steepest expansion trajectory as managed services democratize access.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Frankfurt's banking corridor concentrates the highest density of WAF procurement activity, driven by PSD2 compliance deadlines and API security mandates across German financial institutions.
Germany
Automotive OEMs in Stuttgart and Munich deploy edge-native WAFs to secure over-the-air vehicle update channels against remote exploitation. The NIS2 Directive forces critical infrastructure operators in North Rhine-Westphalia to consolidate point solutions before enforcement deadlines. Berlin's fintech cluster drives managed services demand for real-time transaction monitoring and bot management.
France
Paris-based banking conglomerates accelerate procurement under EU AI Act documentation requirements for automated blocking decisions. The CNIL enforces GDPR Article 32 through fines for inadequate application-layer logging, expanding breach detection spend. Lyon and Toulouse host aerospace suppliers retrofitting legacy systems with hybrid WAF architectures.
United Kingdom
London's financial services sector leads absolute WAF spending due to SWIFT CSP mandates and open-banking API hardening. Mid-market organizations across Manchester and Birmingham outsource 24/7 rule-tuning to regional MSSPs rather than purchasing premium vendor tiers. The Financial Conduct Authority tightens incident reporting requirements for payment service providers.
Sweden
Regional health authorities in Stockholm retrofit pharmacovigilance portals with immutable audit logging to satisfy EMA adverse event reporting guidelines. The Swedish Authority for Privacy Protection enforces GDPR through application-layer security assessments. Gothenburg's automotive suppliers pilot sub-millisecond behavioral models for API abuse detection.
Netherlands
Amsterdam payment processors favor cloud-native WAF deployments for sub-millisecond latency across distributed API gateways. Rotterdam's port operators under NIS2 resilience mandates adopt multi-cloud strategies to eliminate single-point-of-failure exposure. The Dutch Data Protection Authority audits supply-chain security assessments for critical infrastructure.
Europe Web Application Firewall Market Competitive Landscape
Premium-margin players sit above commodity-margin players across specialization depth and managed service bundling. The vendor base organizes into three tiers: hyperscale cloud platforms with edge-network density, cybersecurity specialists with vertical compliance workflows, and network equipment vendors integrating WAF modules into broader SASE contracts. Dominant competitive moves include portfolio diversification into adjacent bot management and API security segments, plus geographic expansion through channel partnerships in underpenetrated Central European markets.
Within the edge-network tier, Cloudflare and Akamai Technologies occupy positions anchored by distributed European POP infrastructure. Imperva exemplifies the compliance-specialist archetype through financial services workflow integration. Fortinet represents the bundled-platform approach, embedding Layer 7 inspection within broader security fabric deployments. These three anchors illustrate how differentiation vectors split across latency performance, regulatory documentation depth, and consolidated procurement convenience.
| Leading Market Players |
|---|
| Cloudflare |
| Barracuda Networks |
| Imperva |
| AWS |
| Radware |
| F5 Networks |
| Fortinet |
| Microsoft |
| Akamai Technologies |
| Others |
Pricing and Supply Chain Analysis
ENISA-certified security engineering talent concentration in Germany's Rhine-Ruhr corridor feeds directly into labor-cost differentials that separate premium managed WAF tiers from economy self-service offerings. French and UK buyers absorb higher per-seat pricing for 24/7 rule-tuning support as certified engineer scarcity intensifies vendor bargaining power across Northern Europe.
Pricing Analysis
Throughput-based pricing anchors enterprise WAF contracts, with financial services buyers in Frankfurt and Paris paying premiums for sub-millisecond API inspection latency and real-time bot management. Three-tier pricing structure across premium managed services, standard cloud-native subscriptions, and economy self-managed tiers separates buyers by compliance complexity and staffing depth. Pricing pressure stems from hyperscale cloud providers bundling Layer 7 inspection into broader infrastructure contracts, compressing standalone WAF margins. Small enterprises in Nordic markets exhibit highest price sensitivity, while German automotive OEMs prioritize performance guarantees over unit cost.
Supply Chain Analysis
Single-source vulnerability sits with Taiwan-based semiconductor fabrication for neural inference accelerators powering edge-deployed behavioral models. Hardware appliance manufacturing concentrates in China and Mexico, while cloud infrastructure provisioning rests on hyperscale data center buildouts across Ireland, the Netherlands, and Germany. Tariff exposure on networking equipment imports from China threatens margin stability for on-premises deployment vendors. Distribution runs through value-added resellers and systems integrators with vertical specialization in financial services compliance workflows.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Europe Web Application Firewall Market functions as a cost-of-compliance story where the EU AI Act's documentation and human-oversight mandates erect barrier-to-entry moats favoring vendors with pre-built audit trail capabilities and regulatory workflow integration.
For Market Incumbents: Cement market position through backward integration into specialized threat intelligence feeds and exclusive channel partnerships with ENISA-certified MSSPs in underpenetrated Central European markets. Acquire boutique compliance consultancies in Belgium and Sweden to deepen interpretability module development for healthcare and public sector verticals. Threat substitution from API-native security meshes demands preemptive bundling of bot management and Layer 7 inspection into unified application protection platforms. For New Entrants and Emerging Players: Enter via Poland and Romania's shared service center corridors, where IT outsourcing hubs remain underpenetrated relative to Western European WAF adoption benchmarks and price sensitivity creates openings for disruptive cloud-native pricing. Target mid-market e-commerce platforms in the UK seeking behavioral biometrics integration without premium vendor-managed tiers. Go-to-market leverage rests with GDPR-specific incident response expertise and fixed-fee rule-tuning packages that disintermediate legacy vendor professional services. For Investors and Strategic Acquirers: Re-rating potential sits with vertical-specialist WAF vendors possessing pre-certified EU AI Act conformity assessment documentation given accelerating compliance-driven procurement cycles across French and German financial institutions. Long-term viability over the projection horizon favors vendors with multi-cloud orchestration capabilities and immutable audit logging architectures. Signal to watch: ENISA cloud-security certification scheme finalization unlocking public sector procurement framework access.| Strategic Initiative | Industry Significance |
|---|---|
| API Security Platform Integration | Consolidates Layer 7 inspection with bot management for PSD2-compliant open banking gateways. |
| Edge-Native Deployment Expansion | Positions vendors for German automotive OTA update channel protection and connected vehicle API security. |
| Regulatory Workflow Partnership | Accelerates EU AI Act documentation compliance for French banking conglomerates via pre-built audit modules. |
| Multi-Cloud Orchestration Development | Eliminates single-point-of-failure exposure for Dutch critical infrastructure operators under NIS2 resilience mandates. |
| Behavioral Biometrics Acquisition | Enables frictionless human-bot distinction for UK e-commerce platforms facing mobile checkout fraud migration. |
Research Methodology
Multi-period observation of WAF procurement cycles, compliance deadline acceleration patterns, and vendor pricing disclosures anchored the trend analysis, supplemented by interviews with CISOs at German banking conglomerates, cloud infrastructure procurement officers at Dutch payment processors, regulatory affairs leads at French automotive suppliers, and MSSP operations directors across the Nordics. Secondary validation drew from ENISA threat landscape reports, national data protection authority enforcement actions, SEC filings of publicly traded cybersecurity vendors, hyperscaler capex disclosures for European edge network expansion, and trade data on networking equipment imports. Bottom-up segment sizing triangulated against top-down market aggregation from technology spending surveys.
Segment-weighting across deployment models, industry verticals, and organization size tiers structured the analytical framework, with cloud-native versus on-premises splits calibrated to infrastructure refresh cycle data. Deployment architecture, compliance exposure level, and regional regulatory cluster shaped the segmentation dimensions modeled across the projection horizon. CAGRs derived from fitted growth curves incorporating compliance deadline impacts, talent scarcity effects on managed services demand, and substitution dynamics from adjacent API security categories. Forecast inputs included ENISA certification timeline scenarios and NIS2 enforcement phase-in assumptions.
Forecast precision tightens around the base case; tail outcomes carry wider variance under accelerated EU AI Act enforcement or prolonged cloud-security certification delays. Forecasts reflect documented assumptions regarding regulatory implementation schedules, talent pipeline development, and hyperscaler competitive positioning. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Patch Management Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Europe Digital Forensics Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
Wireless Network Security Market
Cybersecurity
North America Extended Detection and Response Market
Cybersecurity
E-Mail Security Market
Cybersecurity
South Korea Cybersecurity Market
Cybersecurity
Cloud-Based Database Security Market
Cybersecurity
Network Traffic Analysis Solutions Market
Cybersecurity
Indonesia Cybersecurity Market
Cybersecurity
IoT Security Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
SSL VPN Market