
 IT and Telecom Cyber Security Market | 2026-2036
IT and Telecom Cyber Security Market Size, Share, and Industry Trends Forecast 2026-2036
IT and Telecom Cyber Security Market Intelligence
The gap between premium zero-trust architectures and commodity firewall bundles is broadening as telecom operators face diverging risk profiles. Palo Alto Networks leverages cloud-native platform consolidation to capture high-complexity enterprise accounts. Fortinet anchors its position through integrated SD-WAN and security fabric scale across mid-market telecom resellers. CrowdStrike differentiates via endpoint detection and response telemetry that feeds directly into operator security operations centers.
IT and telecom cyber security encompasses the hardware, software, and service layers that protect network infrastructure, subscriber data, and signaling systems from unauthorized access, disruption, or exploitation. Core functional parameters include sub-100-millisecond threat detection latency, 99.999% availability for inline security controls, and AES-256 encryption for data-in-transit across multi-vendor network elements. Endpoint security and managed services represent the fastest-expanding margin pools as operators outsource 24/7 security operations rather than building in-house Security Operations Centers. Cloud deployment models are displacing on-premise appliances in greenfield 5G cores, though hybrid architectures dominate brownfield telecom transformations where legacy signaling equipment persists.
NIST cybersecurity frameworks, the EU Cybersecurity Act, and FCC supply chain security rules collectively mandate baseline encryption, vendor risk assessment, and incident reporting timelines that reshape procurement specifications and market access conditions. Compliance with these overlapping regimes now functions as a competitive filter that excludes smaller vendors lacking certification resources. Stakeholders must monitor how quantum-resistant cryptography standards from NIST and ETSI redefine product roadmaps before regulatory deadlines harden into binding procurement requirements.
Market Dynamics
Cloud-native security platforms are compressing deployment cycles for 5G standalone cores, forcing vendors to abandon appliance-centric architectures in favor of containerized, API-first delivery models that align with operator DevOps pipelines.
Growth Catalysts
- NIST Zero-Trust Framework:Federal mandates in the United States require continuous verification architectures, driving procurement of microsegmentation and identity-aware proxies across critical infrastructure operators.
- 5G Standalone Deployments:Mobile network operators in Germany and Japan are greenfielding security stacks that embed threat detection directly into service-based architectures rather than bolting on perimeter controls.
- EU Cybersecurity Act Certification:Common Criteria-based product approvals create harmonized market access across member states, reducing fragmentation costs for vendors targeting pan-European telecom groups.
Market Restraints
- Semiconductor Supply Concentration:Specialized ASICs for inline encryption and deep packet inspection concentrate fabrication among Taiwan-based foundries, exposing lead time volatility for security appliance vendors.
- Legacy Signaling Integration:SS7 and Diameter protocol stacks in brownfield cores resist API-based security instrumentation, forcing parallel overlay architectures that inflate total cost of ownership.
- Quantum-Resistant Migration Costs:NIST post-quantum cryptography standards impose certificate and key management overhauls that strain R&D budgets before regulatory deadlines crystallize.
Strategic Opportunities
- Managed Detection and Response:Tier-two mobile operators in India outsource 24/7 security operations to specialized providers, creating recurring revenue pools that bypass capital-intensive SOC buildouts.
- Confidential Computing:Hardware-based trusted execution environments from Intel SGX and AMD SEV converge with Kubernetes orchestration to protect subscriber data during active processing in multi-tenant cloud cores.
- Open RAN Security Instrumentation:Disaggregated radio access networks in the United States mandate embedded security agents at the O-RAN distributed unit and radio unit boundaries, opening new attach points for specialized vendors.
Industry Challenges
- Multi-Cloud Security Operations:Operators spanning AWS, Azure, and private edge clouds struggle with inconsistent policy enforcement and telemetry correlation across disparate control planes.
- Certification Timeline Compression:Common Criteria evaluations and FIPS 140-3 validations now span 18-24 months, lagging product release cycles and freezing feature roadmaps during assessment windows.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | IT and Telecom Cyber Security Market |
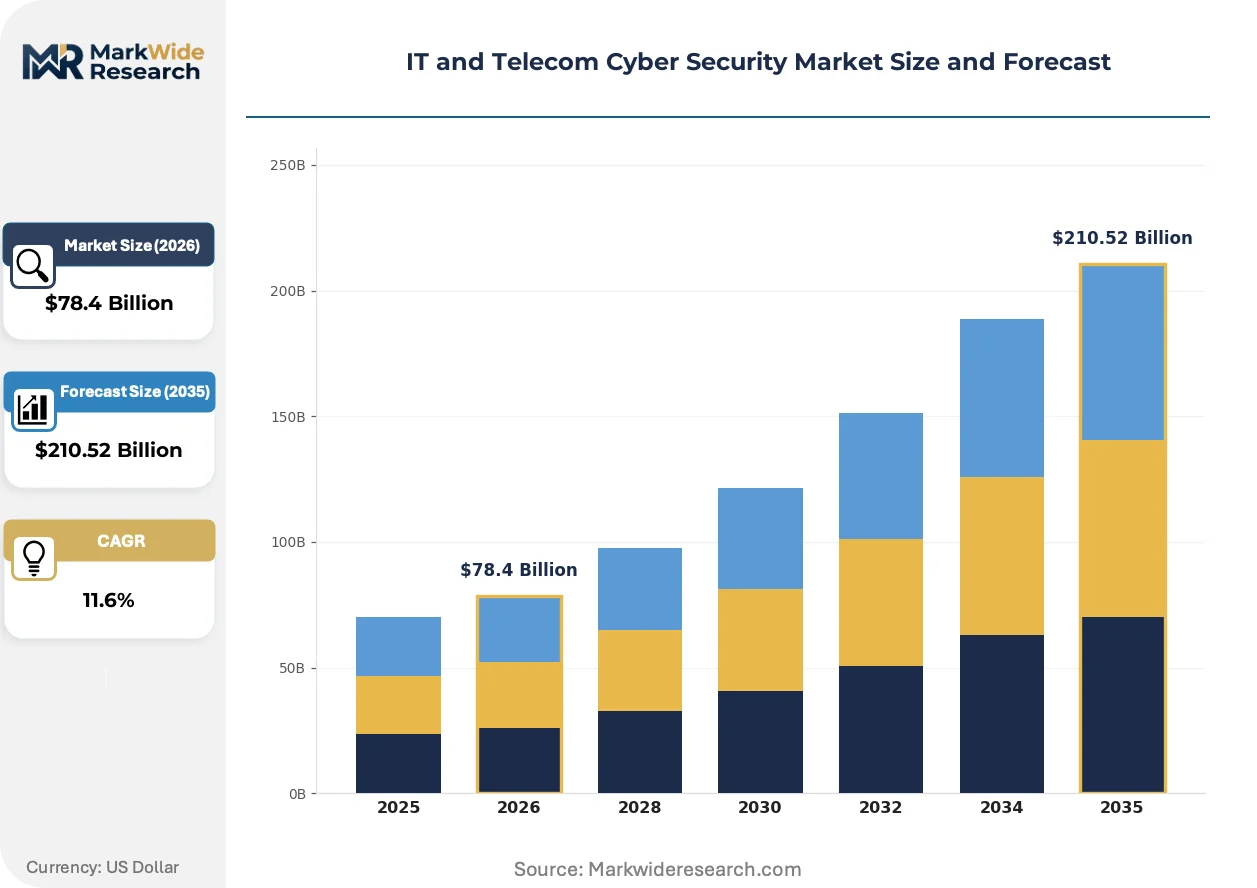
| Market Size in 2026 | $78.4 Billion |
| Market Size in 2035 | $210.52 Billion |
| CAGR (2026 – 2036) | 11.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Intrusion Detection System, Firewall, Endpoint Security, Application Security Deployment Model: On-Premise, Cloud, Hybrid, Managed End User: Telecom Operators, Enterprises, Government Agencies, SMEs Service Type: Consulting, Implementation, Training, Managed Services |
| Companies Covered | Cisco Systems, Check Point Software Technologies, Palo Alto Networks, Microsoft Security, IBM Security, CrowdStrike, Zscaler, Trellix, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
IT and Telecom Cyber Security Market Strategic Shifts & Innovations
Security delivery models are fragmenting across cloud-native, hybrid, and edge-native architectures as operators reconcile divergent latency, sovereignty, and cost constraints across their infrastructure footprints.
Extended detection and response platforms are unifying endpoint, network, and identity telemetry into single-pane security operations centers. Tier-one operators in Japan and Germany deploy these consolidated stacks to collapse mean-time-to-detection below 100 milliseconds. This unification compresses vendor consolidation cycles, marginalizing point-product specialists who lack cross-domain correlation engines.
The EU Cybersecurity Act's certification schemes for ICT products are hardening procurement pre-qualification requirements across member states. Hardware and software vendors must now obtain Common Criteria or EUCC ratings before bidding on critical digital infrastructure contracts. German telecom incumbents have restructured supplier onboarding to front-load certification validation, extending evaluation timelines but reducing downstream compliance risk.
Subscription-based security consumption is displacing perpetual license purchases among mid-market operators facing capital expenditure constraints. Managed security service providers in the United States now capture 60% of new endpoint protection deployments through usage-based pricing that scales with subscriber volumes. This shift favors vendors with native multi-tenant architectures over those dependent on on-premise appliance refreshes.
IT and Telecom Cyber Security Market Segmentation
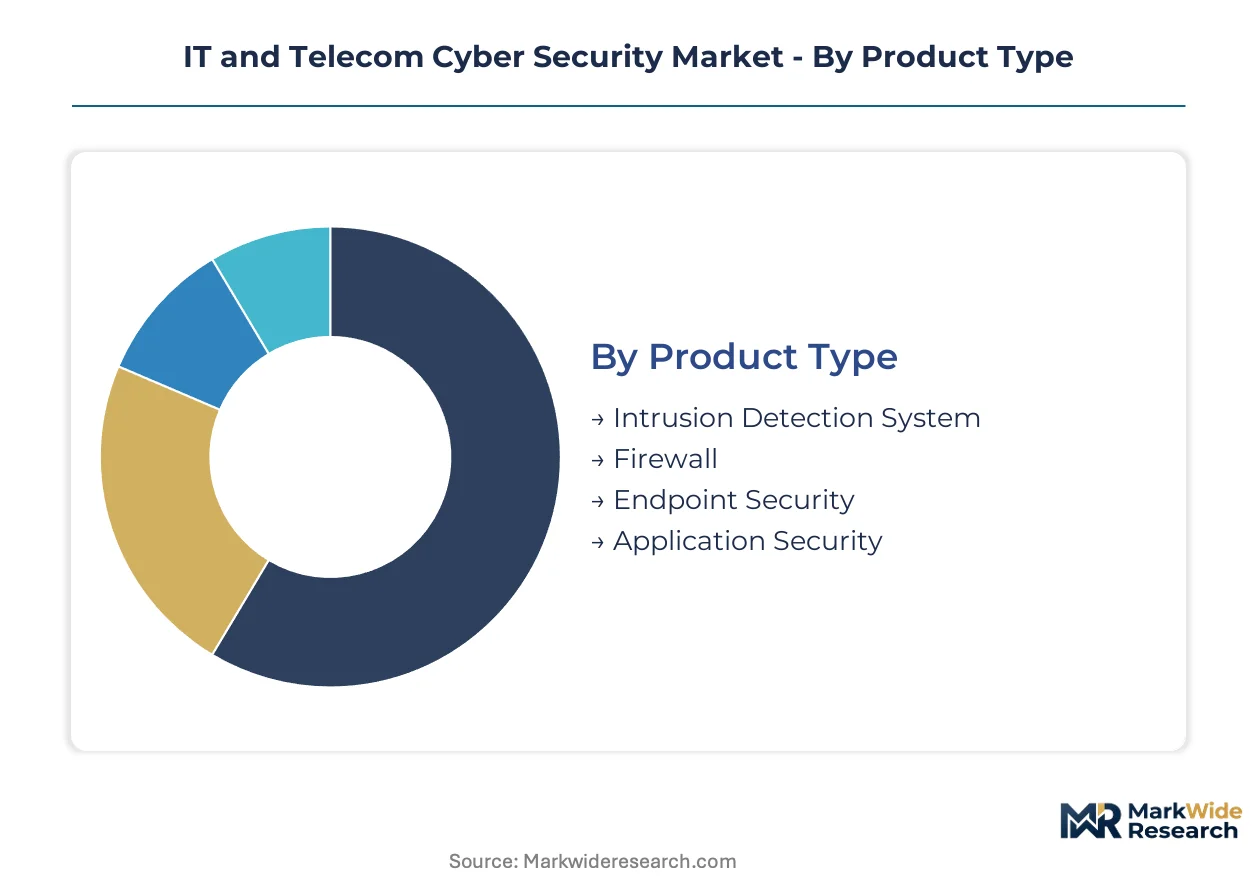
IT and telecom cyber security procurement fragments across product architectures, delivery models, and buyer sophistication levels. Understanding these divides reveals where vendor R&D investments concentrate and which customer profiles drive margin expansion.
Product Type:
Supply concentration tilts toward platforms integrating multiple control layers rather than standalone appliances, compressing margins for point-product specialists.
- Endpoint Security:Agent-based protection for subscriber devices and operator workstations leverages kernel-level telemetry to detect fileless malware. German mobile operators deploy these agents across millions of IoT endpoints, driven by EU Cybersecurity Act certification mandates for critical infrastructure.
- Firewall:Next-generation firewalls with deep packet inspection and application-layer visibility form the perimeter backbone for brownfield telecom cores. United States tier-one carriers prioritize models with FIPS 140-3 validation to satisfy federal procurement rules.
- Intrusion Detection System:Network traffic analyzers with signature and behavioral detection capabilities monitor signaling plane anomalies.
- Application Security:Runtime protection and code-scanning tools secure microservices in containerized 5G cores.
Endpoint Security absorbs the bulk of installed capacity; Application Security is expanding most quickly.
Deployment Model:
Cost tier differentiation separates capital-intensive on-premise builds from operational expenditure models favored by mid-market operators.
- Cloud:Containerized security functions delivered via API integrate directly into operator DevOps pipelines for greenfield 5G standalone cores. Japanese mobile network operators lead adoption here, compressing deployment cycles from months to weeks.
- Managed:Outsourced 24/7 security operations transfer SOC burden to specialized providers under subscription contracts. Indian tier-two operators favor this model to bypass talent scarcity and infrastructure buildout costs.
- Hybrid:Split architectures preserve on-premise controls for legacy signaling while cloud-native functions handle new service-based interfaces.
- On-Premise:Appliance-based deployments persist where data sovereignty or latency constraints prohibit off-premises processing.
Managed deployments are climbing the fastest as outsourcing appetite grows; On-Premise retains the largest installed base.
End User:
Volume concentration among telecom operators shapes feature roadmaps, while government agencies impose the strictest certification requirements.
- Telecom Operators:Mobile and fixed-line carriers demand sub-100-millisecond threat detection latency and 99.999% availability for inline controls. United States operators face additional FCC supply chain security rules that reshape vendor qualification.
- Government Agencies:National security and defense communications bodies require Common Criteria EAL4+ or higher ratings. German federal networks mandate these certifications for all critical digital infrastructure procurement.
- Enterprises:Large corporations with private 5G networks seek security stacks mirroring operator-grade capabilities at smaller scale.
- SMEs:Small and medium enterprises rely heavily on managed service providers for security coverage without internal expertise.
Telecom Operators command the dominant share of vendor attention; SMEs represent the steepest expansion trajectory as private 5G adoption broadens.
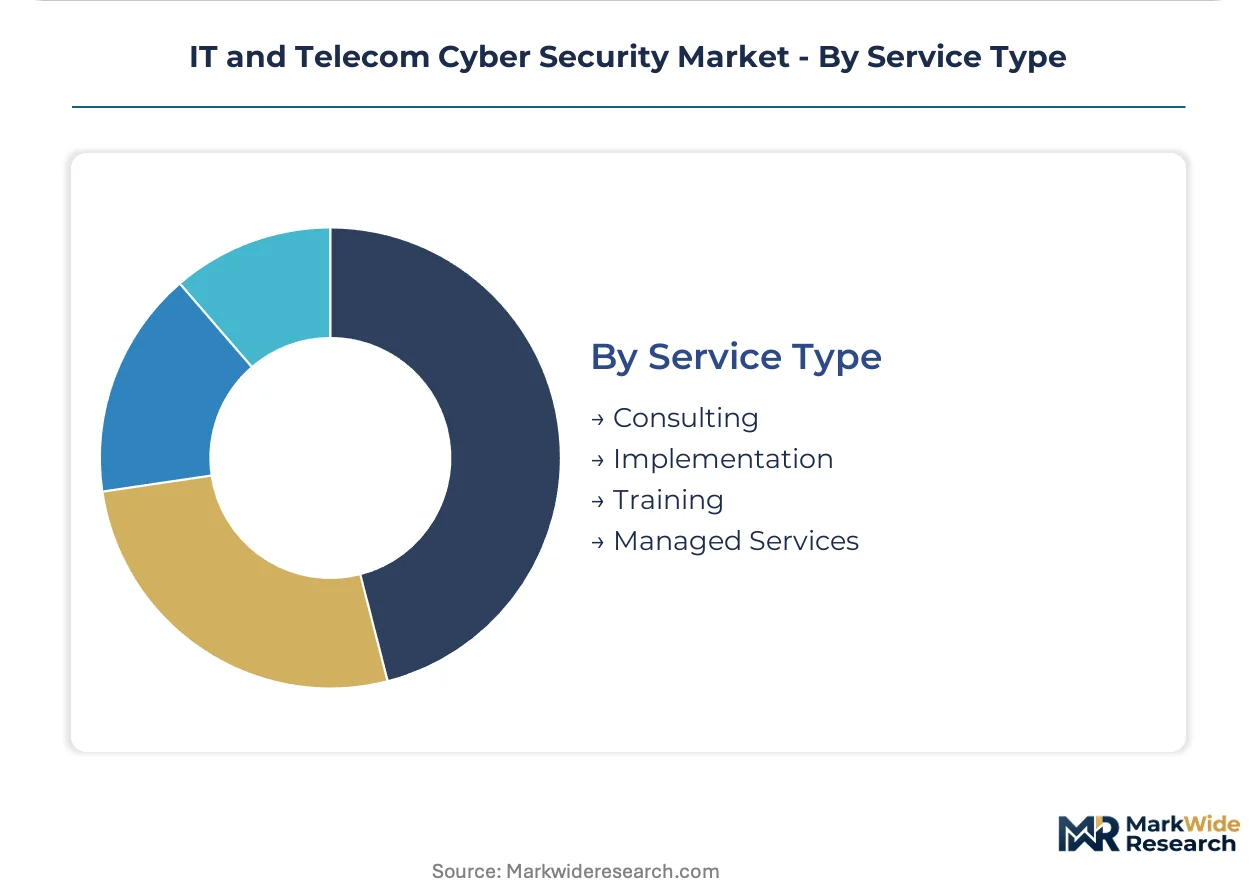
Service Type:
Margin structure favors recurring revenue streams over one-time professional engagements, reorienting vendor business models.
- Managed Services:Continuous monitoring, threat hunting, and incident response delivered under multi-year contracts. United States providers capture the majority of new endpoint deployments through usage-based pricing tied to subscriber volumes.
- Consulting:Risk assessment, architecture design, and compliance gap analysis for pre-deployment planning. Japanese operators engage these services heavily for zero-trust transformation roadmapping.
- Implementation:Deployment, integration, and tuning of security technologies within existing network stacks.
- Training:Operator staff certification programs for security tool administration and threat response.
Managed Services dominates revenue recurrence; Consulting shows the fastest growth as zero-trust mandates drive pre-deployment advisory demand.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley anchors security innovation for telecom infrastructure, with venture deployment clustering around San Jose and San Francisco corridors where cloud-native security architectures incubate before scaling to operator networks.
United States
FCC supply chain security rules and NIST zero-trust mandates drive procurement of microsegmentation platforms across tier-one carriers. Federal infrastructure operators in the Washington DC metro area require FIPS 140-3 validated controls for all critical network equipment. Security vendors concentrate engineering resources in Northern Virginia data center corridors to support federal and commercial operator demand simultaneously.
Germany
EU Cybersecurity Act certification schemes reshape vendor qualification timelines for Deutsche Telekom and Vodafone infrastructure divisions. German federal networks mandate Common Criteria EAL4+ ratings for critical digital infrastructure procurement under national security regulations. Berlin and Munich host the primary security operations centers serving pan-European telecom groups undergoing 5G standalone transformations.
Japan
NTT Docomo and KDDI embed threat detection directly into service-based 5G core architectures rather than perimeter overlays. METI industrial security guidelines accelerate confidential computing adoption for subscriber data protection in multi-tenant cloud environments. Tokyo and Osaka metropolitan areas concentrate security engineering talent for operator-grade latency requirements below 100 milliseconds.
India
Tier-two mobile operators in Mumbai and Bengaluru outsource security operations to managed detection and response providers under usage-based subscription contracts. TRAI data localization requirements mandate domestic processing of subscriber metadata, favoring indigenous security vendors with certified data centers. Hyderabad and Pune emerging as secondary hubs for telecom security implementation services.
United Kingdom
NCSC telecommunications security guidance imposes supply chain assurance requirements on BT Group and Virgin Media O2 infrastructure refresh programs. London financial district proximity drives demand for security stacks mirroring operator-grade capabilities in private 5G enterprise deployments. Cambridge security research clusters feed specialized cryptographic talent into national telecom infrastructure protection programs.
IT and Telecom Cyber Security Market Key Industry Players
Premium-margin players sit above commodity-margin players across certification complexity and cloud-native architecture maturity. The vendor base stratifies into three tiers: platform consolidators with multi-product integration, point-product specialists with deep protocol expertise, and managed service wrappers with operator outsourcing relationships. Consolidation pressure intensifies as procurement committees favor vendors with Common Criteria and FIPS pre-certification. Competitive moves center on API-first delivery model development and DevOps pipeline integration partnerships.
Within the platform consolidator tier, Palo Alto Networks and Cisco Systems exemplify cloud-native architecture strategies that compress deployment cycles for 5G standalone cores. Fortinet occupies a position bridging mid-market scale with integrated SD-WAN and security fabric delivery. CrowdStrike represents the endpoint-centric archetype where telemetry feeds directly into operator security operations centers. Check Point Software Technologies anchors the perimeter-specialist segment with deep packet inspection heritage adapted for signaling plane protection.
| Leading Market Players |
|---|
| Cisco Systems |
| Check Point Software Technologies |
| Palo Alto Networks |
| Microsoft Security |
| IBM Security |
| CrowdStrike |
| Zscaler |
| Trellix |
| Fortinet |
| Others |
Cost & Logistics Intelligence
Private-equity-rolled-up managed security service providers now dominate mid-market distribution channels, compressing pricing discipline for point-product vendors while amplifying volume leverage for platform consolidators with multi-tenant architectures.
Pricing Analysis
Outcome-based pricing tied to threat detection latency and mean-time-to-response anchors enterprise procurement negotiations. Subscription-SaaS tiering dominates as managed security service providers in the United States capture endpoint deployments through usage-based contracts scaling with subscriber volumes. Price differentiation rests on Common Criteria certification grade and FIPS 140-3 validation status, with federal-compliant vendors commanding premium positioning. Cost compression in mid-market firewall bundles intensifies as appliance-centric specialists lose share to cloud-native platform consolidators. Tier-two mobile operators in India exhibit highest price sensitivity, while German federal networks show least sensitivity due to mandated security spending floors.
Supply Chain Analysis
Certification and qualification gating through Common Criteria evaluation facilities and FIPS 140-3 testing laboratories concentrates vendor onboarding timelines. Specialized ASIC fabrication concentrates in Taiwan and South Korea, with advanced packaging capabilities anchoring in the United States. Deep packet inspection chipsets, hardware security modules, and trusted execution environment processors constitute critical input dependencies. Single-source vulnerability around Taiwan-based foundry capacity exposes lead time volatility for inline encryption appliance vendors. Distribution runs through authorized telecom equipment distributors and direct federal procurement channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Cloud-native security instrumentation is displacing legacy appliance stacks across 5G standalone cores, forcing procurement committees to requalify vendor rosters around containerized delivery models.
For Market Incumbents: To counter margin erosion from subscription-based consumption models, accelerate API-first platform consolidation and deepen backward integration into hardware security module manufacturing. Fortify certification moats by front-loading Common Criteria EAL4+ and FIPS 140-3 validation investments ahead of EU Cybersecurity Act enforcement deadlines. For New Entrants and Emerging Players: Begin with confidential computing specialization for multi-tenant cloud cores, targeting tier-two mobile operators in India and private 5G enterprise deployments in the United Kingdom. Channel partnerships with systems integrators familiar with NIST zero-trust implementation offer the most penetrable go-to-market angle against entrenched platform vendors. For Investors and Strategic Acquirers: NIST post-quantum cryptography standard finalization is the leading indicator that quantum-resistant migration services will command premium valuations. Acquisition targets should display pre-certified cryptographic libraries and existing operator DevOps pipeline integrations. Watch for EU Cybersecurity Act certification backlog clearance as the signal that pan-European vendor consolidation will accelerate.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidated telemetry feeds from Palo Alto Networks and CrowdStrike collapse detection latency below 100 milliseconds for Japanese operators. |
| Certification Pre-Investment | Early FIPS 140-3 validation secures federal procurement eligibility before NIST zero-trust mandates harden. |
| Managed Service Wrapper | Outsourced SOC contracts bypass capital constraints for Indian tier-two operators facing talent scarcity. |
| Confidential Computing Partnership | Intel SGX and AMD SEV integrations protect subscriber data in German multi-tenant cloud cores. |
| Open RAN Security Instrumentation | Embedded agents at O-RAN DU/RU boundaries capture United States federal infrastructure refresh demand. |
Research Approach
Document review covered NIST cybersecurity framework publications, EU Cybersecurity Act implementing regulations, FCC supply chain security orders, and ETSI quantum-resistant cryptography standards, complemented by interviews with chief information security officers at tier-one mobile operators, federal procurement officers, managed security service provider executives, and semiconductor fabrication specialists. Secondary validation drew from SEC 10-K cybersecurity risk disclosures, Common Criteria evaluation facility reports, and hyperscaler security capex announcements. Bottom-up deployment modeling across 5G standalone core greenfield sites was triangulated against top-down telecom operator security spending surveys.
Historical deployment trajectories in Germany, Japan, and the United States were cross-referenced against panel input from security vendor product managers and operator network architects. Segmentation modeling spanned product architecture, deployment model, buyer sophistication tier, and regional regulatory cluster. CAGRs were derived from slope analysis of annual security spending intensity per subscriber across the projection horizon. Forecast inputs incorporated 5G standalone core rollout schedules, NIST post-quantum cryptography migration timelines, and EU Cybersecurity Act certification queue depths.
Underlying measurement precision varies by segment; cloud-native deployment forecasts carry tighter precision than legacy appliance refresh projections due to disclosed hyperscaler partnership volumes. Forecasts reflect documented assumptions regarding regulatory deadline adherence and foundry capacity allocation. A model refresh is warranted upon material change in NIST quantum-resistant cryptography standard publication or Taiwan semiconductor export restriction expansion.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Digital Forensic Laboratory As a Service Market
Cybersecurity
E-Mail Security Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Nigeria Cybersecurity Market
Cybersecurity
Enterprise Mobility Security Market
Cybersecurity
Global Serverless Security Market
Cybersecurity
Data Center Logical Security Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Global Mobile Application Security Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Cyber Security Consulting Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Education Data Security Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Global Cyber Security in Healthcare Market