
 Global Serverless Security Market | 2026-2036
Global Serverless Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Serverless Security Market Foresight
Enterprise-grade runtime protection is redrawing competitive boundaries in serverless security. Palo Alto Networks leverages deep packet inspection capabilities to anchor its position in threat detection for distributed functions. Microsoft Corporation sustains momentum through native integration with Azure Functions and Logic Apps. Aqua Security specializes in container-to-serverless continuity, occupying a narrow but defensible niche in workload-centric security.
Serverless security encompasses the policies, tools, and practices that protect event-driven computing architectures where cloud providers dynamically manage infrastructure allocation. Core functional parameters include sub-second function spin-up monitoring, ephemeral storage encryption, and least-privilege identity validation across stateless execution environments. Runtime protection and threat detection command the largest margin pools within the security offering dimension, while identity and access management retains foundational status across all deployment configurations. The multicloud segment is expanding fastest as enterprises distribute serverless workloads across AWS Lambda, Azure Functions, and Google Cloud Run to avoid vendor lock-in.
The EU AI Act and GDPR impose strict data residency and automated decision-making audit requirements that directly shape serverless security procurement criteria in Europe. The US SEC cybersecurity disclosure rules and HIPAA mandate granular access logging, pushing healthcare and financial services buyers toward compliance management modules with real-time telemetry. Stakeholders must weigh the trade-off between native cloud provider security stacks and third-party specialized platforms as function density and cross-cloud orchestration complexity intensify.
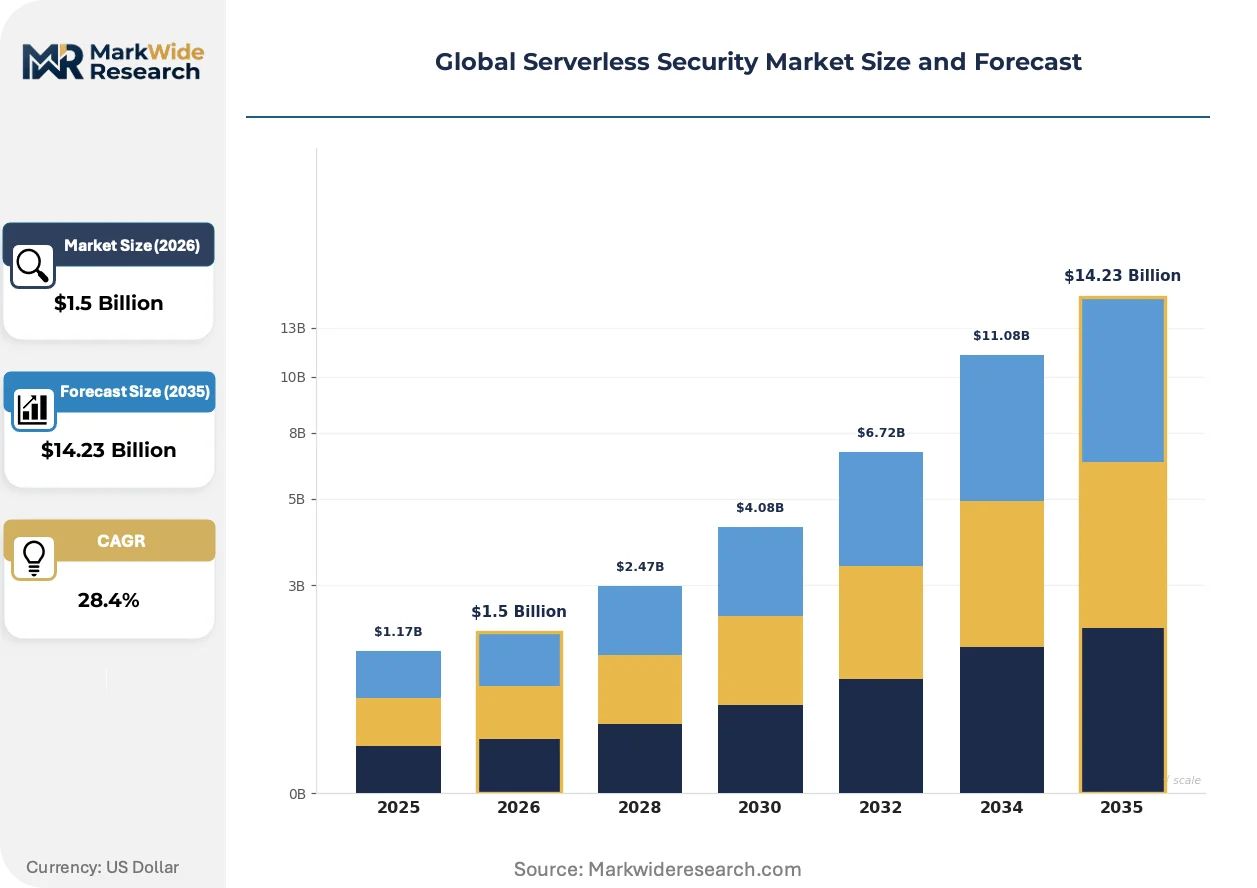
Market Dynamics
Multicloud workload distribution is fragmenting procurement patterns across the serverless security landscape, forcing vendors to engineer portable runtime protection that transcends native cloud provider stacks.
Growth Catalysts
- GDPR Article 32 mandates:European enterprises must implement encryption and access controls for automated processing systems, accelerating investment in serverless-native data protection modules.
- Financial services runtime hardening:Banks and payment processors deploying AWS Lambda and Azure Functions require sub-second threat detection for transaction flows, creating specialized demand for ephemeral workload monitoring.
- Container-to-serverless migration pipelines:DevOps teams extending Kubernetes security postures into function-as-a-service environments are consolidating vendor relationships around workload-centric platforms.
Market Restraints
- Cloud provider security bundling:AWS Shield, Azure Security Center, and Google Cloud Armor embed baseline protections at marginal cost, compressing pricing power for standalone serverless security vendors.
- Skills concentration in California and New York:Serverless architecture expertise clusters in coastal technology hubs, constraining enterprise deployment velocity in secondary US markets and European industrial centers.
- Function cold-start latency trade-offs:Deep packet inspection and runtime behavioral analysis add milliseconds to invocation times, conflicting with performance requirements in high-frequency trading and real-time analytics applications.
Strategic Opportunities
- India's BIS cloud security framework:Emerging data localization requirements for financial and government workloads are creating first-mover advantages for serverless security vendors establishing local engineering presence.
- Edge-to-core orchestration convergence:5G network slicing and IoT function deployment at telecom edge nodes is extending serverless security requirements to distributed infrastructure previously managed separately.
- EU AI Act automated decision auditing:Compliance mandates for explainability in AI-driven serverless functions are opening specialized markets for runtime logging and decision-traceability tools.
Industry Challenges
- Ephemeral forensics expertise:Security operations teams lack training in evidence preservation for stateless execution environments where function instances terminate within seconds, complicating incident response.
- Cross-cloud identity federation complexity:Synchronizing least-privilege policies across AWS IAM, Azure Active Directory, and Google Cloud IAM requires architectural investment that delays multicloud security deployments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Serverless Security Market |
| Market Size in 2026 | $1.5 Billion |
| Market Size in 2035 | $14.23 Billion |
| CAGR (2026 – 2036) | 28.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Multicloud Security Offering: Identity & Access Management, Threat Detection, Data Encryption, Compliance Management, Runtime Protection Use Case: Microservices Security, API Security, Function Monitoring, Event Monitoring, Configuration Management End User Industry: Telecommunications, Manufacturing, Government, Education, Media & Entertainment |
| Companies Covered | Amazon Web Services, Microsoft Corporation, Google, Palo Alto Networks, Imperva, IBM, Oracle, Aqua Security, Rackspace Technology, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Serverless Security Market Shifts & Advancements
Agentless runtime monitoring architectures are overtaking traditional endpoint-based approaches, enabling security telemetry extraction without function performance degradation or code modification requirements.
eBPF-based kernel instrumentation is displacing conventional agent deployments in serverless environments. Cloud-native enterprises in California and New York are piloting this technology for zero-overhead visibility into function execution. The approach is displacing legacy sidecar proxy architectures that added latency and resource overhead to ephemeral workloads.
EU AI Act algorithmic accountability requirements are mandating runtime logging for automated decision systems. Financial services institutions deploying credit-scoring and fraud-detection functions must now maintain immutable audit trails of inference inputs and outputs. European banks are responding by integrating compliance modules directly into CI/CD pipelines for serverless deployment.
Consolidated security procurement is replacing point-solution buying for serverless protection. Enterprise CISOs in healthcare and financial services are bundling runtime monitoring, encryption, and identity management under single-vendor contracts to reduce operational complexity. This pattern is most visible in the United States, where SEC cybersecurity disclosure rules intensify board-level scrutiny of vendor fragmentation.
Global Serverless Security Market Segmentation
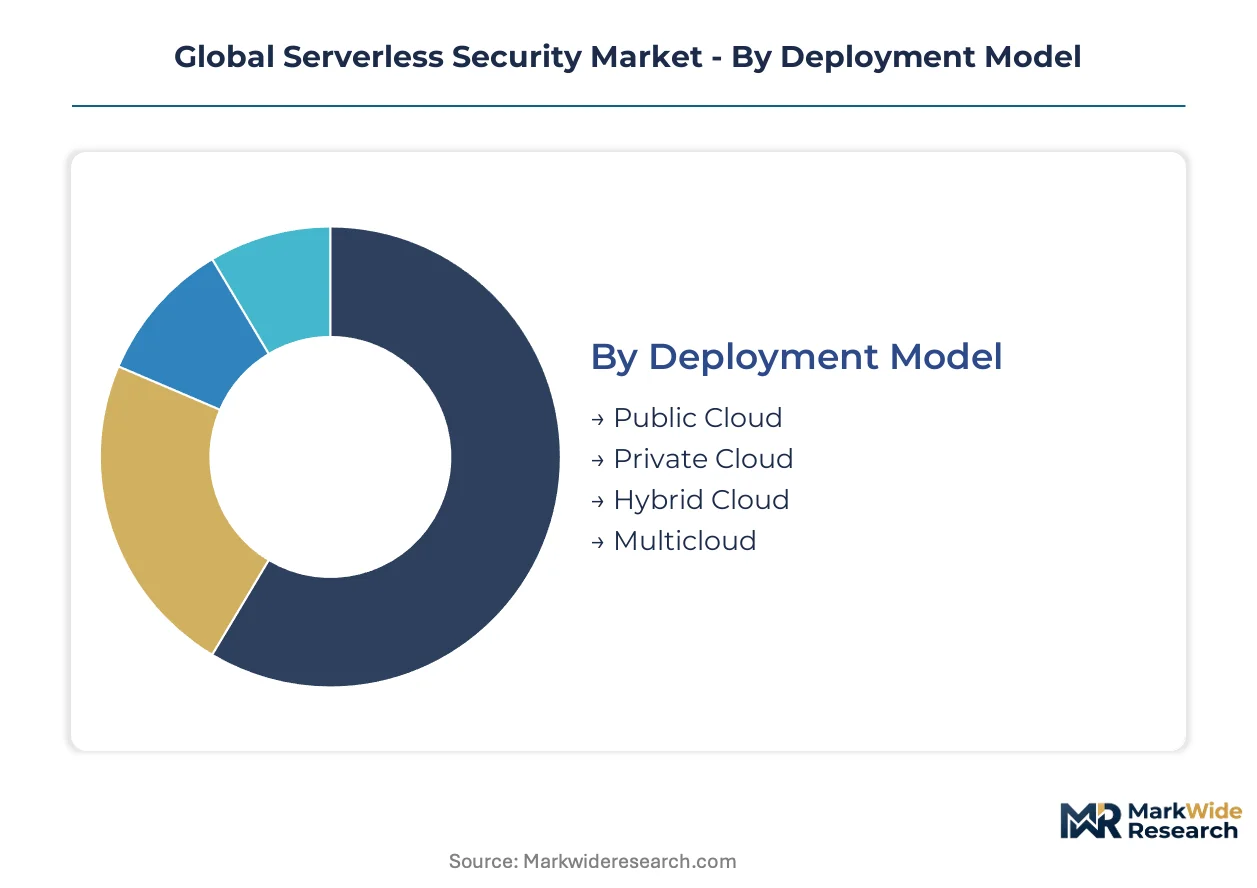
Serverless security procurement patterns diverge sharply across deployment architectures and workload types. Buyers prioritize runtime protection for financial transaction flows while favoring compliance modules for regulated healthcare and government environments.
Deployment Model:
Margin pools concentrate in multicloud configurations where portability premiums offset engineering complexity.
- Public Cloud:Native AWS Lambda, Azure Functions, and Google Cloud Run security stacks dominate transaction volume. Financial services institutions in California and New York default to these environments for rapid function deployment despite vendor lock-in risks.
- Multicloud:Workload distribution across AWS, Azure, and Google Cloud Run commands pricing premiums for portable runtime protection. European banks facing GDPR data residency mandates are accelerating investment here to maintain cross-border operational continuity.
- Private Cloud:On-premises function platforms serve defense and intelligence agencies with air-gapped requirements. Government buyers in Germany and France specify these deployments for classified workload processing.
- Hybrid Cloud:Split architectures spanning owned data centers and public cloud functions address legacy system integration needs. Manufacturing firms in Japan deploy these configurations to bridge ERP systems with cloud-native analytics.
The dominant share belongs to Public Cloud, while Multicloud is closing the gap fastest.
Security Offering:
Application intensity varies by regulatory exposure, with runtime protection and compliance management seeing concentrated investment from SEC-regulated and HIPAA-covered entities.
- Runtime Protection:Sub-second threat detection for ephemeral function instances anchors enterprise procurement. Banks deploying credit-scoring functions require behavioral analysis that terminates malicious invocations before transaction completion.
- Threat Detection:Deep packet inspection and anomaly identification for event-driven architectures. Healthcare systems in Texas and Florida prioritize these capabilities for PHI-access monitoring in serverless EMR integrations.
- Identity & Access Management:Least-privilege validation across stateless execution environments. Cross-cloud IAM synchronization challenges delay deployment timelines for multinational enterprises.
- Data Encryption:Ephemeral storage and transit protection for function inputs and outputs. EU AI Act mandates are pushing automated decision systems toward enhanced encryption protocols.
- Compliance Management:Audit logging and policy enforcement for regulated industries. HIPAA and SEC disclosure rules drive healthcare and financial services adoption of integrated compliance modules.
Runtime Protection holds the largest revenue concentration, though Compliance Management is expanding most quickly under regulatory pressure.
Use Case:
Volume concentrates in API security as microservices architectures proliferate across cloud-native enterprises.
- API Security:Authentication, rate limiting, and payload inspection for serverless API gateways. E-commerce platforms in India and Brazil deploy these protections for payment processing functions.
- Microservices Security:Service mesh integration and inter-function traffic monitoring. Container-to-serverless migration pipelines are consolidating vendor relationships around workload-centric platforms.
- Function Monitoring:Performance and behavioral telemetry for individual function instances. DevOps teams in Singapore use these tools to optimize cold-start latency and resource allocation.
- Event Monitoring:Trigger source validation and event stream analysis. IoT function deployments at telecom edge nodes are extending requirements to distributed 5G infrastructure.
- Configuration Management:Infrastructure-as-code security scanning and drift detection. Misconfiguration remains the dominant breach vector in serverless environments.
API Security commands the dominant deployment volume, with Microservices Security climbing fastest as Kubernetes adoption extends into function-as-a-service environments.
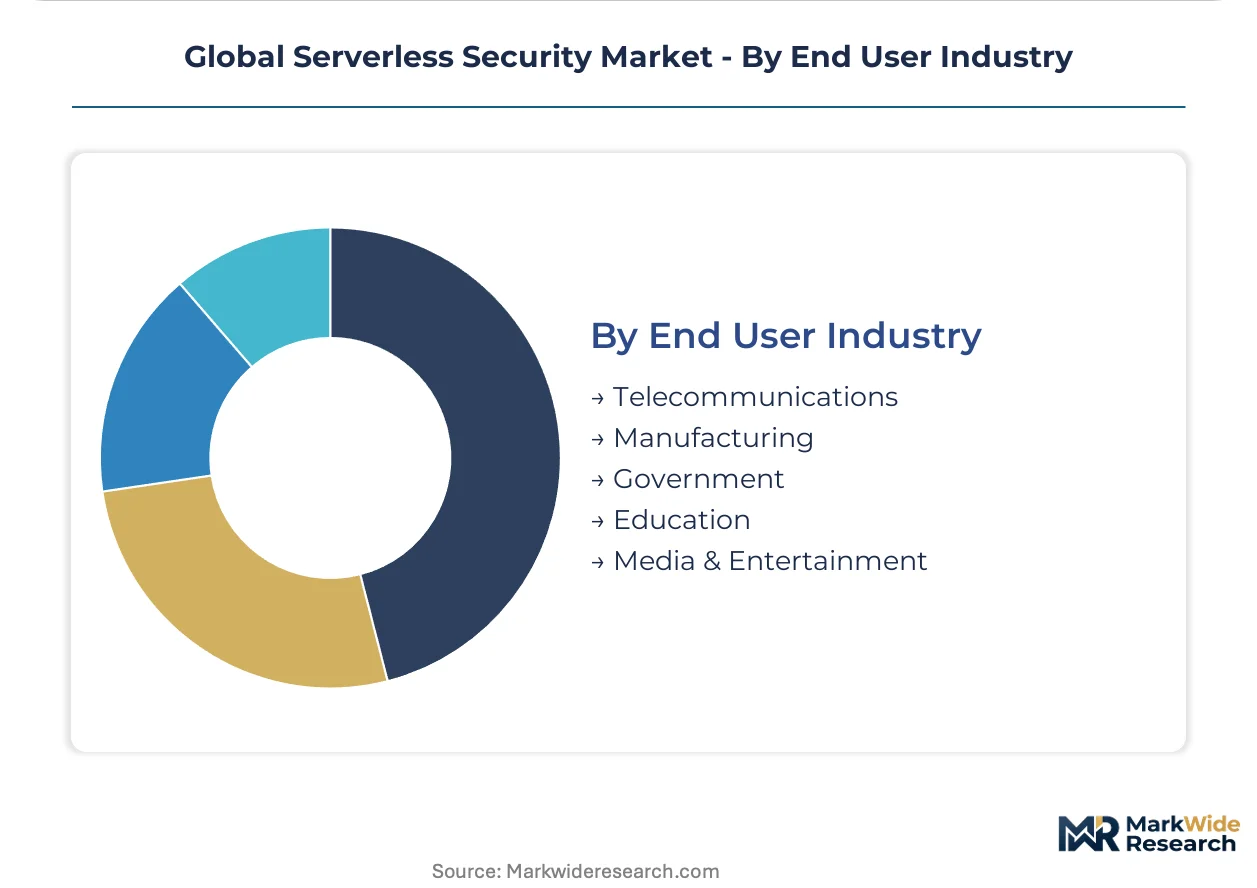
End User Industry:
Customer type determines procurement sophistication, with telecommunications and government buyers driving specification complexity.
- Telecommunications:5G network slicing and edge function security for distributed infrastructure. Indian carriers responding to BIS cloud security frameworks are localizing serverless deployments for subscriber data protection.
- Government:Classified workload protection and supply chain security for national infrastructure. FedRAMP and EU cybersecurity certification schemes filter vendor eligibility for public sector contracts.
- Manufacturing:OT/IT convergence security for industrial IoT functions. German automotive suppliers deploy these protections for predictive maintenance pipelines.
- Media & Entertainment:Content delivery and streaming function protection. Live event platforms require sub-second scaling with embedded DDoS mitigation.
- Education:Research computing and student data protection for cloud-native learning platforms. University systems prioritize cost efficiency over advanced threat detection capabilities.
Telecommunications holds the dominant procurement volume, while Government is gaining share fastest under tightening cybersecurity certification mandates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Serverless security vendor engineering and sales operations concentrate heavily in the United States, with secondary clusters in Western Europe and emerging buildouts in India and Japan. Cloud provider headquarters and specialized security software development drive this geographic pattern.
United States
Financial services institutions in California and New York drive enterprise procurement of runtime protection for AWS Lambda and Azure Functions deployments. SEC cybersecurity disclosure rules mandate granular access logging, pushing healthcare and financial services buyers toward compliance management modules with real-time telemetry. The San Francisco Bay Area and Manhattan host the densest concentrations of serverless architecture expertise, constraining deployment velocity in secondary markets.
Germany
Automotive suppliers and industrial manufacturers deploy serverless security for predictive maintenance pipelines bridging ERP systems with cloud-native analytics. GDPR Article 32 mandates encryption and access controls for automated processing systems, accelerating investment in serverless-native data protection modules. Bavaria and Baden-Württemberg lead industrial IoT function security adoption among German automotive suppliers.
United Kingdom
London-based fintechs and cloud-native enterprises pilot eBPF-based kernel instrumentation for zero-overhead visibility into function execution. The UK Information Commissioner's Office enforces GDPR-aligned data residency requirements that shape procurement criteria for cross-border operational continuity. The Thames Valley corridor concentrates specialized security software engineering talent.
India
BIS cloud security framework data localization requirements for financial and government workloads create first-mover advantages for vendors establishing local engineering presence. Mumbai and Bangalore lead telecom carrier deployments of edge function security for 5G network slicing and subscriber data protection. Indian e-commerce platforms deploy API security protections for payment processing functions at scale.
Japan
Manufacturing firms deploy hybrid cloud configurations to bridge legacy ERP systems with cloud-native analytics functions. METI industrial cybersecurity guidelines shape procurement specifications for OT/IT convergence security in industrial IoT deployments. The Tokyo-Osaka corridor concentrates enterprise serverless adoption among precision manufacturers and electronics assemblers.
Global Serverless Security Market Competitive Landscape
Technology leadership and cost leadership are held by different player archetypes across the serverless security landscape. Hyperscale cloud providers bundle baseline protections at marginal cost, compressing pricing power for standalone vendors. Three archetypes dominate: cloud-native security specialists with workload-centric platforms, diversified cybersecurity incumbents with deep packet inspection capabilities, and infrastructure software vendors extending container security postures into function-as-a-service environments. Competitive moves center on strategic partnerships for multicloud portability and portfolio diversification into edge-to-core orchestration.
Within the cloud-native specialist tier, Palo Alto Networks and Aqua Security exemplify contrasting positioning strategies. Palo Alto Networks occupies a position in threat detection for distributed functions through deep packet inspection capabilities. Aqua Security represents the container-to-serverless continuity archetype, anchoring a narrow but defensible niche in workload-centric security. Microsoft Corporation sits within the hyperscale provider tier, sustaining momentum through native integration with Azure Functions and Logic Apps.
| Leading Market Players |
|---|
| Amazon Web Services |
| Microsoft Corporation |
| Palo Alto Networks |
| Imperva |
| IBM |
| Oracle |
| Aqua Security |
| Rackspace Technology |
| Others |
Supply & Pricing Matrix
Hyperscale cloud provider capacity utilization in serverless infrastructure anchors margin structures for standalone security vendors, compressing pricing power as AWS, Azure, and Google Cloud embed baseline protections at marginal incremental cost. This scale dynamic forces third-party vendors toward premium specialization or volume commoditization, with regulatory compliance modules commanding the widest spreads.
Pricing Analysis
EU AI Act and GDPR mandates dictate the pricing tier structure across the serverless security landscape, with compliance-heavy modules for automated decision auditing carrying substantial premiums over baseline runtime protection. Three-tier pricing structure across enterprise, mid-market, and developer-economy levels separates FedRAMP-authorized deployments from standard cloud-native configurations. Pricing pressure stems from cloud provider security bundling, which erodes standalone vendor margins in the public cloud segment. Financial services buyers in California and New York demonstrate the lowest price sensitivity, prioritizing sub-second threat detection latency over cost optimization, while education sector procurement teams favor economy-tier solutions with limited behavioral analytics.
Supply Chain Analysis
Inventory cycles for eBPF-based kernel instrumentation components run 8-12 weeks, constraining rapid scaling for agentless runtime monitoring vendors competing against established endpoint-based architectures. Engineering talent concentrates in the United States, Israel, and India, with Bangalore and Tel Aviv emerging as secondary development hubs beyond Silicon Valley. Raw material dependencies center on specialized semiconductor IP for deep packet inspection hardware, cryptographic accelerators, and cloud-native software development kits. Single-source vulnerability in eBPF toolchain maintenance creates supply chain risk, as the Linux kernel community governs critical instrumentation interfaces. Distribution runs through direct enterprise sales for large financial services contracts, supplemented by cloud marketplace listings for developer-led adoption.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Serverless security operates as a defensive-moat market where regulatory entrenchment creates sticky revenue streams; switching costs escalate as enterprises embed compliance modules into CI/CD pipelines and face audit continuity requirements.
For Market Incumbents: Compound native cloud provider partnerships to secure co-sell positioning within AWS Marketplace and Azure Partner Center, defending against margin compression from bundled security stacks. Deepen vertical integration into eBPF toolchain development to reduce dependency on upstream kernel community release cycles. Prioritize FedRAMP and EU cybersecurity certification investment to maintain eligibility for government procurement pipelines where vendor lists narrow annually.
For New Entrants and Emerging Players: Lead with edge-to-core orchestration capabilities targeting telecommunications carriers deploying 5G network slicing, the most penetrable white-space segment with limited incumbent specialization. Focus initial go-to-market on India's BIS cloud security framework compliance, where data localization mandates create first-mover advantages for vendors establishing local engineering presence. Emphasize runtime logging for EU AI Act algorithmic accountability as a differentiated wedge against generalized threat detection platforms.
For Investors and Strategic Acquirers: Mid-cycle technology positioning favors workload-centric security specialists with container-to-serverless continuity expertise over point-solution runtime monitoring vendors. Long-term viability hinges on multicloud portability architecture, with acquisition targets demonstrating functional parity across AWS Lambda, Azure Functions, and Google Cloud Run deployment models. Monitor hyperscaler security roadmap disclosures as the critical inflection signal; aggressive feature expansion in native cloud provider stacks would accelerate standalone vendor consolidation pressure.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Native Azure Functions and Logic Apps embedding compresses third-party standalone pricing power. |
| Strategic Partnership | Co-sell agreements with AWS Marketplace accelerate procurement velocity for runtime protection modules. |
| Acquisition of Specialist Firm | eBPF instrumentation expertise addresses zero-overhead monitoring demand from California cloud-native enterprises. |
| Geographic Expansion | Local engineering presence in India captures BIS framework compliance opportunities in financial services. |
| Product Launch | EU AI Act algorithmic accountability modules open specialized markets for decision-traceability tooling. |
Research Methodology
Cross-validation between primary fieldwork with CISOs and platform engineers and secondary analysis of SEC cybersecurity disclosure filings anchors the qualitative findings in this study. Conversations with cloud architects at financial services institutions, compliance officers at HIPAA-covered healthcare systems, procurement leads at telecommunications carriers, and DevOps directors at cloud-native enterprises generated demand-side intelligence. Secondary sources include hyperscaler capex disclosures, FedRAMP authorization databases, EU cybersecurity certification schemes, and cloud marketplace transaction data. Bottom-up deployment estimates triangulate against top-down security software spending allocations.
Sensitivity analysis across regulatory enforcement intensity scenarios shapes the forecast framework, with outputs reflecting variance in GDPR fine activity and SEC disclosure rule compliance timelines. Segmentation dimensions modeled include deployment architecture, security offering type, use case intensity, and end-user industry regulatory exposure. CAGRs derive from function deployment density trajectories and compliance module attach rates. Industry-specific inputs encompass eBPF adoption curves in cloud-native enterprises and container-to-serverless migration pipeline completion rates.
The analysis sits within stated boundaries; outcomes outside sustained multicloud workload distribution or accelerated EU AI Act enforcement would require recalibration. Forecasts reflect assumptions regarding cloud provider security stack expansion velocity and enterprise skills concentration persistence in coastal technology hubs. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Austria Cybersecurity Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
Cloud Workload Protection Market
Cybersecurity
Global Virtualization Security Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
Web Filtering Market
Cybersecurity
V2X Cybersecurity Market
Cybersecurity
Cyber Security Consulting Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Asia Pacific Digital Forensics Market
Cybersecurity
Global Network Forensics Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Cybersecurity in Gaming Market
Cybersecurity
Malaysia Cybersecurity Market