
 Global Mobile Application Security Market | 2026-2036
Global Mobile Application Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Mobile Application Security Market Foresight
Shift-left security integration into CI/CD pipelines is reconfiguring how mobile applications are built and tested before release. IBM Corporation leverages extensive enterprise security portfolios to anchor large financial services contracts. Cisco Systems competes through network-layer integration with mobile threat defense. Veracode specializes in static and dynamic application security testing for mobile binaries.
Mobile application security encompasses the technologies, processes, and practices designed to protect applications running on smartphones and tablets from unauthorized access, data exfiltration, and code manipulation through encryption protocols, runtime application self-protection, and binary hardening. Its primary purpose is to preserve confidentiality, integrity, and availability of data processed by mobile software across enterprise and consumer contexts. Cloud deployment models capture expanding margin pools as organizations prioritize scalable, API-driven security orchestration. Banking applications represent the most security-intensive segment, driving premium pricing for authentication and threat detection solutions. Encryption and vulnerability management form mature, high-volume categories, while code obfuscation gains traction among gaming and fintech developers.
The EU AI Act and GDPR impose strict algorithmic transparency and data processing requirements on AI-enabled mobile security tools in Europe. The FDA regulates mobile health applications with diagnostic functions, while India's TRAI and BIS frameworks shape local data localization and encryption standards. Stakeholders must monitor how fragmented national cybersecurity certifications reshape go-to-market economics for cross-border security vendors.
Market Dynamics
Shift-left security integration into CI/CD pipelines is collapsing traditional boundaries between development and security operations, forcing vendors to embed runtime protection and binary hardening directly into build automation rather than bolt them on post-deployment.
Growth Catalysts
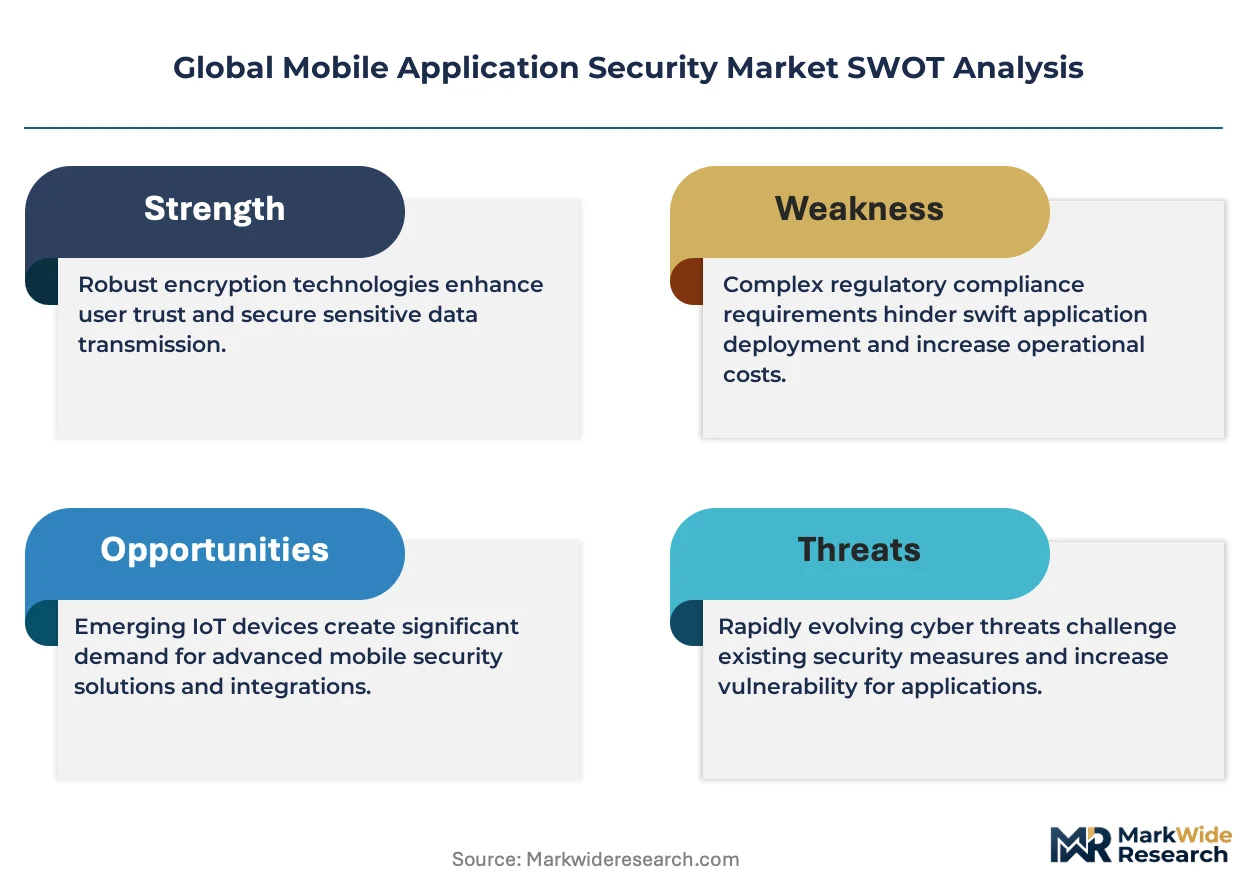
- EU AI Act compliance mandates:Financial services institutions across Germany, France, and Italy must implement algorithmic transparency controls in AI-enabled mobile security tools, creating mandatory upgrade cycles for authentication systems.
- Mobile banking expansion:India's digital payment infrastructure and Brazil's open banking frameworks are driving enterprise procurement of runtime application self-protection for consumer-facing financial apps.
- API-driven orchestration:Cloud-native security platforms enable scalable deployment models that reduce operational overhead for mid-market enterprises managing distributed mobile workforces.
Market Restraints
- Specialized talent scarcity:Shortage of engineers proficient in both mobile OS internals and cryptographic protocol implementation limits vendor scaling velocity.
- Fragmented certification requirements:India's BIS encryption standards, UAE's data localization rules, and Singapore's MAS technology risk guidelines create compliance multiplication costs for cross-border vendors.
- Binary analysis tooling limitations:Current static analysis engines struggle with obfuscated code in gaming and fintech applications, creating false negative vulnerabilities.
Strategic Opportunities
- Underpenetrated healthcare segment:FDA-regulated mobile diagnostic applications in the United States require specialized security validation that generalist vendors have not addressed.
- Zero-trust architecture convergence:Integration of mobile threat defense with identity-aware proxies creates unified endpoint security stacks for enterprise buyers.
- India's PLI scheme for electronics:Domestic manufacturing incentives are attracting security software development centers to Bangalore and Hyderabad, building local R&D capabilities.
Industry Challenges
- Legacy mainframe integration:Financial institutions running core banking systems on decades-old infrastructure face API gateway complexity when connecting mobile channels.
- Certification timeline compression:Common Criteria and FIPS 140-3 validation cycles for cryptographic modules extend 12-18 months, delaying product launches.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Mobile Application Security Market |
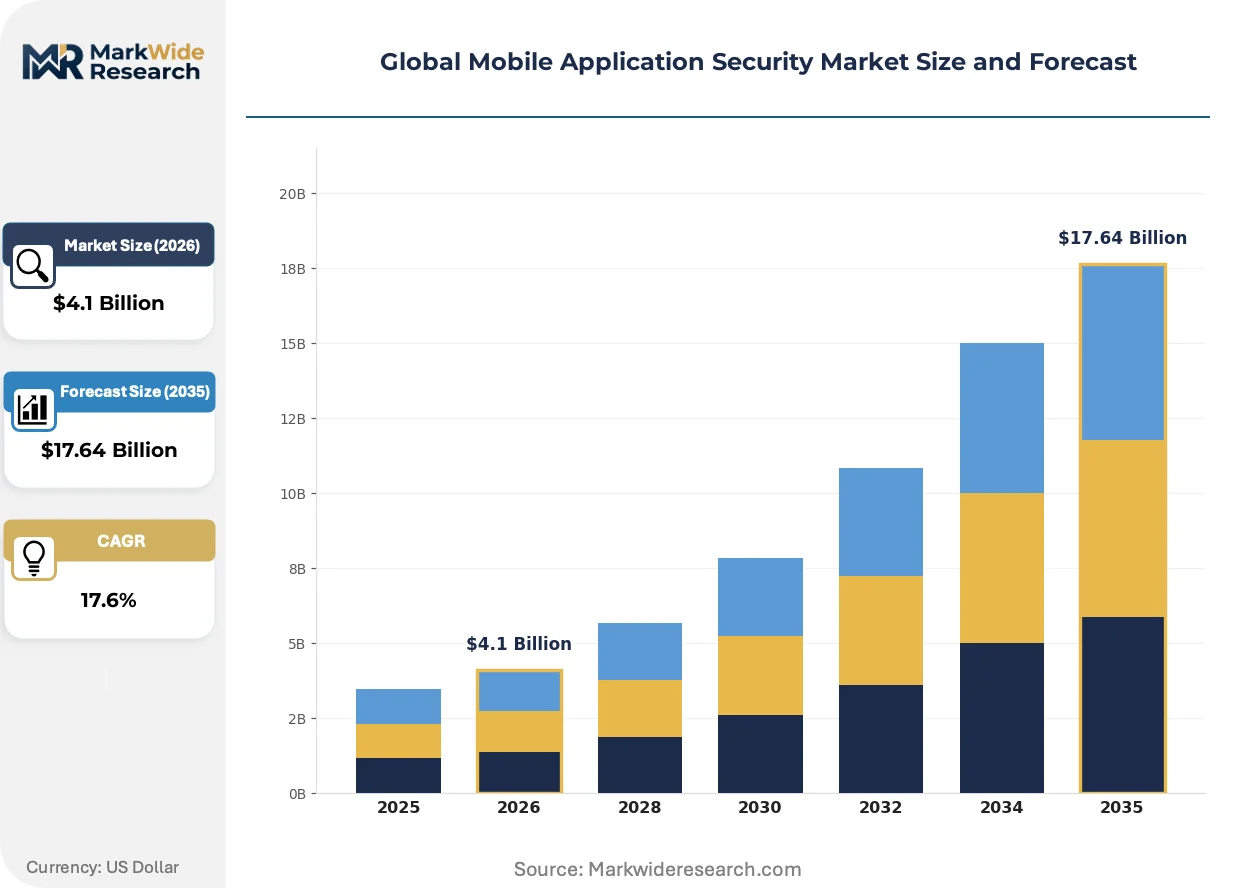
| Market Size in 2026 | $4.1 Billion |
| Market Size in 2035 | $17.64 Billion |
| CAGR (2026 – 2036) | 17.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud, Hybrid, Managed Services Security Solution: Encryption, Authentication, Threat Detection, Vulnerability Management, Code Obfuscation Application Type: Enterprise Apps, Banking Apps, E-Commerce Apps, Social Networking Apps, Gaming Apps End User Industry: Financial Services, Telecommunications, Government Agencies, IT & Software, Media & Entertainment |
| Companies Covered | IBM Corporation, Cisco Systems, Broadcom, Veracode, Check Point Software Technologies, F5, Symantec Corporation, Trend Micro, NowSecure, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Mobile Application Security Market Shifts & Advancements
Runtime application self-protection is collapsing the traditional perimeter between detection and response, embedding behavioral monitoring directly inside mobile binaries rather than relying on external scanning tools.
RASP technology is collapsing the functional separation between application layer and security layer by injecting instrumentation code during compilation. Banking and fintech developers in the United States and United Kingdom are adopting this approach at accelerating pace as regulatory pressure mounts. This compression is collapsing demand for standalone mobile device management solutions as endpoint protection converges into unified platforms.
The EU AI Act's algorithmic transparency requirements are forcing vendors to document decision logic in machine-learning-based threat detection systems. European financial services institutions must now maintain audit trails for automated security decisions affecting customer access. Mobile health applications with diagnostic functions face overlapping compliance burdens from the EU AI Act and FDA pre-market clearance pathways in the United States.
Enterprise procurement of mobile security is consolidating around platform vendors capable of unified endpoint, identity, and cloud workload protection. Mid-market buyers in Germany and India are abandoning point solutions for integrated suites that reduce vendor management overhead. This concentration is most visible in financial services, where CISOs prioritize single-pane-of-glass visibility over best-of-breed functional depth.
Global Mobile Application Security Market Segmentation
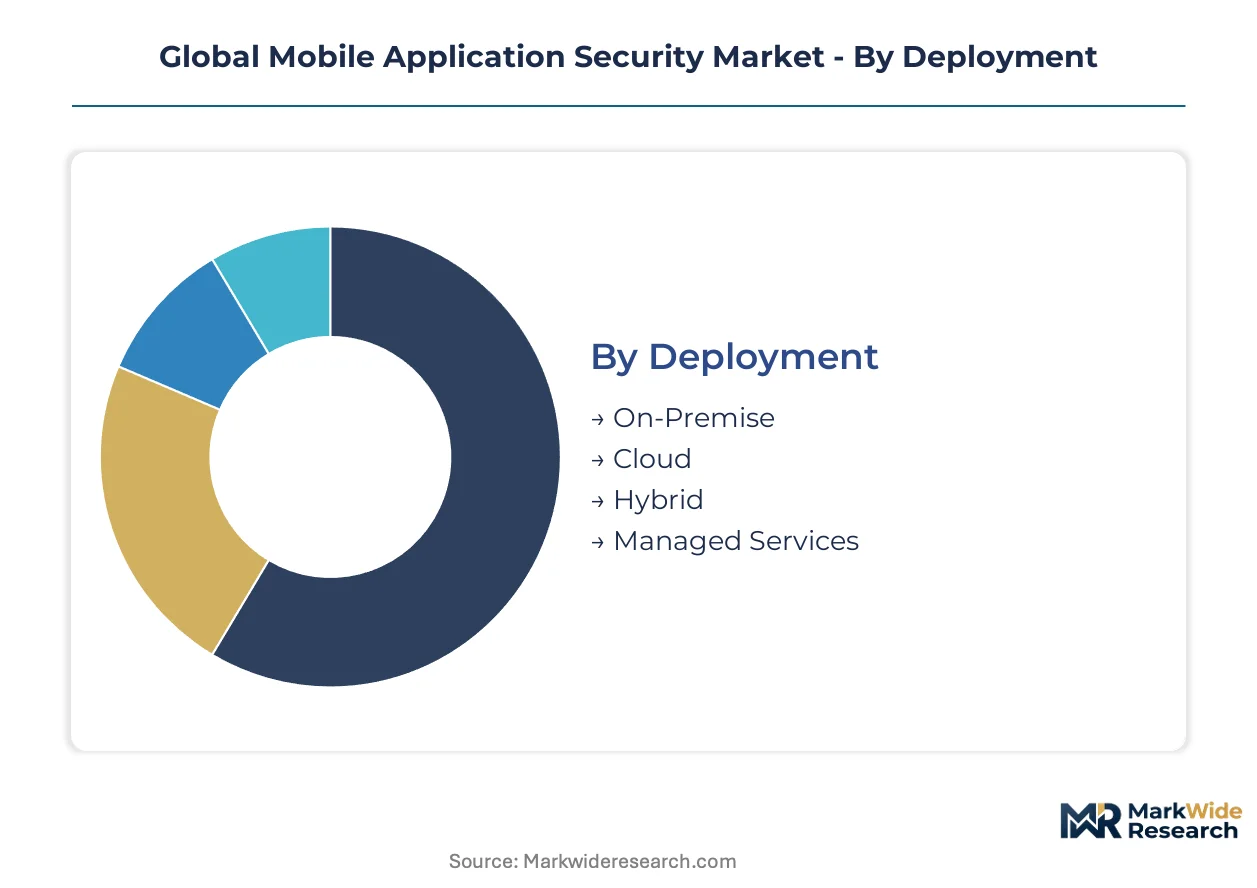
Mobile application security procurement varies sharply across deployment models, security functions, and application contexts. Buyers prioritize different capabilities based on regulatory exposure, data sensitivity, and integration complexity with existing infrastructure.
Deployment:
After-sales service intensity escalates dramatically with deployment complexity, as on-premise installations demand sustained engineering support while cloud models shift burden to vendor infrastructure teams.
- Cloud:API-driven orchestration enables scalable security policy distribution across distributed mobile workforces. Financial services institutions in Germany and the United States are consolidating procurement around cloud-native platforms to reduce operational overhead.
- On-Premise:Organizations with strict data sovereignty requirements maintain direct control over cryptographic key management and audit logging. Government agencies across India and France mandate on-premise deployment for classified mobile communications.
- Hybrid:Combines cloud orchestration with localized sensitive data processing. Enterprises with legacy mainframe integration requirements favor this model for phased migration.
- Managed Services:Third-party security operations centers monitor mobile threat landscapes and incident response. Mid-market enterprises in Brazil and Singapore adopt this to bypass specialized talent scarcity.
Cloud holds the largest share; momentum sits with Managed Services as talent constraints deepen.
Security Solution:
Solution selection tracks directly to application risk profiles, with financial services demanding multi-layered authentication while gaming developers prioritize code protection against reverse engineering.
- Encryption:Protects data at rest and in transit through cryptographic protocols including AES-256 and TLS implementations. GDPR and India's BIS standards mandate specific encryption grades for financial and health data processing.
- Authentication:Biometric, behavioral, and multi-factor verification systems gate mobile access. EU AI Act compliance now requires algorithmic transparency documentation for AI-enabled authentication decisions in France and Italy.
- Threat Detection:Behavioral analytics identify anomalous device and network activity patterns.
- Vulnerability Management:Continuous scanning and patch orchestration for mobile binaries and dependencies.
- Code Obfuscation:Binary hardening techniques resist reverse engineering and tampering. Fintech and gaming developers in the United States and United Kingdom are expanding adoption as regulatory pressure mounts.
Authentication commands premium pricing; code obfuscation is expanding most quickly among gaming and fintech segments.
Application Type:
Application architecture determines security stack configuration, with banking applications requiring runtime protection while social platforms emphasize data loss prevention.
- Banking Apps:Runtime application self-protection embeds behavioral monitoring directly inside mobile binaries. India's digital payment infrastructure and Brazil's open banking frameworks are driving enterprise procurement of specialized authentication and threat detection solutions.
- Enterprise Apps:Integration with identity-aware proxies and zero-trust architecture creates unified endpoint security stacks. CISOs in Germany and the United States prioritize single-pane-of-glass visibility over best-of-breed functional depth.
- E-Commerce Apps:Payment card industry compliance drives encryption and tokenization requirements.
- Social Networking Apps:Content moderation APIs and data exfiltration controls dominate security spending.
- Gaming Apps:Anti-cheat engines and binary integrity verification protect revenue models. Static analysis engines struggle with obfuscated code in this segment, creating false negative vulnerabilities.
Banking Apps absorb the highest security spend per install; Enterprise Apps are gaining share fastest as distributed workforces expand.
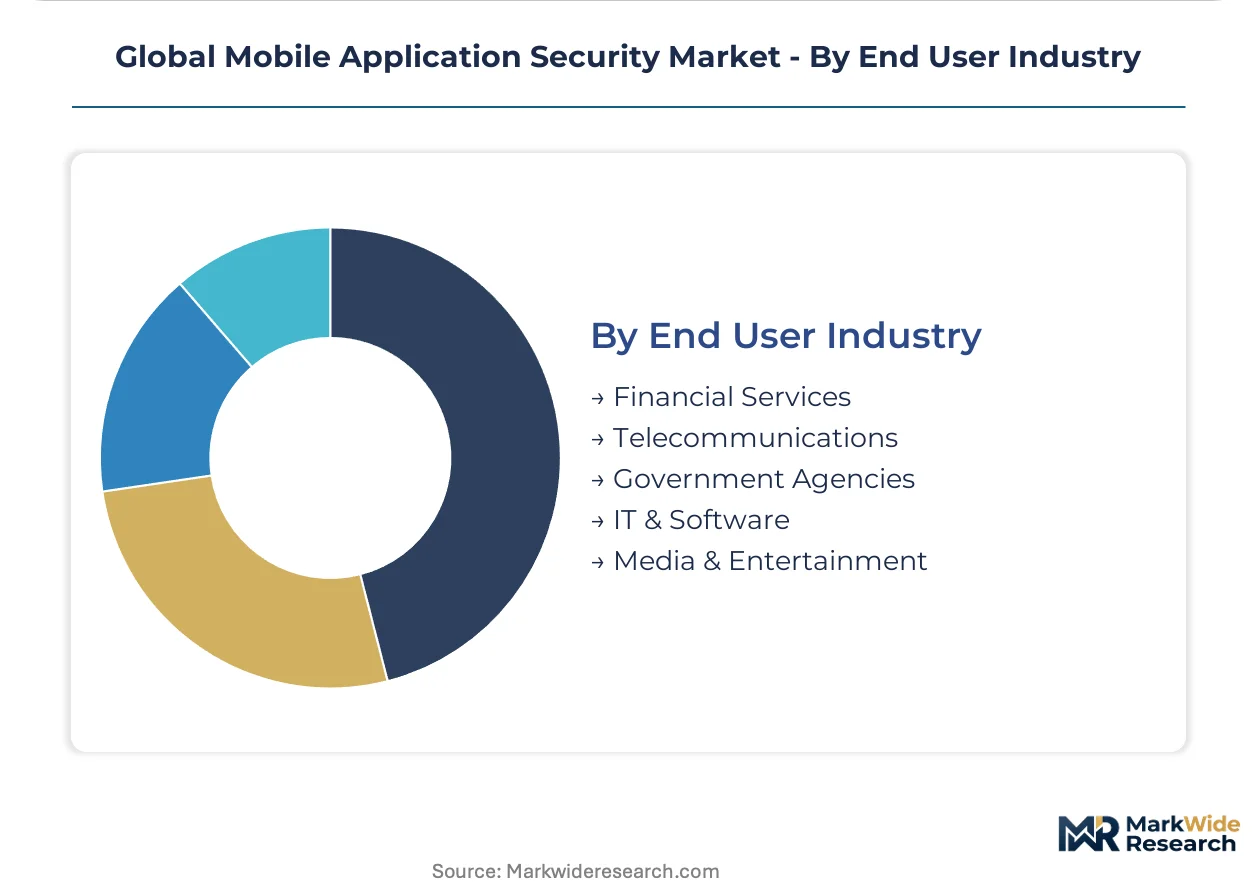
End User Industry:
Industry-specific regulatory frameworks reshape product development priorities, with FDA-regulated health applications and EU AI Act-covered financial services imposing distinct compliance burdens.
- Financial Services:Algorithmic transparency mandates under the EU AI Act and GDPR compliance requirements reshape authentication system upgrades. Institutions across Germany, France, and Italy must implement documented audit trails for automated security decisions affecting customer access.
- Government Agencies:Classified mobile communications require FIPS 140-3 validated cryptographic modules and Common Criteria certification. India's TRAI and BIS frameworks shape local data localization and encryption standards.
- Telecommunications:Network-layer integration with mobile threat defense protects subscriber devices.
- IT & Software:Shift-left security integration into CI/CD pipelines collapses traditional boundaries between development and security operations.
- Media & Entertainment:Digital rights management and content protection against piracy drive security investment.
Financial Services dominates procurement volume; Government Agencies show the steepest expansion trajectory as national cybersecurity frameworks tighten.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
India exports mobile application security services to financial institutions across Germany, the United States, and the United Kingdom, with Bangalore and Hyderabad serving as primary development centers for runtime protection and binary hardening solutions.
United States
Enterprise mobility expansion and FDA-regulated mobile health applications drive procurement of specialized security validation. HIPAA compliance requirements shape encryption standards for healthcare data processing. The San Francisco Bay Area concentrates venture capital flows into cloud-native security orchestration platforms.
Germany
Automotive and industrial IoT applications generate demand for embedded mobile security in connected vehicle systems. EU AI Act algorithmic transparency mandates require documented audit trails for automated authentication decisions. Munich and Stuttgart host engineering centers integrating mobile threat defense with manufacturing execution systems.
India
Digital payment infrastructure expansion and open banking frameworks accelerate enterprise adoption of runtime application self-protection. TRAI data localization rules and BIS encryption standards reshape product architecture for domestic deployment. Bangalore and Hyderabad attract security software development centers under the PLI scheme for electronics manufacturing.
United Kingdom
Fintech regulatory sandboxes and open banking APIs create specialized demand for code obfuscation and binary integrity verification. GDPR compliance requirements influence authentication system design for consumer-facing financial applications. London's financial district anchors procurement of unified endpoint security stacks integrating mobile threat defense with identity-aware proxies.
Brazil
Open banking frameworks and instant payment infrastructure drive enterprise investment in mobile banking security solutions. ANVISA regulations for mobile health applications with diagnostic functions impose validation requirements. São Paulo concentrates fintech development activity and security procurement decisions for Latin American operations.
Global Mobile Application Security Market Competitive Landscape
On the supply side, the industry is consolidating around platform vendors capable of unified endpoint, identity, and cloud workload protection. Tiered competitive dynamics separate enterprise security incumbents from specialized mobile-focused developers. Three archetypes dominate: diversified cybersecurity conglomerates with extensive enterprise portfolios, network-layer specialists integrating mobile threat defense with infrastructure, and application security purists focusing on static and dynamic testing. M&A activity concentrates on acquiring runtime application self-protection capabilities, while strategic partnerships with cloud service providers expand distribution reach.
Among diversified cybersecurity incumbents, IBM Corporation and Cisco Systems exemplify the platform consolidation archetype, anchoring large financial services contracts through extensive security portfolios and network-layer integration respectively. Veracode occupies a position within the application security specialist tier, representing the static and dynamic testing focus that fintech and gaming developers prioritize for binary hardening requirements.
| Leading Market Players |
|---|
| IBM Corporation |
| Cisco Systems |
| Broadcom |
| Veracode |
| Check Point Software Technologies |
| F5 |
| Symantec Corporation |
| Trend Micro |
| NowSecure |
| Others |
Supply & Pricing Matrix
Overcapacity in cloud-native security tooling across India's development centers is compressing margins for runtime application self-protection vendors while simultaneously enabling aggressive pricing postures among platform consolidators. This utilization dynamic rewards vendors with captive infrastructure and punishes pure-play specialists dependent on third-party orchestration layers.
Pricing Analysis
Next-generation RASP-enabled solutions command 40-60% premiums over legacy static analysis tools, while prior-generation mobile device management suites face steep erosion as endpoint protection converges into unified platforms. Three-tier pricing structure across premium, standard, and economy levels reflects certification grade differentiation, with FIPS 140-3 validated modules capturing top-tier positioning. Cost compression in the standard tier is intensifying because mid-market buyers in Germany and India are consolidating procurement around integrated suites. Government agencies exhibit lowest price sensitivity due to mandatory compliance requirements, while gaming developers demonstrate highest sensitivity given thin margins and high volume deployment.
Supply Chain Analysis
Contract manufacturing concentration for cryptographic hardware modules rests on Gemalto, Thales, and domestic Indian vendors operating under the PLI scheme for electronics. Software development capacity concentrates in India, the United States, and Israel, with Bangalore and Hyderabad anchoring runtime protection engineering. Raw material dependencies include specialized cryptographic processors, secure element chips, and cloud compute infrastructure. Single-source vulnerability around FIPS 140-3 validated hardware security modules creates supply chain risk for vendors serving government agencies. Distribution runs through direct enterprise sales teams for large financial services contracts and hyperscaler marketplaces for mid-market cloud-native deployment.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform economics is concentrating procurement power around vendors capable of unified endpoint, identity, and cloud workload protection, with API-driven orchestration interoperability emerging as the decisive ecosystem battleground.
For Market Incumbents: Harden runtime application self-protection capabilities through targeted acquisition of binary hardening specialists, as standalone mobile device management vendors face displacement from converged endpoint platforms. Invest in FIPS 140-3 and Common Criteria certification pipelines to defend government agency contracts against emerging domestic competitors in India. Capacity addition in Bangalore and Hyderabad under the PLI scheme anchors cost-competitive R&D expansion. For New Entrants and Emerging Players: Establish a beachhead in FDA-regulated mobile health applications, where specialized security validation requirements have deterred generalist vendors and created white-space opportunity. Target mid-market healthcare systems in the United States seeking HIPAA-compliant mobile diagnostic security without enterprise-scale procurement overhead. Partner with clinical workflow platform vendors to embed security instrumentation during application compilation rather than post-deployment bolt-on. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among cloud-native security orchestration platforms with API-driven distribution models, positioning these archetypes for superior long-term viability across a 5-10 year holding window. Prioritize acquisition targets with runtime application self-protection intellectual property and established CI/CD pipeline integrations. Monitor Common Criteria certification timeline compression as an inflection indicator for vendor scaling velocity and competitive positioning.| Strategic Initiative | Industry Significance |
|---|---|
| Runtime Application Self-Protection Acquisition | Binary instrumentation capabilities collapse detection-response latency for financial services clients in Germany. |
| FIPS 140-3 Certification Pipeline Investment | Government agencies in India and France mandate validated cryptographic modules for classified mobile communications. |
| CI/CD Pipeline Native Integration | Shift-left security embedding captures developer workflow mindshare ahead of post-deployment alternatives. |
| Healthcare Vertical Specialization | FDA pre-market clearance pathways for mobile diagnostics create defensible moat against generalist competitors. |
| Hyperscaler Marketplace Distribution | AWS and Azure procurement channels unlock mid-market enterprise access without direct sales infrastructure. |
Research Methodology
A spread of perspectives from CISOs at financial services institutions, mobile platform engineers, regulatory compliance officers, and healthcare IT procurement leads converged on the working assumptions underlying demand modeling. Primary interview data combined with secondary validation from SEC filings, EU AI Act implementation guidance, FDA 510(k) clearance databases, and TRAI regulatory circulars. Bottom-up deployment model adoption curves and top-down enterprise security spending patterns were triangulated to anchor volume estimates.
Demand-supply-balance framing shaped the analytical framework across the analysis window, with segmentation modeled across deployment architecture, security function, application type, and end-user industry vertical. CAGRs were derived from fitted adoption curves calibrated to named regulatory mandate effective dates and enterprise procurement cycle timing. Industry-specific forecast inputs included EU AI Act algorithmic transparency compliance deadlines and India's PLI scheme capacity buildout trajectories.
Stress conditions across talent scarcity intensity, certification timeline elongation, and cloud infrastructure cost volatility were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions about regulatory enforcement consistency and enterprise mobility expansion rates. Quarterly review of Common Criteria certification queue lengths and hyperscaler security marketplace transaction velocity is advised to detect inflection.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Online Fraud Detection and Prevention Market
Cybersecurity
Germany Ransomware Protection Market
Cybersecurity
Global Managed Detection and Response (MDR) Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Deception Technology Market
Cybersecurity
Threat Intelligence Security Market
Cybersecurity
Europe Web Application Firewall Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Network Sandboxing Market
Cybersecurity
Network Traffic Analysis Solutions Market
Cybersecurity
Data Security Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Europe Data Exfiltration Market
Cybersecurity
Endpoint Protection Platforms (EPP) Market
Cybersecurity
Enterprise Network Firewall Market
Cybersecurity
Global Dynamic Data Masking Market