
 Cloud Firewalls Market | 2026-2036
Cloud Firewalls Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Firewalls Market Outlook
Buyer concentration among large enterprises and government organizations is hardening as procurement authority centralizes under CISO offices and federal acquisition frameworks. Palo Alto Networks leverages its platform consolidation strategy to capture multi-year enterprise commitments. Fortinet anchors its position through integrated SD-WAN and firewall bundles that reduce vendor sprawl. Zscaler competes by routing traffic through its zero-trust cloud fabric rather than premises appliances.
Cloud firewalls are network security systems deployed as software-defined perimeter controls within virtualized infrastructure, inspecting traffic through deep packet inspection engines operating at throughput thresholds exceeding 100 Gbps in hyperscale configurations. Their primary purpose is to enforce segmentation policies across distributed cloud workloads without hardware dependency. Next-generation firewall solutions dominate value capture by embedding intrusion prevention and application-aware filtering in unified control planes. Public cloud deployment models generate the fastest expansion as AWS, Azure, and Google Cloud native firewall services absorb mid-market volume. Managed services margin pools are deepening as enterprises outsource rule-base tuning and threat response to specialized providers.
US federal procurement operates under FedRAMP authorization requirements administered by GSA, while the EU Cybersecurity Act mandates CE marking for ICT products through ENISA oversight. NIS2 expands incident reporting obligations across critical infrastructure operators, directly expanding mandated firewall coverage. Stakeholders must monitor how fragmented sovereignty requirements across national cloud frameworks reshape architectural standards and certification burdens.
Market Dynamics
CISO procurement centralization is compressing vendor selection cycles while mandating platform consolidation over point solutions, reshaping how firewall capabilities bundle with broader security fabrics.
Growth Catalysts
- EU NIS2 Directive:Critical infrastructure operators across energy, transport, and healthcare sectors must deploy certified network security controls, expanding mandated firewall coverage to previously exempt mid-tier utilities.
- Hyperscale throughput demands:Financial services exchanges processing sub-microsecond trades require software-defined perimeter inspection exceeding 100 Gbps without hardware chokepoints.
- FedRAMP authorization pipelines:US federal cloud modernization programs are standardizing on authorized firewall-as-a-service architectures, creating procurement velocity for pre-certified vendors.
Market Restraints
- Specialized engineering talent scarcity:Deep packet inspection engine development requires rare expertise in kernel-level networking and hardware acceleration, constraining vendor R&D scaling.
- Hyperscaler native service substitution:AWS Network Firewall, Azure Firewall, and Google Cloud Firewall absorb mid-market volume through bundled pricing, compressing independent vendor addressable space.
- Cross-border data sovereignty fragmentation:Divergent national cloud frameworks in Germany, France, and India impose conflicting architectural certification requirements, inflating compliance overhead.
Strategic Opportunities
- Managed detection and response integration:Firewall rule-base tuning and autonomous threat response outsourcing is deepening margin pools for specialized security service providers.
- India's data localization mandates:RBI and CERT-In directives on financial data residency are forcing multinational banks to deploy in-country cloud firewall infrastructure.
- Zero-trust architecture convergence:Integration of software-defined perimeter controls with identity-aware proxy architectures creates unified policy enforcement opportunities.
Industry Challenges
- Multi-cloud policy orchestration complexity:Enterprises operating across AWS, Azure, and Google Cloud struggle to maintain consistent segmentation rules across divergent native control planes.
- FedRAMP authorization timeline compression:The 12-18 month certification cycle for federal deployment eligibility creates revenue recognition delays for emerging vendors.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Firewalls Market |
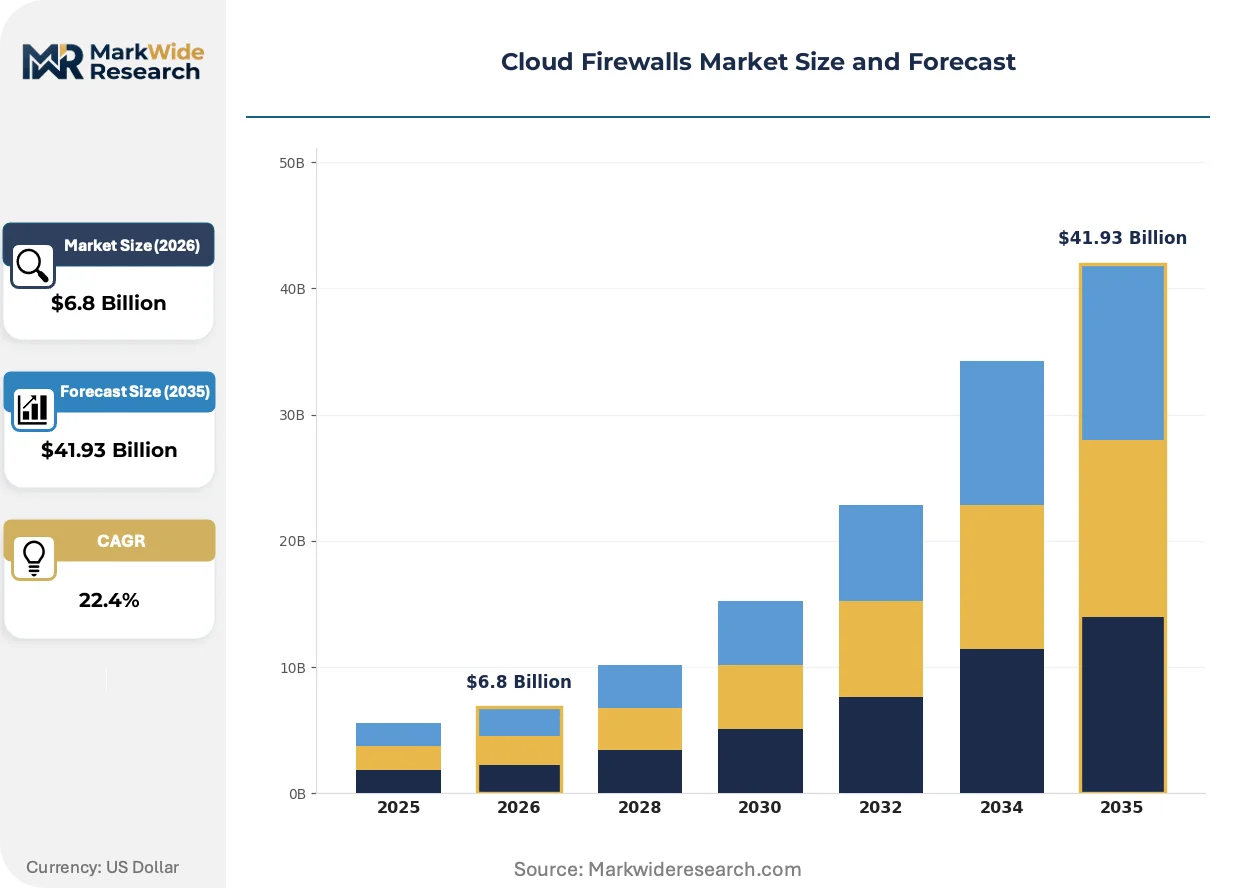
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $41.93 Billion |
| CAGR (2026 – 2036) | 22.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud Solution Type: Next-Generation Firewall, Virtual Firewall, Web Application Firewall, Intrusion Prevention System End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Organizations Service Type: Managed Services, Professional Services, Integration Services, Consulting Services |
| Companies Covered | Palo Alto Networks, Zscaler, Fortinet, Cisco Systems, Check Point Software Technologies, Cloudflare, Amazon Web Services, Microsoft Azure, Google Cloud, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Firewalls Market Strategic Shifts
Artificial intelligence inference at the network edge is reshaping threat detection latency requirements, forcing firewall architectures to embed machine learning models directly within packet processing paths rather than shipping telemetry to centralized analytics.
Intelligent traffic analysis engines is expanding into real-time encrypted payload inspection without decryption, using behavioral baselining and metadata correlation to identify anomalous patterns in TLS 1.3 sessions. Large financial institutions in London and Singapore are piloting these capabilities for high-frequency trading environments where latency budgets preclude traditional SSL inspection. The technology is expanding into compliance automation by generating audit-ready evidence streams that satisfy SEC and MAS regulatory examination requirements.
The EU AI Act's risk-based classification system now mandates conformity assessments for security products incorporating machine learning components, treating certain autonomous firewall decision systems as high-risk AI. ENISA is developing technical standards for AI-enabled network security controls, creating a certification pathway that will become mandatory for critical infrastructure procurement. German and French energy utilities are front-running these requirements by pre-qualifying vendors against draft standards.
Enterprise buying committees are consolidating security procurement under platform-centric evaluation frameworks, displacing best-of-breed point solution selection. CISO offices at Fortune 500 manufacturers and US federal agencies now require firewall capabilities to integrate with existing SIEM and SOAR investments through standardized APIs. This pattern is most pronounced in hybrid manufacturing clusters across Michigan and South Carolina, where OT-IT convergence demands unified policy management across plant floor and cloud workloads.
Cloud Firewalls Market Segmentation
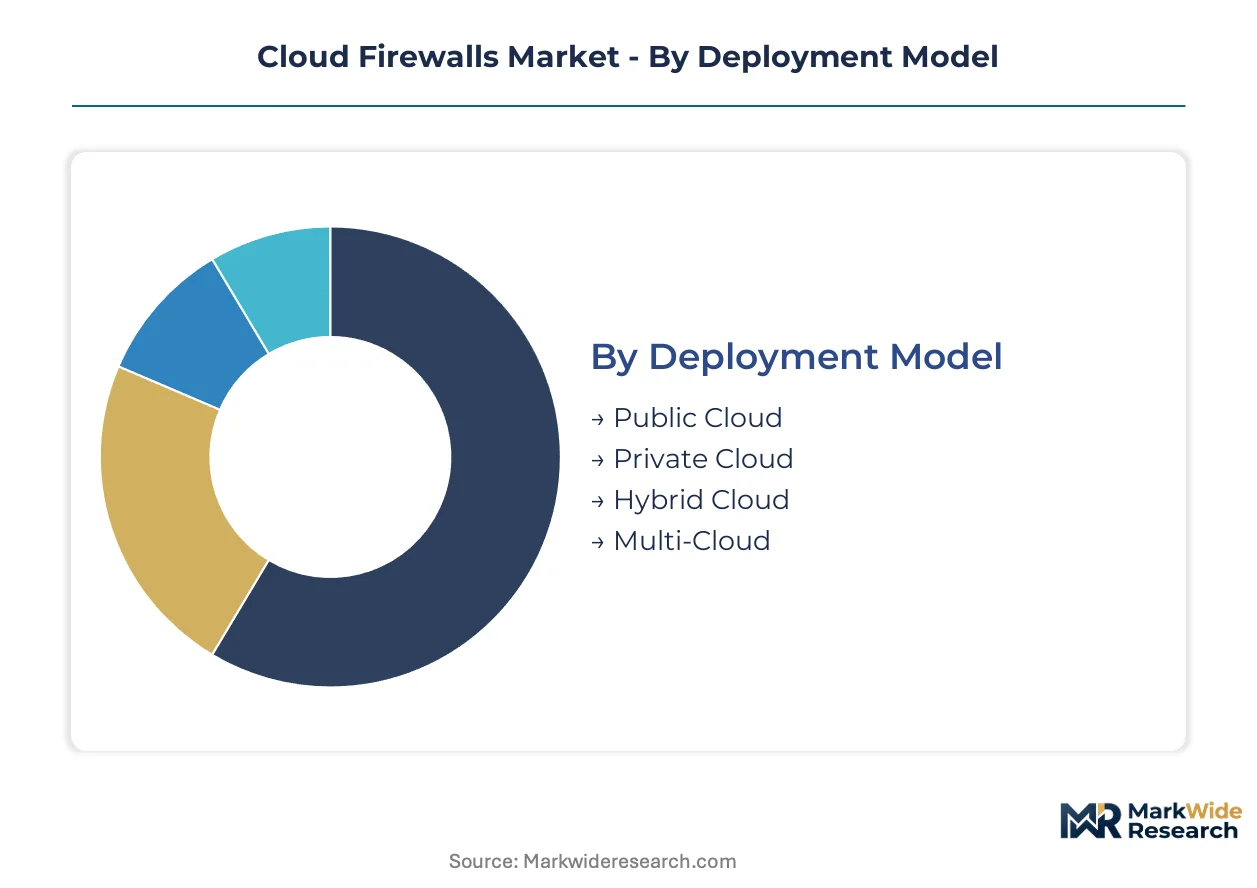
Cloud firewall procurement patterns diverge sharply across deployment architectures and organizational scale, with integration depth determining whether solutions operate as standalone perimeter controls or embedded security fabrics. Understanding these segment boundaries illuminates where vendor consolidation pressures concentrate versus where specialized point solutions retain pricing power.
Deployment Model:
Integration depth varies dramatically across deployment architectures, with some models demanding embedded security fabrics while others accommodate standalone perimeter controls.
- Public Cloud:Native firewall services from AWS, Azure, and Google Cloud absorb mid-market volume through bundled consumption pricing. Financial services firms in Singapore and London select these for high-frequency trading environments where sub-microsecond latency budgets preclude hardware inspection.
- Hybrid Cloud:Unified policy enforcement across on-premises data centers and cloud workloads requires API-integrated control planes that synchronize segmentation rules. US federal agencies under FedRAMP authorization mandates favor this architecture for classified-unclassified workload separation.
- Private Cloud:Dedicated virtualized infrastructure within single-tenant environments supports regulated industries with data residency constraints. German energy utilities deploy these to satisfy BSI baseline protection requirements.
- Multi-Cloud:Orchestration layers spanning AWS, Azure, and Google Cloud struggle with divergent native control plane semantics. India's RBI-mandated financial data localization is forcing multinational banks toward this complexity.
Public Cloud leads volumes today; Multi-Cloud is gaining share fastest.
Solution Type:
Cost tier stratification separates premium unified platforms from commoditized single-function appliances, with price differentiation tracking capability bundling intensity.
- Next-Generation Firewall:Unified control planes embed intrusion prevention, application-aware filtering, and threat intelligence feeds within single policy engines. Large enterprises in Michigan manufacturing clusters select these for OT-IT convergence scenarios requiring plant floor-to-cloud segmentation.
- Web Application Firewall:Specialized Layer 7 inspection for HTTP/HTTPS traffic protects against OWASP Top 10 vulnerabilities without full perimeter replacement. E-commerce platforms in France front-run ENISA draft standards for API security.
- Virtual Firewall:Software-defined instances deployable across hypervisor environments without hardware dependency. Mid-tier utilities expanding under EU NIS2 Directive coverage favor these for rapid procurement cycles.
- Intrusion Prevention System:Signature and anomaly-based detection engines operating inline to block malicious payloads. Healthcare operators in Singapore pilot these for MAS regulatory examination compliance.
Next-Generation Firewall dominates revenue concentration; Web Application Firewall is expanding most quickly.
End User:
Customer type determines procurement authority centralization, with CISO office consolidation most pronounced at scale extremes.
- Large Enterprises:Fortune 500 manufacturers and financial institutions mandate platform consolidation over point solutions, compressing vendor selection cycles. South Carolina automotive clusters require unified policy management across supplier cloud workloads.
- Government Organizations:US federal cloud modernization programs standardize on FedRAMP-authorized architectures, creating procurement velocity for pre-certified vendors. EU critical infrastructure operators face expanded NIS2 coverage obligations.
- Medium Enterprises:Hybrid deployment adoption accelerates as managed service providers bundle firewall capabilities with broader security outsourcing. India's CERT-In directives are reshaping procurement priorities.
- Small Enterprises:Native cloud service substitution absorbs volume through AWS Network Firewall and Azure Firewall bundled pricing. Compliance automation demands remain minimal at this scale.
Large Enterprises anchor procurement value; Government Organizations are climbing the fastest.
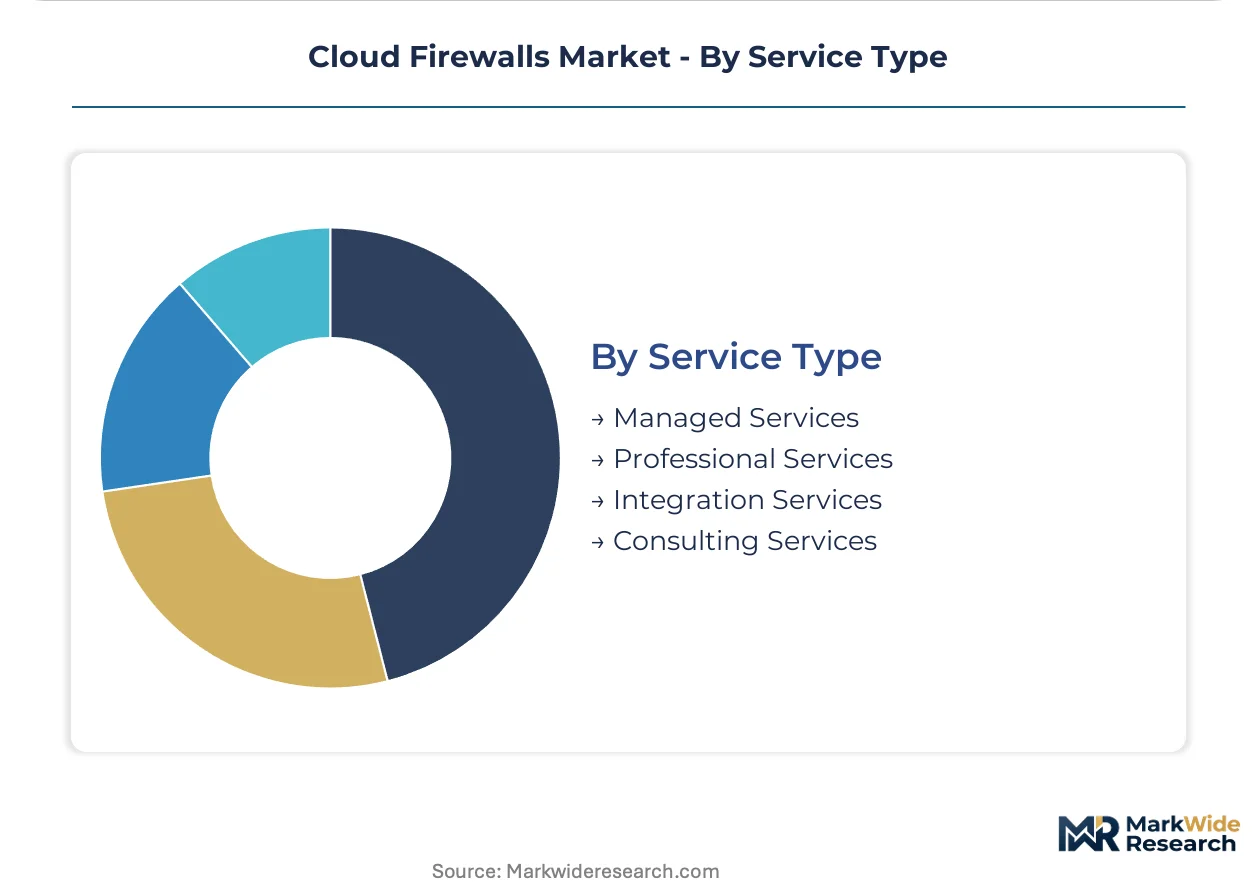
Service Type:
Margin pool depth tracks outsourcing intensity, with autonomous operations commanding premium pricing over staff-augmentation models.
- Managed Services:Rule-base tuning and autonomous threat response outsourcing deepens recurring revenue pools. Specialized providers in London's financial district capture multi-year commitments from trading infrastructure operators.
- Professional Services:Implementation and architecture design engagements support complex hybrid and multi-cloud deployments. German energy utilities leverage these for BSI compliance pathway navigation.
- Integration Services:API connectivity with existing SIEM and SOAR investments satisfies Fortune 500 platform-centric evaluation frameworks. Singapore banks prioritize these for MAS audit-ready evidence stream generation.
- Consulting Services:Zero-trust architecture migration planning and policy rationalization engagements. France's energy sector front-runs EU AI Act conformity assessments through these advisory relationships.
Managed Services captures the steepest expansion trajectory; Professional Services maintains the largest installed base.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States federal procurement velocity outpaces German utility sector deployment cycles, while Singapore's financial district pilots edge-AI inspection capabilities that London trading floors are beginning to emulate.
United States
FedRAMP authorization pipelines and Fortune 500 hybrid deployments drive procurement concentration. GSA-administered certification requirements create 12-18 month vendor eligibility timelines. South Carolina automotive clusters demand unified policy management across supplier cloud workloads.
Germany
BSI baseline protection requirements and EU NIS2 Directive coverage expansion reshape utility procurement. ENISA oversight of CE marking mandates creates certification pathway complexity. Bavarian energy operators pre-qualify vendors against draft EU AI Act technical standards.
Singapore
MAS regulatory examination requirements and sub-microsecond latency budgets attract encrypted payload inspection pilots. The financial district's trading infrastructure operators outsource rule-base tuning to specialized managed service providers. Local banks prioritize API connectivity for audit-ready evidence stream generation.
United Kingdom
High-frequency trading environments in London drive software-defined perimeter inspection exceeding 100 Gbps. Financial services exchanges pilot behavioral baselining for TLS 1.3 sessions without decryption. The capital's regulatory technology providers deepen recurring revenue pools through autonomous threat response outsourcing.
India
RBI and CERT-In data localization directives force multinational banks toward in-country cloud firewall infrastructure. Maharashtra and Delhi-NCR financial centers deploy dedicated virtualized instances for rapid procurement cycles. Mid-tier enterprises accelerate hybrid adoption through managed service provider bundling.
Cloud Firewalls Market Competitive Environment
United States-based platform consolidators anchor one tier; Israeli and European security specialists hold differentiated positions in high-assurance segments. Market structure exhibits moderate concentration with three distinct strategic tiers: hyperscaler-native services, integrated platform vendors, and zero-trust cloud fabric specialists. Dominant competitive moves include strategic partnerships with managed security service providers and portfolio diversification into AI-enabled threat detection engines.
Within the integrated platform tier, Palo Alto Networks exemplifies multi-year enterprise commitment capture through consolidation strategies. Zscaler occupies a distinct position routing traffic through cloud-native zero-trust architectures rather than premises appliances. Fortinet anchors the bundled infrastructure segment through SD-WAN and firewall integration that reduces vendor sprawl for mid-market procurement committees.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Zscaler |
| Fortinet |
| Cisco Systems |
| Check Point Software Technologies |
| Cloudflare |
| Amazon Web Services |
| Microsoft Azure |
| Google Cloud |
| Others |
Value Chain & Pricing Dynamics
FedRAMP authorization timelines and CE marking pathways under ENISA oversight gate both qualified supply and premium-tier pricing access for cloud firewall vendors, compressing procurement eligibility to pre-certified providers while elevating compliance-invested competitors above commodity alternatives.
Pricing Analysis
Capacity additions in India and Singapore are reshaping price floors for virtual firewall instances as local data center buildouts satisfy RBI and MAS localization mandates. SaaS-tiered subscription models dominate, with pricing stratifying across FedRAMP-authorized premium tiers, standard enterprise bundles, and economy native-cloud alternatives. Certification level and throughput performance separate tiers, while AWS Network Firewall bundled pricing drives cost compression in mid-market segments. Large enterprises exhibit lowest price sensitivity; small enterprises absorbing native services show highest elasticity.
Supply Chain Analysis
Dual-sourcing requirements from US federal agencies and EU critical infrastructure operators mandate multi-supplier qualification across hardware-agnostic software development and managed security service delivery. Supply concentrates in the United States, Israel, and India for deep packet inspection engine development and kernel-level networking expertise. The chain draws from specialized semiconductor IP for hardware acceleration, open-source networking stacks, and cloud hyperscaler infrastructure. Single-source vulnerability in FedRAMP-authorized vendor pools creates concentration risk. Distribution runs through direct enterprise sales, managed security service providers, and hyperscaler marketplaces.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Geographic arbitrage opportunities concentrate where India's data localization mandates force infrastructure deployment at 40-60% cost differentials versus Singapore or London financial district buildouts.
For Market Incumbents: Lock in multi-year enterprise commitments through platform consolidation bundling SIEM and SOAR integration, while accelerating FedRAMP authorization pipelines to preempt emerging vendor eligibility. Hyperscaler native service substitution threatens independent vendor margins; vertical integration into managed detection and response services deepens recurring revenue pools and raises switching costs. For New Entrants and Emerging Players: The premium-to-economy price-point gap in multi-cloud orchestration layers opens white-space targeting for mid-tier utilities expanding under EU NIS2 Directive coverage. India's CERT-In compliance-driven procurement cycles offer fastest penetration velocity. Zero-trust architecture convergence with identity-aware proxy integration provides differentiated go-to-market positioning against appliance-centric incumbents. For Investors and Strategic Acquirers: Roll-up economics work for specialized managed security service providers because CISO procurement centralization compresses vendor selection cycles and favors outsourced rule-base tuning. Long-term viability centers on AI-enabled threat detection engine capabilities and autonomous response integration. The signal to watch is ENISA technical standard finalization for EU AI Act high-risk system classification, which will reshape critical infrastructure procurement eligibility.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Acceleration | Pre-certified vendors capture US federal cloud modernization procurement velocity under GSA frameworks. |
| Zero-Trust Architecture Integration | Unified policy enforcement across identity-aware proxies satisfies Fortune 500 platform-centric evaluation requirements. |
| Managed Detection and Response Expansion | Autonomous threat response outsourcing deepens recurring revenue pools for London financial district operators. |
| Multi-Cloud Orchestration Development | API-integrated control planes address segmentation rule consistency across AWS, Azure, and Google Cloud environments. |
| Edge-AI Inference Embedding | Machine learning model integration within packet processing paths reduces latency for sub-microsecond trading environments. |
Study Parameters
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with CISOs, federal procurement officers, managed security service provider executives, and cloud platform engineers alongside secondary validation through FedRAMP authorization databases, ENISA certification registries, SEC 10-K cybersecurity segment disclosures, and hyperscaler capex reports. Bottom-up deployment model sizing and top-down regulatory mandate impact assessment provided triangulation across the analysis window.
Comparable historical periods anchored the projection horizon to pre-pandemic baseline growth patterns and post-NIS2 Directive implementation trajectories. Segmentation modeling spanned deployment architecture, solution type, end-user scale, and service delivery mode, with CAGRs derived from policy enforcement throughput scaling curves and compliance-driven procurement cycle compression. FedRAMP pipeline velocity and EU AI Act technical standard development served as key forecast inputs.
Caveats apply where ENISA standard finalization timelines or FedRAMP authorization backlog clearance could materially shift the outlook for vendor eligibility and procurement concentration. Forecasts reflect documented assumptions about regulatory enforcement intensity and hyperscaler native service pricing trajectories. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Hong Kong Cybersecurity Market
Cybersecurity
Netherlands Cybersecurity Market
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
Vietnam Cybersecurity Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
Enterprise Network Firewall Market
Cybersecurity
Latin America IoT Security Market
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
Education Data Security Market
Cybersecurity
Japan Ransomware Protection Market
Cybersecurity
Bahrain Cybersecurity Market
Cybersecurity
Global Ddos Protection Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
Server Security Market
Cybersecurity
Post-Quantum Cryptography Market
Cybersecurity
Global Database Encryption Market