
 Global Cyber Security in Healthcare Market | 2026-2036
Global Cyber Security in Healthcare Market Size, Share, and Industry Trends Forecast 2026-2036
Global Cyber Security in Healthcare Market Foresight
Legacy antivirus is broadening into AI-driven behavioral analytics as healthcare organizations replace signature-based tools with machine-learning detection. Palo Alto Networks leverages cloud-native architectures to anchor its position in hospital network security. CrowdStrike sustains R&D intensity in endpoint telemetry for medical devices. Fortinet dominates secure SD-WAN deployments connecting rural clinics to central health systems.
Cyber security in healthcare encompasses technologies, processes, and controls that protect patient health information, medical devices, and clinical infrastructure from unauthorized access, disruption, or destruction through encryption protocols, access controls, and continuous threat monitoring. Its primary purpose is ensuring confidentiality, integrity, and availability of health data while maintaining operational continuity of care delivery. Network Security and Cloud Security segments lead current spending as hospitals migrate electronic health records to hybrid environments. Identity & Access Management is the fastest-growing solution category as zero-trust architectures replace perimeter-based models in multi-facility health systems.
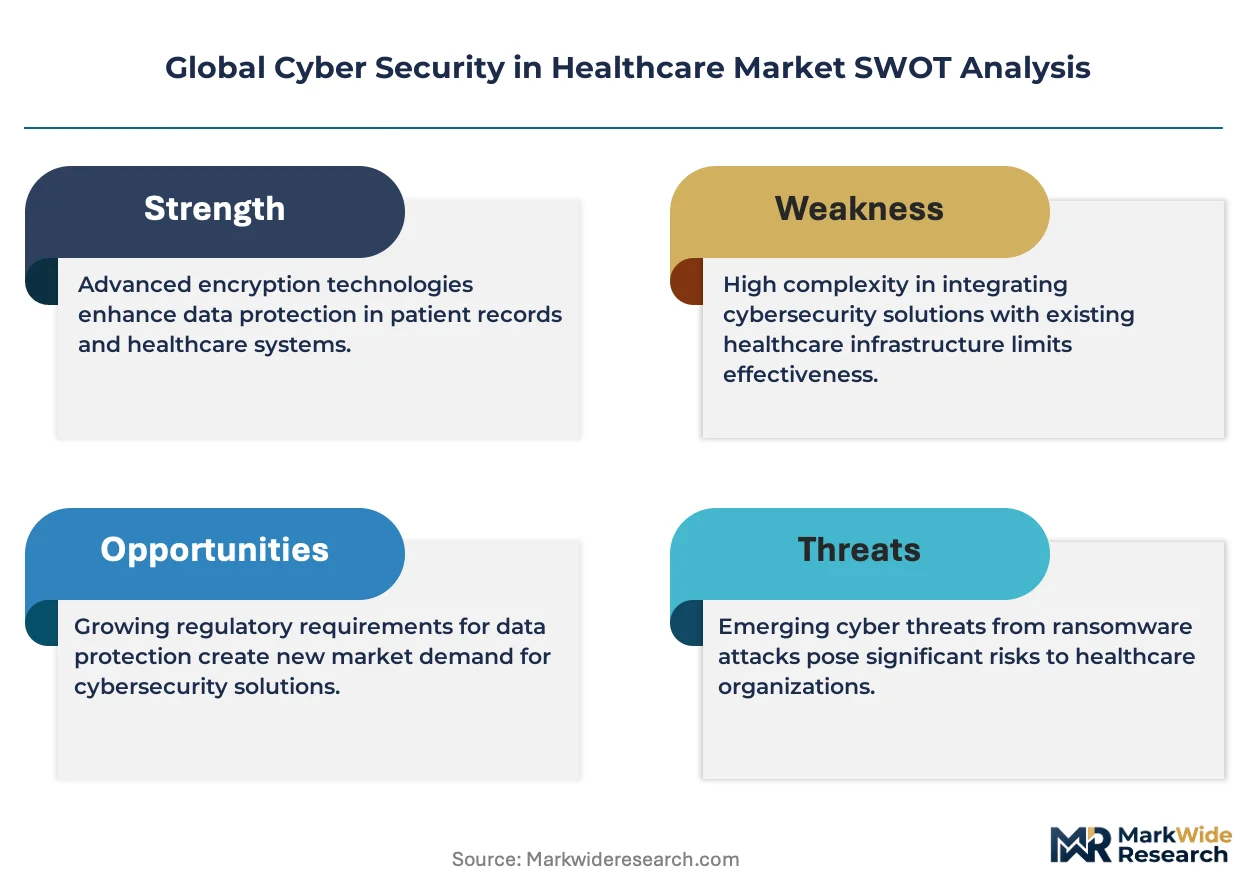
FDA guidance on medical device cyber security, HIPAA security rule enforcement by the Department of Health and Human Services, and the EU NIS2 Directive collectively tighten product standards and incident-response obligations for healthcare delivery organizations. These frameworks shape demand by mandating specific technical controls, driving procurement of managed security services and compliance automation platforms. Stakeholders must monitor the divergence between US sector-specific rules and EU cross-sector mandates when architecting product roadmaps for international health system customers.
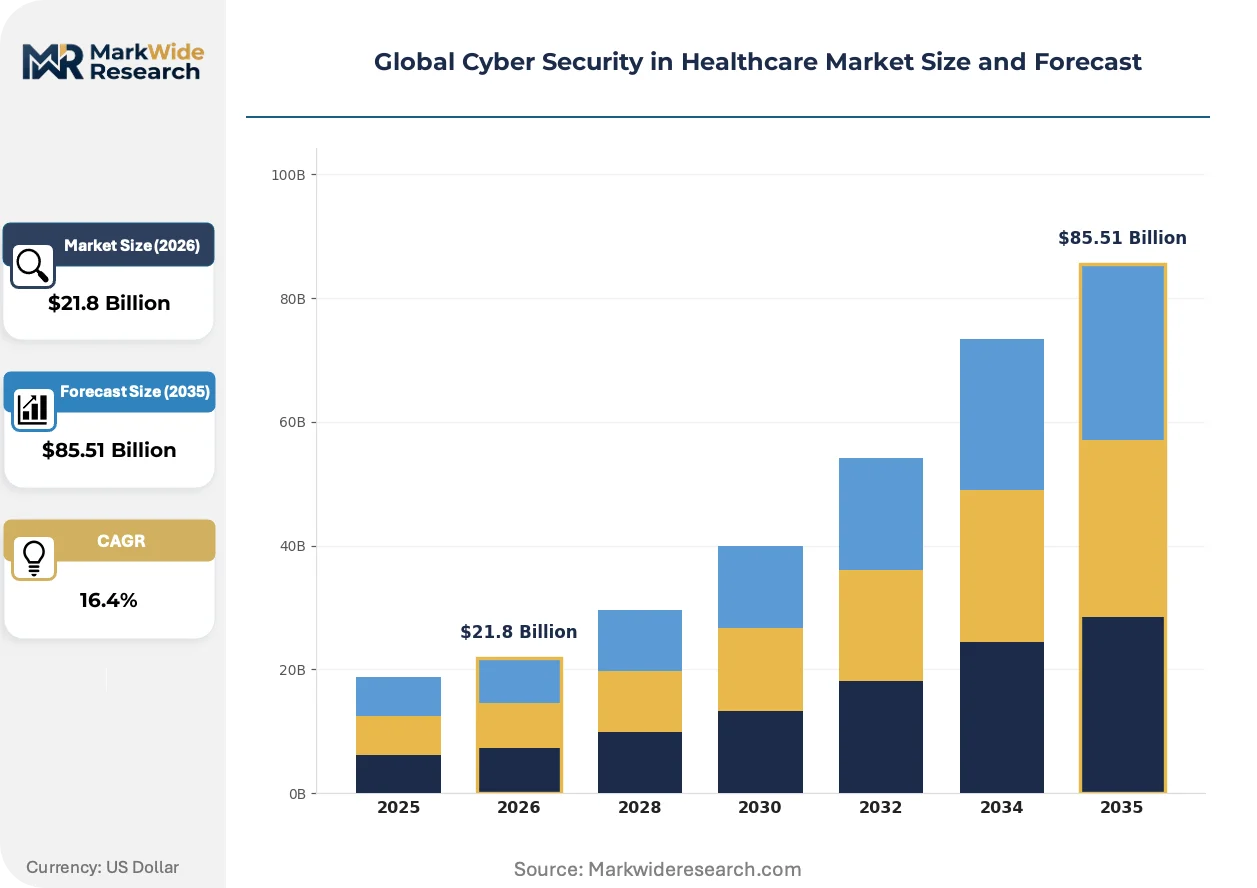
Market Dynamics
The migration of electronic health records to hybrid cloud environments is compressing security architecture refresh cycles across hospital networks, forcing simultaneous investments in network segmentation and zero-trust identity frameworks.
Growth Catalysts
- EU NIS2 Directive:Healthcare operators face mandatory breach-reporting timelines measured in hours rather than days, accelerating procurement of automated incident-response platforms.
- Medical device telemetry expansion:Connected infusion pumps and patient monitors generate continuous data streams that require real-time endpoint detection and response coverage.
- German hospital digitization funds:Federal reimbursement programs tie infrastructure grants to mandatory third-party security audits, creating structural demand for compliance services.
Market Restraints
- Specialized talent scarcity:Healthcare security operations centers struggle to recruit analysts with dual expertise in clinical workflows and threat hunting methodologies.
- Legacy infrastructure interdependence:Decades-old picture archiving and communication systems resist patching without disrupting radiology department productivity.
- Input cost concentration:Cloud security licensing from hyperscale providers consumes disproportionate shares of IT budgets relative to on-premise alternatives.
Strategic Opportunities
- India's hospital digitization wave:The country's national health stack creates greenfield deployments where security-by-design architectures bypass retrofit constraints.
- FDA premarket guidance:Medical device manufacturers must embed security controls during product development, opening consulting and testing service revenue streams.
- Convergence of AI and behavioral analytics:Machine learning models trained on clinical device baselines enable anomaly detection without signature-dependent updates.
Industry Challenges
- Interoperability certification delays:Health Level Seven International standards evolve slower than vendor implementation timelines, fragmenting secure data exchange.
- Clinical workflow integration friction:Security controls that interrupt physician authentication sequences face adoption resistance despite policy mandates.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Cyber Security in Healthcare Market |
| Market Size in 2026 | $21.8 Billion |
| Market Size in 2035 | $85.51 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Network Security, Endpoint Protection, Identity & Access Management, Data Loss Prevention, Application Security, Cloud Security Deployment Mode: On-Premises, Cloud-Based, Hybrid, Managed Security Service Application Area: Patient Data Protection, Medical Device Security, Compliance Management, Insider Threat Detection, Threat Intelligence End User: Hospitals, Diagnostic Laboratories, Health Insurance Providers, Telehealth Services, Research Institutions, Pharmacies |
| Companies Covered | IBM, Cisco Systems, Palo Alto Networks, Fortinet, Trend Micro, CrowdStrike, Check Point Software Technologies, Imperva, CyberArk, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Cyber Security in Healthcare Market Shifts & Advancements
Security architecture in healthcare is pivoting from perimeter defense to continuous verification models, with artificial intelligence and regulatory pressure as twin accelerants reshaping procurement priorities.
Extended detection and response platforms are integrating machine-learning inference directly at the network edge to process medical device telemetry without cloud round-trip latency. Rural health systems with limited security staffing adopt managed detection services that aggregate telemetry across dozens of clinics. This distributed architecture is integrating clinical operational technology networks with traditional IT security operations centers, collapsing silos that previously obscured lateral movement paths.
The FDA's premarket cyber security guidance for medical devices now mandates software bill of materials disclosure and vulnerability management plans as conditions for market authorization. Device manufacturers must demonstrate patchability and secure update mechanisms during design review phases. European manufacturers exporting to the United States are restructuring quality management systems to satisfy both FDA documentation requirements and EU MDR technical file standards simultaneously.
Hospital procurement committees now evaluate security vendors on clinical workflow impact metrics rather than technical feature checklists alone. Chief medical information officers veto endpoint agents that degrade electronic health record responsiveness during peak census periods. This behavioral shift is most pronounced in academic medical centers where physician satisfaction scores influence vendor selection alongside security efficacy benchmarks.
Global Cyber Security in Healthcare Market Segmentation
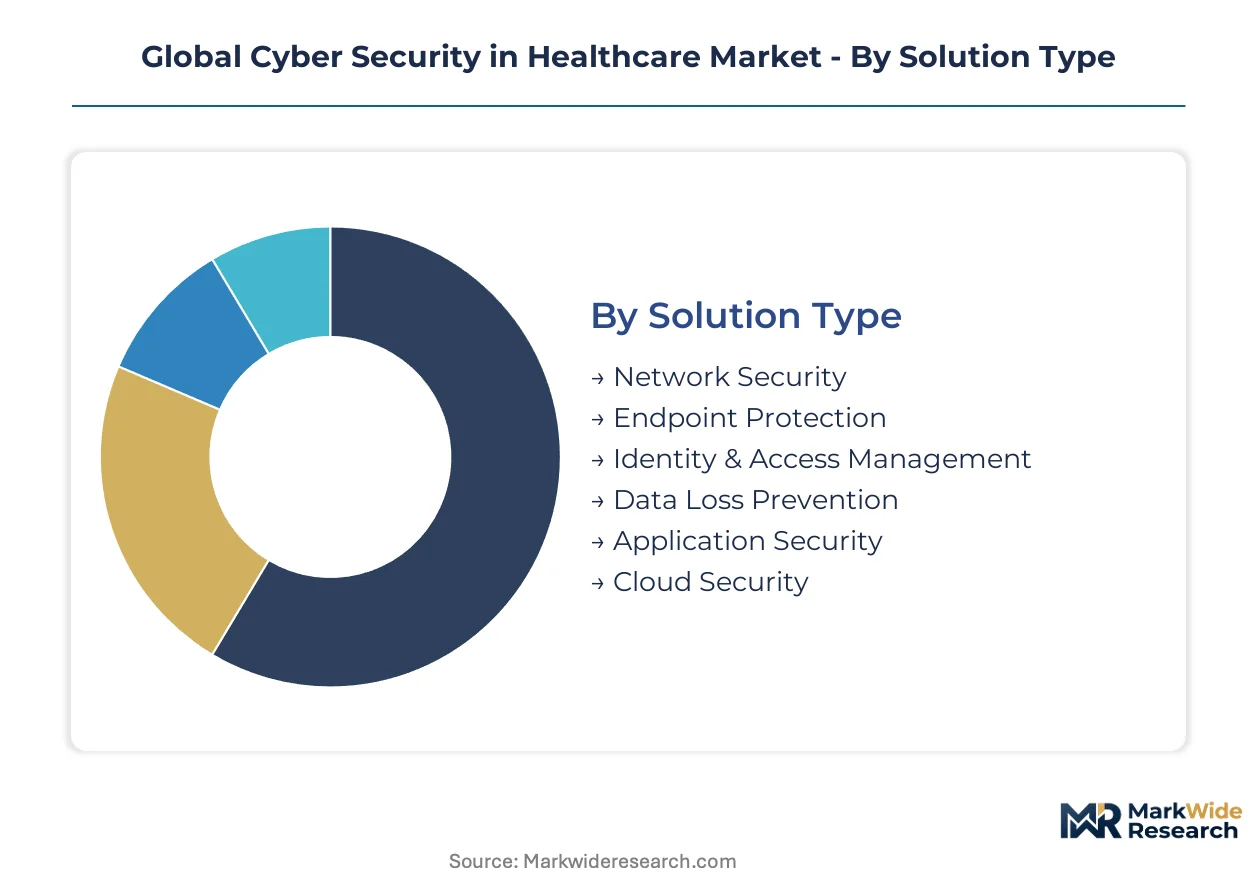
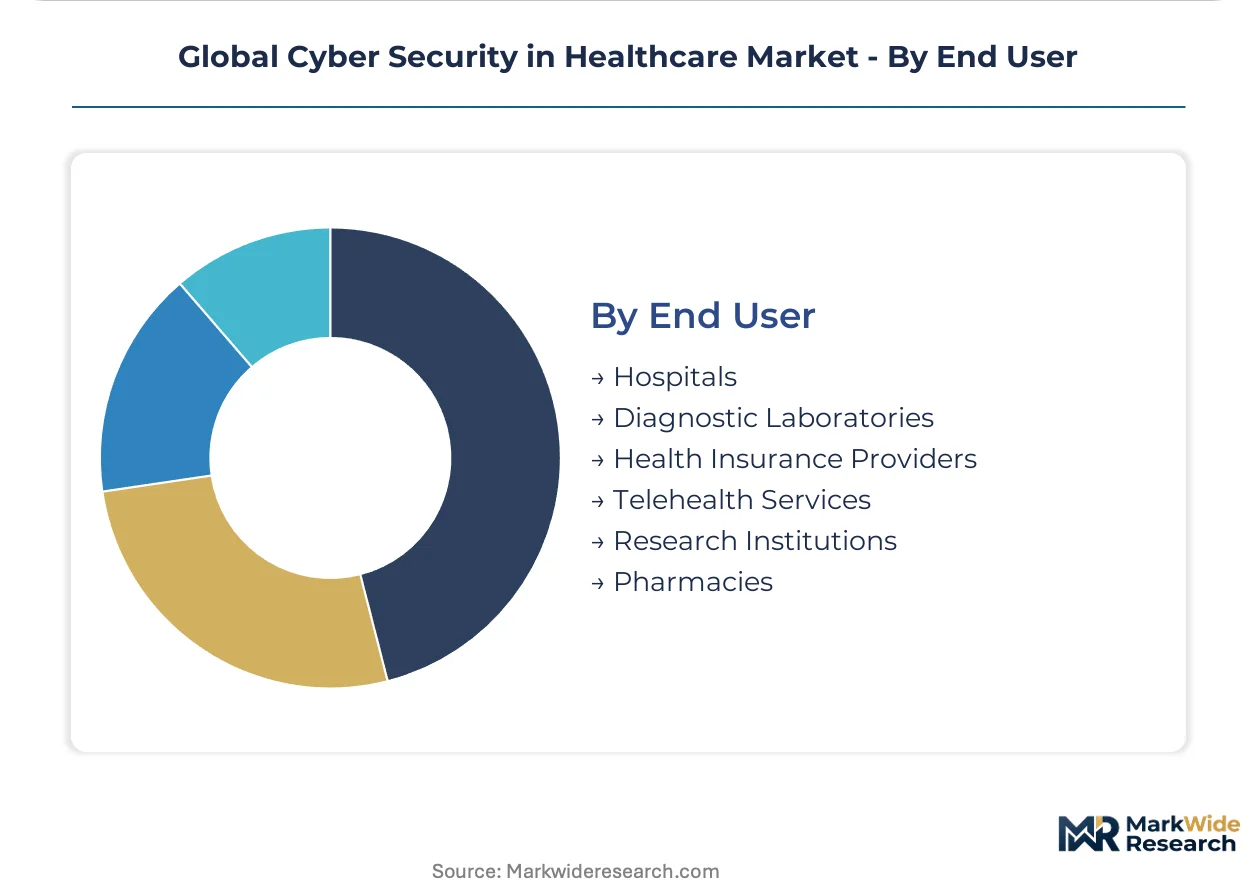
Healthcare procurement committees evaluate cyber security investments through multiple lenses simultaneously. Solution capabilities, deployment economics, clinical workflow integration, and end-user scale each reshape vendor selection criteria across hospital networks and ambulatory settings.
Solution Type:
Procurement committees prioritize technical capabilities that map directly to breach scenarios their institutions have experienced or observed in peer organizations.
- Network Security:Segmentation architectures isolate electronic health record systems from guest Wi-Fi and medical device VLANs. United States hospital networks allocate capital here first following ransomware incidents that propagated laterally through flat architectures.
- Identity & Access Management:Zero-trust frameworks replace perimeter-based VPN models as multi-facility health systems consolidate authentication across dozens of clinical sites. German hospital digitization funds mandate privileged access management as a condition of federal reimbursement.
- Endpoint Protection:Agent-based detection covers workstations and clinical servers against commodity malware.
- Data Loss Prevention:Content inspection prevents unauthorized exfiltration of patient records through email and web channels.
- Application Security:Code scanning and runtime protection secure custom-developed patient portals and revenue cycle applications.
- Cloud Security:Configuration management and workload protection address misconfigurations in hybrid electronic health record environments.
Network Security leads on scale; Identity & Access Management leads on momentum.
Deployment Mode:
IT budget concentration and security staffing levels determine whether health systems build internal capabilities or consume security as a managed service.
- Cloud-Based:Elastic capacity supports seasonal census fluctuations without capital expenditure cycles. Telehealth services expanding across India deploy here to avoid data center construction timelines.
- Managed Security Service:Twenty-four-hour coverage from external security operations centers substitutes for scarce analyst talent in rural United States health systems. The EU NIS2 Directive's hourly breach-reporting requirements accelerate outsourcing decisions.
- On-Premises:Air-gapped architectures satisfy risk-averse compliance officers in research institutions handling genomic data.
- Hybrid:Split architectures keep patient data on-premise while leveraging cloud analytics for threat detection.
Cloud-Based deployments dominate new procurement; Managed Security Service expands most quickly among resource-constrained organizations.
Application Area:
Regulatory enforcement patterns and incident publicity direct investment toward specific risk domains.
- Patient Data Protection:Encryption at rest and in transit satisfies HIPAA security rule requirements enforced by the Department of Health and Human Services through settlement agreements.
- Medical Device Security:FDA premarket guidance mandates vulnerability management plans for connected infusion pumps and patient monitors. Manufacturers must demonstrate patchability during design reviews.
- Compliance Management:Automated evidence collection reduces audit preparation burden for multi-jurisdictional health systems.
- Insider Threat Detection:Behavioral analytics identify unusual access patterns by employees with legitimate credentials.
- Threat Intelligence:Information sharing with sector-specific organizations accelerates detection of campaigns targeting healthcare.
Patient Data Protection absorbs the largest share of recurring investment; Medical Device Security gains share fastest as device connectivity proliferates.
End User:
Scale and regulatory exposure create diverging procurement sophistication across healthcare delivery models.
- Hospitals:Enterprise security operations centers with dedicated staff manage complex multi-vendor environments. Academic medical centers in the United States evaluate vendors on physician workflow impact metrics alongside technical benchmarks.
- Telehealth Services:Greenfield platforms without legacy technical debt implement security-by-design architectures. India's national health stack enables this approach at scale.
- Diagnostic Laboratories:High-volume test processing creates attractive ransomware targets requiring specialized backup architectures.
- Health Insurance Providers:Member data aggregation across provider networks demands robust third-party risk management.
- Research Institutions:International collaboration requirements complicate data residency and access control policies.
- Pharmacies:Distributed retail footprints with limited IT staff rely heavily on managed services and franchise-mandated security standards.
Hospitals command the largest absolute spending; Telehealth Services demonstrate the steepest expansion trajectory as virtual care models mature.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Hospital digitization funds in Germany create structural demand for compliance services, while ransomware incidents in the United States accelerate procurement of endpoint protection platforms across acute care networks.
United States
Ransomware attacks against hospital networks drive procurement of network segmentation and zero-trust identity frameworks. The Department of Health and Human Services enforces HIPAA security rule violations through settlement agreements exceeding millions of dollars. Academic medical centers in Boston and the Research Triangle evaluate vendors on physician workflow impact metrics alongside technical benchmarks.
Germany
Federal reimbursement programs tie infrastructure grants to mandatory third-party security audits, creating structural demand for compliance automation platforms. The EU NIS2 Directive tightens breach-reporting timelines for healthcare operators to hours rather than days. Hospital networks in North Rhine-Westphalia and Bavaria concentrate procurement of privileged access management solutions.
India
The national health stack enables greenfield deployments where security-by-design architectures bypass retrofit constraints of legacy systems. The country's national pharmaceutical regulator aligns medical device security standards with international frameworks. Telehealth platforms in Bangalore and Hyderabad implement cloud-native security without data center construction timelines.
Japan
Aging demographics expand connected home healthcare devices requiring endpoint detection and response coverage. METI guidelines on medical device cyber security mandate vulnerability disclosure and patch management plans. Medical device manufacturers in the Kansai region restructure quality management systems to satisfy both domestic and export market requirements.
United Kingdom
NHS Digital mandates cyber security standards for all health and care organizations, with enforcement through the Data Security and Protection Toolkit. The National Cyber Security Centre provides sector-specific threat intelligence to healthcare delivery organizations. London-based hospital trusts consolidate security operations across multiple acute sites under unified governance structures.
Global Cyber Security in Healthcare Market Competitive Landscape
Strategic partnerships dominate the current landscape as vendors integrate clinical workflow expertise with threat detection capabilities. The market exhibits tiered concentration with global platform providers, regional specialists, and emerging cloud-native entrants competing for procurement contracts. Two archetypes prevail: endpoint protection platforms with medical device telemetry capabilities, and managed security services delivering twenty-four-hour coverage to resource-constrained health systems. Portfolio diversification and technology licensing represent the dominant competitive moves as vendors expand beyond traditional network security into identity management and cloud workload protection.
Within the cloud-native platform tier, Palo Alto Networks and CrowdStrike occupy positions exemplifying the shift toward AI-driven behavioral analytics replacing signature-based detection. Fortinet represents the secure networking archetype with dominant deployments connecting rural clinics to central health systems. These three companies anchor the competitive dynamics as hospital procurement committees evaluate vendors on clinical workflow impact metrics rather than technical feature checklists alone.
| Leading Market Players |
|---|
| IBM |
| Cisco Systems |
| Palo Alto Networks |
| Fortinet |
| Trend Micro |
| CrowdStrike |
| Check Point Software Technologies |
| Imperva |
| CyberArk |
| Others |
Supply & Pricing Matrix
Cloud infrastructure licensing indices cascade through healthcare security procurement, compressing margins for mid-tier vendors while hyperscale providers capture premium pricing through bundled analytics capabilities. Hospital procurement committees in Germany and the United States now negotiate enterprise agreements that tether endpoint protection costs to electronic health record deployment scale.
Pricing Analysis
Input-cost pass-through from hyperscale cloud providers dominates pricing dynamics, with SaaS-tiered subscription models stratifying across premium AI-driven behavioral analytics, standard signature-based detection, and economy managed service tiers. Price differentiation rests on FDA certification alignment and clinical workflow integration depth rather than raw technical specifications. Pricing pressure stems from federal reimbursement programs in Germany mandating security audits as grant conditions, forcing budget reallocation toward compliance services. Rural United States health systems exhibit highest price sensitivity, while academic medical centers prioritize physician workflow impact metrics over unit cost.
Supply Chain Analysis
Direct-to-OEM channels handle hyperscale hospital network demand, while value-added distributors serve mid-market ambulatory chains with bundled implementation services. Component manufacturing concentrates in the United States, Israel, and Ireland, with threat intelligence feeds drawing from Tallinn-based sector-specific sharing centers. Supply chain risk centers on single-source vulnerability for medical device firmware signing certificates, where compromise would propagate across entire hospital fleets. Distribution runs through GPO-affiliated procurement platforms that aggregate demand across multi-facility health systems for volume-based pricing leverage.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market represents a late-cycle quality story where zero-trust architecture mandates are displacing perimeter-based solutions, elevating procurement criteria toward clinical workflow integration and continuous verification capabilities.
For Market Incumbents: Extend platform consolidation into identity management and cloud workload protection to defend against cloud-native entrants eroding endpoint protection margins. Fortify medical device telemetry partnerships with infusion pump and patient monitor manufacturers, as FDA premarket guidance hardens patchability requirements into design-phase obligations. Prioritize R&D investment in edge-based machine learning inference to eliminate cloud round-trip latency that academic medical centers reject during peak census periods.
For New Entrants and Emerging Players: Cloud-native channel routes through India's national health stack offer white-space penetration without legacy retrofit constraints, bypassing the technical debt that slows United States hospital procurement cycles. Target telehealth platforms in Bangalore and Hyderabad implementing security-by-design architectures from inception. Pursue managed detection service contracts with rural United States health systems where twenty-four-hour coverage substitutes for scarce analyst talent.
For Investors and Strategic Acquirers: Asymmetric upside sits with cloud-native platform providers possessing medical device telemetry capabilities and existing hospital procurement committee relationships. Long-term viability across the analysis window favors vendors with integrated clinical workflow expertise rather than pure-play threat detection specialists. Monitor FDA enforcement patterns on software bill of materials disclosure as inflection indicator for medical device security service demand acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Deployment | Multi-facility health systems in Germany mandate privileged access management for federal reimbursement eligibility. |
| Medical Device Security Partnership | FDA premarket guidance requires manufacturers to demonstrate patchability during design review phases. |
| Managed Detection Service Expansion | EU NIS2 Directive hourly breach-reporting requirements accelerate outsourcing decisions among rural United States systems. |
| Clinical Workflow Integration Investment | Academic medical centers veto endpoint agents degrading electronic health record responsiveness during peak census. |
| Cloud-Native Platform Development | India's national health stack enables greenfield deployments without data center construction timelines. |
Research Methodology
Multiple input streams — hospital procurement committee interviews, biomedical engineer surveys, GPO contract database analysis, and regulatory filing review — were reconciled through bottom-up and top-down triangulation. Primary fieldwork engaged hospital CISOs, clinical informatics officers, medical device quality managers, and federal reimbursement program administrators across the United States, Germany, and India. Secondary validation drew from FDA premarket submission databases, EU NIS2 implementation guidance, hospital procurement platform disclosures, and CMS Medicare reimbursement schedules.
Data-stream reconciliation anchored the analytical framework across the projection horizon, modeling solution type, deployment mode, application area, and end-user scale dimensions alongside regional regulatory cluster variations. CAGRs were derived from segment-level growth trajectory synthesis rather than aggregate market extrapolation. Forecast inputs incorporated medical device connectivity proliferation rates, zero-trust architecture adoption curves in multi-facility systems, and cloud infrastructure licensing cost trajectories from hyperscale providers.
The model assumes a particular technology adoption path; alternative pathways for AI-driven behavioral analytics replacing signature-based detection would alter the outlook if clinical workflow integration friction proves more persistent than baseline assumptions. Forecasts reflect documented assumptions on regulatory enforcement intensity and hospital digitization fund disbursement timing. Periodic stress-testing of base assumptions is recommended.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
Threat Hunting Market
Cybersecurity
Cloud-Based IDS IPS Market
Cybersecurity
Cyber Security in Energy Market
Cybersecurity
Penetration Testing Market
Cybersecurity
Cloud Authentication Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Kuwait Cybersecurity Market
Cybersecurity
Managed SIEM Service Market
Cybersecurity
Data Diode Solution Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Global Cloud Encryption Market
Cybersecurity
Global Virtualization Security Market
Cybersecurity
Middle East and Africa Cybersecurity Market