
 Cyber Security Consulting Market | 2026-2036
Cyber Security Consulting Market Size, Share, and Industry Trends Forecast 2026-2036
Cyber Security Consulting Market Analysis
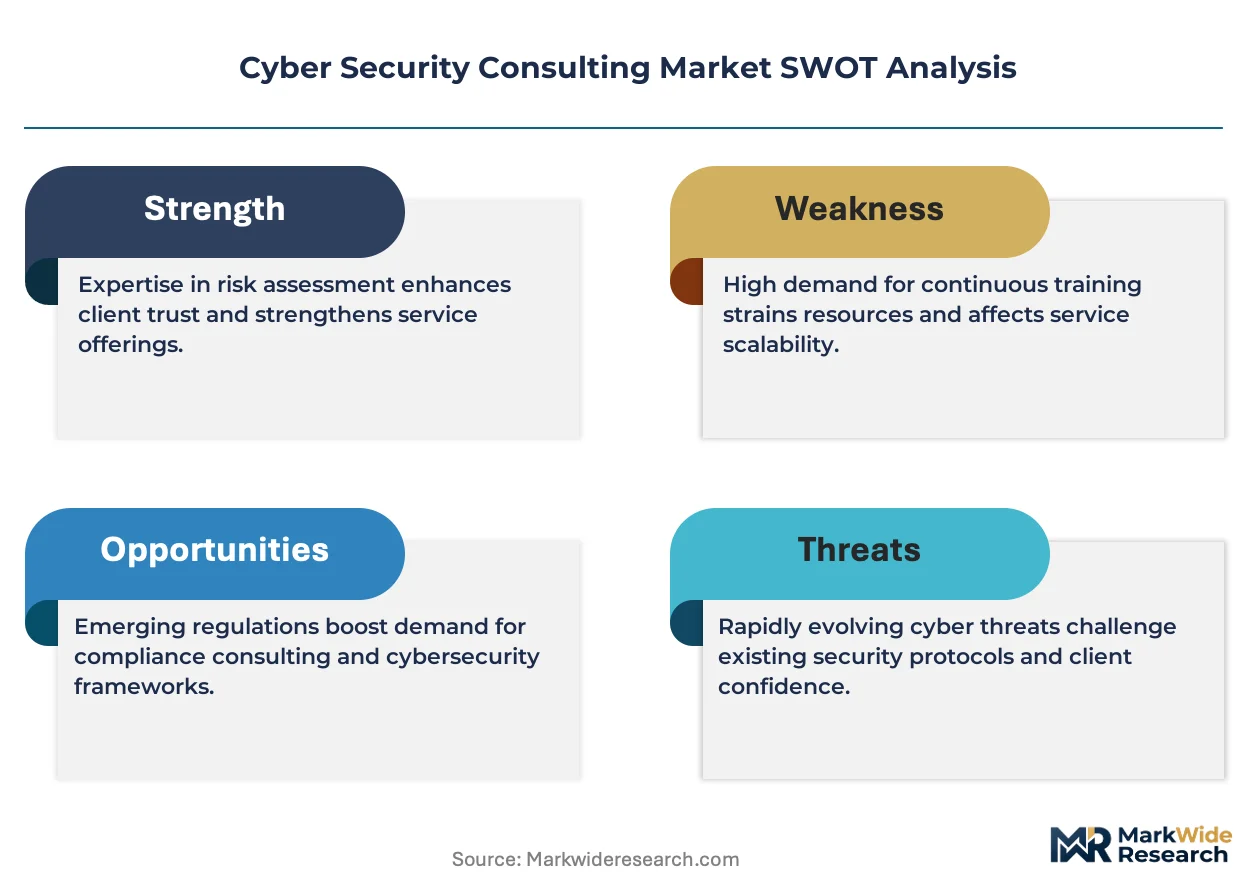
The available pool of seasoned cloud-security architects is collapsing across North America and Western Europe, forcing consultancies to raise compensation and extend training pipelines. Deloitte leverages its risk-advisory heritage to anchor enterprise transformation engagements. Booz Allen Hamilton dominates federal and defense-sector mandates in the United States. Accenture competes through its managed-security-services overlay, bundling consulting with continuous monitoring.
Cyber security consulting encompasses advisory, assessment, and implementation services that protect digital assets, ensure regulatory compliance, and respond to breaches; practitioners deploy frameworks such as NIST SP 800-53 to evaluate control maturity and map residual risk to business-critical operations. Risk assessment and incident response services lead revenue generation as boards prioritize breach-readiness over checkbox compliance. Cloud-based deployment models represent the fastest-growing structural segment, reflecting enterprise migration to distributed infrastructure and the complexity of securing multi-tenant environments.
The U.S. SEC mandates timely disclosure of material cyber incidents, the EU NIS2 Directive imposes stricter supply-chain security obligations, and India's CERT-In issues mandatory reporting timelines for critical sectors—each framework expanding the scope and urgency of external advisory engagements. Stakeholders must monitor how fragmented national requirements reshape cross-border service delivery and certification portability.
Market Dynamics
The collapse of seasoned cloud-security architect availability across North America and Western Europe is forcing consultancies to extend training pipelines and raise compensation, fundamentally reshaping how advisory services scale and price.
Growth Catalysts
- EU NIS2 Directive:Tightened incident-reporting obligations for critical infrastructure operators across European member states are expanding mandatory external advisory engagements and compliance audit volumes.
- Financial services:Banks and asset managers are expanding advisory budgets specifically for ransomware preparedness, creating dedicated procurement lines for breach-readiness assessments.
- Cloud migration complexity:Enterprise shifts to multi-tenant distributed infrastructure are generating sustained demand for architecture review and control-mapping services.
Market Restraints
- Certified talent scarcity:The shallow pool of professionals holding CISSP or CISM credentials in Germany and India is constraining delivery capacity and inflating project costs.
- Input cost volatility:Specialized threat-intelligence feeds and automated scanning tools represent rising fixed costs that compress margins on fixed-fee engagements.
- Regulatory fragmentation:Divergent national reporting timelines between the U.S. SEC, EU NIS2, and India's CERT-In create compliance friction for cross-border advisory mandates.
Strategic Opportunities
- Underpenetrated segments:Mid-market manufacturers in India lack mature security operations centers, presenting white space for packaged assessment-to-implementation offerings.
- Technology convergence:The intersection of zero-trust architecture with identity governance platforms enables consultancies to bundle advisory with tooling procurement.
- Managed service overlay:Continuous monitoring contracts attached to initial transformation engagements create recurring revenue streams and deepen client retention.
Industry Challenges
- Skill pipeline gaps:Universities in the United States and Germany produce insufficient graduates with practical cloud-security architecture experience, forcing firms to build internal academies.
- Integration complexity:Legacy mainframe environments at U.S. federal agencies resist standard NIST SP 800-53 control mapping, extending project timelines and requiring specialized subcontractor networks.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cyber Security Consulting Market |
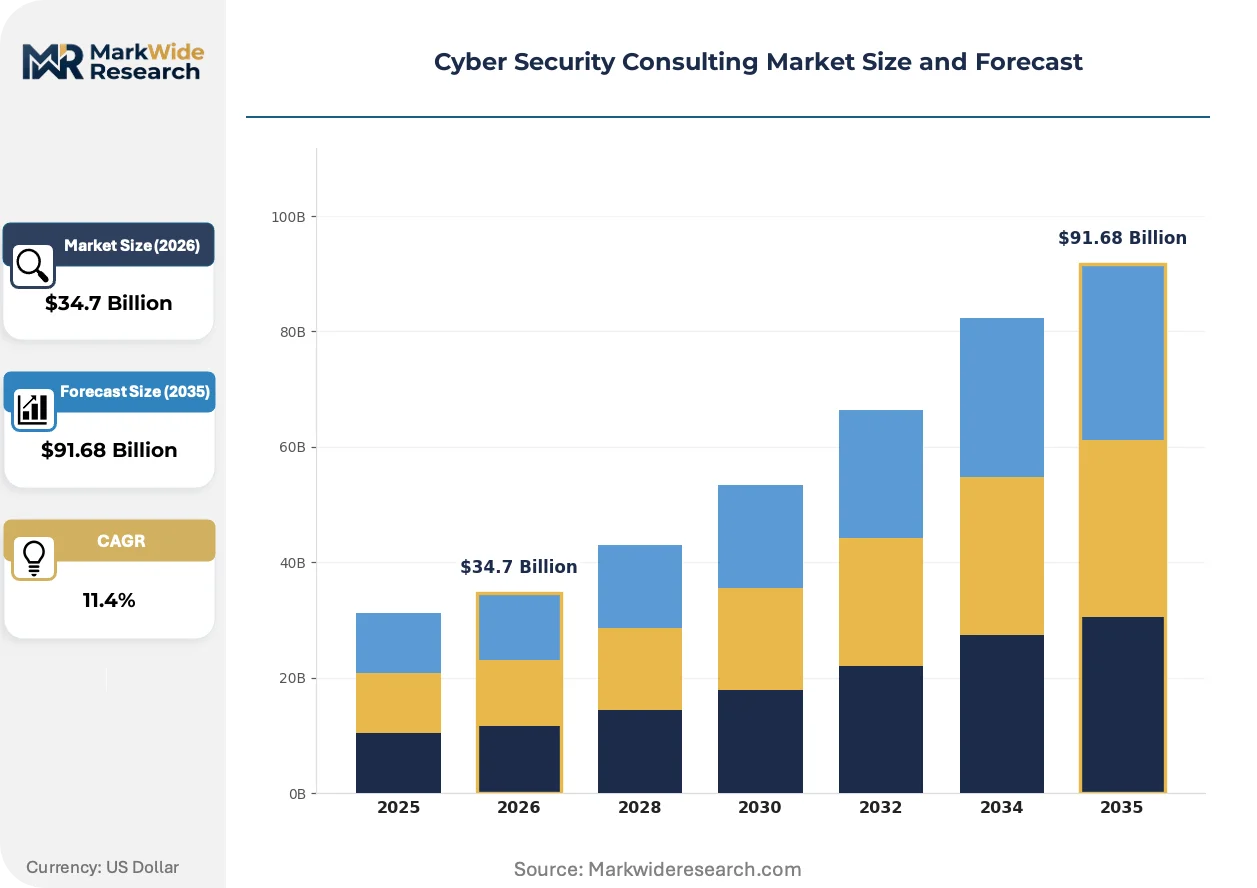
| Market Size in 2026 | $34.7 Billion |
| Market Size in 2035 | $91.68 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Risk Assessment, Incident Response, Compliance Management, Managed Security Services Industry Vertical: Finance, Healthcare, Retail, Government Deployment Model: On-Premises, Cloud-Based, Hybrid, Virtualized Client Type: SMEs, Enterprises, Startups, Corporates |
| Companies Covered | KPMG, Booz Allen Hamilton, Deloitte, CrowdStrike Services, IBM Security, Accenture, EY, FTI Consulting, PwC, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cyber Security Consulting Market Emerging Trajectories
Generative AI tooling is actively reshaping how security assessments are conducted, compressing documentation cycles while introducing new verification requirements that advisory firms must address.
Automated penetration-testing platforms equipped with machine-learning exploit generation are displacing manual red-team exercises for routine compliance validations. Mid-market enterprises in the United States are adopting these tools at accelerated procurement cycles. The shift is compressing pricing for baseline assessment services while elevating demand for human-led interpretation of machine-generated findings.
The EU AI Act imposes risk-classification requirements on automated decision systems used in critical infrastructure. Industrial operators must now document algorithmic transparency and conduct adversarial robustness testing before deployment. German energy utilities and French transportation networks are engaging consultancies to map AI system inventories against the Act's prohibited and high-risk categories.
Enterprise buyers are unbundling after-sales advisory from initial implementation contracts, opting for discrete statement-of-work engagements tied to specific breach scenarios or regulatory deadlines. This pattern is displacing traditional multi-year managed service retainers. Financial services firms in India demonstrate the most pronounced shift, procuring incident-response retainers separately from transformation architecture work.
Cyber Security Consulting Market Segmentation
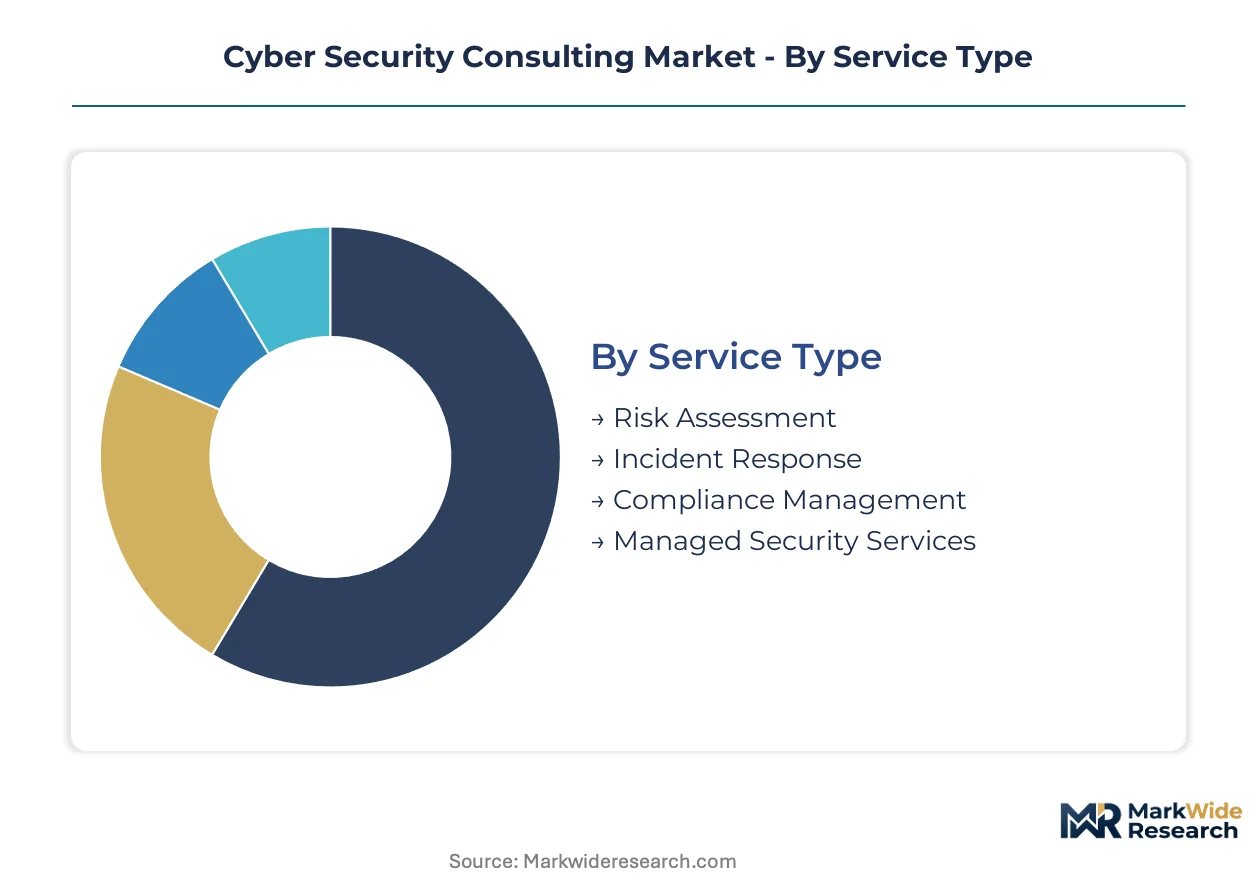
Cyber security consulting segments map directly to procurement workflows, with service type dictating contract structure and deployment model determining delivery architecture. Understanding these splits reveals where advisory margins concentrate and which client configurations require specialized staffing.
Service Type:
Channel mix varies sharply across service categories, with risk assessment flowing through direct sales teams while managed security services increasingly route through technology distributors and cloud marketplaces.
- Risk Assessment:Comprehensive evaluation of control maturity against frameworks like NIST SP 800-53, producing gap analyses and remediation roadmaps. Financial services firms in the United States commission these engagements most intensively as SEC disclosure rules harden board accountability for breach preparedness.
- Incident Response:Retainer-based advisory and post-breach containment services including forensic investigation and recovery coordination. German critical infrastructure operators are expanding procurement here as EU NIS2 mandates tighten reporting windows and penalty structures.
- Compliance Management:Continuous advisory on regulatory adherence across fragmented national frameworks.
- Managed Security Services:Ongoing monitoring and threat detection bundled with consulting overlays.
Risk assessment dominates installed base. Incident response is where expansion concentrates.
Industry Vertical:
Cost tier stratification separates these verticals, with government and finance commanding premium pricing for cleared personnel and specialized certifications while retail operates at compressed rates.
- Finance:Banks, asset managers, and insurers requiring ransomware preparedness assessments and fraud detection architecture. Indian banks under RBI supervision are expanding advisory budgets fastest as digital payment volumes surge and regulatory scrutiny intensifies.
- Government:Federal, state, and defense-sector mandates demanding cleared consultants and air-gapped assessment protocols. United States agencies consume the largest absolute volume, with Booz Allen Hamilton and comparable contractors capturing multi-year transformation contracts.
- Healthcare:HIPAA-covered entities navigating medical device security and patient data protection.
- Retail:Payment card industry compliance and e-commerce fraud prevention at scale.
Government anchors revenue concentration. Finance is climbing the fastest.
Deployment Model:
Customer type alignment shapes these segments, with enterprises distributing across all four models while SMEs cluster in cloud-based and virtualized delivery to minimize capital commitment.
- Cloud-Based:Architecture review and control mapping for multi-tenant distributed infrastructure. German energy utilities and French transportation networks are procuring these services urgently as EU AI Act risk-classification requirements extend to automated systems hosted in cloud environments.
- Hybrid:Integrated security spanning on-premises legacy systems and cloud workloads. United States federal agencies with mainframe dependencies drive specialized demand here, requiring subcontractors with decades-old system expertise.
- On-Premises:Traditional air-gapped assessments for classified or regulated environments.
- Virtualized:Container and virtual machine security for software-defined infrastructure.
Hybrid retains the largest project pipeline. Cloud-based is gaining share fastest.
Client Type:
Maturity differentiation separates these tiers, with enterprises demanding bespoke transformation roadmaps and SMEs accepting standardized assessment packages.
- Enterprises:Global organizations with complex multi-jurisdiction compliance obligations and dedicated CISO functions. These clients unbundle advisory from implementation, procuring discrete statement-of-work engagements tied to specific breach scenarios rather than traditional multi-year retainers.
- SMEs:Mid-market organizations lacking mature security operations centers. Indian manufacturers represent significant white space, with packaged assessment-to-implementation offerings penetrating this historically underserved tier.
- Startups:Venture-backed technology firms prioritizing speed-to-market security baselines.
- Corporates:Large non-technology enterprises with legacy IT estates and compliance-driven procurement.
Enterprises dominate absolute spend. SMEs are where expansion concentrates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The SEC mandates timely disclosure of material cyber incidents in the United States, establishing the most demanding transparency regime worldwide and driving advisory demand across federal and commercial sectors.
United States
Financial services firms commission breach-readiness assessments most intensively as board accountability hardens. The SEC disclosure framework compels asset managers and banks to document incident response protocols. New York and Washington DC concentrate procurement for federal and defense-sector transformation mandates.
Germany
Critical infrastructure operators expand incident-response retainers as EU NIS2 reporting windows tighten. The national cybersecurity authority enforces supply-chain security obligations across energy and transportation networks. Munich and Frankfurt anchor advisory demand from industrial conglomerates and financial institutions.
India
Banks under RBI supervision accelerate advisory budgets fastest as digital payment volumes surge. CERT-In mandates mandatory reporting timelines for critical sectors including finance and telecommunications. Mumbai and Bangalore cluster procurement for assessment-to-implementation services targeting mid-market manufacturers.
United Kingdom
Enterprises unbundle advisory from implementation, procuring discrete engagements tied to specific regulatory deadlines. The Information Commissioner's Office enforces data protection obligations across cloud migration projects. London dominates spend concentration for multi-jurisdiction compliance architecture.
France
Transportation networks engage consultancies to map AI system inventories against EU AI Act risk classifications. The national data protection regulator supervises algorithmic transparency requirements for automated decision systems. Paris anchors demand from energy utilities confronting cloud-hosted infrastructure complexity.
Cyber Security Consulting Market Vendor Landscape
A small set of integrated leaders sits above a broader specialist tier, creating a two-layer structure where scale confers bundling advantages. The upper tier commands premium pricing through managed-security-service overlays that attach recurring monitoring to initial transformation work. Specialist competitors differentiate through cleared personnel for federal mandates or vertical-specific compliance expertise. Dominant competitive moves include strategic partnerships with cloud hyperscalers and portfolio diversification into zero-trust architecture tooling.
Among advisory-led conglomerates, Deloitte and Accenture exemplify the integrated archetype by combining risk-advisory heritage with continuous monitoring capabilities. Booz Allen Hamilton occupies a distinct position within the federal-specialist tier, anchoring defense-sector mandates through security-cleared delivery networks. These three entities represent how scale, clearance access, and service bundling separate market tiers.
| Leading Market Players |
|---|
| KPMG |
| Booz Allen Hamilton |
| Deloitte |
| CrowdStrike Services |
| IBM Security |
| Accenture |
| EY |
| FTI Consulting |
| PwC |
| Others |
Supply Flow & Price Mechanics
CISSP and CISM certification requirements gate both consultant qualification and project rate differentiation, compressing margins for uncredentialed delivery while enabling premium pricing for cleared federal practitioners. This dual-gating mechanism concentrates pricing power among firms with established training academies and security-cleared labor pools.
Pricing Analysis
United States federal mandates command 40-60% rate premiums over commercial engagements due to clearance overhead and air-gapped delivery protocols. Project-based pricing dominates, with risk assessment engagements structured as fixed-fee deliverables and managed security services migrating toward subscription models. Price differentiation hinges on certification tier and vertical specialization, with cleared personnel and AI-act compliance expertise commanding sustained premiums. Cost compression in baseline assessment services is intensifying as automated penetration-testing platforms displace manual red-team exercises. Mid-market manufacturers in India exhibit highest price sensitivity, while United States federal agencies demonstrate lowest sensitivity due to mandate-driven procurement.
Supply Chain Analysis
The United States and Germany produce the deepest pools of cleared security architects and framework-certified practitioners, anchoring high-value advisory delivery. India supplies rapidly scaling delivery capacity for implementation and monitoring services, though credential density lags. Specialized threat-intelligence feeds from Israel and the United Kingdom, automated scanning platforms from the United States, and cloud-security tooling from hyperscalers constitute critical input dependencies. Single-source vulnerability concentrates in cleared personnel pipelines, where security clearance backlogs create 12-18 month hiring friction. Distribution runs through direct enterprise sales for transformation engagements, with managed services increasingly routing through cloud marketplaces and technology distributors.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Regulatory fragmentation across the United States SEC, EU NIS2, and India's CERT-In creates specialization niches for compliance-native advisory practices. This fragmentation rewards targeted capability investments over scale-based bundling.
For Market Incumbents: Compound recurring revenue attachment by embedding continuous monitoring contracts within initial transformation engagements. Build captive training academies in the United States and Germany to offset certified talent scarcity and defend margin position against automated assessment platforms. Channel control through hyperscaler partnerships protects access to cloud-native implementation workloads. For New Entrants and Emerging Players: Mid-market manufacturers in India lacking mature security operations centers present the most penetrable white space, with packaged assessment-to-implementation offerings addressing historically underserved demand. Zero-trust architecture integration with identity governance platforms offers a discrete entry wedge, enabling advisory-tooling bundles that bypass incumbent managed-service scale advantages. Channel partnerships with regional system integrators accelerate procurement access. For Investors and Strategic Acquirers: EU NIS2 implementation reshapes the acquisition landscape by elevating incident-response capability valuations as reporting windows tighten. Firms with cleared federal networks and AI-act compliance methodologies represent priority target archetypes. The signal to watch is consolidation velocity among mid-tier specialists as compliance deadlines compress buyer decision cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Managed Security Service Launch | Attaches recurring revenue to transformation engagements and deepens client retention across federal and commercial accounts. |
| Zero-Trust Architecture Certification | Enables bundling of advisory services with identity governance tooling procurement in EU and United States markets. |
| Cleared Personnel Pipeline Investment | Builds defensible moat for United States federal and defense-sector mandates with 12-18 month competitive lag. |
| AI-Act Compliance Methodology Development | Captures German energy utility and French transportation network demand for algorithmic transparency documentation. |
| Hyperscaler Cloud Partnership | Distributes assessment services through AWS, Azure, and GCP marketplaces to mid-market enterprise procurement workflows. |
Methodological Framework
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CISOs at financial services and critical infrastructure operators, partner-level consultants at advisory conglomerates, federal procurement officers, and cloud-security architects at hyperscaler partners. Secondary validation drew from SEC disclosure filings, EU NIS2 implementation guidance, CERT-In directive documents, and NIST SP 800-53 control frameworks. Bottom-up service-line revenue estimates were triangulated against top-down market sizing derived from advisory firm headcount and billing rate analysis.
Across the projection horizon, the analytical framework modeled cyber security consulting demand through service type, deployment model, and client maturity tier, with additional segmentation by regulatory jurisdiction complexity. CAGRs were derived from weighted scenario analysis incorporating compliance deadline acceleration, cloud migration velocity, and cleared labor supply constraints. Industry-specific forecast inputs included federal budget appropriation trajectories and EU member state transposition timelines for NIS2 obligations.
Material uncertainties — regulatory deadline delays, clearance processing acceleration, or generative AI displacement of baseline assessment work — sit outside the modeled envelope. Forecasts reflect assumptions regarding sustained compliance investment and cloud migration continuity. Recalibration cycles align with material shifts in federal procurement policy and EU regulatory enforcement intensity.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Hungary Cybersecurity Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
Enterprise Firewall Market
Cybersecurity
Global Patch Management Market
Cybersecurity
Data Security Market
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
Global Managed Detection and Response (MDR) Market
Cybersecurity
Turkey Cybersecurity Market
Cybersecurity
Artificial Intelligence-Based Cybersecurity Market
Cybersecurity
Global Quantum Cryptography Solutions Market
Cybersecurity
Advanced Malware Detection (AMD) Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
China Ransomware Protection Market
Cybersecurity
Global SSH Terminal Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Global Mobile Data Protection Market