
 Insider Threat Protection Market | 2026-2036
Insider Threat Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Insider Threat Protection Market Foresight
Market Context with Strategic Players
Enterprise software distribution is fragmenting as cybersecurity procurement shifts from centralized IT budgets to line-of-business units with autonomous security spending authority. Microsoft Corporation leverages its Entra identity suite and Purview data governance stack to anchor insider threat capabilities within existing enterprise subscriptions. Cisco Systems, Inc. competes through extended detection and response integrations that map user behavior to network telemetry at the edge. Forcepoint LLC specializes in risk-adaptive protection that dynamically adjusts data access policies based on real-time behavioral scoring.
Technical Definition and Structural Segments
Insider threat protection encompasses behavioral analytics engines, user activity monitoring infrastructure, and data loss prevention controls engineered to detect anomalous access patterns, credential misuse, and unauthorized data movement by authenticated personnel within organizational perimeters. The technology fuses endpoint telemetry, network flow records, and identity signals through machine-learned baselines to flag deviation from established behavioral norms before material breach occurs. Behavioral analytics solutions command the dominant share of solution-type revenue as financial institutions and healthcare organizations prioritize early-warning detection over retrospective audit trails. Cloud-based deployment models represent the fastest-expanding segment within deployment architecture, though on-premises installations retain stronghold status among government agencies with air-gapped classification requirements. Hybrid deployments concentrate margin pools where vendors bundle managed detection services with subscription software licenses.
Regulatory Framework and Forward Outlook
The US Securities and Exchange Commission imposes disclosure obligations on publicly traded entities for material cybersecurity incidents including insider-driven breaches, while the EU AI Act classifies certain behavioral analytics systems as high-risk AI requiring conformity assessments and audit documentation. HIPAA security rules in the United States mandate access controls and audit procedures that directly shape healthcare procurement specifications for user activity monitoring platforms. Stakeholders must weigh the compliance overhead of emerging AI governance frameworks against the detection efficacy gains from advanced behavioral models as regulatory scrutiny intensifies across both sides of the Atlantic.
Market Dynamics
Hybrid work architectures have permanently expanded the credential misuse attack surface, forcing organizations to rearchitect identity-centric security around continuous behavioral verification rather than perimeter-based trust models.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Publicly traded entities must report material insider-driven breaches within four business days, accelerating procurement of user activity monitoring platforms with real-time alerting capabilities.
- Healthcare digitization:HIPAA security rules mandate granular access controls and audit trails for electronic health records, driving hospital systems toward integrated behavioral analytics suites.
- Cloud migration velocity:Financial institutions deploying hybrid infrastructure require cloud-native insider threat solutions that correlate identity signals across SaaS applications and on-premises legacy systems.
Market Restraints
- False positive fatigue:Behavioral analytics engines generate excessive alerts in heterogeneous IT environments, eroding security team confidence and delaying incident response workflows.
- EU AI Act compliance burden:High-risk AI classification for certain behavioral scoring systems imposes conformity assessment costs and audit documentation requirements that compress vendor margins.
- Skills concentration:Data science expertise for machine-learned baseline development clusters in North American and Western European labor markets, constraining deployment velocity elsewhere.
Strategic Opportunities
- Asia-Pacific financial hubs:Singapore and Hong Kong banking regulators are implementing data governance frameworks that mirror Western mandates, creating first-mover advantage for vendors with localized behavioral models.
- Critical infrastructure protection:Energy sector operators face NERC CIP requirements for insider access controls, opening specialized procurement channels beyond traditional IT security budgets.
- Managed detection convergence:Security service providers are bundling insider threat monitoring with SOC-as-a-service offerings, enabling subscription revenue streams from mid-market enterprises lacking in-house expertise.
Industry Challenges
- Legacy SIEM integration complexity:Behavioral analytics platforms must ingest and normalize disparate log formats from decades-old security information systems, extending deployment timelines and professional services costs.
- Privacy engineering talent scarcity:Cross-functional teams combining data science, security operations, and legal compliance expertise remain difficult to assemble, constraining program maturity at enterprise scale.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Insider Threat Protection Market |
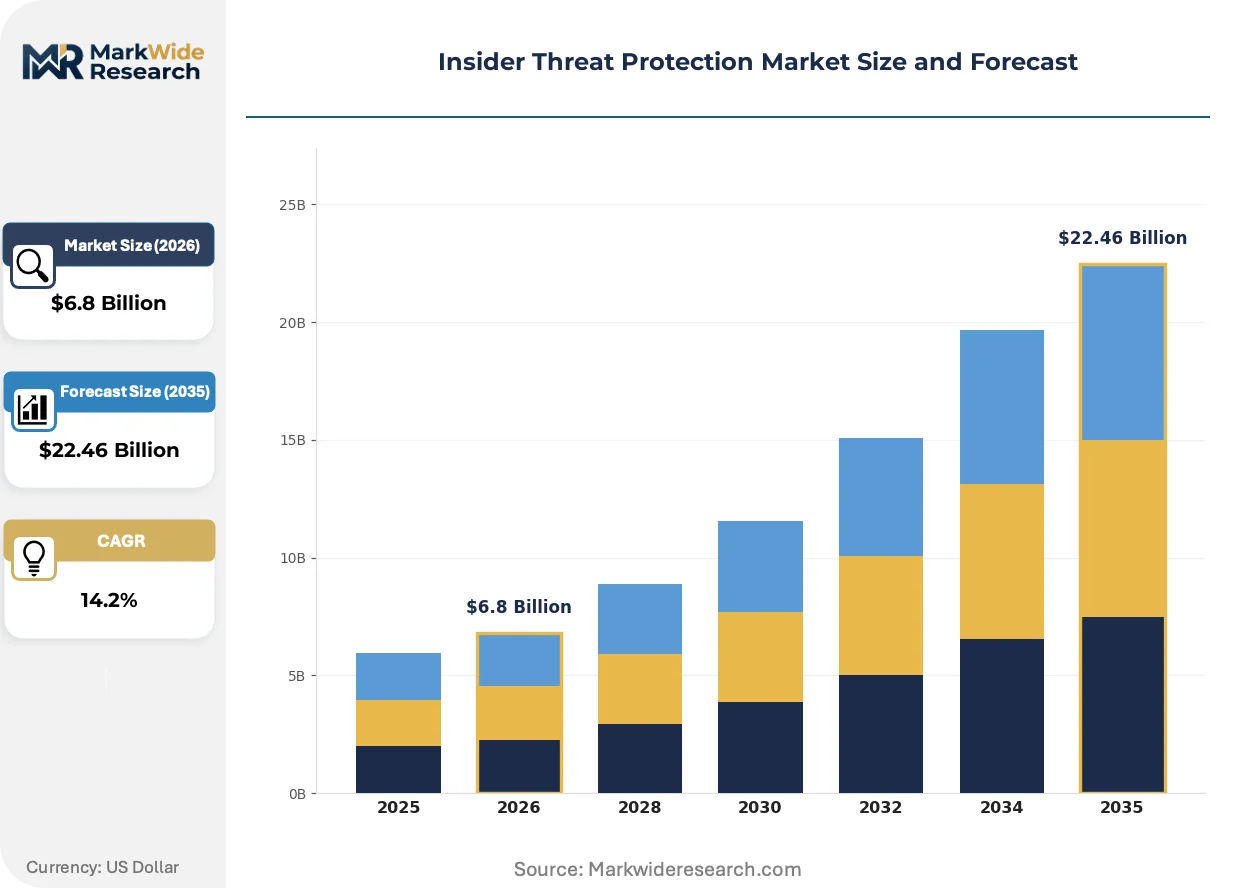
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $22.46 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Behavioral Analytics, Data Loss Prevention, User Activity Monitoring, Identity Management End User: Enterprises, Government Agencies, Financial Institutions, Healthcare Organizations Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services Industry Vertical: IT Services, Telecommunications, Energy, Retail |
| Companies Covered | Microsoft Corporation, Cisco Systems, Inc, Broadcom, Inc., VMware, Inc., Citrix Systems, Inc., Ivanti, Inc., McAfee Corp., Proofpoint Inc., Forcepoint LLC, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Insider Threat Protection Market Shifts & Advancements
Artificial intelligence is compressing detection latency while regulatory pressure is hardening audit requirements, creating simultaneous demand for automation sophistication and explainability transparency.
Extended detection and response platforms are hybridizing insider threat telemetry with network edge analytics, enabling security teams to trace anomalous user sessions through cloud workloads and on-premises endpoints within unified investigation workflows. Financial services institutions in London and New York are deploying these converged architectures fastest, collapsing previously separate procurement cycles for user behavior analytics and endpoint detection tools.
The EU AI Act mandates conformity assessments for high-risk behavioral scoring systems, requiring vendors to document training data provenance and algorithmic decision logic. Healthcare organizations deploying patient-facing access monitoring must now maintain technical documentation and human oversight protocols, shifting competitive advantage toward established providers with compliance engineering resources.
Line-of-business units are displacing centralized IT departments as primary security buyers, with CISOs delegating budget authority to data owners in legal, finance, and research functions. This fragmentation favors vendors offering self-service policy configuration and role-based reporting dashboards, particularly visible in German and Swiss pharmaceutical firms where data stewards demand direct control over access governance without ticketing through enterprise security operations.
Insider Threat Protection Market Segmentation
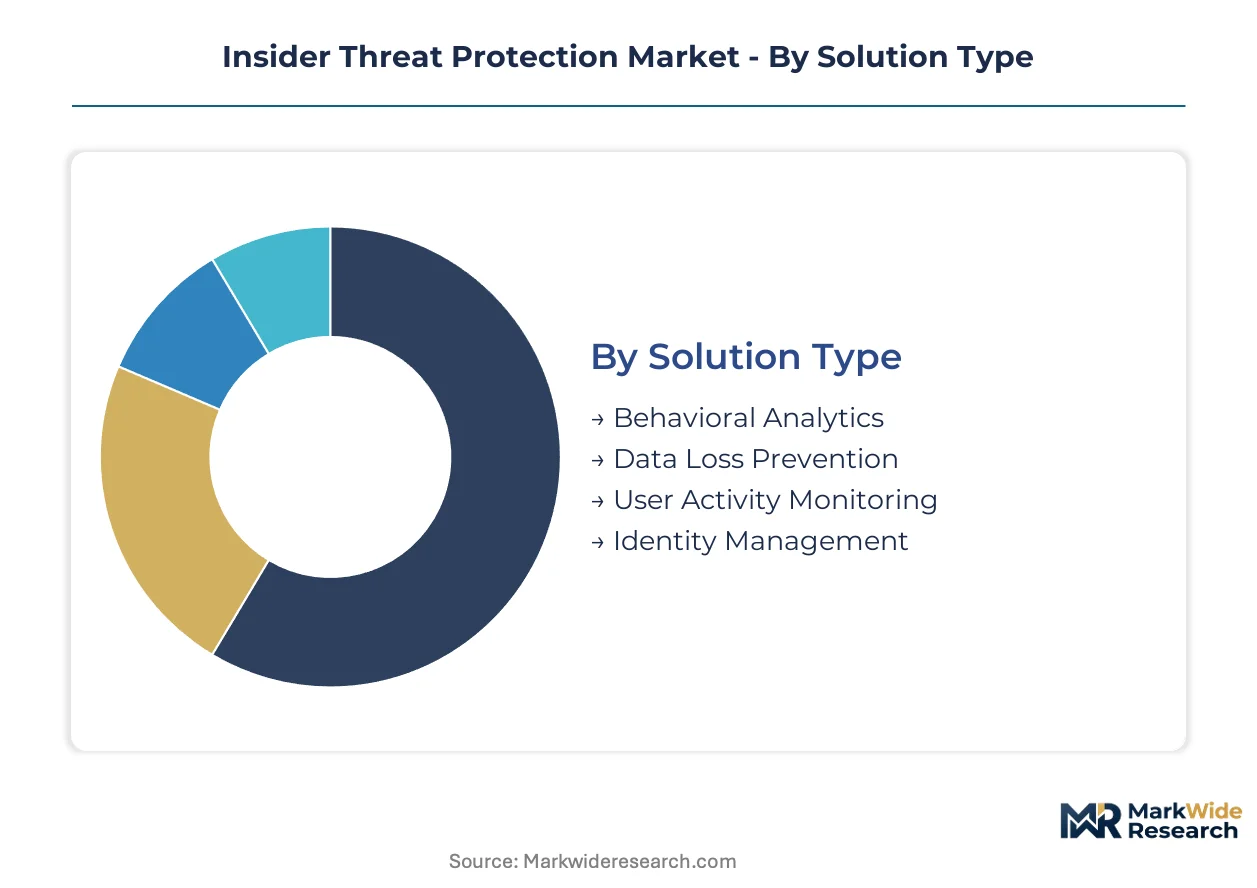
Insider threat protection vendors architect product portfolios around distinct operational requirements, from real-time behavioral inference to retrospective audit compliance. Procurement patterns diverge sharply across deployment architectures and regulatory environments, forcing suppliers to maintain parallel engineering tracks.
Solution Type:
Mature behavioral analytics engines dominate procurement budgets while emerging identity-centric platforms capture greenfield installations.
- Behavioral Analytics:Machine-learned baselines correlate endpoint telemetry, network flows, and identity signals to flag deviation from established norms before material breach occurs. Financial institutions in London and New York prioritize these systems for early-warning detection over retrospective audit trails, driven by SEC disclosure mandates requiring four-day reporting windows for material incidents.
- Data Loss Prevention:Policy engines inspect content-in-motion across email, cloud storage, and removable media to block unauthorized exfiltration. Healthcare organizations deploying patient-facing access monitoring rely on DLP controls to satisfy HIPAA security rule requirements for granular audit documentation.
- User Activity Monitoring:Session recording and keystroke logging infrastructure captures forensic evidence for post-incident investigation.
- Identity Management:Continuous authentication and privileged access controls verify user legitimacy beyond initial login.
Behavioral analytics handles the majority of throughput; identity management is climbing the fastest on share as zero-trust architectures displace perimeter-based trust models.
End User:
Cost tier segmentation separates enterprise-scale integrated suites from departmental point solutions with limited telemetry correlation.
- Enterprises:Multi-divisional organizations deploy converged platforms unifying user behavior analytics with extended detection and response workflows. Hybrid work architectures at Fortune 500 technology firms drive demand for cloud-native correlation across SaaS applications and on-premises legacy systems.
- Financial Institutions:Banks and investment managers face overlapping SEC, FINRA, and PCI-DSS mandates requiring real-time alerting capabilities. Singapore and Hong Kong banking regulators are implementing data governance frameworks that mirror Western disclosure obligations, accelerating procurement velocity in Asia-Pacific financial hubs.
- Government Agencies:Air-gapped classification requirements sustain on-premises deployment preferences despite cloud migration trends elsewhere.
- Healthcare Organizations:Hospital systems integrate behavioral analytics with electronic health record access controls to satisfy HIPAA audit procedures.
Enterprises command the largest absolute spend; financial institutions are expanding most quickly as regulatory harmonization spreads across jurisdictions.
Deployment Model:
Application context determines architecture selection, with classified workloads retaining physical infrastructure while commercial operations migrate to elastic cloud consumption.
- Cloud-Based:Native SaaS delivery eliminates capital expenditure for telemetry storage and compute-intensive behavioral modeling. Western European pharmaceutical firms with distributed research operations favor cloud deployment for rapid provisioning across multinational sites without centralized IT bottlenecks.
- Hybrid:Split architectures process sensitive data on-premises while leveraging cloud analytics for non-classified workloads. Energy sector operators under NERC CIP requirements use hybrid models to maintain critical infrastructure access controls within physical perimeters while outsourcing threat intelligence correlation.
- On-Premises:Air-gapped installations serve government and defense contractors with formal classification requirements.
- Managed Services:Security service providers bundle insider threat monitoring with SOC-as-a-service offerings for mid-market enterprises lacking in-house data science expertise.
Cloud-based deployment absorbs the steepest expansion trajectory; managed services are gaining share fastest among organizations under 5,000 employees.
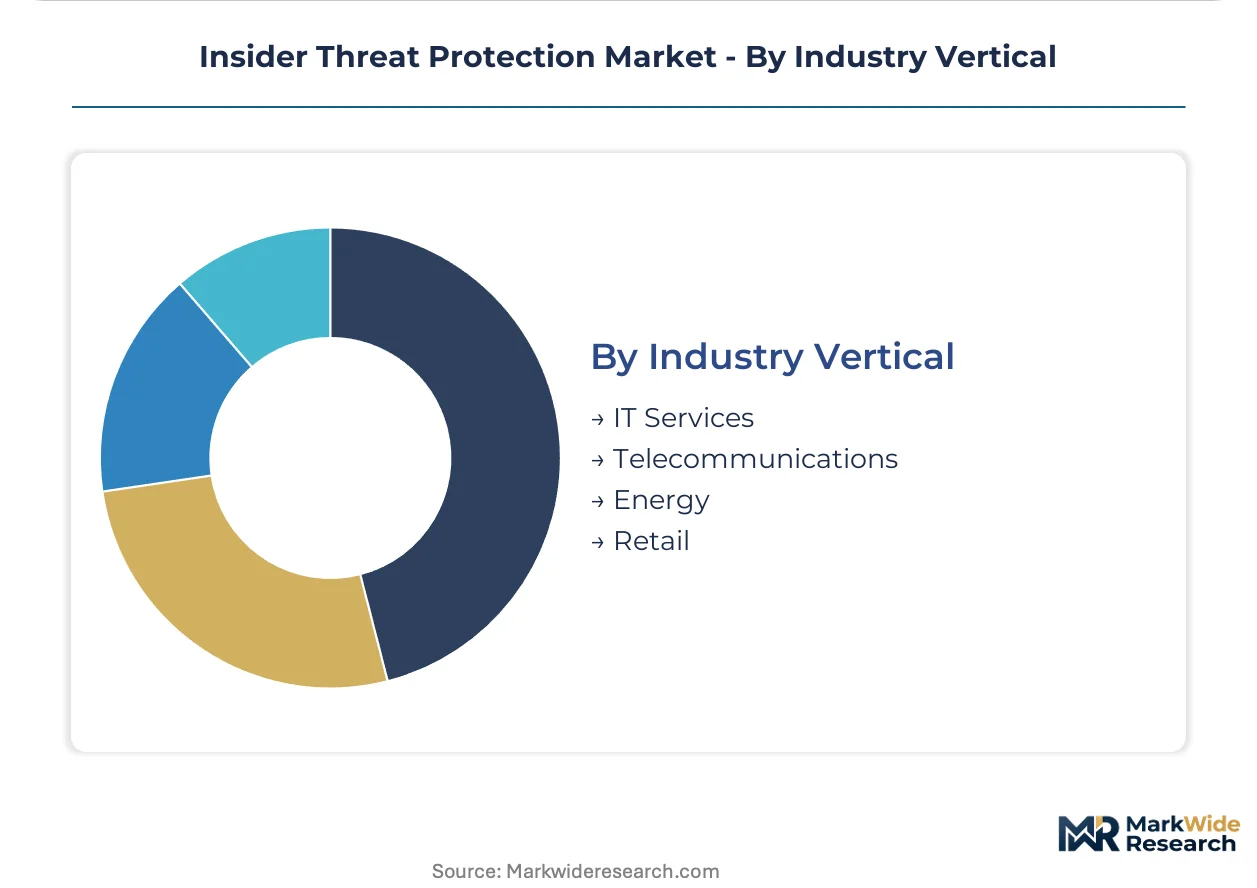
Industry Vertical:
Customer type segmentation reflects divergent risk appetites, with regulated sectors prioritizing audit defensibility over detection latency.
- IT Services:Technology consultancies and systems integrators deploy insider threat platforms to protect client source code and configuration data across multi-tenant development environments. Remote engineering teams with privileged access to customer infrastructure drive behavioral analytics procurement.
- Energy:Electric utilities and oil and gas operators face NERC CIP mandates for insider access controls at critical cyber assets. Specialized procurement channels outside traditional IT security budgets open for vendors with industrial control system integration expertise.
- Telecommunications:Network operators monitor subscriber data access patterns to prevent credential misuse at customer-facing systems.
- Retail:E-commerce platforms and brick-and-mortar chains deploy user activity monitoring to protect payment card data and supplier pricing intelligence.
IT services concentrates the largest procurement volume; energy is advancing fastest as critical infrastructure protection frameworks harden across North America and Europe.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
SEC disclosure mandates in the United States are accelerating procurement velocity for behavioral analytics platforms with real-time alerting capabilities. The analysis examines five countries where insider threat protection procurement concentrates amid divergent regulatory frameworks and industrial digitization patterns.
United States
Financial institutions in New York and Chicago face compressed four-day reporting windows for material cybersecurity incidents under SEC rules. HIPAA security rules simultaneously drive hospital systems toward integrated user activity monitoring platforms. Silicon Valley technology firms deploy cloud-native solutions correlating identity signals across distributed SaaS environments.
Germany
Pharmaceutical manufacturers in Frankfurt and Munich prioritize self-service policy configuration for data stewards in legal and research functions. EU AI Act conformity assessments impose documentation burdens on behavioral scoring systems deployed in patient-facing access monitoring. Industrial automation clusters in Stuttgart integrate insider threat controls with operational technology security frameworks.
United Kingdom
London-based investment managers procure converged architectures unifying user behavior analytics with extended detection and response workflows. Financial Conduct Authority guidelines on operational resilience shape procurement specifications for real-time monitoring capabilities. Edinburgh and Manchester financial services hubs mirror London deployment patterns at reduced scale.
Singapore
Banking regulators implement data governance frameworks mirroring Western disclosure obligations, accelerating procurement among asset managers and private banks. Monetary Authority of Singapore cybersecurity guidelines mandate granular access controls for critical systems. Marina Bay financial district operators favor cloud-native deployment for rapid provisioning across regional offices.
Japan
Tokyo-headquartered manufacturers deploy hybrid architectures processing sensitive intellectual property on-premises while leveraging cloud analytics for non-classified workloads. METI guidelines on supply chain cybersecurity influence procurement specifications for user activity monitoring. Osaka pharmaceutical clusters prioritize audit defensibility over detection latency in platform selection.
Insider Threat Protection Market Competitive Landscape
Platform consolidators and specialized behavioral analytics vendors split the market between bundled enterprise suites and point solutions with deep functional focus. The vendor base concentrates around three strategic archetypes: identity-centric platform providers extending existing cloud subscriptions, network-security incumbents integrating user telemetry with edge detection infrastructure, and risk-adaptive specialists offering dynamic policy adjustment engines. Dominant competitive moves include portfolio diversification into adjacent data governance categories and strategic partnerships bundling managed detection services with software licenses.
Within the platform consolidator tier, Microsoft Corporation anchors enterprise procurement through identity and data governance stack integration. Cisco Systems, Inc. occupies a position bridging network telemetry with behavioral inference capabilities. Forcepoint LLC exemplifies the risk-adaptive specialist archetype through policy engines adjusting access controls based on real-time behavioral scoring. These three vendors represent divergent strategic bets on whether insider threat protection converges with broader security platforms or sustains standalone procurement cycles.
| Leading Market Players |
|---|
| Microsoft Corporation |
| Cisco Systems, Inc |
| Broadcom, Inc. |
| VMware, Inc. |
| Citrix Systems, Inc. |
| Ivanti, Inc. |
| McAfee Corp. |
| Proofpoint Inc. |
| Forcepoint LLC |
| Others |
Supply & Pricing Matrix
Machine learning compute infrastructure concentrates in North American hyperscaler regions, anchoring margin pools for vendors with captive cloud capacity against pure-play software competitors forced into third-party hosting arrangements. This upstream concentration cascades into pricing power asymmetries where integrated platform providers bundle behavioral analytics at marginal cost while specialist vendors face escalating inference expenses.
Pricing Analysis
North American enterprise deployments command 15-25% premiums over Asia-Pacific equivalent configurations due to compliance engineering overhead and localized data residency requirements. Pricing stratifies across premium, standard, and economy tiers differentiated by integration depth with existing identity infrastructure and managed detection service bundling. Cost compression in the standard tier is intensifying because Forcepoint LLC and Cisco Systems, Inc. are converging insider threat capabilities with broader security platform subscriptions. Mid-market enterprises under 5,000 employees exhibit highest price sensitivity, while Fortune 500 financial institutions prioritize detection latency over per-seat cost.
Supply Chain Analysis
Contract manufacturing for behavioral analytics hardware appliances concentrates with Foxconn and Quanta Computer facilities in Taiwan and Mexico, though cloud-native deployment is displacing physical appliance demand. Software supply chains draw from open-source telemetry libraries maintained in the United States and Germany, with proprietary machine learning frameworks sourced from Google Cloud and Microsoft Azure development centers. Single-source vulnerability in GPU accelerator supply from NVIDIA creates procurement bottlenecks for compute-intensive behavioral modeling workloads. Distribution runs through direct enterprise sales organizations and hyperscaler marketplaces, with managed security service providers capturing growing share of mid-market deployment.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a defensive-moat arena where regulatory entrenchment creates sticky revenue streams through mandatory audit documentation and conformity assessment requirements.
For Market Incumbents: Build switching-cost moats through deep integration with Microsoft Entra and Cisco ISE identity infrastructure, embedding behavioral analytics into authentication workflows that become painful to extract. Incumbents should acquire managed detection service providers in London and Singapore to capture recurring revenue from mid-market financial institutions facing SEC and Monetary Authority of Singapore disclosure mandates. The threat of cloud-native entrants with superior machine learning latency demands continuous R&D investment in edge-deployed inference models.
For New Entrants and Emerging Players: Pursue white-space penetration in Asia-Pacific financial hubs where localized behavioral models remain underdeveloped relative to Western pattern libraries. Singapore and Hong Kong asset managers present the most penetrable segment due to regulatory harmonization with Western disclosure frameworks without incumbent saturation. A vertical-specific go-to-market angle targeting NERC CIP compliance for North American electric utilities opens procurement channels outside traditional IT security budgets.
For Investors and Strategic Acquirers: Secondary-cycle assets sit with private equity-backed risk-adaptive specialists possessing EU AI Act conformity documentation but limited geographic expansion capital. Long-term viability across the analysis window favors vendors with hybrid deployment architectures serving government air-gapped requirements alongside cloud-native commercial growth. The signal to watch is consolidation velocity among managed security service providers bundling insider threat monitoring with SOC-as-a-service offerings, indicating platformization pressure on standalone point solutions.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration with Identity Infrastructure | Microsoft Entra and Cisco ISE embedding creates extraction friction for enterprise customers. |
| Managed Detection Service Acquisition | London and Singapore service providers capture recurring revenue from disclosure-mandated institutions. |
| EU AI Act Conformity Engineering | Documentation investment shifts competitive advantage toward established providers in healthcare procurement. |
| Edge-Deployed Inference Development | Latency reduction counters cloud-native entrants threatening behavioral analytics incumbents. |
| Critical Infrastructure Vertical Expansion | NERC CIP specialization opens energy sector procurement outside traditional IT security channels. |
Research Methodology
A standing panel of CISOs, identity infrastructure architects, managed security service provider executives, and healthcare compliance officers provided ongoing calibration across the study period. Primary interviews with these stakeholders combined with secondary validation from SEC disclosure filings, HIPAA audit documentation, EU AI Act conformity assessment registers, and hyperscaler capex disclosures. Bottom-up deployment estimates triangulated against top-down security software spending benchmarks from financial services and healthcare verticals.
Scenario-bracketing framed projections across regulatory intensification and cloud migration velocity assumptions over the projection horizon. Segmentation dimensions modeled include deployment architecture, organization size, vertical regulatory exposure, integration complexity with legacy SIEM infrastructure, and regional compliance framework adoption. CAGRs derived from weighted average of historical procurement velocity and forward-looking budget allocation surveys. Forecast inputs incorporated machine learning compute cost trajectories and cybersecurity insurance premium adjustments for disclosed insider incidents.
Macroeconomic conditions sit as an overlay; deviation in enterprise software budget cycles and cloud infrastructure pricing would shift the trajectory. Forecasts reflect documented assumptions regarding regulatory enforcement consistency and behavioral analytics false positive tolerance thresholds. Quarterly review of SEC disclosure filing volumes and EU AI Act conformity assessment completion rates is advised to detect inflection.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Critical Infrastructure Protection
North America Public Infrastructure Safety Market
Critical Infrastructure Protection
Critical Infrastructure Monitoring Market
Critical Infrastructure Protection
Europe Tank Protection Market
Critical Infrastructure Protection
Global Advanced Persistent Threat (APT) Protection Market
Critical Infrastructure Protection
Global Threat Intelligence Platform Market
Critical Infrastructure Protection
Middle East and Africa Pipeline Security Market
Critical Infrastructure Protection
Asia-Pacific Public Infrastructure Safety Market
Critical Infrastructure Protection
Critical Infrastructure Protection Market
Critical Infrastructure Protection
UK Critical Infrastructure Protection Market
Critical Infrastructure Protection
Asia Pacific Tank Protection Market
Critical Infrastructure Protection
Middle East Commercial Security Market
Critical Infrastructure Protection
Asia-Pacific High-Integrity Pressure Protection System (HIPPS) Market
Critical Infrastructure Protection
Perimeter Defense System Market
Critical Infrastructure Protection
Global Airport and Marine Port Security Market
Critical Infrastructure Protection
Middle East and Africa Public Infrastructure Safety Market
Critical Infrastructure Protection
Global High Integrity Pressure Protection System (HIPPS) Market