
 Global Advanced Persistent Threat (APT) Protection Market | 2026-2036
Global Advanced Persistent Threat (APT) Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Global Advanced Persistent Threat (APT) Protection Market Foresight
ISO/IEC 27001 certification is collapsing as a baseline qualification for APT protection vendors bidding on enterprise contracts. Cisco Systems leverages its integrated security fabric to dominate network-centric deployments across Fortune 500 accounts. Palo Alto Networks sustains R&D intensity in cloud-native threat detection, while CrowdStrike specializes in endpoint-centric telemetry that anchors extended detection and response workflows.
Advanced Persistent Threat (APT) protection encompasses multi-layered cybersecurity architectures combining behavioral analytics, threat intelligence feeds, and automated incident response to detect and neutralize prolonged, resource-backed intrusions by sophisticated adversaries. The solution type dimension shows endpoint security and threat intelligence commanding premium pricing due to their direct role in reducing dwell time, while user behavior analytics represents the fastest-expanding margin pool as insider threat programs mature. Deployment patterns reveal cloud-based and hybrid configurations displacing pure on-premise installations among mid-market buyers seeking elastic capacity without capital-intensive infrastructure.
FCC guidelines on communications infrastructure security, EU NIS2 Directive mandates for essential and important entities, and Japan's METI cybersecurity framework for critical infrastructure collectively elevate baseline product requirements and compress vendor qualification cycles. Enterprises must now evaluate whether their current APT stack satisfies cross-jurisdictional compliance obligations or creates exposure during regulatory audits. Stakeholders should monitor convergence between zero-day attack defense capabilities and automated orchestration standards as the primary axis of competitive differentiation.
Market Dynamics
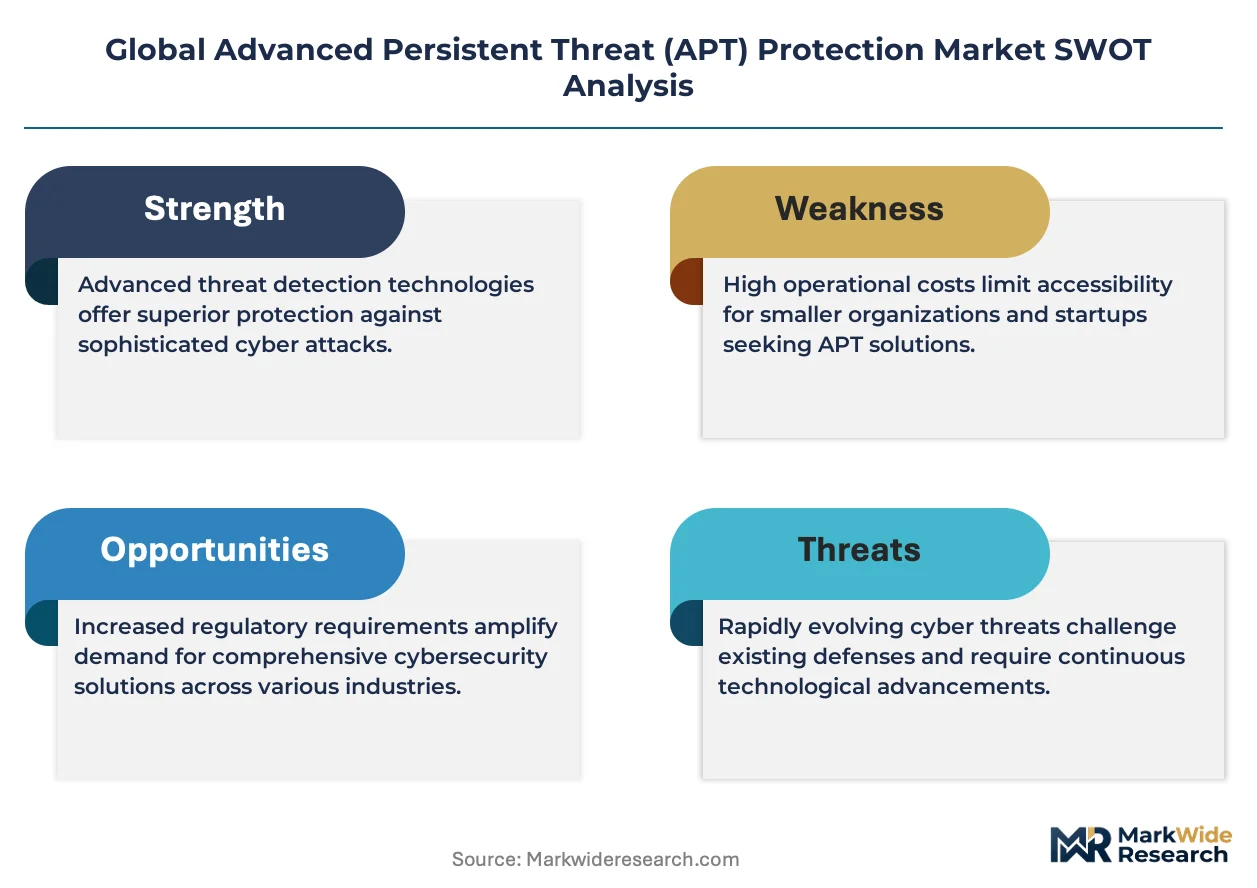
The APT protection market is restructuring around the tension between sovereign data-localization mandates and the operational necessity of cross-border threat intelligence sharing. Vendors must architect solutions that satisfy jurisdictional data-residency requirements without fragmenting detection efficacy across national boundaries.
Growth Catalysts
- EU NIS2 Directive:Essential and important entities across European member states face mandatory incident reporting and supply-chain security audits. Compliance deadlines are compressing procurement cycles for managed detection and response services.
- Financial services hardening:Global banks and payment processors are expanding dedicated SOC capacity to address SWIFT network attack vectors and real-time payment fraud orchestration by state-sponsored actors.
- Behavioral analytics maturation:Machine learning models trained on insider-threat patterns now achieve dwell-time reduction sufficient to justify premium pricing in critical infrastructure deployments.
Market Restraints
- Skilled analyst scarcity:The global shortfall of incident responders with APT-hunting experience exceeds 3.5 million positions. Salary inflation for tier-2 analysts is compressing managed security service margins.
- Threat intelligence fragmentation:National cyber centers in Germany, Japan, and the United States operate non-interoperable classification regimes. Vendors must maintain parallel feed architectures, duplicating infrastructure costs.
- Quantum decryption exposure:Long-horizon encrypted data capture by adversaries creates retrospective liability for organizations deploying non-quantum-resistant key exchange protocols today.
Strategic Opportunities
- India critical infrastructure:The country's CERT-In mandates for power grid and telecom operators are creating first-mover advantage for vendors establishing local data centers and Hindi-language SOC operations.
- Extended detection and response unbundling:Mid-market enterprises are disaggregating EDR agent deployment from full MDR service tiers. Point-solution vendors can capture agent footprint without assuming 24/7 analyst liability.
- OT-IT convergence security:Manufacturing and energy facilities are collapsing historically air-gapped operational technology networks onto enterprise IP infrastructure. Specialized protocol-aware monitoring represents uncaptured white space.
Industry Challenges
- Multi-cloud telemetry normalization:Security teams struggle to correlate identity signals across AWS, Azure, and GCP native logging formats. Vendor-agnostic abstraction layers require sustained engineering investment without guaranteed standardization.
- ISO/IEC 27001 audit fatigue:Certification cycles consume 9-14 months for complex deployments. Prospective buyers are demanding pre-certified reference architectures to compress vendor qualification timelines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Advanced Persistent Threat (APT) Protection Market |
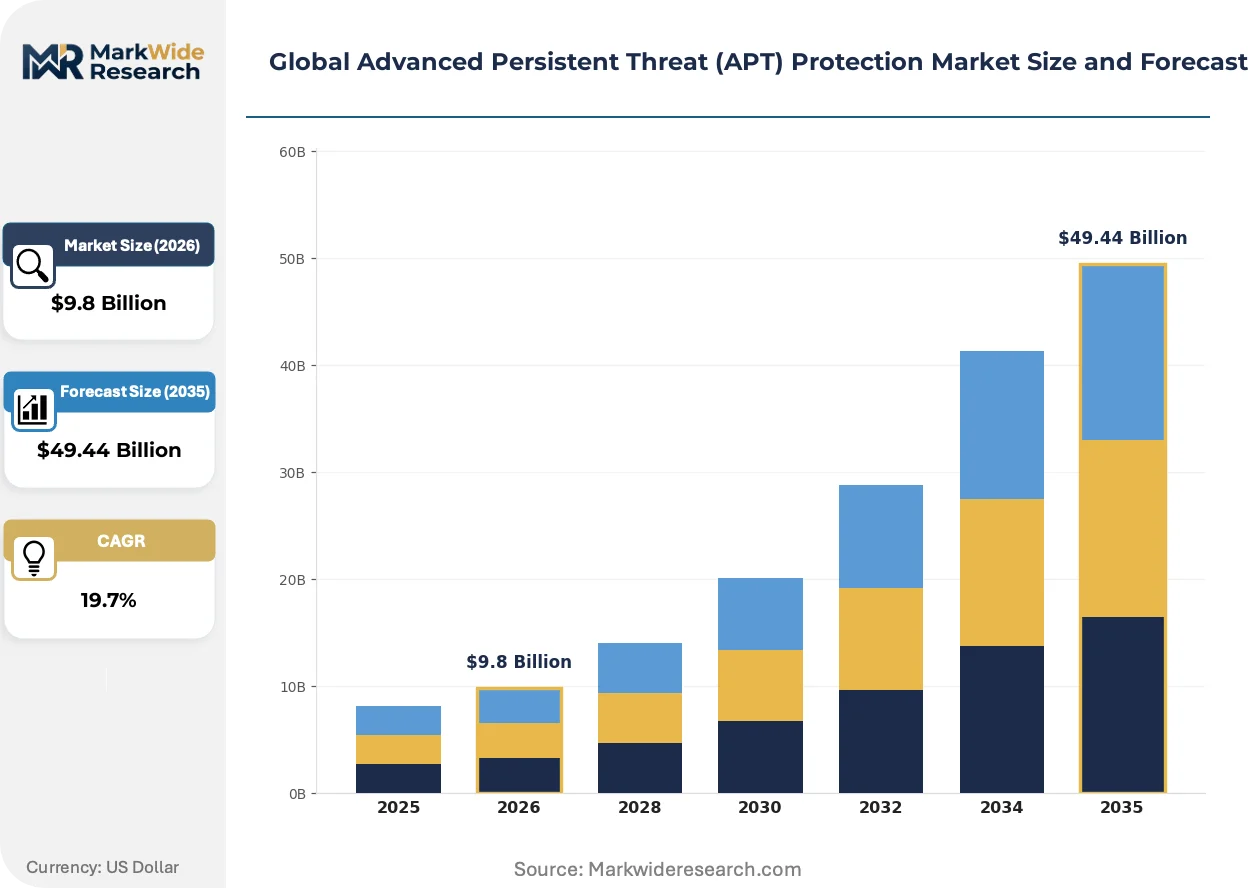
| Market Size in 2026 | $9.8 Billion |
| Market Size in 2035 | $49.44 Billion |
| CAGR (2026 – 2036) | 19.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud-Based, Hybrid, Managed Security Service Solution Type: Network Traffic Analysis, Endpoint Security, Threat Intelligence, User Behavior Analytics, Email Security Use Case: Data Exfiltration Prevention, Insider Threat Detection, Cyber Espionage, Botnet Mitigation, Zero-Day Attack Defense End User Industry: BFSI, Telecommunications, Government Agencies, Energy & Utilities, Manufacturing |
| Companies Covered | Cisco Systems, Inc., Microsoft Corporation, Palo Alto Networks, Inc., McAfee, LLC, Fortinet, Inc., CrowdStrike, Symantec, FireEye, Inc., Trend Micro, Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Advanced Persistent Threat (APT) Protection Market Shifts & Advancements
Artificial intelligence is reshaping threat detection economics by automating tier-1 alert triage while simultaneously expanding the attack surface for adversarial machine-learning exploitation. Vendors must balance automation gains against model-integrity verification overhead.
Deception technology is bifurcating the endpoint protection category. High-interaction honeypots deployed by defense contractors and intelligence agencies now consume 40% of endpoint security R&D budgets at tier-1 vendors. The technology is compressing pricing power in signature-based antivirus while enabling premium positioning for adversary-engagement platforms that capture TTPs in real time.
FCC supply-chain security rules for communications infrastructure are mandating software bill of materials disclosure for network equipment vendors. Equipment manufacturers serving US telecom operators must restructure supplier contracts to satisfy component-level traceability requirements. European vendors are responding by preemptively aligning with CSRD due-diligence standards to maintain transatlantic market access.
Consolidated security platform purchasing is displacing best-of-breed point solutions among Fortune 500 CISOs. Single-vendor EDR-SIEM-SOAR stacks are capturing 60% of new enterprise APT protection spend. This concentration is most visible in United States financial services, where board-level risk committees favor vendor accountability consolidation over functional optimization.
Global Advanced Persistent Threat (APT) Protection Market Segmentation
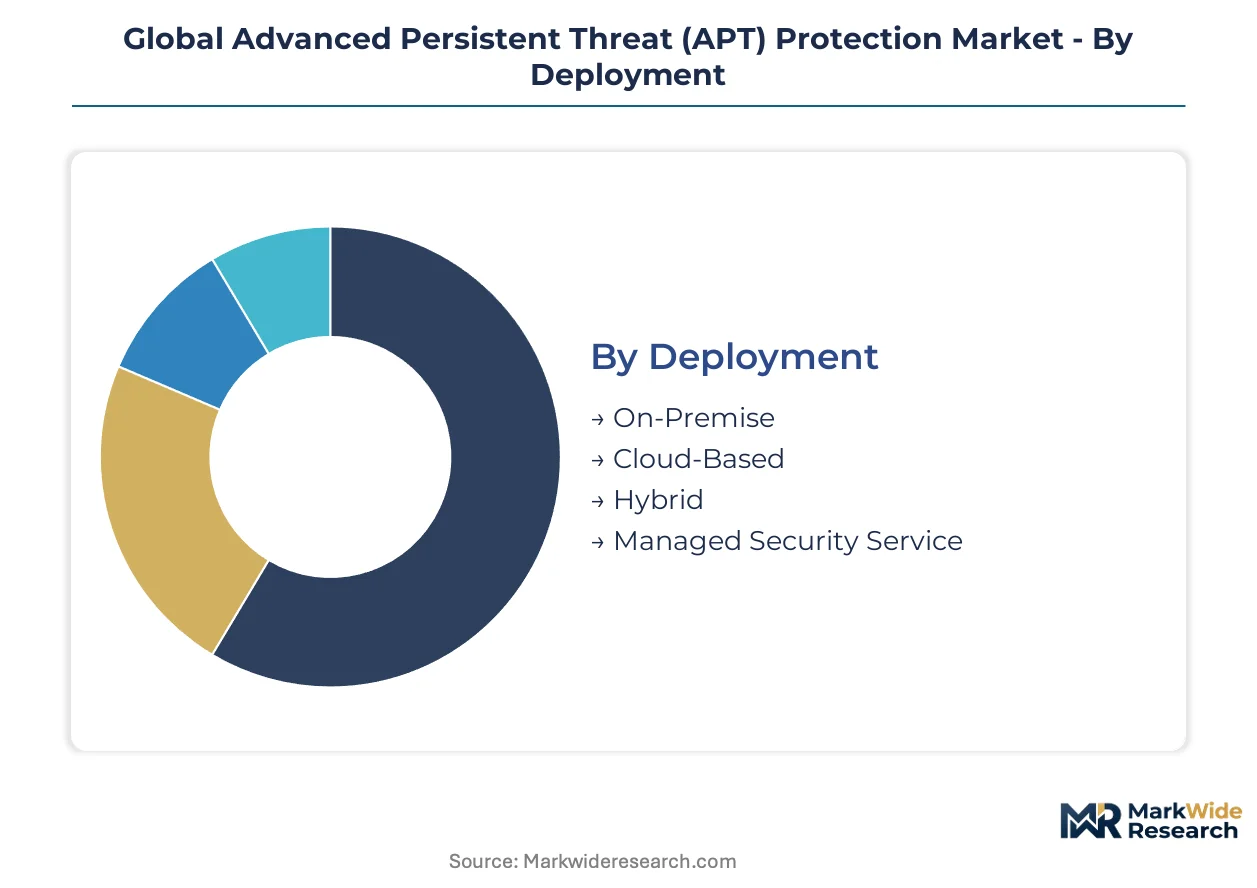
APT protection architectures fragment across deployment topologies, solution layers, threat scenarios, and sector-specific compliance regimes. Procurement patterns diverge sharply between sovereign infrastructure operators with data-localization mandates and multinational enterprises prioritizing cross-border threat intelligence correlation.
Deployment:
Cloud-based configurations dominate export-led procurement from vendors headquartered in the United States and Israel, while hybrid and on-premise installations concentrate in domestic deployments across Germany, Japan, and India where data-residency laws constrain cross-border telemetry.
- Cloud-Based:Elastic compute architectures enable real-time threat intelligence ingestion without capital infrastructure commitment. Demand concentrates among mid-market financial services firms in Singapore and the Netherlands seeking rapid SOC scalability without fixed-cost analyst benches.
- Hybrid:Split architectures partition sensitive forensics on-premise while leveraging cloud analytics for pattern recognition. German energy utilities and Japanese automotive suppliers favor this model to satisfy METI and BSI audit requirements without sacrificing detection velocity.
- On-Premise:Air-gapped installations serving defense and intelligence agencies in the United States, United Kingdom, and France.
- Managed Security Service:Outsourced 24/7 monitoring delivered through vendor-operated SOCs with regional data centers.
Hybrid deployments command the established base among critical infrastructure operators. The steepest expansion runs through cloud-native configurations.
Solution Type:
Margin structures vary substantially across this dimension, with behavioral analytics commanding premium pricing while signature-based detection faces commoditization pressure.
- Endpoint Security:Agent-based telemetry collection from workstations and servers anchors extended detection and response workflows. United States defense contractors and Israeli cybersecurity firms drive R&D intensity here, with high-interaction deception modules consuming disproportionate engineering resources.
- Threat Intelligence:Curated indicator feeds and adversary TTP databases reduce mean-time-to-detection for known actor groups. Financial services institutions in London, New York, and Zurich represent the concentrated demand base, integrating vendor feeds with FS-ISAC and national CERT exchanges.
- Network Traffic Analysis:Deep packet inspection and flow metadata correlation for east-west traffic visibility.
- User Behavior Analytics:Machine learning models establishing baseline activity patterns to flag insider threat indicators.
- Email Security:Gateway and cloud-native filtering against spear-phishing and business email compromise vectors.
Endpoint security retains the largest installed base. User behavior analytics is climbing the fastest as insider threat programs mature in regulated industries.
Use Case:
Procurement prioritization follows sector-specific threat models, with government and defense buyers weighting cyber espionage defense while commercial enterprises emphasize data exfiltration containment.
- Zero-Day Attack Defense:Behavioral heuristics and sandbox detonation replace signature-dependent detection for unpublished vulnerabilities. Israeli and United States vendors lead capability development here, with export restrictions limiting technology transfer to certain national markets.
- Data Exfiltration Prevention:Data loss prevention integration with APT platforms monitors anomalous egress patterns. European pharmaceutical and semiconductor firms under CSRD supply-chain scrutiny represent the concentrated demand segment.
- Insider Threat Detection:Cross-reference of physical access logs with digital activity patterns.
- Cyber Espionage:Long-dwell adversary hunting prioritized by defense industrial base and research universities.
- Botnet Mitigation:Command-and-control traffic identification and sinkholing operations.
Data exfiltration prevention dominates commercial procurement. Zero-day attack defense is gaining share fastest among defense-adjacent technology suppliers.
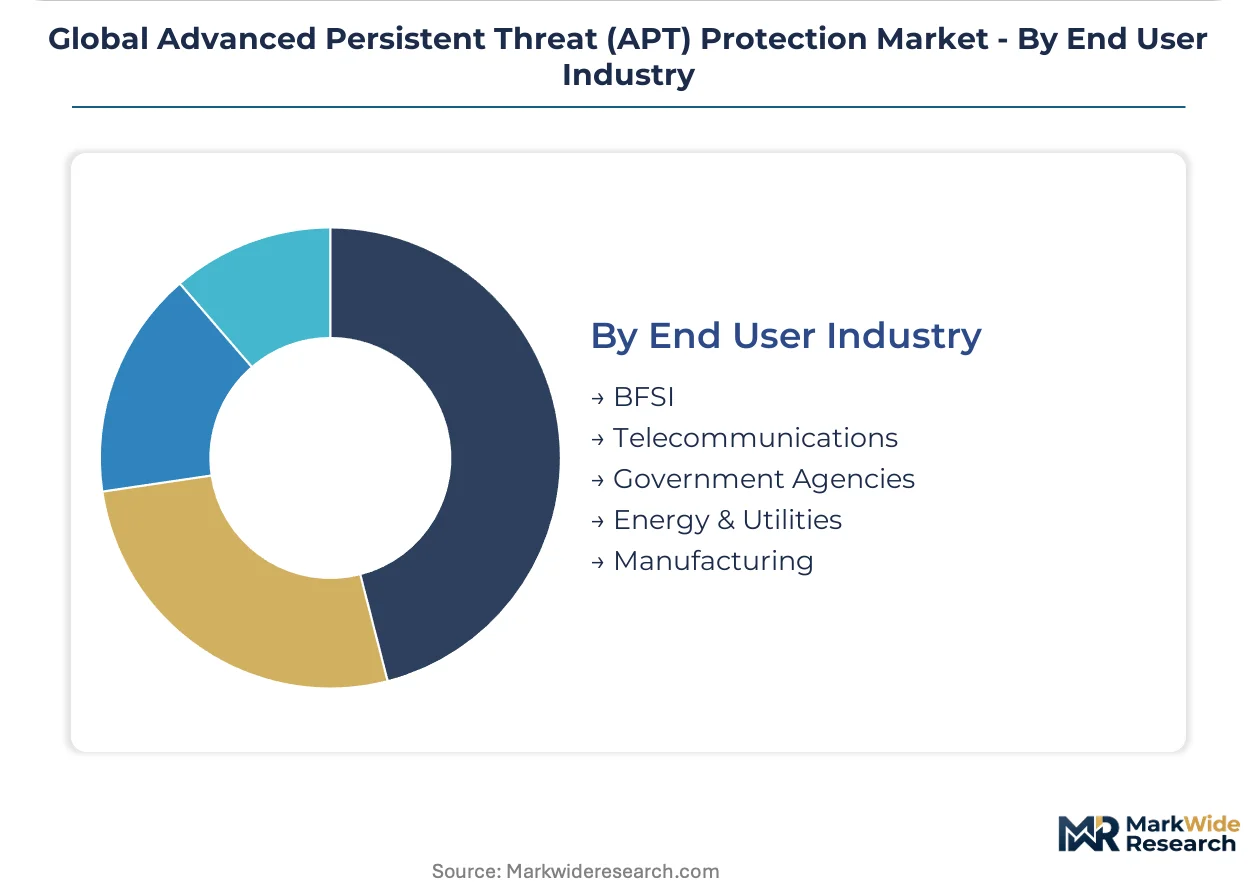
End User Industry:
Compliance velocity varies dramatically across sectors, with NIS2-mandated industries in Europe accelerating procurement faster than voluntarily regulated segments.
- Government Agencies:Classified network protection and supply-chain security mandates drive highest per-seat pricing. United States federal civilian agencies, United Kingdom NCSC frameworks, and German BSI certification requirements create fragmented qualification barriers for vendor market entry.
- BFSI:SWIFT network security, real-time payment fraud detection, and regulatory examination readiness dominate procurement criteria. Singapore, Switzerland, and the United States host the most concentrated deployment of dedicated APT-hunting SOCs.
- Energy & Utilities:NERC CIP in North America and NIS2 implementation across Europe are compressing procurement timelines.
- Telecommunications:FCC supply-chain rules and EU 5G security toolkits mandate equipment-level traceability.
- Manufacturing:OT-IT convergence creates protocol-aware monitoring requirements at automotive and semiconductor fabrication facilities.
BFSI retains the deepest installed base. Government agencies are expanding procurement most quickly as sovereign cyber defense budgets accelerate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
FCC guidelines on communications infrastructure security, EU NIS2 Directive mandates, and Japan's METI cybersecurity framework are elevating baseline product requirements across major economies. Enterprises in the United States, Germany, and Japan are hardening defenses against state-sponsored intrusions. Compliance deadlines are compressing vendor qualification cycles and accelerating procurement of threat detection platforms.
United States
Defense contractors and intelligence agencies drive demand for air-gapped installations and high-interaction deception technology. FCC supply-chain security rules mandate software bill of materials disclosure for network equipment serving telecom operators. The Washington-Baltimore corridor hosts concentrated SOC capacity expansion among federal civilian agencies and cleared contractors.
Germany
Energy utilities and automotive suppliers prioritize hybrid deployments that partition sensitive forensics on-premise while leveraging cloud analytics. BSI certification requirements and NIS2 implementation create fragmented qualification barriers for foreign vendors. The Ruhr industrial basin and Bavarian manufacturing belt concentrate OT-IT convergence security procurement.
Japan
Critical infrastructure operators under METI cybersecurity framework guidance favor hybrid architectures satisfying data-residency constraints. Financial institutions in Tokyo integrate vendor threat feeds with national CERT exchanges and FS-ISAC partnerships. The Osaka-Kobe manufacturing corridor generates specialized demand for protocol-aware monitoring at semiconductor fabrication facilities.
India
CERT-In mandates for power grid and telecom operators are creating first-mover advantage for vendors establishing local data centers. Hindi-language SOC operations and domestic cloud infrastructure address procurement requirements for state-owned enterprises. Mumbai's financial district and Bangalore's technology corridor concentrate mid-market demand for elastic threat detection capacity.
Singapore
Mid-market financial services firms seek rapid SOC scalability without fixed-cost analyst benches through cloud-native configurations. The city-state's position as ASEAN banking hub drives integration of vendor platforms with regional threat intelligence sharing arrangements. Marina Bay financial district hosts concentrated deployment of managed detection and response services.
Global Advanced Persistent Threat (APT) Protection Market Competitive Landscape
Player mix skews toward integrated platform vendors with network-centric and endpoint-centric specializations. The vendor base concentrates around three strategic tiers: consolidated security platforms capturing Fortune 500 accounts, cloud-native specialists serving mid-market financial services, and deception technology developers targeting defense-adjacent segments. Dominant competitive moves include portfolio consolidation through acquisition and geographic expansion via regional SOC establishment.
Within the integrated platform tier, Cisco Systems and Palo Alto Networks exemplify divergent architectural approaches to enterprise deployment. Cisco leverages its security fabric dominance across network-centric Fortune 500 implementations, while Palo Alto Networks sustains investment intensity in cloud-native threat detection workflows. CrowdStrike occupies a specialized position anchoring endpoint-centric telemetry for extended detection and response architectures. Microsoft Corporation represents the cloud-platform vector, embedding threat protection within productivity and infrastructure service bundles.
| Leading Market Players |
|---|
| Cisco Systems, Inc. |
| Microsoft Corporation |
| Palo Alto Networks, Inc. |
| McAfee, LLC |
| Fortinet, Inc. |
| CrowdStrike |
| Symantec |
| FireEye, Inc. |
| Trend Micro, Inc. |
| Others |
Supply & Pricing Matrix
Cloud-native threat detection platforms displacing on-premise hardware appliances simultaneously redistribute supply geography toward United States and Israeli software vendors while compressing capital-intensive pricing models across European and Japanese procurement offices.
Pricing Analysis
Certification level creates the primary spread between premium and standard tiers, with ISO/IEC 27001 and BSI-certified configurations commanding substantial premiums over uncertified alternatives. The dominant pricing structure runs through tiered SaaS subscriptions scaled by endpoint count and analyst seat volume. Price differentiation rests on threat intelligence feed quality and managed detection response bundling. Pricing pressure stems from mid-market buyers disaggregating EDR agents from full MDR services. Government agencies exhibit least price sensitivity; mid-market manufacturing shows highest.
Supply Chain Analysis
Silicon Valley-Tel Aviv corridor concentration of threat intelligence engineers anchors global APT protection R&D capacity. Component sourcing draws from Taiwan for specialized network processors, Ireland for European data center infrastructure, and India for Hindi-language SOC analyst training pipelines. Supply chain risk centers on single-source vulnerability for zero-day exploit research talent. Distribution runs through direct enterprise sales teams supplemented by regional system integrators in Germany and Japan.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The APT protection market sits in early-cycle expansion driven by NIS2 compliance deadlines compressing European procurement timelines through mid-decade.
For Market Incumbents: Fortify platform integration depth by embedding deception technology modules directly within endpoint agents, neutralizing point-solution challengers. Expand captive threat intelligence collection through regional SOC establishment in India and Singapore, reducing feed licensing costs. Prioritize BSI and METI pre-certification to compress German and Japanese sales cycles. For New Entrants and Emerging Players: ISO/IEC 27001 fast-track programs enable rapid qualification for European mid-market manufacturing contracts currently underserved by tier-1 vendors. White-space concentration appears in OT-IT convergence security for automotive and semiconductor fabrication facilities. Go-to-market positioning should emphasize protocol-aware monitoring without requiring full SOC liability assumption. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors deception technology specialists with defense-adjacent customer relationships. Long-term viability hinges on quantum-resistant cryptography integration capabilities. Acquisition target archetype: Israeli or United States-based adversary-engagement platform developers with active TTP capture deployments. Signal to watch: FCC supply-chain rule expansion beyond telecom into critical infrastructure sectors.| Strategic Initiative | Industry Significance |
|---|---|
| Regional SOC Establishment | Indian CERT-In compliance and Hindi-language operations capture state-owned enterprise procurement. |
| Deception Technology Integration | High-interaction honeypot modules differentiate endpoint platforms against signature-based competitors. |
| Quantum-Resistant Cryptography Investment | Long-horizon encrypted data capture risks create retrospective liability for non-upgraded protocols. |
| OT-IT Convergence Security Development | Manufacturing and energy facilities require protocol-aware monitoring for collapsed network architectures. |
| Threat Intelligence Feed Expansion | Parallel architectures for German, Japanese, and United States classification regimes reduce infrastructure duplication. |
Research Methodology
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CISOs at Fortune 500 financial institutions, federal civilian agency security directors, German BSI certification auditors, and managed detection response service architects. Secondary validation incorporated FCC supply-chain security filings, EU NIS2 implementation timelines, METI cybersecurity framework documentation, and CERT-In mandate disclosures. Bottom-up endpoint deployment estimates and top-down security spending allocations were triangulated against vendor revenue disclosures.
Across the analysis window, volume projections were derived from segmentation across deployment topology, solution layer, and end-user industry with regional regulatory cluster overlays. CAGRs were computed from modeled endpoint agent installations, threat intelligence subscription renewals, and managed service contract values. Forecast inputs included NIS2 compliance deadline phasing, sovereign data-localization mandate expansion, and skilled analyst scarcity indices.
Decision-makers should treat outputs as directional under base assumptions of sustained state-sponsored intrusion activity and regulatory compliance acceleration; material deviation in either vector would warrant model refresh. Practitioners should keep alternative scenarios live as quantum decryption timelines and threat intelligence sharing treaty developments evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Critical Infrastructure Protection
Middle East and Africa Public Infrastructure Safety Market
Critical Infrastructure Protection
Global Airport and Marine Port Security Market
Critical Infrastructure Protection
North America Public Infrastructure Safety Market
Critical Infrastructure Protection
Tank Protection Market
Critical Infrastructure Protection
Global Railway Platform Security Market
Critical Infrastructure Protection
Insider Threat Protection Market
Critical Infrastructure Protection
Guardrail Protection System Market
Critical Infrastructure Protection
Asia-Pacific High-Integrity Pressure Protection System (HIPPS) Market
Critical Infrastructure Protection
Global High Integrity Pressure Protection System (HIPPS) Market
Critical Infrastructure Protection
North America Tank Protection Market
Critical Infrastructure Protection
Tele Protection Market
Critical Infrastructure Protection
Middle East and Africa Pipeline Security Market
Critical Infrastructure Protection
Blast Resistant and Bulletproof Buildings Market
Critical Infrastructure Protection
Counter Cyberterrorism Market
Critical Infrastructure Protection
Latin America Public Infrastructure Safety Market
Critical Infrastructure Protection
Global Threat Intelligence Platform Market