
 Role-Based Access Control (RBAC) Market | 2026-2036
Role-Based Access Control (RBAC) Market Size, Share, and Industry Trends Forecast 2026-2036
Role-Based Access Control (RBAC) Market Analytics
Legacy on-premises identity infrastructure is pivoting toward cloud-native architectures as enterprises retire siloed directory systems. Microsoft Corporation leverages its Azure Active Directory ecosystem to anchor enterprise identity workflows across hybrid environments. Amazon Web Services, Inc. competes through IAM-native integrations that extend permissions management into serverless and containerized workloads. Okta, Inc. specializes in workforce identity orchestration, sustaining differentiation via pre-built connectors to thousands of SaaS applications.
Role-Based Access Control is a security methodology that assigns permissions to users based on predefined organizational roles rather than individual identity attributes, typically enforced through policy engines that evaluate role hierarchies, separation-of-duty rules, and temporal constraints before granting resource access. Its primary purpose is to enforce least-privilege principles at scale while reducing administrative overhead in complex multi-system environments. Cloud-Based deployment now leads solution uptake as enterprises abandon capital-intensive directory hardware, while Privileged Access Management within the Solution segment captures disproportionate margin pools due to high-stakes use cases in critical infrastructure and financial services. Healthcare and BFSI end users dominate current spending, though Government verticals are accelerating procurement amid supply-chain security mandates.
The National Institute of Standards and Technology Special Publication 800-207 zero-trust framework and the Cybersecurity Maturity Model Certification program reshape federal procurement criteria, compelling contractors to implement dynamic role enforcement or risk disqualification. State-level data privacy laws in California and Virginia add compliance complexity that drives healthcare and retail buyers toward automated identity governance platforms. Stakeholders must monitor how AI-generated synthetic identities challenge static role definitions and whether adaptive access policies become a procurement prerequisite rather than a premium feature.
Market Dynamics
The migration from static role definitions to dynamic, context-aware access policies represents the dominant structural force reshaping RBAC architectures, as zero-trust mandates eliminate implicit trust models that once governed perimeter-based security.
Growth Catalysts
- NIST SP 800-207 Zero-Trust Framework:Federal contractors must implement continuous verification or face disqualification from Department of Defense procurement pools, accelerating identity governance modernization across the defense industrial base.
- Healthcare digitization:Patient record systems require granular access controls that RBAC delivers at scale, with HIPAA enforcement driving hospital system investments in automated provisioning.
- Cloud-native architectures:Kubernetes and serverless workloads demand policy engines that evaluate role hierarchies in real-time, replacing static directory-bound permissions.
Market Restraints
- Legacy directory consolidation costs:Enterprises face substantial capital outlays to decommission on-premises Active Directory forests and migrate decades of nested group policies.
- Identity sprawl complexity:Multi-cloud environments fragment role definitions across AWS IAM, Azure AD, and Google Cloud IAM, creating governance gaps that resist standardization.
- Synthetic identity fraud:AI-generated credentials exploit static role assignments, forcing costly upgrades to behavioral analytics and continuous authentication layers.
Strategic Opportunities
- CMMC compliance services:The Cybersecurity Maturity Model Certification program creates a captive market for managed identity governance among small defense contractors lacking in-house expertise.
- Operational technology convergence:Manufacturing and energy sectors seek unified RBAC spanning IT networks and industrial control systems, a white space largely unaddressed by current vendors.
- State privacy law fragmentation:California's CPRA and Virginia's CDPA impose divergent access-log retention requirements, creating demand for jurisdiction-aware policy automation.
Industry Challenges
- Identity architect scarcity:Organizations struggle to hire engineers proficient in both legacy LDAP protocols and cloud-native policy-as-code frameworks.
- Cross-domain integration friction:RBAC deployments stall when connecting modern SaaS provisioning to mainframe-era systems still governing core financial transactions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Role-Based Access Control (RBAC) Market |
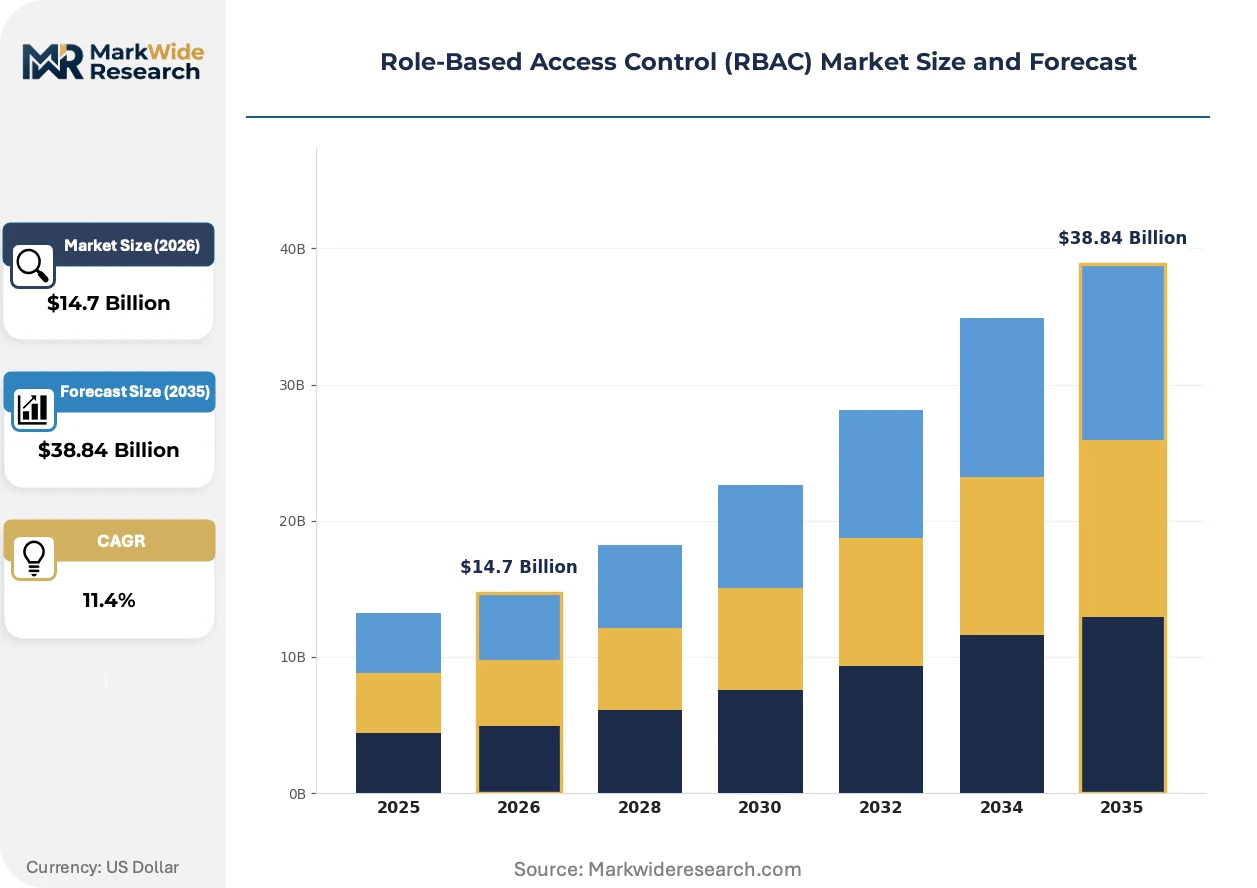
| Market Size in 2026 | $14.7 Billion |
| Market Size in 2035 | $38.84 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Healthcare, BFSI, Retail, Government Solution: Identity Management, Privileged Access Management, Directory Services, Compliance Management Industry Vertical: Education, Manufacturing, Energy, Telecommunications |
| Companies Covered | Microsoft Corporation, Amazon Web Services, Inc., IBM Corporation, Oracle Corporation, Okta, Inc., CyberArk Software Ltd., Broadcom Inc., SolarWinds, JumpCloud Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Role-Based Access Control (RBAC) Market Evolving Landscape
Artificial intelligence and policy-as-code frameworks are dissolving the boundary between identity governance and infrastructure automation, compressing deployment cycles while elevating technical sophistication requirements.
Attribute-based access control (ABAC) is modularizing traditional RBAC implementations by enabling runtime policy evaluation against user context, device posture, and resource sensitivity rather than pre-defined role assignments. Financial services institutions are adopting hybrid models fastest, layering ABAC rules atop existing role hierarchies to satisfy transaction-level audit requirements without forklift upgrades. This convergence is compressing vendor differentiation around static directory features while elevating policy-engine performance as the primary procurement criterion.
GDPR Article 32 mandates for access-log integrity and breach-notification timelines are forcing European enterprises to retire manual provisioning workflows in favor of automated identity lifecycle management. The regulation's extraterritorial reach extends compliance obligations to any organization processing EU resident data, reshaping procurement specifications for multinational healthcare and retail buyers. German automotive suppliers and French pharmaceutical manufacturers now prioritize identity platforms with built-in data-residency controls and EU-sovereign cloud deployment options.
Buyer organizations are consolidating vendor relationships from point-solution identity stacks toward integrated platforms spanning workforce, customer, and privileged access use cases. Healthcare delivery networks and regional banks, historically fragmented across Okta, CyberArk, and SailPoint deployments, now issue unified RFPs demanding consolidated entitlements visibility. This concentration is most visible in the United States, where mid-market enterprises seek to reduce integration tax and streamline SOC 2 audit preparation through single-vendor accountability.
Role-Based Access Control (RBAC) Market Segmentation
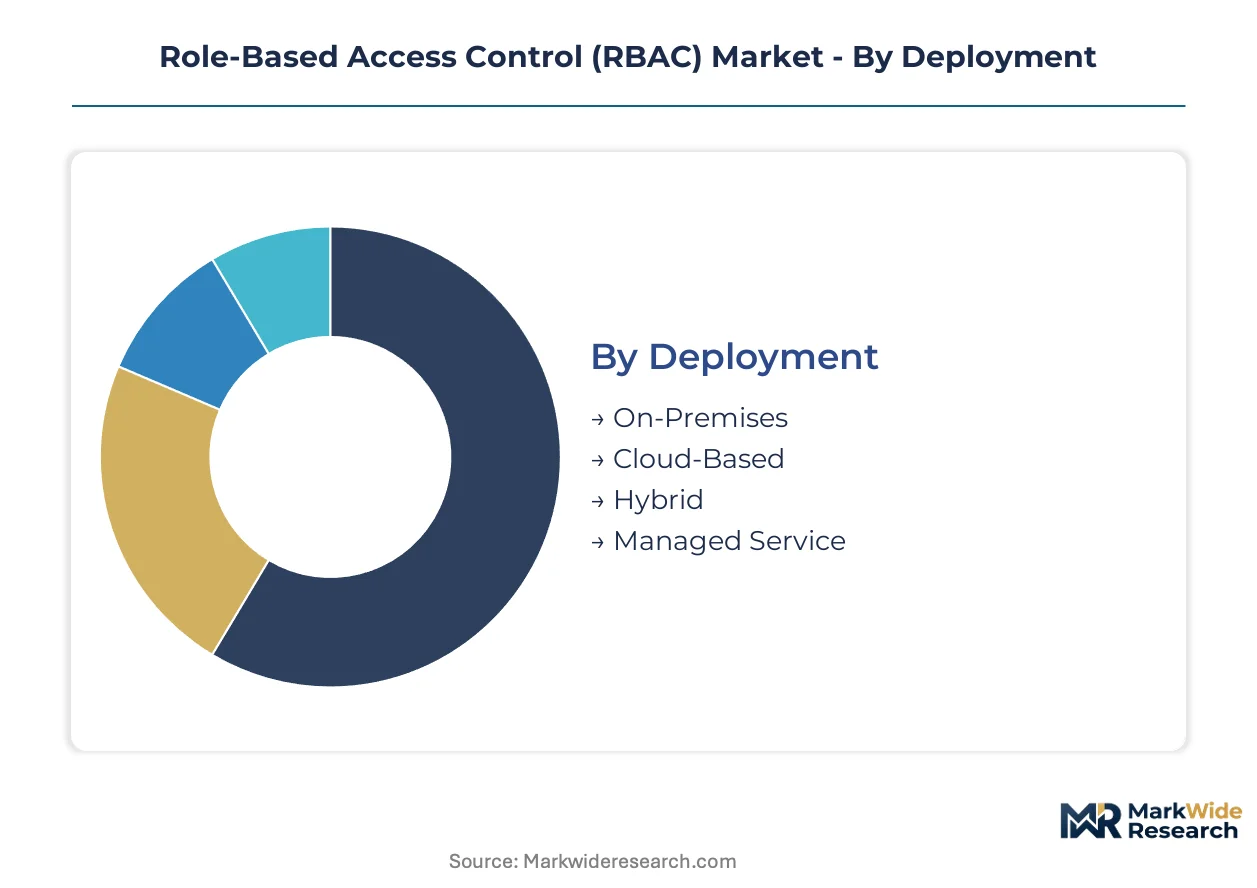
RBAC procurement patterns diverge sharply across deployment models and end-use contexts. Solution architecture choices directly determine compliance posture and operational scalability for identity governance programs.
Deployment:
Cloud-native configurations now command premium pricing while legacy infrastructure retains volume share in regulated sectors.
- Cloud-Based:Multi-tenant architectures with API-first policy engines enable real-time role synchronization across distributed SaaS estates. Healthcare delivery networks in the United States favor this model for HIPAA-aligned audit trails and rapid provisioning of temporary clinical staff.
- On-Premises:Dedicated hardware deployments with air-gapped directory services persist where data residency mandates prohibit external hosting. Defense contractors facing CMMC requirements maintain these configurations for controlled unclassified information environments despite higher capital intensity.
- Hybrid:Split architectures synchronizing legacy Active Directory forests with cloud identity providers bridge migration timelines for Fortune 500 enterprises.
- Managed Service:Outsourced identity operations with SLA-backed uptime commitments appeal to mid-market organizations lacking internal security engineering depth.
Mature deployment sits with On-Premises. Newer deployment is concentrated in Cloud-Based.
End User:
Regulatory pressure intensity, not organization size, determines segment profitability and solution complexity requirements.
- Healthcare:Patient record systems demand granular role hierarchies with temporal access constraints for rotating clinical staff. HIPAA enforcement actions against major hospital systems accelerate replacement of manual provisioning workflows with automated identity lifecycle management.
- BFSI:Transaction systems require separation-of-duty enforcement and privileged session recording to satisfy SOX and PCI-DSS audit requirements. Large North American banks layer behavioral analytics atop core RBAC to detect anomalous access patterns in real-time.
- Government:Federal agencies and contractors implement zero-trust architectures with continuous verification replacing static perimeter models.
- Retail:Seasonal workforce fluctuations drive demand for rapid role provisioning and deprovisioning across point-of-sale and e-commerce platforms.
Procurement sophistication clusters in BFSI. Fastest expansion trajectory appears in Government verticals responding to federal cybersecurity mandates.
Solution:
Margin concentration follows risk exposure, with high-stakes access scenarios commanding disproportionate investment.
- Privileged Access Management:Vaulting and session isolation technologies for administrative credentials protect critical infrastructure against lateral movement attacks. Energy sector operators deploy these solutions to secure industrial control system access where compromise threatens physical safety.
- Identity Management:Core provisioning and lifecycle automation platforms form the foundational layer of enterprise access governance. Manufacturing enterprises adopt these systems to unify workforce identity across acquired subsidiaries with disparate directory histories.
- Directory Services:Centralized authentication stores with hierarchical group policy enforcement remain essential for hybrid cloud architectures.
- Compliance Management:Automated access certification and attestation workflows reduce audit preparation burden for publicly traded entities.
Technology maturity centers on Directory Services. Innovation investment flows toward Privileged Access Management.
Industry Vertical:
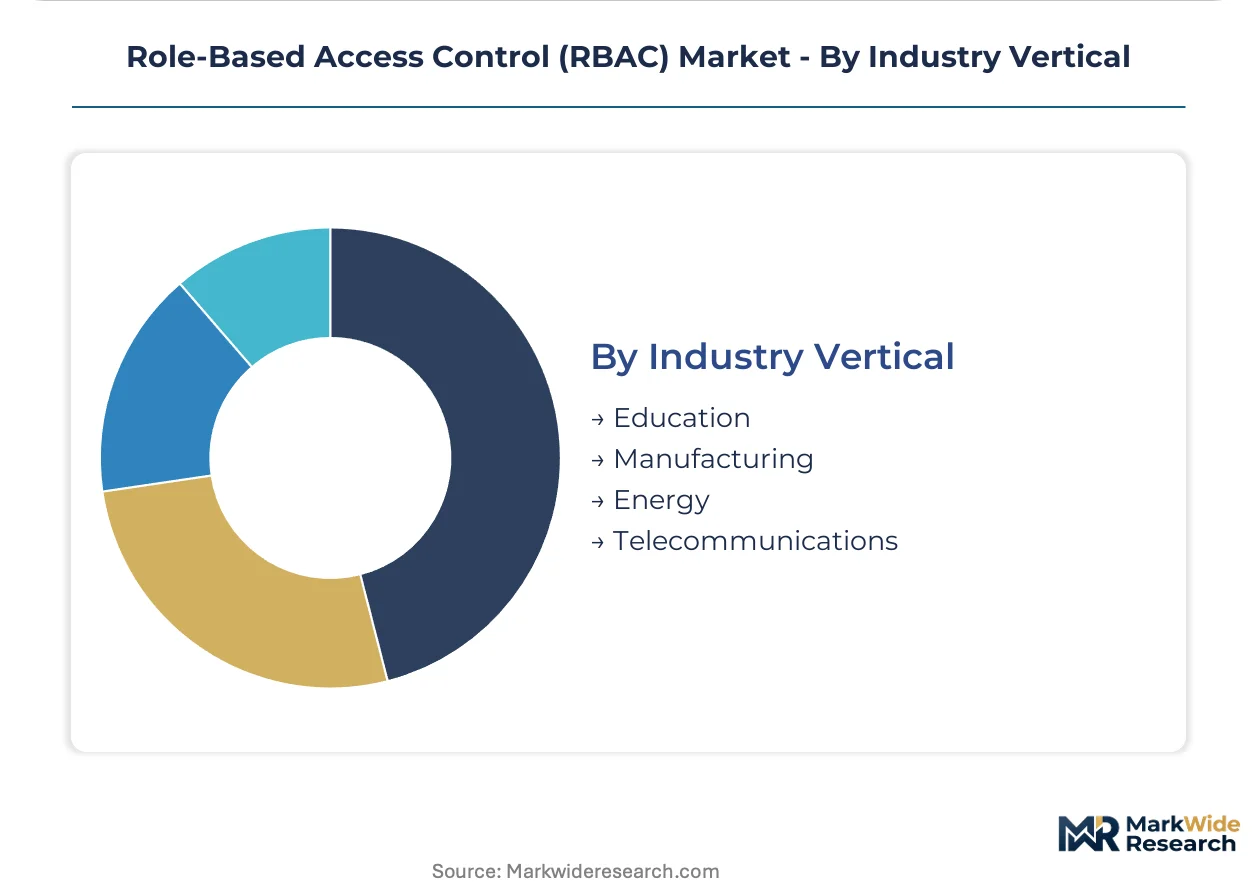
Operational technology convergence creates white-space opportunities where IT-centric vendors lack industrial domain expertise.
- Manufacturing:Unified RBAC spanning enterprise ERP systems and shop-floor industrial control networks addresses long-standing governance gaps. German automotive suppliers lead adoption, driven by supply-chain security requirements from OEM customers.
- Energy:Critical infrastructure protection mandates from national regulators compel utilities to implement role-based access for both IT and OT environments. North American electric utilities face NERC CIP compliance deadlines that accelerate procurement timelines.
- Telecommunications:Subscriber data protection and network equipment access controls drive investment in scalable policy engines.
- Education:Federated identity for multi-campus systems and research collaboration networks creates demand for inter-institutional trust frameworks.
Established deployments concentrate in Telecommunications. Emerging demand surfaces in Manufacturing as IT-OT convergence accelerates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Enterprise demand for identity governance concentrates in the United States, where federal cybersecurity mandates and cloud-first modernization programs accelerate procurement timelines. Healthcare systems and defense contractors drive substantial deployment volumes across distinct compliance frameworks.
United States
Federal agencies and defense contractors dominate procurement under CMMC and NIST SP 800-207 mandates requiring continuous verification architectures. The Cybersecurity and Infrastructure Security Agency enforces binding operational directives that compel civilian departments to retire perimeter-based trust models. Defense industrial base clusters in Northern Virginia and San Diego sustain concentrated vendor engagement for zero-trust implementations.
Germany
Automotive suppliers and pharmaceutical manufacturers prioritize identity platforms with EU-sovereign cloud deployment options to satisfy GDPR Article 32 access-log integrity requirements. The national data protection authority enforces strict data residency rules that disadvantage non-European cloud providers. Industrial automation hubs in Baden-Württemberg and Bavaria drive unified RBAC demand spanning enterprise ERP and shop-floor control systems.
United Kingdom
Financial services institutions in London deploy hybrid ABAC-RBAC models to satisfy transaction-level audit requirements without forklift infrastructure upgrades. The Financial Conduct Authority mandates operational resilience standards that accelerate replacement of manual provisioning workflows. Fintech clusters in London and Edinburgh generate concentrated demand for API-first policy engines supporting real-time role synchronization.
Japan
Manufacturing enterprises and telecommunications operators seek scalable policy engines for subscriber data protection and multi-cloud workload governance. METI guidelines on supply-chain security reshape procurement specifications for automotive and electronics exporters. Industrial concentrations in the Kanto and Kansai regions anchor workforce identity orchestration investments amid aging IT infrastructure replacement cycles.
India
IT services exporters and banking networks drive cloud-native identity adoption as RBI cybersecurity guidelines harden access control requirements for financial transactions. The Digital India program accelerates public sector modernization, creating demand for automated lifecycle management in government health and education systems. Technology clusters in Bengaluru and Hyderabad sustain concentrated vendor development and deployment partnerships.
Role-Based Access Control (RBAC) Market Competitive Landscape
Branded specialists and contract manufacturers split share differently across segments, with hyperscale cloud providers capturing foundational directory services while pure-play identity vendors defend premium workforce orchestration positions. Market structure tilts toward consolidation at the infrastructure layer and fragmentation in specialized privileged access and compliance automation niches. Three archetypes dominate: platform conglomerates extending identity from adjacent cloud ecosystems, standalone identity specialists sustaining differentiation via connector breadth, and cybersecurity incumbents bundling RBAC within broader zero-trust portfolios. Competitive dynamics center on M&A activity absorbing point-solution vendors and strategic partnerships bridging legacy mainframe systems with cloud-native policy engines.
Within the platform conglomerate tier, Microsoft Corporation and Amazon Web Services, Inc. anchor enterprise identity workflows through native integration with dominant cloud compute and productivity ecosystems. Okta, Inc. occupies a position exemplifying the standalone specialist archetype, with workforce identity orchestration sustained through pre-built SaaS connector libraries. These three entities collectively represent the competitive fault lines shaping procurement decisions across hybrid and multi-cloud environments.
| Leading Market Players |
|---|
| Microsoft Corporation |
| Amazon Web Services, Inc. |
| IBM Corporation |
| Oracle Corporation |
| Okta, Inc. |
| CyberArk Software Ltd. |
| Broadcom Inc. |
| SolarWinds |
| JumpCloud Inc. |
| Others |
Value Network & Pricing Analysis
Identity architect scarcity in Northern California and the Washington DC corridor widens labor-cost differentials between premium-tier managed service providers and economy-tier self-service platforms, compressing mid-market pricing spreads as vendors compete for finite cloud-security engineering talent.
Pricing Analysis
Volume concentrates in standardized SaaS subscriptions while margins accrue to customized zero-trust implementations. Pricing stratifies across premium, standard, and economy tiers, with differentiation anchored in FedRAMP certification level and API integration depth. Cost compression in the economy tier intensifies because hyperscaler bundling subsidizes directory services. Federal contractors exhibit least price sensitivity given CMMC disqualification risk, while mid-market healthcare systems demonstrate highest sensitivity amid capital-constrained EMR modernization cycles.
Supply Chain Analysis
Workforce availability constraints in India, Poland, and Romania shape delivery capacity for implementation services and managed security operations. Software development draws from open-source policy-engine frameworks, proprietary AI/ML training pipelines, and cloud infrastructure APIs. Single-source vulnerability sits with hyperscaler identity API dependencies. Distribution runs through direct enterprise sales, channel partners, and cloud marketplace listings.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market is consolidating as zero-trust mandates force point-solution vendors toward platform acquisition or obsolescence.
For Market Incumbents: Deploy policy-engine performance optimization to defend against ABAC-native challengers eroding static RBAC differentiation. Acquire specialized OT-security boutiques to capture manufacturing convergence demand before industrial vendors lock in channel relationships. CMMC compliance service capabilities anchor retention across the defense industrial base. For New Entrants and Emerging Players: AI-generated synthetic identity detection offers a technology-first wedge against legacy vendors with behavioral analytics gaps. Manufacturing IT-OT convergence presents the most penetrable white space, with German automotive suppliers and North American electric utilities seeking unified governance. A channel-first go-to-market through industrial automation distributors bypasses entrenched enterprise software procurement cycles. For Investors and Strategic Acquirers: Re-rating potential sits with ABAC-native specialists given NIST SP 800-207 continuous verification mandates accelerating runtime policy evaluation procurement. Long-term viability centers on platforms spanning workforce, customer, and privileged access use cases under single architectural control. The signal to watch is defense contractor RFP language shifting from "RBAC-compatible" to "ABAC-required" as a binary qualification criterion.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unified entitlements visibility reduces SOC 2 audit preparation burden for healthcare delivery networks. |
| Acquisition of Specialist Firm | OT-security boutiques capture manufacturing convergence demand ahead of industrial vendor lock-in. |
| Product Launch | AI-native synthetic identity detection addresses static role assignment vulnerabilities in financial services. |
| Strategic Partnership | Hyperscaler marketplace listings accelerate procurement velocity for mid-market cloud-first enterprises. |
| Geographic Expansion | EU-sovereign cloud deployments satisfy German automotive supplier GDPR Article 32 data residency requirements. |
Research Methodology
Independent corroboration across CISO interviews, identity architect surveys, and federal procurement database analysis underwrites the qualitative findings. Primary fieldwork engaged cloud security engineers, healthcare IT directors, defense contractor compliance officers, and SaaS procurement leads. Secondary validation drew from NIST SP 800-207 implementation guidance, CMMC accreditation body records, hyperscaler identity service disclosures, and HIPAA enforcement action summaries. Bottom-up deployment estimates and top-down vendor revenue analysis triangulate market sizing.
Rate-of-change decomposition separates structural zero-trust adoption velocity from cyclical healthcare EMR replacement timing. Segmentation modeling spans deployment architecture, end-user vertical, solution type, and integration complexity across the projection horizon. CAGRs derive from policy-engine transaction volume trajectories and workforce identity orchestration seat expansion. Cloud-native workload governance penetration and federal contractor certification timelines feed scenario-weighted outputs.
Forecast precision tightens around the base case; tail outcomes carry wider variance under synthetic identity fraud acceleration or hyperscaler bundling subsidy withdrawal. Assumptions reflect current regulatory enforcement intensity and cloud migration completion rates. Material deviation in CMMC audit backlogs or NIST framework revision timing warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Access Control Systems
Industrial Barrier Systems Market
Access Control Systems
Smart Door Lock Market
Access Control Systems
Global Industrial Access Control Market
Access Control Systems
US Restricted Access Barrier System Market
Access Control Systems
Access Control and Authentication Market
Access Control Systems
Wireless Security System Market
Access Control Systems
Facial Recognition Access Control Solution Market
Access Control Systems
Global Industrial Security Systems Market
Access Control Systems
Pedestrian Entrance Control System Market
Access Control Systems
India Access Control Hardware Market
Access Control Systems
RFID Locks Market
Access Control Systems
Access Control Readers Market
Access Control Systems
Global Fingerprint Access Control Systems Market
Access Control Systems
Global Automatic Door Control Market
Access Control Systems
Electronic Security Systems Market
Access Control Systems
Airport Passenger Screening System Market