
 Specialized Threat Analysis and Protection Market | 2026-2036
Specialized Threat Analysis and Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Specialized Threat Analysis and Protection Market Outlook
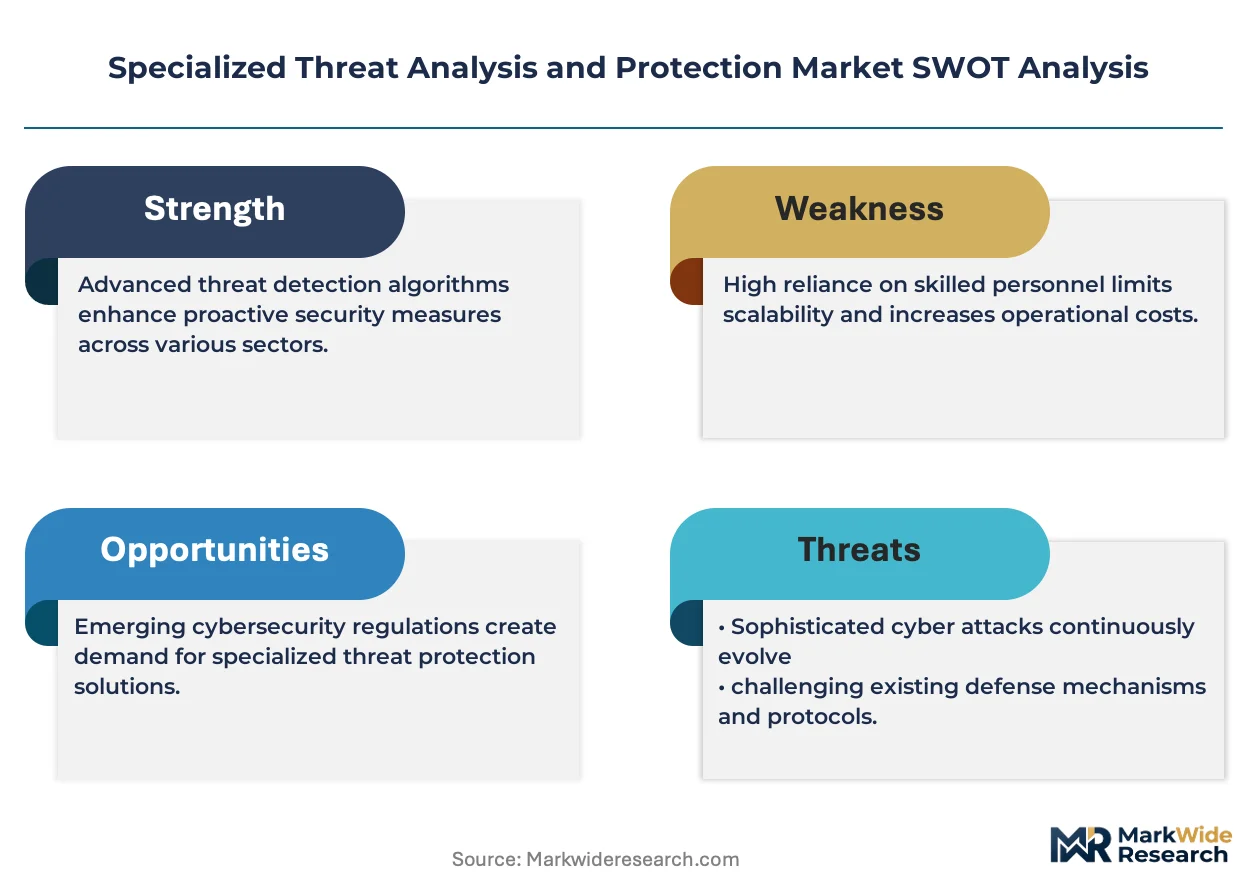
The capability gap between asset-intensive platform builders and lightweight analytics vendors is unwinding competitive dynamics across the sector. Palo Alto Networks leverages its integrated hardware-software stack to dominate enterprise firewall deployments with embedded threat intelligence. Claroty anchors its position through deep specialization in industrial control system visibility, sustaining premium pricing in manufacturing and energy verticals. Dragos competes narrowly but intensely on operational technology expertise, occupying a defensible niche that broader IT-security players struggle to replicate.
Specialized threat analysis and protection encompasses integrated cybersecurity platforms engineered to detect, analyze, and neutralize advanced persistent threats through real-time telemetry correlation across endpoints, networks, and operational technology environments, typically processing millions of events per second with sub-second response latency. Its primary commercial purpose centers on preventing unauthorized access, data exfiltration, and operational disruption in high-consequence infrastructure. Endpoint Security solutions lead current revenue pools as distributed workforces multiply attack surfaces, while behavioral analysis capabilities within the technology dimension represent the fastest-expanding segment as AI-driven anomaly detection displaces signature-based methods. Cloud-based deployment models now capture disproportionate growth investment from vendors restructuring delivery architectures away from on-premises appliance dependency.
The NIS2 Directive and GDPR framework in Europe, alongside FDA cybersecurity guidance for connected medical devices in the United States, collectively elevate baseline product standards and compress market access for non-compliant vendors. CISA binding operational directives for federal agencies further shape procurement specifications, mandating specific threat intelligence sharing protocols and vulnerability disclosure timelines. Stakeholders must monitor the divergence between European regulatory harmonization and U.S. sector-specific mandates, as compliance architecture choices made now will determine geographic scalability of platform investments.
Market Dynamics
AI-driven behavioral analytics is compressing detection latency from hours to milliseconds, forcing platform vendors to rearchitect around real-time inference engines or cede enterprise accounts to integrated stack providers.
Growth Catalysts
- Operational technology mandates:NATO defense agencies now require continuous OT monitoring for critical infrastructure, creating procurement pull for specialized threat platforms in energy and transportation systems.
- Behavioral analysis displacement:AI-driven anomaly detection is replacing signature-based methods, expanding addressable market for platforms processing high-velocity telemetry across distributed endpoints.
- NIS2 Directive enforcement:The European regulatory framework tightens baseline cybersecurity requirements for essential entities, elevating compliance-driven demand across manufacturing and healthcare verticals.
Market Restraints
- Specialized talent scarcity:The operational technology security skill gap constrains deployment velocity, with industrial control system expertise concentrated among a narrow practitioner pool.
- Integration complexity:Legacy industrial infrastructure lacks standardized telemetry interfaces, forcing costly custom engineering for threat platform deployment in brownfield environments.
- Input cost volatility:GPU and specialized inference hardware pricing fluctuates with semiconductor supply constraints, compressing margin for appliance-dependent vendors.
Strategic Opportunities
- Cloud-native delivery architectures:Vendors restructuring away from on-premises dependency capture disproportionate growth investment as federal agencies accelerate CISA-directed platform deployment.
- Medical device security:FDA cybersecurity guidance for connected devices creates compliance-driven demand in healthcare, an underpenetrated vertical for OT-specialized vendors.
- Convergence of IT-OT security:Unified platforms correlating enterprise network and industrial control telemetry address the visibility gap that siloed solutions cannot bridge.
Industry Challenges
- Certification timeline compression:Federal procurement mandates increasingly require FedRAMP and Common Criteria certification, extending sales cycles by 12-18 months for new market entrants.
- Legacy system integration friction:Proprietary protocols in aging industrial infrastructure resist standardized telemetry extraction, forcing vendor investment in protocol-specific parsers.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Specialized Threat Analysis and Protection Market |
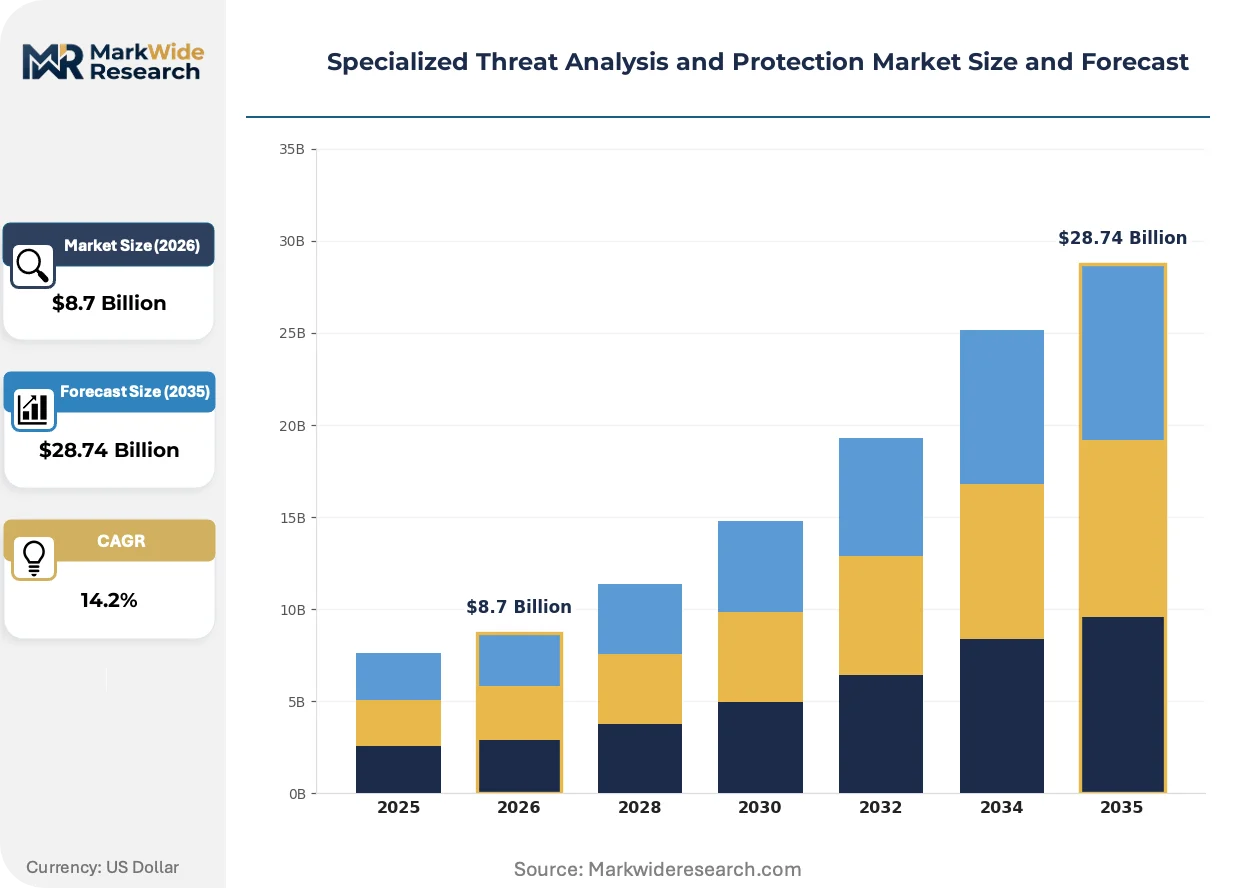
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $28.74 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
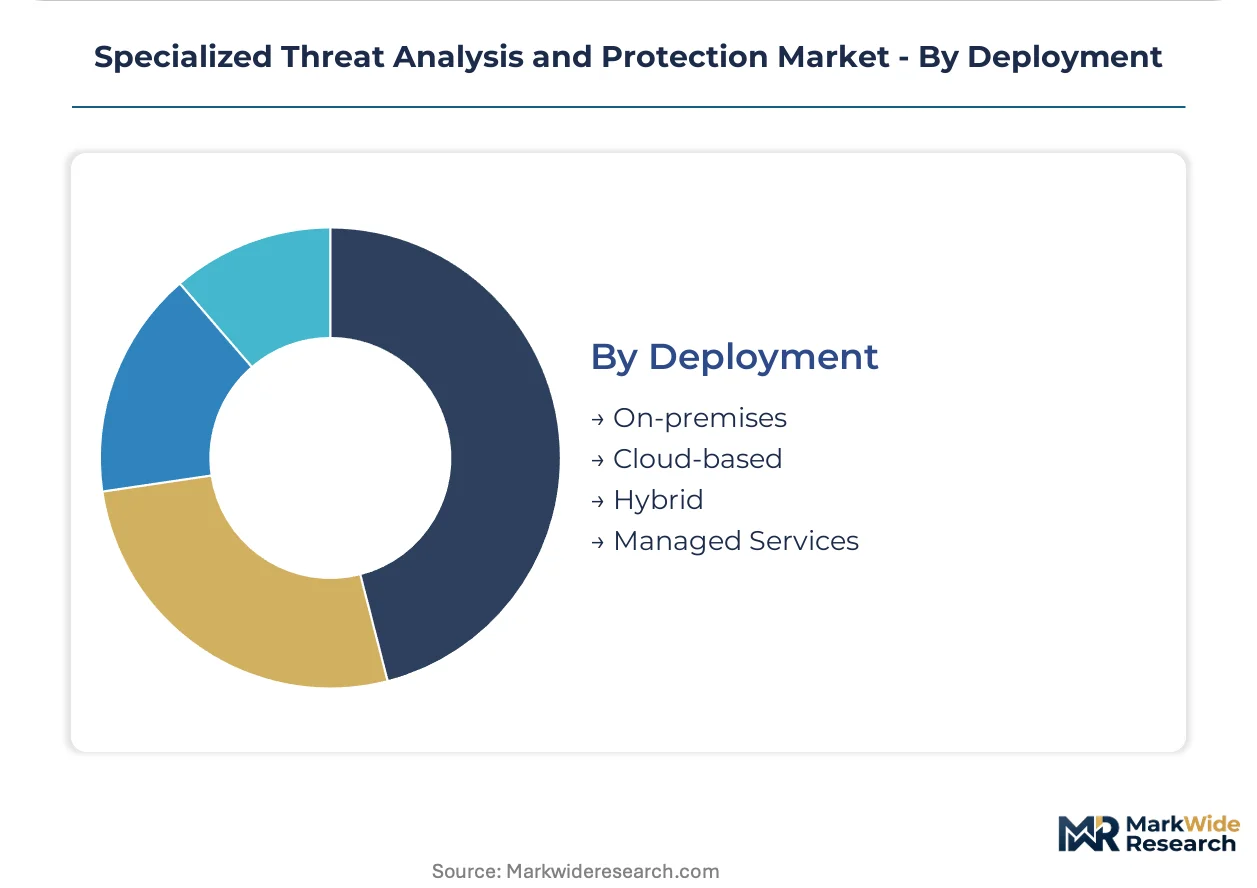
| Segmentation | Product Type: Endpoint Security, Firewall, Intrusion Detection, Security Information and Event Management Technology: Artificial Intelligence, Machine Learning, Behavioral Analysis, Threat Intelligence End User: Healthcare, Financial Services, Government, Retail Deployment: On-premises, Cloud-based, Hybrid, Managed Services |
| Companies Covered | Armis, Palo Alto Networks, Claroty, Elisity, Tenable, Dragos, Microsoft, SecurityScorecard, Nozomi Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Specialized Threat Analysis and Protection Market Strategic Shifts
Threat detection architectures are pivoting from perimeter-centric models to continuous telemetry correlation across hybrid environments, compressing the competitive window for single-vector specialists.
Edge-deployed inference engines are miniaturizing detection logic for deployment directly on industrial controllers and medical devices. Manufacturing operators with distributed plant networks are adopting these embedded modules fastest, compressing the addressable market for centralized SIEM-only vendors as response latency requirements tighten.
CISA binding operational directives now mandate specific threat intelligence sharing protocols and vulnerability disclosure timelines for federal agencies. This regulatory architecture shapes procurement specifications, forcing platform vendors to restructure product roadmaps around automated indicator exchange or exit the federal channel entirely.
Security procurement in critical infrastructure is consolidating around multi-year managed detection and response contracts. Energy utilities and water treatment operators are unbundling point-product purchases in favor of outcome-guaranteed service relationships, a pattern most visible in United States federal and state-level procurement where budget predictability outweighs capital expenditure flexibility.
Specialized Threat Analysis and Protection Market Segmentation
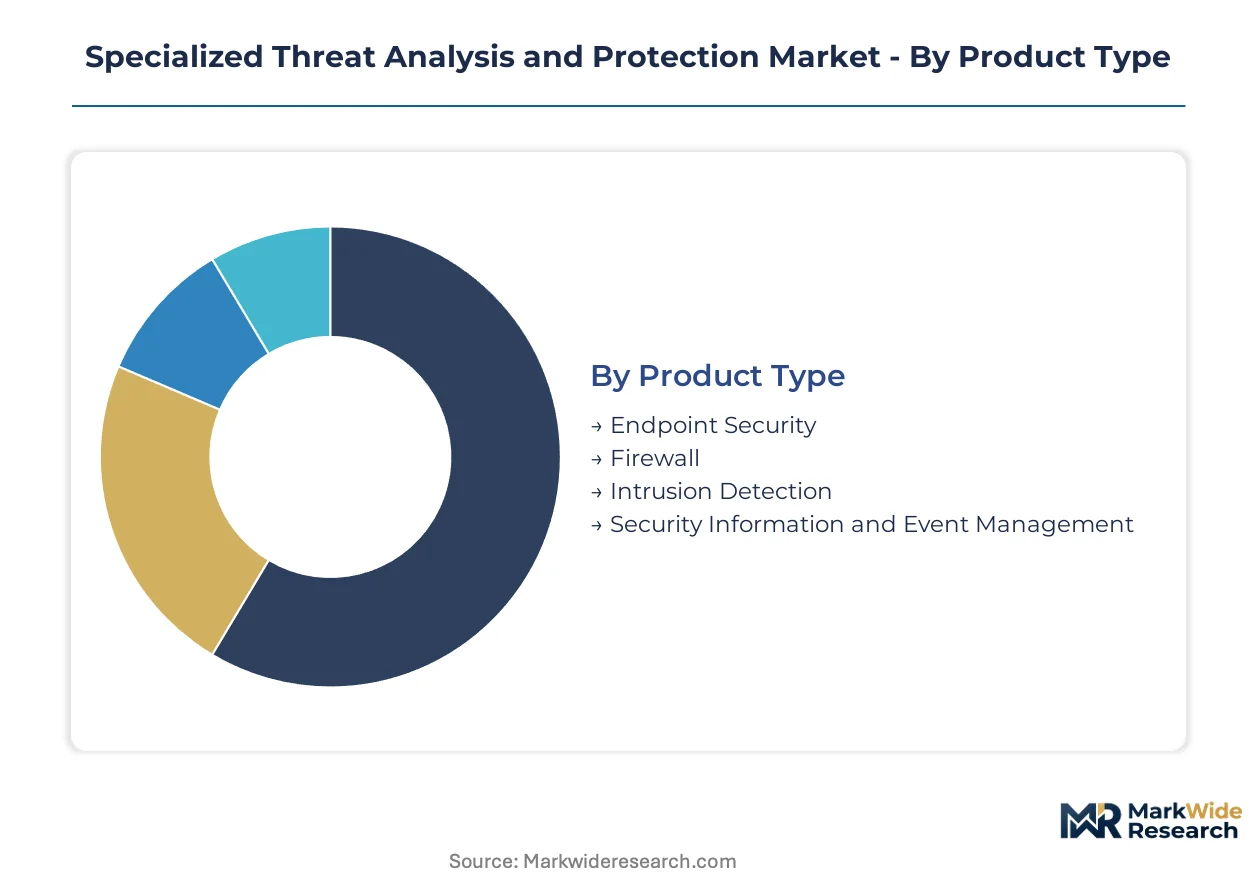
Segmentation in specialized threat analysis and protection reveals how procurement priorities diverge across infrastructure types and regulatory environments. Buyers in defense and critical infrastructure channels select for OT-specific capabilities, while enterprise accounts prioritize cloud-native delivery and AI-driven detection speed.
Product Type:
Domestic procurement dominates for on-premises appliances serving classified environments, whereas cloud-delivered platforms increasingly serve export markets seeking scalable threat intelligence.
- Endpoint Security:Distributed agent architectures monitor laptops, servers, and mobile devices through continuous telemetry collection. Demand concentrates in United States federal agencies implementing CISA binding operational directives, with procurement cycles extending 12-18 months for FedRAMP certification compliance.
- Firewall:Next-generation appliances integrate deep packet inspection with application-aware policy enforcement. Energy utilities and water treatment operators in NATO member states favor hardware-software bundles that embed threat intelligence feeds directly into perimeter defenses.
- Intrusion Detection:Network sensors identify anomalous traffic patterns through signature and behavioral matching. Manufacturing verticals deploy these systems for legacy protocol visibility.
- Security Information and Event Management:Centralized log aggregation platforms correlate alerts across heterogeneous security stacks. Managed security service providers consume these platforms as multi-tenant infrastructure.
Endpoint Security holds the largest share; momentum sits with Security Information and Event Management as service providers consolidate customer telemetry.
Technology:
Cost tiering separates premium AI inference engines from commoditized signature databases, with behavioral methods commanding 40-60% pricing premiums over static rule sets.
- Artificial Intelligence:Neural network architectures process millions of events per second through GPU-accelerated inference clusters. United States defense agencies mandate sub-millisecond detection latency for critical infrastructure, driving procurement of specialized inference hardware.
- Behavioral Analysis:Statistical models establish baseline activity profiles and flag deviations without predefined attack signatures. Healthcare delivery organizations adopt these capabilities fastest as FDA cybersecurity guidance tightens monitoring requirements for connected medical devices.
- Machine Learning:Supervised and unsupervised algorithms refine detection accuracy through continuous retraining on labeled threat data. Financial services deploy these tools for fraud pattern recognition.
- Threat Intelligence:Curated indicator feeds and adversary attribution databases enrich detection context. Government sector procurement specifies automated STIX/TAXII exchange protocols.
Artificial Intelligence captures dominant investment; Behavioral Analysis is expanding most quickly as signature methods lose efficacy against polymorphic attacks.
End User:
Application intensity varies by attack surface complexity, with operational technology environments requiring specialized parsers that IT-centric vendors struggle to deliver.
- Government:Federal, state, and local agencies operate under mandatory continuous monitoring regimes with classified threat intelligence access. United States procurement channels specify Common Criteria certification and CISA-directed vulnerability disclosure timelines.
- Healthcare:Hospital systems and medical device manufacturers face FDA cybersecurity guidance requiring premarket submission of software bills of materials. Endpoint agents on clinical workstations must avoid disrupting patient care workflows.
- Financial Services:Banks and payment processors prioritize real-time transaction monitoring and SWIFT network protection. Regulatory examinations drive refresh cycles.
- Retail:Point-of-sale networks and e-commerce platforms defend payment card data against credential stuffing and web skimming. Seasonal volume spikes stress detection infrastructure.
Government holds the largest share; momentum sits with Healthcare as FDA enforcement tightens device security requirements.
Deployment:
Customer type segmentation shows enterprise buyers favoring capital expenditure models while critical infrastructure operators shift toward operational expenditure predictability.
- Cloud-based:SaaS delivery eliminates appliance maintenance and enables elastic processing capacity during attack campaigns. United States federal agencies accelerate migration under CISA cloud security guidance.
- Managed Services:Outsourced security operations centers deliver 24/7 monitoring with outcome-guaranteed service level agreements. Energy utilities and municipal water systems adopt these contracts fastest.
- On-premises:Air-gapped deployments serve classified networks and regulatory jurisdictions with data residency requirements. Hardware supply constraints extend lead times.
- Hybrid:Split architectures process sensitive telemetry locally while forwarding sanitized metadata to cloud analytics. Manufacturing with distributed plant networks favors this model.
On-premises retains the largest installed base; Cloud-based deployment is gaining share fastest as federal procurement accelerates CISA-directed platform modernization.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Federal buyers in the United States demonstrate the lowest price elasticity, absorbing 40-60% premiums for FedRAMP-certified platforms, while municipal utilities and mid-market manufacturers in India and Brazil negotiate aggressively on total cost of ownership.
United States
CISA binding operational directives mandate automated threat intelligence sharing protocols for federal agencies, compressing procurement cycles for compliant vendors. Defense agencies anchor demand through NATO-aligned OT monitoring requirements for critical infrastructure. The Washington DC-Baltimore corridor concentrates cybersecurity procurement decision-making, with Virginia data centers serving classified cloud workloads.
Germany
Industrial manufacturers in the Ruhr and Bavaria drive demand for OT-specific visibility platforms as NIS2 enforcement tightens baseline requirements for essential entities. The country's national cybersecurity regulator, BSI, mandates incident reporting timelines that favor vendors with German-located security operations centers. Munich and Stuttgart host dense clusters of automotive and machinery producers adopting converged IT-OT security architectures.
United Kingdom
Financial services regulators in London prioritize real-time transaction monitoring and SWIFT network protection, refreshing detection infrastructure on compressed cycles. The National Cyber Security Centre shapes procurement specifications for critical national infrastructure operators. The Thames Valley corridor anchors cybersecurity R&D concentration, with Cambridge emerging as a behavioral analytics talent hub.
Japan
Manufacturing conglomerates in the Chubu region around Nagoya deploy edge-deployed inference engines for distributed plant networks, miniaturizing detection logic on industrial controllers. METI guidance on supply chain cybersecurity elevates platform standards for automotive and electronics exporters. The Tokyo-Osaka corridor concentrates managed security service provider consolidation.
India
IT services exporters in Bangalore and Hyderabad drive cloud-native platform adoption as they assume managed detection and response contracts for North American and European clients. The country's national cybersecurity agency, CERT-In, mandates incident reporting that shapes vendor localization requirements. Mumbai's financial district anchors domestic banking sector procurement for real-time fraud detection.
Specialized Threat Analysis and Protection Market Competitive Environment
A small set of integrated leaders sits above a broader specialist tier, with Palo Alto Networks and Microsoft leveraging stack breadth to capture enterprise firewall and cloud security consolidation, while Claroty and Dragos defend premium positions through OT-specific expertise that generalist vendors struggle to replicate. Three archetypes dominate: full-stack platform builders with hardware-software integration, vertical specialists with protocol-level industrial control system visibility, and cloud-native challengers rearchitecting delivery away from appliance dependency. Competitive moves concentrate on FedRAMP certification acceleration for federal channel access and managed detection and response contract unbundling to capture multi-year service relationships.
Among the integrated platform tier, Palo Alto Networks and Microsoft exemplify stack breadth strategies that embed threat intelligence across firewall, endpoint, and cloud workloads. Claroty and Dragos occupy the specialist vector, anchoring positions through deep operational technology expertise that commands pricing premiums in energy and manufacturing verticals. Tenable and Nozomi Networks sit within the converged IT-OT visibility segment, correlating enterprise network and industrial control telemetry where siloed solutions fail.
| Leading Market Players |
|---|
| Armis |
| Palo Alto Networks |
| Claroty |
| Elisity |
| Tenable |
| Dragos |
| Microsoft |
| SecurityScorecard |
| Nozomi Networks |
| Others |
Value Chain & Pricing Dynamics
GPU-accelerated inference hardware displacing CPU-bound detection engines simultaneously concentrates supply geography around Taiwan and South Korea while compressing pricing economics for appliance-dependent vendors unable to absorb semiconductor cost volatility.
Pricing Analysis
Managed detection and response contracts drive lifetime value beyond initial platform licensing, with three-tier pricing structure across premium, standard, and economy levels separating FedRAMP-certified federal deployments from municipal utilities and mid-market manufacturers. Price differentiation rests on certification grade and vertical integration depth, with integrated stack providers commanding premiums while point-product vendors face price erosion from GPU and specialized inference hardware cost compression. United States federal buyers demonstrate lowest price sensitivity, absorbing substantial premiums for compliant platforms, whereas procurement officers in India and Brazil negotiate aggressively on total cost of ownership.
Supply Chain Analysis
Taiwan and South Korea anchor advanced semiconductor fabrication for GPU and inference accelerator production, with the United States and Japan contributing specialized networking silicon and edge-deployed hardware modules. Component dependencies draw from rare earth processing concentrated in China, high-bandwidth memory from South Korean fabs, and precision analog components from Japanese suppliers. Single-source vulnerability around Taiwan Strait logistics chokepoints threatens delivery timelines for federal procurement channels. Distribution runs through direct enterprise sales teams serving classified environments, cloud marketplaces for SaaS delivery, and managed security service providers consolidating multi-tenant infrastructure.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The specialized threat analysis and protection market sits in cyclical recovery as defense procurement cycles accelerate NATO-aligned OT monitoring mandates and federal agencies modernize under CISA-directed platform deployment.
For Market Incumbents: Shield market position by accelerating FedRAMP and Common Criteria certification timelines to capture federal channel consolidation, while deepening backward integration into GPU-accelerated inference hardware to offset semiconductor cost volatility threatening appliance margins. Vertical control over threat intelligence feed curation defends against cloud-native challengers unbundling point-product architectures.
For New Entrants and Emerging Players: Lead with medical device security verticals where FDA cybersecurity guidance creates compliance-driven demand that OT-specialized incumbents have underpenetrated, and target managed detection and response contracts for municipal water systems and regional energy utilities seeking outcome-guaranteed service relationships rather than capital expenditure flexibility.
For Investors and Strategic Acquirers: Secondary-cycle assets sit with private equity-backed vertical specialists possessing protocol-level industrial control system expertise but lacking cloud-native delivery architectures to scale beyond manufacturing and energy verticals. Five-to-ten year viability hinges on convergence platform capabilities bridging IT-OT visibility gaps; monitor CISA binding operational directive expansion into state-level procurement as inflection signal for federal channel access premiumization.
| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Certification Acceleration | Compresses 12-18 month sales cycles for federal agency procurement under CISA mandates. |
| Cloud-Native Architecture Migration | Captures disproportionate growth investment as agencies exit on-premises appliance dependency. |
| OT Protocol Specialization Investment | Builds defensible moats in energy and manufacturing verticals that generalist vendors cannot replicate. |
| Managed Detection and Response Unbundling | Converts point-product purchases into multi-year service relationships with budget predictability. |
| Edge-Deployed Inference Miniaturization | Compresses response latency for distributed plant networks and connected medical devices. |
Study Parameters
Initial hypotheses were tested against primary input from CISOs at critical infrastructure operators, federal procurement officers, OT security practitioners, managed security service provider executives, and industrial control system engineers, and refined through secondary validation against SEC 10-K filings, CISA directive documentation, FDA cybersecurity guidance, NATO procurement records, and hyperscaler capex disclosures. Bottom-up deployment estimates across segmentation dimensions were triangulated with top-down market sizing from vendor revenue disclosures and federal contract databases.
Variance decomposition across the projection horizon isolates growth contributions from regulatory mandate expansion, technology displacement cycles, and vertical penetration patterns. Segmentation dimensions modeled encompass product type, deployment architecture, end-user vertical, and geographic regulatory cluster. CAGRs derive from logistic adoption curves fitted to procurement cycle data and compliance deadline acceleration. Industry-specific forecast inputs include CISA binding operational directive implementation timelines and NIS2 enforcement progression across European member states.
The analysis sits within stated boundaries; outcomes outside sustained federal procurement acceleration or semiconductor supply normalization would require recalibration. Forecasts reflect assumptions around regulatory harmonization and threat actor sophistication progression. Recalibration cycles align with material shifts in CISA directive scope or NATO OT mandate expansion.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Air Cargo Security Equipment Market
Security and Surveillance
Cargo and Vehicle Screening Market
Security and Surveillance
India Electronic Security Market
Security and Surveillance
Lawful Interception Market
Security and Surveillance
Integrated Security Services Market
Security and Surveillance
Global Security Orchestration Market
Security and Surveillance
Destructible Security Labels Market
Security and Surveillance
Sirens Market
Security and Surveillance
Europe Rockfall Radar Market
Security and Surveillance
Intrusion Alarm System Market
Security and Surveillance
Underwater Security (Systems and Services) Market
Security and Surveillance
Explosive Detection Kit Market
Security and Surveillance
Europe Security Services Market
Security and Surveillance
Home Security Sensors Market
Security and Surveillance
Riot Control System Market
Security and Surveillance
Global Wireless Monitoring and Surveillance Market