
 Identity and Access Management (IAM) Market | 2026-2036
Identity and Access Management (IAM) Market Size, Share, and Industry Trends Forecast 2026-2036
Identity and Access Management (IAM) Market Analysis
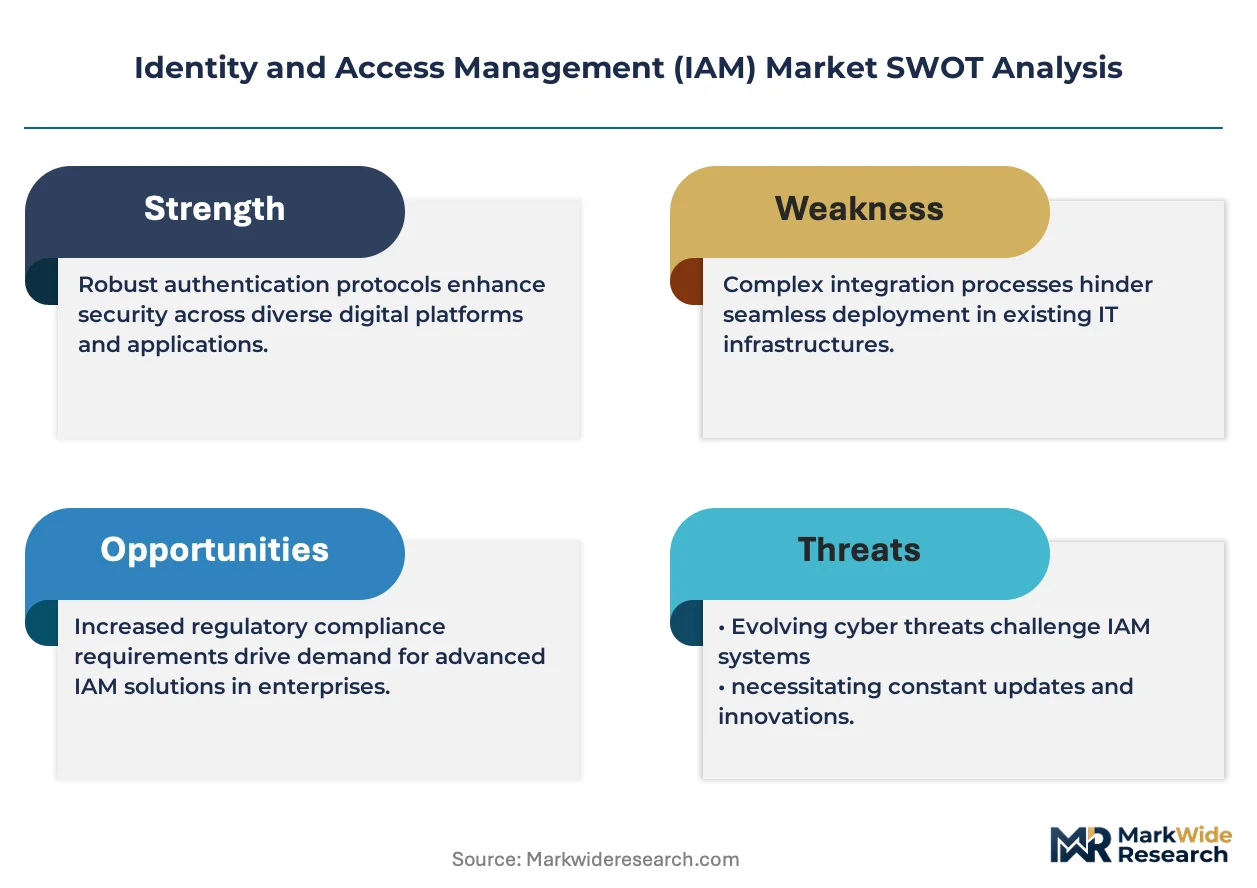
Password-based authentication is shifting toward biometric and behavioral credential frameworks, compressing legacy licensing economics while expanding recurring revenue pools. Microsoft leverages its Entra platform to anchor enterprise identity fabrics across hybrid cloud estates. Okta competes through extensive third-party application integration density. CyberArk specializes in privileged access management, sustaining premium positioning among financial services and critical infrastructure operators.
Identity and access management comprises the policies, technologies, and processes governing digital identity verification, authentication, and authorization across enterprise IT environments. Core functional parameters include session management, credential lifecycle orchestration, and real-time risk scoring based on user behavior analytics. Cloud-based deployment leads structural expansion as organizations retire on-premises directory services, while multi-factor authentication and governance solutions capture concentrated margin pools due to compliance-driven renewal stickiness. Biometric and artificial intelligence technologies are the fastest-growing capability layers, displacing static rule-based access controls with continuous adaptive trust models.
FDA cybersecurity guidance for medical devices, HIPAA identity safeguards, and NIST zero-trust architecture standards collectively shape product requirements and procurement criteria across healthcare and federal sectors. The SEC's incident disclosure rules and state-level privacy statutes in California and New York further fragment compliance obligations, forcing vendors to modularize governance engines. Stakeholders must monitor how quantum-resistant cryptography mandates and decentralized identity standards redefine trust architecture investments before incumbent certificate infrastructures depreciate.
Market Dynamics
Zero-trust architecture mandates from federal agencies are forcing enterprises to retire perimeter-based security models and rebuild identity verification around continuous authentication workflows. This structural pivot compresses legacy firewall spending while expanding demand for real-time risk engines and privileged access governance platforms.
Growth Catalysts
- Federal zero-trust directives:US government agencies must implement identity-centric security per NIST SP 800-207, driving procurement across defense contractors and critical infrastructure operators.
- Medical device cybersecurity:FDA premarket guidance requires authentication safeguards for connected healthcare equipment, expanding IAM deployment in hospital networks and device manufacturers.
- Behavioral biometrics:Continuous authentication using keystroke dynamics and mouse patterns reduces credential theft losses for financial services and e-commerce platforms.
Market Restraints
- Implementation complexity:Multi-cloud identity federation requires specialized engineering talent that concentrates in Silicon Valley and Seattle metropolitan clusters.
- Legacy directory lock-in:Active Directory dependencies in Fortune 500 enterprises create switching costs that delay cloud-native IAM migration timelines.
- Quantum vulnerability:Current PKI certificate infrastructures face obsolescence risk as cryptographically relevant quantum computers advance, forcing premature infrastructure reinvestment.
Strategic Opportunities
- Decentralized identity standards:W3C Verifiable Credentials and DID protocols enable passwordless consumer onboarding for banking and telecommunications sectors.
- EU AI Act compliance:Automated access logging and audit trails for high-risk AI systems create governance software demand across European healthcare and financial institutions.
- Operational technology convergence:IAM vendors can extend platforms to secure industrial control systems in manufacturing and energy infrastructure.
Industry Challenges
- Identity architect scarcity:Enterprises struggle to hire personnel with cross-domain expertise in cloud infrastructure, security engineering, and compliance frameworks.
- Interoperability fragmentation:Proprietary protocols from hyperscale cloud providers complicate unified policy enforcement across hybrid environments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Identity and Access Management (IAM) Market |
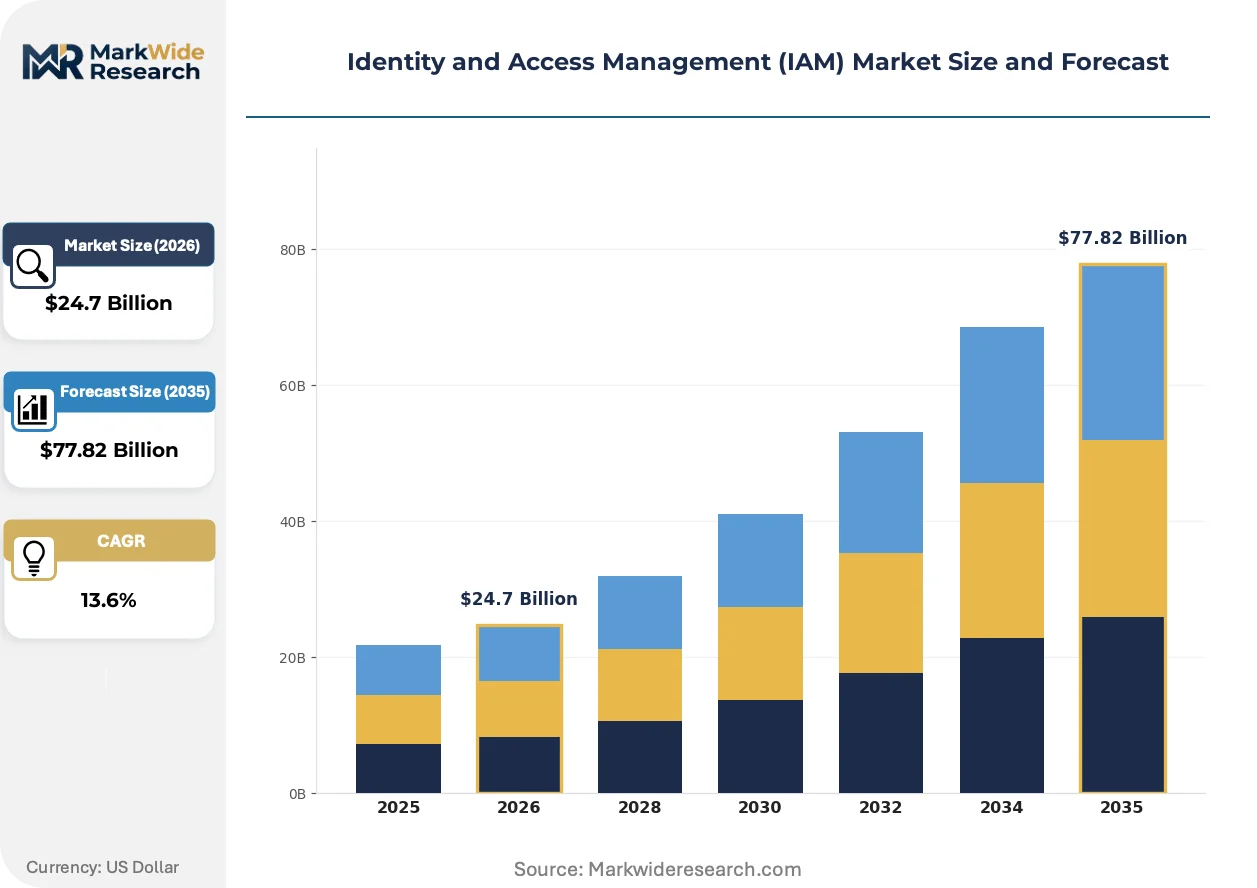
| Market Size in 2026 | $24.7 Billion |
| Market Size in 2035 | $77.82 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Solution: Single Sign-On, Multi-Factor Authentication, Governance, User Provisioning End User: Healthcare, BFSI, Retail, Government Technology: Artificial Intelligence, Biometric, Blockchain, Directory Services |
| Companies Covered | Microsoft, Okta, IBM, Oracle, Ping Identity, CyberArk, SailPoint, Saviynt, Broadcom, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Identity and Access Management (IAM) Market Emerging Trajectories
Artificial intelligence is transforming identity verification from static credential checks into continuous risk assessment, compressing authentication latency while expanding threat detection coverage. Three developments are restructuring competitive positioning and procurement criteria.
Machine learning-based risk scoring is automating real-time access decisions by analyzing device posture, location anomalies, and behavioral biometrics in sub-second intervals. Financial institutions and healthcare networks are deploying these engines to reduce helpdesk password reset volumes. The technology is automating tier-1 security operations center workflows, forcing legacy rule-based vendors to reengineer product architectures or cede mid-market accounts.
The EU AI Act's risk classification framework mandates human oversight for automated identity decisions affecting fundamental rights. Healthcare providers deploying AI-driven patient matching must implement explainable audit trails and appeal mechanisms. German and French hospital networks are prioritizing vendors with built-in governance modules, shifting procurement evaluation criteria toward compliance automation rather than pure authentication speed.
Enterprise buyers are consolidating vendor relationships around integrated identity fabrics rather than point solutions for single functions. Mid-market organizations are replacing fragmented MFA, PAM, and IGA tools with unified platforms delivered through managed security service providers. This consolidation pattern is most pronounced in the United States, where CISOs face board-level pressure to reduce vendor sprawl and streamline incident response coordination.
Identity and Access Management (IAM) Market Segmentation
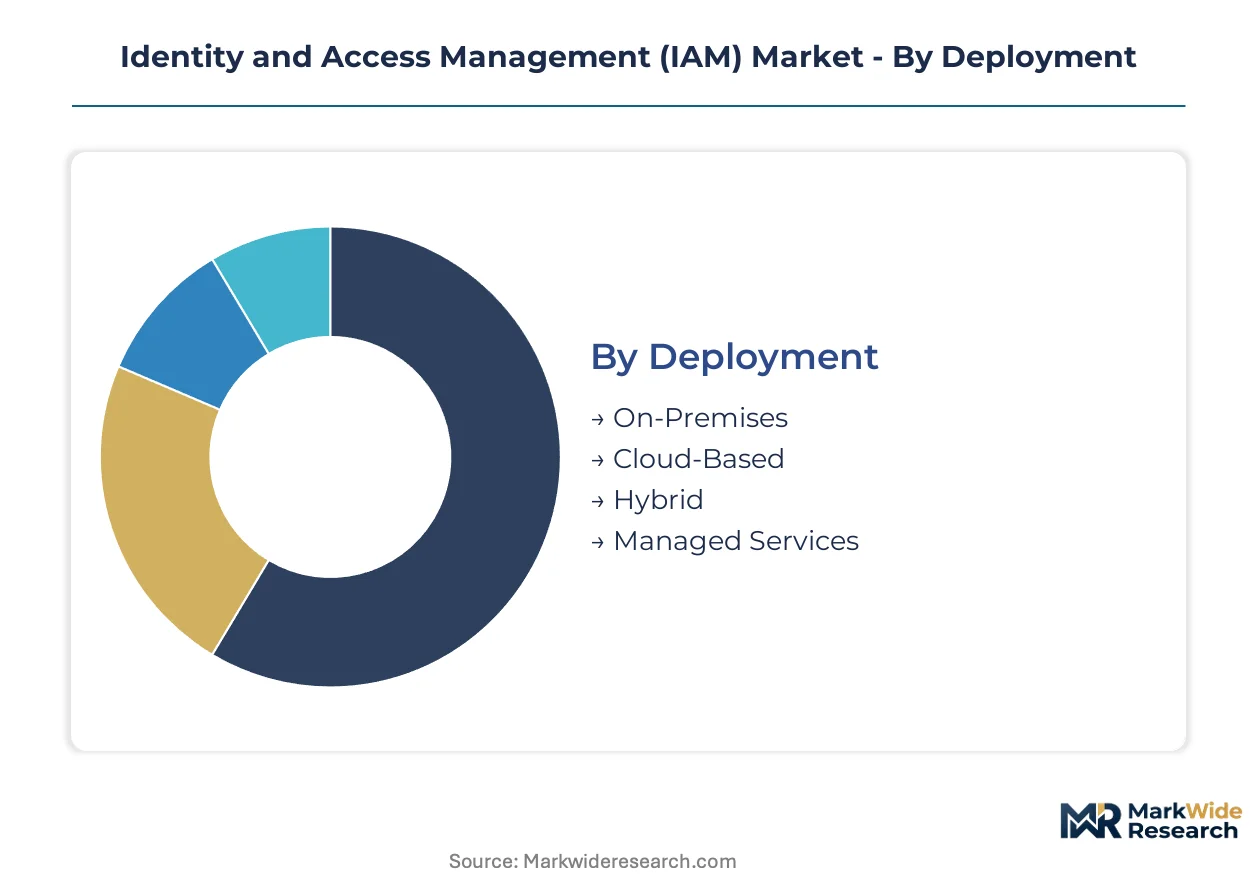
IAM procurement patterns diverge sharply across deployment architectures and compliance regimes. Buyers segment solutions based on where identity data resides, who operates infrastructure, and which regulatory frameworks govern credential lifecycle management.
Deployment:
FedRAMP authorization requirements for cloud-hosted identity platforms create tiered compliance burdens across deployment modes. On-premises installations face NIST SP 800-53 controls, while cloud-native deployments must satisfy continuous monitoring mandates.
- On-Premises:Legacy directory infrastructure operated within enterprise data centers requires hardware maintenance contracts and dedicated security operations staff. Defense contractors and classified government facilities concentrate demand here due to air-gapped network requirements and CMMC Level 3+ certification obligations.
- Cloud-Based:SaaS-delivered identity platforms eliminate capital expenditure on directory hardware while introducing shared responsibility models for encryption key management. Healthcare systems in Texas and California are migrating here to satisfy HIPAA business associate agreement streamlining.
- Hybrid:Split architectures synchronize on-premises Active Directory with cloud identity providers through federation protocols. Manufacturing conglomerates with operational technology islands favor this model for segmented trust boundaries.
- Managed Services:Third-party security operations centers assume full IAM operational responsibility under SLA-governed contracts. Mid-market financial services firms in Illinois and Georgia outsource here to address SEC cybersecurity rule staffing gaps.
Cloud-Based sits at the top of the volume ranking, with Managed Services climbing the fastest.
Solution:
Functional modules carry distinct margin profiles based on renewal stickiness and integration complexity. Governance suites command premium pricing due to audit automation capabilities, while authentication layers compete on throughput metrics.
- Single Sign-On:Session federation technology centralizes application access through token-based authentication protocols. Technology sector enterprises in Washington state and North Carolina prioritize SSO density to reduce SaaS application password fatigue.
- Multi-Factor Authentication:Step-up verification combining possession, knowledge, and inherence factors. Banking networks deploy FIDO2 hardware keys here to satisfy FFIEC authentication guidance and shift liability from transaction fraud.
- Governance:Policy engines automating access certification campaigns and segregation-of-duties enforcement. European pharmaceutical manufacturers select governance modules with built-in EU AI Act explainability features for automated provisioning decisions.
- User Provisioning:Lifecycle automation for account creation, modification, and deactivation across HR system triggers. State government agencies in Virginia and Ohio standardize here to accelerate contractor onboarding during legislative session staffing surges.
Governance captures the highest margin expansion, with Multi-Factor Authentication expanding most quickly.
End User:
Vertical-specific procurement criteria reflect divergent threat models and regulatory exposure. Healthcare and financial services drive premium solution uptake, while retail and government segments prioritize cost containment.
- Healthcare:Patient data protection requirements under HIPAA and FDA cybersecurity guidance shape authentication workflows. Hospital networks in Florida and Massachusetts deploy biometric patient matching to reduce medical record duplication errors.
- BFSI:Anti-money laundering mandates and PSD2 strong customer authentication rules govern transaction security architecture. Investment banks in New York and London concentrate demand for privileged access governance around trading system credentials.
- Retail:Seasonal workforce scaling and franchisee network federation create identity sprawl challenges. E-commerce platforms prioritize passwordless checkout experiences to reduce cart abandonment rates.
- Government:Federal zero-trust architecture directives and state-level privacy statutes fragment procurement standards. Defense agencies mandate hardware-backed credentials, while municipal governments seek simplified cloud-native alternatives.
Healthcare leads absolute spending, with BFSI gaining share fastest.
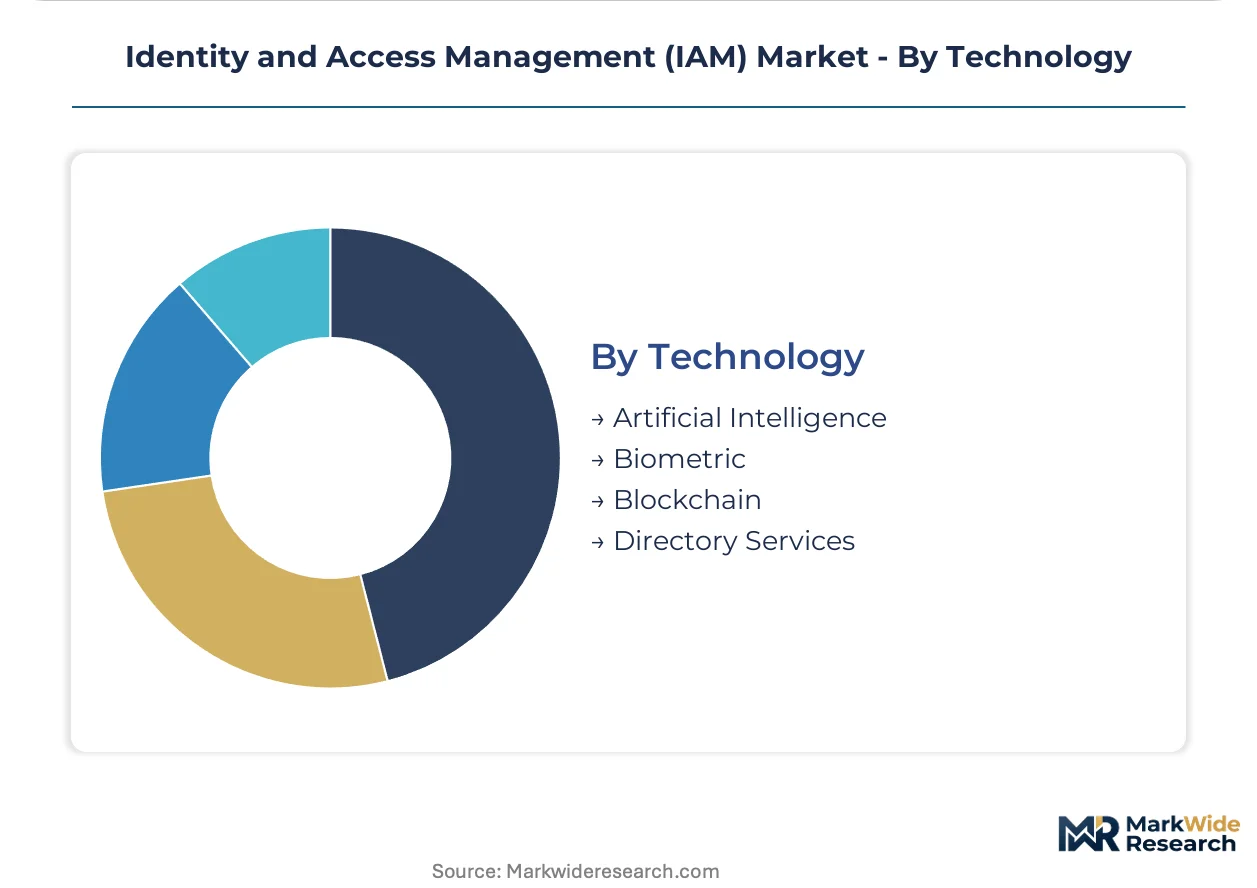
Technology:
Underlying capability layers differentiate vendor architectures and determine roadmap investment priorities. Biometric and AI engines attract venture funding, while directory services consolidation reflects mature market dynamics.
- Artificial Intelligence:Machine learning models scoring access risk from behavioral telemetry and device posture signals. Fraud detection teams at payment processors deploy these engines to identify account takeover attempts in sub-second windows.
- Biometric:Fingerprint, facial recognition, and voiceprint authentication replacing password-based credentials. Smartphone manufacturers integrate these sensors to enable FIDO Alliance passwordless standards adoption.
- Blockchain:Decentralized identity protocols enabling self-sovereign credential verification without centralized authorities. Pilot programs at German automotive suppliers test blockchain for supply chain partner onboarding.
- Directory Services:Hierarchical databases storing user attributes and group membership for authentication queries. Legacy Microsoft Active Directory estates dominate Fortune 500 infrastructure, creating migration friction for cloud-native alternatives.
Directory Services anchors current installed base, with Artificial Intelligence showing steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's cybersecurity cluster anchors global IAM innovation, with venture deployment and federal procurement pipelines concentrated across the San Francisco Bay Area. National regulatory regimes fragment compliance requirements. Cloud migration velocity varies by data sovereignty frameworks and critical infrastructure classification.
United States
Federal zero-trust mandates from NIST SP 800-207 and CMMC certification requirements drive defense contractor procurement. SEC cybersecurity disclosure rules accelerate governance automation among publicly traded enterprises. The Washington DC-Baltimore corridor concentrates demand from intelligence community integrators and healthcare systems serving federal beneficiaries.
Germany
Automotive supply chain digitization and industrial control system security requirements expand privileged access governance deployment. EU AI Act compliance mandates for high-risk automated decision systems reshape healthcare and financial services procurement. Munich and Stuttgart host concentrated engineering talent pools serving Siemens, BMW, and supplier networks.
United Kingdom
Financial services regulatory pressure from the Prudential Regulation Authority and FCA operational resilience rules compress authentication modernization timelines. NHS digital transformation programs mandate identity federation across fragmented hospital trusts. London's fintech density generates continuous authentication demand for payment infrastructure modernization.
Japan
Critical infrastructure protection guidelines from METI and aging workforce demographics accelerate passwordless deployment in manufacturing. 2020 Tokyo Olympics legacy investments in biometric systems established vendor relationships now extending to railway and hospitality sectors. Osaka-Kobe industrial corridor concentrates operational technology IAM deployment for chemical and steel producers.
India
Digitization of financial inclusion programs and RBI's cyber security framework for urban cooperative banks expand multi-factor authentication penetration. State-level data localization requirements in Karnataka and Maharashtra complicate cloud identity provider selection. Bengaluru's SaaS export ecosystem generates IAM engineering talent competing with domestic enterprise demand.
Identity and Access Management (IAM) Market Vendor Landscape
Platform consolidation dominates the current landscape as enterprise buyers reduce vendor sprawl and streamline incident response coordination. The vendor base stratifies across three tiers: hyperscale cloud platforms with bundled identity services, standalone specialists in privileged access or governance, and regional managed security service providers. Strategic archetypes include authentication-centric platforms competing on application integration density, governance-heavy suites commanding audit automation premiums, and emerging passwordless specialists. M&A activity and strategic partnerships represent the dominant competitive moves, with incumbents acquiring behavioral biometrics and decentralized identity startups to fill capability gaps.
Within the hyperscale platform tier, Microsoft and Okta exemplify divergent positioning strategies. Microsoft leverages Entra's native integration with productivity suites to anchor hybrid cloud identity fabrics. Okta competes through extensive third-party application integration density, particularly among technology sector enterprises with fragmented SaaS portfolios. CyberArk occupies a specialist position in privileged access management, sustaining premium pricing among financial services and critical infrastructure operators where credential vaulting carries regulatory weight.
| Leading Market Players |
|---|
| Microsoft |
| Okta |
| IBM |
| Oracle |
| Ping Identity |
| CyberArk |
| SailPoint |
| Saviynt |
| Broadcom |
| Others |
Supply Flow & Price Mechanics
Cloud-native delivery architectures are compressing on-premises infrastructure margins while concentrating procurement leverage among hyperscale platform operators. This shift simultaneously reduces hardware-dependent cost structures and elevates software engineering talent scarcity as the primary supply constraint.
Pricing Analysis
Input-cost pass-through from specialized security engineering labor and FedRAMP certification compliance expenses shapes SaaS-tiered subscription models. Pricing stratifies across premium governance suites, standard authentication platforms, and economy SSO tiers. Cost compression in the economy tier intensifies because managed security service providers bundle commoditized identity functions. Mid-market healthcare systems exhibit highest price sensitivity, while defense contractors accepting CMMC-mandated solutions show lowest.
Supply Chain Analysis
Biometric sensor hardware rests on Taiwanese semiconductor foundries and South Korean image sensor producers, with algorithm development concentrated in United States and Israeli engineering clusters. Cloud compute infrastructure draws from hyperscale data center networks across Virginia, Oregon, and Frankfurt. Single-source vulnerability in FIDO2 hardware key manufacturing creates procurement risk. Distribution runs through direct enterprise sales teams and managed security service provider channel partnerships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Identity and Access Management market functions as a stable compounder, with compliance mandate renewal cycles generating predictable revenue visibility regardless of macroeconomic volatility.
For Market Incumbents: Anchor platform consolidation strategies around zero-trust architecture integration to defend against point-solution disaggregation. Deepen backward integration into behavioral biometrics R&D to reduce dependency on acquisition-driven capability gaps. Prioritize FedRAMP High authorization investment to capture defense contractor procurement pipelines. For New Entrants and Emerging Players: Launch via managed security service provider white-label partnerships to bypass direct enterprise sales cost structures. Target operational technology identity convergence in manufacturing verticals as the most penetrable white space. Emphasize EU AI Act explainability modules as differentiated go-to-market positioning. For Investors and Strategic Acquirers: Valuations sit cheapest among regional managed security service providers lacking cloud-native platform scale. Long-term viability centers on recurring revenue base stability and compliance-driven switching costs. Watch quantum-resistant cryptography standardization timelines as inflection signal for infrastructure reinvestment cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies MFA, PAM, and governance modules to reduce vendor sprawl for CISOs. |
| Acquisition of Specialist Firm | Fills behavioral biometrics or decentralized identity capability gaps rapidly. |
| FedRAMP Authorization | Unlocks federal agency and defense contractor procurement eligibility. |
| Strategic Partnership | Extends reach into operational technology environments via industrial automation vendors. |
| Geographic Expansion | Establishes EU data residency to satisfy GDPR and EU AI Act localization requirements. |
Methodological Framework
Multiple input streams — CISO interviews, IAM vendor product roadmap disclosures, and federal procurement database analysis — were reconciled against secondary validation from NIST guidance documents, SEC cybersecurity disclosure filings, and healthcare system RFP archives. Primary fieldwork engaged identity architects, cloud security engineers, and compliance officers at healthcare networks, financial institutions, and defense contractors. Bottom-up deployment estimates and top-down compliance mandate penetration models were cross-referenced for triangulation.
Historical adoption curves were cross-referenced against expert panel input regarding zero-trust implementation timelines. The analytical framework segmented by deployment architecture, solution function, end-user vertical, and underlying technology capability across the projection horizon. CAGRs were derived from compliance-driven renewal elasticity and cloud migration velocity assumptions. Forecast inputs incorporated FedRAMP authorization pipeline data and EU AI Act implementation schedules.
Forecast precision tightens around the base case; tail outcomes carry wider variance under quantum computing breakthrough timelines or decentralized identity standardization acceleration. Forecasts reflect documented assumptions regarding federal procurement continuity and cloud provider market concentration. A small set of triggers — NIST post-quantum cryptography mandate timing, EU AI Act enforcement severity, and hyperscaler platform bundling intensity — warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Digital Risk Protection Software Market
Security Software
Next-Generation Intrusion Prevention System (NGIPS) Market
Security Software
Europe IP Video Intercom Device and Equipment Market
Security Software
Global Secure Access Service Edge Market
Security Software
Device Vulnerability Management Market
Security Software
Cloud Security Software Market
Security Software
Global Security Orchestration Automation and Response (SOAR) Market
Security Software
Global Digital Vehicle Forensics Market
Security Software
Europe Video Management System Market
Security Software
Information Rights Management Market
Security Software
Global Optical Encryption Market
Security Software
US and Latin America Identity and Access Management (IAM) Market
Security Software
Global Log Management Market
Security Software
Encryption Software Market
Security Software
Cloud Intrusion Protection Software Market
Security Software
Passwordless Authentication Market