
 Global User Activity Monitoring Market | 2026-2036
Global User Activity Monitoring Market Size, Share, and Industry Trends Forecast 2026-2036
Global User Activity Monitoring Market Foresight
Subscription-based financing and asset-light SaaS delivery is rewriting capital requirements for user activity monitoring vendors, enabling mid-tier challengers to scale without heavy infrastructure commitments. CyberArk Software Ltd. leverages privileged access integration to anchor enterprise-grade deployments across financial and government verticals. Splunk Inc. competes through behavior analytics specialization that extends platform utility beyond security into operational intelligence. Teramind Inc. differentiates via real-time screen capture and automated policy enforcement that occupies niche compliance-intensive segments.
User activity monitoring encompasses software systems that record, analyze, and alert on digital behaviors across endpoints, networks, and cloud applications through keystroke logging, application tracking, and session replay functionalities. These systems serve primary commercial purposes of insider threat mitigation, forensic investigation support, and workforce productivity measurement. Cloud-based deployment is accelerating fastest as organizations abandon capital-intensive on-premise infrastructure, while behavior analytics solutions command premium positioning due to AI-driven anomaly detection capabilities. Compliance management applications sustain steady demand from regulated industries confronting escalating audit frequency and penalty severity.
The U.S. SEC cybersecurity disclosure rules, EU GDPR Article 32 technical measures, and HIPAA Security Rule audit controls collectively mandate demonstrable workforce oversight that directly shapes procurement specifications for monitoring platforms. ISO 27001 certification requirements further tighten vendor qualification thresholds across multinational enterprise RFP processes. Stakeholders must weigh integration complexity against the operational risk of fragmented point solutions as vendor consolidation pressures intensify.
Market Dynamics
Zero-trust architecture mandates from the US federal government are compressing procurement cycles and forcing vendors to demonstrate continuous verification capabilities that integrate identity, endpoint, and network telemetry into unified monitoring fabrics.
Growth Catalysts
- EU AI Act compliance deadlines:Article 52 transparency obligations for high-risk AI systems are compelling financial institutions to deploy auditable workforce oversight tools with automated logging and explainable anomaly detection.
- Behavioral biometrics convergence:Keystroke dynamics and mouse-movement pattern recognition are hardening insider threat detection beyond static rule-based alerting into adaptive risk scoring engines.
- India's digital banking expansion:RBI cybersecurity guidelines for scheduled commercial banks are accelerating cloud-native monitoring deployments across Mumbai, Bangalore, and Hyderabad financial hubs.
Market Restraints
- Data residency fragmentation:China's PIPL cross-border transfer restrictions and Russia's data localization laws are forcing vendors to maintain redundant infrastructure across incompatible sovereignty zones.
- Specialized talent scarcity:Shortage of professionals holding CISSP-SABSA dual certifications capable of bridging security architecture with privacy engineering is inflating implementation costs.
- Privacy-preserving alternatives:Differential privacy techniques and federated learning approaches are emerging as functional substitutes that reduce centralized monitoring dependency.
Strategic Opportunities
- Brazilian financial modernization:PIX instant payment system adoption and BCBS 239-aligned data governance requirements at Banco Central do Brasil are creating greenfield demand for real-time transaction monitoring overlays.
- Extended detection and response integration:Convergence of user activity monitoring with XDR platforms is opening unified security operations workflows that compress vendor consolidation cycles.
- ISO 27701 certification differentiation:Privacy information management system accreditation is becoming a decisive RFP criterion for European enterprise procurement committees evaluating vendor shortlists.
Industry Challenges
- Legacy SIEM migration complexity:Enterprises running Splunk Enterprise Security or IBM QRadar deployments face 18-24 month integration timelines for modern UAM telemetry ingestion without disrupting existing correlation rules.
- Algorithmic bias audit requirements:Automated behavior scoring systems must demonstrate fairness across demographic cohorts under emerging NYC Local Law 144 and EU AI Act conformity assessment protocols.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global User Activity Monitoring Market |
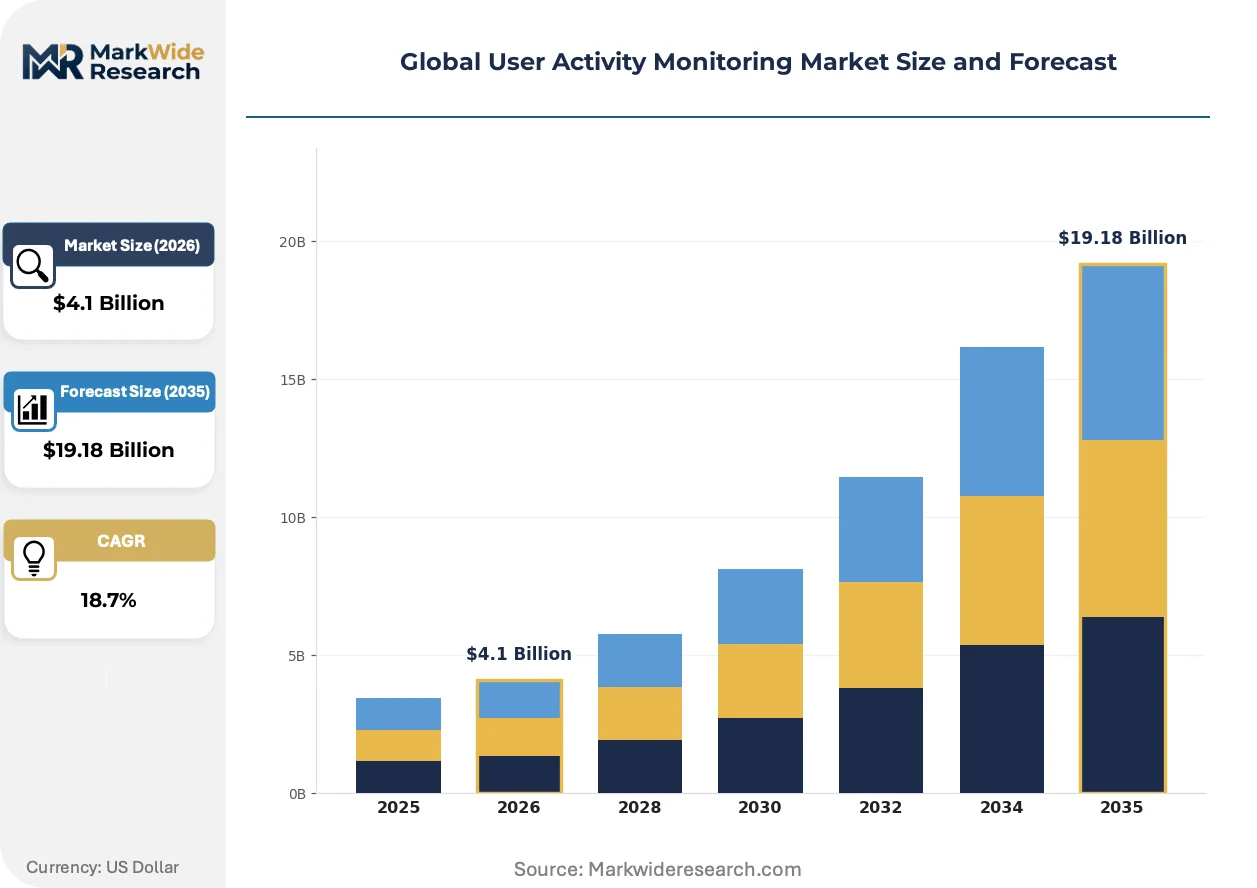
| Market Size in 2026 | $4.1 Billion |
| Market Size in 2035 | $19.18 Billion |
| CAGR (2026 – 2036) | 18.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premise, Cloud-Based, Hybrid, Virtualized Solution: Real-Time Monitoring, Behavior Analytics, Risk Management, Insider Threat Detection, Compliance Management Application: Financial Services, Government Agencies, Education Sector, Telecommunication, Legal Services End User: Enterprises, Managed Security Service Providers, Small & Medium Businesses, Non-Profit Organizations |
| Companies Covered | Micro Focus International PLC, Splunk Inc., Imperva Inc., CyberArk Software Ltd., Forcepoint LLC, Teramind Inc., ActivTrak Inc., IBM Corporation, Microsoft Corporation, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global User Activity Monitoring Market Shifts & Advancements
Artificial intelligence is compressing detection latency from hours to seconds while fragmenting vendor architectures between monolithic platforms and specialized point solutions. This technological inflection is redrawing competitive boundaries and procurement evaluation criteria across enterprise security stacks.
Session recording and screen capture technology is hybridizing with natural language processing to enable semantic search across visual workflows, not just metadata tagging. Healthcare providers and pharmaceutical manufacturers are piloting these capabilities for FDA 21 CFR Part 11 compliance documentation. The structural result is collapsing the distinction between security monitoring and quality management systems into single audit-ready repositories.
EU GDPR Article 32 technical and organizational measures enforcement is intensifying through supervisory authority fines exceeding operational budgets. German DPA rulings on employee monitoring proportionality are narrowing lawful use cases to documented security incidents rather than productivity measurement. Financial services firms in Frankfurt and Paris are responding by segmenting monitoring deployments across jurisdiction-specific data processing agreements.
Buyer committees are consolidating vendor relationships from an average of seven point solutions toward three integrated platforms with API-extensible architectures. Managed security service providers are capturing this consolidation value by offering UAM-as-a-service with guaranteed SLA-backed detection metrics. This pattern is most pronounced in United Kingdom financial services, where Prudential Regulation Authority operational resilience directives mandate demonstrable third-party risk management.
Global User Activity Monitoring Market Segmentation
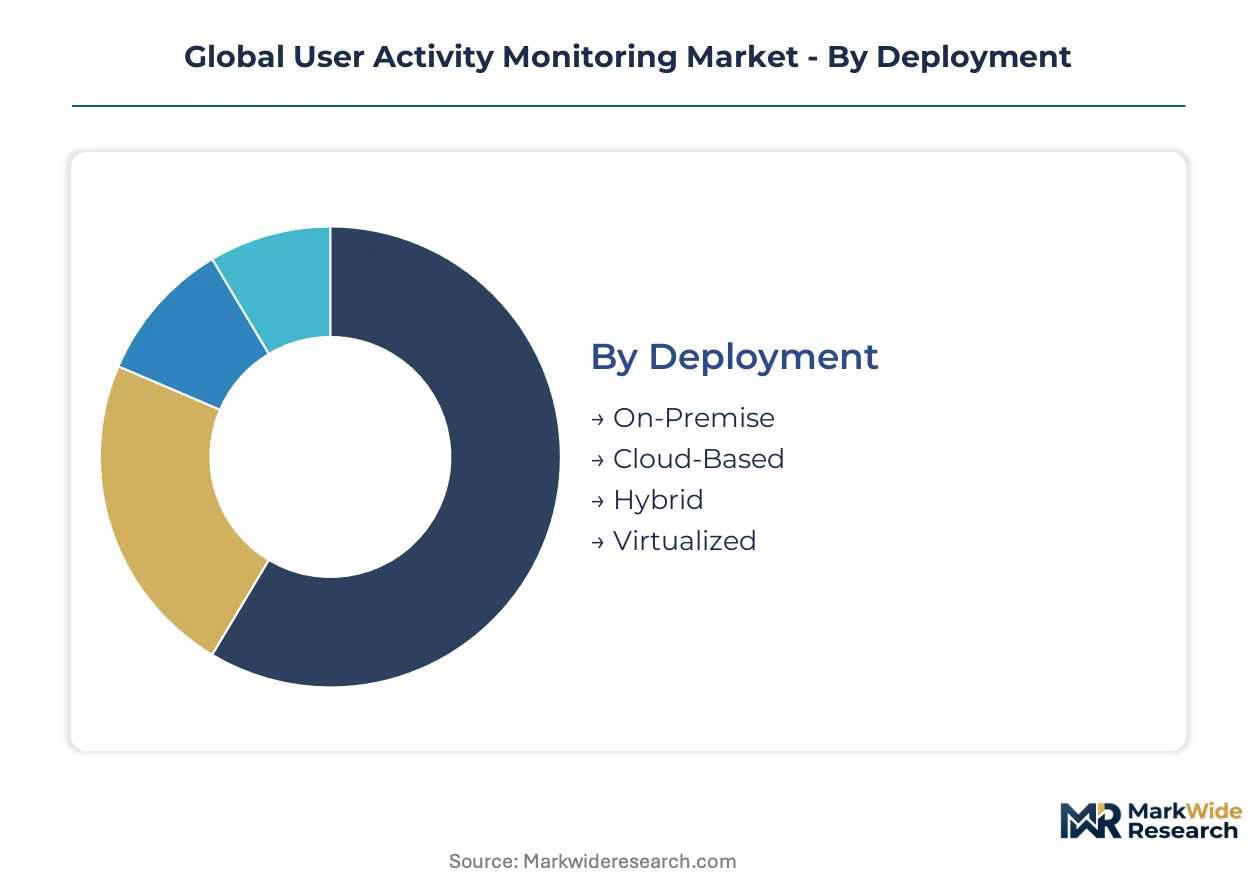
Deployment architecture and solution specialization determine integration complexity, recurring revenue potential, and customer lifetime value for user activity monitoring vendors. Segmentation reveals where capital requirements concentrate and which buyer profiles command premium pricing.
Deployment:
After-sales service intensity varies sharply by deployment mode, with cloud-native platforms requiring continuous feature delivery and on-premise installations demanding sustained engineering support for patch management and hardware refresh cycles.
- On-Premise:Organizations in defense contracting and classified government facilities mandate air-gapped infrastructure with dedicated appliance stacks. Demand concentrates in Virginia, Maryland, and Texas federal corridors where FedRAMP authorization remains elusive for cloud alternatives.
- Cloud-Based:Multi-tenant SaaS architectures with API-first telemetry ingestion are displacing capital-intensive alternatives. Financial services firms in London, Singapore, and New York are standardizing on cloud-native deployments to satisfy SEC cybersecurity disclosure timelines without infrastructure procurement delays.
- Hybrid:Split architectures preserve sensitive data on-premise while routing analytics to cloud processing layers. Healthcare systems deploying Epic and Cerner environments favor this model for HIPAA Security Rule audit trail segmentation.
- Virtualized:Containerized monitoring agents deployed via Kubernetes orchestration support ephemeral workforce scenarios. Technology sector adoption is climbing fastest for contractor-heavy development environments.
By volume, Cloud-Based leads. By growth pace, Virtualized is ahead.
Solution:
Solution specialization maps directly to buyer procurement authority, with compliance management tools selling to legal and audit functions while behavior analytics platforms require CISO sponsorship and security operations integration.
- Real-Time Monitoring:Continuous session capture and keystroke logging with sub-second alerting thresholds. Contact centers in Philippines and India deploy these capabilities for PCI-DSS 4.0 requirement 10.2 compliance around privileged user actions.
- Behavior Analytics:AI-driven anomaly detection establishing baseline user patterns and flagging deviation through unsupervised machine learning. Banking regulators in Brazil and Mexico are mandating these capabilities for insider threat programs under BCBS 239 data aggregation principles.
- Risk Management:Quantified scoring frameworks translating user actions into operational risk metrics. Insurance underwriters in Lloyd's of London market are requiring these outputs for cyber policy renewals.
- Insider Threat Detection:Purpose-built correlation engines identifying data exfiltration precursors through file access pattern analysis. Critical infrastructure operators in Germany and France prioritize this capability under NIS2 directive security requirements.
- Compliance Management:Pre-configured policy templates aligned to GDPR Article 32, HIPAA Security Rule, and SOX Section 404 audit controls. Pharmaceutical manufacturers in Switzerland and Denmark standardize on these solutions for FDA 21 CFR Part 11 electronic record integrity.
Compliance Management captures the largest installed base. Behavior Analytics is expanding most quickly.
Application:
Application verticals determine regulatory exposure and therefore solution configuration complexity, with financial services and government segments requiring jurisdiction-specific data residency and sovereign cloud integration.
- Financial Services:Trading floor surveillance, SWIFT messaging monitoring, and algorithmic trading behavior audit trails. Singapore, Hong Kong, and UAE financial hubs are mandating these deployments under Monetary Authority of Singapore TRM-G 17 and Dubai Financial Services Authority cybersecurity rules.
- Government Agencies:Classified network segmentation monitoring with mandatory two-person integrity controls. Federal deployments in Australia, Canada, and United Kingdom follow Five Eyes intelligence-sharing protocols for insider threat information exchange.
- Education Sector:Student data privacy-compliant oversight for research computing environments and administrative systems. University systems in California, Massachusetts, and Ontario are piloting these capabilities for FERPA and PIPEDA alignment.
- Telecommunication:Lawful intercept preparation and network operations center workforce oversight. Operators in South Korea and Japan deploy these under Telecommunications Business Act security obligations.
- Legal Services:Client matter isolation and privilege-preserving activity logging for document management systems. Magic Circle firms in London and white-shoe practices in New York are standardizing deployments for Solicitors Regulation Authority and ABA Model Rule compliance.
Financial Services dominates revenue contribution. Legal Services is gaining share fastest.
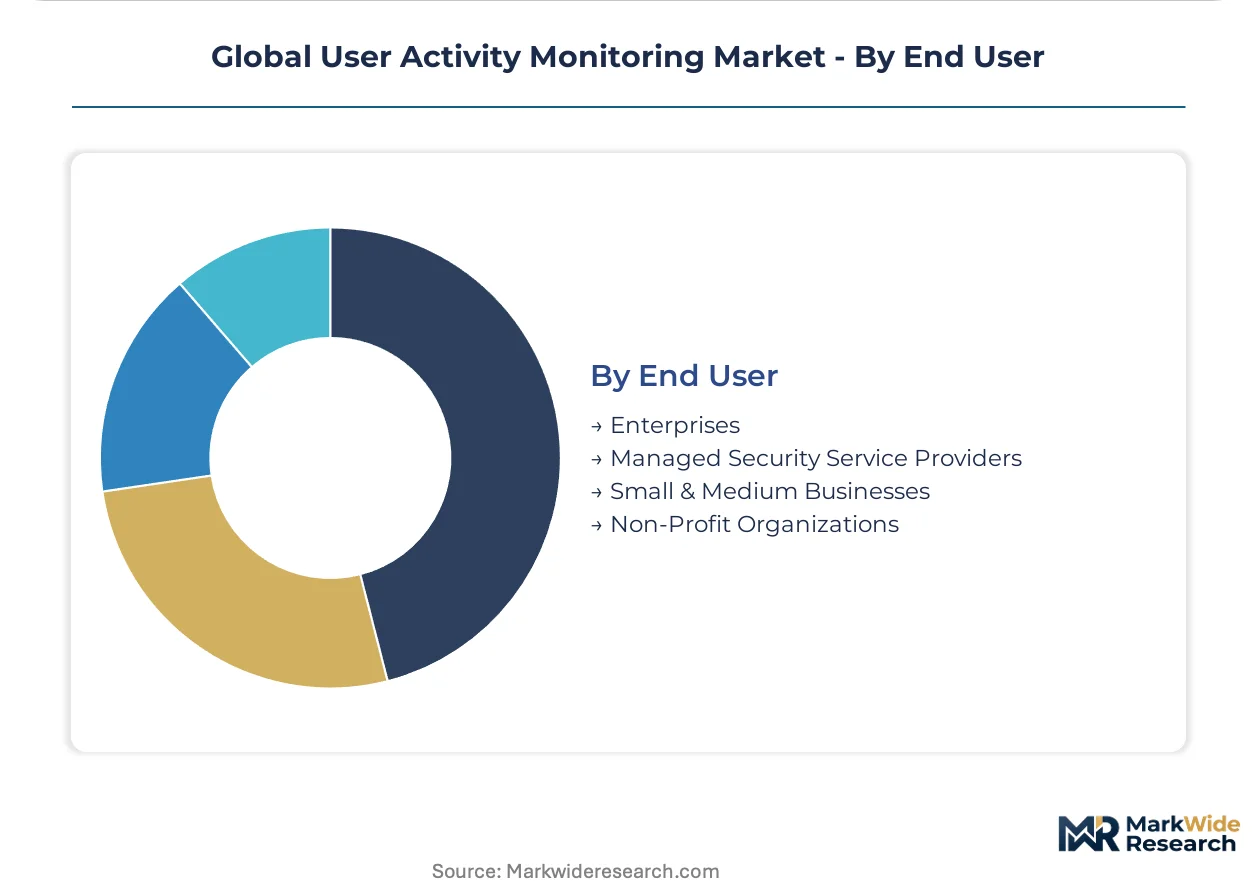
End User:
End user scale determines pricing model elasticity and sales cycle duration, with enterprise accounts demanding custom professional services while managed security service providers seek white-label platform economics.
- Enterprises:Global 2000 organizations with dedicated security operations centers and 24/7 monitoring requirements. Manufacturing conglomerates in Germany, automotive OEMs in Japan, and energy majors in Norway are consolidating vendor relationships under three-year enterprise agreements.
- Managed Security Service Providers:Multi-tenant platform operators delivering UAM-as-a-service with SLA-backed detection metrics. British and Irish MSSPs are capturing consolidation value from UK financial services firms facing Prudential Regulation Authority operational resilience directives.
- Small & Medium Businesses:Subscription-based simplified deployments with pre-configured policy templates. Professional services firms in Australia and accounting networks in Netherlands are adopting these for baseline GDPR and tax authority audit preparedness.
- Non-Profit Organizations:Grant-funded security improvements for humanitarian and development organizations. International NGOs operating in Brussels, Geneva, and Washington DC are deploying these capabilities for donor cybersecurity due diligence requirements.
Enterprises account for the majority of current spending. Managed Security Service Providers are climbing the fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Zero-trust architecture mandates from the US federal government are compressing procurement cycles and forcing vendors to demonstrate continuous verification capabilities that integrate identity, endpoint, and network telemetry into unified monitoring fabrics.
United States
Financial services firms in New York and Chicago are accelerating insider threat detection deployments to satisfy SEC cybersecurity disclosure rules and zero-trust architecture directives. HIPAA Security Rule audit controls mandate demonstrable workforce oversight across healthcare systems in Boston and the Research Triangle. Cloud-native monitoring adoption concentrates in Silicon Valley technology corridors where contractor-heavy development environments require ephemeral workforce oversight.
Germany
Critical infrastructure operators in Frankfurt and Munich prioritize insider threat detection capabilities under NIS2 directive security requirements. German DPA rulings on employee monitoring proportionality are narrowing lawful use cases to documented security incidents rather than productivity measurement. Manufacturing conglomerates in Baden-Württemberg and Bavaria are consolidating vendor relationships under three-year enterprise agreements with ISO 27001 certification requirements.
United Kingdom
Prudential Regulation Authority operational resilience directives mandate demonstrable third-party risk management across London financial services. Managed security service providers in British and Irish markets are capturing consolidation value by offering UAM-as-a-service with SLA-backed detection metrics. Magic Circle law firms in London are standardizing deployments for Solicitors Regulation Authority compliance with client matter isolation requirements.
Singapore
Monetary Authority of Singapore TRM-G 17 guidelines mandate trading floor surveillance and SWIFT messaging monitoring across financial hubs. Cloud-native deployments satisfy cybersecurity disclosure timelines without infrastructure procurement delays for banks in the Marina Bay district. Technology sector adoption climbs fastest for contractor-heavy development environments in one-north and Changi business parks.
Brazil
Banco Central do Brasil BCBS 239-aligned data governance requirements are creating greenfield demand for real-time transaction monitoring overlays. PIX instant payment system adoption accelerates cloud-native monitoring deployments across São Paulo and Rio de Janeiro financial hubs. Banking regulators mandate behavior analytics capabilities for insider threat programs under data aggregation principles.
Global User Activity Monitoring Market Competitive Landscape
Channel-controlling players compete with product-specialist players across deployment architectures and solution specializations. The vendor base organizes around three strategic archetypes: privileged access integration specialists, behavior analytics platforms, and real-time compliance enforcement providers. Consolidation pressures intensify as buyer committees reduce vendor relationships from seven point solutions toward three integrated platforms. M&A activity and API-extensible architecture development represent the dominant competitive moves reshaping market structure.
Within the privileged access integration tier, CyberArk Software Ltd. anchors enterprise-grade deployments across financial and government verticals. Splunk Inc. occupies a position among behavior analytics specialists extending platform utility beyond security into operational intelligence. Teramind Inc. exemplifies the real-time compliance enforcement archetype through automated policy enforcement capabilities. These three companies represent distinct strategic positioning vectors that vendors must navigate as zero-trust mandates and AI-driven anomaly detection reshape procurement evaluation criteria.
| Leading Market Players |
|---|
| Micro Focus International PLC |
| Splunk Inc. |
| Imperva Inc. |
| CyberArk Software Ltd. |
| Forcepoint LLC |
| Teramind Inc. |
| ActivTrak Inc. |
| IBM Corporation |
| Microsoft Corporation |
| Others |
Supply & Pricing Matrix
Transatlantic fiber routes connecting Frankfurt to Northern Virginia data centers transmit the bulk of UAM telemetry ingestion workloads, with bandwidth cost fluctuations directly compressing SaaS margins for cloud-native vendors while amplifying price spreads between ISO 27001-certified premium tiers and uncertified alternatives. This logistics-cost transmission mechanism concentrates pricing power among vendors with redundant peering agreements across Singapore and London financial hubs.
Pricing Analysis
Certification level creates the primary spread, with ISO 27701-accredited privacy management tiers commanding substantial premiums over baseline SOC 2 offerings in European enterprise RFPs. Three-tier pricing structure across premium, standard, and economy levels segments by deployment complexity, with FedRAMP-authorized packages anchoring the top tier for US federal contractors. Price erosion runs through the mid-market SaaS tier as venture-backed challengers absorb customer acquisition costs to displace legacy on-premise incumbents. Managed security service providers exhibit lowest price sensitivity due to white-label economics, while independent software vendors in the SMB segment face acute procurement pressure from pre-configured template commoditization.
Supply Chain Analysis
Extended payment terms from hyperscale cloud infrastructure providers anchor working capital structures for SaaS-native UAM vendors, with supply-chain finance facilities bridging 60-90 day receivables cycles. Component concentration centers on Ireland and Netherlands for EU data residency compliance, with Singapore and Japan serving Asia-Pacific financial services deployments. Raw material dependencies include GPU clusters for behavioral analytics inference, encrypted storage arrays for session replay retention, and API gateway bandwidth for real-time telemetry ingestion. Single-source vulnerability concentrates in NVIDIA H100 allocations for AI-driven anomaly detection workloads. Distribution runs through direct enterprise sales teams for Global 2000 accounts, with channel partners capturing mid-market volume across professional services and healthcare verticals.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform economics inflect as buyer committees consolidate from seven point solutions toward three integrated architectures, with API-extensible interoperability becoming the decisive procurement criterion across London, Singapore, and New York financial hubs.
For Market Incumbents: Insulate enterprise relationships by embedding UAM telemetry into broader zero-trust fabric deployments, leveraging existing privileged access integration to resist displacement by behavior-analytics specialists. Prioritize ISO 27701 certification investment to defend margin position against emerging privacy-engineering challengers. Channel control through managed security service provider white-label agreements preserves recurring revenue as direct sales cycles lengthen. For New Entrants and Emerging Players: Establish a beachhead in Brazilian financial modernization, where Banco Central do Brasil BCBS 239 mandates create greenfield demand without entrenched incumbent saturation. Target PIX instant payment system monitoring overlays as the most penetrable use case, with cloud-native deployment positioning against legacy on-premise architectures. Go-to-market through regional system integrators familiar with local data residency requirements accelerates traction. For Investors and Strategic Acquirers: EU AI Act Article 52 conformity deadlines reshape the acquisition landscape, elevating vendors with auditable explainability frameworks above black-box behavioral scoring engines. Long-term viability hinges on differentiation durability as AI compression commoditizes detection latency. Acquisition target archetype: specialized compliance enforcement providers with pre-configured GDPR Article 32 templates. Signal to watch: NHS procurement committee vendor consolidation announcements as operational resilience directives tighten.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Embedding UAM telemetry into XDR fabrics satisfies SEC cybersecurity disclosure consolidation mandates. |
| Acquisition of Specialist Firm | Behavioral biometrics capabilities harden insider threat detection beyond rule-based alerting engines. |
| Geographic Expansion | Local PIX overlay development captures Brazilian real-time transaction monitoring greenfield demand. |
| Strategic Partnership | Hyperscaler marketplace listings compress procurement cycles for cloud-native financial services deployments. |
| Product Launch | Semantic search across visual workflows collapses security and quality management system distinctions. |
Research Methodology
Cross-validation between CISO interview transcripts and SEC cybersecurity disclosure filings anchors the qualitative findings, with secondary validation against vendor RFP response patterns. Primary interviews engaged security operations directors, privacy engineering leads, MSSP platform architects, and compliance audit managers across financial services, healthcare, and critical infrastructure verticals. Secondary sources encompassed vendor 10-K risk disclosures, EU AI Act implementation guidance, GDPR supervisory authority enforcement registers, and cloud infrastructure capex disclosures. Bottom-up deployment volume estimates triangulated against top-down enterprise IT security budget allocations.
Calibration against historical adoption curves for SIEM and privileged access management platforms informed the analytical framework across the projection horizon. Segmentation dimensions modeled encompassed deployment architecture, solution specialization, application vertical, and end-user scale, with regional regulatory cluster differentiation for GDPR, HIPAA, and NIS2 compliance pathways. CAGRs derived from logistic diffusion curves adjusted for zero-trust mandate acceleration effects. Industry-specific forecast inputs included FedRAMP authorization timelines and Banco Central do Brasil PIX transaction volume trajectories.
Stress conditions across cloud infrastructure cost inflation, AI compute availability constraints, and cross-border data transfer restriction severity were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions regarding regulatory enforcement continuity and enterprise consolidation appetite. Macroeconomic contraction, sovereign data localization expansion, or breakthrough privacy-preserving alternative maturation would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Mobile Antivirus Software Market
Security Software
Global Enterprise Key Management Market
Security Software
Asia Pacific Video Management System Market
Security Software
Saudi Arabia Managed Security Services Market
Security Software
Security Software for Consumers Market
Security Software
Global Software-Defined Security Market
Security Software
Confidential Computing Market
Security Software
Global Anti-Spam Software Market
Security Software
Cloud Security Software Market
Security Software
Business Email Compromise (BEC) Market
Security Software
Embedded Security Market
Security Software
Facial Recognition Market
Security Software
Privileged Identity Management Market
Security Software
Privacy Management Software Market
Security Software
Data Leakage Prevention Product Market
Security Software
Asia-Pacific Fraud Detection & Prevention Market