
 Data Leakage Prevention Product Market | 2026-2036
Data Leakage Prevention Product Market Size, Share, and Industry Trends Forecast 2026-2036
Data Leakage Prevention Product Market Analysis
The migration from signature-based detection to behavioral analytics is tilting how Data Leakage Prevention products process and classify sensitive information. Microsoft leverages its cloud infrastructure to embed DLP natively across productivity suites. CrowdStrike anchors its offering in endpoint telemetry, competing on real-time threat correlation rather than policy enforcement alone.
Data Leakage Prevention products combine content inspection engines, contextual analysis, and policy enforcement mechanisms to block unauthorized exfiltration of structured and unstructured data across endpoints, networks, and cloud repositories. Endpoint DLP dominates current deployments due to the proliferation of remote work devices accessing corporate resources outside traditional network perimeters. Cloud DLP represents the fastest-expanding segment as organizations migrate storage to distributed architectures. The compliance standard dimension stratifies procurement, with GDPR and HIPAA driving the most rigorous technical requirements.
The EU AI Act, GDPR, and HIPAA collectively shape product roadmaps by mandating automated data classification, audit logging, and cross-border transfer controls. Enforcement actions by national data protection authorities in Germany, France, and Italy have elevated DLP from discretionary security spend to compliance infrastructure. Stakeholders must weigh whether to consolidate around platform-native tools or retain standalone specialists as regulatory scope broadens beyond traditional PII to encompass AI training data and model outputs.
Market Dynamics
The migration from perimeter-based security to zero-trust architectures is fragmenting how organizations deploy Data Leakage Prevention controls across distributed endpoints and cloud repositories. This architectural shift elevates behavioral analytics over static policy enforcement.
Growth Catalysts
- EU AI Act:Automated data classification mandates for AI training datasets are expanding DLP scope beyond traditional PII to model inputs and outputs across member states.
- Healthcare endpoint proliferation:HIPAA-covered entities are deploying agent-based monitoring on clinical workstations and telehealth devices to satisfy breach notification timelines.
- Remote work persistence:Distributed workforces accessing corporate resources from unmanaged devices outside traditional network perimeters are accelerating endpoint DLP procurement cycles.
Market Restraints
- Cloud-native platform bundling:Microsoft and Google embed baseline DLP within productivity suites at marginal cost, compressing standalone vendor pricing power.
- Technical debt in legacy environments:On-premises data repositories with custom schema require expensive content inspection engine reconfiguration before policy enforcement.
- Cross-border transfer friction:GDPR Article 44 restrictions on data flows to third countries complicate cloud DLP deployment architectures for multinational organizations.
Strategic Opportunities
- AI training data governance:The EU AI Act's documentation requirements for high-risk systems create new demand for automated lineage tracking and exfiltration prevention.
- Small and medium enterprise underpenetration:Mid-market organizations in France and Italy lack dedicated security operations centers, creating managed DLP service openings.
- API-first integration:Security orchestration platforms are consuming DLP functions as embedded modules rather than standalone appliances, favoring vendors with robust REST interfaces.
Industry Challenges
- False positive fatigue:Overly aggressive content inspection policies generate alert volumes that overwhelm security analyst teams, eroding trust in automated enforcement.
- Shadow SaaS visibility gaps:Unsanctioned cloud application usage bypasses traditional network monitoring, requiring agent deployment on endpoints where user resistance is highest.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Data Leakage Prevention Product Market |
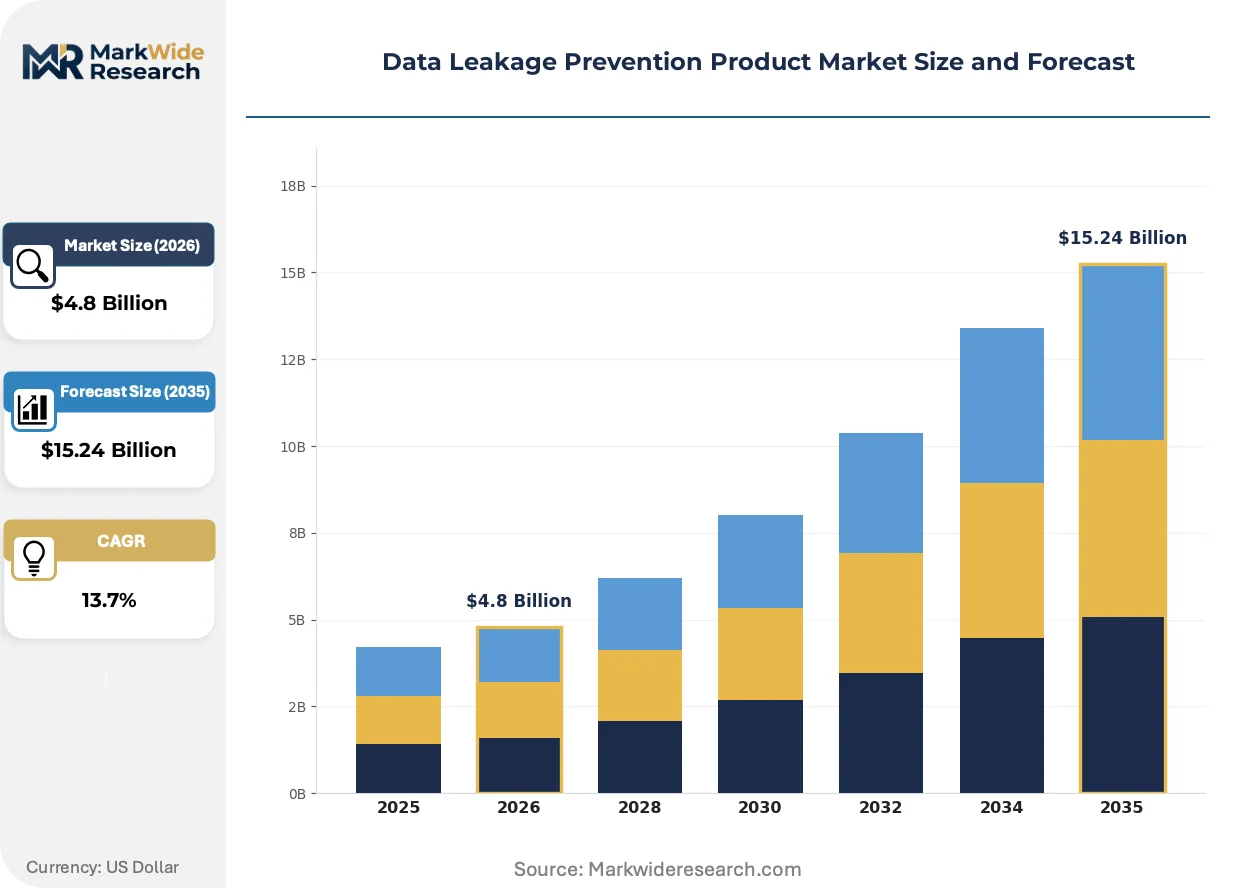
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $15.24 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint DLP, Network DLP, Storage DLP, Cloud DLP Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: SMEs, Large Enterprises, Government, Healthcare Compliance Standard: GDPR, HIPAA, PCI DSS, CCPA |
| Companies Covered | Proofpoint, Broadcom, Microsoft, Forcepoint, Trend Micro, CrowdStrike, IBM, McAfee, Cyberhaven, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Data Leakage Prevention Product Market Emerging Trajectories
Behavioral analytics is displacing signature-based detection as the primary classification mechanism, while regulatory scope expansion forces vendors to automate audit trails and cross-border transfer controls.
Machine learning-based content inspection is hybridizing static pattern matching with user behavior baselines to reduce false positives in unstructured data environments. Financial services firms in Germany are piloting these engines for trading floor communications surveillance. The technology is hybridizing policy enforcement from reactive blocking to predictive risk scoring that preempts exfiltration attempts.
The EU AI Act's risk-based classification system mandates automated logging for high-risk AI systems, directly expanding DLP functional requirements. National data protection authorities in France and Italy are interpreting these obligations broadly, requiring model training data provenance tracking. Healthcare AI developers face the steepest compliance burden as clinical decision support systems fall under high-risk designations.
Security procurement is consolidating around platform-native tools rather than standalone specialists as buyers prioritize integration over best-of-breed depth. Large enterprises in the United Kingdom are retiring point solutions in favor of Microsoft Purview and CrowdStrike Falcon bundles. This consolidation is most pronounced in regulated industries where vendor audit fatigue drives preference for fewer supplier relationships.
Data Leakage Prevention Product Market Segmentation
DLP procurement patterns diverge sharply across deployment architectures and regulatory exposure levels. Understanding these fault lines clarifies why endpoint solutions dominate current spending while cloud-native alternatives capture strategic attention.
Product Type:
Endpoint DLP, Network DLP, Storage DLP, and Cloud DLP address distinct exfiltration vectors across the data lifecycle.
- Endpoint DLP:Agent-based monitoring on workstations, laptops, and mobile devices inspects data at rest and in motion at the device boundary. Healthcare providers in Germany and France deploy these tools on clinical workstations to satisfy CNIL and BfDI breach notification timelines.
- Cloud DLP:API-driven inspection of SaaS applications and IaaS repositories enables policy enforcement without endpoint agent deployment. Financial services firms in the United Kingdom favor this architecture for shadow SaaS visibility where traditional network monitoring fails.
- Network DLP:Gateway appliances intercept traffic at perimeter chokepoints for protocol-level content inspection. Legacy manufacturing environments retain these deployments despite zero-trust migration pressure.
- Storage DLP:Repository scanning tools classify structured and unstructured data at rest in file shares and databases. Organizations with decades of on-premises data lakes require these engines before cloud migration.
Established volume favors Endpoint DLP; emerging adoption favors Cloud DLP.
Deployment Model:
Cost-to-complexity trade-offs stratify procurement across on-premises, cloud-native, and hybrid architectures.
- Cloud-Based:Fully managed SaaS delivery eliminates infrastructure overhead and accelerates time-to-policy for mid-market organizations lacking dedicated security operations centers. French and Italian SMEs gravitate toward this model to bypass technical debt in legacy environments.
- Hybrid:Split architectures preserve on-premises inspection engines for regulated data while extending policy enforcement to cloud repositories. Multinational organizations facing GDPR Article 44 transfer restrictions adopt this configuration to maintain data residency controls.
- On-Premises:Appliance-based deployment within customer data centers satisfies air-gapped requirements in defense and critical infrastructure sectors. High capital expenditure and specialized staffing demands limit this model to large enterprises with mature security operations.
- Managed Service:Outsourced policy tuning, incident response, and compliance reporting addresses capability gaps in organizations without internal DLP expertise. United Kingdom mid-market firms increasingly procure DLP as a subscription service bundled with SOC operations.
Cost efficiency concentrates in Cloud-Based; compliance rigor concentrates in Hybrid.
End User:
Organizational scale and sectoral regulation dictate functional requirements and procurement authority structures.
- Large Enterprises:Complex data estates spanning multiple jurisdictions demand centralized policy orchestration with granular exception handling. These buyers prioritize integration with existing SIEM and SOAR investments over standalone feature depth.
- Healthcare:HIPAA-covered entities and EU health data processors require automated classification of PHI combined with audit trails for clinical decision support systems. The EU AI Act's high-risk designation for healthcare AI intensifies documentation requirements.
- Government:National security and civilian agencies mandate certified encryption, data residency guarantees, and supply chain provenance. Procurement runs through specialized frameworks with extended vendor vetting cycles.
- SMEs:Resource-constrained organizations seek simplified policy templates and managed detection services. Underpenetration in France and Italy creates openings for channel-delivered solutions.
Regulatory complexity peaks in Healthcare; volume expansion concentrates in Large Enterprises.
Compliance Standard:
Regulatory scope directly maps to technical requirements for automated classification, logging granularity, and cross-border transfer controls.
- GDPR:Comprehensive personal data protection mandates automated data mapping, breach notification workflows, and Article 44 transfer impact assessments. EU national data protection authorities in Germany, France, and Italy enforce these obligations through substantial administrative fines.
- HIPAA:US healthcare privacy and security rules require access logging, encryption standards, and business associate agreement enforcement. Covered entities face OCR audit scrutiny and state attorney general enforcement.
- PCI DSS:Payment card industry standards prescribe network segmentation and data loss prevention for cardholder data environments. Merchants and processors undergo mandatory third-party assessment cycles.
- CCPA:California consumer privacy rights create data inventory and deletion obligations with private right of action for certain breaches. Enforcement by the California Attorney General shapes vendor risk assessments.
Extraterritorial reach distinguishes GDPR; sectoral specificity distinguishes HIPAA.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German DLP vendors supply endpoint monitoring solutions to healthcare networks across France and the United Kingdom, while US-based cloud security platforms capture financial services procurement in London and Frankfurt.
Germany
Healthcare providers in Bavaria and North Rhine-Westphalia deploy agent-based monitoring on clinical workstations to satisfy BfDI breach notification timelines. The EU AI Act mandates automated data classification for high-risk AI systems used in diagnostic imaging. Munich's medical technology cluster drives demand for DLP tools that track model training data lineage.
France
CNIL enforcement actions have elevated DLP from discretionary security spend to mandatory compliance infrastructure for mid-market enterprises. The EU AI Act's documentation requirements for high-risk systems expand DLP scope to encompass AI training datasets and model outputs. Paris-based financial institutions pilot behavioral analytics engines for trading floor communications surveillance.
United Kingdom
Large enterprises in London are retiring point solutions in favor of platform-native bundles to reduce vendor audit fatigue. GDPR Article 44 transfer restrictions complicate cloud DLP architectures for multinational organizations with US data centers. The financial services sector in the City of London drives procurement of API-first DLP modules for security orchestration platforms.
United States
HIPAA-covered entities face OCR audit scrutiny and state attorney general enforcement for breach notification failures. Healthcare providers deploy endpoint monitoring on telehealth devices to satisfy shortened disclosure timelines. Boston's health technology corridor accelerates adoption of automated classification tools for clinical decision support systems.
Italy
Mid-market organizations in Lombardy and Lazio lack dedicated security operations centers, creating openings for managed DLP service providers. The national data protection authority interprets EU AI Act obligations broadly, requiring model training data provenance tracking. Milan's manufacturing base retains network gateway appliances despite zero-trust migration pressure from cloud-native alternatives.
Data Leakage Prevention Product Market Vendor Landscape
On the supply side, the industry is consolidating around platform-native tools rather than standalone specialists as buyers prioritize integration over best-of-breed depth. The vendor base stratifies into three tiers: cloud infrastructure giants embedding DLP natively, endpoint security specialists competing on real-time threat correlation, and emerging players targeting AI training data governance. Dominant competitive moves include strategic bundling within productivity suites and API-first integration partnerships with security orchestration platforms.
Within the cloud infrastructure tier, Microsoft leverages its productivity suite dominance to embed DLP at marginal cost. CrowdStrike anchors its offering in endpoint telemetry, competing on behavioral analytics rather than static policy enforcement. Among emerging specialists, Cyberhaven occupies a position targeting AI training data lineage tracking for high-risk system compliance.
| Leading Market Players |
|---|
| Proofpoint |
| Broadcom |
| Microsoft |
| Forcepoint |
| Trend Micro |
| CrowdStrike |
| IBM |
| McAfee |
| Cyberhaven |
| Others |
Supply Flow & Price Mechanics
Munich's medical technology cluster anchors European DLP software development capacity, with engineering talent concentration sustaining premium pricing for behavioral analytics engines while cloud-native alternatives compress margins at the standard tier.
Pricing Analysis
Next-generation behavioral analytics engines command 40-60% premiums over signature-based detection tools, while prior-generation network gateway appliances face accelerating price erosion. The dominant model is subscription-based SaaS tiering across premium, standard, and economy levels, with price differentiation resting on certification depth (ISO 27001, SOC 2 Type II) and integration complexity. Pricing pressure stems from Microsoft and Google embedding baseline DLP at marginal cost within productivity suites. Mid-market healthcare providers in France and Italy exhibit highest price sensitivity, while German financial institutions prioritize compliance rigor over cost.
Supply Chain Analysis
Upstream machine learning training data and specialized threat intelligence feeds draw from concentrated sources in the United States, Israel, and Estonia. Component dependencies span GPU compute infrastructure, natural language processing libraries, and behavioral telemetry datasets. Supply chain risk centers on single-source vulnerability for real-time threat intelligence APIs. Distribution runs through direct enterprise sales teams for large accounts and channel partners for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fragmentation across deployment architectures and regulatory jurisdictions creates specialist openings as buyers resist full platform consolidation. The EU AI Act's documentation mandates for high-risk systems fragment demand into compliance-specific niches.
For Market Incumbents: Build switching-cost moats through deep SIEM and SOAR integration investments. Defensive moves center on certifying for EU AI Act high-risk system requirements and expanding managed detection services to offset cloud-native bundling pressure. The threat of Microsoft Purview margin compression demands channel control reinforcement in German healthcare networks. For New Entrants and Emerging Players: Build out API-first architectures targeting security orchestration platform integration gaps. White-space targets concentrate on AI training data lineage tracking for high-risk system compliance and managed DLP services for Italian mid-market manufacturers lacking security operations centers. Go-to-market leverage rests on CNIL and BfDI enforcement messaging. For Investors and Strategic Acquirers: Mid-cycle technology positioning favors behavioral analytics specialists with proven EU regulatory compliance pathways. Long-term viability over a multi-year window rests on differentiation sustainability against platform bundling. Acquisition targets should demonstrate automated classification engine maturity. The signal to watch is CrowdStrike and Microsoft pricing actions in the United Kingdom financial services sector.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration Partnership | Embedding DLP modules within CrowdStrike Falcon reduces vendor audit fatigue for London banks. |
| EU AI Act Compliance Certification | Automated lineage tracking for Munich diagnostic imaging developers satisfies BfDI documentation mandates. |
| Managed Detection Service Launch | Outsourced policy tuning addresses SOC capability gaps among Lombardy manufacturing mid-market firms. |
| API-First Architecture Investment | REST interface depth enables consumption by Palo Alto and Splunk security orchestration platforms. |
| Healthcare Vertical Specialization | PHI classification engines for Boston clinical decision support systems satisfy OCR audit scrutiny. |
Methodological Framework
Initial hypotheses were tested against primary input from CISOs at HIPAA-covered entities, data protection officers at GDPR-regulated multinationals, and channel partners distributing endpoint security tools, then refined through secondary validation against SEC 10-K filings, CNIL enforcement action records, and hyperscaler capex disclosures. Bottom-up deployment counts across German healthcare networks combined with top-down IT security spend estimates to triangulate market sizing.
Demand-supply-balance framing anchored the analytical framework across the projection horizon, with segmentation modeling across deployment architecture, organization scale, compliance standard, and regional regulatory cluster. CAGRs derived from historical adoption curve analysis and policy enforcement intensity indicators. Forecast inputs incorporated EU AI Act implementation timelines and healthcare breach notification timeline compressions.
The forecast holds incumbent behavior within observed patterns; aggressive bundling moves by Microsoft or Google would shift outcomes materially. Cross-checking against CNIL and BfDI administrative fine trajectories is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Cloud Security Software Market
Security Software
Cyber Attack Simulation Software Market
Security Software
Global Mobile Identification Market
Security Software
Certificate Authority Market
Security Software
Software Assurance Market
Security Software
Europe Encryption Software Market
Security Software
ATM Security Market
Security Software
Content Protection and Watermarking Market
Security Software
Security Testing Market
Security Software
Endpoint Detection and Response Market
Security Software
Global Log Management Market
Security Software
Spam Blocking Software Market
Security Software
Sound Masking Systems Market
Security Software
Anomaly Detection Market
Security Software
Global Visitor Management System Market
Security Software
Device Vulnerability Management Market