
 Global Enterprise Key Management Market | 2026-2036
Global Enterprise Key Management Market Size, Share, and Industry Trends Forecast 2026-2036
Global Enterprise Key Management Market Foresight
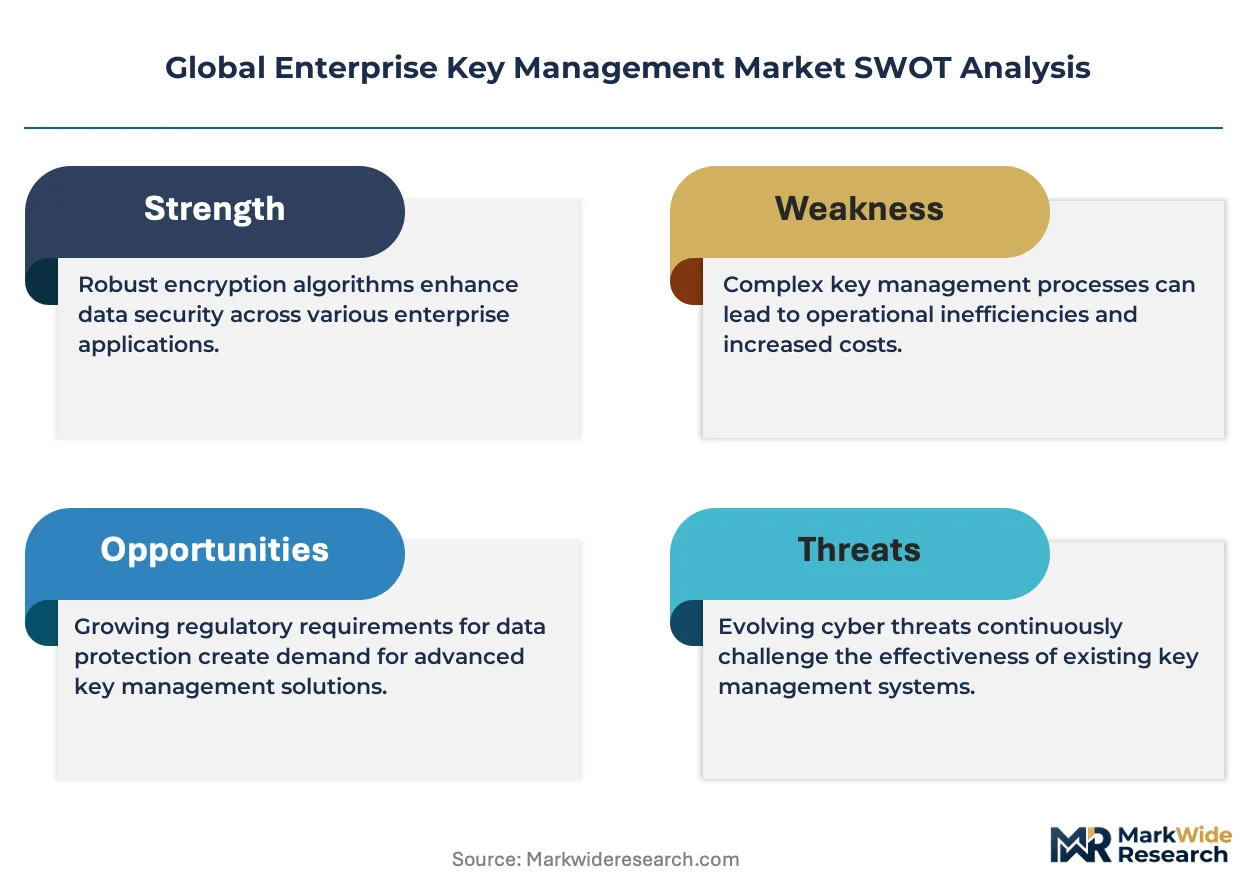
North American cloud infrastructure providers is expanding cryptographic capacity to serve enterprise workloads governed by HIPAA and SEC cybersecurity disclosure rules. IBM Corporation leverages its zSystems mainframe integration to anchor high-assurance key lifecycle management for regulated workloads. Thales Group competes through dedicated hardware security module manufacturing and NATO-certified supply chains. Microsoft Corporation differentiates via Azure Dedicated HSM and confidential computing key isolation for multi-tenant environments.
Enterprise key management encompasses the centralized generation, distribution, storage, rotation, and destruction of cryptographic keys using hardware security modules that process operations within FIPS 140-2 Level 3 or Common Criteria EAL4+ certified boundaries. Its primary purpose is to prevent unauthorized data decryption while enabling auditable compliance for encrypted databases, file systems, and communication channels. Cloud key management solutions now capture the fastest expansion as organizations migrate encryption policy orchestration away from on-premises hardware toward API-native services. Hardware security modules retain the deepest margin pools due to tamper-responsive physical architectures and lengthy certification cycles that limit vendor entry. Hybrid key management architectures are gaining structural importance where data residency laws fragment key custody across sovereign and commercial cloud boundaries.
FDA 21 CFR Part 11 guidelines shape pharmaceutical key management for electronic record integrity, while HIPAA Security Rule mandates drive healthcare provider investment in access-controlled encryption infrastructure. The EU AI Act and GDPR together compel algorithmic transparency and breach notification timelines that elevate automated key rotation from optional to compulsory. Stakeholders must monitor the divergence between NIST post-quantum cryptographic standards and ISO/IEC 27040 storage security frameworks as algorithm transitions force hardware refresh cycles and interoperability testing regimes.
Market Dynamics
Post-quantum cryptographic migration is compressing hardware refresh cycles across financial and defense infrastructure, forcing enterprises to replace FIPS 140-2 Level 3 modules before end-of-life depreciation schedules complete.
Growth Catalysts
- EU AI Act algorithmic transparency mandates:Automated key rotation requirements in high-risk AI systems are expanding HSM procurement across automotive and healthcare verticals.
- Cloud-native API orchestration:Multi-tenant encryption policy management is displacing on-premises hardware governance in enterprise data center consolidation programs.
- Germany industrial conglomerate centralization:Automotive OEMs and machinery manufacturers are consolidating cryptographic governance under single key management platforms to satisfy GDPR data sovereignty rulings.
Market Restraints
- Common Criteria EAL4+ certification timelines:Hardware security module vendors face 18-24 month evaluation periods that delay product launches and freeze R&D capital.
- Belgium-Dutch supply chain concentration:NATO-certified semiconductor foundries for tamper-responsive architectures operate from limited European facilities vulnerable to geopolitical disruption.
- Quantum-resistant algorithm uncertainty:NIST post-quantum standard finalization delays are freezing enterprise procurement committees awaiting cryptographic stability.
Strategic Opportunities
- India BIS cybersecurity localization:Data localization mandates under the Digital Personal Data Protection Act are creating sovereign cloud key management demand from Mumbai and Bangalore IT clusters.
- Confidential computing convergence:Trusted execution environments are merging with hardware security modules to enable encrypted processing without data decryption in memory.
- Japan METI critical infrastructure designation:Financial and energy sector operators must deploy certified key management by regulatory deadline, accelerating domestic vendor partnerships.
Industry Challenges
- Post-quantum cryptographic engineering talent scarcity:Lattice-based and hash-based algorithm implementation expertise concentrates in academic and national laboratory channels, not commercial vendor pools.
- Hybrid architecture integration complexity:Enterprises operating across AWS, Azure, and sovereign cloud boundaries struggle with key custody synchronization and audit trail unification.
- FIPS 140-3 migration capex burden:Level 3 physical tamper detection upgrades require complete module replacement rather than firmware updates, straining federal and healthcare IT budgets.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Enterprise Key Management Market |
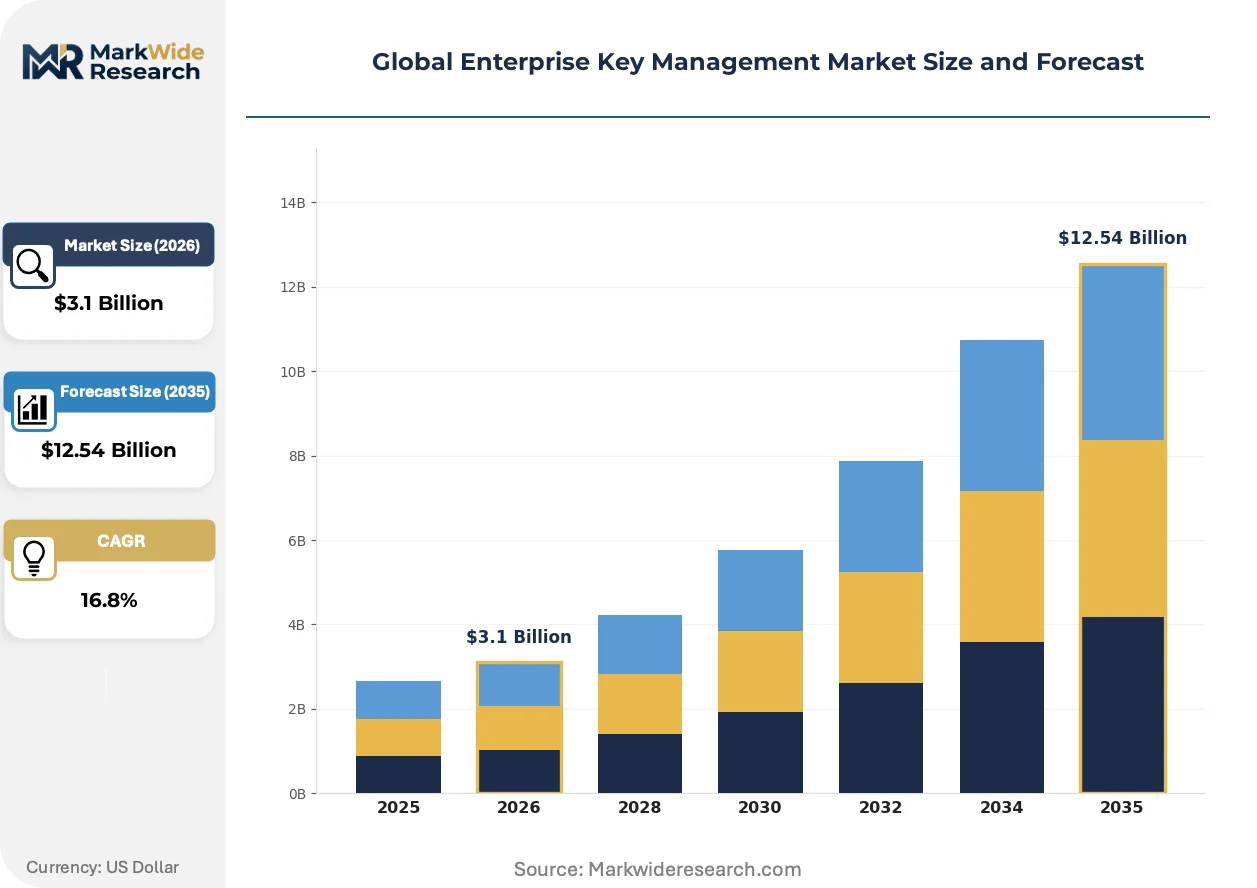
| Market Size in 2026 | $3.1 Billion |
| Market Size in 2035 | $12.54 Billion |
| CAGR (2026 – 2036) | 16.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Cloud Key Management, On-Premises Key Management, Hybrid Key Management, Key Encryption Key, Hardware Security Module Application: Data Encryption, Secure Access, Digital Signatures, Identity Management, Payment Processing End User Industry: Information Technology, Telecommunications, Financial Services, Government Agencies, Education, Energy Deployment Model: Private Cloud, Public Cloud, Virtual Private Cloud, Community Cloud, Dedicated Hosting |
| Companies Covered | Amazon Web Services, Inc., IBM Corporation, Microsoft Corporation, Thales Group, Oracle Corporation, Google LLC, Hewlett Packard Enterprise Company, Venafi, Inc., WinMagic Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Enterprise Key Management Market Shifts & Advancements
Software-defined key lifecycle management is absorbing operational control from dedicated hardware appliances, redistributing cryptographic policy enforcement across containerized and serverless infrastructure layers.
Confidential computing enclaves are absorbing sensitive key material from traditional hardware security modules, enabling financial services firms to process encrypted transactions in multi-tenant cloud environments without hardware custody. Major payment processors in Singapore and London are piloting Intel SGX and AMD SEV integrations for cardholder data protection. This absorption is compressing demand for physical HSM appliances in greenfield cloud-native deployments while sustaining hybrid requirements in regulated on-premises workloads.
The EU AI Act risk classification framework is mandating cryptographic audit trails for high-risk algorithmic decision systems, compelling healthcare and transportation AI vendors to deploy automated key rotation with sub-24-hour breach notification capabilities. German automotive suppliers and French medical device manufacturers are restructuring encryption governance to satisfy both GDPR data minimization and AI Act explainability requirements. This regulatory layering is elevating key management from infrastructure cost center to board-level compliance liability.
Centralized procurement of encryption services through cloud marketplaces is displacing direct vendor relationships for mid-market enterprises, with AWS KMS and Azure Key Vault absorbing contract volume previously captured by Thales and Entrust hardware distributors. Japanese pharmaceutical conglomerates and Australian healthcare networks are consolidating cryptographic spend under single-cloud master service agreements to simplify HIPAA and PMDA audit preparation. This channel compression is forcing traditional HSM vendors to develop managed service wrappers or risk margin erosion in sub-enterprise segments.
Global Enterprise Key Management Market Segmentation
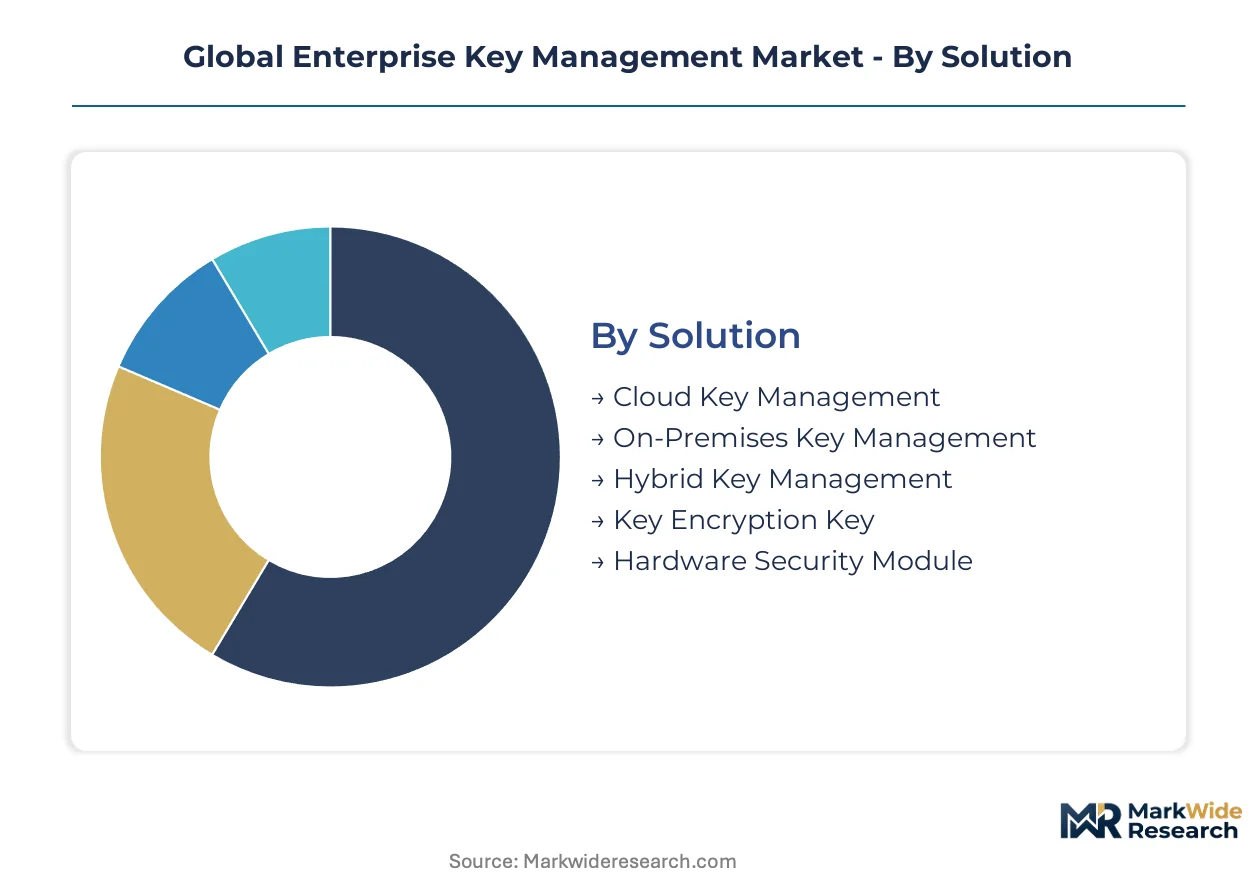
Hardware refresh cycles and post-quantum migration pressures fragment procurement patterns across solution architectures. End-user requirements diverge sharply between regulated on-premises custody and API-native cloud orchestration, forcing vendors to maintain parallel certification tracks.
Solution:
Upgrade timelines compress most aggressively where FIPS 140-2 Level 3 modules face premature replacement before depreciation schedules complete.
- Hardware Security Module:Tamper-responsive physical architectures with Common Criteria EAL4+ boundaries anchor transaction protection for financial services institutions. Demand concentrates in Germany where automotive OEMs centralize cryptographic governance under GDPR data sovereignty rulings; NATO-certified supply chains from Belgium-Dutch foundries constrain volume expansion.
- Cloud Key Management:API-native services displace on-premises hardware governance through multi-tenant encryption policy orchestration. Healthcare providers in Singapore and London pilot Intel SGX and AMD SEV integrations for cardholder data protection; automated key rotation mandates under the EU AI Act accelerate procurement.
- Hybrid Key Management:Architectures fragment key custody across sovereign and commercial cloud boundaries to satisfy data residency laws.
- On-Premises Key Management:Dedicated appliances retain deepest margin pools in federal and healthcare IT budgets requiring physical custody.
- Key Encryption Key:Hierarchical key wrapping schemes enable policy separation between data-encrypting keys and master key material.
Volume placements concentrate in Hardware Security Module; the faster expansion belongs to Cloud Key Management.
Application:
Regulatory layering elevates specific applications from infrastructure cost center to board-level compliance liability.
- Payment Processing:Cardholder data environments mandate HSM-backed encryption for transaction authorization and PIN verification. Major processors in Singapore and London absorb Intel SGX and AMD SEV integrations; PCI-DSS audit compression drives consolidated procurement through cloud marketplaces.
- Data Encryption:Database and file-system protection spans structured healthcare records through unstructured automotive telemetry. German automotive suppliers and French medical device manufacturers restructure governance to satisfy GDPR data minimization; automated rotation with sub-24-hour breach notification becomes compulsory.
- Identity Management:Privileged access credential vaulting integrates with enterprise SSO and PAM platforms.
- Digital Signatures:Qualified electronic signatures under eIDAS regulation require certified key generation and lifecycle audit trails.
- Secure Access:VPN and zero-trust network architectures depend on certificate and key provisioning automation.
Payment Processing captures the steepest expansion trajectory as real-time transaction volumes climb; Data Encryption retains the largest installed base.
End User Industry:
Margin concentration follows regulatory enforcement intensity rather than IT spend scale.
- Financial Services:Transaction protection mandates accelerate hardware security module adoption for real-time payment networks and trading infrastructure. Institutions face compressed refresh cycles as post-quantum cryptographic migration forces FIPS 140-2 Level 3 replacement; SEC cybersecurity disclosure rules tighten audit requirements.
- Government Agencies:Classified and sensitive-but-unclassified workloads demand NATO-certified supply chains and sovereign manufacturing. Belgium-Dutch semiconductor foundries for tamper-responsive architectures face geopolitical vulnerability; federal IT budgets strain under FIPS 140-3 migration capex burden.
- Information Technology:Cloud service providers and SaaS vendors integrate key management into platform offerings.
- Telecommunications:5G network slicing and edge computing expand key distribution complexity across distributed infrastructure.
- Energy:Critical infrastructure operators in Japan face METI regulatory deadlines for certified deployment.
- Education:Research institutions manage cryptographic credentials for federated identity and data sharing agreements.
Financial Services dominates current procurement volume; Government Agencies show the most constrained expansion due to certification bottlenecks.
Deployment Model:
Customer type stratification separates regulated entities requiring physical isolation from cloud-native adopters prioritizing operational velocity.
- Public Cloud:Multi-tenant key vault services from AWS and Azure absorb mid-market contract volume previously captured by hardware distributors. Japanese pharmaceutical conglomerates and Australian healthcare networks consolidate spend under single-cloud master service agreements; HIPAA and PMDA audit preparation simplifies through unified procurement.
- Private Cloud:Dedicated infrastructure within enterprise data centers preserves custody control for regulated workloads. German automotive and industrial conglomerates centralize governance; GDPR data sovereignty rulings fragment key custody across sovereign boundaries.
- Virtual Private Cloud:Logically isolated cloud segments bridge compliance requirements with operational flexibility.
- Dedicated Hosting:Single-tenant hardware deployments satisfy financial services and government physical custody mandates.
- Community Cloud:Shared infrastructure for specific industry sectors reduces individual compliance burden.
Private Cloud retains the deepest margin pool; Public Cloud is gaining share fastest through marketplace channel compression.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Belgium-Dutch semiconductor foundries supply tamper-responsive architectures anchoring NATO-certified hardware production. Geopolitical vulnerability concentrates in these limited European fabrication facilities. Demand fragmentation follows data sovereignty rulings across multiple jurisdictions.
United States
Cloud infrastructure providers expand cryptographic capacity for enterprise workloads governed by HIPAA and SEC cybersecurity disclosure rules. FDA 21 CFR Part 11 guidelines shape pharmaceutical key management for electronic record integrity. Financial institutions in New York and healthcare networks in Boston accelerate hardware security module adoption for transaction protection.
Germany
Automotive OEMs and machinery manufacturers consolidate cryptographic governance under single key management platforms. GDPR data sovereignty rulings fragment key custody across sovereign and commercial cloud boundaries. Industrial conglomerates in Bavaria and Baden-Württemberg centralize HSM procurement to satisfy algorithmic transparency mandates under the EU AI Act.
Japan
Financial and energy sector operators face METI regulatory deadlines for certified key management deployment. Critical infrastructure designation accelerates domestic vendor partnerships for cryptographic compliance. Tokyo-based payment processors and Osaka medical device manufacturers restructure encryption governance to satisfy breach notification timelines.
India
Data localization mandates under the Digital Personal Data Protection Act create sovereign cloud key management demand. BIS cybersecurity localization requirements drive procurement from Mumbai and Bangalore IT clusters. Pharmaceutical exporters and IT services firms in Hyderabad and Pune consolidate cryptographic spend under compliance-focused master agreements.
Singapore
Major payment processors pilot Intel SGX and AMD SEV integrations for cardholder data protection in multi-tenant environments. Confidential computing enclaves absorb sensitive key material from traditional hardware security modules. Financial services firms in the central business district process encrypted transactions without hardware custody.
Global Enterprise Key Management Market Competitive Landscape
Global majors compete with regional champions across certification depth and cloud-native velocity. The vendor base stratifies into three tiers: hyperscale cloud platforms with API-native services, dedicated hardware security module manufacturers with NATO-certified supply chains, and enterprise software vendors with mainframe integration capabilities. Consolidation pressure intensifies as mid-market procurement shifts toward cloud marketplaces. Dominant competitive moves include strategic partnerships for confidential computing convergence and portfolio diversification into hybrid key management architectures.
Within the hardware security module tier, Thales Group exemplifies European manufacturing concentration with Belgium-Dutch supply chain dependencies. IBM Corporation anchors high-assurance key lifecycle management through mainframe integration capabilities for regulated workloads. Microsoft Corporation occupies a position in the cloud-native vector via Azure Dedicated HSM and confidential computing key isolation for multi-tenant environments. These three entities represent distinct competitive archetypes: physical tamper-responsive manufacturing, legacy infrastructure anchoring, and API-native policy orchestration.
| Leading Market Players |
|---|
| Amazon Web Services, Inc. |
| IBM Corporation |
| Microsoft Corporation |
| Thales Group |
| Oracle Corporation |
| Google LLC |
| Hewlett Packard Enterprise Company |
| Venafi, Inc. |
| WinMagic Inc. |
| Others |
Supply & Pricing Matrix
Post-quantum cryptographic migration simultaneously compresses hardware refresh cycles and concentrates supply leverage among NATO-certified foundries. Common Criteria EAL4+ certification timelines stretching 18-24 months lock procurement committees into long-term vendor relationships that resist price negotiation.
Pricing Analysis
Extended warranty and firmware-update bundling separates premium HSM tiers from unbundled economy offerings where certification maintenance carries separate fees. Three-tier pricing structure across FIPS 140-3 Level 3, Level 2, and cloud-native API tiers reflects physical tamper-detection investment and audit trail depth. Price differentiation centers on Common Criteria certification grade and sovereign manufacturing origin. Cost compression in mid-market cloud key management intensifies as AWS KMS and Azure Key Vault absorb contract volume. Healthcare providers and pharmaceutical exporters exhibit highest price sensitivity; defense contractors and central banks demonstrate lowest elasticity due to custody mandates.
Supply Chain Analysis
Photoresist-grade semiconductor substrates for tamper-responsive architectures rest on Belgium-Dutch foundry concentration and Japanese specialty chemical producers. Raw material dependencies span NATO-certified ceramic packaging, lattice-based algorithm IP cores, and FIPS-validated firmware stacks. Single-source vulnerability concentrates in Belgium-Dutch fabrication facilities for physical tamper-detection modules. Distribution runs through direct enterprise sales for regulated workloads and cloud marketplaces for mid-market API services.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Cloud marketplace channel compression is accelerating vendor consolidation as mid-market procurement shifts toward AWS and Azure native services. Weak hardware distributors without managed service wrappers face margin erosion and exit pressure.
For Market Incumbents: Acquire confidential computing IP portfolios to anchor hybrid key management architectures before cloud-native entrants capture regulated workloads. Thales Group and IBM Corporation must defend NATO-certified manufacturing positions against API-native policy orchestration from hyperscalers. Certification investment in FIPS 140-3 Level 3 physical tamper detection preserves federal and healthcare IT pricing power.
For New Entrants and Emerging Players: Cloud marketplace listings through AWS Marketplace and Azure Partner Center offer lowest-friction customer acquisition for API-native key lifecycle management. White-space targets concentrate in India BIS-certified sovereign cloud deployments and Japan METI-critical infrastructure compliance deadlines. Japan's financial sector and Germany's automotive suppliers present most penetrable segments due to regulatory deadline pressure without incumbent cloud relationships.
For Investors and Strategic Acquirers: Exit pathways concentrate in hyperscaler acquisition of confidential computing specialists and private equity rollup of regional HSM distributors. Long-term viability favors vendors with dual certification tracks spanning physical hardware and API-native services. Acquisition target archetype: mid-cap HSM manufacturers with NATO supply chain access and undeveloped cloud service layers. NIST post-quantum standard finalization serves as the critical inflection signal to watch.
| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Partnership | Intel SGX and AMD SEV integrations enable cardholder data protection without hardware custody in Singapore and London. |
| FIPS 140-3 Certification Investment | Level 3 physical tamper-detection upgrades satisfy SEC cybersecurity disclosure rules for New York financial institutions. |
| Sovereign Cloud Localization | India BIS-compliant deployments under the Digital Personal Data Protection Act capture Mumbai and Bangalore demand. |
| Post-Quantum Algorithm R&D | Lattice-based cryptographic expertise addresses talent scarcity concentrated in academic and national laboratory channels. |
| Hybrid Architecture Development | Key custody synchronization across AWS, Azure, and sovereign cloud boundaries resolves GDPR data sovereignty fragmentation. |
Research Methodology
Independent corroboration across primary interviews with CISOs, cloud infrastructure architects, hardware security module procurement leads, and regulatory compliance officers underwrites the qualitative findings. Secondary validation draws from SEC cybersecurity disclosure filings, NIST post-quantum standard drafts, EU AI Act implementation guidance, and hyperscaler capex disclosures. Bottom-up segment sizing triangulates against top-down market envelope calculations.
Comparable-period anchoring to historical FIPS certification cycles and cloud migration trajectories shapes the projection horizon. Segmentation dimensions span solution architecture, deployment model, end-user industry, and regional regulatory cluster. CAGRs derive from installed base turnover rates, post-quantum migration urgency, and cloud API adoption curves. Forecast inputs incorporate EU AI Act enforcement timelines and Japan METI critical infrastructure deadlines.
The model holds under stable NIST standardization schedules and intact NATO supply chains; deviation in Belgium-Dutch foundry access or quantum-resistant algorithm finalization delays would shift hardware refresh assumptions. A small set of named triggers—NIST post-quantum standard publication, EU AI Act audit enforcement, and India BIS localization deadlines—warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Italy Endpoint Detection and Response Market
Security Software
Device Vulnerability Management Market
Security Software
Smartphone Security Market
Security Software
Social Media Security Market
Security Software
Phone Antivirus Software Market
Security Software
Global Digital Vehicle Forensics Market
Security Software
DNS Protection Software Market
Security Software
Global Visitor Management System Market
Security Software
Mobile Antivirus Software Market
Security Software
Passport Reader Market
Security Software
IAM Security Services Market
Security Software
Public Key Infrastructure (PKI) Market
Security Software
Anomaly Detection Market
Security Software
Global Automatic Number Plate Recognition (ANPR) System Market
Security Software
Security Software Market
Security Software
Vsaas Market