
 Global Security Operation Center As a Service Market | 2026-2036
Global Security Operation Center As a Service Market Size, Share, and Industry Trends Forecast 2026-2036
Global Security Operation Center As a Service Market Foresight
The certified cybersecurity analyst labor pool is bifurcating into elite threat-hunting specialists and commoditized alert-triage operators, constraining enterprise self-built SOC scalability. SecureWorks Inc. leverages its Taegis platform to anchor managed detection services for mid-market clients lacking in-house expertise. IBM Corporation competes through Watson-powered security analytics that extend across hybrid cloud footprints. Arctic Wolf Networks, Inc. specializes in concierge-style incident response, differentiating through named security operations experts assigned per account.
Security Operation Center as a Service denotes the outsourced delivery of continuous threat monitoring, detection, and response functions via cloud-native platforms, typically integrating SIEM correlation engines with SOAR orchestration layers operating at sub-15-minute mean time-to-detect thresholds. Its primary commercial purpose is to replace capital-intensive internal security operations with subscription-based expertise accessible to organizations below Fortune 500 scale. Managed Detection services dominate current revenue as enterprises prioritize 24/7 coverage over periodic vulnerability scanning, while Cloud-Based deployment models capture the fastest growth trajectory as multi-tenant architectures reduce per-customer infrastructure costs. Threat Intelligence offerings concentrate margin pools through proprietary dark-web monitoring feeds and adversary-tracking databases that command premium pricing.
The EU AI Act, NIS2 Directive, and GDPR collectively mandate stricter incident disclosure timelines and supply-chain security attestations, compelling European enterprises toward certified SOCaaS providers with auditable response protocols. In the United States, SEC cybersecurity disclosure rules and HIPAA breach notification standards similarly shape procurement criteria, filtering vendor eligibility by demonstrated mean-time-to-respond metrics. Stakeholders must monitor regulatory divergence between jurisdictions as compliance fragmentation risks locking organizations into geographically constrained service architectures.
Market Dynamics
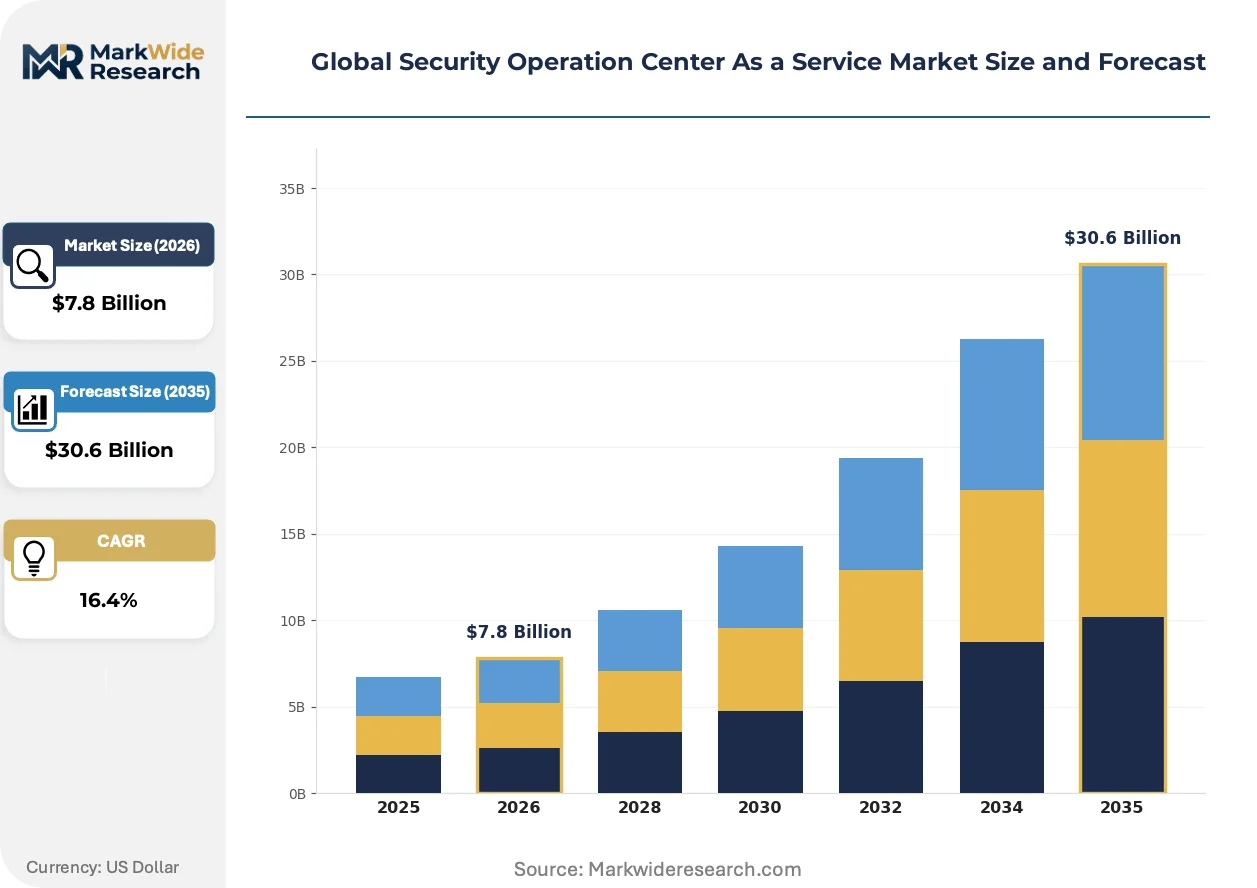
Certified cybersecurity analyst scarcity is compressing enterprise self-built SOC scalability while subscription-based expertise models capture mid-market procurement budgets. Financial services institutions now outsource continuous threat monitoring to offset internal staffing shortfalls.
Growth Catalysts
- EU NIS2 Directive:Mandatory incident-reporting timelines across member states compel European enterprises toward certified SOCaaS providers with auditable response protocols.
- Cloud-native SIEM-SOAR convergence:Multi-tenant architectures operating at sub-15-minute mean time-to-detect thresholds reduce per-customer infrastructure costs and expand addressable markets.
- Singapore cybersecurity hub construction:Government-certified security operations infrastructure attracts regional headquarters deployments from multinational financial institutions.
Market Restraints
- Dark-web intelligence feed concentration:Proprietary threat intelligence databases command premium pricing, compressing margins for providers without captive data sources.
- GDPR-AI Act compliance friction:Overlapping disclosure obligations create jurisdictional complexity for cross-border service architectures.
- Elite threat-hunter supply bottleneck:Bifurcated labor pools constrain scalable delivery of concierge-style incident response.
Strategic Opportunities
- Germany certified hub buildout:Federal cybersecurity infrastructure investments create anchor demand for localized SOCaaS operations.
- Hybrid cloud security analytics:Convergence of endpoint detection with containerized workload monitoring opens mid-market manufacturing verticals.
- Named security operations expert models:Assignment of dedicated analysts per account differentiates commoditized alert-triage offerings.
Industry Challenges
- Multi-tenant data segregation certification:ISO 27001 and SOC 2 Type II audit timelines delay new market entry for regional challengers.
- Legacy SIEM migration complexity:On-premises correlation engine replacement requires phased orchestration layer deployment.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Security Operation Center As a Service Market |
| Market Size in 2026 | $7.8 Billion |
| Market Size in 2035 | $30.6 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Detection, Incident Response, Threat Intelligence, Compliance Management, Vulnerability Assessment Deployment Model: Cloud-Based, On-Premises, Hybrid, Multi-Cloud, Private Cloud End User Industry: BFSI, Telecommunications, Government Agencies, Energy & Utilities, Retail Chains Solution Offering: Real-Time Monitoring, Alert Management, Security Analytics, Log Management, Forensics & Investigation |
| Companies Covered | SecureWorks Inc., IBM Corporation, AT&T Inc., Arctic Wolf Networks, Inc., Trustwave Holdings, Inc., Fortinet, Inc., NTT DATA Group, Check Point Software Technologies Ltd., Thales, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Security Operation Center As a Service Market Shifts & Advancements
Threat detection infrastructure is compressing toward edge-deployed sensors with centralized analytics, displacing hub-and-spoke architectures that dominated the previous decade. This reconfiguration demands new vendor capabilities.
Extended detection and response (XDR) telemetry aggregation is miniaturizing the functional footprint required for enterprise-grade threat visibility. Mid-market healthcare providers now deploy lightweight endpoint agents feeding cloud-native correlation engines. The technology is miniaturizing capital barriers that previously restricted 24/7 monitoring to Fortune 500 scale.
The EU AI Act's risk-classification framework for automated security decision-making imposes documentation burdens on machine-learning-driven alert prioritization. Providers must maintain algorithmic audit trails for high-risk system categorizations. German financial institutions are responding by procuring only from vendors with established conformity assessment procedures.
Subscription-based expertise procurement is displacing perpetual license-plus-staffing models across European manufacturing and logistics verticals. Channel partners now bundle SOCaaS with managed network services rather than reselling point products. The United Kingdom exhibits the fastest behavioral transition as post-Brexit regulatory divergence increases compliance outsourcing preference.
Global Security Operation Center As a Service Market Segmentation
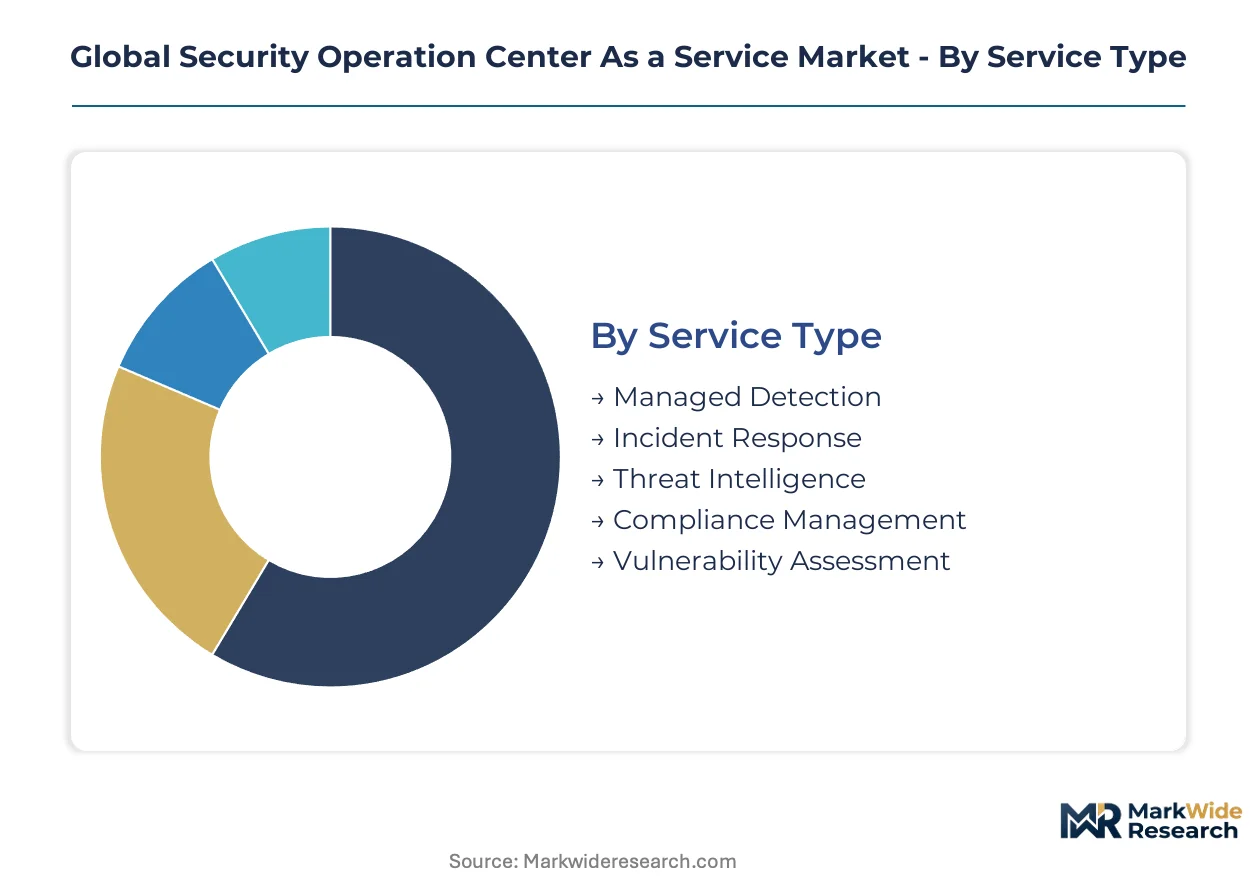
SOCaaS procurement patterns diverge sharply across service tiers and infrastructure choices, with regulatory pressure fragmenting vendor selection criteria by jurisdiction. Buyers weight mean-time-to-detect thresholds against data residency requirements when mapping segments to operational needs.
Service Type:
GDPR, EU AI Act, and NIS2 Directive disclosure timelines reshape procurement priorities across European member states, elevating segments with auditable response protocols.
- Managed Detection:Continuous 24/7 threat monitoring via cloud-native SIEM-SOAR convergence delivers sub-15-minute detection thresholds. German financial institutions and Singapore-based multinational headquarters anchor demand as staffing shortfalls intensify outsourcing preference.
- Incident Response:Concierge-style remediation with named security operations experts assigned per account. United Kingdom post-Brexit regulatory divergence accelerates adoption among mid-market enterprises seeking demonstrable response capabilities for SEC disclosure rules.
- Threat Intelligence:Proprietary dark-web monitoring feeds command premium pricing in competitive tenders.
- Compliance Management:Automated mapping to HIPAA, GDPR, and NIS2 reporting obligations reduces audit preparation cycles.
- Vulnerability Assessment:Periodic scanning services face margin compression as continuous monitoring displaces point-in-time evaluations.
Established volume favors Managed Detection; emerging adoption favors Incident Response.
Deployment Model:
Cost tier differentiation separates capital-intensive on-premises builds from subscription-based cloud alternatives, with multi-tenant architectures compressing per-customer infrastructure expenditure.
- Cloud-Based:Multi-tenant SIEM-SOAR platforms operating at sub-15-minute detection thresholds expand addressable markets below Fortune 500 scale. Singapore government-certified security operations infrastructure attracts regional headquarters deployments from multinational financial institutions.
- Hybrid:Split architectures preserving sensitive log data on-premises while leveraging cloud analytics for correlation. German federal cybersecurity infrastructure investments create anchor demand for localized processing with centralized intelligence feeds.
- On-Premises:Legacy correlation engine retention persists in highly regulated national security contexts.
- Multi-Cloud:Containerized workload monitoring across AWS, Azure, and GCP environments addresses manufacturing verticals with distributed supply chains.
- Private Cloud:Single-tenant isolation satisfies ISO 27001 and SOC 2 Type II certification requirements for healthcare providers.
Cloud-Based deployment captures the steepest expansion trajectory; On-Premises retains entrenched positions in defense and classified government systems.
End User Industry:
Application-specific risk profiles determine service tier selection, with financial services institutions prioritizing 24/7 coverage over periodic assessment models.
- BFSI:Continuous threat monitoring offsets internal cybersecurity analyst staffing shortfalls across retail and investment banking operations. United Kingdom and Singapore jurisdictions exhibit the fastest behavioral transition toward subscription-based expertise procurement.
- Government Agencies:Mandatory incident-reporting obligations under NIS2 Directive and national security classifications demand certified providers with auditable protocols. Germany's federal cybersecurity infrastructure investments concentrate procurement authority at the Länder level.
- Telecommunications:Network-scale visibility requirements drive XDR telemetry aggregation for core infrastructure protection.
- Energy & Utilities:Operational technology convergence with IT networks expands attack surface monitoring requirements.
- Retail Chains:Point-of-sale system protection and supply-chain security attestations shape vendor evaluation criteria.
BFSI commands the dominant revenue share; Government Agencies demonstrate the fastest procurement acceleration under tightening disclosure mandates.
Solution Offering:
Margin concentration pools in proprietary analytics layers, with commoditized log aggregation facing pricing pressure from open-source alternatives.
- Security Analytics:Watson-powered and machine-learning-driven correlation engines command premium positioning. EU AI Act risk-classification frameworks impose documentation burdens on automated alert prioritization, favoring vendors with established conformity assessment procedures.
- Real-Time Monitoring:Edge-deployed sensors with centralized analytics displace hub-and-spoke architectures from the previous decade. Mid-market healthcare providers in the United States deploy lightweight endpoint agents feeding cloud-native correlation engines.
- Alert Management:Tiered triage workflows separate elite threat-hunting specialists from commoditized operators.
- Log Management:Retention compliance for GDPR and HIPAA breach notification standards drives storage architecture decisions.
- Forensics & Investigation:Post-incident analysis capabilities differentiate concierge-style providers in competitive tenders.
Security Analytics captures premium pricing; Real-Time Monitoring expands most quickly through edge-deployment miniaturization.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Pricing power in Germany and the United Kingdom exceeds that in Singapore by substantial margins, reflecting regulatory complexity premiums rather than pure capability differentials. Jurisdictional certification requirements fragment procurement across national boundaries.
United States
SEC cybersecurity disclosure rules and HIPAA breach notification standards filter vendor eligibility by demonstrated response metrics. Financial services institutions in New York and Chicago accelerate outsourcing to offset internal analyst staffing shortfalls. The SEC mandates four-day incident disclosure windows for material cybersecurity events.
Germany
Federal cybersecurity infrastructure investments at the Länder level create anchor demand for localized SOCaaS operations. The EU AI Act and NIS2 Directive impose overlapping disclosure obligations that favor providers with established conformity assessment procedures. Frankfurt's financial district concentrates procurement authority among Bundesbank-regulated institutions.
United Kingdom
Post-Brexit regulatory divergence from EU frameworks increases compliance outsourcing preference among mid-market enterprises. The Information Commissioner's Office enforces GDPR-aligned breach notification standards with 72-hour reporting windows. London's cybersecurity cluster attracts regional headquarters deployments from multinational financial institutions.
Singapore
Government-certified security operations infrastructure attracts regional headquarters deployments from multinational financial institutions seeking ASEAN hub status. The Cyber Security Agency operates licensing frameworks for managed security service providers. The Marina Bay financial district anchors demand from banking operations covering Southeast Asian markets.
Japan
METI guidelines on critical infrastructure protection drive adoption among energy and telecommunications operators. The Personal Information Protection Commission mandates breach reporting with strict notification timelines. Tokyo's Otemachi financial district concentrates procurement from megabank security operations seeking 24/7 coverage.
Global Security Operation Center As a Service Market Competitive Landscape
Technology leadership and cost leadership are held by different player archetypes, creating a bifurcated competitive structure. The market consolidates around three strategic tiers: global platform providers with hybrid cloud analytics capabilities, regional specialists delivering concierge-style incident response, and telecommunications carriers bundling security operations with network services. Dominant competitive moves include M&A to acquire threat intelligence feed assets and strategic partnerships to embed SOCaaS within broader IT outsourcing contracts.
Within the global platform tier, IBM Corporation and SecureWorks Inc. exemplify divergent approaches to scaled delivery. Arctic Wolf Networks, Inc. occupies a distinct position in the concierge-response segment. These three entities represent the primary competitive anchors around which mid-market procurement decisions cluster, with each archetype commanding premium pricing in its respective service tier.
| Leading Market Players |
|---|
| SecureWorks Inc. |
| IBM Corporation |
| AT&T Inc. |
| Arctic Wolf Networks, Inc. |
| Trustwave Holdings, Inc. |
| Fortinet, Inc. |
| NTT DATA Group |
| Check Point Software Technologies Ltd. |
| Thales |
| Others |
Supply & Pricing Matrix
Cloud-native SIEM-SOAR platform substitution for on-premises correlation engines simultaneously shifts supply geography toward multi-tenant infrastructure hubs and compresses per-customer pricing economics across mid-market segments. This reconfiguration concentrates vendor margin pressure in legacy deployment tiers while expanding addressable volume through subscription-based expertise procurement.
Pricing Analysis
Germany and the United Kingdom command substantial premiums over Singapore, reflecting regulatory complexity rather than capability differentials. Three-tier pricing structure across concierge-response, managed detection, and commoditized alert-triage levels dominates procurement frameworks. Price differentiation rests on ISO 27001 certification status and named analyst assignment guarantees. Margins are tightening in vulnerability assessment tiers as continuous monitoring displaces periodic scanning demand. Mid-market healthcare providers exhibit highest price sensitivity; Bundesbank-regulated Frankfurt institutions show lowest.
Supply Chain Analysis
Germany, Singapore, and the United Kingdom anchor certified security operations infrastructure, feeding downstream multi-tenant platform delivery. Raw material dependencies center on proprietary dark-web intelligence feeds, elite threat-hunter labor pools, and cloud compute capacity from hyperscale providers. Single-source vulnerability in boutique threat-intelligence databases exposes margin compression risks. Distribution runs through channel partners bundling SOCaaS with managed network services rather than point-product resale.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a defensive-moat arena where regulatory entrenchment creates durable switching costs for certified providers with established conformity assessment procedures.
For Market Incumbents: Secure auditable response protocols aligned with NIS2 Directive disclosure timelines to lock in European financial services procurement. Deepen threat intelligence feed assets through targeted acquisition to defend margin position against open-source correlation alternatives. Elite analyst retention programs represent the critical lever against labor pool bifurcation. For New Entrants and Emerging Players: Lead with concierge-style incident response targeting United Kingdom mid-market enterprises navigating post-Brexit compliance divergence. Manufacturing verticals in Germany offer penetrable white space through hybrid cloud security analytics bundling. Channel partnership with managed network service providers accelerates go-to-market velocity against direct platform competition. For Investors and Strategic Acquirers: Secondary-cycle assets sit with PE-backed regional specialists possessing ISO 27001 certification but lacking multi-tenant platform scale. Long-term viability over the next decade hinges on regulatory certification moats rather than pure technology differentiation. Watch for EU AI Act conformity assessment procedure completion as inflection signal for premium valuation multiples.| Strategic Initiative | Industry Significance |
|---|---|
| Threat Intelligence Feed Acquisition | Proprietary dark-web monitoring databases command premium pricing in competitive tenders. |
| Conformity Assessment Procedure Investment | EU AI Act documentation burdens favor vendors with established algorithmic audit trails. |
| Named Analyst Assignment Model | Concierge-style differentiation separates elite providers from commoditized alert-triage operators. |
| Multi-Cloud Containerized Monitoring | AWS-Azure-GCP workload visibility opens manufacturing verticals with distributed supply chains. |
| Channel Partnership with Network Services | Bundled procurement displaces point-product resale across European manufacturing segments. |
Research Methodology
A standing panel of CISOs at European financial institutions, SOC operations directors, channel partner account managers, and regulatory compliance officers provided ongoing calibration against primary fieldwork. Secondary validation drew from SEC cybersecurity disclosure filings, EU NIS2 Directive implementation guidance, Cyber Security Agency Singapore licensing frameworks, and hyperscaler infrastructure capex disclosures. Bottom-up service tier sizing and top-down regulatory mandate impact modeling underwent iterative reconciliation.
Consistency checks against external benchmarks validated volume and value outputs across the projection horizon. Segmentation dimensions modeled include service type, deployment architecture, end-user industry vertical, and jurisdictional regulatory cluster. CAGRs derived from exponential smoothing of adoption curves weighted by compliance deadline proximity. Forecast inputs incorporated certified analyst labor pool constraints and multi-tenant infrastructure cost compression trajectories.
Forecasts assume regulatory continuity in EU member states, United Kingdom post-Brexit frameworks, and Singapore licensing regimes; material policy shifts would require re-modeling. Specific risk factors include GDPR-AI Act compliance friction, elite threat-hunter supply bottlenecks, and multi-tenant data segregation certification delays. Recalibration cycles align with material shifts in disclosure mandate enforcement and cloud infrastructure cost trajectories.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Background Check Software Market
Security Software
Cloud File Security Software Market
Security Software
DNS Protection Software Market
Security Software
Mobile Security Market
Security Software
Anomaly Detection Market
Security Software
Employee Computer Monitoring Software Market
Security Software
Network Security Appliance Market
Security Software
Automotive Over-the-Air Cybersecurity Hardening Test Equipment Market
Security Software
Global Data Privacy Management Software Tools Market
Security Software
Global Optical Encryption Market
Security Software
Global Digital Identity Solutions Market
Security Software
Video Intercom Devices Market
Security Software
Mobile Identity Management Market
Security Software
Secaas Market
Security Software
Consumer Endpoint Security Market
Security Software
Global Network Encryption Market