
 Key Management Service Market | 2026-2036
Key Management Service Market Size, Share, and Industry Trends Forecast 2026-2036
Key Management Service Market Outlook
The enterprise reseller channel is tilting toward cloud-native key orchestration platforms as customers abandon perpetual-license hardware models. Amazon Web Services leverages its integrated IAM and KMS stack to dominate consumption-based pricing. Microsoft anchors enterprise trust through Azure Dedicated HSM deployments in regulated verticals. Thales competes on FIPS 140-3 Level 3 certification density across its Luna hardware portfolio.
Key Management Service denotes a cryptographic infrastructure layer governing the generation, storage, rotation, and destruction of encryption keys across distributed systems, typically enforcing policies through hardware security modules operating at FIPS 140-2 Level 2 or higher. Its primary purpose is to prevent unauthorized data decryption while maintaining audit trails for compliance verification. Cloud-Based deployment captures the fastest expansion as organizations migrate key material to multi-tenant HSM services. Banking as an end user sustains premium pricing due to PCI-DSS mandate density. Hardware Security Module technology leads margin pools despite slower growth, while Software key management displaces legacy on-premises appliances in mid-market accounts.
The National Institute of Standards and Technology FIPS 140-3 standard and the EU Cybersecurity Act certification framework constrain product design by mandating physical tamper evidence and side-channel resistance. Germany's BSI and France's ANSSI national cybersecurity agencies enforce additional country-specific evaluation criteria that fragment vendor compliance roadmaps. Stakeholders must monitor whether quantum-resistant algorithms displace RSA and ECC key lengths before NIST post-quantum standards stabilize procurement specifications.
Market Dynamics
Cloud migration is collapsing the traditional hardware security module procurement model as enterprises abandon capital-intensive on-premises key storage for consumption-based multi-tenant services. This structural shift compresses vendor margins while expanding addressable market volume across mid-market accounts previously priced out of FIPS-certified infrastructure.
Growth Catalysts
- GDPR Article 32 mandates:European enterprises must implement encryption with technical measures ensuring key confidentiality, driving hardware-backed key management adoption across Frankfurt and Dublin data center clusters.
- PCI-DSS 4.0 key rotation requirements:Payment processors face stricter cryptographic key lifecycle controls, forcing banking infrastructure upgrades in the United States and Japan.
- Quantum-resistant algorithm preparation:NIST's post-quantum cryptography standardization is accelerating enterprise key inventory audits and long-term migration planning across distributed systems.
Market Restraints
- Hardware security module supply concentration:FIPS 140-3 Level 3 certified chip fabrication concentrates among a limited set of foundries, creating procurement bottlenecks for Thales and Entrust validation timelines.
- EU Cybersecurity Act certification delays:Common Criteria evaluations for key management products extend 18-24 months, freezing vendor release cycles and enterprise procurement decisions.
- Cloud key escrow substitution risk:Hyperscalers' native encryption services reduce standalone KMS attach rates among small and medium enterprises seeking simplified procurement.
Strategic Opportunities
- India's data localization mandate:The RBI's requirement for financial data domestic storage creates demand for in-country key management infrastructure previously served from Singapore or European hubs.
- Confidential computing convergence:Integration of trusted execution environments with hardware security modules enables key processing without memory exposure, opening healthcare and government verticals.
- Bring-your-own-key models:Enterprise customers demand sovereign control over cloud encryption keys, creating white space for hybrid key orchestration platforms spanning on-premises and AWS or Azure environments.
Industry Challenges
- FIPS 140-3 physical security engineering:Vendor engineering teams face acute shortages of specialists capable of designing tamper-responsive enclosures meeting NIST side-channel resistance requirements.
- Legacy PKCS#11 integration complexity:Financial institutions maintain decades-old cryptographic applications requiring extensive middleware development to connect with modern REST-based key management APIs.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Key Management Service Market |
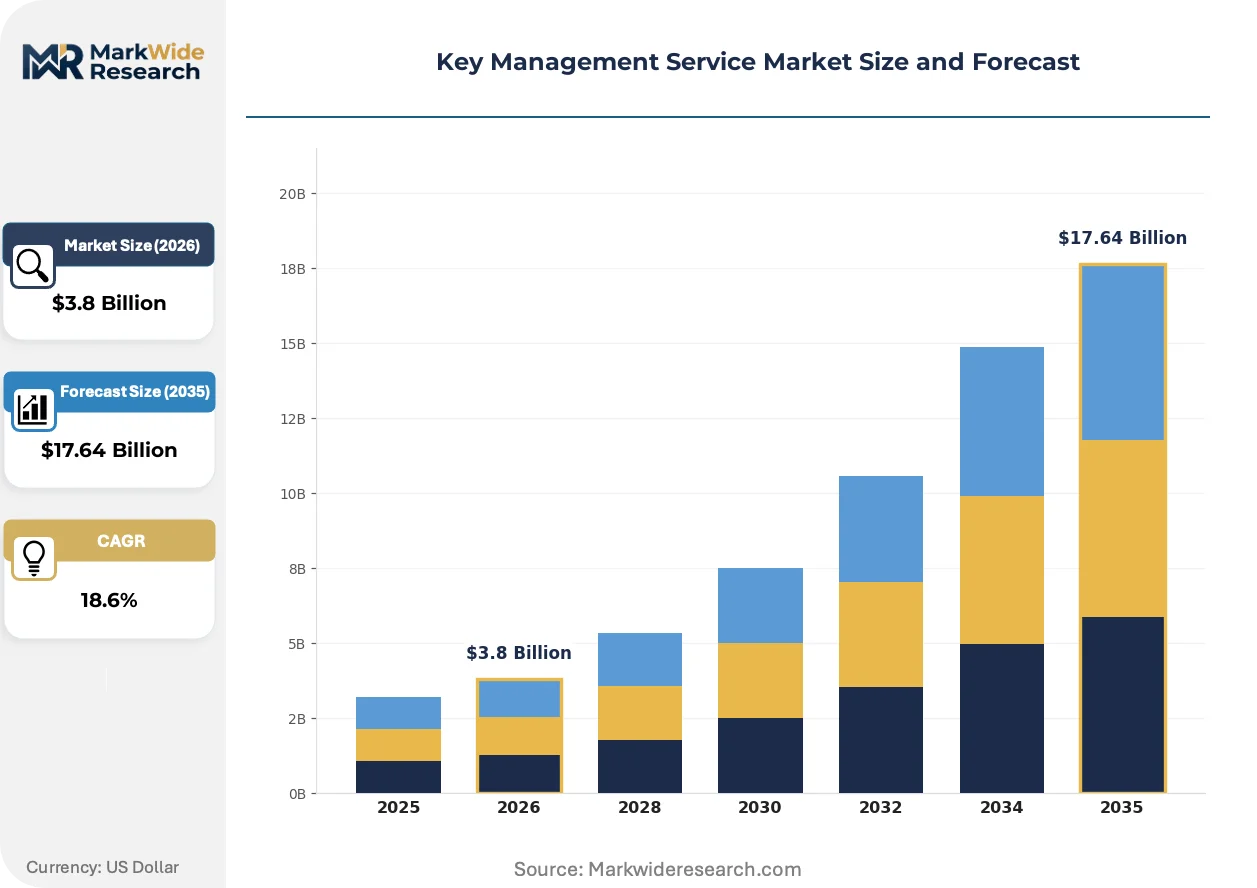
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $17.64 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Banking, Healthcare, Government, Retail Technology: Hardware Security Module, Software, Cloud Key Management, Open Source Service Type: Encryption, Tokenization, Access Control, Audit Management |
| Companies Covered | Amazon Web Services, Microsoft, IBM, Google, Oracle, Thales, Hewlett Packard Enterprise, Gemalto, Keyfactor, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Key Management Service Market Strategic Shifts
Post-quantum cryptographic migration is actively restructuring vendor R&D priorities and enterprise procurement specifications across the key management stack. This transformation compresses traditional algorithm lifecycles while creating new certification requirements.
Multi-cloud key orchestration is collapsing the single-vendor lock-in model that dominated enterprise encryption strategies for two decades. Large financial institutions in Germany and the United States now demand portable key policies spanning AWS, Azure, and Google Cloud environments. This interoperability mandate is fragmenting vendor market power and accelerating open-source key management framework adoption.
The EU AI Act's risk-based classification system imposes encryption requirements on high-risk artificial intelligence systems handling biometric or critical infrastructure data. European national cybersecurity agencies in France and Germany are issuing supplementary technical guidance on key segregation for machine learning training datasets. Banking and healthcare verticals in these jurisdictions face the steepest compliance ramps.
Consumption-based pricing for hardware security module capacity is displacing perpetual license models across mid-market enterprise procurement. Value-added resellers in the United States and Japan report contract structures tying key management costs to actual cryptographic operation volumes rather than provisioned hardware. This shift aligns vendor incentives with customer utilization patterns while compressing upfront implementation barriers.
Key Management Service Market Segmentation
Encryption key lifecycle complexity varies sharply across deployment modes and regulatory contexts. Service intensity—from hardware tamper-response engineering to cloud-native API integration—determines vendor margin structures and customer switching costs. Understanding these segment boundaries clarifies where procurement consolidation will accelerate versus fragment.
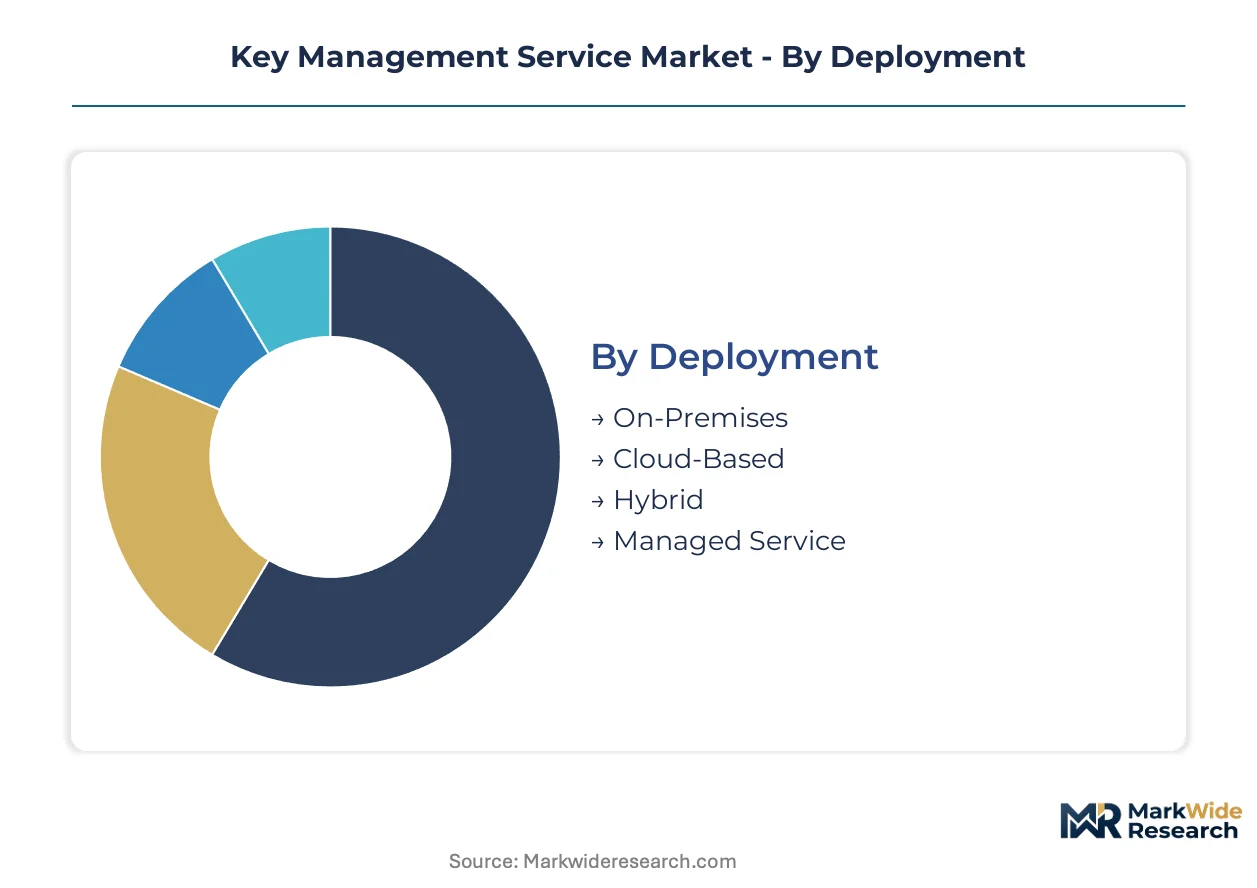
Deployment:
After-sales engineering intensity peaks in hybrid configurations requiring continuous synchronization between on-premises hardware and cloud key stores. Vendors must maintain field service teams capable of diagnosing policy conflicts across distributed environments.
- On-Premises:Dedicated hardware security modules housed within enterprise data centers enforce key confidentiality through physical tamper-evident enclosures. Financial institutions in Frankfurt and Tokyo sustain demand here due to data sovereignty mandates that prohibit cross-border key material movement.
- Cloud-Based:Multi-tenant hardware security module services delivered via API abstract physical infrastructure management from enterprise IT teams. Banking infrastructure teams in the United States are migrating payment processing keys to these models to eliminate capital expenditure cycles and accelerate PCI-DSS audit preparation.
- Hybrid:Split key custody across on-premises and cloud environments with policy-orchestrated rotation. Healthcare systems in Germany deploy this architecture to keep patient decryption keys local while pushing operational logs to cloud analytics platforms.
- Managed Service:Third-party operators assume full responsibility for key generation, storage, rotation, and compliance documentation. Mid-market retailers lacking cryptographic engineering expertise contract these services to satisfy GDPR Article 32 technical measure requirements without internal capability investment.
On-Premises retains the largest installed base; Cloud-Based is climbing the fastest as hyperscaler integration deepens.
End User:
Cost tier segmentation separates premium compliance-driven procurement from volume-sensitive mid-market adoption. Banking and government verticals absorb FIPS 140-3 certification premiums that retailers reject.
- Banking:Payment processors and retail banks operate under PCI-DSS 4.0 key rotation mandates requiring automated lifecycle management across thousands of merchant terminals. Japanese megabanks are consolidating previously fragmented country-specific key management infrastructures onto unified platforms.
- Healthcare:HIPAA-covered entities protect patient records with encryption keys segregated from cloud storage providers. German university hospitals are pioneering confidential computing integrations that process keys within trusted execution environments.
- Government:National security and civilian agencies demand Common Criteria EAL4+ evaluations with country-specific national cryptography approvals. France's ANSSI and Germany's BSI maintain separate evaluation queues that fragment vendor certification roadmaps.
- Retail:Point-of-sale and e-commerce operators prioritize cost minimization over certification density. India's domestic payment networks are driving localized key management procurement as RBI data localization deadlines approach.
Banking commands premium pricing; retail is expanding most quickly as cloud-native services penetrate mid-market accounts.
Technology:
Margin concentration follows physical security engineering complexity. Hardware modules capture value despite slower growth; software displacement accelerates in price-sensitive segments.
- Hardware Security Module:Tamper-responsive physical enclosures with side-channel resistant cryptographic processors certified to FIPS 140-3 Level 3. Supply concentrates among limited foundries qualified for secure element fabrication, creating procurement bottlenecks for Thales and Entrust validation timelines.
- Software:Pure software key management deploying on standard compute without hardware root of trust. Mid-market enterprises in the United States are displacing legacy on-premises appliances with these solutions to reduce physical infrastructure footprints.
- Cloud Key Management:Native encryption services integrated with AWS, Azure, or Google Cloud IAM stacks. Small enterprises seeking simplified procurement increasingly substitute these for standalone KMS purchases, compressing vendor attach rates.
- Open Source:Community-developed frameworks such as HashiCorp Vault enabling vendor-agnostic key orchestration. Large financial institutions in Germany and the United States are adopting these to enforce portable policies across multi-cloud environments.
Hardware Security Module leads revenue concentration; Open Source is gaining share fastest as interoperability mandates fragment vendor lock-in.
Service Type:
Application-driven segmentation reveals where cryptographic operations integrate directly into business workflows versus compliance documentation layers.
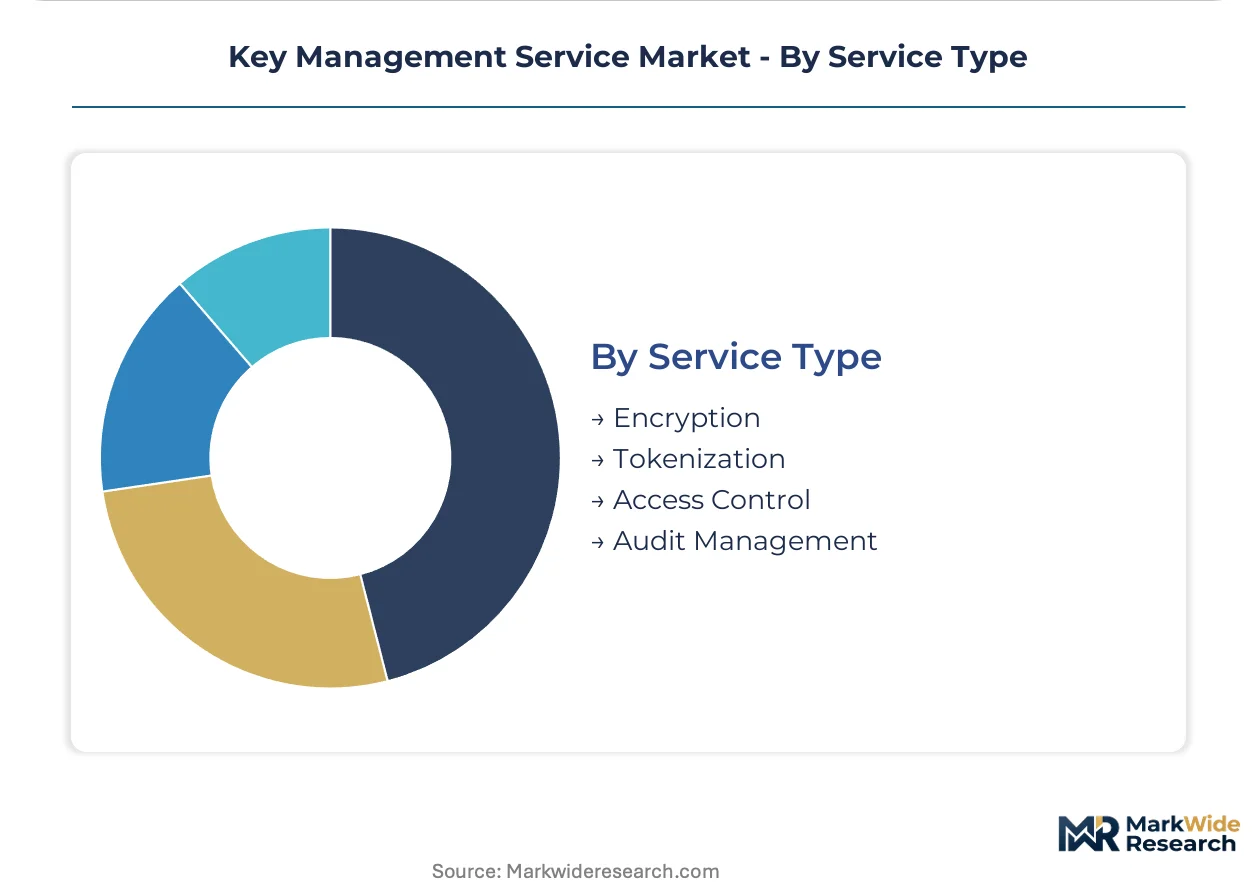
- Encryption:Core key lifecycle services governing data-at-rest and data-in-transit protection. Universal demand across all verticals, with steepest growth in cloud-native database and object storage integrations.
- Tokenization:Replacement of sensitive data elements with non-sensitive equivalents using vaultless or vaulted schemes. Payment processors in the United States and Japan are expanding tokenization scope beyond primary account numbers to encompass personal identifiable information.
- Access Control:Policy enforcement linking key usage authorization to identity verification and contextual risk signals. Healthcare providers are converging these services with zero-trust network architectures.
- Audit Management:Compliance documentation, key usage logging, and forensic trail maintenance for regulatory examination. European enterprises facing GDPR supervisory authority audits are prioritizing automated audit stream generation.
Encryption holds the dominant share; tokenization is expanding most quickly as payment data protection scope broadens.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Pricing power concentrates in Frankfurt and Tokyo data center clusters where data sovereignty mandates justify FIPS 140-3 Level 3 certification premiums. Cost-sensitive mid-market procurement dominates in Mumbai and São Paulo, compressing margins for hardware-backed deployments.
United States
Banking infrastructure teams in New York and Chicago are migrating payment processing keys to cloud-native multi-tenant HSM services to eliminate capital expenditure cycles. PCI-DSS 4.0 key rotation mandates from the Federal Reserve's oversight framework force automated lifecycle upgrades across thousands of merchant terminals. Seattle and Northern Virginia hyperscaler regions anchor consumption-based pricing expansion as AWS and Azure deepen enterprise IAM integration.
Germany
Frankfurt data center clusters sustain premium hardware security module demand as BSI national cybersecurity agency evaluations enforce stricter tamper-evidence requirements than baseline EU standards. GDPR Article 32 technical measure obligations drive healthcare systems in Berlin and Munich toward confidential computing integrations with trusted execution environments. Bavarian automotive suppliers are consolidating fragmented key management infrastructures onto unified platforms to satisfy export control cryptography regulations.
Japan
Tokyo megabanks are unifying previously country-specific key management silos onto single orchestration platforms to reduce operational complexity across ASEAN payment corridors. METI industrial policy encourages quantum-resistant algorithm preparation through subsidized enterprise key inventory audits. Osaka-based payment processors face compressed procurement timelines as FISC security standards tighten cryptographic key lifecycle documentation requirements.
India
RBI data localization mandates for financial data domestic storage are creating demand for in-country key management infrastructure previously served from Singapore hubs. Mumbai payment networks and Bangalore fintech clusters are driving localized procurement as regulatory deadlines approach. Delhi-NCR enterprise IT teams are displacing legacy on-premises appliances with software key management to reduce physical infrastructure footprints while satisfying central bank audit requirements.
United Kingdom
London financial services firms are adopting multi-cloud key orchestration to enforce portable policies across AWS, Azure, and Google Cloud environments without vendor lock-in. The Information Commissioner's Office GDPR enforcement posture pressures healthcare providers in Manchester and Birmingham toward automated audit stream generation for supervisory authority examinations. Edinburgh-based banking infrastructure teams are integrating tokenization scope expansion beyond primary account numbers to encompass personal identifiable information.
Key Management Service Market Competitive Environment
Platform integrators command the system tier; component specialists sit upstream with certification density. The vendor base spans three distinct strata: hyperscalers with native IAM-KMS integration, hardware security module fabricators with FIPS 140-3 Level 3 density, and open-source framework providers enabling vendor-agnostic orchestration. Consolidation pressure concentrates among mid-market software vendors as cloud-native services displace perpetual-license appliances. Strategic moves center on hybrid deployment capability expansion and post-quantum cryptographic migration partnerships.
Within the hardware certification tier, Thales and Gemalto exemplify the physical security engineering archetype required for banking and government verticals. Among hyperscaler-integrated platforms, Amazon Web Services and Microsoft occupy positions anchoring consumption-based pricing models that compress standalone vendor attach rates. IBM represents the legacy enterprise software provider archetype navigating middleware complexity for financial institutions maintaining decades-old cryptographic applications.
| Leading Market Players |
|---|
| Amazon Web Services |
| Microsoft |
| IBM |
| Oracle |
| Thales |
| Hewlett Packard Enterprise |
| Gemalto |
| Keyfactor |
| Others |
Value Chain & Pricing Dynamics
Undercapacity in FIPS 140-3 Level 3 certified secure element fabrication is tightening vendor pricing power while lengthening procurement timelines for banking and government verticals. Thales and Entrust validation queues now stretch eighteen to twenty-four months, forcing enterprises toward cloud-native consumption models that trade certification density for deployment velocity.
Pricing Analysis
Configured-to-order FIPS 140-3 Level 3 hardware security modules command three to five times the per-key cost of standard cloud-native API services, with the premium reflecting physical tamper-response engineering and side-channel resistance certification. Pricing stratifies across premium certified hardware, standard hybrid orchestration platforms, and economy-grade software-only deployments, with certification grade and after-sales engineering intensity as the primary differentiation drivers. Cost compression in the standard tier is intensifying because hyperscalers bundle native encryption services with IAM subscriptions, eroding standalone vendor attach rates. Mid-market retailers exhibit the highest price sensitivity, while Frankfurt and Tokyo banking clusters absorb premium hardware costs under data sovereignty mandates.
Supply Chain Analysis
Upstream feedstock for tamper-responsive cryptographic processors centers on specialized secure element fabrication concentrated in Taiwan, South Korea, and the United States, with limited foundry capacity qualified for FIPS 140-3 physical security requirements. Supply chains draw from rare earth substrates for tamper-evident enclosures, advanced packaging for side-channel resistant architectures, and precision mechanical components for intrusion-responsive mesh designs. Single-source vulnerability pervades the certified chip layer, as only three foundries maintain active NIST validation for Level 3 enclosure integration. Distribution runs through value-added resellers in the United States and Japan, direct enterprise sales in Germany, and hyperscaler marketplace integrations for cloud-native consumption.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The acute shortage of engineers capable of designing NIST-compliant physical tamper-response systems is constraining vendor expansion and inflating certified product premiums. This capability gap favors incumbents with established certification pipelines while raising barriers for new hardware entrants.
For Market Incumbents: Pre-empt cloud-native displacement by embedding hardware-backed key orchestration into hybrid deployment architectures spanning on-premises Luna HSMs and multi-tenant cloud services. Accelerate FIPS 140-3 Level 3 certification density across the portfolio before EU Cybersecurity Act evaluation queues lengthen further, and secure captive supply agreements with Taiwan-based secure element foundries to insulate against single-source fabrication risk. For New Entrants and Emerging Players: Mid-market healthcare systems in India lacking cryptographic engineering expertise represent the most penetrable entry point, with RBI data localization deadlines forcing urgent procurement without established vendor relationships. Software-only key management deploying on standard compute infrastructure offers a lower-certification foothold, with managed service wrappers delivering GDPR Article 32 compliance documentation as the primary go-to-market angle. For Investors and Strategic Acquirers: Capital is best deployed toward hybrid key orchestration platforms with active multi-cloud policy portability and post-quantum cryptographic migration roadmaps, as algorithm standardization will reshape procurement specifications across the forecast window. Watch NIST post-quantum standard finalization as the inflection signal triggering enterprise inventory audits and long-term contract renegotiations.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptographic Migration | NIST standardization is forcing enterprise key inventory audits and algorithm replacement planning. |
| Hybrid Deployment Architecture Expansion | Split custody models spanning on-premises HSMs and cloud stores satisfy data sovereignty mandates. |
| Confidential Computing Integration | Trusted execution environments processing keys without memory exposure open healthcare verticals. |
| Multi-Cloud Policy Portability | Portable key orchestration across AWS, Azure, and Google Cloud fragments vendor lock-in power. |
| Consumption-Based Pricing Transition | Per-operation billing aligns vendor incentives with utilization and compresses upfront barriers. |
Study Parameters
A spread of perspectives from chief information security officers at Frankfurt and Tokyo banks, cloud infrastructure architects at U.S. payment processors, BSI evaluation officers, and healthcare IT procurement leads converged on the working assumptions. These primary inputs were validated against secondary sources including NIST FIPS 140-3 validation certificates, EU Cybersecurity Act Common Criteria evaluation reports, SEC 10-K filings from listed cybersecurity vendors, and RBI circulars on data localization. Bottom-up sizing of encryption key lifecycle deployments was triangulated against top-down estimates of banking and healthcare IT security expenditure.
Demand-supply balance modeling tracked enterprise migration from on-premises hardware to cloud-native services against secure element fabrication capacity constraints. Segmentation dimensions included deployment mode, end-user vertical, technology tier, and regional regulatory cluster, with CAGRs derived from slope analysis of adoption curves and certification pipeline throughput. Post-quantum algorithm readiness and confidential computing integration velocity served as industry-specific forecast modifiers.
Practitioners should monitor NIST post-quantum standard finalization, EU Cybersecurity Act evaluation queue lengths, and hyperscaler IAM-KMS bundling intensity for early signals of forecast revision. Cross-checking against vendor-reported FIPS 140-3 validation timelines and foundry capacity disclosures is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Security Orchestration Automation and Response (SOAR) Market
Security Software
Endpoint Detection and Response [EDR] Market
Security Software
Risk-Based Authentication (RBA) Market
Security Software
Global Secure Mobile Communications Software Market
Security Software
Global Background Check Software Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
North America Secure Access Service Edge Market
Security Software
Automotive Endpoint Authentication Market
Security Software
Biometric POS Terminals Market
Security Software
Application Control Software Market
Security Software
Anomaly Detection Tools Market
Security Software
Cloud Data Loss Prevention Solution Market
Security Software
Passwordless Authentication Market
Security Software
Contactless Smart Card Market
Security Software
Digital Risk Protection Platform Market
Security Software
Facial Recognition Market