
 IAM Security Services Market | 2026-2036
IAM Security Services Market Size, Share, and Industry Trends Forecast 2026-2036
IAM Security Services Market Outlook
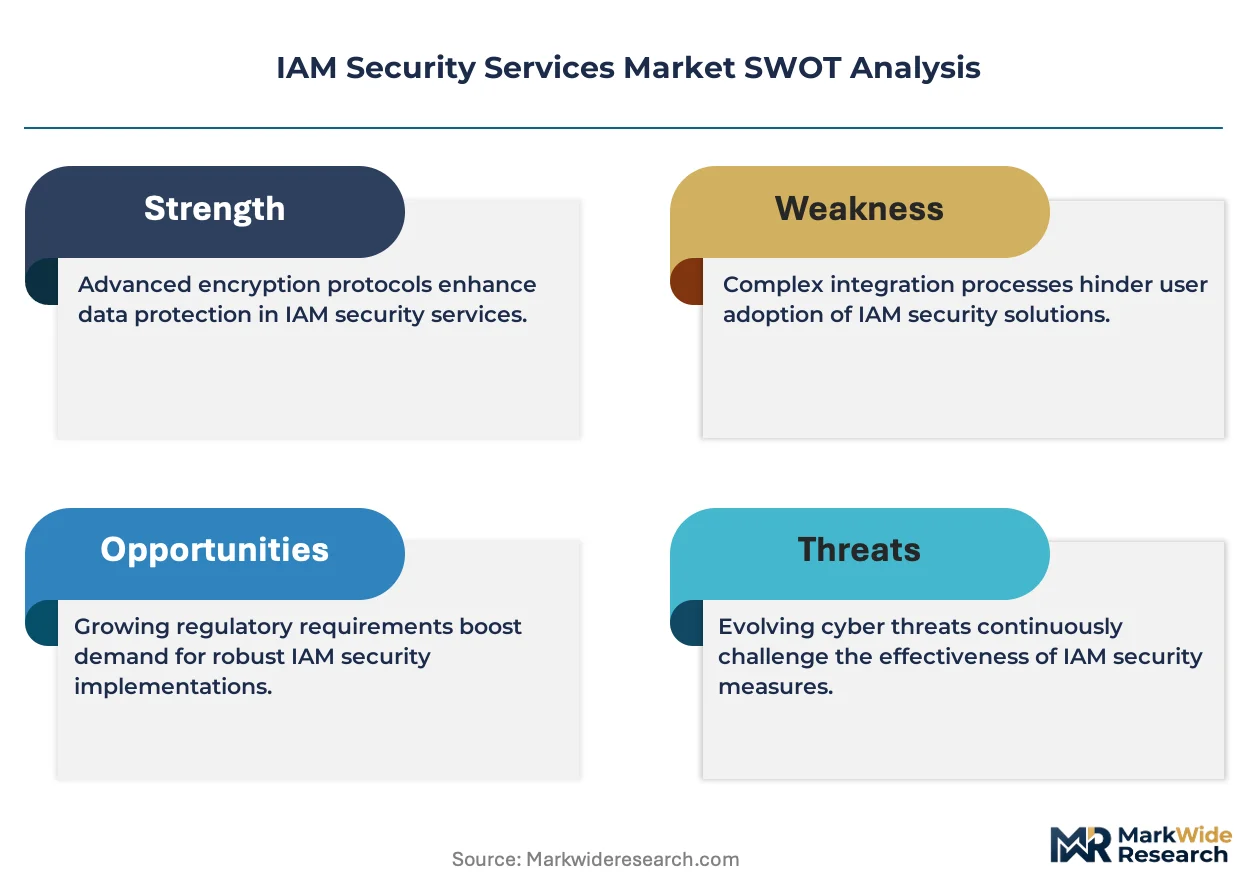
Chronic shortages of certified cloud security architects and identity engineers is unwinding delivery timelines for enterprise IAM rollouts. Microsoft leverages its Azure Active Directory ecosystem to anchor hybrid deployment contracts across Fortune 500 accounts. Okta competes through native SaaS integrations that reduce custom development overhead for mid-market buyers. CyberArk specializes in privileged access management, sustaining premium pricing through deep mainframe and DevOps vaulting capabilities.
IAM Security Services encompass the policy frameworks, software tools, and managed operations that govern digital identity lifecycle management, enforce least-privilege access controls, and authenticate users across heterogeneous IT environments using protocols such as SAML, OAuth, and FIDO2. Cloud-based deployment models now lead new contract value as organizations retire legacy on-premises identity stacks, while hybrid architectures retain stronghold status in regulated verticals requiring data residency controls. Authentication Services and Privileged Access Management represent the fastest-expanding service type segments, reflecting concentrated investment in passwordless methods and secrets management for cloud-native workloads.
NIST zero-trust guidelines, HIPAA identity safeguards, and the EU AI Act's biometric authentication provisions collectively elevate compliance-driven IAM spending across healthcare, financial services, and government verticals. FDA cybersecurity premarket guidance for connected medical devices further tightens identity verification requirements in healthcare supply chains. Stakeholders must weigh sovereign cloud mandates against the interoperability demands of distributed workforces when architecting multi-region identity infrastructures.
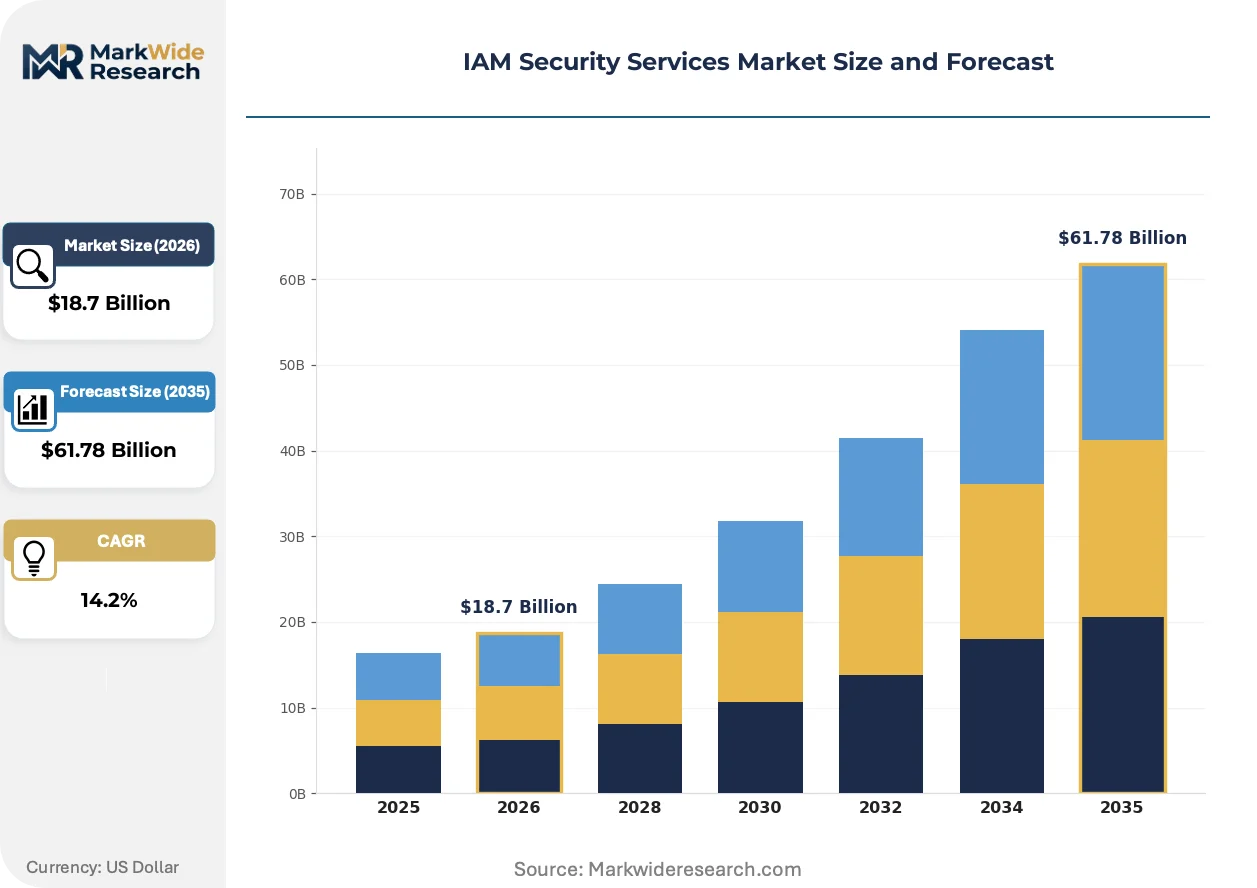
Market Dynamics
Zero-trust architecture mandates from NIST and equivalent bodies across Germany, Japan, and Australia are compressing procurement cycles and forcing wholesale replacement of perimeter-based identity stacks with continuous verification frameworks.
Growth Catalysts
- NIST Zero-Trust Guidelines:Federal agencies and defense contractors in the United States must re-architect identity infrastructure by fiscal deadlines, creating immediate contract velocity for privileged access management and micro-segmentation services.
- HIPAA Identity Safeguards:Healthcare providers face audit pressure to implement multi-factor authentication for all workforce access to electronic protected health information, driving authentication services procurement.
- Passwordless Methods:Financial services firms deploy FIDO2 and biometric authentication to reduce credential theft exposure and satisfy cyber insurance underwriting requirements.
Market Restraints
- Certified Talent Scarcity:Chronic shortages of cloud security architects and identity engineers extend enterprise IAM rollout timelines by six to eighteen months.
- Legacy System Entrenchment:Mainframe and AS/400 environments in banking and government resist API-based integration, forcing expensive middleware layers.
- Data Residency Requirements:Germany's sovereign cloud mandates and Australia's data localization rules fragment identity infrastructure across incompatible regional instances.
Strategic Opportunities
- Connected Medical Devices:FDA cybersecurity premarket guidance tightens identity verification requirements across healthcare supply chains, creating specialized authentication demand.
- DevOps Secrets Management:Cloud-native workload expansion drives investment in vaulting solutions for API keys, tokens, and service account credentials.
- EU AI Act Biometric Provisions:Compliance-driven spending on explainable authentication algorithms opens premium service tiers for European financial institutions.
Industry Challenges
- Interoperability Complexity:Heterogeneous IT environments spanning SaaS, on-premises, and edge locations require custom SAML and OAuth federation engineering.
- Skills Pipeline Constraints:Universities and certification bodies lag in producing identity engineers proficient in both legacy directory services and cloud-native architectures.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | IAM Security Services Market |
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $61.78 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Identity Governance, Access Management, Authentication Services, Privileged Access Management Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User Type: Large Enterprises, SMEs, Government, Education Industry Vertical: Healthcare, Financial Services, Retail, Manufacturing |
| Companies Covered | Microsoft, Okta, IBM, Oracle, Ping Identity, CyberArk, SailPoint, Saviynt, Amazon Web Services, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
IAM Security Services Market Strategic Shifts
Identity infrastructure is fragmenting into modular, API-first components that decouple authentication, authorization, and audit functions from monolithic platforms. This architectural shift enables precise capability sourcing but demands sophisticated integration orchestration.
Passwordless authentication is decomposing traditional credential-based security models. FIDO2 and WebAuthn standards enable cryptographic key pairs bound to hardware devices, eliminating phishing vectors. Financial services firms and healthcare providers adopt these methods fastest due to regulatory pressure. The technology is decomposing market concentration among legacy identity providers by lowering switching costs between authentication vendors.
The EU AI Act's biometric authentication provisions impose strict accuracy, bias-testing, and human-oversight requirements on facial recognition and behavioral biometrics deployments. Identity service providers must re-engineer algorithms and documentation workflows to achieve conformity. European financial institutions and border control agencies represent the most affected buyer segments, accelerating procurement of explainable AI auditing tools alongside authentication infrastructure.
Enterprise buyers now unbundle identity services from bundled platform contracts, selecting best-of-breed components for specific use cases. Mid-market firms lead this pattern, purchasing standalone privileged access management or customer identity tools rather than comprehensive suites. This fragmentation is most visible in the United States, where venture-backed SaaS vendors compete aggressively on API coverage and pre-built integrations.
IAM Security Services Market Segmentation
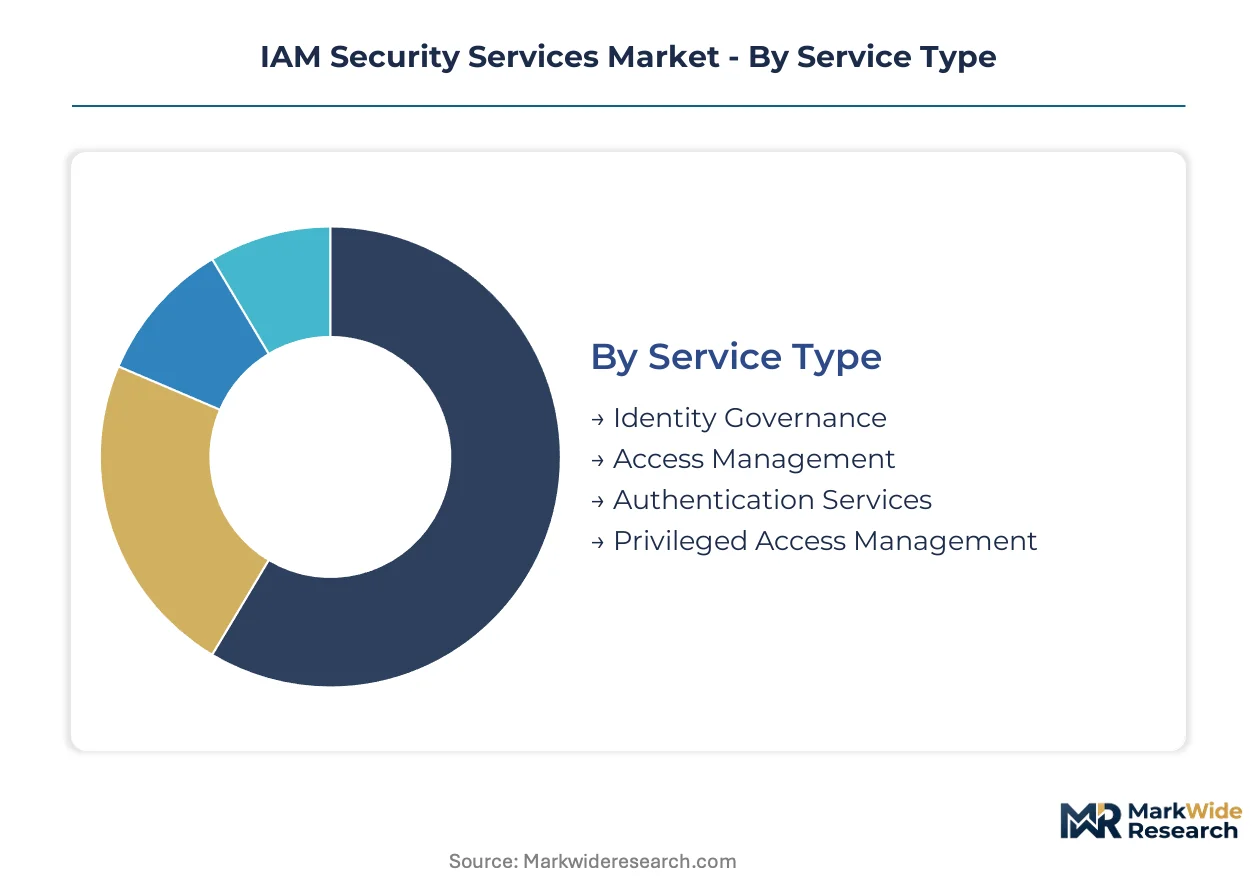
IAM procurement patterns diverge sharply across organizational scale and regulatory exposure, with cloud-native segments displacing legacy on-premises contracts in financial services while hybrid architectures retain defensive positions in healthcare and government verticals.
Service Type:
Privileged Access Management and Authentication Services face the strongest substitution pressure from passwordless standards and secrets vaulting automation, while Identity Governance maintains stickiness through audit trail requirements.
- Privileged Access Management:Vaulting solutions for root credentials, API keys, and service accounts enforce just-in-time elevation protocols. Demand concentrates among DevOps teams in United States financial services firms replacing static credential repositories to satisfy cyber insurance underwriters and SEC disclosure rules.
- Authentication Services:Multi-factor and passwordless verification systems using FIDO2, WebAuthn, and biometric modalities. United States healthcare providers drive procurement volume under HIPAA audit pressure for workforce access to electronic protected health information systems.
- Identity Governance:Lifecycle management and compliance reporting for user provisioning and de-provisioning workflows.
- Access Management:Single sign-on and session management across SaaS and on-premises application portfolios.
Authentication Services retains volume leadership; Privileged Access Management holds the steepest expansion curve.
Deployment Model:
Cost tier stratification separates capital-intensive on-premises implementations from operational expenditure cloud contracts, with hybrid deployments commanding premium pricing for data residency compliance.
- Cloud-Based:SaaS-delivered identity platforms with API-first architectures and continuous feature deployment. United States mid-market enterprises favor this model to avoid identity engineering hiring bottlenecks, though Germany's sovereign cloud mandates fragment procurement for European subsidiaries.
- Hybrid:Split architectures retaining directory services on-premises while extending authentication to cloud workloads. Regulated United States healthcare systems and federal contractors maintain this posture to satisfy HIPAA data location requirements and NIST zero-trust segmentation mandates.
- On-Premises:Legacy directory and federation servers in mainframe-connected environments.
- Managed Services:Third-party operated identity infrastructure with SLA-backed uptime guarantees.
Cloud-Based deployments gain share fastest; Hybrid architectures defend revenue concentration in regulated accounts.
End User Type:
Customer type determines integration complexity, with Large Enterprises demanding bespoke federation engineering while SMEs prioritize pre-configured SaaS connectors.
- Large Enterprises:Complex heterogeneous environments spanning Active Directory, cloud identity providers, and legacy mainframe access controls. United States Fortune 500 accounts drive demand for micro-segmentation and continuous verification frameworks under NIST zero-trust deadlines.
- Government:Federal, state, and local agencies with classified and unclassified identity requirements. United States federal identity modernization programs concentrate procurement through fiscal year contracting cycles, with defense contractors facing accelerated re-architecture mandates.
- SMEs:Resource-constrained organizations prioritizing out-of-box integrations over custom development.
- Education:Universities and K-12 districts managing transient student and researcher populations.
Large Enterprises retain volume leadership; Government holds the steepest expansion curve.
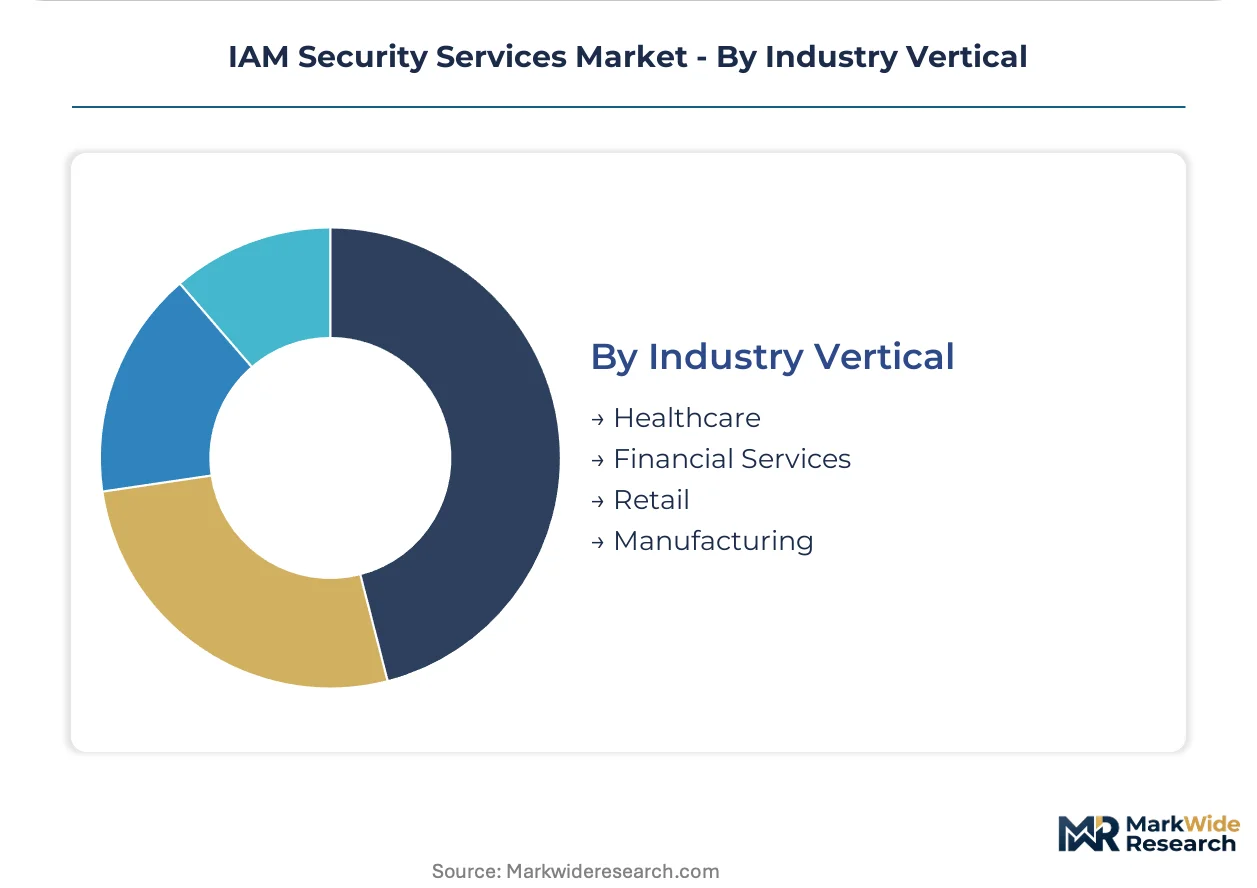
Industry Vertical:
Application context dictates authentication rigor, with Financial Services and Healthcare facing the most stringent regulatory triggers for identity infrastructure replacement.
- Financial Services:Banks, insurers, and payment processors deploying passwordless methods to reduce credential theft exposure. United States firms accelerate FIDO2 adoption to satisfy cyber insurance underwriting requirements and SEC cybersecurity disclosure rules, while European counterparts navigate EU AI Act biometric provisions.
- Healthcare:Hospitals, clinics, and medical device manufacturers implementing multi-factor authentication for workforce access. United States providers face OCR audit pressure under HIPAA identity safeguards, with FDA premarket guidance tightening verification requirements for connected device supply chains.
- Retail:Customer identity and access management for e-commerce and loyalty program platforms.
- Manufacturing:Operational technology identity controls for industrial control systems and supply chain portals.
Financial Services retains volume leadership; Healthcare holds the steepest expansion curve.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Pricing power in IAM Security Services concentrates in United States federal contracting corridors, while Germany's sovereign cloud mandates fragment procurement economics across European subsidiaries. This asymmetry shapes vendor go-to-market strategies and service tier configurations.
United States
Federal identity modernization programs and HIPAA audit pressure drive authentication services procurement. NIST zero-trust deadlines compress implementation timelines for defense contractors and healthcare systems. Washington DC metro and Seattle anchor cloud identity engineering clusters serving Fortune 500 accounts.
Germany
Sovereign cloud mandates and data residency requirements sustain premium pricing for hybrid deployment architectures. BSI technical guidelines enforce strict identity verification standards for financial services. Frankfurt and Munich concentrate IAM engineering talent serving EU-wide regulated accounts.
Japan
Financial services firms deploy passwordless methods to satisfy cyber insurance underwriters and METI cybersecurity frameworks. Government digital identity initiatives accelerate privileged access management procurement. Tokyo and Osaka host specialized identity engineering teams for mainframe-connected banking environments.
Australia
Data localization rules and critical infrastructure protection mandates reshape identity infrastructure procurement for energy and healthcare sectors. TGA cybersecurity guidance tightens verification requirements for connected medical device supply chains. Sydney and Melbourne concentrate cloud security architecture talent serving Asia-Pacific regulated verticals.
United Kingdom
Financial services regulators enforce multi-factor authentication for open banking and payment processing infrastructure. NCSC zero-trust guidance accelerates replacement of perimeter-based identity stacks. London's fintech corridor drives demand for customer identity and access management solutions.
IAM Security Services Market Competitive Environment
Technology leadership and cost leadership are held by different player archetypes, with hyperscale cloud providers anchoring platform ecosystems while specialists capture premium pricing in privileged access niches. The vendor base stratifies across three tiers: integrated platform vendors, best-of-breed specialists, and regional managed service providers. Platform vendors compete through API coverage and pre-built SaaS connectors. Specialists defend margin through deep vaulting capabilities and mainframe integration expertise. Dominant competitive moves include portfolio diversification into adjacent security segments and strategic partnerships to extend geographic reach.
Within the integrated platform tier, Microsoft and Okta occupy positions that exemplify contrasting deployment philosophies, with the former anchoring hybrid enterprise contracts and the latter representing native SaaS-first approaches. CyberArk sits within the specialist archetype, commanding premium positioning through privileged access management depth. These three entities collectively illustrate how vendor selection in IAM Security Services depends on organizational scale, legacy system exposure, and regulatory complexity rather than feature parity alone.
| Leading Market Players |
|---|
| Microsoft |
| Okta |
| IBM |
| Oracle |
| Ping Identity |
| CyberArk |
| SailPoint |
| Saviynt |
| Amazon Web Services |
| Others |
Value Chain & Pricing Dynamics
Platform-scale economies in cloud identity delivery concentrate pricing power among hyperscale providers while compressing margins for regional managed service competitors. This asymmetry shapes procurement patterns: Fortune 500 buyers negotiate volume discounts on Azure Active Directory and Okta contracts, while mid-market firms face SaaS-tier pricing rigidities with limited customization leverage. Supply concentration in United States federal contracting corridors and German sovereign cloud zones reinforces geographic price stratification.
Pricing Analysis
Configured-to-order pricing for hybrid deployments commands 40-60% premiums over standard SaaS tiers due to data residency engineering and legacy directory integration. Subscription-based SaaS pricing dominates new contracts, with price differentiation driven by API call volume tiers and FIDO2 certification levels. Pricing pressure stems from venture-backed authentication vendors undercutting established platforms in mid-market segments. SMEs exhibit highest price sensitivity, prioritizing pre-built connectors over bespoke federation engineering.
Supply Chain Analysis
Just-in-time feature deployment through continuous integration pipelines characterizes cloud-native identity platforms, contrasting with strategic stockpiling of certified engineering talent by systems integrators. Supply concentrates in the United States, Germany, and Japan, drawing from specialized labor pools in Seattle, Frankfurt, and Tokyo. Raw material dependencies include cryptographic hardware modules, biometric sensor components, and API middleware licenses. Single-source vulnerability in FIDO2 authenticator chip supply creates concentration risk. Distribution runs through hyperscaler marketplaces and direct enterprise sales teams.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform economics in IAM Security Services are inflecting toward API-first unbundling, as enterprise buyers disaggregate authentication, authorization, and audit functions from monolithic suites. Interoperability demands from heterogeneous SaaS portfolios are accelerating this shift.
For Market Incumbents: Secure privileged access management moats through deeper mainframe and DevOps vaulting integration before cloud-native competitors replicate CyberArk's credential-rotation capabilities. Vertical integration into hardware security module manufacturing reduces FIDO2 authenticator supply exposure. Certification investment in EU AI Act conformity for biometric algorithms defends European financial services pricing power against emerging explainable-AI specialists. For New Entrants and Emerging Players: Mid-market customer identity and access management for healthcare SaaS vendors represents an under-served service-layer gap where Okta's enterprise focus creates whitespace. Target United States regional hospital systems with pre-configured HIPAA-compliant authentication bundles. API-first positioning against legacy directory synchronization tools enables rapid proof-of-concept conversion without engineering-heavy procurement cycles. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among privileged access management specialists with DevOps secrets vaulting capabilities, reflecting sticky credential-rotation workflows and cyber insurance underwriting dependencies. Acquisition target archetype: cloud-native authentication vendors with FIDO2-native architectures and healthcare vertical penetration. Watch NIST zero-trust deadline extensions as inflection indicator for federal procurement velocity.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unbundled API-first architectures enable precise capability sourcing across authentication, authorization, and audit layers. |
| Acquisition of Specialist Firm | Privileged access management depth in mainframe and DevOps vaulting commands sustained premium pricing power. |
| Strategic Partnership | Hyperscaler marketplace distribution extends reach to mid-market buyers avoiding identity engineering hiring bottlenecks. |
| Geographic Expansion | German sovereign cloud compliance and BSI technical guidelines sustain hybrid deployment premiums in EU regulated accounts. |
| Product Launch | FIDO2-native passwordless platforms capture financial services procurement driven by SEC cybersecurity disclosure rules. |
Study Parameters
Cross-validation between primary stakeholder interviews and secondary regulatory filings anchors the qualitative findings in this analysis. Conversations with CISOs, identity engineering directors, cloud procurement officers, and healthcare compliance leads inform deployment model preferences and vendor selection criteria. Secondary sources include NIST cybersecurity framework updates, FDA premarket guidance documents, SEC disclosure filings, and hyperscaler identity service roadmaps. Bottom-up contract value aggregation and top-down market sizing triangulate volume estimates.
Sensitivity analysis across deployment model adoption curves, zero-trust mandate compliance timelines, and certified talent availability shapes the analytical framework. Segmentation dimensions modeled encompass service type, deployment architecture, organization scale, and industry vertical regulatory exposure. CAGRs derive from weighted scenario analysis of cloud displacement rates against legacy on-premises retention in regulated verticals. Inputs include cyber insurance underwriting requirement diffusion and EU AI Act biometric provision implementation pacing.
Forecasts assume regulatory continuity in NIST, HIPAA, and EU AI Act enforcement regimes; material policy shifts would require re-modeling. Revision becomes warranted when federal zero-trust deadline extensions or sovereign cloud mandate relaxations cross implementation thresholds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Sound Masking Systems Market
Security Software
Parental Control Software Market
Security Software
Network Security Appliance Market
Security Software
Certification Authority Market
Security Software
Saudi Arabia Managed Security Services Market
Security Software
Global Data Loss Prevention Software Market
Security Software
Stalkerware Market
Security Software
Asia-Pacific Smart Doorbell Market
Security Software
Network Video Recorder (NVR) Market
Security Software
Security Software for Consumers Market
Security Software
North America Secure Access Service Edge Market
Security Software
Security Information and Event Management (SIEM) Market
Security Software
Endpoint Security Solutions Market
Security Software
Global Digital Signature Software Market
Security Software
Hardware OTP Token Authentication Market
Security Software
Confidential Computing Market