
 Software Assurance Market | 2026-2036
Software Assurance Market Size, Share, and Industry Trends Forecast 2026-2036
Software Assurance Market Analytics
The gap between premium enterprise-grade assurance and commodity automated scanning is recalibrating competitive dynamics across the sector. Accenture leverages its global consulting footprint to bundle governance consulting with continuous validation services. IBM anchors its position through proprietary AI-driven threat modeling platforms integrated with hybrid cloud infrastructure. Wipro differentiates by specializing in sector-specific compliance frameworks for regulated industries.
Software assurance encompasses systematic verification, validation, and governance processes that ensure code integrity, security posture, and regulatory adherence throughout the software development lifecycle. The discipline employs static and dynamic analysis tools, fuzz testing protocols, and formal verification methods to detect vulnerabilities before production deployment. Cloud-based deployment models now lead expansion as organizations migrate security operations to scalable, API-native platforms. Managed services represent the fastest-growing delivery format, capturing margin pools through recurring subscription structures and shared-risk outcome models. On-premise installations retain dominance in defense and classified government environments where data sovereignty requirements prohibit external hosting.
The US Federal Risk and Authorization Management Program (FedRAMP), the European Union's Cyber Resilience Act, and ISO/IEC 27001 standards collectively determine market access thresholds and product certification requirements for cross-border service delivery. FedRAMP authorization functions as a de facto gate for federal procurement, while the EU Cyber Resilience Act imposes mandatory security update obligations and conformity assessment procedures on all software placed on the European market. Stakeholders must monitor divergence between US executive-branch zero-trust mandates and EU harmonized standards to avoid compliance architecture fragmentation.
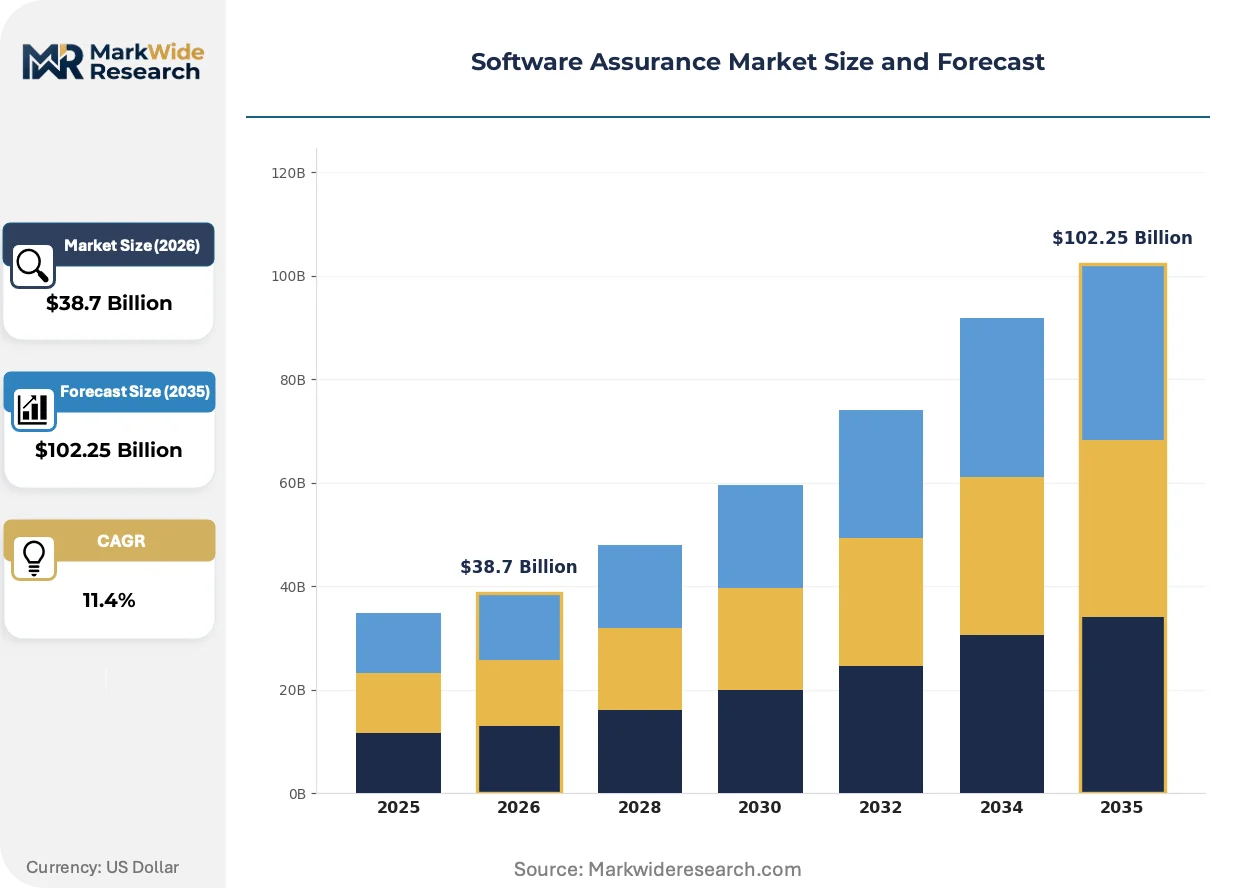
Market Dynamics
Zero-trust architecture mandates from US federal agencies and the European Cyber Resilience Act are compressing procurement cycles while forcing vendors to embed continuous validation into DevSecOps pipelines. This dual regulatory pressure is restructuring how assurance services bundle with cloud infrastructure.
Growth Catalysts
- FedRAMP Authorization Requirements:US government contractors must obtain standardized security certifications before federal cloud procurement, creating captive demand for authorized assurance providers.
- Financial Services:Banks and payment processors face intensified regulatory scrutiny, driving investment in automated compliance verification and continuous monitoring systems.
- API-Native Platforms:Cloud-based deployment models enable scalable security operations, allowing enterprises to shift capital expenditure to operational subscription structures.
Market Restraints
- Specialized Talent Scarcity:Shortages of professionals trained in formal verification methods and fuzz testing protocols constrain service delivery capacity.
- Defense Sector Data Sovereignty:Classified environments in the United States and allied nations prohibit external hosting, limiting cloud-native solution penetration.
- Fragmented Standards:Divergence between US zero-trust mandates and EU harmonized compliance frameworks forces vendors to maintain dual certification architectures.
Strategic Opportunities
- India's Digital Infrastructure:The country's expanding software export sector and RBI cybersecurity guidelines create demand for ISO/IEC 27001 certification services.
- Convergence of AI and Static Analysis:Machine learning integration with traditional code scanning is opening new vulnerability detection capabilities in embedded systems.
- Managed Service Subscriptions:Shared-risk outcome models allow assurance providers to capture recurring revenue through continuous validation rather than episodic consulting.
Industry Challenges
- Legacy System Integration:Mainframe and COBOL environments in government and financial institutions resist automated scanning tool deployment.
- Certification Timeline Compression:FedRAMP authorization processes averaging 12-18 months delay revenue recognition and strain working capital.
- Cross-Border Data Transfer Rules:GDPR restrictions on EU personal data processing complicate centralized security operations for multinational clients.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Software Assurance Market |
| Market Size in 2026 | $38.7 Billion |
| Market Size in 2035 | $102.25 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Code Review, Vulnerability Assessment, Compliance Management, Penetration Testing Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Service End User: SMBs, Enterprises, Government Agencies, Educational Institutions Industry Vertical: Finance, Healthcare, Retail, Telecommunications |
| Companies Covered | Infosys, Capgemini, Deloitte, Wipro, HCLTech, Accenture, Cognizant, EPAM, IBM, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Software Assurance Market Evolving Landscape
Software assurance is pivoting from episodic audit cycles to continuous validation embedded within CI/CD pipelines. This shift demands new tooling architectures and service delivery models.
Software Bill of Materials (SBOM) generation and verification is decentralizing supply chain risk management across enterprise technology stacks. Automotive and medical device manufacturers now require component-level traceability from tier-three suppliers. This transparency mandate is compressing liability exposure while expanding the addressable market for composition analysis tools.
The EU Cyber Resilience Act imposes mandatory security update obligations and conformity assessment procedures on all software placed on the European market. Hardware manufacturers must now certify firmware and embedded code before CE marking authorization. German automotive suppliers and French industrial automation vendors are restructuring quality assurance departments to accommodate recurring certification audits.
Enterprise buyers are unbundling assurance from systems integration contracts and sourcing validation services through specialized cybersecurity marketplaces. This disintermediation favors pure-play assurance vendors over bundled consulting offerings. The pattern is most visible in United States federal contracting, where FedRAMP-authorized vendors now compete directly against traditional systems integrators for standalone validation work.
Software Assurance Market Segmentation
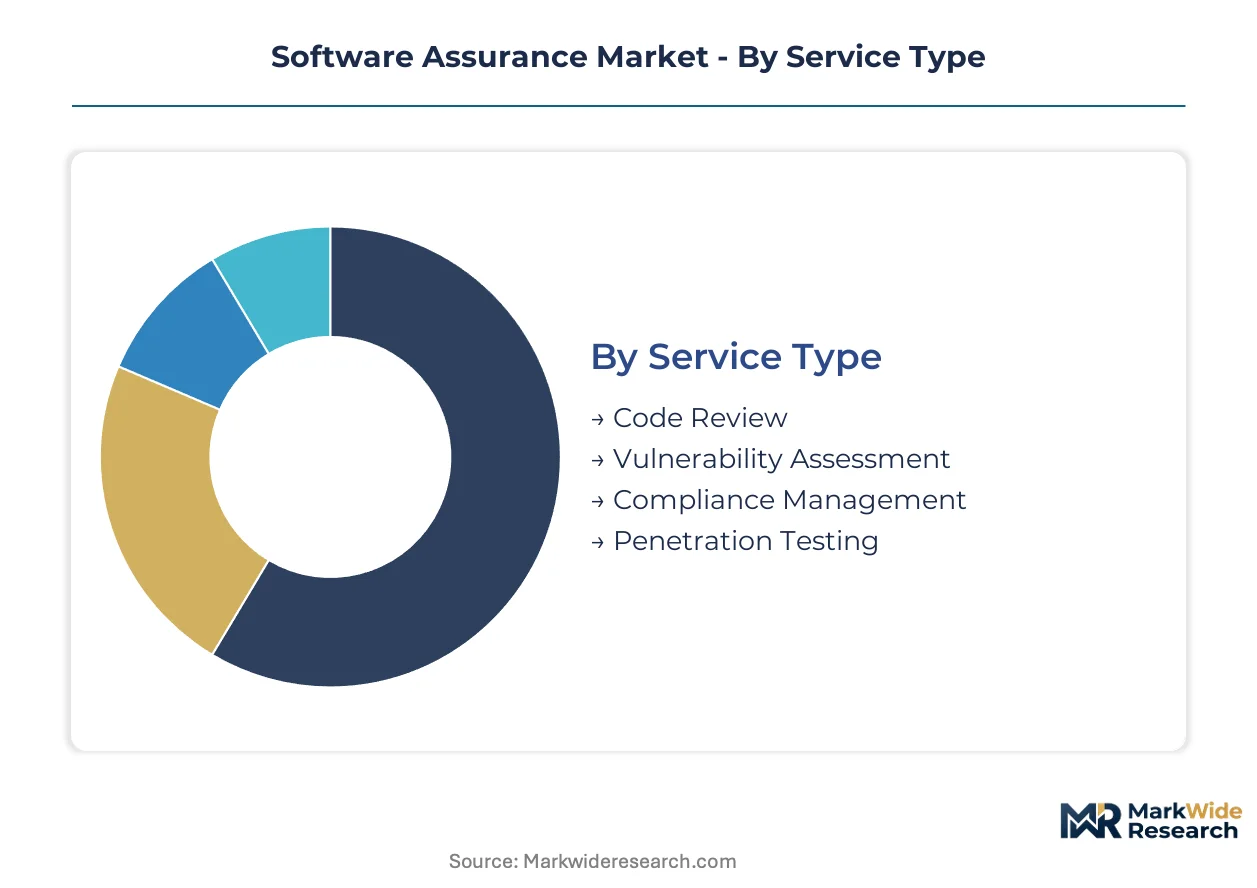
Software assurance segmentation reveals how capital allocation, compliance mandates, and operational constraints reshape procurement patterns across service delivery formats. Understanding these divisions exposes where margin pools concentrate and which infrastructure investments unlock market access.
Service Type:
Capital intensity varies sharply across service categories, with automated tooling platforms demanding substantial R&D investment while human-intensive offerings require working capital for talent acquisition.
- Code Review:Systematic manual and automated examination of source code to identify logic errors, security flaws, and maintainability issues. Demand concentrates among US federal contractors facing FedRAMP authorization deadlines, where embedded validation in CI/CD pipelines has become non-negotiable.
- Vulnerability Assessment:Automated scanning and manual verification protocols that catalog exploitable weaknesses across applications and infrastructure. Financial services firms in Frankfurt and Singapore drive expansion, compelled by ECB and MAS operational resilience mandates to maintain continuous monitoring postures.
- Compliance Management:Governance frameworks ensuring adherence to ISO/IEC 27001, GDPR, and sector-specific regulations through policy automation and audit preparation.
- Penetration Testing:Simulated adversarial attacks evaluating defensive controls through ethical exploitation techniques.
Most installed capacity flows through Code Review. Expansion is steepest in Vulnerability Assessment.
Deployment Model:
Customer risk tolerance and data sovereignty requirements partition the market between capital-heavy on-premise installations and recurring-revenue cloud subscriptions.
- Cloud-Based:API-native platforms delivering scalable security operations through multi-tenant SaaS architectures. US federal agencies and German automotive suppliers lead adoption, with FedRAMP authorization and EU Cyber Resilience Act compliance forcing migration from legacy tooling.
- Managed Service:Third-party operated assurance functions delivered through shared-risk outcome models with recurring subscription structures. British banking consortia and Australian healthcare networks favor this format, outsourcing continuous validation to specialized providers.
- On-Premise:Self-hosted installations maintaining complete data control within organizational perimeter defenses.
- Hybrid:Distributed architectures combining cloud scalability with on-premise control for sensitive workloads.
Revenue concentrates in Cloud-Based delivery. The steepest expansion trajectory belongs to Managed Service.
End User:
Procurement sophistication and compliance exposure create distinct service tiers across organizational scale and regulatory burden.
- Government Agencies:Federal, state, and municipal entities subject to mandatory security certification frameworks. US defense contractors and EU member state administrations dominate demand, with FedRAMP and NIS2 Directive requirements compressing vendor selection criteria.
- Enterprises:Large organizations with complex multi-cloud environments and global regulatory obligations. Japanese automotive manufacturers and Swiss pharmaceutical firms invest heavily, driven by UN R155 vehicle cybersecurity regulations and FDA software validation expectations.
- SMBs:Mid-market organizations adopting standardized assurance packages through channel partners.
- Educational Institutions:Universities and research facilities managing open-source dependencies and research data protection.
Contract value peaks with Government Agencies. Enterprise segment expansion is gaining share fastest.
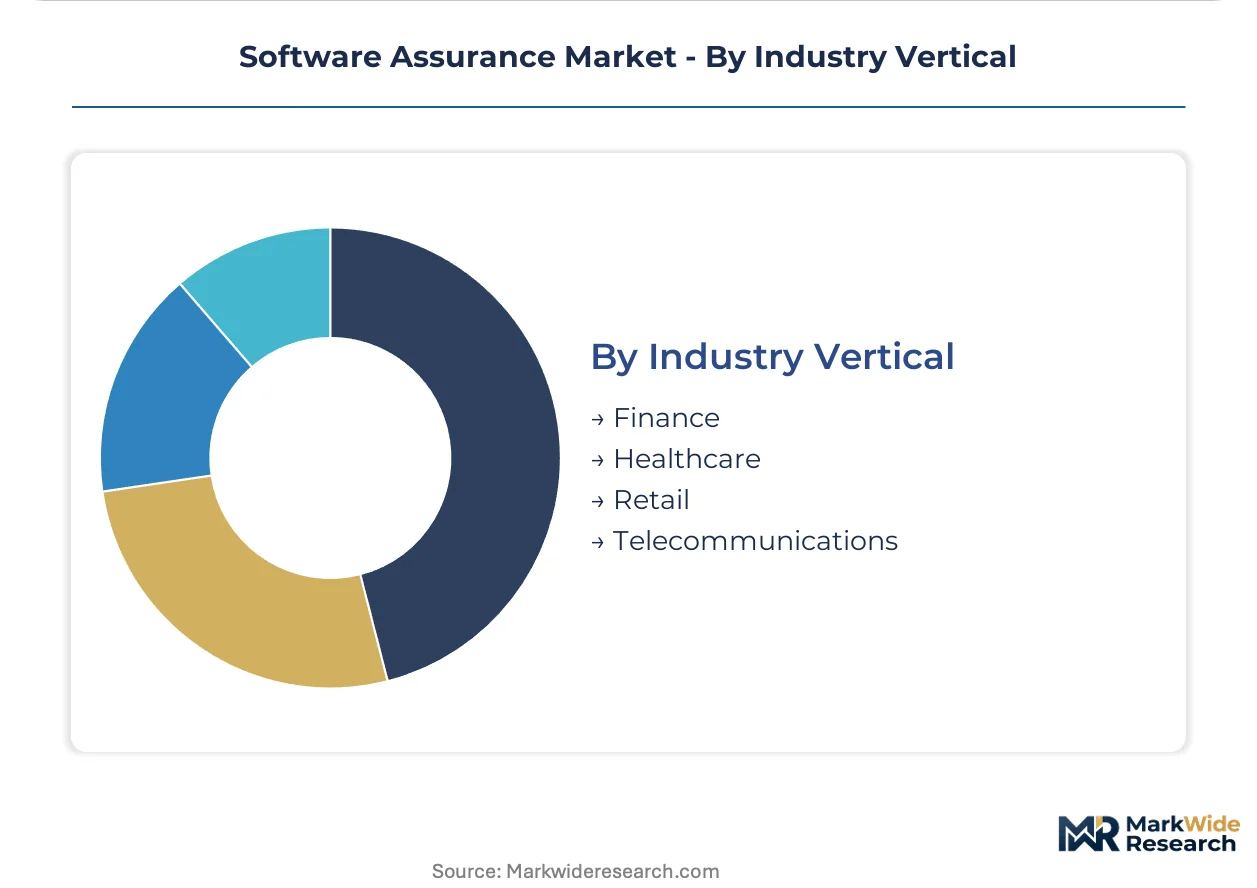
Industry Vertical:
Regulatory density and liability exposure determine willingness to pay for assurance depth across sectors.
- Finance:Banks, insurers, and payment processors facing intensified supervisory scrutiny. US regional banks and EU systemic institutions drive investment, responding to DORA implementation timelines and SEC cybersecurity disclosure rules.
- Healthcare:Providers, payers, and medical device manufacturers managing protected health information and FDA software validation. German hospital networks and US health systems expand procurement, constrained by HIPAA enforcement and EU MDR software classification requirements.
- Retail:E-commerce platforms and physical merchants defending payment card ecosystems and customer data.
- Telecommunications:Network operators and equipment vendors securing critical infrastructure against supply chain compromise.
Finance captures the largest assurance budgets. Healthcare is climbing the fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States federal procurement dwarfs European government spending on assurance services, while India's software export sector generates faster organic growth than established Western markets.
United States
FedRAMP authorization mandates and zero-trust architecture directives from the Office of Management and Budget dominate federal contractor procurement. The Cybersecurity and Infrastructure Security Agency continuously revises baseline controls, compressing vendor qualification timelines. Washington DC metro and Northern Virginia data center clusters host the densest concentration of authorized cloud assurance providers serving intelligence and defense communities.
Germany
Automotive suppliers and industrial automation vendors drive embedded software certification demand under EU Cyber Resilience Act implementation timelines. The Kraftfahrt-Bundesamt enforces UN R155 vehicle cybersecurity regulations with mandatory type approval processes. Stuttgart's automotive engineering corridor and Munich's industrial software cluster host specialized assurance practices focused on functional safety and firmware validation.
United Kingdom
Financial services operational resilience rules from the Prudential Regulation Authority mandate continuous third-party risk monitoring. The National Cyber Security Centre operates certification schemes for assured service providers handling government data. London's fintech concentration and Edinburgh's banking headquarters generate concentrated demand for managed detection and response capabilities.
India
Reserve Bank of India cybersecurity guidelines and SEBI mandate compliance investments across banking and capital markets. Software Technology Parks of India and Special Economic Zone incentives attract multinational assurance delivery centers. Bengaluru's technology corridor and Hyderabad's IT cluster export ISO/IEC 27001 certification services to North American and European clients.
Japan
Ministry of Economy, Trade and Industry guidelines on software supply chain security reshape procurement for critical infrastructure operators. The Personal Information Protection Commission enforces strict data handling standards affecting cross-border assurance service delivery. Tokyo's enterprise software district and Osaka's manufacturing technology base concentrate domestic demand for embedded systems validation.
Software Assurance Market Competitive Landscape
Top-tier vendors anchor federal and financial services verticals, while mid-tier specialists capture share in regulated industries through sector-specific compliance expertise. The market structures around three distinct archetypes: global consulting conglomerates bundling governance with technical validation, pure-play cybersecurity firms offering continuous monitoring subscriptions, and systems integrators embedding assurance into cloud migration contracts. Dominant competitive moves include strategic partnerships with hyperscale cloud providers and vertical integration into managed detection and response operations.
Within the global consulting tier, Accenture and Deloitte exemplify the bundled service model combining governance consulting with continuous validation infrastructure. IBM occupies a position at the intersection of proprietary AI tooling and hybrid cloud integration. Wipro and HCLTech represent the India-headquartered delivery archetype, leveraging scale advantages in code review and vulnerability assessment services for North American and European clients.
| Leading Market Players |
|---|
| Infosys |
| Capgemini |
| Deloitte |
| Wipro |
| HCLTech |
| Accenture |
| Cognizant |
| EPAM |
| IBM |
| Others |
Value Network & Pricing Analysis
FedRAMP-authorized government contractors concentrate procurement power and force vendors toward subscription-based recurring revenue models rather than project-based consulting fees. This buyer archetype dominance compresses margins for episodic penetration testing while elevating premiums for continuous validation services embedded in DevSecOps pipelines.
Pricing Analysis
Bundled governance-consulting offerings from global integrators command premium fees against unbundled pure-play validation services now sold through cybersecurity marketplaces. Three-tier pricing structure across premium, standard, and economy levels reflects certification depth, with FedRAMP High authorizations fetching multiples over Moderate baselines. Cost compression in commodity automated scanning stems from open-source tool proliferation and hyperscaler bundling. SMBs through channel partners exhibit highest price sensitivity; defense contractors facing mandatory authorization deadlines show lowest.
Supply Chain Analysis
Regional distribution centers in Northern Virginia, Stuttgart, and Bengaluru anchor hub-and-spoke delivery patterns for assurance services. Talent supply concentrates in India, Poland, and the United States for code review and vulnerability assessment capacity. Service delivery draws from cloud infrastructure subscriptions, proprietary AI tooling licenses, and certified personnel pipelines. Single-source vulnerability in specialized formal verification expertise constrains scaling. Distribution runs through direct enterprise sales, hyperscaler marketplaces, and specialized cybersecurity channel partners.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a geographic-arbitrage play where Indian delivery centers capture margin pools from North American compliance mandates while European regulatory divergence inflates certification costs for vendors lacking localized presence.
For Market Incumbents: Lock in FedRAMP authorization moats before timeline compression accelerates, and deepen backward integration into AI-driven static analysis engines to defend against pure-play automation vendors eroding consulting attach rates. Certification investment in EU Cyber Resilience Act conformity assessment procedures offers channel control leverage against unbundled competitors. For New Entrants and Emerging Players: Cloud-native managed service providers represent the most penetrable channel partner type for white-space entry. Target mid-market financial services firms in secondary US metro areas underserved by federal-contractor-heavy incumbents, and pursue ISO/IEC 27001 certification services for India's software export sector as the lowest-friction go-to-market angle. For Investors and Strategic Acquirers: Hyperscale cloud providers are the most active acquirer in this space, seeking continuous validation capabilities to embed in platform marketplaces. Over a multi-year horizon, vendors with embedded systems expertise for automotive and medical device verticals offer superior viability against commodity scanning automation. Watch for divergence between US executive-branch zero-trust implementation velocity and EU harmonized standard adoption as the critical inflection signal.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Investment | Unlocks federal procurement access through CISA-validated security controls. |
| AI-Static Analysis Integration | Machine learning enhances embedded systems vulnerability detection beyond rule-based scanning. |
| EU Cyber Resilience Act Compliance | Mandatory conformity assessment creates recurring certification revenue from hardware manufacturers. |
| Managed Service Subscription Pivot | Shared-risk outcome models capture recurring revenue from British banking consortia outsourcing. |
| India Delivery Center Expansion | RBI cybersecurity guidelines and SEZ incentives attract multinational assurance operations. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window. Primary fieldwork engaged CISOs at financial institutions, federal procurement officers, DevSecOps platform engineers, and channel partners at hyperscaler marketplaces. Secondary validation drew from FedRAMP authorization databases, SEC cybersecurity disclosure filings, EU Cyber Resilience Act implementation guidance, and RBI circulars. Bottom-up service revenue estimates triangulated against top-down compliance spend projections.
Comparable historical periods anchored the projection horizon across multi-year modeling. Segmentation dimensions spanned deployment model, organization scale, vertical regulatory density, integration complexity, and regional adoption pattern. CAGRs derived from fitted growth curves calibrated to authorization timeline data and cloud migration velocity indicators. Forecast inputs incorporated FedRAMP pipeline backlogs, EU NIS2 Directive implementation schedules, and software export growth from Indian technology corridors.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to regulatory divergence between US zero-trust mandates and EU harmonized standards, plus talent scarcity in formal verification methods. Outputs reflect documented assumptions around authorization timeline compression and cloud migration rates. Decision-makers should treat outputs as directional within the stated assumption set.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Employee Fraud Detection Market
Security Software
Secure Email Gateway Market
Security Software
Global Electronic Passports Market
Security Software
Global Runtime Application Self-Protection Market
Security Software
Certification Authority Market
Security Software
Disk Encryption Software Market
Security Software
Global Anti-Spam Software Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Italy Endpoint Detection and Response Market
Security Software
Personal Data Recovery Software Market
Security Software
Global Privileged Access Management (PAM) Solutions Market
Security Software
Global Electronic Offender Monitoring Solutions Market
Security Software
Embedded Security Market
Security Software
Public Cloud Management and Security Services Market
Security Software
Europe Video Management System Market
Security Software
ATM Security Market