
 Nordics Cybersecurity Market | 2026-2036
Nordics Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Nordics Cybersecurity Market Analytics
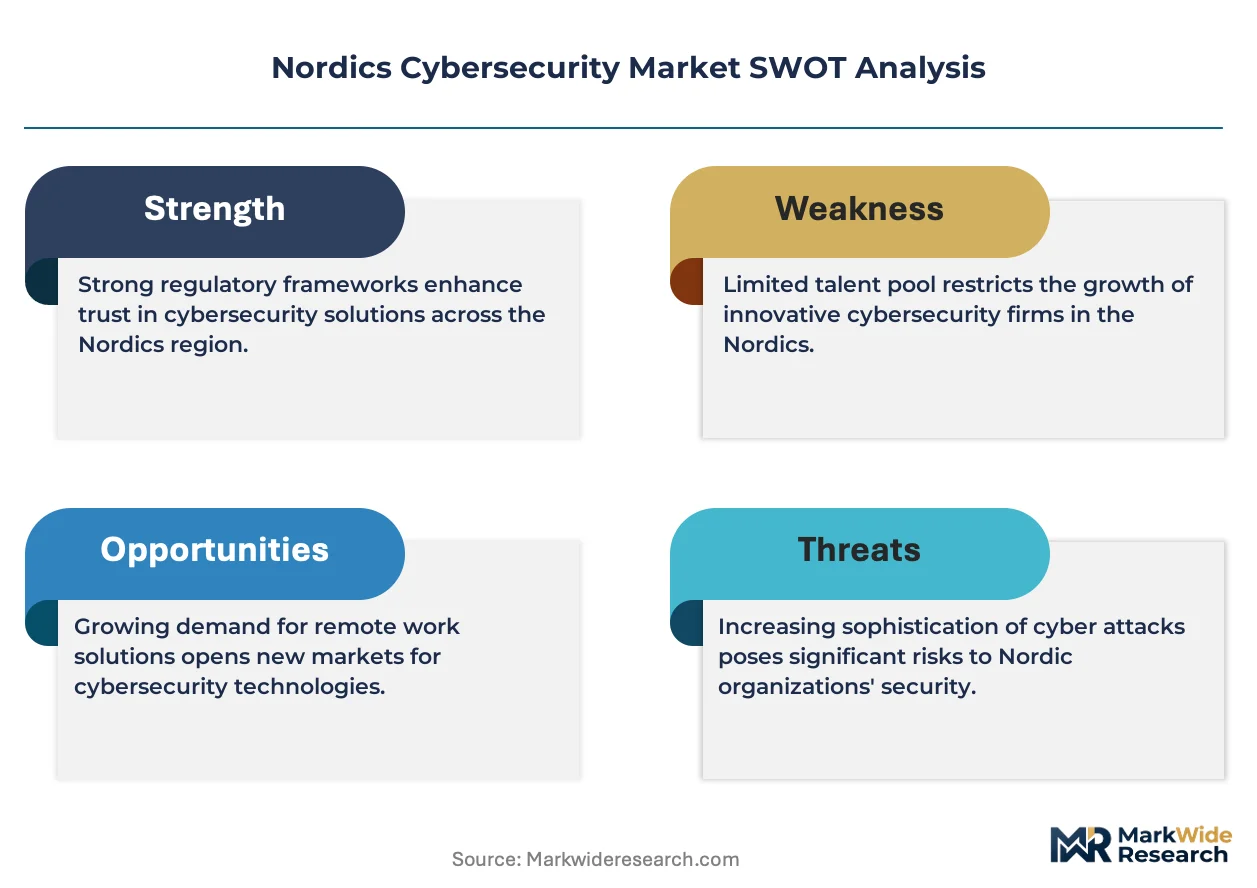
Enterprise-grade zero-trust architecture is rotating through Nordic boardrooms as the baseline procurement standard rather than a premium add-on. Cisco Systems, Inc. leverages its established networking installed base to bundle security controls into existing infrastructure contracts across Scandinavian telcos and energy utilities. WithSecure Corporation anchors its competitive position through deep specialization in European data sovereignty requirements and localized threat intelligence. Palo Alto Networks, Inc. competes by extending its platform consolidation pitch to mid-market enterprises seeking to reduce vendor sprawl.
Nordics cybersecurity encompasses the technologies, services, and governance frameworks that protect digital assets, networks, and data across interconnected enterprise, government, and cloud environments, typically integrating encryption protocols, behavioral analytics, and automated threat response with mean-time-to-detect targets measured in minutes. Its primary purpose is to ensure operational continuity, regulatory compliance, and data integrity for organizations operating within or across Denmark, Finland, Iceland, Norway, and Sweden. Cloud Security commands expanding budget allocation as Nordic enterprises migrate remaining on-premises workloads to distributed cloud architectures, while Endpoint Security retains foundational status due to persistent remote and hybrid work patterns. Network Security margin pools concentrate in managed detection and response services tailored to operational technology environments, particularly among Nordic manufacturing and maritime logistics firms.
EU NIS2 Directive enforcement through national regulators in Denmark, Finland, Norway, and Sweden is expanding mandatory security audit scopes and tightening incident reporting timelines for critical infrastructure operators. GDPR continues shaping data localization requirements, pushing Nordic enterprises toward EU-sovereign cloud deployments and encryption key management strategies that limit third-country data exposure. Stakeholders must monitor how Sweden's and Finland's NATO accession reshapes national security classifications and cross-border data sharing protocols for defense-adjacent technology suppliers.
Market Dynamics
EU NIS2 Directive enforcement is compressing procurement cycles across Nordic critical infrastructure as operators race to meet mandatory incident reporting timelines and supply chain audit requirements before national transposition deadlines.
Growth Catalysts
- Cloud Migration Acceleration:Swedish hyperscale data center clusters in Stockholm-Uppsala are drawing Nordic enterprises away from on-premises infrastructure, creating sustained demand for cloud-native security controls and encryption key sovereignty solutions.
- NATO Accession Security Reclassification:Sweden's and Finland's NATO membership is elevating national security classifications for defense-adjacent technology suppliers, mandating stricter cross-border data sharing protocols and encrypted communications standards.
- Operational Technology Convergence:Maritime logistics and manufacturing firms across Norway and Denmark are integrating IT-OT security fabrics, expanding managed detection and response services into industrial control environments previously air-gapped from enterprise networks.
Market Restraints
- Specialized Talent Scarcity:The shallow pool of Nordic professionals holding both EU security clearance and cloud architecture certifications is inflating implementation timelines and service delivery costs for zero-trust deployments.
- Data Localization Hardware Premium:GDPR-mandated EU-sovereign cloud deployments require dedicated physical infrastructure, adding 15-25% capital overhead compared to global hyperscale alternatives for equivalent compute capacity.
- Legacy Protocol Entrenchment:Decades-old SCADA and maritime navigation systems across Finnish and Norwegian critical infrastructure resist seamless API integration with modern security orchestration platforms.
Strategic Opportunities
- Icelandic Data Center Expansion:Iceland's geothermal-powered, naturally cooled facilities are attracting Nordic and continental European enterprises seeking carbon-neutral compute with embedded encryption-at-rest capabilities.
- Quantum-Resistant Cryptography Mandates:Swedish and Finnish defense procurement guidelines are beginning to specify post-quantum encryption standards, creating first-mover advantage for vendors with NIST-compliant algorithm portfolios.
- Consolidated Platform Displacement:Mid-market enterprises across Denmark are abandoning point-solution stacks in favor of unified security platforms, opening wallet share for vendors with integrated SASE and XDR offerings.
Industry Challenges
- Multi-Framework Compliance Burden:Operators must simultaneously satisfy EU NIS2 incident reporting, GDPR data breach notification, and national critical infrastructure regulations with conflicting timeline requirements.
- OT-IT Skill Bridging:Security teams lack personnel conversant in both industrial control system protocols and cloud-native threat hunting, forcing expensive contractor reliance for hybrid environment monitoring.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Nordics Cybersecurity Market |
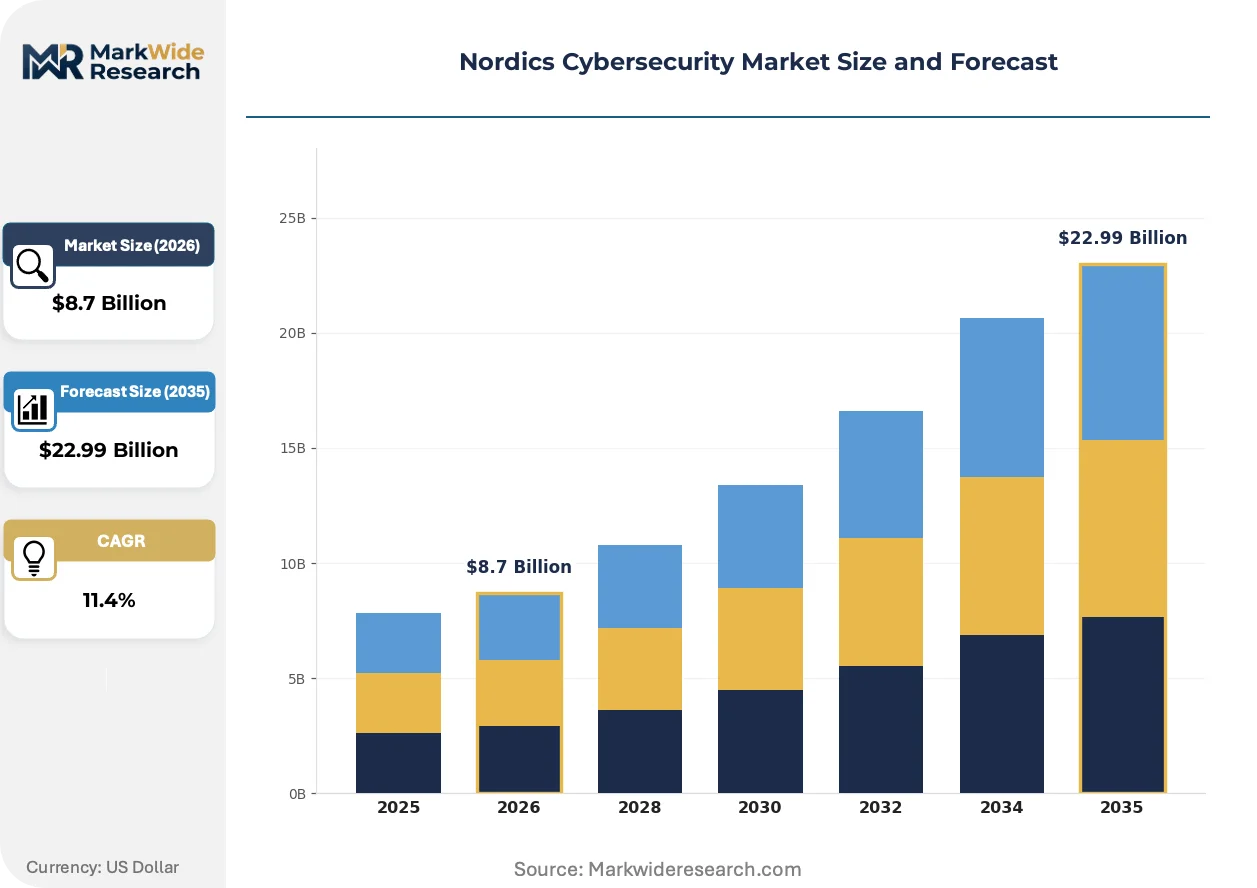
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $22.99 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
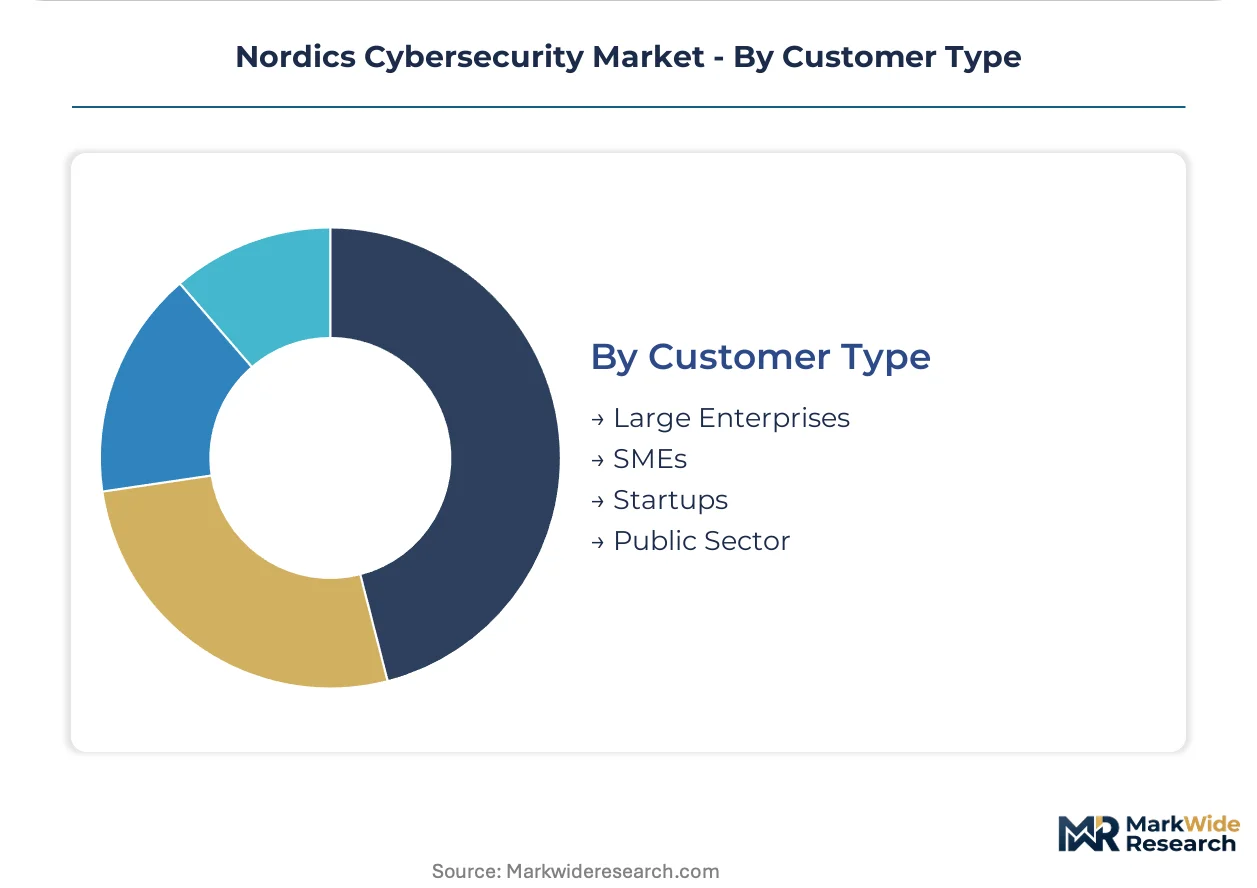
| Segmentation | Product Type: Endpoint Security, Network Security, Application Security, Cloud Security Deployment Model: On-premises, Cloud-based, Hybrid, Managed Services Industry Vertical: Finance, Healthcare, Retail, Government Customer Type: Large Enterprises, SMEs, Startups, Public Sector |
| Companies Covered | International Business Machines Corporation, Cisco Systems, Inc., Fortinet, Inc., WithSecure Corporation, Dell Technologies Inc., Palo Alto Networks, Inc., CrowdStrike Holdings, Inc., Clavister Holding AB, Logpoint, Others |
| Regions Covered | Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Nordics Cybersecurity Market Evolving Landscape
Security architecture is converging around identity-centric perimeter models that treat every access request as untrusted, compressing the attack surface across distributed Nordic workforces and multi-cloud estates.
Extended detection and response platforms are miniaturizing sensor deployment footprints to accommodate containerized microservices and serverless architectures prevalent in Swedish fintech development pipelines. Copenhagen-based neobanks and Oslo payment processors are adopting these lightweight agents within CI/CD workflows, embedding security telemetry directly into build processes. This compression is collapsing the traditional gap between development velocity and security review cycles.
EU AI Act implementation through Danish and Finnish national regulators is classifying certain cybersecurity automation tools as high-risk AI systems, mandating conformity assessments and human oversight protocols for automated threat response decisions. Industrial operators deploying autonomous SOAR playbooks must now document algorithmic decision trails and maintain human-in-the-loop capabilities for critical infrastructure protection. Maritime logistics firms in Norway are restructuring security operations centers to satisfy these oversight requirements.
Enterprise buyers are unbundling managed security service contracts, separating detection engineering from incident response retainers and threat intelligence subscriptions. Danish energy utilities and Finnish healthcare providers are negotiating these components through distinct RFP processes, pressuring vendors to demonstrate standalone value propositions for each service layer. This fragmentation is most pronounced among organizations with mature internal SOC capabilities seeking specialized external augmentation rather than full outsourcing.
Nordics Cybersecurity Market Segmentation
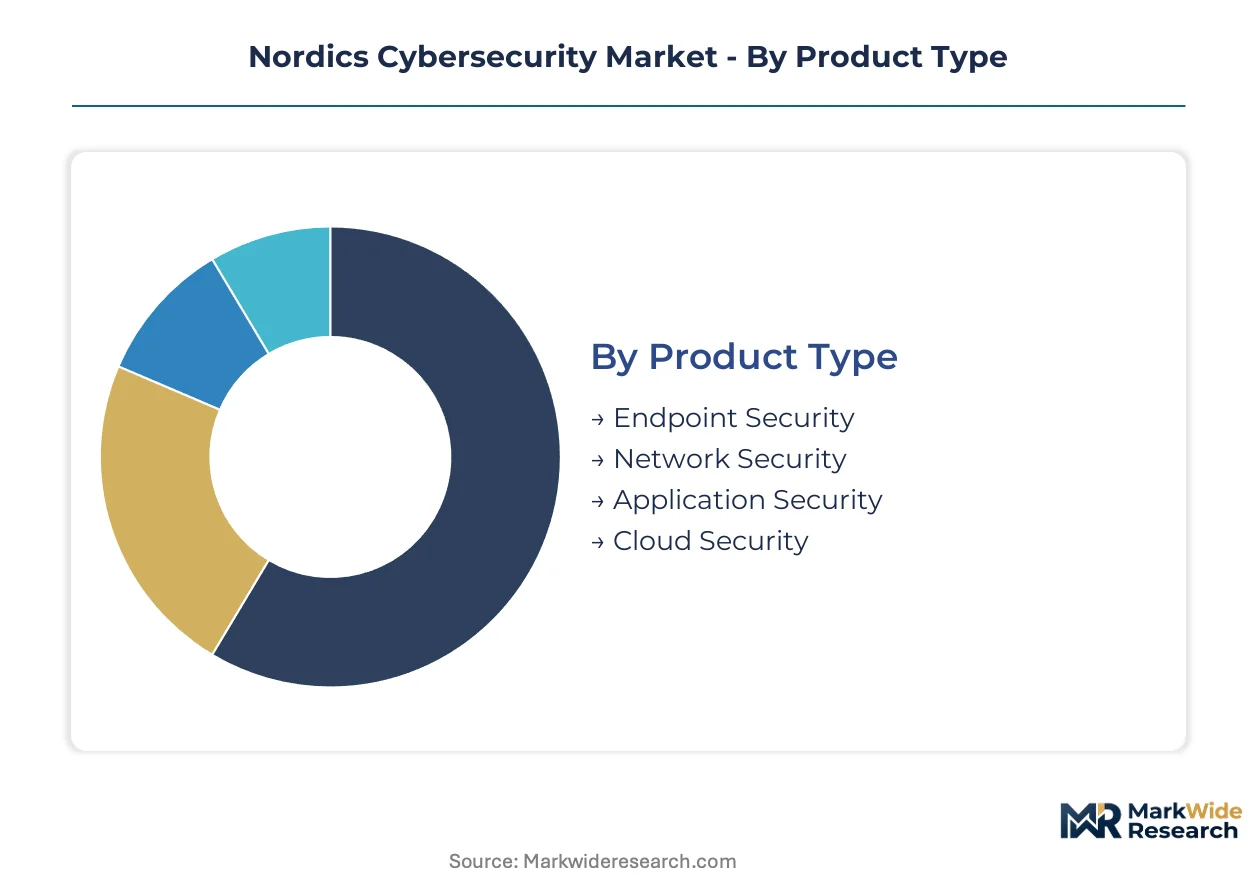
Nordic procurement teams evaluate cybersecurity solutions through multiple lenses simultaneously. Product architecture, operational constraints, and regulatory exposure each filter vendor shortlists differently across Danish fintechs, Swedish industrial operators, and Norwegian maritime logistics firms.
Product Type:
Channel mix varies sharply by product complexity. Cloud-native solutions flow through hyperscaler marketplaces and direct vendor relationships, while network security hardware maintains systems integrator dominance.
- Cloud Security:Native controls for distributed cloud architectures including encryption key sovereignty and containerized workload protection. Swedish hyperscale clusters in Stockholm-Uppsala concentrate demand as enterprises migrate from on-premises estates. EU NIS2 Directive enforcement accelerates procurement for automated compliance telemetry.
- Endpoint Security:Agent-based protection for distributed devices with behavioral analytics and automated threat containment. Persistent hybrid work patterns across Danish and Finnish enterprises sustain foundational budget allocation despite platform consolidation trends.
- Network Security:Perimeter and segmentation controls for enterprise traffic flows. Maritime logistics firms in Norway deploy specialized variants for satellite-linked vessel communications.
- Application Security:Code scanning and runtime protection for software development pipelines. Copenhagen neobanks embed these tools within CI/CD workflows.
By volume, Endpoint Security leads. By growth pace, Cloud Security is expanding most quickly.
Deployment Model:
Cost tier stratification separates capital-intensive on-premises builds from operational expenditure models favored by mid-market enterprises.
- Cloud-based:Fully managed security controls delivered via SaaS architecture with elastic scaling. Swedish enterprises in the Stockholm-Uppsala corridor dominate consumption, driven by proximity to hyperscale data center clusters and GDPR-aligned data residency requirements.
- Managed Services:Outsourced security operations including SOC-as-a-service and threat hunting retainers. Norwegian manufacturing and Danish energy utilities favor this model to address specialized talent scarcity without internal capability builds.
- Hybrid:Split architectures preserving sensitive workloads on-premises while leveraging cloud analytics. Finnish defense-adjacent suppliers adopt this posture following NATO accession security reclassifications.
- On-premises:Dedicated hardware and software installations within customer facilities. Legacy protocol entrenchment in Finnish and Norwegian critical infrastructure sustains residual demand despite migration pressure.
Cloud-based deployments capture the largest share of new contract value. Hybrid architectures show the steepest expansion trajectory among regulated industries.
Industry Vertical:
Application context determines feature prioritization and compliance rigor across buyer segments.
- Government:Classified network protection and cross-border data sharing controls. Sweden's and Finland's NATO membership elevates encryption standards for defense-adjacent procurement.
- Finance:Real-time transaction monitoring and zero-trust architecture for digital payment rails. Scandinavian banking consortiums mandate API security and fraud detection at branch and cloud layers.
- Healthcare:Patient data protection with GDPR breach notification workflows. Finnish healthcare providers unbundle managed services to augment internal SOC capabilities.
- Retail:Point-of-sale protection and e-commerce platform defense. Danish merchants prioritize payment card industry compliance alongside EU NIS2 readiness.
Finance verticals generate the highest per-account contract values. Government segment spending is climbing the fastest following security reclassification mandates.
Customer Type:
Maturity and procurement sophistication divide the customer base into distinct engagement patterns.
- Large Enterprises:Complex multi-site deployments with dedicated security architecture teams. These buyers negotiate platform consolidation deals to reduce vendor sprawl across Nordic operations.
- Public Sector:Regulated procurement with mandatory incident reporting and supply chain audit requirements. National transposition of EU NIS2 Directive compresses implementation timelines.
- SMEs:Mid-market enterprises seeking unified security platforms without dedicated security personnel. Danish SMEs increasingly favor integrated SASE and XDR offerings.
- Startups:Early-stage companies with cloud-native infrastructure and limited security staffing. Stockholm-Uppsala tech corridor startups embed lightweight EDR agents within containerized development pipelines.
Large Enterprises dominate absolute spending. Public Sector procurement is gaining share fastest under regulatory compression.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Swedish buyers demonstrate the lowest price elasticity, absorbing 15-25% premiums for EU-sovereign cloud infrastructure, while Danish SMEs and Norwegian maritime operators drive harder bargains on managed service contracts. This demand-elasticity contrast shapes vendor go-to-market strategies across the Nordic cluster.
Sweden
Stockholm-Uppsala hyperscale data center clusters concentrate cloud security procurement as enterprises migrate from on-premises estates. The Swedish Post and Telecom Authority enforces EU NIS2 Directive transposition with compressed incident reporting timelines. Ericsson's home market sustains specialized demand for telecom-grade encryption and 5G network security controls.
Denmark
Copenhagen neobanks and payment processors anchor application security spending within CI/CD development pipelines. The Danish Business Authority mandates supply chain security audits for critical infrastructure operators under national NIS2 implementation. Odense robotics manufacturers integrate OT-security fabrics, expanding managed detection services into industrial control environments.
Norway
Oslo-based maritime logistics firms drive specialized network security demand for satellite-linked vessel communications and port automation systems. The Norwegian National Security Authority elevates cross-border data sharing protocols following NATO security reclassifications. Stavanger energy operators compress procurement cycles to meet mandatory audit deadlines.
Finland
Helsinki defense-adjacent technology suppliers face stricter encryption standards and classified network protection requirements post-NATO accession. The Finnish Transport and Communications Agency coordinates national cybersecurity center operations with EU incident response frameworks. Tampere manufacturing clusters resist legacy SCADA system modernization, sustaining hybrid security architecture demand.
Iceland
Reykjavik geothermal-powered data centers attract carbon-neutral compute demand from Nordic and continental European enterprises. The country's national regulator aligns data localization requirements with GDPR sovereign cloud mandates. Keflavik's positioning between North American and European fiber routes supports encryption-at-rest capabilities for latency-sensitive workloads.
Nordics Cybersecurity Market Competitive Landscape
Technology leadership and cost leadership are held by different player archetypes across the Nordic cybersecurity market. Platform consolidation vendors with integrated SASE and XDR portfolios capture mid-market wallet share, while specialized European data sovereignty providers defend premium positioning in regulated verticals. Three archetypes dominate: global platform consolidators bundling networking and security, regional specialists emphasizing GDPR-compliant architectures, and managed service providers addressing talent scarcity through outsourced SOC capabilities. Competitive moves concentrate on strategic partnerships with hyperscale cloud providers and portfolio diversification into OT-security fabrics for industrial clients.
Among Nordic-headquartered specialists, WithSecure Corporation and Clavister Holding AB exemplify the regional data sovereignty archetype, anchoring competitive positioning through deep specialization in European regulatory requirements and localized threat intelligence. Palo Alto Networks, Inc. and Cisco Systems, Inc. occupy the platform consolidation tier, leveraging established networking installed bases to bundle security controls into existing infrastructure contracts across Scandinavian telcos and energy utilities. These four entities represent the strategic positioning spectrum from regional compliance depth to global scale economics.
| Leading Market Players |
|---|
| International Business Machines Corporation |
| Cisco Systems, Inc. |
| Fortinet, Inc. |
| WithSecure Corporation |
| Dell Technologies Inc. |
| Palo Alto Networks, Inc. |
| CrowdStrike Holdings, Inc. |
| Clavister Holding AB |
| Logpoint |
| Others |
Value Network & Pricing Analysis
EU NIS2 Directive compliance certification gates vendor qualification for Nordic critical infrastructure procurement, simultaneously segmenting price tiers between audit-ready platform providers and point-solution specialists serving less regulated segments. This dual-gating mechanism concentrates pricing power among vendors with pre-established regulatory entrenchment while compressing margins for commodity security tools.
Pricing Analysis
Managed detection and response service contracts drive lifetime value through multi-year retainer renewals and incident response surge fees. Pricing stratifies across integrated SASE-XDR platforms, standalone endpoint agents, and specialized OT-security fabrics, with EU-sovereign cloud deployments commanding 15-25% premiums over global hyperscale alternatives. Cost compression in mid-market SaaS tiers is intensifying because Danish and Swedish SMEs are consolidating vendor stacks. Norwegian maritime operators exhibit the highest price sensitivity due to satellite bandwidth constraints, while Swedish government buyers absorb premiums for NATO-aligned encryption standards.
Supply Chain Analysis
Container availability through Rotterdam and Hamburg ports constrains hardware security module delivery timelines for Nordic data center deployments. Semiconductor fabrication concentrates in Taiwan, South Korea, and the United States, with encryption chip supply resting on advanced node production. Supply chain risk centers on single-source vulnerability for post-quantum cryptography components as Swedish defense procurement guidelines mandate NIST-compliant algorithms. Distribution runs through Stockholm-Uppsala hyperscaler clusters and Copenhagen systems integrators serving fintech and energy verticals.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a defensive-moat arena where regulatory entrenchment creates durable switching costs. EU NIS2 Directive compliance timelines and NATO security reclassifications erect qualification barriers that protect incumbent positions.
For Market Incumbents: Fortify platform consolidation positioning by embedding OT-security capabilities into existing networking contracts with Norwegian manufacturing and Danish energy utilities. Invest in EU-sovereign cloud certification to defend margin position against global hyperscale alternatives. Address emerging threat from specialized European data sovereignty providers through localized threat intelligence partnerships. For New Entrants and Emerging Players: Differentiate on quantum-resistant cryptography portfolios targeting Swedish and Finnish defense-adjacent suppliers. Penetrate Icelandic data center expansion wave through carbon-neutral compute positioning and encryption-at-rest specialization. Pursue channel partnerships with Stockholm-Uppsala hyperscaler clusters rather than direct enterprise sales. For Investors and Strategic Acquirers: Capital-intensity ratios are inflecting upward across managed security service operations due to specialized talent scarcity and 24/7 SOC infrastructure requirements. Target acquisition archetypes include regional OT-security specialists with maritime logistics expertise and GDPR-compliant cloud encryption vendors. Monitor NATO procurement guideline revisions as inflection signal for defense-adjacent technology supplier valuations.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Consolidation | Danish mid-market enterprises reduce vendor sprawl through unified SASE-XDR procurement. |
| OT-Security Fabric Integration | Norwegian maritime logistics firms embed IT-OT convergence into vessel automation systems. |
| EU-Sovereign Cloud Certification | Swedish hyperscale data centers meet GDPR localization mandates for continental European clients. |
| Post-Quantum Cryptography Investment | Finnish defense suppliers align with NIST algorithm standards in NATO procurement guidelines. |
| Managed Detection and Response Expansion | Icelandic geothermal facilities attract carbon-neutral SOC outsourcing from Nordic enterprises. |
Research Methodology
Initial hypotheses were tested against primary input from CISOs at Scandinavian banking consortiums, cybersecurity procurement officers at Danish energy utilities, OT-security architects at Norwegian maritime firms, and platform engineers at Swedish hyperscale data centers, then refined through secondary validation against SEC filings from listed security vendors, EU NIS2 Directive national transposition documents, NATO procurement guideline releases, and hyperscaler capex disclosures. Bottom-up segment sizing triangulated with top-down market envelope estimates.
Variance decomposition across deployment models, industry verticals, customer types, and regulatory compliance tiers structured the analytical framework over the projection horizon. CAGRs were derived from segment-level growth rate reconciliation against aggregate market expansion. Forecast inputs incorporated EU AI Act implementation timelines for automated threat response tools and Swedish-Finnish NATO accession security reclassification impacts on defense-adjacent supplier demand.
Material uncertainties — accelerated quantum computing breakthroughs, EU NIS2 enforcement variance across national regulators, and NATO data sharing protocol revisions — sit outside the modeled envelope. Forecasts reflect documented assumptions about regulatory stability and talent pool expansion. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
North America Extended Detection and Response Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Big Data Security Market
Cybersecurity
M2M Network Security Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Global Deep Packet Inspection (DPI) Market
Cybersecurity
Vietnam Cybersecurity Market
Cybersecurity
E-Mail Security Market
Cybersecurity
Germany Cybersecurity Market
Cybersecurity
Cognitive Security Market
Cybersecurity
Application Security Market
Cybersecurity
Data Center Logical Security Market
Cybersecurity
Advanced Malware Detection (AMD) Market