
 Germany Ransomware Protection Market | 2026-2036
Germany Ransomware Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Germany Ransomware Protection Market Insights
Germany is narrowing its cybersecurity capability gap through sovereign infrastructure investments and federal procurement programs. Secunet Security Networks AG leverages its BSI certification portfolio to anchor government contract pipelines. G Data CyberDefense sustains endpoint detection specialization through its Bochum-based malware research lab. Rohde & Schwarz Cybersecurity competes across classified networks with hardware-rooted encryption products.
Ransomware protection encompasses endpoint detection, network segmentation, cryptographic backup isolation, and automated incident response orchestration designed to interrupt kill chains before data exfiltration completes. The primary commercial purpose centers on operational continuity assurance against encryption-based extortion targeting critical infrastructure and intellectual property. Endpoint Protection dominates current procurement volumes among German SMEs confronting resource-constrained security operations. Cloud-Based deployment models capture the fastest expansion trajectory as Mittelstand firms migrate workloads to compliant sovereign cloud frameworks. Managed Security Services concentrate margin pools through recurring revenue structures and vendor consolidation incentives.
The BSI (Federal Office for Information Security) mandates baseline protection standards across KRITIS operators, while EU NIS2 transposition tightens incident disclosure windows to 24 hours for essential entities. GDPR enforcement by German state data protection authorities amplifies breach cost exposure, directly accelerating encryption and backup investment cycles. Stakeholders must monitor BSI technical guideline revisions and federal IT security procurement preference shifts to anticipate compliance-driven demand inflections.
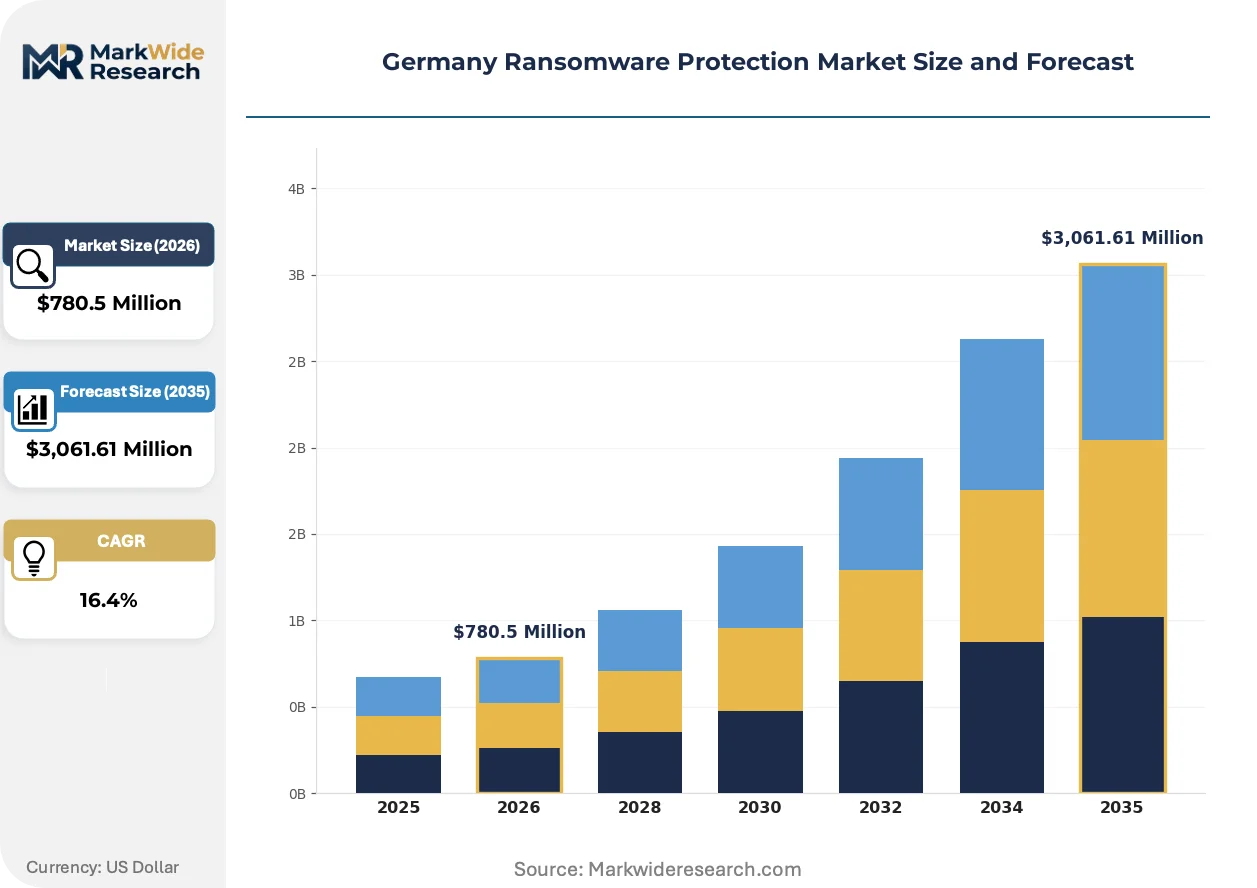
Market Dynamics
German ransomware protection procurement pivots on BSI-mandated baseline protection standards for KRITIS operators, compressing vendor selection cycles toward certified sovereign solutions while federal IT security procurement preferences favor domestic hardware-rooted encryption.
Growth Catalysts
- EU NIS2 Directive:The transposed 24-hour incident disclosure mandate for essential entities accelerates automated incident response orchestration investments across energy and transport operators.
- Automotive cybersecurity procurement:German OEMs confront encryption-based extortion targeting connected vehicle architectures, driving endpoint detection specialization for embedded systems.
- Sovereign cloud migration:Mittelstand firms in Bavaria and Baden-Württemberg migrate workloads to compliant frameworks, expanding cloud-based deployment demand for cryptographic backup isolation.
Market Restraints
- Certified talent scarcity:BSI-certified security architects command premium compensation, constraining SME security operations center staffing across eastern German states.
- Hardware-rooted encryption supply concentration:Domestic semiconductor packaging for trusted platform modules concentrates in Dresden and Munich corridors, creating single-source vulnerability.
- GDPR enforcement amplification:German state data protection authorities impose breach cost exposure that outpaces cyber insurance coverage limits, forcing self-insurance reserves.
Strategic Opportunities
- Underpenetrated healthcare networks:German hospital IT infrastructure retains legacy Windows architectures, creating endpoint protection white space for managed security services consolidation.
- Convergence of AI-driven threat hunting with confidential computing:Hardware-based enclaves enable encrypted data processing without decryption exposure, opening new product categories for research-intensive sectors.
- BSI technical guideline revisions:Anticipated updates to baseline protection standards will mandate network segmentation for additional critical infrastructure categories beyond current KRITIS scope.
Industry Challenges
- Integration complexity with operational technology:Manufacturing execution systems in automotive plants run on proprietary protocols that resist standard endpoint agent deployment without production downtime.
- Compliance timeline compression:EU NIS2 transposition deadlines force simultaneous security architecture redesign and documentation overhaul for mid-sized utilities with constrained IT budgets.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Germany Ransomware Protection Market |
| Market Size in 2026 | $780.5 Million |
| Market Size in 2035 | $3,061.61 Million |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Endpoint Protection, Network Security, Data Backup, Incident Response Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: SMEs, Large Enterprises, Government Entities, Educational Institutions Service Type: Consulting, Integration, Managed Security Services, Training |
| Companies Covered | Secunet Security Networks AG, G Data CyberDefense, Rohde & Schwarz Cybersecurity, Microsoft, Palo Alto Networks, Fortinet, CrowdStrike, Bitdefender, Check Point Software, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Germany Ransomware Protection Market Trends and Innovations
Extended detection and response platforms are compressing dwell-time metrics from months to hours, while sovereign infrastructure requirements reshape vendor qualification criteria across German federal procurement channels.
Confidential computing architectures utilizing hardware-based trusted execution environments are collapsing the traditional boundary between data-at-rest encryption and operational processing. German automotive suppliers with connected vehicle development pipelines adopt these enclaves for telemetry analysis without exposing raw driver data. The technology is collapsing liability frameworks that previously separated cloud providers from data controller responsibilities under GDPR.
The EU NIS2 Directive's transposition into German federal law imposes strict supply chain security vetting for critical infrastructure software procurement. Operators of energy distribution networks must now document third-party code provenance and maintain software bill of materials for all security-relevant components. German state regulators are enforcing these requirements through unannounced compliance audits with penalty structures tied to essential service continuity.
German Mittelstand procurement patterns favor subscription-based managed detection and response over perpetual license endpoint protection. Industrial machinery manufacturers in Stuttgart and Mannheim trade capital expenditure predictability for 24/7 security operations center coverage. This preference concentrates vendor relationships toward domestic providers with BSI certification and established federal contract performance records.
Germany Ransomware Protection Market Segmentation
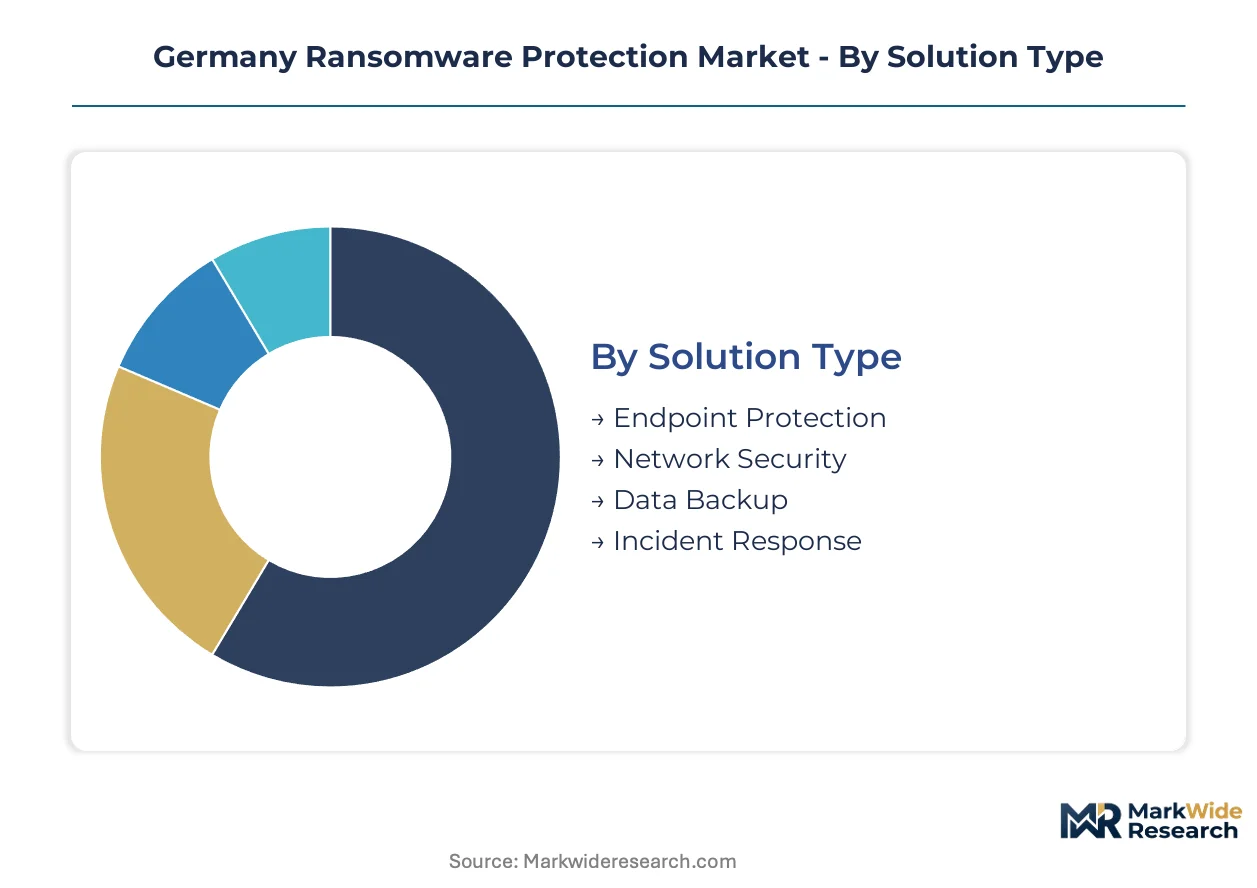
German ransomware protection procurement splits across four structural dimensions that determine vendor qualification, pricing architecture, and deployment complexity. Solution type and deployment model concentrate margin pools, while end-user scale dictates service bundling intensity and compliance documentation requirements.
Solution Type:
Mature endpoint protection dominates current procurement volumes, while emerging data backup isolation technologies capture the steepest expansion trajectory as KRITIS operators confront dwell-time compression mandates.
- Endpoint Protection:Agent-based detection platforms monitor file system behavior and process execution across Windows and Linux workstations. Bavarian automotive suppliers in Ingolstadt and Munich corridors deploy these solutions to protect connected vehicle development environments from encryption-based extortion.
- Network Security:Segmentation appliances and intrusion prevention systems isolate lateral movement paths within flat manufacturing networks. Energy distribution operators in North Rhine-Westphalia prioritize these investments to satisfy BSI baseline protection standards for critical infrastructure.
- Data Backup:Immutable backup architectures with cryptographic isolation prevent ransomware from reaching secondary recovery targets. Mittelstand firms migrating to sovereign cloud frameworks drive demand concentration in Baden-Württemberg.
- Incident Response:Automated orchestration platforms compress detection-to-containment intervals from hours to minutes. German hospital networks retain these services on retainer given constrained internal security operations staffing.
Endpoint Protection handles the majority of throughput; Data Backup is the fastest mover on share.
Deployment Model:
Cost tier stratification separates capital-intensive on-premises hardware from operational expenditure models, with hybrid architectures occupying the mid-tier price-performance position for manufacturers with legacy operational technology constraints.
- On-Premises:Hardware appliances and perpetual software licenses deployed within customer data centers. Classified government networks and defense contractors in Bonn and Berlin corridors mandate these air-gapped configurations.
- Cloud-Based:SaaS-delivered protection with elastic scaling across multi-tenant infrastructure. Stuttgart industrial machinery manufacturers favor this model for predictable operational expenditure and rapid deployment cycles.
- Hybrid:Split architectures preserving sensitive data on-premises while leveraging cloud analytics for threat intelligence. Automotive OEMs with connected vehicle telemetry pipelines adopt this configuration to satisfy GDPR data residency requirements.
- Managed Services:24/7 security operations center coverage with vendor assumption of detection and response responsibilities. Eastern German utilities with certified talent scarcity outsource entire security functions to BSI-certified domestic providers.
Managed Services captures margin expansion through recurring revenue structures; Cloud-Based deployment climbs fastest as sovereign cloud migration accelerates.
End User:
Customer type segmentation aligns procurement sophistication with compliance exposure, where government entities face strictest BSI certification requirements and educational institutions present underpenetrated white space.
- SMEs:Resource-constrained Mittelstand firms across Bavaria and Baden-Württemberg prioritize endpoint protection with minimal operational overhead. Subscription pricing and managed detection services dominate their procurement patterns.
- Large Enterprises:Multi-site manufacturers and financial institutions operate dedicated security operations centers with integrated threat hunting capabilities. These organizations demand API-rich platforms for custom workflow integration.
- Government Entities:Federal ministries and state agencies mandate BSI-certified solutions with hardware-rooted encryption. Procurement runs through centralized federal IT security frameworks with preference for domestic vendors.
- Educational Institutions:Universities and research hospitals retain heterogeneous endpoint populations with limited centralized IT governance. Endpoint protection vendors target this segment with discounted academic licensing and managed service bundles.
Large Enterprises concentrate absolute spending volume; Government Entities expand most quickly as NIS2 transposition tightens procurement standards.
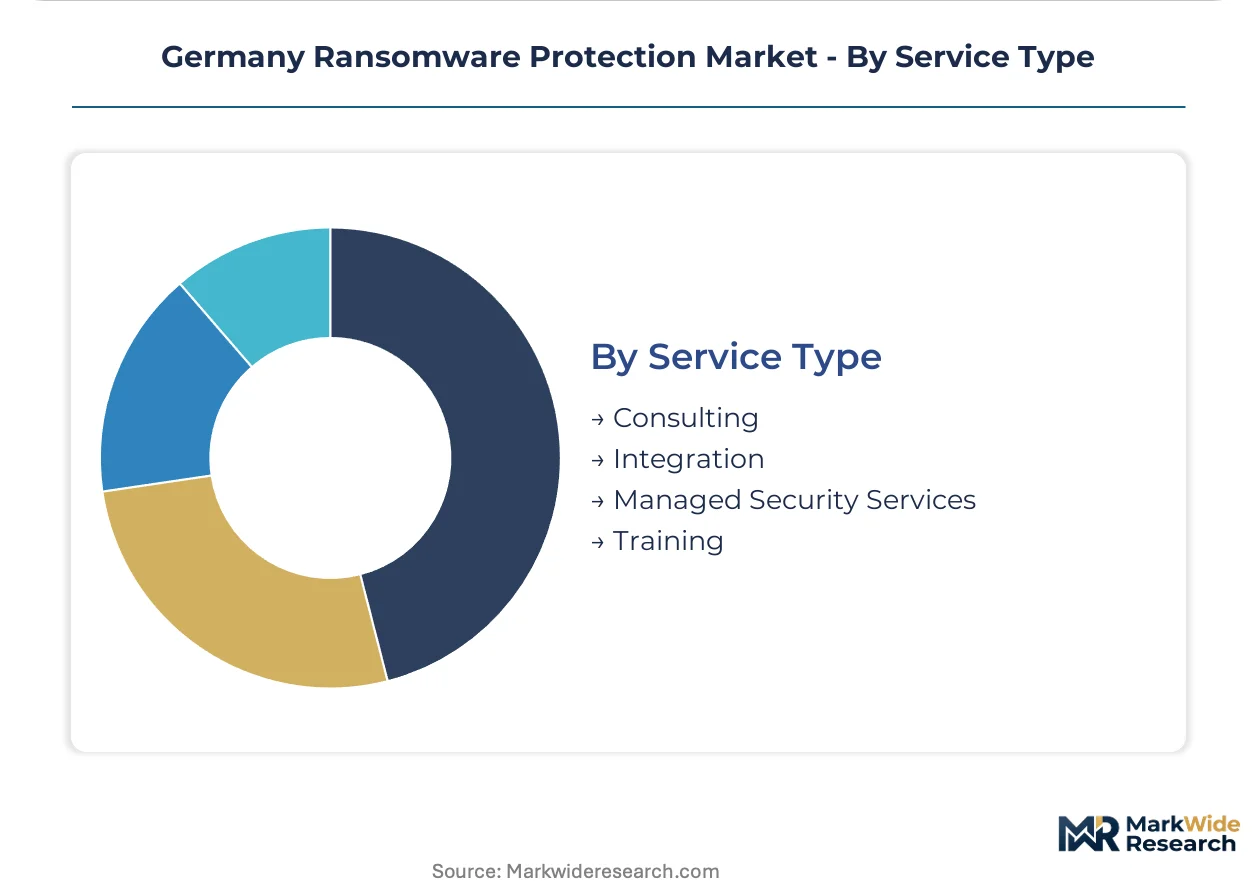
Service Type:
Margin structure varies sharply across the service spectrum, with consulting and integration capturing project-based fees while managed security services generate multi-year recurring revenue with vendor consolidation incentives.
- Consulting:Risk assessment and security architecture design services preceding technology procurement. BSI-certified advisory practices in Munich and Frankfurt command premium rates for KRITIS operator engagements.
- Integration:Deployment engineering and legacy system migration services. Manufacturing execution system integration in automotive plants requires specialized operational technology expertise with production downtime minimization protocols.
- Managed Security Services:Continuous monitoring, threat detection, and incident response delivered as subscription offerings. These services concentrate vendor relationships through long-term contracts with penalty clauses for missed service levels.
- Training:Security awareness programs and technical certification preparation for customer personnel. German state data protection authorities mandate periodic training for essential entities under NIS2 transposition requirements.
Managed Security Services generates the recurring revenue base; Integration services gain share fastest as operational technology convergence complexity intensifies.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Rhine-Main corridor's fiber-optic backbone and Frankfurt's DE-CIX internet exchange anchor Germany's cybersecurity infrastructure density, creating demand concentration for sovereign data protection solutions across federal and commercial networks.
Bavaria
Automotive OEMs in Munich and Ingolstadt drive endpoint protection procurement for connected vehicle development environments. The BSI mandates baseline protection standards for KRITIS operators headquartered in the region. Cybersecurity vendors cluster around the Munich Security Network initiative serving defense and aerospace contractors.
North Rhine-Westphalia
Energy distribution operators in the Ruhr industrial belt prioritize network segmentation investments to satisfy tightened NIS2 disclosure timelines. State-level data protection authorities enforce GDPR breach notification protocols with penalty structures tied to essential service continuity. Düsseldorf and Cologne host managed security service providers targeting utilities with certified talent scarcity.
Baden-Württemberg
Industrial machinery manufacturers in Stuttgart and Mannheim favor cloud-based deployment models for predictable operational expenditure. Mittelstand firms migrate workloads to compliant sovereign cloud frameworks, expanding demand for cryptographic backup isolation. The region's automotive supplier ecosystem adopts confidential computing architectures for telemetry analysis.
Berlin-Brandenburg
Federal ministries and defense contractors mandate BSI-certified solutions with hardware-rooted encryption for classified networks. Procurement runs through centralized federal IT security frameworks with explicit preference for domestic vendors. The capital region concentrates advisory practices serving KRITIS operator compliance engagements.
Lower Saxony
Healthcare networks in Hanover and Braunschweig retain legacy Windows architectures, creating endpoint protection white space for managed security services consolidation. Hospital IT infrastructure modernization programs accelerate under state-level digital health initiatives. Regional utilities confront simultaneous NIS2 compliance deadlines and constrained IT budgets.
Germany Ransomware Protection Market Competitive Landscape
Platform integrators command the system tier; component specialists sit upstream supplying encryption modules and threat intelligence feeds. The vendor base stratifies across three tiers: multinational cybersecurity platforms with broad endpoint portfolios, domestic specialists with BSI certification anchoring federal procurement, and managed security service providers consolidating SME relationships through subscription structures. Competitive dynamics center on certification acquisition for KRITIS market access and sovereign cloud partnership formation to capture Mittelstand migration cycles.
Among domestic specialists, Secunet Security Networks AG exemplifies the BSI-certified archetype anchoring government contract pipelines, while G Data CyberDefense occupies a position representing endpoint detection specialization sustained through malware research capabilities. Rohde & Schwarz Cybersecurity sits within the hardware-rooted encryption tier competing across classified network deployments. These three German entities collectively represent the sovereign solution vector that federal procurement preferences increasingly favor.
| Leading Market Players |
|---|
| Secunet Security Networks AG |
| G Data CyberDefense |
| Rohde & Schwarz Cybersecurity |
| Microsoft |
| Palo Alto Networks |
| Fortinet |
| CrowdStrike |
| Bitdefender |
| Check Point Software |
| Others |
Pricing and Supply Chain Analysis
Single-source dependency on Dresden and Munich semiconductor packaging corridors for trusted platform modules compresses pricing power toward hardware-rooted encryption vendors while forcing buyers into long-term offtake commitments to secure allocation. This concentration simultaneously elevates premium-tier pricing for BSI-certified solutions and constrains economy-tier availability as domestic foundries prioritize federal contract fulfillment.
Pricing Analysis
Volume-discount tiering structures separate enterprise-scale deployments from Mittelstand subscription bundles, with per-endpoint SaaS pricing dominating SME procurement across Bavaria and Baden-Württemberg. Certification grade under BSI technical guidelines and managed security service bundling intensity drive price differentiation between sovereign and non-sovereign vendor tiers. Cost compression in economy-tier endpoint protection intensifies as multinational platforms sacrifice margin to establish German market presence. Government entities exhibit lowest price sensitivity given procurement preference mandates, while eastern German utilities with constrained IT budgets demonstrate highest elasticity.
Supply Chain Analysis
Contract manufacturing concentration for hardware security modules rests with Infineon Technologies' Dresden fab and domestic EMS providers in Munich industrial corridors. Semiconductor wafer supply draws from Taiwan, South Korea, and Germany, while cryptographic component assembly centers on domestic facilities. Single-source vulnerability in trusted platform module packaging creates supply chain risk given absence of qualified secondary sources. Distribution runs through BSI-certified system integrators serving federal procurement channels and direct vendor relationships with KRITIS operators.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
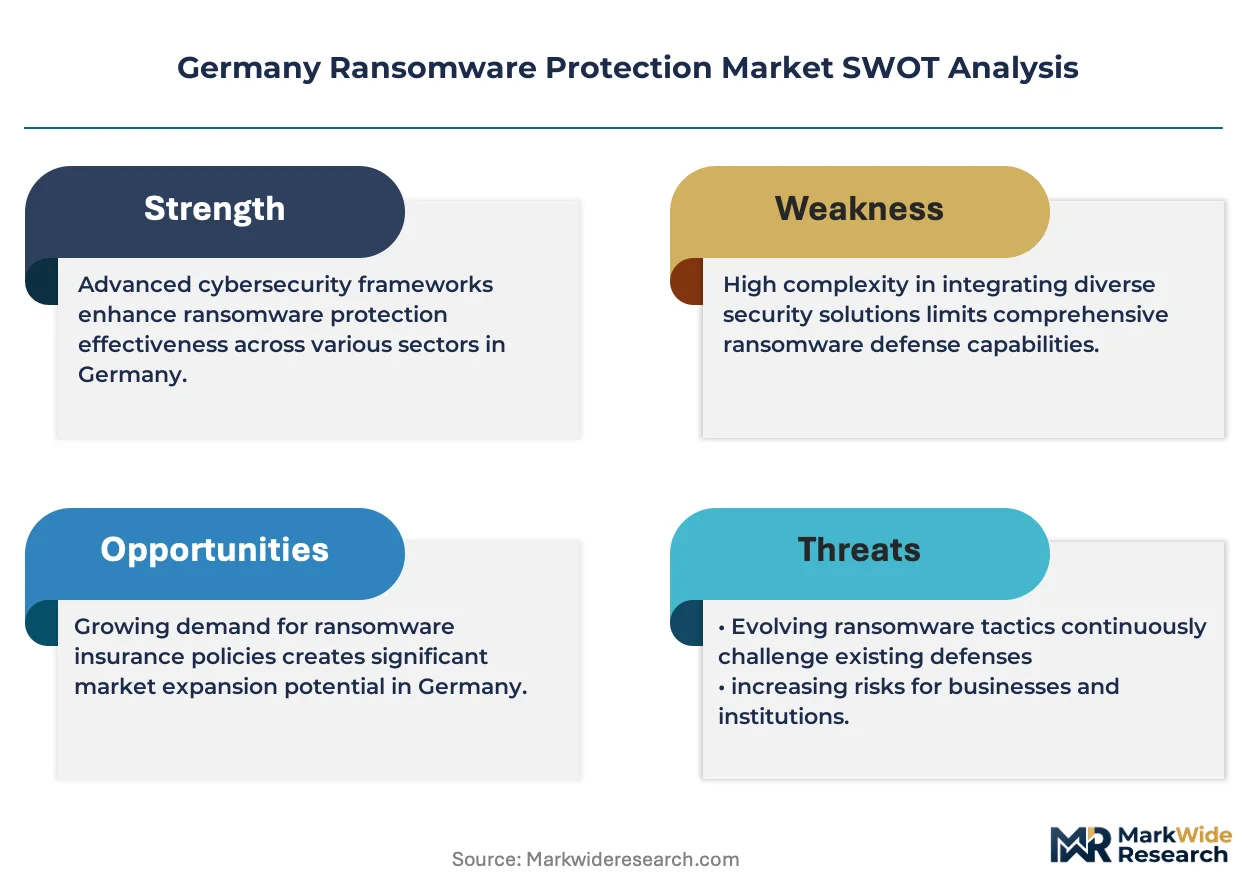
Germany's ransomware protection market functions as a regulatory-moat architecture where BSI certification entrenchment and federal procurement preference lock-in create durable competitive shelter for domestic specialists.
For Market Incumbents: Build certification-depth moats by acquiring niche BSI advisory practices in Munich and Frankfurt to capture NIS2 compliance consulting revenue streams ahead of guideline revisions. Deepen vertical integration into sovereign cloud infrastructure partnerships with Gaia-X compliant providers to anchor Mittelstand migration cycles and forestall multinational platform encroachment. For New Entrants and Emerging Players: Eastern German healthcare networks present underpenetrated white space where legacy Windows architectures and certified talent scarcity create managed security service consolidation opportunities. Target hospital IT modernization programs in Lower Saxony with subscription-based endpoint protection bundled with 24/7 security operations center coverage, leveraging academic partnerships for discounted talent pipeline development. For Investors and Strategic Acquirers: EU NIS2 transposition reshapes the acquisition landscape toward BSI-certified domestic specialists with established federal contract performance records and recurring revenue concentration. Long-term viability favors platform-agnostic managed security service providers capable of bridging sovereign cloud and on-premises deployment complexity. Monitor BSI technical guideline revision announcements as inflection signals for compliance-driven demand acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| BSI Certification Acquisition | Unlocks federal procurement pipelines and KRITIS operator contract eligibility under tightened NIS2 standards. |
| Sovereign Cloud Partnership Formation | Captures Mittelstand workload migration to Gaia-X compliant frameworks across Baden-Württemberg manufacturing corridors. |
| Managed Security Service Expansion | Converts endpoint protection licenses into recurring revenue with penalty-clause service level agreements. |
| Operational Technology Integration Capability Buildout | Addresses automotive manufacturing execution system deployment complexity without production downtime. |
| Confidential Computing Architecture Development | Opens telemetry analysis product categories for connected vehicle suppliers under GDPR liability compression. |
Research Methodology
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CISOs at automotive OEMs, federal IT security procurement officers, BSI certification auditors, managed security service provider executives, and hospital IT directors across German states. Secondary validation drew from BSI technical guideline publications, federal IT security procurement frameworks, EU NIS2 transposition documents, state data protection authority enforcement records, and vendor certification databases. Bottom-up endpoint deployment estimates and top-down federal cybersecurity budget allocations were triangulated to anchor market sizing.
Calibration across the analysis window employed segment-specific growth drivers including NIS2 compliance deadline proximity, sovereign cloud migration velocity, and automotive cybersecurity procurement cycles. Modeled dimensions encompassed solution type, deployment model, end-user scale, and service bundling intensity alongside regional adoption patterns reflecting Mittelstand concentration in southern states. CAGRs were derived from elasticity-adjusted penetration curves and federal procurement pipeline visibility.
The forecast holds incumbent behavior within observed patterns; aggressive capacity expansion by multinational cloud platforms or accelerated BSI guideline revision schedules would shift outcomes beyond projected ranges. Quarterly review of federal procurement award announcements, BSI certification issuance rates, and state-level hospital IT modernization program launches is advised to detect inflection.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Egypt Cybersecurity Market
Cybersecurity
Europe Data Protection-As-A-Service Market
Cybersecurity
Thailand Cybersecurity Market
Cybersecurity
Global API Security Market
Cybersecurity
Data Center Security Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
CDN Security Market
Cybersecurity
China Ransomware Protection Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Cloud Siem Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Firewall-As-A-Service (Fwaas) Market
Cybersecurity
Middle East and Africa Cybersecurity Market
Cybersecurity
IoT Security Market
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Bangladesh Cybersecurity Market