
 Global Internet Security Market | 2026-2036
Global Internet Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Internet Security Market Outlook
The EU AI Act is decoupling automated security analytics from legacy compliance frameworks across European critical infrastructure operators. Palo Alto Networks leverages its platform consolidation strategy to sustain premium positioning in enterprise firewall replacement cycles. Fortinet anchors its growth through ASIC-powered hardware differentiation at price points that challenge software-only rivals. CrowdStrike competes by extending cloud-native endpoint detection into identity protection and workload security adjacencies.
Internet security encompasses hardware, software, and service layers designed to protect networks, endpoints, and data from unauthorized access, malware propagation, and denial-of-service attacks, typically operating at throughput rates exceeding 100 Gbps in carrier-grade deployments and sub-10 millisecond latency thresholds for real-time threat blocking. Its primary purpose is preserving confidentiality, integrity, and availability of digital assets across interconnected systems. The solution dimension shows firewall and intrusion detection system categories commanding established installed bases while encryption solutions capture expanding margin pools from quantum-resistant algorithm transitions. Deployment patterns reveal managed service and hybrid configurations gaining share as skills scarcity pushes mid-market buyers toward outsourced security operations.
FCC network resilience directives in the United States, combined with GDPR data breach notification requirements across Europe and NIS2 critical infrastructure standards, are tightening product certification thresholds and expanding mandatory incident reporting scope. Japan's METI has issued supply chain cybersecurity guidelines that shape vendor qualification protocols for manufacturing sector procurement. Stakeholders must monitor the divergence between sovereign cloud mandates and cross-border threat intelligence sharing frameworks when allocating R&D and partnership resources.
Market Dynamics
Zero-trust architecture mandates from financial regulators are compressing enterprise procurement cycles while fragmenting vendor consolidation patterns across critical infrastructure operators.
Growth Catalysts
- FCC Network Resilience Directives:US telecommunications carriers face mandatory outage reporting thresholds and backup power requirements, accelerating hardware refresh investments in distributed denial-of-service protection systems.
- Quantum-Resistant Encryption:NIST post-quantum cryptographic standards are forcing algorithm migrations across government and defense contractors, creating replacement demand for certificate management infrastructure.
- Japan's METI Supply Chain Guidelines:Manufacturing sector procurement protocols now embed vendor cybersecurity qualification requirements, expanding addressable market for industrial control system security solutions.
Market Restraints
- Specialized Engineering Talent Scarcity:Shortage of professionals holding CISSP and cloud security certifications constrains managed security service provider capacity expansion and drives wage inflation.
- Silicon Supply Concentration:ASIC fabrication for high-throughput firewalls depends on Taiwan-based foundry capacity, exposing hardware vendors to geopolitical disruption risks and extended lead times.
- GDPR-EU AI Act Friction:Automated threat detection systems face divergent compliance requirements between data protection and artificial intelligence risk classification frameworks, complicating product architecture decisions.
Strategic Opportunities
- India's Digital Public Infrastructure:UIDAI and NPCI platform expansions create sovereign cloud security procurement opportunities for domestic and international vendors meeting CERT-In certification requirements.
- Convergence of SASE and SSE:Secure access service edge architectures merging with security service edge platforms enable unified vendor positioning against fragmented point-solution competitors.
- Germany's Industrial Cybersecurity Cluster:Munich and Frankfurt manufacturing automation hubs concentrate demand for operational technology security integration with enterprise IT frameworks.
Industry Challenges
- Multi-Cloud Architecture Complexity:Enterprises operating across AWS, Azure, and Google Cloud environments struggle with inconsistent security policy enforcement and identity federation across heterogeneous control planes.
- NIS2 Certification Timelines:EU critical infrastructure operators face compressed implementation deadlines for incident response capabilities and supply chain risk management procedures.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Internet Security Market |
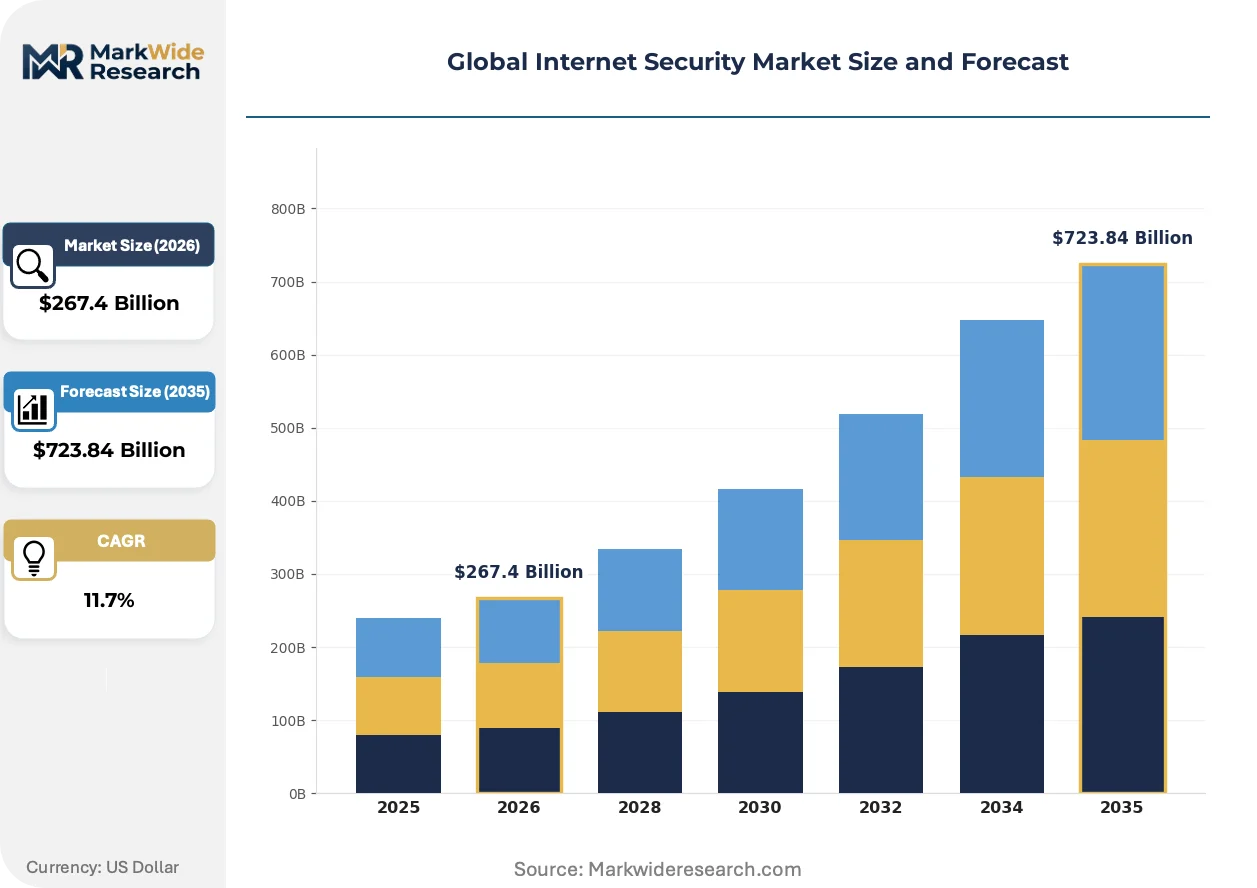
| Market Size in 2026 | $267.4 Billion |
| Market Size in 2035 | $723.84 Billion |
| CAGR (2026 – 2036) | 11.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Firewall, Anti-virus, Intrusion Detection System, Encryption Deployment: On-premises, Cloud, Hybrid, Managed Service End User: Enterprise, SMB, Government, Individual Service Type: Consulting, Training, Support, Maintenance |
| Companies Covered | Palo Alto Networks, Fortinet, Microsoft, Cisco Systems, IBM, CrowdStrike, Check Point Software Technologies, Trend Micro, Broadcom, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Internet Security Market Strategic Shifts
Threat detection architectures are fragmenting from monolithic platforms into composable services, while regulatory fragmentation accelerates regional product specialization and sovereign cloud qualification requirements.
Extended detection and response platforms are modularizing security operations center workflows into API-first components. Mid-market enterprises in healthcare and retail are adopting these modular configurations faster than full-stack replacements. This modularity is compressing incumbent vendor maintenance revenue streams while enabling specialist vendors to capture discrete functional budgets.
The EU AI Act risk classification framework is redefining automated security analytics compliance obligations. High-risk system providers must implement human oversight mechanisms and algorithmic transparency documentation. European critical infrastructure operators are responding by bifurcating procurement between explainable rule-based systems and black-box machine learning with audit trails.
Consumption-based licensing models are displacing perpetual firewall purchases in enterprise accounts. Managed service providers and systems integrators capture margin through bundled deployment and monitoring services. This shift is most visible in US financial services, where capital efficiency metrics favor operational expenditure treatment of security infrastructure.
Global Internet Security Market Segmentation
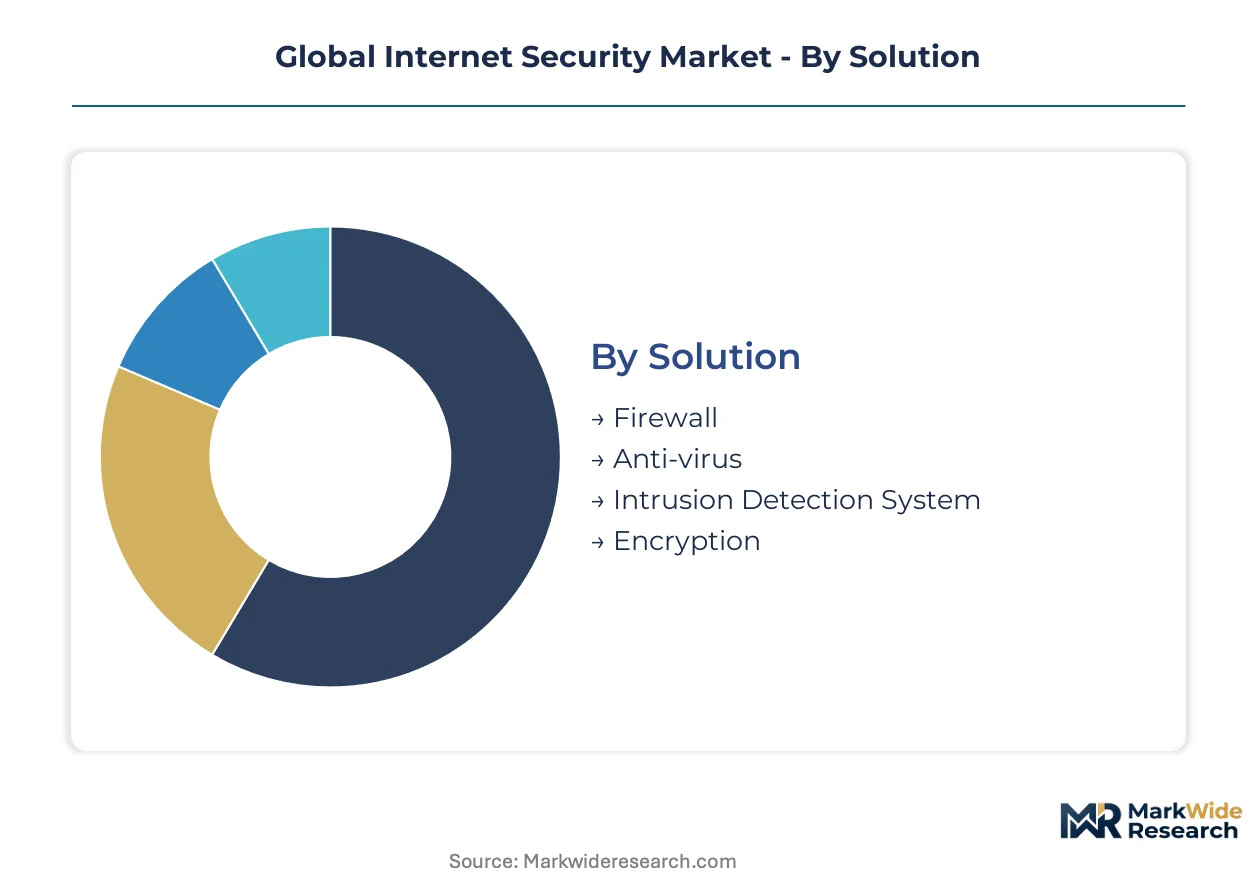
Internet security procurement patterns fragment sharply across solution architectures and operational models. Vendors must align R&D investments with deployment modality preferences and compliance requirements specific to buyer scale and sector.
Solution:
Supply concentration in high-throughput hardware tilts margin capture toward vendors with captive ASIC fabrication relationships.
- Firewall:Deep packet inspection engines operating at 100+ Gbps throughput anchor carrier-grade deployments. Financial services institutions in the United States drive replacement demand as FCC resilience mandates compress refresh cycles.
- Intrusion Detection System:Signature and anomaly-based network monitors deployed at perimeter and east-west traffic junctions. Germany's industrial cybersecurity cluster around Munich concentrates operational technology integration demand.
- Anti-virus:Endpoint scanning engines with behavioral heuristics for fileless malware detection.
- Encryption:Certificate management and key lifecycle systems transitioning to post-quantum algorithms.
Firewall absorbs the bulk of installed capacity; Encryption is expanding most quickly.
Deployment:
Cost tier stratification separates capital-intensive hardware buyers from operational expenditure-focused service adopters.
- Managed Service:Outsourced security operations centers delivering 24/7 monitoring and incident response. Mid-market enterprises in healthcare and retail accelerate adoption as CISSP-certified talent scarcity constrains in-house staffing.
- Hybrid:Split architectures combining on-premises appliances with cloud-delivered policy management. European critical infrastructure operators favor this model under NIS2 supply chain risk management requirements.
- Cloud:Native security service edge and secure access service edge platforms.
- On-premises:Appliance-based deployments retaining data sovereignty and sub-10 millisecond latency thresholds.
Managed Service climbs the fastest as skills gaps persist; On-premises retains the largest installed base.
End User:
Application criticality and regulatory exposure determine security spending intensity across buyer categories.
- Enterprise:Multi-site organizations with dedicated CISO functions and zero-trust architecture mandates. Financial services institutions deploy the most complex multi-layered defenses under combined SEC and FFIEC supervision.
- Government:Defense and civilian agencies with classified data handling requirements. India's UIDAI and NPCI platform expansions create sovereign cloud procurement opportunities meeting CERT-In certification.
- SMB:Resource-constrained organizations purchasing through channel partners and bundled service packages.
- Individual:Consumer endpoint protection sold through retail and OEM pre-installation channels.
Enterprise absorbs the bulk of installed capacity; Government is expanding most quickly.
Service Type:
Margin pools concentrate in recurring revenue streams attached to product lifecycles rather than discrete professional engagements.
- Maintenance:Firmware updates, threat signature refreshes, and hardware replacement programs. Consumption-based licensing models in US financial services favor operational expenditure treatment of these recurring commitments.
- Support:Technical assistance centers and severity-tiered incident escalation. Japan's METI supply chain guidelines embed vendor qualification requirements that elevate support service standards.
- Consulting:Architecture design and compliance readiness assessments.
- Training:Certification programs and security awareness workforce development.
Maintenance absorbs the bulk of installed capacity; Support is expanding most quickly.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Munich and Frankfurt anchor the industrial cybersecurity cluster commanding European operational technology security procurement, while regulatory divergence across major economies fragments vendor qualification protocols and shapes regional specialization patterns.
United States
Financial services institutions drive zero-trust architecture procurement under combined SEC and FFIEC supervision. FCC network resilience directives mandate outage reporting thresholds and backup power requirements for telecommunications carriers. The Washington-Boston corridor concentrates defense contractor demand for post-quantum cryptographic migration.
Germany
Manufacturing automation hubs concentrate demand for operational technology security integration with enterprise IT frameworks. NIS2 critical infrastructure standards compress implementation deadlines for incident response capabilities. Bavaria's industrial corridor around Munich leads procurement of intrusion detection systems with east-west traffic monitoring.
Japan
Manufacturing sector procurement embeds vendor cybersecurity qualification requirements under METI supply chain guidelines. Critical infrastructure operators accelerate hardware refresh investments in distributed denial-of-service protection systems. Tokyo-Osaka manufacturing belt dominates industrial control system security solution adoption.
India
UIDAI and NPCI platform expansions create sovereign cloud security procurement opportunities for vendors meeting CERT-In certification requirements. Government agencies prioritize classified data handling infrastructure under national cybersecurity directives. Bangalore-Hyderabad technology corridor concentrates domestic vendor development and international partnership activity.
United Kingdom
Financial services institutions in the City of London deploy complex multi-layered defenses under Bank of England operational resilience requirements. GDPR data breach notification requirements tighten product certification thresholds for cross-border data flows. Thames Valley technology cluster anchors managed security service provider expansion into European markets.
Global Internet Security Market Competitive Environment
Premium-margin players sit above commodity-margin players across platform consolidation and hardware differentiation dimensions. The vendor base stratifies between integrated platform providers, ASIC-powered hardware specialists, and cloud-native endpoint detection firms. Three archetypes dominate: consolidation platforms leveraging cross-sell expansion, hardware-anchored vendors exploiting fabrication relationships, and API-first modular specialists capturing discrete functional budgets. Dominant competitive moves include platform consolidation through portfolio integration and strategic partnerships bridging sovereign cloud qualification requirements.
Within the platform consolidation archetype, Palo Alto Networks and Fortinet exemplify divergent hardware-software positioning, while CrowdStrike occupies a position in the cloud-native endpoint detection tier. These three entities represent the spectrum from ASIC-powered hardware differentiation to software-only delivery models, each anchoring distinct margin pools across enterprise procurement cycles. Their collective positioning illustrates how vendor architecture choices align with buyer preferences for capital efficiency versus performance optimization.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Fortinet |
| Microsoft |
| Cisco Systems |
| IBM |
| CrowdStrike |
| Check Point Software Technologies |
| Trend Micro |
| Broadcom |
| Others |
Value Chain & Pricing Dynamics
Certification-grade bifurcation between sovereign-cloud-qualified and standard-commercial deployments manifests in both margin capture and fabrication sourcing strategies. Premium-tier vendors with captive ASIC programs command pricing power through throughput guarantees, while commodity software providers compete on operational expenditure conversion.
Pricing Analysis
Value-based pricing anchored to threat-blocking throughput and uptime guarantees dominates enterprise procurement. Three-tier pricing structure across premium, standard, and economy levels separates carriers with 100+ Gbps requirements from mid-market hybrid deployments and SMB managed service bundles. Cost compression in the standard tier intensifies because software-only entrants challenge hardware incumbents with consumption-based licensing. Government and defense buyers show least price sensitivity due to post-quantum cryptographic mandates.
Supply Chain Analysis
ASIC fabrication for high-throughput firewalls rests on Taiwan-based foundry capacity, with secondary sourcing from South Korean and US semiconductor producers. Silicon wafers, specialized networking processors, and quantum-resistant cryptographic modules constitute critical input dependencies. Single-source vulnerability around Taiwan-based fabrication exposes hardware vendors to geopolitical disruption risks. Distribution runs through systems integrators and managed service providers who bundle deployment with monitoring services.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market operates as a vertical-integration race where captive silicon design and sovereign cloud qualification determine margin durability. Players are pursuing backward integration into ASIC development to escape foundry dependency and sustain hardware differentiation.
For Market Incumbents: Anchor platform consolidation through API-first module integration that compresses specialist vendor maintenance revenue streams. Threat detection modularization by CrowdStrike-style entrants erodes full-stack pricing power. Prioritize certification investment for EU AI Act high-risk system compliance and India's CERT-In sovereign cloud qualification.
For New Entrants and Emerging Players: Enter via India's Digital Public Infrastructure expansion where UIDAI and NPCI platform security creates procurement openings for certified domestic and international vendors. Germany's industrial cybersecurity cluster around Munich offers penetrable operational technology integration demand. Pursue channel partnerships with systems integrators serving NIS2-pressured European critical infrastructure operators.
For Investors and Strategic Acquirers: Re-rating potential sits with modular API-first specialists given extended detection and response platform fragmentation across healthcare and retail mid-market buyers. Long-term viability favors vendors with demonstrated sovereign cloud qualification traction and recurring revenue attachment above hardware refresh cycles. Watch quantum-resistant encryption certificate management infrastructure as inflection indicator for replacement demand velocity.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Palo Alto Networks leverages cross-sell expansion to sustain premium enterprise firewall positioning. |
| ASIC Development Investment | Fortinet anchors hardware differentiation through captive fabrication relationships at challenging price points. |
| Strategic Partnership | CrowdStrike extends cloud-native endpoint detection into identity protection and workload security adjacencies. |
| Geographic Expansion | Vendors target India's CERT-In certification requirements for UIDAI and NPCI platform security procurement. |
| Acquisition of Specialist Firm | Consolidation platforms capture modular API-first components to compress specialist maintenance revenue streams. |
Study Parameters
Trade association data, regulatory filings, and customs records anchored secondary inputs for this analysis. Primary interviews with CISOs, IT procurement officers, managed security service provider operations leads, and channel partner technical directors combined with FCC outage reports, EU NIS2 implementation guidance, Japan METI supply chain documentation, and India CERT-In certification databases. Bottom-up deployment modeling and top-down market sizing triangulated across solution, deployment, and end-user segmentation dimensions.
Reconciliation of hardware shipment data, managed service contract disclosures, and cloud security platform adoption metrics informed the analytical framework. Deployment model, organization size, vertical sector, integration complexity, and regional regulatory cluster segmentation dimensions were modeled across the projection horizon. CAGRs derived from regression analysis against historical refresh cycle compression and regulatory mandate timing. Quantum-resistant encryption migration timelines and sovereign cloud qualification velocity served as industry-specific forecast inputs.
Forecast precision tightens around the base case; tail outcomes carry wider variance under Taiwan foundry disruption scenarios and EU AI Act enforcement divergence. Forecasts reflect documented assumptions regarding regulatory implementation schedules and enterprise procurement cycle elasticity. Geopolitical friction in semiconductor supply, NIS2 deadline extensions, and post-quantum cryptographic standard adoption delays represent specific risk factors that could revise projections. A small set of named triggers warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
South Korea Ransomware Protection Market
Cybersecurity
Education Data Security Market
Cybersecurity
Cloud-Based Database Security Market
Cybersecurity
DNS Firewall Market
Cybersecurity
Global Network Forensics Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Middle East Cybersecurity Market
Cybersecurity
M2M Network Security Market
Cybersecurity
Europe Zero Trust Security Market
Cybersecurity
Global Online Fraud Detection and Prevention Market
Cybersecurity
Oman Cybersecurity Market
Cybersecurity
Global Breach and Attack Simulation Market
Cybersecurity
Global Sandboxing Market