
 Cloud Endpoint Protection Market | 2026-2036
Cloud Endpoint Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Endpoint Protection Market Intelligence
Agentless architecture and extended detection and response integration is rewriting how endpoint security layers deploy across distributed enterprises. CrowdStrike Holdings, Inc. leverages its native cloud platform to anchor real-time threat hunting at scale. Microsoft Corporation dominates enterprise endpoint protection through deep integration with Azure Active Directory and Office 365 ecosystems. Palo Alto Networks, Inc. competes by extending Cortex XDR capabilities into cloud workload protection platforms.
Cloud Endpoint Protection encompasses software agents and cloud-delivered security services that monitor, detect, and remediate threats on endpoint devices without on-premises infrastructure, typically operating through lightweight kernel-level drivers that stream telemetry to centralized cloud analytics engines for sub-second response orchestration. The technology serves commercial and industrial organizations seeking to replace legacy signature-based antivirus with continuous behavioral monitoring across laptops, servers, containers, and IoT gateways. Deployment through hybrid cloud configurations captures the largest margin pools as enterprises straddle regulated private infrastructure and scalable public compute. Machine Learning-based threat detection represents the fastest-expanding technology segment, displacing static signature repositories with adaptive models trained on billions of endpoint events. Financial Services end users sustain premium pricing for real-time transaction security and fraud prevention integrations.
FDA cybersecurity guidance for connected medical devices, the EU AI Act's risk classification for automated threat response systems, and GDPR data breach notification mandates collectively elevate compliance costs while creating procurement preference for certified cloud endpoint platforms. HIPAA security rule enforcement in the United States similarly channels healthcare provider spending toward audited vendors with documented encryption and access control architectures. Stakeholders must monitor how NIS2 directive implementation across European member states reshapes incident reporting obligations and liability frameworks for managed security service providers.
Market Dynamics
Agentless security architecture is compressing deployment timelines from weeks to hours, forcing incumbent vendors to reengineer kernel-level telemetry collection while healthcare and automotive supply chains demand continuous compliance attestation.
Growth Catalysts
- EU AI Act risk classification:Automated threat response systems face mandatory conformity assessments, creating procurement preference for pre-certified cloud endpoint platforms among European financial institutions and healthcare providers.
- Kernel-level telemetry streaming:Lightweight drivers now capture behavioral indicators without resident agents, enabling security coverage for containerized workloads and ephemeral cloud instances previously invisible to traditional monitoring.
- German industrial digitization:Automotive supply chain cybersecurity requirements under the NIS2 directive are accelerating enterprise deployments across Bavarian manufacturing clusters and Baden-Württemberg supplier networks.
Market Restraints
- GDPR data sovereignty compliance:Cross-border telemetry routing requires regional cloud infrastructure investments that fragment vendor economics and extend sales cycles for multinational deployments.
- Machine learning model training costs:Billions of endpoint events require specialized GPU clusters for adaptive threat detection, concentrating capability among vendors with captive cloud compute resources.
- Legacy antivirus substitution resistance:Signature-based tools retain procurement inertia in cost-constrained municipal and educational sectors where security budgets compete with operational IT spending.
Strategic Opportunities
- Connected medical device security:FDA cybersecurity guidance for premarket submissions creates validated demand for cloud endpoint platforms with documented encryption and access control architectures in hospital systems.
- Behavioral biometrics convergence:Integration of keystroke dynamics and mouse movement analysis with endpoint telemetry is opening fraud prevention contracts with North American financial services institutions.
- Managed detection and response channel expansion:MSSP partners are white-labeling cloud-native platforms to serve mid-market enterprises lacking internal security operations centers, particularly in Canadian and Australian markets.
Industry Challenges
- Kernel driver compatibility certification:Each operating system update requires revalidation of telemetry collection mechanisms, compressing development resources and delaying feature releases across Windows, macOS, and Linux variants.
- Security operations analyst scarcity:Cloud-native platforms generate alert volumes that exceed human triage capacity, forcing vendors to invest in automated response orchestration that itself requires specialized ML operations expertise.
- Multi-cloud environment fragmentation:Hybrid deployments spanning private data centers and multiple public providers create policy synchronization complexity that extends professional services engagements and strains margin structures.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Endpoint Protection Market |
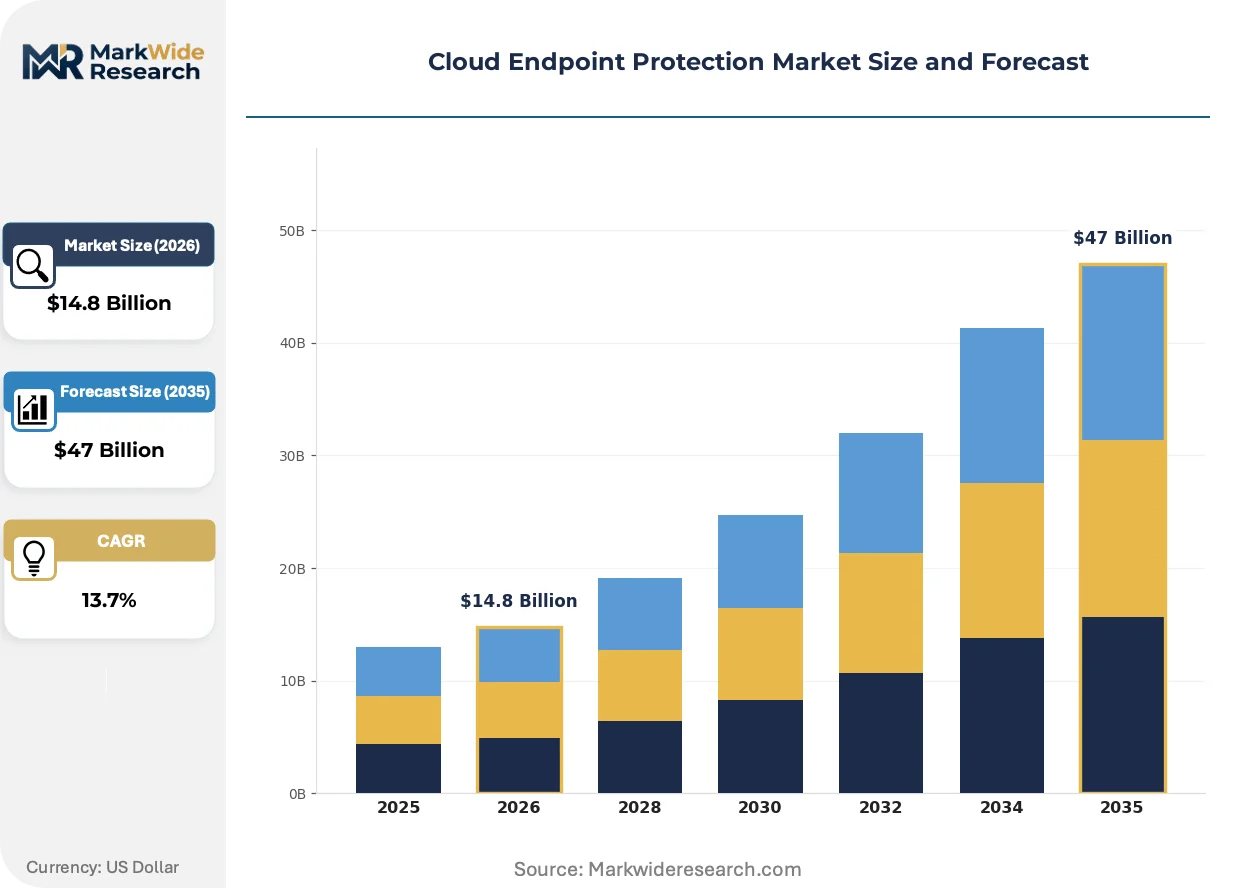
| Market Size in 2026 | $14.8 Billion |
| Market Size in 2035 | $47 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud, Community Cloud Solution Type: Antivirus, Anti-Malware, Intrusion Detection, Threat Intelligence, Data Loss Prevention End User Industry: Financial Services, Telecommunications, Government Agencies, Education Institutions, Manufacturing Technology: Machine Learning, Behavioral Analysis, Signature-Based Detection, Heuristic Analysis, Sandboxing |
| Companies Covered | Microsoft Corporation, CrowdStrike Holdings, Inc., Palo Alto Networks, Inc., Trend Micro Incorporated, SentinelOne Inc., Sophos Group plc, Bitdefender, Kaspersky Lab Inc., McAfee LLC, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Endpoint Protection Market Strategic Shifts & Innovations
Extended detection and response capabilities are migrating from standalone products to embedded platform features, compressing vendor differentiation while elevating the importance of native cloud telemetry integration.
Extended detection and response (XDR) is virtualizing the security operations center by unifying endpoint, network, and identity telemetry into single-pane analysis workflows. Mid-market enterprises without dedicated threat hunting teams are adopting managed XDR services at accelerating rates. This convergence is collapsing the distinction between endpoint protection and security analytics markets, forcing pure-play vendors to develop or acquire cloud SIEM capabilities.
The EU AI Act's risk-based classification for automated security decision-making is mandating human oversight mechanisms for high-risk deployments. Financial institutions deploying autonomous threat containment must now document intervention protocols and audit trails. German automotive manufacturers are responding by requiring contractual human-in-the-loop guarantees from cloud endpoint vendors serving their connected vehicle platforms.
Consumption-based licensing is displacing per-seat endpoint pricing as containerized and serverless workloads proliferate without fixed device counts. Cloud-native enterprises are negotiating usage-metered contracts tied to telemetry volume or compute hours protected. This shift is most visible among software-as-a-service providers in Silicon Valley and Bangalore who scale infrastructure elastically and reject traditional endpoint agent economics.
Cloud Endpoint Protection Market Segmentation
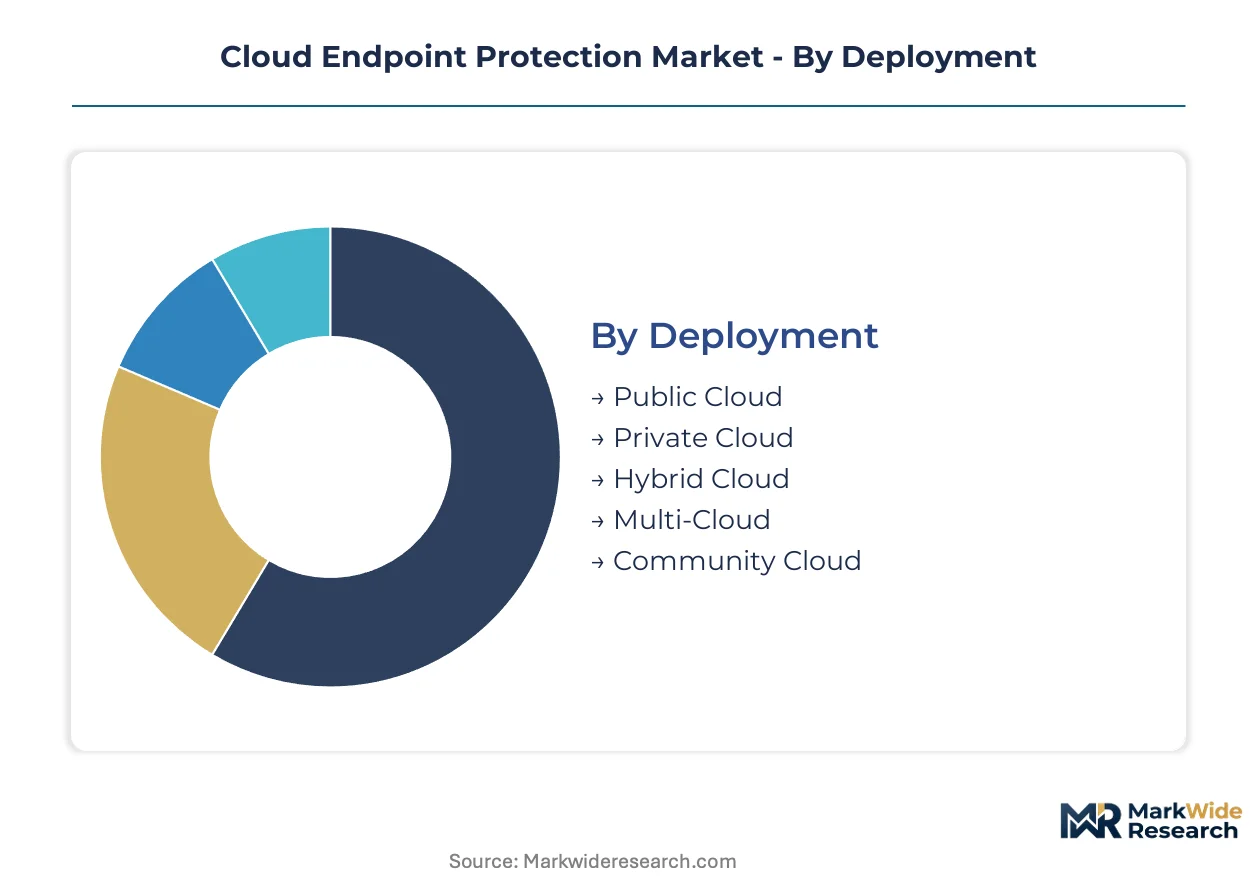
Cloud Endpoint Protection vendors architect pricing and R&D roadmaps around deployment topology, solution maturity, and compliance intensity across end-user industries. Segment boundaries are blurring as platform consolidation compresses standalone product categories into unified telemetry stacks.
Deployment:
Hybrid Cloud configurations turn over fastest as enterprises straddle regulated private infrastructure and scalable public compute, while Community Cloud deployments cycle slowest due to sector-specific certification requirements.
- Public Cloud:Fully managed security services operating over AWS, Azure, and Google Cloud infrastructure with elastic compute scaling. North American SaaS providers in Silicon Valley and Bangalore negotiate usage-metered contracts tied to telemetry volume rather than per-seat pricing.
- Private Cloud:Dedicated infrastructure deployments within enterprise data centers or colocation facilities with isolated tenant environments. German automotive manufacturers under NIS2 directive requirements mandate private cloud for connected vehicle platform telemetry to satisfy data sovereignty constraints.
- Hybrid Cloud:Policy synchronization spanning on-premises workloads and public cloud instances through unified management planes. Financial services institutions in Frankfurt and Singapore sustain premium pricing for real-time transaction security across distributed infrastructure.
- Multi-Cloud:Cross-provider orchestration protecting workloads across AWS, Azure, and Google Cloud simultaneously. Policy synchronization complexity extends professional services engagements and strains vendor margin structures.
- Community Cloud:Shared infrastructure serving specific sectors like healthcare or defense with common compliance requirements. FDA cybersecurity guidance for connected medical devices channels hospital system spending toward validated community cloud architectures.
Hybrid Cloud anchors the volume base while Public Cloud gains share at the steepest rate.
Solution Type:
Cost tier stratification separates commodity antivirus from premium threat intelligence, with mid-market intrusion detection capturing expanding procurement budgets.
- Antivirus:Legacy signature-based malware scanning with periodic definition updates and scheduled system scans. Municipal and educational sectors retain procurement inertia for cost-constrained deployments competing with operational IT spending.
- Anti-Malware:Real-time behavioral blocking of ransomware, spyware, and trojan payloads through kernel-level interception. Healthcare systems expanding cloud endpoint adoption prioritize anti-malware for remote patient data access security.
- Intrusion Detection:Network traffic analysis identifying anomalous connection patterns and lateral movement indicators. Mid-market enterprises without dedicated threat hunting teams adopt managed intrusion detection services at accelerating rates.
- Threat Intelligence:Curated indicator feeds and adversary attribution supporting proactive threat hunting operations. Financial services sustain premium pricing for fraud prevention integrations with real-time transaction monitoring.
- Data Loss Prevention:Content inspection and egress control preventing exfiltration of sensitive records through email, cloud storage, or removable media. GDPR data breach notification mandates elevate procurement preference for certified DLP platforms among European healthcare providers.
Antivirus retains the installed base while Threat Intelligence climbs the fastest as security operations centers prioritize proactive hunting over reactive blocking.
End User Industry:
Application intensity varies sharply, with financial services demanding real-time transaction security and manufacturing prioritizing operational technology convergence.
- Financial Services:Real-time fraud prevention, transaction integrity monitoring, and regulatory reporting for banking and insurance operations. North American institutions integrate behavioral biometrics with endpoint telemetry for keystroke dynamics and mouse movement analysis.
- Telecommunications:Subscriber device protection and network edge security for mobile and fixed-line service providers. 5G network slicing architectures require containerized workload protection across distributed radio access networks.
- Government Agencies:Classified information handling with mandatory encryption and access control architectures. NIS2 directive implementation reshapes incident reporting obligations and liability frameworks for managed security service providers serving European public sector.
- Education Institutions:Student and faculty device protection across heterogeneous bring-your-own-device environments. Budget constraints favor multi-tenant community cloud deployments over dedicated infrastructure.
- Manufacturing:Operational technology integration securing industrial control systems and connected production equipment. Bavarian manufacturing clusters and Baden-Württemberg supplier networks accelerate enterprise deployments under automotive supply chain cybersecurity requirements.
Financial Services commands premium pricing while Manufacturing shows the steepest expansion trajectory as industrial digitization converges IT and OT security domains.
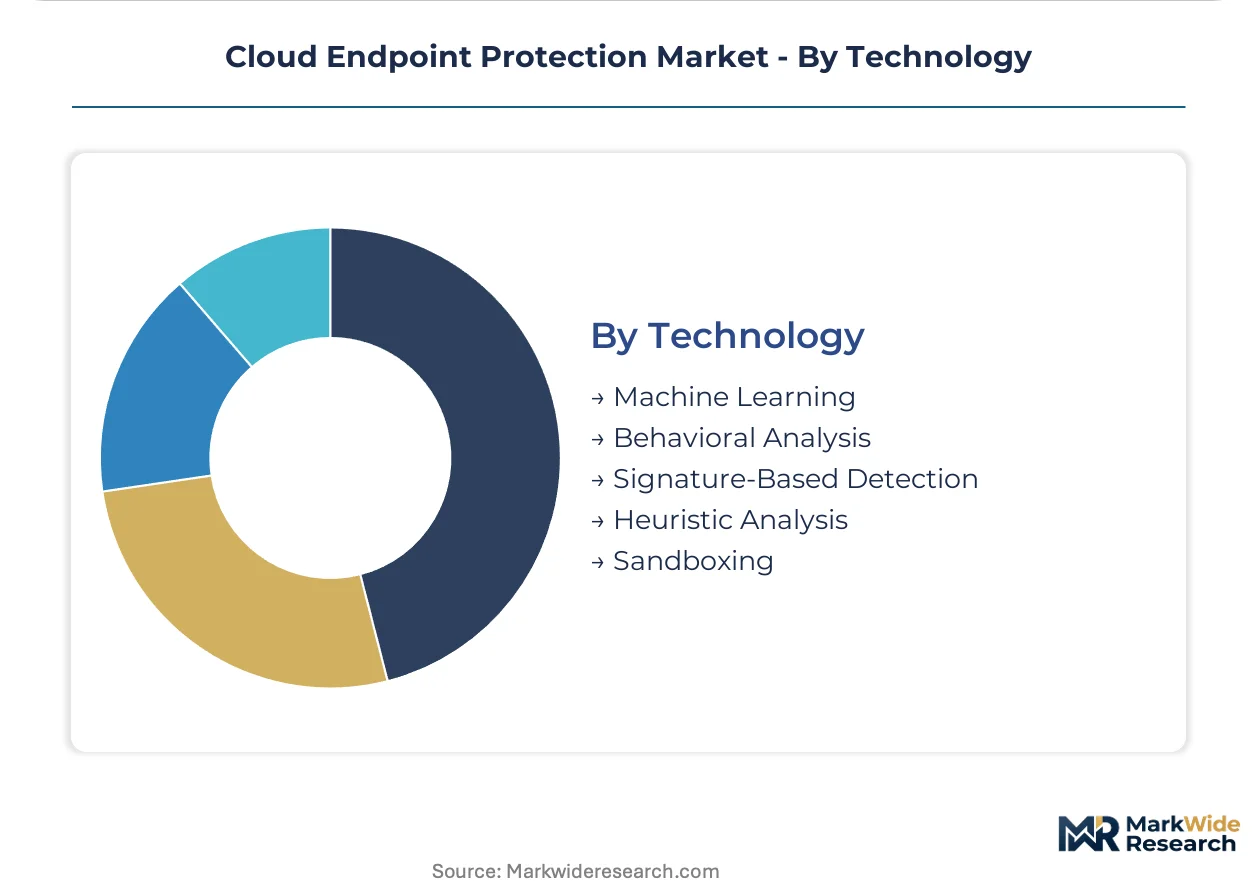
Technology:
Maturity gradients separate established signature methods from emerging ML pipelines, with heuristic analysis occupying a transitional middle ground.
- Machine Learning:Adaptive threat models trained on billions of endpoint events for behavioral anomaly detection without static signatures. Specialized GPU clusters for model training concentrate capability among vendors with captive cloud compute resources.
- Behavioral Analysis:Real-time monitoring of process execution, memory allocation, and API call sequences to identify malicious activity. Kernel-level telemetry streaming enables coverage for containerized workloads previously invisible to traditional monitoring.
- Signature-Based Detection:Pattern matching against known malware hash databases with rapid definition distribution. Legacy tools retain procurement inertia in cost-constrained sectors where security budgets compete with operational priorities.
- Heuristic Analysis:Rule-based suspicion scoring for unknown files based on structural characteristics and code behavior emulation. Serves as bridge technology during enterprise transitions from signature to ML-based protection.
- Sandboxing:Isolated execution environments for detonating suspicious files and observing malicious behavior without production risk. Automated containment decisions under EU AI Act risk classification now require documented human oversight protocols and audit trails.
Signature-Based Detection retains volume leadership while Machine Learning expands most quickly as adaptive models displace static repositories.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Israeli cybersecurity firms export behavioral analytics engines to German automotive manufacturers and American healthcare systems, creating a transatlantic trade corridor in cloud-native threat detection infrastructure.
United States
FDA cybersecurity guidance for connected medical devices drives hospital system procurement of validated cloud endpoint platforms. HIPAA security rule enforcement channels provider spending toward audited vendors with documented encryption architectures. Silicon Valley SaaS providers negotiate usage-metered contracts tied to telemetry volume rather than per-seat pricing.
Germany
Automotive supply chain cybersecurity requirements under the NIS2 directive accelerate enterprise deployments across Bavarian manufacturing clusters. GDPR data sovereignty compliance mandates regional cloud infrastructure investments that fragment vendor economics. Baden-Württemberg supplier networks demand continuous compliance attestation from cloud security vendors.
United Kingdom
Financial services institutions integrate behavioral biometrics with endpoint telemetry for keystroke dynamics analysis in fraud prevention contracts. The country's national cybersecurity center issues guidance on automated threat response systems that shapes procurement standards. London-based managed security service providers white-label cloud-native platforms for mid-market enterprises lacking internal security operations centers.
Japan
Manufacturing digitization converges IT and operational technology security domains, expanding cloud endpoint adoption for industrial control system protection. METI industrial security guidelines elevate compliance costs while creating preference for certified platforms. The Kanto region's precision equipment manufacturers deploy kernel-level telemetry streaming to secure containerized production workloads.
India
Bangalore software-as-a-service providers scale infrastructure elastically and reject traditional endpoint agent economics in favor of consumption-based licensing. The country's central bank mandates incident reporting frameworks that reshape liability structures for managed security service providers. Mumbai financial institutions sustain premium pricing for real-time transaction security integrations.
Cloud Endpoint Protection Market Key Industry Players
Channel-controlling players compete with product-specialist players across a tiered market structure where platform consolidation compresses standalone product categories. The vendor base clusters around three strategic archetypes: native cloud platforms with real-time threat hunting capabilities, enterprise software ecosystems with deep directory service integration, and network security incumbents extending into cloud workload protection. Dominant competitive moves include portfolio diversification through extended detection and response capability acquisition and geographic expansion via managed security service provider channel partnerships.
Among platform-native specialists, CrowdStrike Holdings, Inc. and SentinelOne Inc. occupy positions exemplifying cloud-first architectures with kernel-level telemetry streaming. Microsoft Corporation anchors the enterprise ecosystem tier through deep integration with productivity and identity infrastructure. Palo Alto Networks, Inc. represents network security incumbents extending Cortex capabilities into cloud workload protection platforms.
| Leading Market Players |
|---|
| Microsoft Corporation |
| CrowdStrike Holdings, Inc. |
| Palo Alto Networks, Inc. |
| Trend Micro Incorporated |
| SentinelOne Inc. |
| Sophos Group plc |
| Bitdefender |
| Kaspersky Lab Inc. |
| McAfee LLC |
| Others |
Cost & Logistics Intelligence
GDPR data sovereignty compliance creates a dual chokepoint that widens pricing spreads between regionalized and global-tier deployments while fragmenting vendor cloud infrastructure investments across European member states. Kernel-level telemetry collection costs concentrate among hyperscale cloud providers, compressing margins for second-tier vendors and forcing geographic specialization.
Pricing Analysis
Legacy signature-based antivirus occupies the economy tier at commoditized rates, behavioral analysis with heuristic engines commands the standard tier, and machine learning-native platforms with autonomous response capabilities anchor premium pricing. Three-tier pricing structure across premium, standard, and economy levels stratifies by detection sophistication, with financial services institutions in Frankfurt and Singapore absorbing premium rates for real-time fraud prevention while municipal education sectors drive cost compression in the antivirus tier. Pricing pressure stems from consumption-based licensing displacing per-seat models as containerized workloads proliferate without fixed device counts. SaaS providers in Bangalore and Silicon Valley exhibit highest price sensitivity, rejecting traditional agent economics for usage-metered telemetry contracts.
Supply Chain Analysis
GPU clusters for ML model training draw from captive hyperscale infrastructure concentrated in the United States, Taiwan semiconductor foundries supply specialized telemetry processing chips, and Irish and German data centers provide regionalized cloud capacity for GDPR-compliant deployments. Raw material dependencies span advanced silicon for edge inference accelerators, rare earth elements for server magnetics, and cobalt for battery backup systems. Single-source vulnerability concentrates in NVIDIA-dominated AI training hardware, creating procurement risk for vendors lacking diversified silicon strategies. Distribution runs through direct enterprise sales for large accounts, managed security service provider channels for mid-market penetration, and hyperscaler marketplaces for cloud-native consumption.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Agentless security architecture threatens to commoditize kernel-level telemetry collection, forcing incumbents to defend through platform consolidation and automated response differentiation.
For Market Incumbents: Insulate margin structures by deepening integration with identity and productivity ecosystems, creating switching costs that offset pure-play vendor price competition. Acquire cloud SIEM capabilities to collapse the distinction between endpoint protection and security analytics markets. Prioritize certification investment under EU AI Act conformity assessment frameworks to capture procurement preference among European financial institutions and healthcare providers. For New Entrants and Emerging Players: Canadian and Australian mid-market enterprises lacking internal security operations centers present geographic underpenetration with accelerated managed detection and response adoption. White-label partnerships with regional MSSPs offer the most penetrable channel structure, bypassing direct sales infrastructure requirements. Target behavioral biometrics convergence with keystroke dynamics and mouse movement analysis as a differentiated entry angle for North American financial services fraud prevention contracts. For Investors and Strategic Acquirers: The market sits at a platform consolidation phase that favors vendors with native cloud telemetry integration and captive ML training infrastructure. Acquisition targets should demonstrate kernel-level driver certification across Windows, macOS, and Linux variants with documented human-in-the-loop protocols for EU AI Act compliance. Monitor NIS2 directive implementation timelines across European member states as the signal for accelerated enterprise deployment cycles and liability framework shifts.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, network, and identity telemetry into single-pane XDR workflows for SOC virtualization. |
| Acquisition of Specialist Firm | Captures cloud SIEM capabilities that collapse standalone product categories into unified telemetry stacks. |
| Geographic Expansion | Establishes regional cloud infrastructure in Germany and Ireland to satisfy GDPR data sovereignty mandates. |
| Product Launch | Introduces consumption-based licensing tied to telemetry volume for containerized and serverless workloads. |
| Strategic Partnership | White-labels cloud-native platforms through MSSP channels serving Canadian and Australian mid-market enterprises. |
Research Approach
Cross-validation between primary interviews with CISOs, security operations directors, cloud architects, and MSSP channel partners and secondary validation through SEC filings, hyperscaler capex disclosures, and FDA cybersecurity guidance documents anchors the qualitative findings. Bottom-up triangulation aggregates deployment data across public, private, hybrid, and community cloud configurations while top-down analysis calibrates against aggregate spending patterns in financial services, healthcare, and manufacturing verticals.
Calibration against historical adoption curves and regulatory implementation timelines shapes the analytical framework across the projection horizon. Segmentation dimensions modeled include deployment topology, solution maturity tier, end-user industry compliance intensity, and technology generation. CAGRs derive from slope analysis of substitution rates from signature-based to ML-based detection, cross-referenced with GPU cluster capacity expansion and kernel driver certification velocity.
Practitioners should monitor EU AI Act conformity assessment rollout schedules, NIS2 directive liability framework finalization, and hyperscaler pricing volatility for early signals of forecast revision. Material shifts in automated threat response regulatory classification or GPU supply chain concentration would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Enterprise Network Firewall Market
Cybersecurity
Bahrain Cybersecurity Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
Europe Data Exfiltration Market
Cybersecurity
Cloud Firewalls Market
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Ddos Protection and Mitigation Security Market
Cybersecurity
Saas-Based IT Security Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
United States Virtualization Security Market
Cybersecurity
Europe Web Application Firewall Market
Cybersecurity
Global Serverless Security Market
Cybersecurity
Cryptojacking Solution Market