
 Cloud-Based Database Security Market | 2026-2036
Cloud-Based Database Security Market Size, Share, and Industry Trends Forecast 2026-2036
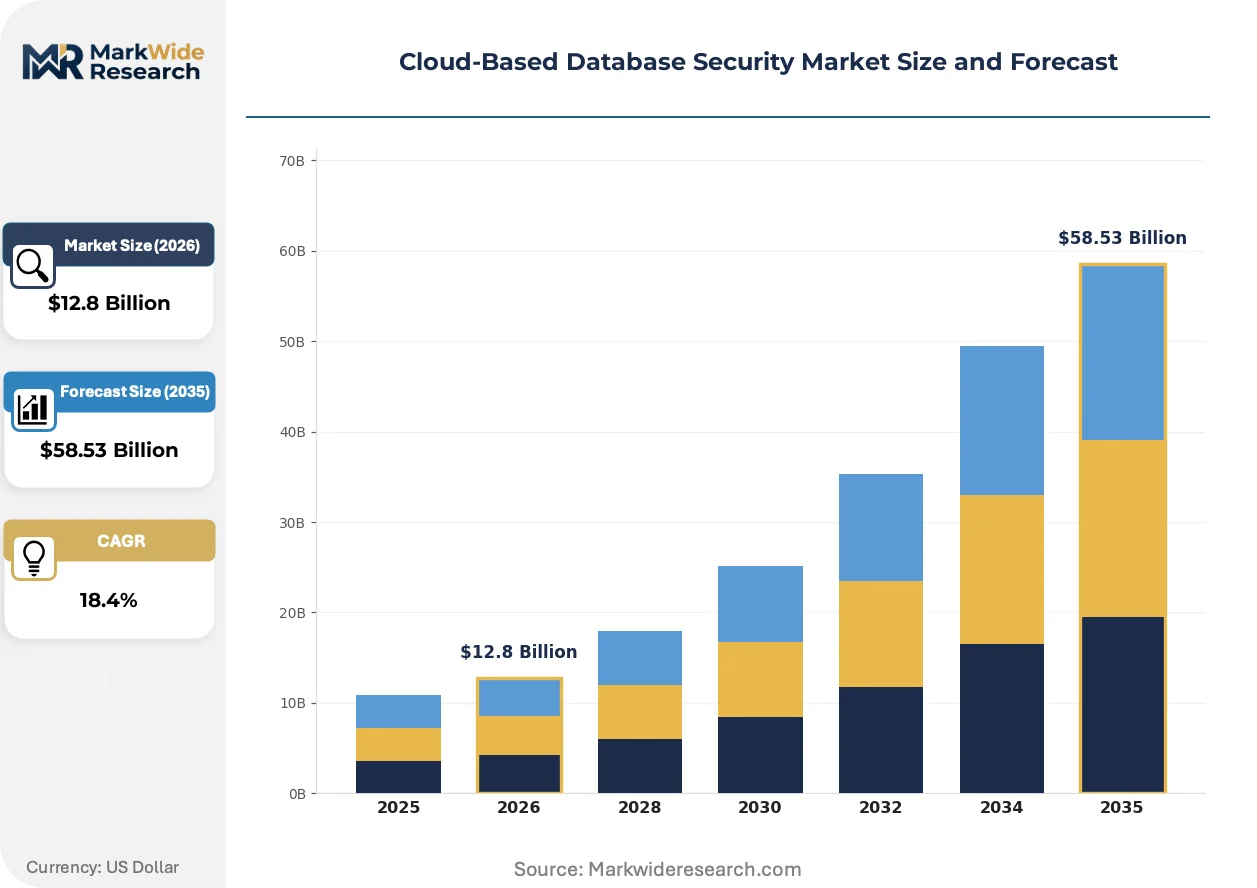
Cloud-Based Database Security Market Outlook
North American hyperscaler infrastructure investment is rebalancing the competitive landscape for database protection software. Oracle Corporation leverages its integrated cloud-autonomous database stack to sustain enterprise lock-in across regulated workloads. Amazon Web Services anchors its security narrative through native encryption and access control layers that compete with third-party alternatives. Microsoft Azure differentiates through Active Directory-backed identity governance that extends across hybrid cloud deployments.
Cloud-based database security encompasses encryption protocols, access governance frameworks, and threat monitoring systems engineered to protect structured data repositories hosted on distributed infrastructure, typically operating across 256-bit AES encryption standards with real-time anomaly detection latency under 50 milliseconds. Its primary commercial purpose is to prevent unauthorized exfiltration, insider abuse, and automated exploitation of relational and non-relational databases operating in virtualized environments. Data encryption solutions dominate current procurement budgets as enterprises confront ransomware exposure and regulatory audit requirements. Hybrid cloud deployment architectures represent the fastest-expanding configuration, driven by data sovereignty constraints and latency-sensitive workload placement across on-premises and off-premises infrastructure.
FDA guidelines on clinical data integrity, SEC cybersecurity disclosure rules, and HIPAA safeguards collectively shape product certification requirements and liability frameworks for cloud database vendors serving regulated industries. The EU AI Act and GDPR impose additional algorithmic transparency and cross-border transfer restrictions that vendors must embed into access control and audit logging architectures. Stakeholders should monitor evolving zero-trust mandates from federal agencies and corresponding procurement qualification criteria that will determine vendor eligibility for enterprise and government contracts.
Market Dynamics
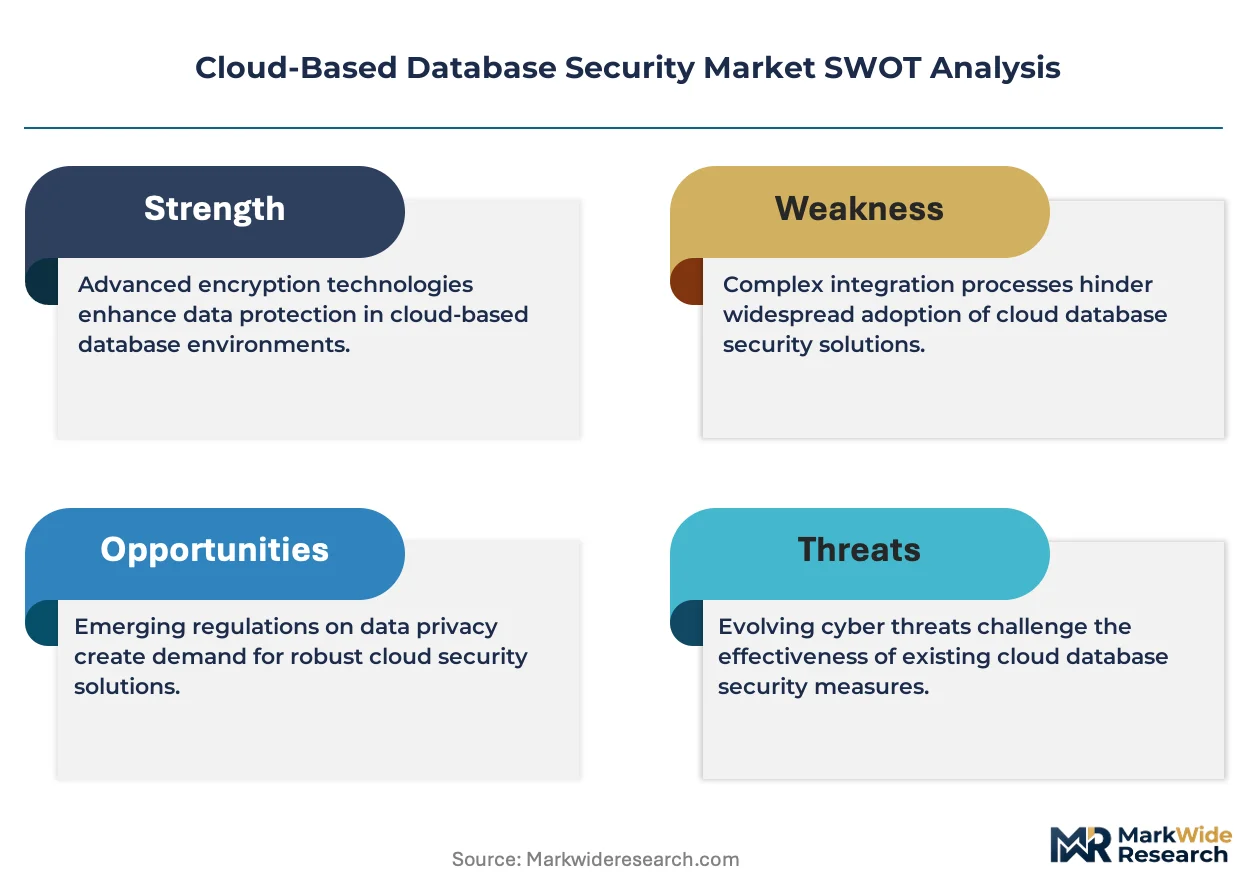
Zero-trust architecture mandates from federal agencies are compressing enterprise procurement cycles and forcing hyperscalers to embed native security controls deeper into database infrastructure layers.
Growth Catalysts
- EU AI Act compliance requirements:Automated decision-making systems hosted on cloud databases must embed algorithmic transparency and audit logging, creating mandatory upgrade cycles for financial services and healthcare data repositories.
- Ransomware exposure in multi-tenant environments:Financial institutions are expanding encryption procurement to isolate tenant data and prevent lateral movement across shared infrastructure.
- Hybrid cloud workload placement:Data sovereignty constraints are accelerating demand for unified security policies spanning on-premises and off-premises database deployments.
Market Restraints
- Specialized talent scarcity:Shortages of cloud security architects with zero-trust implementation experience are extending deployment timelines and inflating professional services costs.
- Cross-border transfer friction:GDPR data localization requirements are fragmenting database architectures and complicating centralized security policy enforcement for multinational enterprises.
- Legacy system integration complexity:On-premises relational databases with decades-old access control schemas resist seamless policy federation with cloud-native identity systems.
Strategic Opportunities
- Confidential computing convergence:Hardware-based trusted execution environments are merging with database encryption to enable query processing on encrypted data without decryption exposure.
- Federal zero-trust procurement mandates:NIST 800-207 compliance requirements are qualifying vendors for enterprise and government contracts that previously favored incumbent providers.
- Edge database security:Latency-sensitive IoT and industrial workloads are creating demand for lightweight encryption and access controls on distributed edge nodes.
Industry Challenges
- Certificate lifecycle management:Shortened TLS certificate validity periods are overwhelming database operations teams with renewal orchestration across thousands of endpoints.
- Insider threat detection:Privileged access monitoring for database administrators requires behavioral analytics that generate false positives and exhaust security operations center capacity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud-Based Database Security Market |
| Market Size in 2026 | $12.8 Billion |
| Market Size in 2035 | $58.53 Billion |
| CAGR (2026 – 2036) | 18.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Data Encryption, Access Control, Threat Detection, Backup and Recovery Deployment: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud End User: Small and Medium Enterprises, Large Enterprises, Government, Educational Institutions Service Type: Managed Services, Professional Services, Consulting Services, Technical Support |
| Companies Covered | IBM Corporation, Oracle Corporation, Amazon Web Services, McAfee, Imperva Inc, Fortinet Technologies Inc, Check Point, Microsoft Azure, Intel Security Group, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud-Based Database Security Market Strategic Shifts
Security automation is displacing manual policy enforcement as database attack surfaces expand across ephemeral containers and serverless functions. Vendors are racing to embed real-time threat response into query execution paths.
AI-powered query pattern analysis is automating anomaly detection in database access logs, flagging insider threats and credential compromise within milliseconds of deviation. Financial services institutions are deploying these systems across trading and customer databases where manual review cannot match transaction velocity. The technology is automating tier-1 security operations center triage and compressing incident response timelines.
SEC cybersecurity disclosure rules are compelling publicly traded companies to document database breach materiality within four business days. Audit committees are demanding continuous compliance monitoring that feeds directly into financial reporting systems. Healthcare and fintech segments are investing in automated evidence collection to satisfy both SEC and HIPAA concurrent audit requirements.
Consumption-based security licensing is replacing perpetual database protection contracts as enterprises scale cloud workloads elastically. Buyers are negotiating usage-tiered encryption and monitoring services that align costs with actual data volume under protection. This shift is most pronounced among SaaS providers and digital-native enterprises operating multi-region database clusters.
Cloud-Based Database Security Market Segmentation
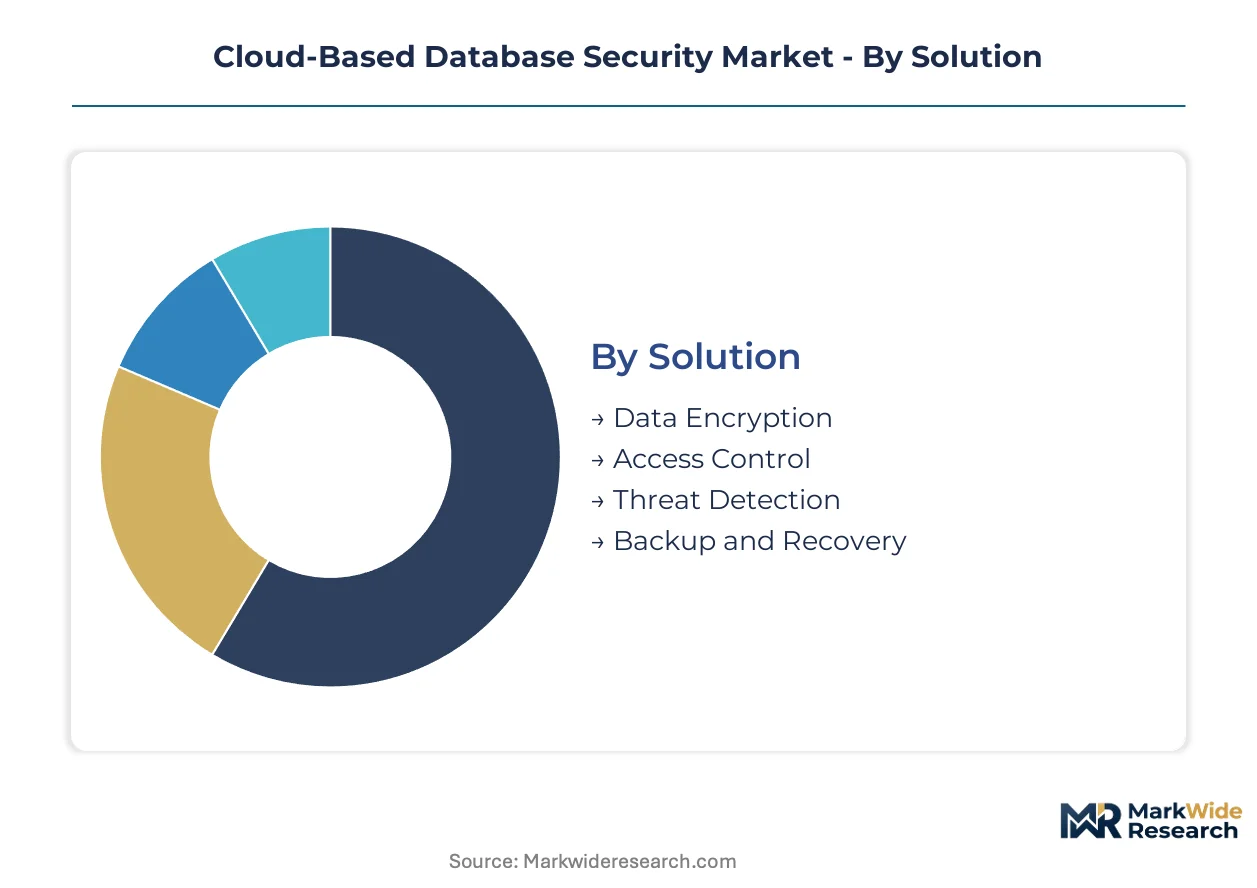
Cloud-based database security procurement diverges sharply across organizational scale, regulatory exposure, and infrastructure maturity. Buyers prioritize encryption depth, deployment flexibility, and service integration depth based on data sensitivity and compliance burden.
Solution:
Procurement budgets concentrate where ransomware exposure and audit scrutiny intersect most intensely.
- Data Encryption:256-bit AES protocols with real-time key rotation dominate financial services and healthcare procurement. United States federal zero-trust mandates accelerate enterprise adoption of column-level and field-level encryption for multi-tenant isolation.
- Access Control:Identity governance frameworks with privileged access monitoring absorb the largest share of professional services spending. European GDPR Article 32 compliance requirements drive demand for attribute-based access control in cross-border data repositories.
- Threat Detection:AI-powered anomaly detection with sub-50 millisecond latency identifies credential compromise and insider abuse patterns.
- Backup and Recovery:Immutable snapshot architectures with air-gapped storage satisfy SEC cybersecurity disclosure timelines.
Data Encryption leads on scale; Access Control leads on momentum.
Deployment:
Infrastructure configuration choices reflect data sovereignty constraints and latency requirements rather than cost optimization alone.
- Hybrid Cloud:Unified policy enforcement spanning on-premises and off-premises databases addresses GDPR localization mandates and FDA clinical data integrity requirements simultaneously. Financial institutions in Germany and France deploy hybrid architectures to retain sensitive customer data within national boundaries while leveraging cloud analytics.
- Public Cloud:Native encryption and identity services from hyperscalers compete directly with third-party alternatives for digital-native enterprises.
- Private Cloud:Dedicated infrastructure with hardware security modules serves defense and intelligence community contracts with classified data handling requirements.
- Multi-Cloud:Cross-platform key management and policy federation reduce vendor lock-in risk for multinational corporations operating across AWS, Azure, and Google Cloud regions.
Hybrid Cloud commands the largest committed spend; Multi-Cloud exhibits the steepest expansion trajectory.
End User:
Security sophistication and procurement authority scale with organizational data volume and regulatory audit frequency.
- Large Enterprises:Dedicated security operations centers with 24/7 database activity monitoring justify premium managed detection and response contracts. United States healthcare systems and European banks maintain the highest per-employee security expenditure ratios.
- Government:Federal zero-trust mandates and FedRAMP certification requirements filter vendor eligibility to a qualified shortlist.
- Small and Medium Enterprises:Consumption-based licensing and automated policy templates reduce deployment complexity without dedicated security staff.
- Educational Institutions:FERPA compliance and research data protection drive demand for cost-optimized encryption with student information system integration.
Large Enterprises anchor current revenue; Government contracts deliver the longest sales cycles but highest retention rates.
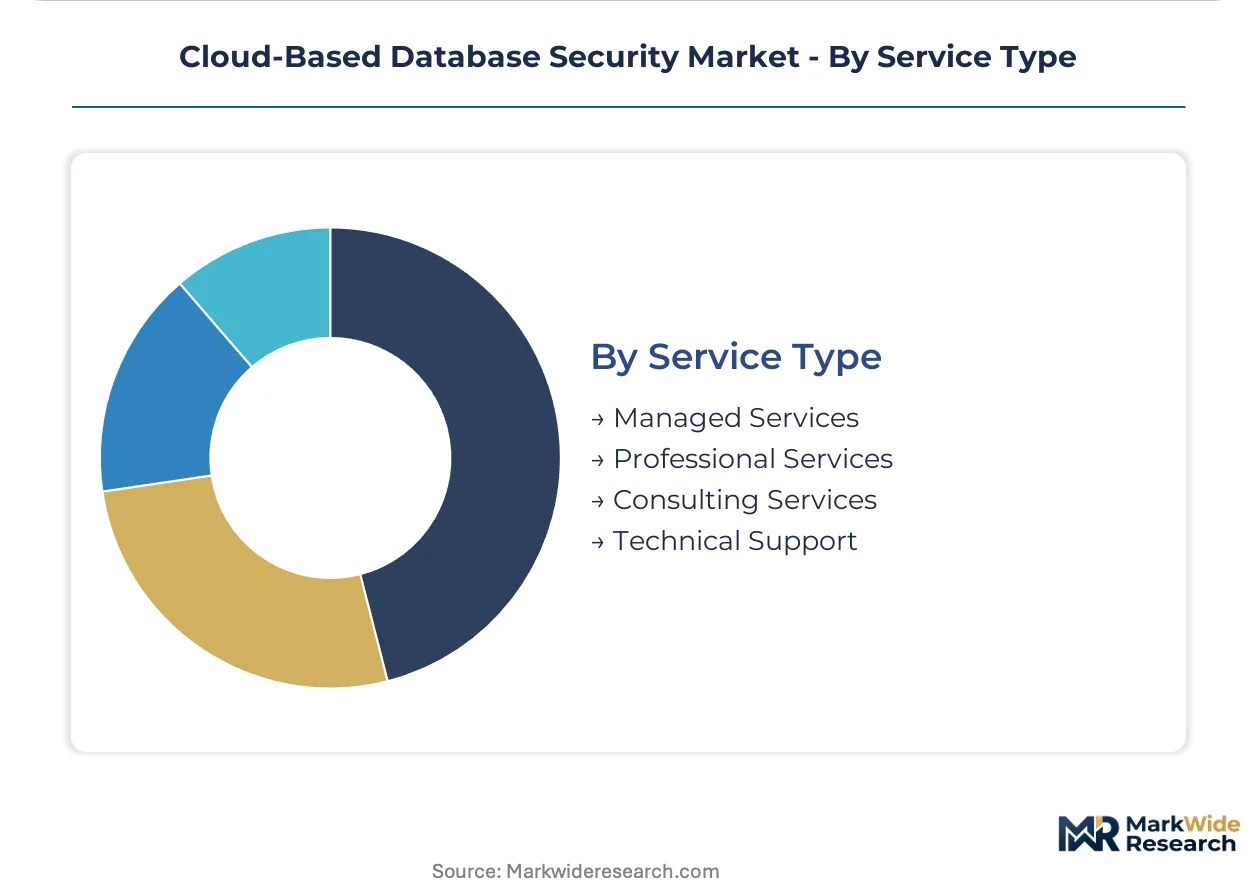
Service Type:
Buyers trade capital expenditure for operational flexibility as cloud workload elasticity renders perpetual licenses obsolete.
- Managed Services:24/7 threat monitoring, patch management, and certificate lifecycle outsourcing relieve internal staffing constraints. United States financial services firms and German automotive manufacturers outsource database security operations to specialized providers.
- Professional Services:Zero-trust architecture design and legacy system integration command premium day rates due to certified practitioner scarcity.
- Consulting Services:Regulatory readiness assessments and audit preparation support SEC disclosure and HIPAA safeguard documentation.
- Technical Support:Tiered response commitments with guaranteed resolution windows underpin enterprise licensing agreements.
Managed Services generates the highest recurring revenue; Professional Services captures the steepest rate inflation from talent scarcity.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory-arbitrage dynamics are redistributing cloud database security procurement as compliance cost differentials widen between jurisdictions. Enterprises now site data infrastructure in locations where encryption mandates and audit requirements align with operational risk tolerance. This geographic reconfiguration favors markets with harmonized federal standards over fragmented state-level regimes.
United States
Federal zero-trust mandates from NIST and OMB are compressing enterprise procurement cycles for database encryption. SEC cybersecurity disclosure rules require four-day breach reporting, compelling Fortune 500 firms to upgrade monitoring infrastructure. Financial services clusters in New York and Chicago dominate committed spend on column-level encryption for multi-tenant isolation.
Germany
Automotive manufacturers and industrial conglomerates are expanding cloud database protection budgets to satisfy GDPR Article 32 technical safeguard requirements. The BSI (Federal Office for Information Security) certifies encryption products for critical infrastructure, creating a qualified vendor shortlist. Manufacturing concentration in Bavaria and Baden-Württemberg drives demand for hybrid architectures that retain sensitive design data within national boundaries.
United Kingdom
Financial services regulators at the Bank of England and FCA are tightening operational resilience requirements for cloud-hosted trading databases. The UK GDPR retains EU-equivalent cross-border transfer restrictions post-Brexit, complicating centralized security policy enforcement. London's fintech corridor represents the densest concentration of consumption-based security licensing adoption in Europe.
Japan
METI guidelines on data free flow with trust are shaping enterprise cloud migration patterns for database workloads. The Act on Protection of Personal Information imposes encryption and access logging requirements comparable to GDPR. Tokyo-Osaka corridor financial institutions are deploying AI-powered anomaly detection with sub-50 millisecond latency requirements for real-time trading surveillance.
India
RBI directives on data localization for payment systems are forcing multinational banks to maintain India-specific database infrastructure with sovereign encryption key control. The Digital Personal Data Protection Act introduces breach notification timelines that accelerate security operations center staffing. Bengaluru and Mumbai technology clusters exhibit the steepest growth trajectory for managed database security services among Asia-Pacific emerging markets.
Cloud-Based Database Security Market Competitive Environment
Established producers occupy the standard tier; emerging entrants pursue confidential computing and edge-native encryption as differentiation vectors. Market structure consolidates around three hyperscalers with native database security stacks, while specialist vendors fragment across encryption, access governance, and threat detection niches. Strategic archetypes include integrated cloud infrastructure providers, standalone cybersecurity platforms, and legacy database vendors with cloud extension portfolios. Dominant competitive moves center on embedding security controls deeper into database execution layers and forging FedRAMP certification partnerships for federal contract eligibility.
Among integrated infrastructure providers, Oracle Corporation and Amazon Web Services exemplify divergent approaches to enterprise lock-in through database-security stack integration. Microsoft Azure anchors the identity-centric archetype with Active Directory-backed governance extending across hybrid deployments. IBM Corporation represents the legacy-transition positioning, bridging on-premises relational systems with cloud-native policy federation. These three entities collectively define the competitive intensity shaping procurement negotiations for regulated industry contracts.
| Leading Market Players |
|---|
| IBM Corporation |
| Oracle Corporation |
| Amazon Web Services |
| McAfee |
| Imperva Inc |
| Fortinet Technologies Inc |
| Check Point |
| Microsoft Azure |
| Intel Security Group |
| Others |
Value Chain & Pricing Dynamics
Federal zero-trust procurement mandates are compressing enterprise sales cycles and forcing vendors to absorb certification costs upfront, reshaping how security software suppliers structure channel economics and tiered service offerings.
Pricing Analysis
Distributor margins in the database security channel typically range from 15-25% for value-added resellers serving mid-market accounts, with direct-to-enterprise discounts of 30-40% for Fortune 500 commitments exceeding multi-year thresholds. Consumption-based SaaS licensing stratifies across premium, standard, and economy tiers aligned with encryption depth and managed detection response coverage. Cost compression in the mid-market tier is intensifying because hyperscalers are bundling native encryption at marginal cost. Small and medium enterprises exhibit highest price sensitivity, while government contracts show lowest elasticity due to FedRAMP qualification barriers.
Supply Chain Analysis
Single-source vulnerability sits with Taiwan-based semiconductor foundries fabricating hardware security modules and specialized cryptographic processors essential for confidential computing deployments. Manufacturing concentration spans Taiwan, South Korea, and the United States for trusted execution environment chips. The supply chain draws from rare earth elements for hardware module fabrication, specialized ASIC designs, and TLS certificate authority infrastructure. Tariff exposure on Chinese-manufactured security hardware is elevating landed costs for encryption appliances. Distribution runs through hyperscaler marketplaces, specialized cybersecurity VARs, and direct enterprise field sales organizations.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a regulatory compounder where SEC cybersecurity disclosure rules and EU AI Act compliance deadlines are generating non-discretionary upgrade cycles across financial services and healthcare data repositories.
For Market Incumbents: Extend FedRAMP certification coverage to capture federal procurement mandates that filter vendor eligibility to qualified shortlists. Embed threat detection deeper into database execution layers to defend against confidential computing specialists eroding encryption margins. Prioritize hybrid cloud policy federation to address data sovereignty constraints fragmenting multinational architectures.
For New Entrants and Emerging Players: AI-powered query pattern analysis with sub-50 millisecond latency offers a technology-first wedge against legacy anomaly detection vendors. Target edge database security for IoT and industrial workloads where lightweight encryption demand outpaces incumbent adaptation. Pursue consumption-based licensing partnerships with SaaS providers operating multi-region clusters as the most penetrable go-to-market angle.
For Investors and Strategic Acquirers: Asymmetric upside sits with confidential computing specialists merging hardware-based trusted execution environments with database encryption capabilities. Five-to-ten year viability hinges on sustaining differentiation as hyperscalers internalize encryption functions. Monitor NIST 800-207 procurement qualification criteria expansion as the signal indicating inflection toward zero-trust native vendors.
| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Integration | Merges hardware TEEs with database encryption to enable query processing without decryption exposure. |
| FedRAMP Certification Acceleration | Qualifies vendors for federal contracts filtering eligibility through NIST 800-207 compliance mandates. |
| Hybrid Cloud Policy Federation | Unifies security controls across on-premises and off-premises databases addressing GDPR localization requirements. |
| AI-Powered Anomaly Detection | Automates tier-1 SOC triage with sub-50 millisecond latency for credential compromise identification. |
| Edge-Native Encryption Development | Captures latency-sensitive IoT workloads distributed across industrial and automotive deployment nodes. |
Study Parameters
Bottom-up enterprise procurement modeling reconciled against top-down hyperscaler security revenue tracking forms the analytical core of this study. Primary interviews with CISOs, cloud architects, database administrators, and cybersecurity procurement officers informed deployment preference and budget allocation patterns. Secondary validation drew from SEC cybersecurity disclosure filings, FedRAMP authorization databases, hyperscaler capex disclosures, and EU regulatory implementation guidance. This dual approach enables triangulation between stated buyer intentions and actual vendor revenue recognition.
Historical trendline analysis across encryption protocol adoption curves, zero-trust architecture penetration, and managed security services growth established baseline momentum vectors. Segmentation modeling incorporated solution type, deployment architecture, organization scale, and regional regulatory cluster dimensions. CAGR derivation applied regression analysis against compliance deadline schedules and ransomware incident frequency correlations. Forecast inputs included federal procurement cycle acceleration, certificate validity period compression effects, and confidential computing hardware availability curves.
The model holds under stable regulatory enforcement timelines and hyperscaler bundling strategies; deviation in EU AI Act implementation severity or federal zero-trust mandate acceleration would shift enterprise upgrade trajectories. Forecasts reflect documented assumptions regarding compliance cost pass-through rates and talent scarcity persistence. Outcomes are best read as a band of plausibility, not a single trajectory.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Finland Cybersecurity Market
Cybersecurity
South Korea Cybersecurity Market
Cybersecurity
Cyber Security As a Service Market
Cybersecurity
India Network Security and Cyber Risk Management Market
Cybersecurity
Threat Intelligence Security Market
Cybersecurity
Global Online Fraud Detection and Prevention Market
Cybersecurity
Cloud Security in Banking Market
Cybersecurity
Cloud Network Security Market
Cybersecurity
Spain Cybersecurity Market
Cybersecurity
Advanced Malware Detection (AMD) Market
Cybersecurity
Global Patch Management Market
Cybersecurity
Cyber Warfare Market
Cybersecurity
Data Center Logical Security Market
Cybersecurity
Hong Kong Cybersecurity Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
IT and Telecom Cyber Security Market