
 South Korea Ransomware Protection Market | 2026-2036
South Korea Ransomware Protection Market Size, Share, and Industry Trends Forecast 2026-2036
South Korea Ransomware Protection Market Insights
Subscription-based managed detection and response financing is reconfiguring competitive entry barriers for mid-sized Korean enterprises. AhnLab leverages its domestic threat-intelligence infrastructure to anchor government contracts. Palo Alto Networks sustains premium positioning through specialized cloud-security modules. SK Shieldus competes via integrated SOC-as-a-service bundles tied to SK Group affiliates.
Ransomware protection encompasses endpoint monitoring, network segmentation, and cryptographic backup systems engineered to detect file-encryption payloads before lateral movement completes. Solutions deploy behavioral heuristics, immutable storage architectures, and automated isolation protocols to preserve operational continuity during active intrusions. Cloud-based deployment models now lead procurement volumes among Korean enterprises migrating from legacy on-premises stacks. Managed services represent the fastest-expanding segment as organizations outsource 24/7 SOC operations to address acute talent shortages. Endpoint security retains the deepest margin pool due to persistent refresh cycles and bundled EDR upgrades.
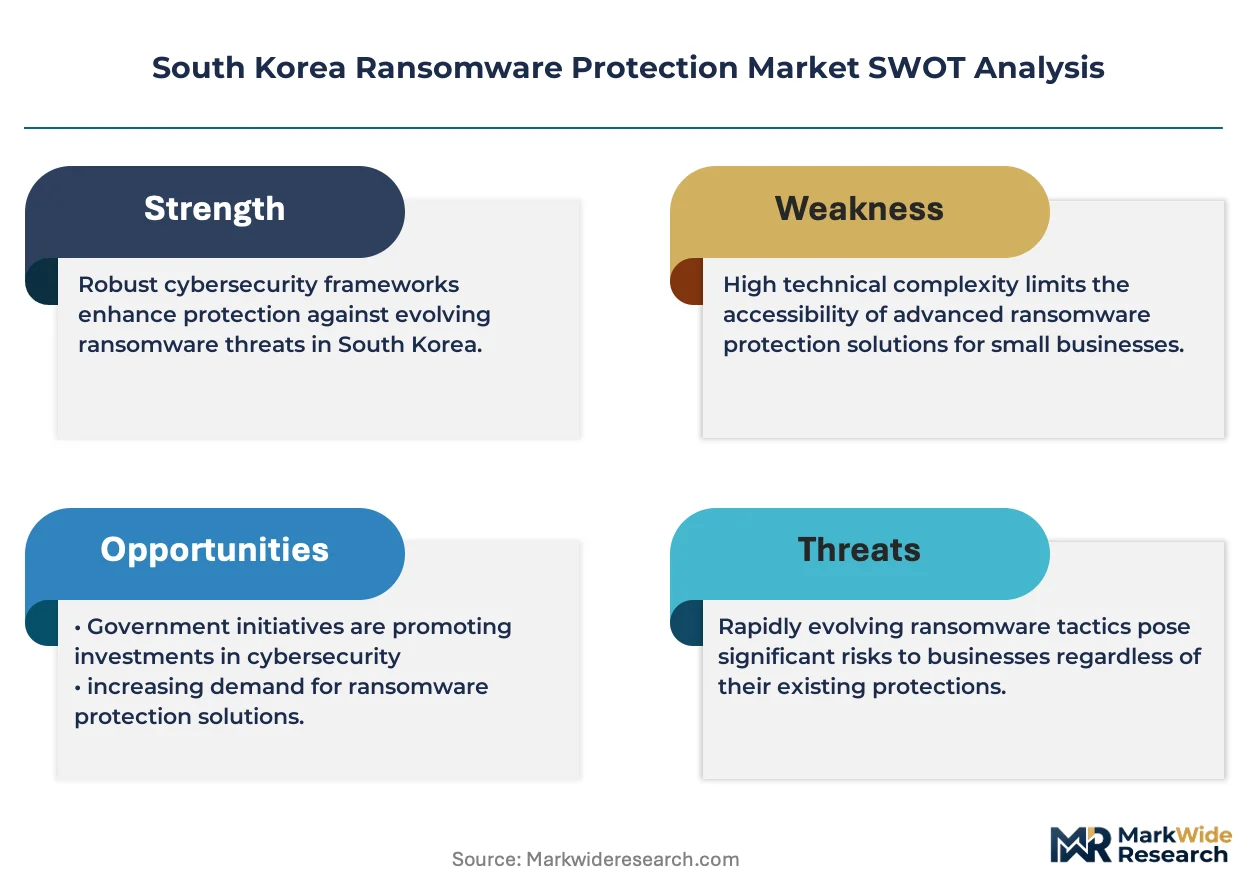
MFDS data-protection standards, NIS zero-trust architecture mandates, and KISA incident-response frameworks collectively shape product certification requirements and procurement eligibility. Compliance with these standards determines market access for foreign vendors and domestic suppliers alike. Stakeholders must monitor evolving KISA encryption-key escrow proposals and their implications for cross-border threat-intelligence sharing arrangements.
Market Dynamics
Zero-trust architecture mandates from NIS are forcing wholesale replacement of perimeter-based security stacks across Korean enterprise networks. Financial services and manufacturing verticals face simultaneous compliance deadlines and ransomware volume spikes.
Growth Catalysts
- NIS Zero-Trust Mandates:Government deadlines for continuous verification architectures are accelerating enterprise procurement cycles. Public-sector contracts now require certified zero-trust implementations.
- Manufacturing IoT Exposure:Gyeonggi-do industrial corridors are deploying ransomware protection for operational technology networks. Smart factory connectivity creates attack surfaces legacy security cannot cover.
- Behavioral Heuristics:File-encryption payload detection before lateral movement completes is reducing dwell time. Machine learning models trained on Korean-language threat intelligence improve accuracy.
Market Restraints
- Encryption-Key Escrow Proposals:KISA frameworks under debate would fragment cross-border threat-intelligence sharing. Foreign vendors face uncertainty about data localization requirements.
- Specialized Talent Scarcity:Domestic SOC analyst shortages constrain 24/7 operations buildouts. Universities produce fewer incident responders than enterprise demand requires.
- Immutable Storage Costs:Air-gapped backup architectures demand redundant infrastructure investments. Mid-sized enterprises defer full deployment due to capital intensity.
Strategic Opportunities
- Busan Port Logistics:Maritime supply chain operators lack ransomware protection for cargo management systems. Terminal operators seek integrated OT-security bundles.
- Subscription MDR Financing:Managed detection and response contracts spread capital costs across operational budgets. Mid-market procurement barriers fall with consumption-based pricing.
- Cloud-Native Convergence:Containerized workloads and serverless architectures require purpose-built protection. Korean SaaS providers need embedded security modules.
Industry Challenges
- Legacy Stack Integration:On-premises security appliances resist API-based orchestration with cloud-native tools. Hybrid environments multiply configuration errors.
- Certification Timeline Compression:MFDS data-protection and KISA incident-response certifications require overlapping documentation. Vendors face duplicated compliance costs.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | South Korea Ransomware Protection Market |
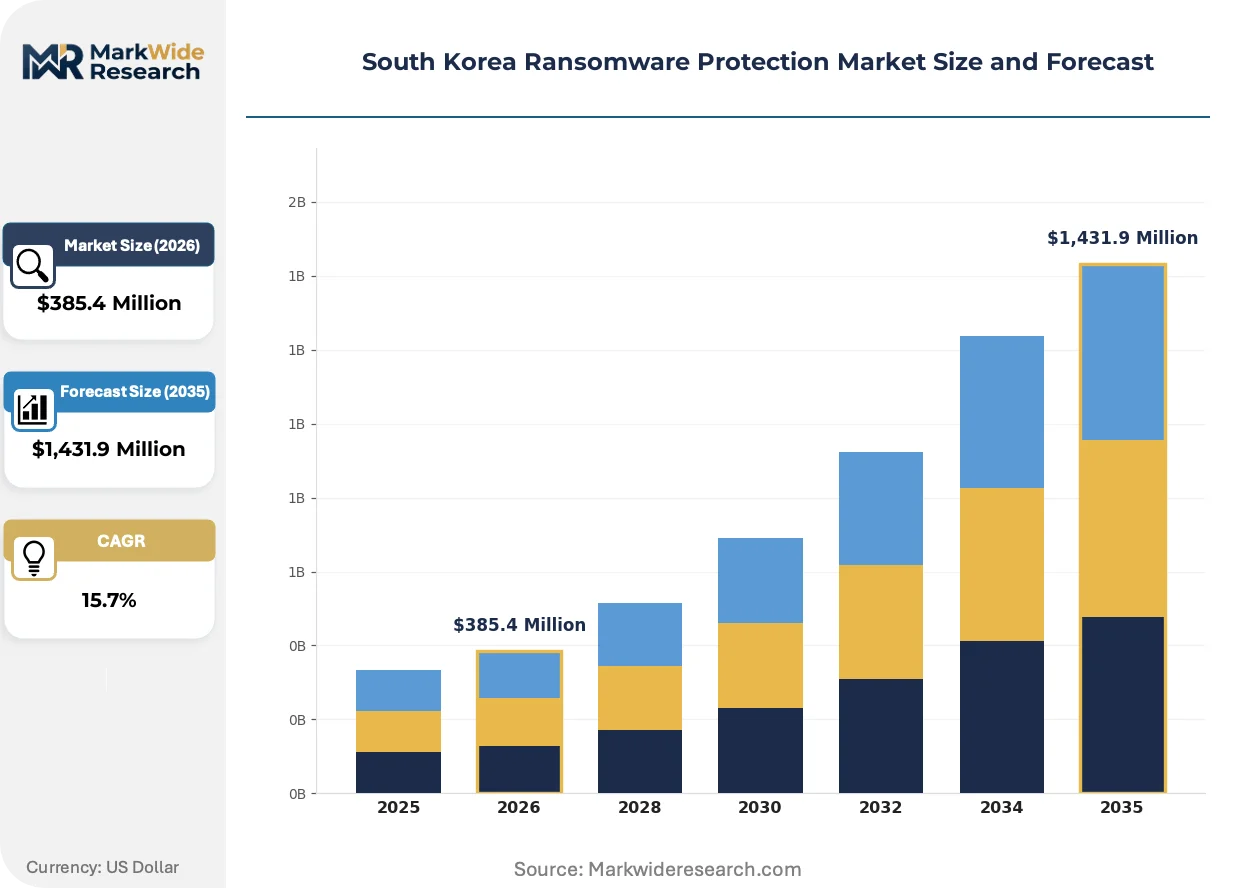
| Market Size in 2026 | $385.4 Million |
| Market Size in 2035 | $1,431.9 Million |
| CAGR (2026 – 2036) | 15.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Protection Type: Endpoint Security, Network Security, Cloud Security, Application Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Government, BFSI, Healthcare, Retail Solution Offering: Backup Solutions, Threat Intelligence, Incident Response, Security Awareness Training |
| Companies Covered | Palo Alto Networks, Check Point Software Technologies, AhnLab, Cisco Systems, IBM Corporation, SK Shieldus, Fortinet, Microsoft, Samsung SDS, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
South Korea Ransomware Protection Market Trends and Innovations
Automated isolation protocols and immutable storage architectures are compressing incident response timelines from hours to minutes. Korean enterprises prioritize technologies that preserve operational continuity during active intrusions.
Extended detection and response platforms are digitizing security operations by unifying telemetry across endpoints, networks, and cloud workloads. Large manufacturers in Incheon and Ulsan are adopting these platforms within eighteen-month refresh cycles. The technology is digitizing how security teams correlate alerts and execute containment playbooks.
MFDS data-protection directives now require cryptographic backup validation for financial services and healthcare sectors. Compliance audits examine backup restoration procedures under simulated attack conditions. Seoul-based institutions are restructuring procurement specifications to prioritize certified immutable storage solutions.
Enterprise buyers are consolidating vendor relationships around integrated SOC-as-a-service bundles. SK Group affiliates and independent manufacturers alike prefer single-accountability models over point-product assemblage. This preference is most visible in Gyeonggi-do, where manufacturing corridors seek unified threat visibility across geographically distributed plants.
South Korea Ransomware Protection Market Segmentation
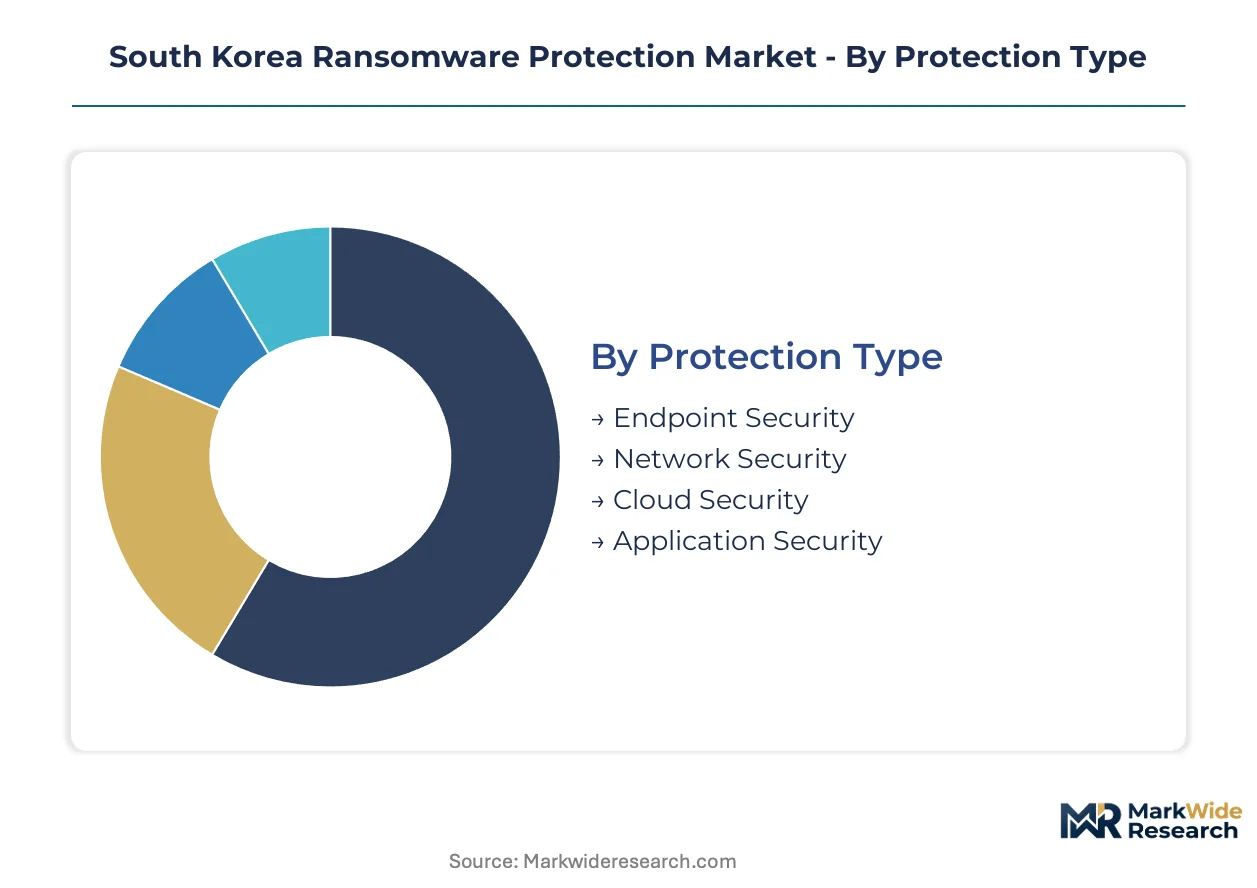
Ransomware protection in South Korea fragments across four critical dimensions. Protection type and deployment model determine technical architecture, while end-user verticals and solution offerings shape procurement specifications and compliance requirements.
Protection Type:
Mature endpoint technologies anchor procurement volumes while cloud-native defenses emerge as the fastest-adoption category across Korean enterprise networks.
- Endpoint Security:Behavioral heuristics and EDR agents deploy across workstations and servers to intercept file-encryption payloads before execution. Seoul financial institutions and Gyeonggi-do manufacturers drive refresh cycles as NIS zero-trust mandates force perimeter replacement. Bundled upgrades and persistent renewal schedules sustain margin concentration.
- Cloud Security:Containerized workload protection and serverless security modules address Korean SaaS providers migrating from legacy stacks. Gyeonggi-do manufacturing corridors absorb the fastest procurement volumes as cloud-native deployment models overtake on-premises alternatives.
- Network Security:Microsegmentation and east-west traffic inspection enforce zero-trust principles across enterprise LANs.
- Application Security:Runtime application self-protection and API security gateways defend web-facing services against injection-based ransomware vectors.
Endpoint Security retains volume leadership; Cloud Security holds the steepest expansion curve.
Deployment Model:
Cost tier stratification separates capital-intensive on-premises builds from operational-expense-driven managed services and cloud subscriptions.
- Managed Services:SOC-as-a-service bundles deliver 24/7 monitoring through outsourced analyst teams, addressing acute domestic talent shortages. Mid-sized Korean enterprises in Busan logistics and regional manufacturing adopt subscription MDR financing to bypass capital barriers. SK Shieldus and domestic competitors anchor integrated bundles tied to affiliate networks.
- Cloud-Based:SaaS-delivered protection scales elastically with containerized workloads and multi-tenant architectures. Korean SaaS providers and cloud-first manufacturers prioritize consumption-based pricing over perpetual licensing.
- On-Premises:Hardware appliances and perpetual software licenses persist in regulated sectors requiring air-gapped control.
- Hybrid:Orchestrated stacks bridge legacy on-premises investments with cloud-native toolchains across transitional architectures.
Managed Services expands most quickly; On-Premises retains installed-base dominance.
End User:
Application intensity varies sharply across verticals, with financial services and government sectors facing simultaneous compliance deadlines and ransomware volume spikes.
- BFSI:Banks, insurers, and securities firms in Seoul deploy cryptographic backup validation and immutable storage under MFDS data-protection directives. Compliance audits examine restoration procedures under simulated attack conditions, restructuring procurement specifications toward certified solutions.
- Government:Public-sector contracts now require certified zero-trust implementations per NIS mandates, accelerating procurement cycles for domestic and foreign vendors alike.
- Healthcare:Hospitals and pharmaceutical distributors face patient-data encryption risks with limited SOC staffing.
- Retail:E-commerce platforms and point-of-sale networks seek cost-effective endpoint protection with managed backup integration.
BFSI commands premium pricing; Government vertical climbs fastest on mandate-driven procurement.
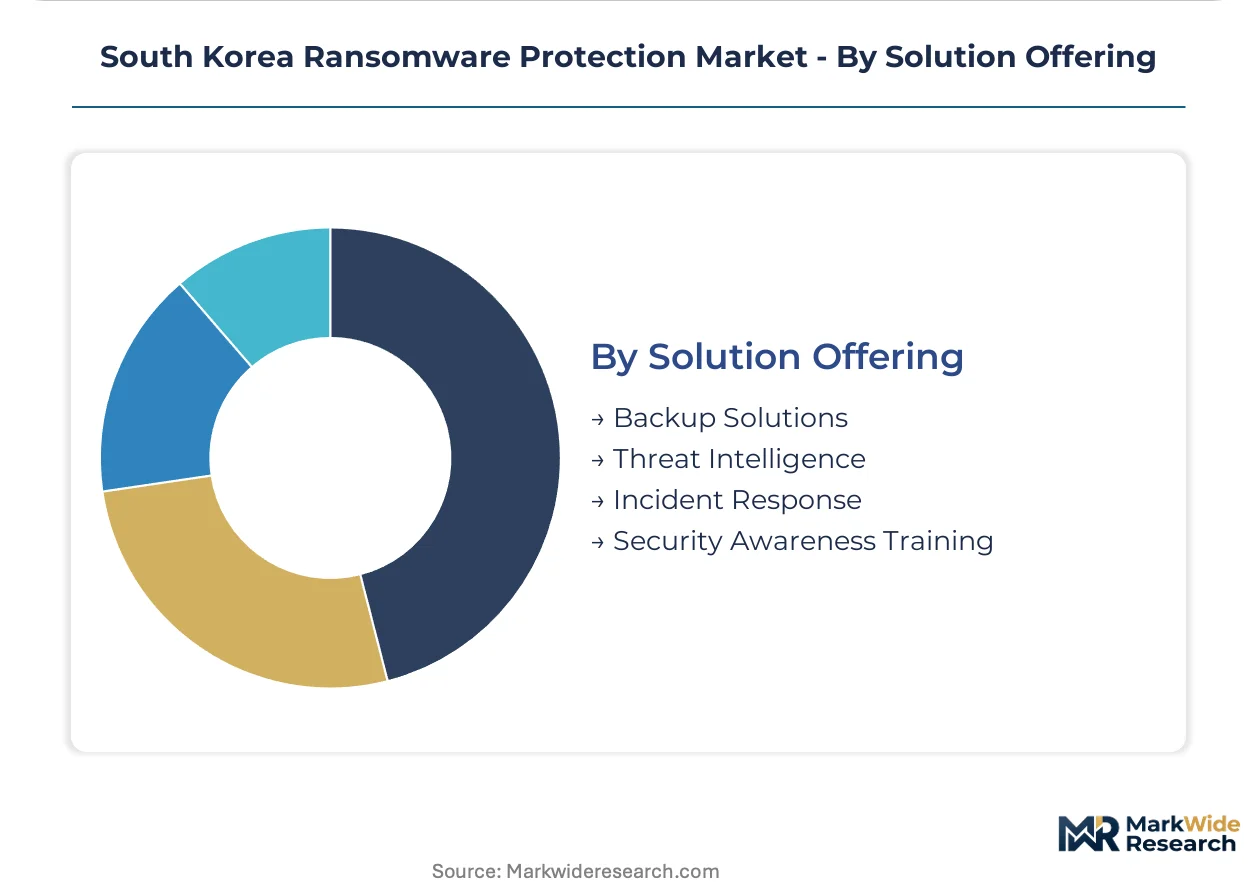
Solution Offering:
Customer type stratification separates integrated platform buyers from point-product purchasers seeking specialized capabilities.
- Incident Response:Retainer-based emergency services and automated containment playbooks compress response timelines from hours to minutes. Korean manufacturers in Incheon and Ulsan adopt these services within eighteen-month refresh cycles as operational continuity priorities harden.
- Backup Solutions:Immutable storage architectures with air-gapped validation satisfy MFDS cryptographic backup requirements for financial and healthcare sectors. Redundant infrastructure investments constrain mid-market deployment.
- Threat Intelligence:Korean-language machine learning models and domestic IOC feeds improve detection accuracy for regional attack patterns.
- Security Awareness Training:Phishing simulation and employee education modules reduce initial compromise vectors across less-mature security organizations.
Backup Solutions anchors revenue concentration; Incident Response gains share fastest on urgency premiums.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Seoul Capital Area commands premium pricing for zero-trust implementations while Busan-Ulsan logistics corridors absorb mid-market solutions. This asymmetry reflects concentration of financial services compliance budgets against distributed manufacturing capital constraints.
Seoul Capital Area
Financial services institutions and government agencies drive demand for certified zero-trust architectures under NIS mandates. MFDS data-protection directives require cryptographic backup validation for banks and insurers headquartered in Seoul. The Yeouido financial district anchors procurement volumes for immutable storage solutions.
Busan-Ulsan
Maritime logistics operators and petrochemical manufacturers seek OT-security bundles for cargo management systems. Port terminal operators face ransomware exposure from connected supply chain platforms. Ulsan industrial complexes deploy network segmentation for smart factory connectivity.
Gyeonggi-do Manufacturing Belt
Electronics and automotive component suppliers migrate from legacy on-premises stacks to cloud-native protection models. NIS deadlines accelerate replacement of perimeter-based security across enterprise networks. Suwon and Pangyo technology corridors absorb the fastest procurement volumes for containerized workload security.
Daegu-Gyeongbuk
Textile and machinery manufacturers confront IoT exposure from operational technology networks. Regional enterprises adopt subscription-based MDR financing to bypass capital barriers. Daegu medical device clusters implement endpoint monitoring under healthcare data-protection requirements.
Daejeon-Sejong
Government research institutes and public-sector agencies anchor demand for certified zero-trust implementations. KISA incident-response frameworks shape procurement specifications for domestic security vendors. Sejong administrative city drives consolidated SOC-as-a-service contracts across state agencies.
South Korea Ransomware Protection Market Competitive Landscape
Platform integrators command the system tier; component specialists sit upstream with narrower scope. The market exhibits moderate consolidation around domestic conglomerate-affiliated providers and multinational security vendors with localized certification. Three archetypes dominate: integrated SOC-as-a-service bundlers, cloud-native platform vendors, and endpoint protection specialists with domestic threat intelligence. Competitive moves center on zero-trust certification racing and managed service portfolio expansion.
Among domestic security providers, AhnLab and SK Shieldus occupy positions tied to government contract eligibility and affiliate network integration. Palo Alto Networks represents the multinational platform tier with specialized cloud-security positioning. These three anchors exemplify the competitive tension between localized compliance advantages and global technology breadth.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Check Point Software Technologies |
| AhnLab |
| Cisco Systems |
| IBM Corporation |
| SK Shieldus |
| Fortinet |
| Microsoft |
| Samsung SDS |
| Others |
Pricing and Supply Chain Analysis
Pangyo technology corridors anchor domestic cloud-security module production, concentrating high-margin zero-trust certification capacity within Gyeonggi-do. This geographic concentration grants certified domestic vendors pricing power over foreign competitors facing KISA compliance delays, while subscription MDR financing spreads procurement costs across operational budgets for mid-market buyers.
Pricing Analysis
Configured-to-order zero-trust implementations command 40-60% premiums over standard endpoint protection packages. Three-tier pricing structure across certified-premium, standard-compliance, and economy-managed tiers reflects MFDS validation levels and NIS mandate deadlines. Pricing pressure stems from SK Shieldus affiliate bundling and AhnLab government contract eligibility compressing margins for non-certified foreign entrants. Mid-sized manufacturers in Daegu-Gyeongbuk exhibit highest price sensitivity; Seoul BFSI institutions show lowest sensitivity due to regulatory penalty exposure.
Supply Chain Analysis
US export-control restrictions on advanced encryption processors limit hardware component flows into Korean security appliance manufacturing. Supply concentrates in Taiwan for specialized ASICs, the United States for threat-intelligence feeds, and domestic foundries for standard silicon. Raw material dependencies span cryptographic processors, immutable storage arrays, and Korean-language ML training datasets. Single-source vulnerability runs through Taiwan semiconductor fabrication for high-performance security chips. Distribution runs through SK Group affiliate networks and systems integrators serving government procurement channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Incumbents face substitution pressure from cloud-native platform vendors displacing perimeter-based legacy stacks. Defense requires building compliance moats faster than competitors can achieve KISA certification.
For Market Incumbents: Build certification moats by accelerating MFDS data-protection validation for immutable storage offerings before Palo Alto Networks completes localization. Deepen threat-intelligence integration with KISA incident-response frameworks to anchor government contract eligibility. Vertical integration into Korean-language ML model training reduces dependency on foreign threat feeds facing escrow uncertainty.
For New Entrants and Emerging Players: Pursue Busan port logistics operators lacking OT-security bundles for cargo management systems. Target textile manufacturers in Daegu-Gyeongbuk with subscription MDR financing bypassing capital barriers. White-space exists in containerized workload protection for Korean SaaS providers migrating from legacy stacks. Go-to-market through regional systems integrators with existing manufacturing relationships accelerates credibility.
For Investors and Strategic Acquirers: Long-term, this sits as a compliance-anchored consolidation play because regulatory certification determines procurement eligibility across public and regulated private sectors. Acquisition targets include domestic SOC-as-a-service specialists with KISA frameworks integration and affiliate network access. Watch NIS zero-trust mandate deadline acceleration as inflection signal for enterprise refresh cycle compression.
| Strategic Initiative | Industry Significance |
|---|---|
| KISA Certification Acceleration | MFDS validation unlocks public-sector contracts and BFSI procurement eligibility. |
| Cloud-Native Platform Integration | Containerized workload protection captures Gyeonggi-do manufacturing migration volumes. |
| SOC-as-a-Service Expansion | 24/7 outsourced monitoring addresses acute domestic analyst talent shortages. |
| Threat Intelligence Localization | Korean-language ML models improve detection accuracy for regional attack patterns. |
| OT-Security Bundle Development | Integrated cargo management protection serves Busan port logistics gaps. |
Research Methodology
Demand-side practitioners and supply-side operators were both consulted across primary fieldwork and secondary validation. Interview subjects included CISOs at Seoul financial institutions, security procurement officers at Gyeonggi-do manufacturers, SOC directors at domestic MSSPs, and channel partners serving government accounts. Secondary sources encompassed KISA incident-response framework documentation, MFDS data-protection directive filings, NIS zero-trust architecture guidelines, and hyperscaler security capex disclosures. Bottom-up segment sizing triangulated against top-down market envelope estimates.
Calibration anchored historical procurement volumes to certified vendor contract announcements and public-sector budget disclosures. Segmentation dimensions modeled span protection type, deployment model, end-user vertical, and solution offering across the projection horizon. CAGRs derived from elasticity-adjusted adoption curves reflecting mandate deadline compression and cloud migration patterns. Industry-specific inputs included NIS zero-trust implementation timelines and KISA encryption-key escrow proposal progression.
The forecast holds incumbent behavior within observed patterns; aggressive moves by cloud-native platform vendors or regulatory deadline acceleration would shift outcomes. Material shifts in KISA data-localization requirements or cross-border threat-intelligence sharing restrictions would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Open RAN Security Market
Cybersecurity
Data Exfiltration Techniques Market
Cybersecurity
Finland Cybersecurity Market
Cybersecurity
South Korea Cybersecurity Market
Cybersecurity
Enterprise Firewall Market
Cybersecurity
Canada Cybersecurity Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Cloud-Based Database Security Market
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
Austria Cybersecurity Market
Cybersecurity
Corporate Web Security Market
Cybersecurity
M2M Network Security Market
Cybersecurity
Internet of Things (IoT) Security Market
Cybersecurity
Data Center Logical Security Market