
 Global Network Forensics Market | 2026-2036
Global Network Forensics Market Size, Share, and Industry Trends Forecast 2026-2036
Global Network Forensics Market Foresight
Cloud-native packet inspection is tilting enterprise security architectures toward continuous traffic monitoring rather than episodic audits. Cisco Systems leverages its networking hardware dominance to embed forensics capabilities directly into switch and router infrastructure. Palo Alto Networks competes through platform consolidation, bundling network forensics with next-generation firewalls and zero-trust access controls. NETSCOUT Systems anchors high-performance carrier and large enterprise deployments with deep-packet inspection appliances engineered for terabit-scale throughput.
Network forensics encompasses the capture, recording, and analysis of network traffic events to reconstruct security incidents, typically operating at line speeds from 1 Gbps to 400 Gbps with full packet retention or metadata extraction depending on storage economics. Its primary purpose is to provide evidentiary-grade reconstruction of cyberattacks for incident response, legal prosecution, and regulatory compliance. Packet capture technology occupies the largest installed base but SaaS-delivered log analysis is expanding fastest as organizations abandon capital-intensive on-premises data lakes. Cloud-based deployment now captures the most active buyer interest among mid-market enterprises lacking dedicated security operations centers, while hybrid architectures dominate among financial institutions requiring air-gapped evidence repositories alongside elastic cloud analytics.
The U.S. Securities and Exchange Commission mandates four-day breach disclosure timelines for publicly traded entities, compelling investment in automated forensics pipelines. The EU Network and Information Security Directive 2 extends incident reporting obligations to critical infrastructure operators across all member states, directly stimulating procurement. Japan's METI cybersecurity framework requires supply-chain risk monitoring that includes network traffic analysis for designated critical service providers. Stakeholders must weigh sovereign data residency requirements against cloud analytics performance when architecting multi-jurisdiction forensics platforms.
Market Dynamics
Cloud-native packet inspection architectures are compressing the traditional boundary between network operations and security operations, forcing vendors to rebuild their platforms for continuous telemetry rather than episodic forensic audits.
Growth Catalysts
- SEC disclosure mandates:The U.S. Securities and Exchange Commission's four-day breach notification rule compels publicly traded entities to deploy automated forensics pipelines capable of near-real-time incident reconstruction.
- EU NIS2 Directive:The Network and Information Security Directive 2 extends mandatory incident reporting to critical infrastructure operators across all member states, directly stimulating procurement of carrier-grade inspection appliances.
- Critical service provider obligations:Japan's METI cybersecurity framework requires supply-chain risk monitoring through network traffic analysis for designated providers, expanding the addressable base beyond traditional enterprise buyers.
Market Restraints
- Storage cost volatility:Full packet retention at 400 Gbps line rates demands petabyte-scale infrastructure, with flash memory and cold storage pricing fluctuations compressing margins for on-premises deployments.
- Silicon supply concentration:Custom ASICs for deep-packet inspection at terabit scale depend on fabrication capacity concentrated in Taiwan, creating vulnerability to geopolitical disruption.
- Encryption proliferation:TLS 1.3 and post-quantum cryptographic standards render passive packet inspection ineffective without certificate management infrastructure that many organizations lack.
Strategic Opportunities
- Mid-market SaaS penetration:Cloud-delivered log analysis and metadata extraction creates accessible entry points for mid-sized enterprises lacking dedicated security operations centers, particularly in Germany and Japan.
- AI-integrated anomaly detection:Convergence of machine learning inference engines with streaming packet capture enables predictive threat hunting, opening subscription revenue models beyond forensic reconstruction.
- Sovereign cloud mandates:Data residency requirements under the EU AI Act and GDPR stimulate demand for regionally isolated forensics platforms with elastic cloud analytics performance.
Industry Challenges
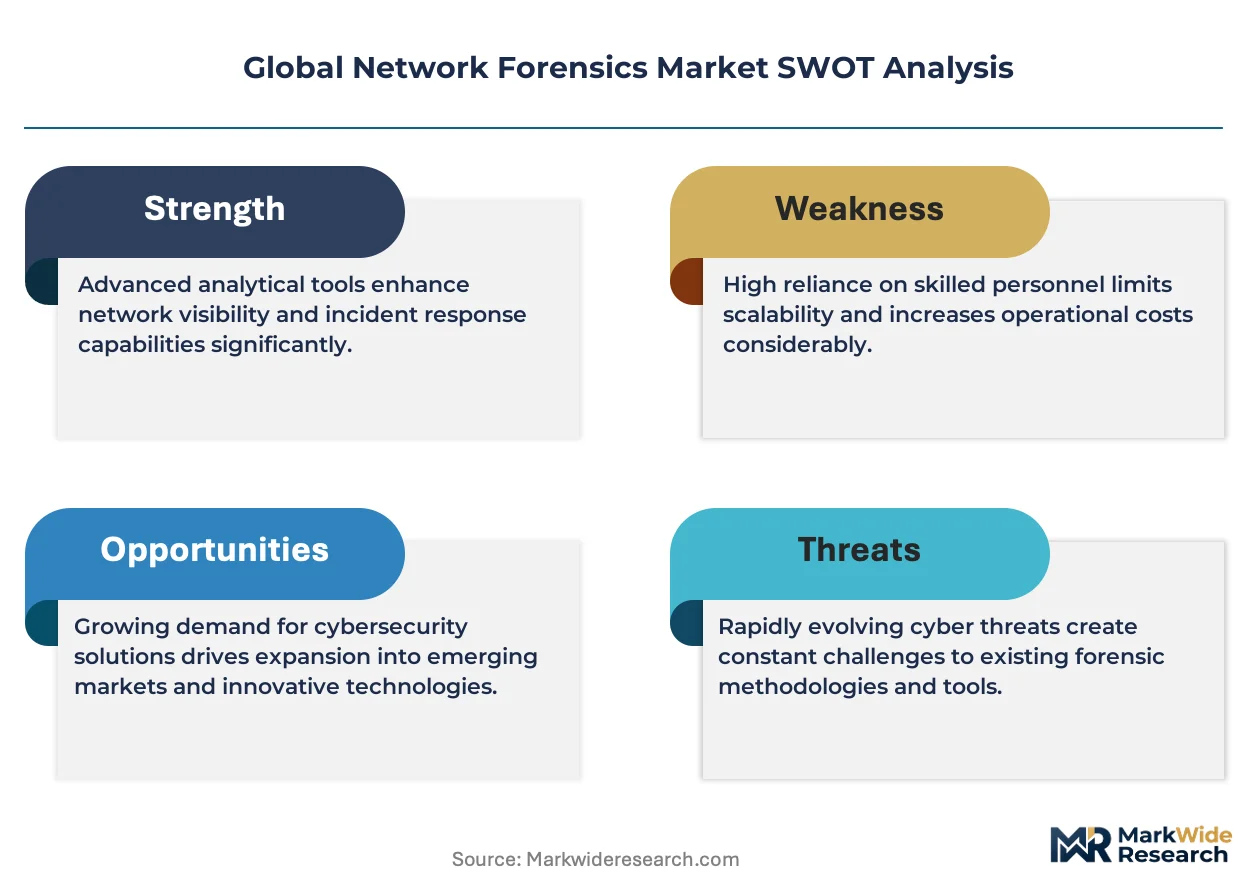
- Forensic analyst scarcity:Organizations struggle to staff security operations centers with personnel capable of reconstructing multi-stage attacks from raw packet captures and correlating evidence across hybrid cloud boundaries.
- Air-gapped integration complexity:Financial institutions require evidence repositories physically isolated from production networks, forcing vendors to engineer bidirectional data pipelines that maintain chain-of-custody integrity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Network Forensics Market |
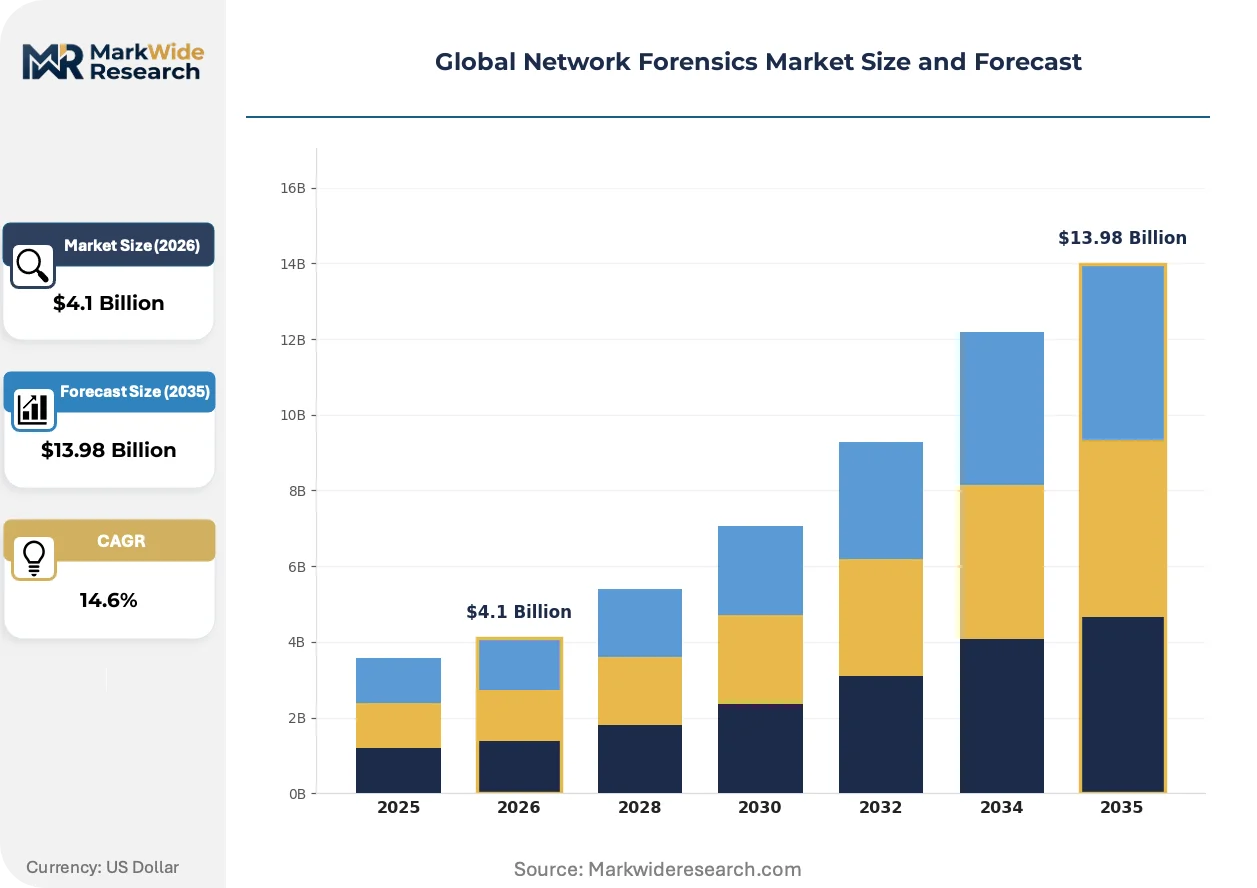
| Market Size in 2026 | $4.1 Billion |
| Market Size in 2035 | $13.98 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Packet Capture, Log Analysis, Malware Analysis, Intrusion Detection Deployment: Cloud-Based, On-Premises, Hybrid, SaaS End User: Cybersecurity Firms, Government Agencies, Financial Institutions, Healthcare Providers Application: Incident Response, Threat Hunting, Compliance Management, Evidence Collection |
| Companies Covered | Cisco Systems, IBM Corporation, Broadcom, Trellix, NETSCOUT Systems, Palo Alto Networks, VIAVI Solutions, LogRhythm, RSA Security, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Network Forensics Market Shifts & Advancements
Telemetry architectures are shifting from batch-oriented forensic investigation toward continuous security monitoring, compressing the detection-to-response timeline and redefining how evidence quality is preserved under real-time constraints.
Extended Berkeley Packet Filter instrumentation is collapsing the performance gap between kernel-space packet capture and user-space analysis. Large financial institutions in New York and London are deploying eBPF-based sensors at 100 Gbps edge locations, eliminating the need for dedicated hardware appliances in branch offices. This kernel-native approach is collapsing capital expenditure requirements for distributed forensics coverage while maintaining evidentiary standards for regulatory examination.
The EU AI Act's risk-based classification system imposes documentation and auditability requirements on automated decision systems used for threat detection. Network forensics vendors must now engineer explainability features that trace machine-generated alerts back to specific packet signatures and behavioral baselines. European critical infrastructure operators face the most stringent compliance burden, driving procurement of platforms with embedded audit trails rather than black-box detection engines.
Security-conscious buyers are unbundling forensic capabilities from bundled security service contracts, preferring specialized vendors with dedicated packet capture expertise over generalist managed security providers. This disintermediation is most pronounced among German automotive manufacturers and Japanese precision equipment makers, where proprietary operational technology networks demand vendor-specific forensic tooling rather than generic log aggregation services.
Global Network Forensics Market Segmentation
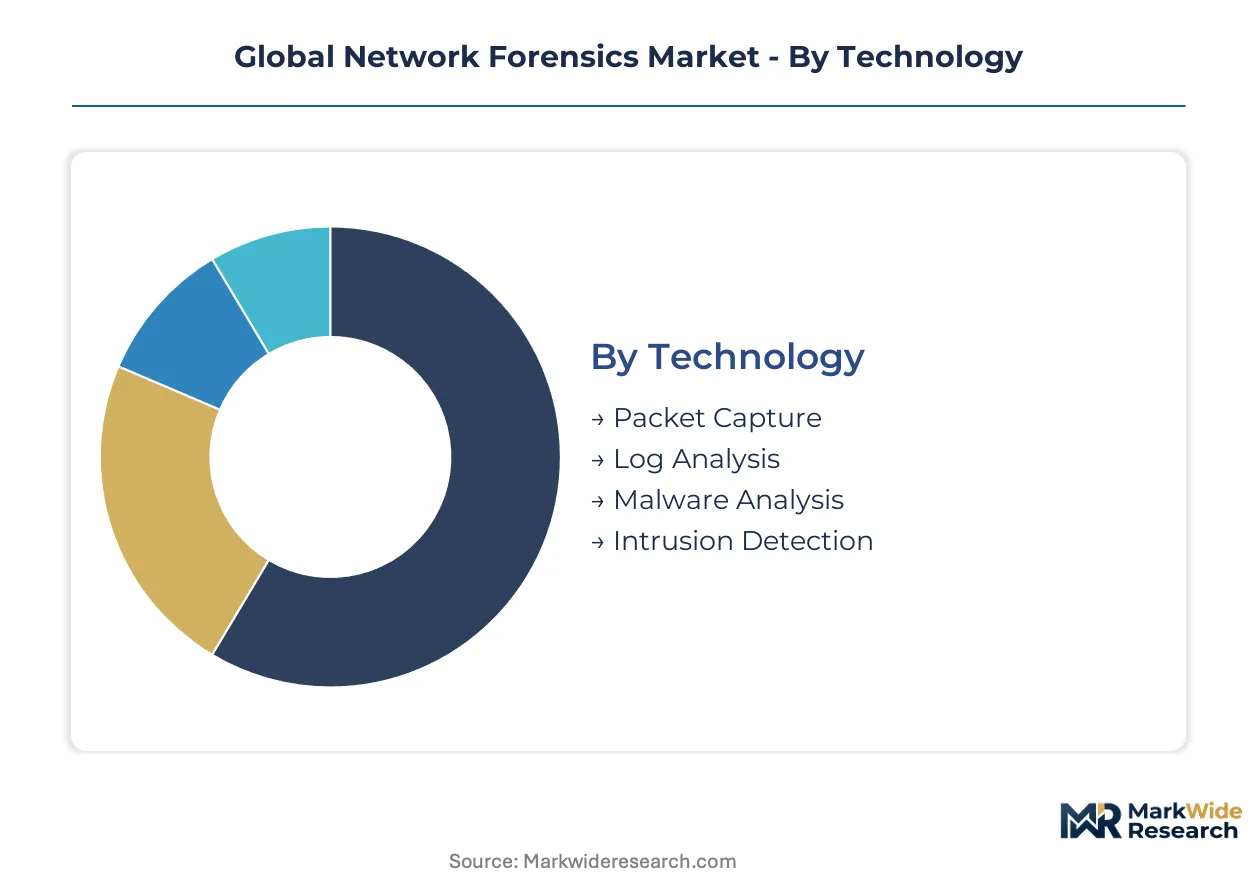
Network forensics vendors engineer distinct product architectures for each deployment context, with service intensity varying dramatically between cloud-native subscriptions and hardware-intensive on-premises installations. Technical support obligations, firmware update cadences, and evidence custody protocols differ fundamentally across these boundaries, reshaping vendor profitability profiles and customer lifetime value calculations.
Technology:
After-sales-service intensity peaks with packet capture deployments requiring continuous hardware maintenance, firmware certification, and chain-of-custody documentation for legal admissibility.
- Packet Capture:Full-packet retention systems operate at line speeds from 1 Gbps to 400 Gbps, storing petabyte-scale traffic repositories for evidentiary reconstruction. Demand concentrates among U.S. financial institutions facing SEC four-day breach disclosure mandates, with storage cost volatility compressing margins for on-premises deployments.
- Log Analysis:Metadata extraction and centralized log correlation platforms process event streams without full payload retention. German automotive manufacturers favor these systems for proprietary operational technology networks where vendor-specific tooling outperforms generic aggregation services.
- Malware Analysis:Sandboxing environments execute suspicious payloads in isolated containers to characterize behavioral signatures. Japan's METI cybersecurity framework drives procurement among designated critical service providers requiring supply-chain risk visibility.
- Intrusion Detection:Signature and anomaly-based systems generate alerts from traffic pattern analysis without comprehensive recording. Mid-market enterprises lacking dedicated security operations centers adopt these for lightweight threat visibility.
Packet Capture holds the largest share; momentum sits with Log Analysis as organizations abandon capital-intensive data lakes.
Deployment:
Cost tier stratification separates enterprise buyers with dedicated infrastructure budgets from mid-market adopters prioritizing operational expenditure predictability over capital deployment flexibility.
- Cloud-Based:Elastic compute resources scale analytics throughput without hardware procurement cycles. European critical infrastructure operators face EU AI Act documentation requirements that favor platforms with embedded audit trails and explainable machine-generated alerts.
- On-Premises:Air-gapped appliances maintain physical isolation between evidence repositories and production networks. Financial institutions in New York and London deploy these for regulatory examination readiness despite higher capital expenditure requirements.
- Hybrid:Bidirectional pipelines synchronize isolated evidence storage with cloud analytics while preserving chain-of-custody integrity. This architecture dominates among financial institutions requiring both air-gapped repositories and elastic processing capacity.
- SaaS:Subscription-delivered log analysis and metadata extraction eliminates security operations center infrastructure requirements. Mid-sized enterprises in Germany and Japan represent the most active buyer cohort for this accessible entry point.
Hybrid deployments capture the most active enterprise buyer interest; SaaS is expanding most quickly among mid-market adopters.
End User:
Application complexity and integration requirements vary sharply across buyer categories, with government procurement cycles extending 18-24 months while financial services demand 90-day implementation timelines.
- Cybersecurity Firms:Managed security providers and specialized consultancies deploy multi-tenant platforms serving heterogeneous client environments. These buyers unbundle forensic capabilities from bundled service contracts, preferring dedicated packet capture expertise.
- Government Agencies:Sovereign cyber defense capabilities in the United States, Germany, and Japan drive classified procurement of carrier-grade inspection appliances. EU NIS2 Directive obligations extend across member states, stimulating public sector investment.
- Financial Institutions:SEC disclosure mandates compel automated forensics pipelines capable of near-real-time incident reconstruction. These organizations require the most stringent evidence custody protocols and air-gapped integration architectures.
- Healthcare Providers:HIPAA obligations intersect with ransomware recovery requirements, driving investment in traffic reconstruction for breach impact assessment. Smaller provider networks lack dedicated security personnel, favoring simplified deployment models.
Financial Institutions represent the most concentrated revenue base; Healthcare Providers are gaining share fastest as ransomware recovery requirements harden.
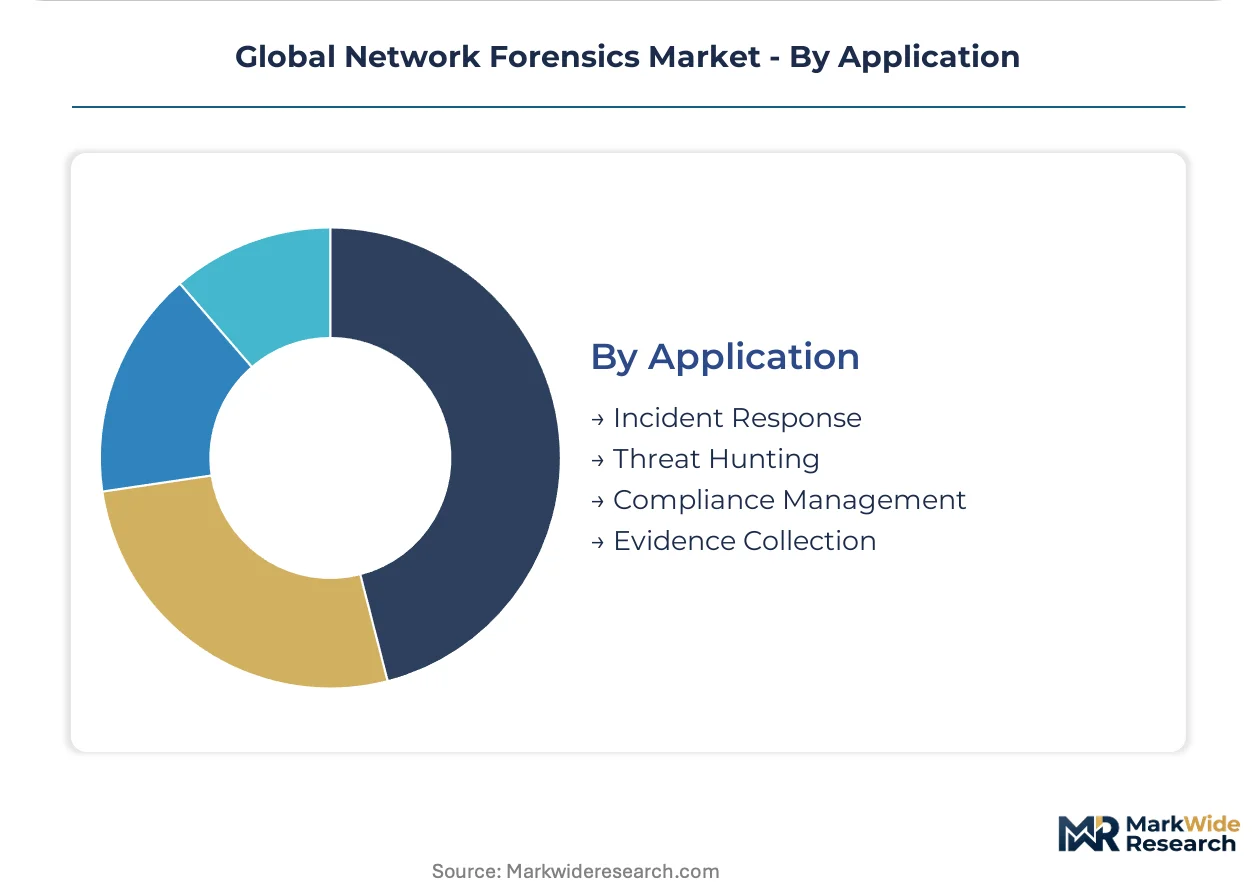
Application:
Volume concentration aligns with regulatory enforcement intensity, where mandated disclosure timelines transform forensic reconstruction from retrospective investigation into real-time operational capability.
- Incident Response:Post-breach traffic reconstruction and timeline development for containment and eradication decisions. U.S. publicly traded entities automate these pipelines to meet compressed disclosure windows.
- Threat Hunting:Proactive hypothesis-driven exploration of historical traffic for undetected adversary presence. Machine learning inference engines converging with streaming capture enable predictive detection beyond signature-based alerting.
- Compliance Management:Continuous monitoring and documentation for regulatory examination readiness. EU AI Act risk-based classification imposes auditability requirements on automated decision systems used for threat detection.
- Evidence Collection:Forensically sound capture and preservation for legal prosecution and civil litigation. Chain-of-custody integrity requirements drive specialized tooling investments distinct from operational security platforms.
Incident Response holds the largest share; Threat Hunting exhibits the steepest expansion trajectory as telemetry architectures shift toward continuous monitoring.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export-import dynamics in network forensics tilt toward technology-exporting economies with advanced cybersecurity manufacturing bases. The United States, Germany, and Japan run structural surpluses in high-performance inspection appliances, while import-dependent markets in Southeast Asia and the Middle East absorb these systems through defense and critical infrastructure procurement channels.
United States
Financial institutions in New York and Chicago drive concentrated procurement of carrier-grade packet capture systems to satisfy SEC four-day breach disclosure mandates. The Cybersecurity and Infrastructure Security Agency coordinates sovereign cyber defense investments across federal agencies and designated critical infrastructure operators. Silicon Valley engineering clusters supply kernel-native eBPF instrumentation that collapses capital expenditure requirements for distributed forensics coverage.
Germany
Automotive manufacturers in Bavaria and Baden-Württemberg unbundle forensic capabilities from generic managed security contracts, demanding vendor-specific tooling for proprietary operational technology networks. The EU NIS2 Directive extends mandatory incident reporting obligations to critical infrastructure operators across all member states, directly stimulating procurement of compliant inspection platforms. Frankfurt's financial services corridor anchors continental Europe's densest concentration of air-gapped evidence repository deployments.
Japan
METI's cybersecurity framework mandates supply-chain risk monitoring through network traffic analysis for designated critical service providers, expanding procurement beyond traditional enterprise buyers. Tokyo and Osaka metropolitan areas concentrate demand for deep-packet inspection appliances engineered for terabit-scale carrier throughput. Domestic semiconductor fabrication capabilities reduce vulnerability to Taiwan supply concentration affecting custom ASIC availability elsewhere.
United Kingdom
London's financial services sector automates forensics pipelines to meet compressed disclosure windows under overlapping SEC and domestic regulatory jurisdictions. The National Cyber Security Centre certifies inspection platforms for critical national infrastructure protection, creating procurement preference for vendor solutions with embedded audit trails. Scottish and Northern English data center clusters host regionally isolated forensics platforms satisfying GDPR data residency requirements.
Singapore
The city-state's position as Southeast Asia's financial hub generates demand for hybrid forensics architectures balancing sovereign data controls with elastic cloud analytics performance. Monetary Authority of Singapore cybersecurity guidelines mandate traffic monitoring for systemically important financial institutions. Regional headquarters of multinational corporations locate security operations centers in Singapore to serve Asia-Pacific subsidiaries with compliant, centralized forensics capabilities.
Global Network Forensics Market Competitive Landscape
On the supply side, the industry is consolidating around platform vendors with networking hardware dominance and specialized deep-packet inspection appliance manufacturers. Three strategic archetypes define competitive positioning: networking incumbents embedding forensics into infrastructure hardware, cybersecurity platforms bundling forensics with adjacent controls, and pure-play specialists engineering high-throughput carrier-grade systems. Dominant competitive moves include strategic partnerships to integrate kernel-native instrumentation and portfolio diversification into SaaS-delivered log analysis for mid-market penetration.
Among networking-centric vendors, Cisco Systems leverages infrastructure hardware dominance to embed forensics capabilities directly into switch and router deployments. Palo Alto Networks occupies the platform consolidation tier, bundling network forensics with next-generation firewalls and zero-trust access controls. NETSCOUT Systems anchors the specialized appliance segment, engineering deep-packet inspection systems for terabit-scale carrier and large enterprise throughput requirements. These three exemplify how vendor archetypes map to distinct buyer segments across financial services, critical infrastructure, and telecommunications verticals.
| Leading Market Players |
|---|
| Cisco Systems |
| IBM Corporation |
| Broadcom |
| Trellix |
| NETSCOUT Systems |
| Palo Alto Networks |
| VIAVI Solutions |
| LogRhythm |
| RSA Security |
| Others |
Supply & Pricing Matrix
Trans-Pacific shipping corridors linking Taiwan to Los Angeles and Long Beach anchor cost dynamics for deep-packet inspection hardware, where concentrated ASIC fabrication capacity in East Asia amplifies pricing power for carrier-grade appliance vendors while compressing margins for systems integrators lacking volume scale. This logistics-cost asymmetry stratifies downstream price differentiation between financial institutions demanding air-gapped evidence repositories and mid-market buyers accepting SaaS-delivered alternatives.
Pricing Analysis
Current-generation 400 Gbps packet capture systems command substantial premiums over prior-generation 100 Gbps platforms, while next-generation terabit-scale appliances remain pre-commercial with pricing yet to stabilize. Three-tier pricing structure across premium, standard, and economy levels reflects certification grade differentiation, with ISO 27001 and FIPS 140-2 compliance tiers separating enterprise buyers from mid-market adopters. Price erosion runs through the economy tier as cloud-native log analysis vendors compress subscription pricing to capture security operations center automation demand. Mid-market enterprises lacking dedicated forensic analysts exhibit highest price sensitivity, while financial institutions facing SEC disclosure mandates accept premium positioning for evidentiary-grade chain-of-custody documentation.
Supply Chain Analysis
Extended payment terms and supply-chain finance facilities from Taiwanese foundries sustain working capital for deep-packet inspection appliance manufacturers, with 90-120 day receivables cycles now standard for carrier-grade equipment procurement. Custom ASIC fabrication concentrates in Taiwan and South Korea, with downstream assembly drawing from China and Mexico manufacturing bases. Flash memory and cold storage components sourced from South Korean and Japanese suppliers create single-source vulnerability to geopolitical disruption. Distribution runs through authorized value-added resellers serving financial services verticals, with direct enterprise sales dominating carrier and government agency procurement channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Forensic analyst scarcity constrains security operations center scaling across buyer segments, with kernel-native instrumentation expertise and evidentiary chain-of-custody protocol engineering representing critical capability gaps that reshape competitive outcomes.
For Market Incumbents: Insulate carrier-grade appliance margins through captive ASIC design partnerships with Taiwanese foundries, reducing exposure to silicon supply concentration that threatens custom hardware availability. Deepen vertical integration into eBPF-based sensor software to collapse branch-office deployment costs and preempt kernel-native entrants from commoditizing distributed forensics coverage. Certification investment in EU AI Act explainability documentation preserves pricing power among European critical infrastructure operators facing automated decision system audit requirements. For New Entrants and Emerging Players: Mid-market healthcare providers in the United States represent the most penetrable entry point, with HIPAA breach notification obligations and ransomware recovery requirements creating procurement urgency among networks lacking dedicated security personnel. German automotive manufacturers' proprietary operational technology networks offer second-mover opportunity through vendor-specific forensic tooling that outperforms generic log aggregation services. SaaS-delivered metadata extraction with embedded compliance documentation enables rapid deployment without security operations center infrastructure requirements. For Investors and Strategic Acquirers: Specialized deep-packet inspection appliance manufacturers with terabit-scale carrier relationships anchor acquisition interest, as platform consolidation by networking incumbents eliminates standalone viability for sub-scale hardware vendors. Long-term viability hinges on subscription revenue transition beyond forensic reconstruction toward predictive threat hunting and continuous monitoring services. Watch for inflection in mid-market SaaS penetration rates among German and Japanese enterprises, where security operations center automation demand signals platform consolidation opportunity.| Strategic Initiative | Industry Significance |
|---|---|
| Kernel-Native Sensor Development | eBPF instrumentation collapses capital expenditure for distributed branch-office forensics coverage. |
| EU AI Act Compliance Certification | Explainability documentation preserves pricing power among European critical infrastructure operators. |
| Mid-Market SaaS Expansion | Subscription delivery captures healthcare providers lacking dedicated security operations centers. |
| Carrier-Grade ASIC Partnership | Taiwanese foundry relationships secure terabit-scale deep-packet inspection fabrication capacity. |
| Hybrid Architecture Integration | Bidirectional pipelines synchronize air-gapped evidence storage with elastic cloud analytics performance. |
Research Methodology
Findings reconcile primary fieldwork against secondary review of SEC disclosure filings, EU regulatory guidance documents, hyperscaler infrastructure expenditure disclosures, and carrier network equipment procurement records. Primary interviews engaged chief information security officers at financial institutions, security operations center directors at managed security providers, forensic analysts at specialized consultancies, and network engineering leads at telecommunications carriers. Bottom-up triangulation across deployment volume estimates and top-down validation against infrastructure investment flows ensure analytical coherence.
Forecast inputs incorporate technology adoption curves across packet capture, log analysis, malware analysis, and intrusion detection segments, with deployment model stratification by cloud-based, on-premises, hybrid, and SaaS delivery. Organization size tiers, vertical regulatory intensity, and regional sovereign cyber defense investment patterns structure the projection framework. CAGRs derive from segment-level growth rate reconciliation against aggregate market expansion across the analysis window. Encryption proliferation timelines and post-quantum cryptographic standard migration pace represent industry-specific forecast sensitivity inputs.
Macroeconomic conditions sit as an overlay; deviation in semiconductor fabrication capacity utilization, flash memory pricing volatility, or cross-border data transfer regulatory enforcement would shift the trajectory. Forecasts reflect documented assumptions regarding TLS 1.3 adoption rates and eBPF kernel instrumentation maturity. Macroeconomic, regulatory, or technological deviation would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Wireless Lan Security Market
Cybersecurity
Kuwait Cybersecurity Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Saas-Based IT Security Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
Qatar Cybersecurity Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
Austria Cybersecurity Market
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
SOC As a Service Market
Cybersecurity
Global Digital Forensic Laboratory As a Service Market
Cybersecurity
Global SSH Terminal Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
SSL VPN Market