
 Global Ddos Protection Market | 2026-2036
Global Ddos Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Global Ddos Protection Market Analysis
Israeli security engineering talent is decoupling from legacy hardware-centric delivery models toward cloud-native mitigation architectures. Akamai Technologies leverages its globally distributed edge network to absorb volumetric attacks before they reach customer origin servers. Cloudflare sustains pricing pressure through integrated CDN and zero-trust bundling that anchors DDoS protection within broader security contracts. Fortinet competes by embedding mitigation directly into its SD-WAN and firewall appliances, reducing vendor sprawl for mid-market enterprises.
DDoS protection encompasses traffic scrubbing, rate limiting, and behavioral analysis systems engineered to sustain throughput exceeding 10 Tbps during peak volumetric events while maintaining sub-millisecond latency for legitimate requests. Its primary commercial purpose is preserving application availability and revenue continuity during coordinated attacks that exploit network protocol weaknesses or application-layer resource exhaustion. Cloud-based deployment leads the technology dimension as enterprises abandon capex-heavy on-premises appliances in favor of elastic scrubbing capacity. Hybrid architectures are growing fastest among regulated financial institutions that must keep sensitive traffic on-premise while bursting to cloud during extreme events. Consulting and incident response services capture expanding margin pools as boards demand retainer-based preparedness rather than reactive procurement.
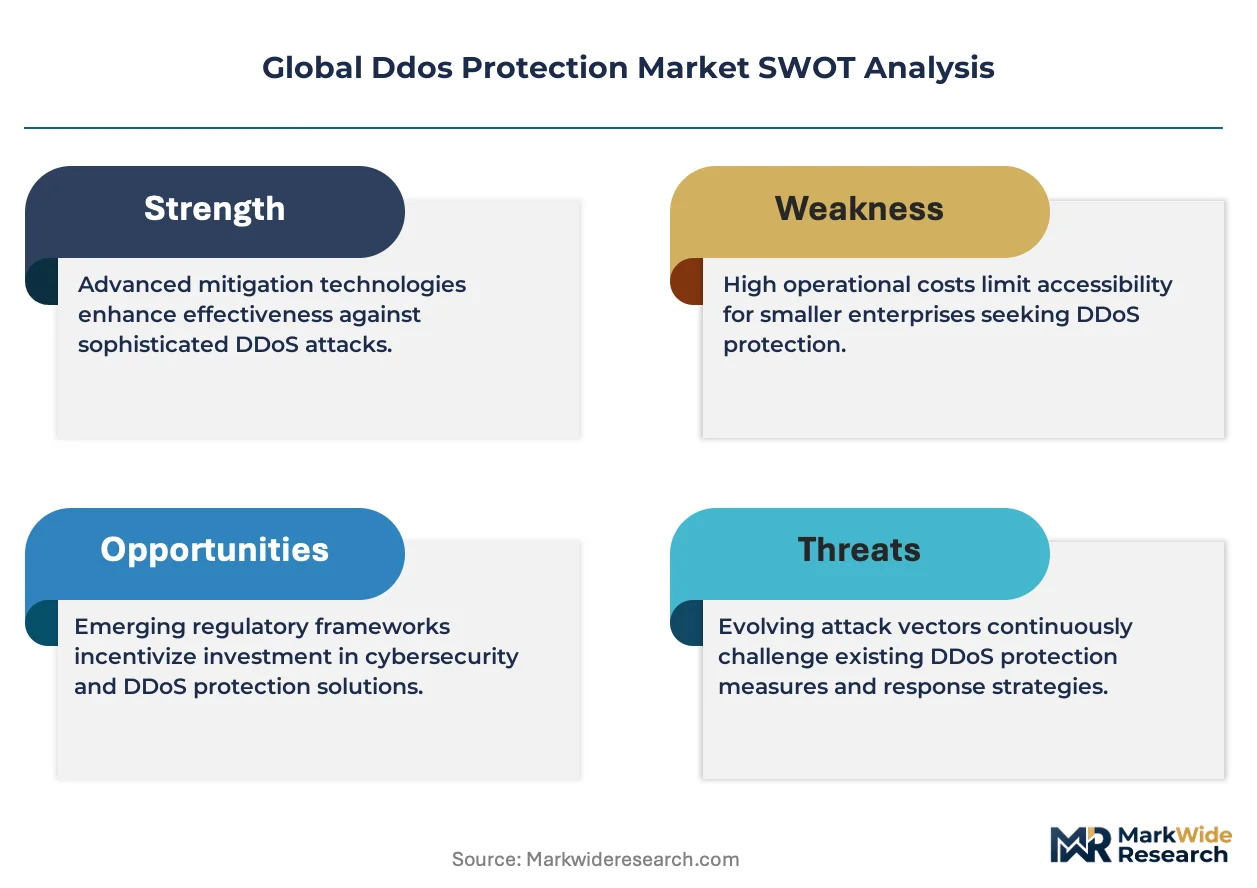
The FCC in the United States enforces communications reliability standards that shape carrier-grade mitigation investments, while the EU NIS2 Directive imposes mandatory risk management and incident reporting obligations across critical sectors. Japan's METI coordinates national cyber exercises that directly stimulate procurement from domestic and foreign protection vendors. Stakeholders must monitor how sovereign data-localization mandates fragment cloud-scrubbing architectures and whether AI-generated attack traffic forces fundamental redesigns of detection heuristics.
Market Dynamics
Cloud-native scrubbing architectures are displacing hardware-centric delivery models as sovereign cyber defense mandates force infrastructure localization across multiple jurisdictions.
Growth Catalysts
- EU NIS2 Directive:Mandatory risk management and incident reporting obligations across critical sectors are accelerating procurement cycles for financial institutions and energy operators.
- Financial services:Always-on cloud scrubbing services are becoming standard infrastructure as payment networks face escalating ransom-driven attack volumes.
- Behavioral analysis:AI-powered detection heuristics are expanding addressable market by reducing false-positive rates that previously blocked legitimate traffic.
Market Restraints
- Elastic capacity costs:Cloud-scrubbing pricing volatility during peak attack events compresses margins for managed security service providers.
- Talent concentration:Israeli security engineering clusters dominate advanced mitigation development, creating single-geography supply risk.
- Data-localization mandates:Sovereign requirements fragment cloud architectures and duplicate infrastructure investment across national boundaries.
Strategic Opportunities
- Germany:Critical infrastructure operators under NIS2 face compliance deadlines creating immediate demand for hybrid on-premise and cloud-scrubbing solutions.
- 5G network slicing:Telco-grade mitigation integrated directly into mobile core networks opens carrier distribution channels previously closed to standalone vendors.
- Zero-trust convergence:Bundling DDoS protection with identity and access management platforms captures expanded security budgets from CISO consolidation mandates.
Industry Challenges
- Detection latency:Sub-millisecond legitimate request processing requirements conflict with deep-packet inspection needed for encrypted attack traffic.
- Legacy appliance integration:Financial institutions with sunk capital in on-premise scrubbing centers face forklift upgrade costs to achieve cloud-burst elasticity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Ddos Protection Market |
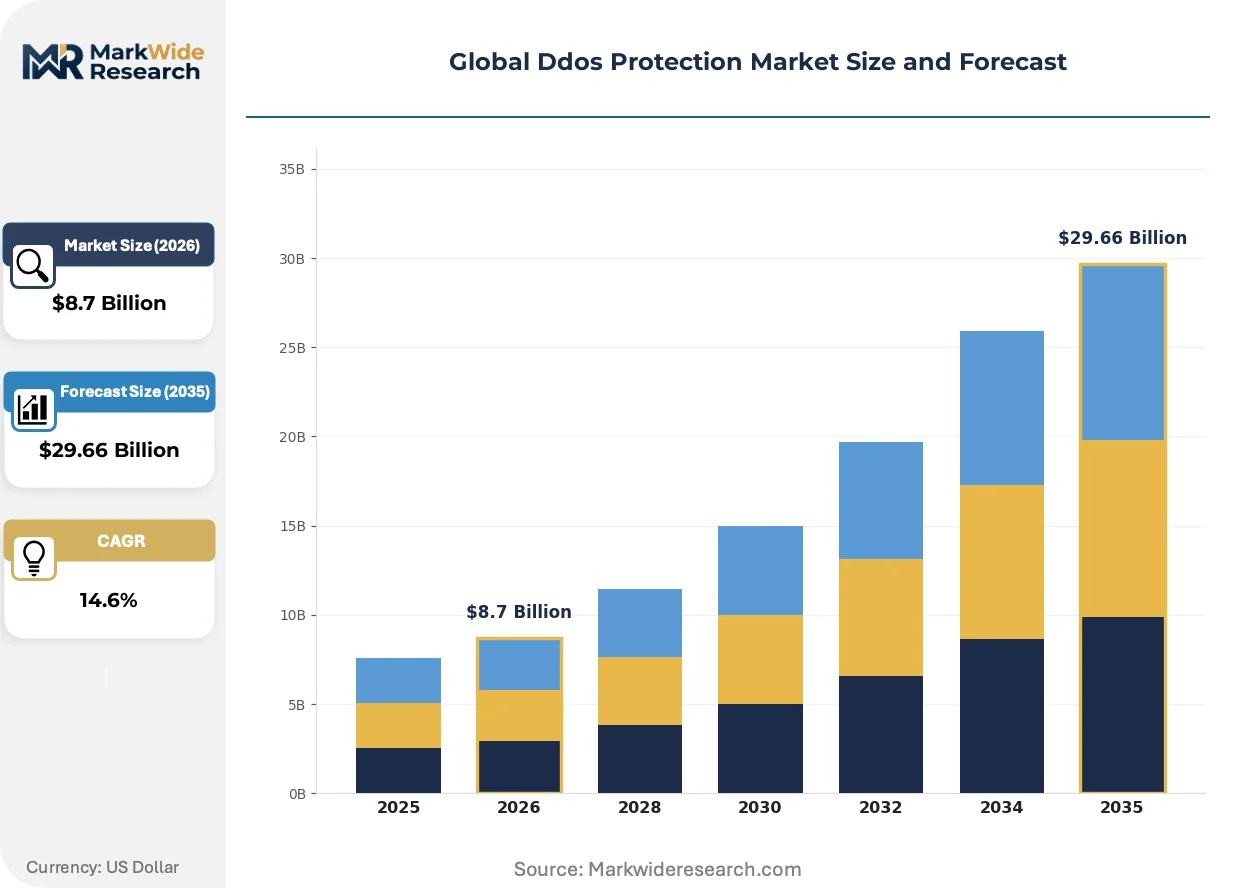
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $29.66 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: On-Premises, Cloud-Based, Hybrid, Software-Defined Service Type: DDoS Mitigation, Monitoring Service, Incident Response, Consulting End User: Retail, Healthcare, Finance, Education Deployment: Public Sector, Private Sector, Telecom, Hosting Provider |
| Companies Covered | Akamai Technologies, Cloudflare, NetScout Systems, Radware, Fortinet, Imperva, F5, A10 Networks, Corero Network Security, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Ddos Protection Market Emerging Trajectories
Attack surface expansion through IoT botnets and API proliferation is forcing fundamental redesign of traffic inspection architectures away from perimeter-based models.
Edge-computing scrubbing nodes are unifying volumetric absorption and application-layer protection within the same physical infrastructure. Tier-one carriers in Japan and the United States are deploying these converged platforms to eliminate backhaul latency to centralized data centers. This unification compresses vendor count in enterprise security stacks from separate network and application specialists toward integrated edge platforms.
The EU NIS2 Directive imposes mandatory 24-hour incident reporting and resilience testing across energy, transport, and digital infrastructure operators. Critical infrastructure procurement now requires demonstrable compliance certification as a gate to contract award. German and French operators are responding by embedding continuous validation into vendor selection criteria rather than treating compliance as post-implementation documentation.
Retainer-based incident response is displacing reactive procurement following board-level pressure for demonstrable preparedness. Financial services and e-commerce platforms in the United States are shifting from per-attack billing to fixed-fee preparedness contracts that include simulation exercises and forensic readiness. This restructures vendor revenue toward predictable recurring streams and away from event-driven spikes.
Global Ddos Protection Market Segmentation
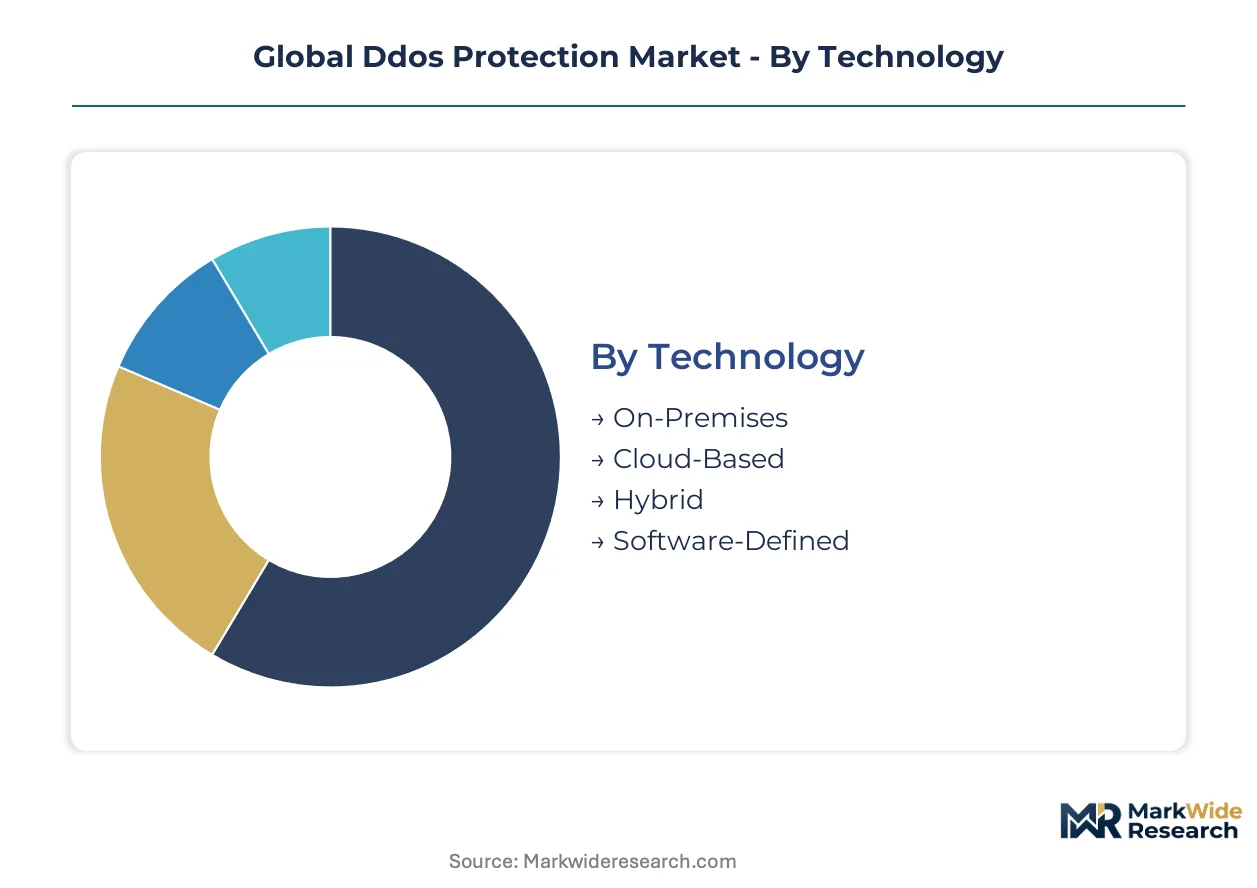
DDoS protection architectures fragment across technology maturity, service bundling, and sector-specific compliance burdens. Each segment carries distinct certification requirements from FCC reliability standards to EU NIS2 resilience mandates.
Technology:
EU NIS2 and FCC reliability standards impose divergent infrastructure mandates across deployment modes, with critical infrastructure operators facing the heaviest compliance documentation.
- Cloud-Based:Elastic scrubbing capacity absorbs volumetric attacks exceeding 10 Tbps through globally distributed edge nodes. Financial services firms in the United States and Germany are standardizing on always-on cloud delivery to satisfy board-level resilience mandates while avoiding capex-heavy infrastructure.
- Hybrid:Burst-to-cloud architectures preserve sensitive traffic on-premise while scaling to cloud during extreme events. Regulated institutions across Germany and Japan favor this model for its data-localization compliance without sacrificing elasticity during peak attacks.
- On-Premises:Hardware-centric appliances dominate legacy installations in defense-sensitive facilities.
- Software-Defined:Virtualized mitigation layers deploy across commodity infrastructure for rapid provisioning.
Cloud-Based sits at the top of the volume ranking, with Hybrid climbing the fastest.
Service Type:
Margin pools concentrate in recurring preparedness contracts rather than reactive event billing, restructuring vendor revenue toward predictable streams.
- DDoS Mitigation:Real-time traffic scrubbing and rate limiting systems process legitimate requests with sub-millisecond latency. Tier-one carriers in Japan deploy converged volumetric and application-layer protection to eliminate backhaul delays.
- Incident Response:Retainer-based forensic readiness and simulation exercises displace per-attack procurement. United States financial services boards now mandate demonstrable preparedness, capturing expanded security budgets.
- Monitoring Service:Continuous traffic analysis detects anomalous patterns before volumetric saturation.
- Consulting:Compliance certification and resilience testing gate contract awards under EU NIS2.
DDoS Mitigation commands the largest revenue share, with Incident Response expanding most quickly.
End User:
Sector-specific attack surfaces dictate protection architecture choices, with payment networks and healthcare records facing distinct regulatory exposure.
- Finance:Payment networks face escalating ransom-driven attack volumes requiring always-on protection. United States and German institutions accelerate procurement of integrated scrubbing services to preserve transaction continuity.
- Healthcare:Patient data protection under HIPAA and equivalent frameworks drives hybrid deployments. Japanese medical systems prioritize edge-computing nodes to maintain diagnostic application availability during attacks.
- Retail:E-commerce platforms require sub-millisecond latency preservation during peak shopping events.
- Education:Research networks face targeted disruption during international collaboration periods.
Finance leads absolute spending, with Healthcare gaining share fastest.
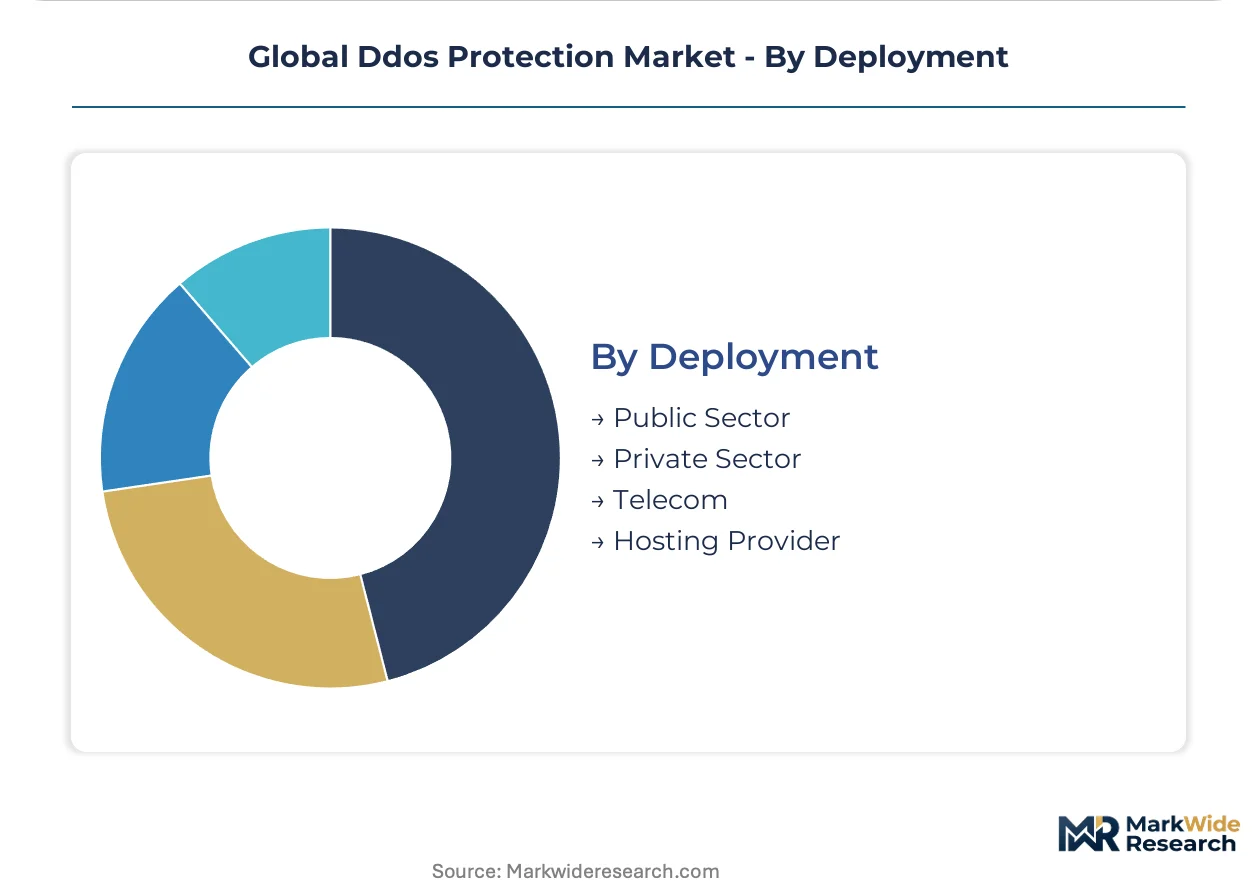
Deployment:
Channel structure determines pricing leverage, with carrier-integrated solutions commanding premium positioning over standalone vendor relationships.
- Telecom:5G network slicing embeds mitigation directly into mobile core infrastructure. Japanese and United States tier-one carriers deploy scrubbing nodes at the network edge, opening distribution channels previously closed to standalone vendors.
- Hosting Provider:Multi-tenant protection consolidates demand across customer portfolios. German and French operators embed continuous validation into vendor selection criteria under NIS2 compliance pressure.
- Private Sector:Enterprise procurement favors bundled zero-trust and CDN-integrated solutions.
- Public Sector:Sovereign cyber defense mandates drive infrastructure localization requirements.
Telecom dominates carrier-grade procurement, with Hosting Provider climbing fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The United States maintains deeper carrier-grade scrubbing infrastructure than Germany, yet Japanese regulators are orchestrating faster national cyber exercise cadences that directly stimulate procurement volumes.
United States
FCC reliability standards enforce communications resilience mandates that shape tier-one carrier mitigation investments. Financial services boards in New York and Chicago now mandate always-on protection as standard infrastructure for payment network continuity. Silicon Valley cloud providers anchor the dominant edge-computing scrubbing architectures displacing hardware-centric models.
Germany
Critical infrastructure operators under EU NIS2 face immediate compliance deadlines for hybrid on-premise and cloud-scrubbing solutions. The national cyber regulator mandates 24-hour incident reporting across energy and transport sectors. Frankfurt's financial district concentrates procurement activity as banks embed continuous validation into vendor selection criteria.
Japan
METI coordinates national cyber exercises that stimulate direct procurement from domestic and foreign protection vendors. Tier-one carriers deploy converged volumetric and application-layer protection at network edges to eliminate backhaul delays. Tokyo and Osaka medical systems prioritize edge-computing nodes to maintain diagnostic application availability during attacks.
United Kingdom
Financial conduct regulators impose operational resilience deadlines that accelerate cloud-scrubbing procurement for London-based payment networks. The national cyber security centre mandates demonstrable preparedness through simulation exercises. The Thames Valley technology corridor hosts expanding security engineering clusters developing behavioral analysis systems.
Israel
Security engineering talent clusters dominate advanced mitigation development for cloud-native architectures. Domestic innovation programs support decoupling from legacy hardware-centric delivery models toward elastic scrubbing capacity. Tel Aviv's cybersecurity district anchors research into AI-powered detection heuristics reducing false-positive rates.
Global Ddos Protection Market Vendor Landscape
United States producers anchor one tier of cloud-scrubbing capacity; Israeli specialists hold advanced behavioral analysis development. The vendor base separates into three functional tiers: globally distributed edge networks, integrated security platform bundlers, and hardware-embedded mitigation appliance manufacturers. Consolidation pressure intensifies as zero-trust convergence and CDN integration reshape procurement patterns toward bundled contracts. Dominant competitive moves include strategic partnerships with tier-one carriers and geographic expansion through localized scrubbing nodes.
Within the edge-network tier, Akamai Technologies and Cloudflare occupy positions exemplifying globally distributed infrastructure scale. Fortinet anchors the integrated-platform archetype through embedded mitigation within broader security stacks. These three represent divergent strategic vectors: pure-play cloud absorption, bundled zero-trust delivery, and hardware-anchored hybrid deployment.
| Leading Market Players |
|---|
| Akamai Technologies |
| Cloudflare |
| NetScout Systems |
| Radware |
| Fortinet |
| Imperva |
| F5 |
| A10 Networks |
| Corero Network Security |
| Others |
Supply Flow & Price Mechanics
Israeli security engineering clusters in Tel Aviv and Herzliya concentrate cloud-native mitigation talent, creating labor-cost differentials that widen pricing-tier spreads between premium behavioral-analysis platforms and commoditized volumetric-scrubbing services.
Pricing Analysis
Capacity additions in the United States are reshaping price floors for cloud-scrubbing services as hyperscaler edge networks absorb volumetric attacks at scale. Pricing stratifies across premium, standard, and economy tiers based on attack-volume thresholds and compliance certification levels. Cost compression in the standard tier intensifies because Cloudflare and Akamai bundle DDoS protection within broader CDN contracts. Managed security service providers face the highest price sensitivity, while financial institutions under NIS2 mandates accept premium pricing for demonstrable resilience certification.
Supply Chain Analysis
FCC reliability certification and EU NIS2 compliance documentation gate vendor participation in carrier-grade procurement across the United States, Germany, and Japan. Hardware components for on-premise appliances draw from Taiwan semiconductor foundries, Israeli FPGA design houses, and United States-based ASIC manufacturers. Single-source vulnerability concentrates in specialized packet-processing silicon from Taiwanese suppliers. Distribution runs through tier-one telecom carriers, hosting providers, and managed security service providers with direct enterprise relationships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a geographic-arbitrage play: Israeli engineering talent costs one-third less than Silicon Valley equivalents, yet produces behavioral-analysis systems that command premium pricing in Frankfurt and Tokyo compliance-driven procurement.
For Market Incumbents: Hedge against margin erosion in commoditized volumetric scrubbing by embedding mitigation deeper into SD-WAN and zero-trust bundles. Fortinet's appliance-integrated approach demonstrates channel control leverage that pure-play cloud vendors struggle to replicate. Capacity additions in Germany under NIS2 deadlines offer defensive positioning against hyperscaler pricing pressure. For New Entrants and Emerging Players: Enter via compliance-certification services rather than scrubbing infrastructure, as German critical infrastructure operators lack internal documentation capacity for NIS2 demonstration. The most penetrable segment is mid-market healthcare in Japan, where METI exercises have stimulated awareness but domestic vendor supply remains thin. A channel partnership with Tokyo-based systems integrators accelerates trust-building faster than direct enterprise sales. For Investors and Strategic Acquirers: Tier-one carriers seeking 5G network-slicing capabilities are the most active acquirer in this space, driving valuations for edge-computing scrubbing specialists. Targets with hybrid-deployment expertise and existing NIS2 certification workflows offer the strongest long-term viability as data-localization mandates fragment pure-cloud architectures. The signal to watch is sovereign cyber defense budget announcements from Japan's METI and Germany's BSI, which directly correlate with procurement acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Edge Network Expansion | Akamai's distributed scrubbing nodes absorb 10+ Tbps attacks before origin saturation. |
| Zero-Trust Platform Integration | Cloudflare bundles DDoS protection with identity management, capturing consolidated CISO budgets. |
| Hybrid Deployment Certification | German NIS2 compliance deadlines create immediate demand for on-premise and cloud-burst architectures. |
| 5G Network Slicing Partnership | Japanese tier-one carriers embed mitigation into mobile core infrastructure, closing standalone vendor channels. |
| Incident Response Retainer Models | United States financial services boards mandate preparedness contracts, restructuring vendor revenue toward recurring streams. |
Methodological Framework
Coverage spans the United States, Germany, Japan, Israel, and the United Kingdom, with primary inputs from each regional cluster. The research combines interviews with CISOs at financial institutions, carrier network architects, compliance officers under NIS2 mandates, and managed security service provider executives with secondary validation from FCC filings, EU regulatory databases, METI procurement records, and hyperscaler capex disclosures. Bottom-up triangulation across deployment-mode segmentation and top-down validation against carrier infrastructure investment patterns anchor the analytical framework.
Rate-of-change decomposition separates volume growth from value expansion across the projection horizon. The forecast framework models technology deployment modes, service type bundling, end-user sector compliance burdens, and geographic regulatory clusters. CAGRs derive from elasticity-adjusted adoption curves for cloud-native versus hybrid architectures. Attack-volume trajectories from IoT botnet proliferation and API surface expansion feed directly into capacity-demand modeling.
Inputs from carrier procurement databases and regulatory filing systems were available through the study window; gaps in real-time attack-volume telemetry from private sector operators introduce uncertainty bands around peak-event capacity requirements. Forecasts reflect assumptions about NIS2 enforcement consistency and sovereign data-localization mandate proliferation. A model refresh is warranted upon material change in EU cyber resilience directive implementation timelines or FCC reliability standard revisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Global Container and Kubernetes Security Market
Cybersecurity
Global Healthcare IoT Security Market
Cybersecurity
Singapore Cybersecurity Market
Cybersecurity
Education Data Security Market
Cybersecurity
Firewall-As-A-Service (Fwaas) Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Cloud-Based IDS IPS Market
Cybersecurity
Global Database Encryption Market
Cybersecurity
Japan Ransomware Protection Market
Cybersecurity
Nigeria Cybersecurity Market
Cybersecurity
Content Delivery Network (CDN) Security Market
Cybersecurity
Europe Software Defined Perimeter Market
Cybersecurity
Micro-Segmentation Solutions Market