
 Global Database Encryption Market | 2026-2036
Global Database Encryption Market Size, Share, and Industry Trends Forecast 2026-2036
Global Database Encryption Market Analysis
A global shortage of cryptographers and cloud-security architects is collapsing implementation timelines for enterprise database encryption projects. IBM Corporation leverages its mainframe heritage and quantum-safe cryptography research to anchor high-assurance deployments in regulated industries. Microsoft Corporation competes through native integration of Azure SQL transparent data encryption across hybrid cloud estates. Thales Group specializes in hardware security module-backed key management, sustaining premium positioning in government and defense verticals.
Database encryption encompasses cryptographic techniques that protect structured data at rest, in transit, and during processing through algorithms such as AES-256, with transparent data encryption operating at the database engine layer to eliminate application-level code changes. Its primary commercial purpose is to render stored data unintelligible to unauthorized parties while preserving query performance and operational continuity for legitimate users. Transparent data encryption dominates deployment volume among large enterprises seeking minimal application disruption, while database column encryption captures margin concentration in healthcare and financial services where field-level granularity supports granular access control. Cloud-based deployment is expanding fastest as AWS, Azure, and Google Cloud embed encryption-by-default into managed database services, though on-premises solutions retain structural importance in jurisdictions with data sovereignty requirements.
The US Federal Risk and Authorization Management Program (FedRAMP) and the EU General Data Protection Regulation (GDPR) together shape procurement standards by mandating encryption for sensitive government and personal data, effectively filtering vendors without certified implementations. The US Health Insurance Portability and Accountability Act (HIPAA) Security Rule and the California Consumer Privacy Act (CCPA) further segment demand by imposing specific technical safeguards on covered entities. Stakeholders must monitor evolving post-quantum cryptography standards from NIST and determine migration timelines before cryptanalytically relevant quantum computers destabilize current asymmetric encryption foundations.
Market Dynamics
Post-quantum cryptography migration timelines are compressing procurement cycles as NIST standardization accelerates enterprise anxiety over asymmetric encryption vulnerabilities. Financial services and government agencies now demand crypto-agility frameworks that isolate quantum-vulnerable algorithms from core database infrastructure.
Growth Catalysts
- HIPAA Security Rule enforcement:US healthcare providers face escalating breach penalties, forcing transparent data encryption deployment across electronic health record systems.
- Cloud migration velocity:FedRAMP authorization requirements push federal agencies toward managed encryption services with automated key rotation.
- AES-256 hardware acceleration:Modern CPU instruction sets eliminate performance penalties that previously deterred encryption-at-rest adoption in high-throughput environments.
Market Restraints
- Cryptographer scarcity:Global talent shortages extend implementation timelines for enterprise key management infrastructure by 8-14 months.
- Hardware security module concentration:Premium HSM supply chains cluster in Germany and Switzerland, creating procurement bottlenecks for defense-grade deployments.
- Legacy database compatibility:Pre-2015 database engines lack native TDE support, forcing expensive middleware layers or full platform replacements.
Strategic Opportunities
- India's data localization mandate:RBI and SEBI encryption requirements for financial data create demand for sovereign cloud encryption services.
- Confidential computing convergence:Integration of memory encryption with database TDE enables processing of encrypted data without decryption exposure.
- EU Cybersecurity Act certification:Common Criteria evaluation schemes create premium positioning for vendors achieving EAL4+ database encryption ratings.
Industry Challenges
- Key management complexity:Multi-cloud estates fragment key custody across AWS KMS, Azure Key Vault, and Google Cloud HSM, increasing operational risk.
- Post-quantum migration planning:Organizations lack frameworks for algorithm transition without service disruption, delaying NIST PQC standard adoption.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Database Encryption Market |
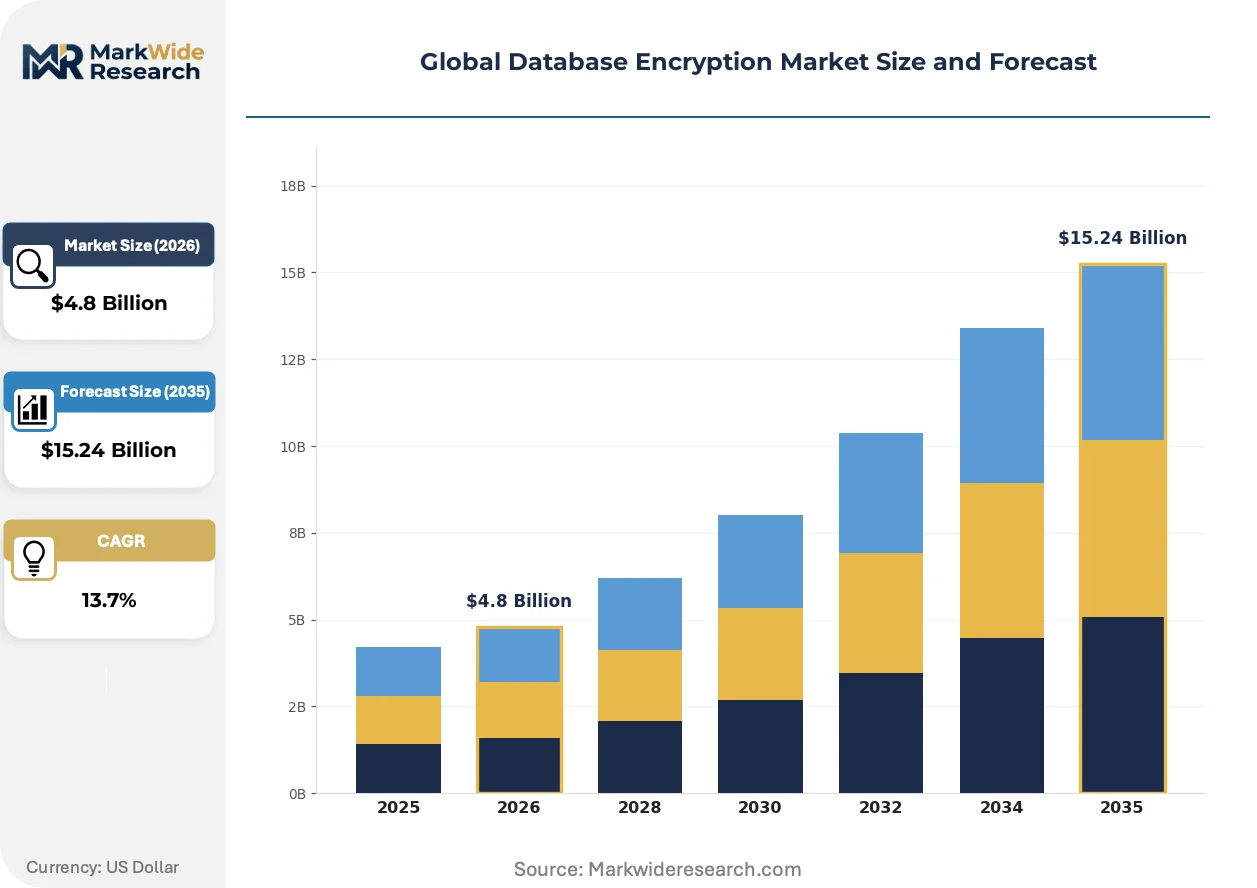
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $15.24 Billion |
| CAGR (2026 – 2036) | 13.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Full Disk Encryption, File/Folder Encryption, Transparent Data Encryption, Database Column Encryption Industry Vertical: Financial Services, Healthcare, Government, Retail Deployment: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Enterprises, SMEs, Government Agencies, Educational Institutions |
| Companies Covered | IBM Corporation, Microsoft Corporation, Oracle Corporation, Symantec Corporation, Thales Group, McAfee, Amazon Web Services, Cisco Systems, Trend Micro, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Database Encryption Market Emerging Trajectories
Database encryption architectures are fragmenting between cloud-native automation and sovereign on-premises control as geopolitical data sovereignty concerns intensify. Vendors must now engineer for regulatory multiplicity rather than unified global deployment patterns.
Homomorphic encryption is bifurcating the analytics market between privacy-preserving computation and traditional decrypted processing models. Pharmaceutical firms and financial risk departments pilot partially homomorphic schemes for cross-institutional data collaboration. The technology is bifurcating vendor roadmaps, forcing separate engineering tracks for performance-optimized versus mathematically rigorous implementations.
GDPR Article 32 technical safeguards and the EU AI Act data governance requirements are mandating encryption-by-design for training datasets containing personal information. German automotive manufacturers now require tier-one suppliers to demonstrate AES-256 encryption for all connected vehicle telemetry storage. French healthcare AI startups face ANSM scrutiny over database encryption adequacy for clinical algorithm development.
Buyer procurement patterns are fragmenting between centralized cybersecurity governance and distributed DevOps autonomy. Large enterprises deploy policy-as-code encryption mandates through infrastructure orchestration platforms, displacing manual database administrator configuration. This shift concentrates most visibly in US technology sector firms adopting GitOps-driven key lifecycle management.
Global Database Encryption Market Segmentation
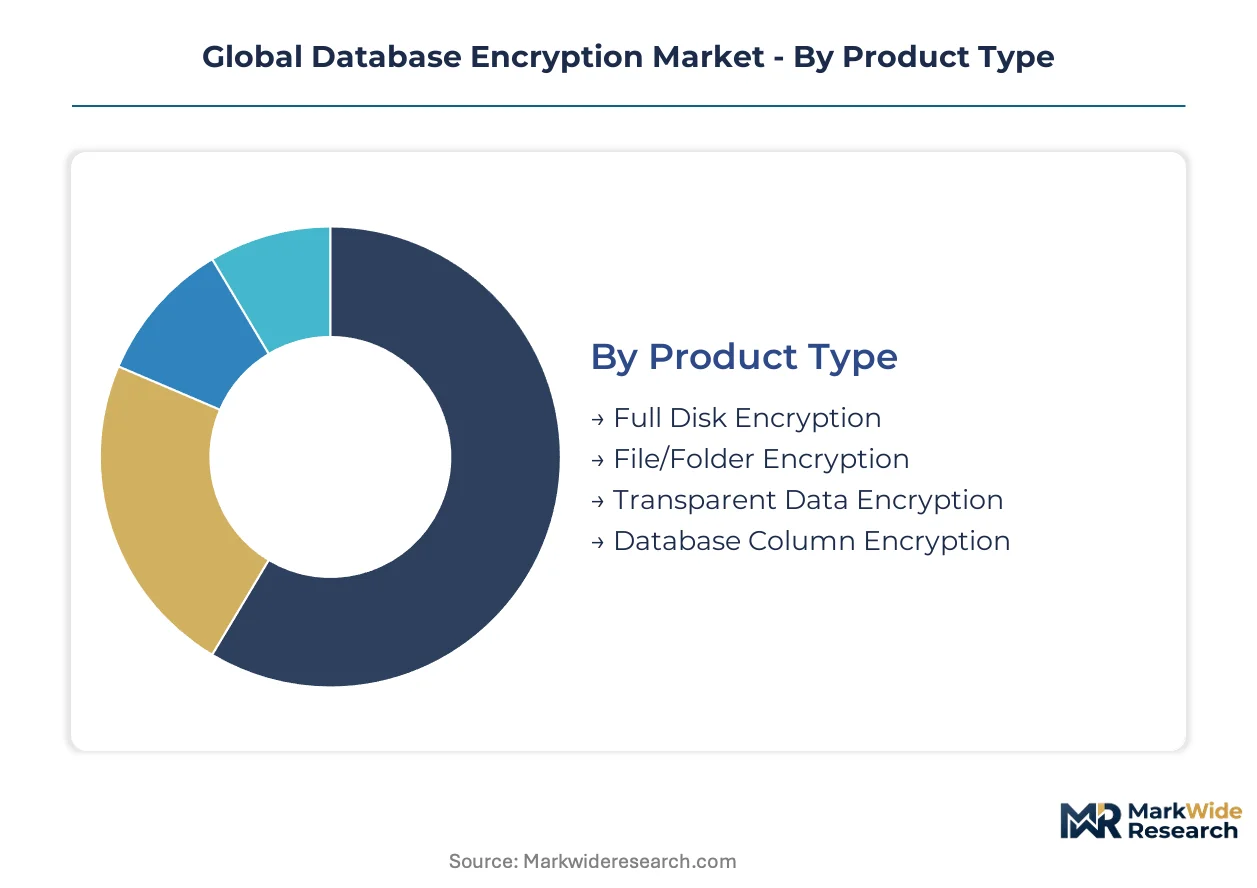
Database encryption architectures diverge sharply across deployment models and regulatory exposure levels. Procurement patterns fragment between legacy on-premises fortification and cloud-native automation, with each segment carrying distinct implementation timelines and talent requirements.
Product Type:
Transparent data encryption faces intensifying substitution pressure from confidential computing architectures that shift cryptographic operations into hardware enclaves. Full disk encryption confronts erosion from file-level granularity demanded by zero-trust frameworks.
- Full Disk Encryption:Encrypts entire storage volumes at the operating system layer using AES-256 block ciphers without application awareness. Demand concentrates in German automotive manufacturing facilities where ANSM-equivalent technical inspectors mandate physical media protection for connected vehicle telemetry archives.
- Transparent Data Encryption:Operates at the database engine layer to encrypt data files automatically, eliminating code changes for existing applications. Financial services firms in the United States deploy this most aggressively as HIPAA Security Rule enforcement hardens liability frameworks for electronic health record adjacent systems.
- File/Folder Encryption:Provides selective protection for specific data containers outside database structures. Japanese pharmaceutical companies utilize this for research dataset compartmentalization under PMDA data integrity guidelines.
- Database Column Encryption:Enables field-level granularity supporting granular access control policies. Healthcare providers in France adopt this for patient identifier isolation under CNIL technical safeguard recommendations.
Transparent data encryption retains volume leadership; database column encryption holds the steepest expansion curve.
Industry Vertical:
Cost tier stratification separates defense-grade deployments from commercial off-the-shelf implementations across verticals. Government and financial services absorb premium pricing for certified configurations while retail operates at standard tiers.
- Financial Services:RBI and SEBI mandates in India drive sovereign cloud encryption procurement for transaction databases. FedRAMP authorization requirements push United States federal credit unions toward managed encryption services with automated key rotation protocols.
- Healthcare:HIPAA Security Rule breach penalties force transparent data encryption across electronic health record systems. German university hospitals deploy AES-256 for clinical algorithm training datasets under EU AI Act data governance requirements.
- Government:Defense-grade deployments require hardware security module concentration from German and Swiss supply chains. Australian federal agencies align with TGA-equivalent information security frameworks for citizen data repositories.
- Retail:Payment card industry compliance drives point-of-sale database protection without specialized cryptographic talent. French e-commerce platforms implement column encryption for customer preference databases under GDPR Article 32 technical safeguards.
Financial services absorbs the highest per-deployment expenditure; healthcare demonstrates the most rapid compliance-driven expansion.
Deployment:
Application context determines architectural choice between control sovereignty and operational velocity. Latency-sensitive transaction processing favors on-premises proximity while analytics workloads migrate to cloud elasticity.
- On-Premises:Retains structural importance in jurisdictions with data sovereignty requirements. Saudi Arabian financial institutions deploy this under SAMA localization mandates for core banking databases.
- Cloud-Based:Expands fastest as AWS, Azure, and Google Cloud embed encryption-by-default into managed database services. South Korean fintech startups leverage this under MFDS-equivalent cloud security guidelines.
- Hybrid:Supports workload portability between regulated on-premises cores and elastic cloud analytics. Canadian provincial health authorities utilize this configuration under Health Canada privacy impact assessment protocols.
- Managed Service:Addresses cryptographer scarcity by outsourcing key lifecycle operations to specialized providers. Brazilian healthcare networks adopt this under ANVISA data protection technical norms.
On-premises installations maintain the largest installed base; managed services are climbing the fastest as talent constraints bite.
End User:
Customer type segmentation reflects procurement autonomy distribution between centralized cybersecurity governance and distributed DevOps teams. Enterprise scale enables dedicated cryptographic architecture functions unavailable to smaller entities.
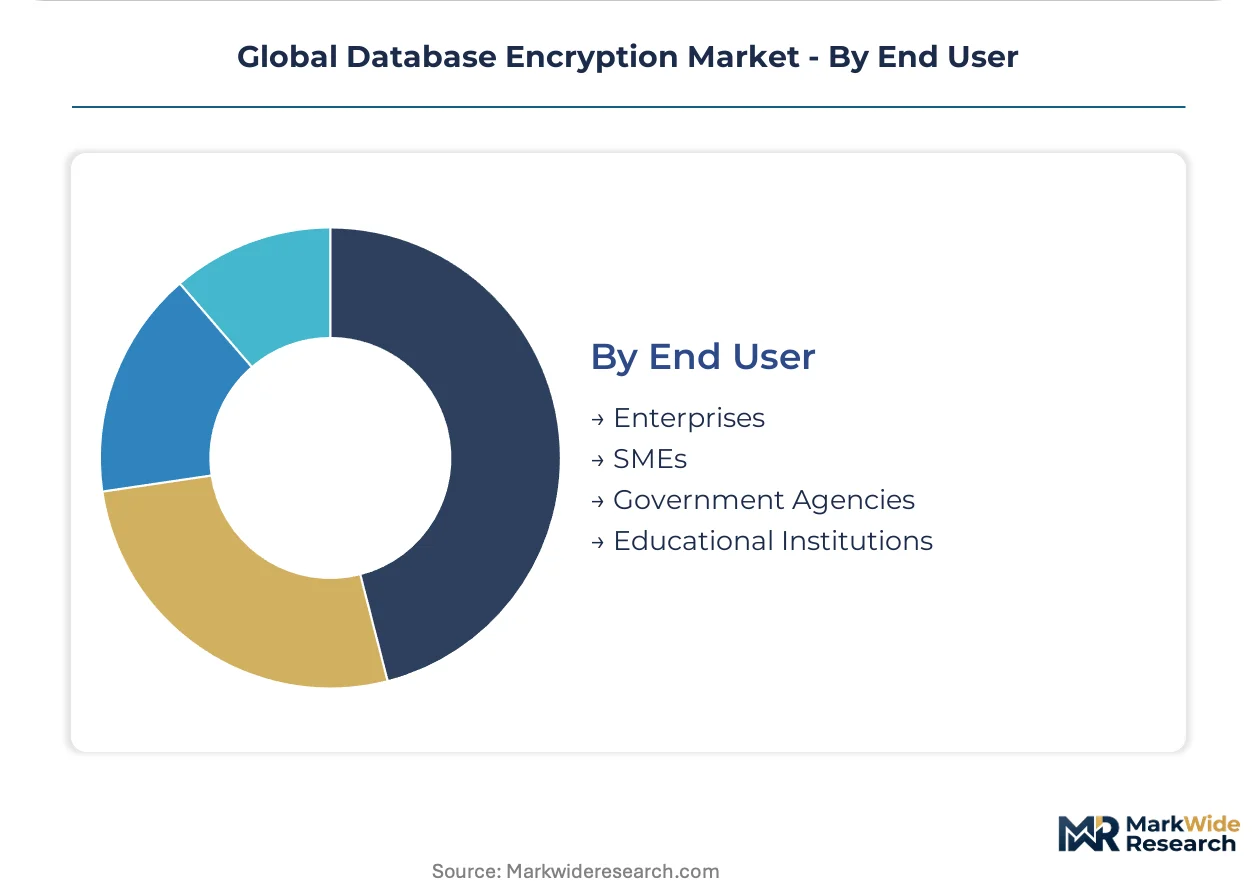
- Enterprises:Deploy policy-as-code encryption mandates through infrastructure orchestration platforms. United States technology sector firms adopt GitOps-driven key lifecycle management across multi-cloud estates.
- SMEs:Rely on cloud-native automation to compensate for absent in-house security architects. Indian manufacturing SMEs utilize RBI-sanctioned encryption templates for supplier data exchange.
- Government Agencies:Demand crypto-agility frameworks isolating quantum-vulnerable algorithms from core infrastructure. United Kingdom central government departments align with NCSC post-quantum migration guidance.
- Educational Institutions:Protect research datasets containing personal information under sector-specific data governance. Australian universities implement this for international student record systems under TGA-equivalent privacy frameworks.
Enterprises dominate absolute deployment counts; government agencies show the most aggressive modernization trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
FedRAMP authorization requirements anchor United States demand, while RBI mandates and EU AI Act data governance rules shape procurement across India and Germany. Sovereign cloud encryption services expand fastest where data localization laws harden.
United States
Financial services firms accelerate transparent data encryption deployment as HIPAA breach penalties escalate and state-level notification laws harden liability. FedRAMP authorization requirements push federal agencies toward managed encryption services with automated key rotation. New York and San Francisco financial technology clusters drive crypto-agility framework adoption for quantum-vulnerable algorithm isolation.
Germany
Automotive manufacturers mandate AES-256 encryption for connected vehicle telemetry storage under EU AI Act data governance requirements. ANSM-equivalent technical inspectors enforce physical media protection standards for manufacturing facilities. Bavarian industrial zones and Stuttgart automotive clusters pilot confidential computing integration with database transparent data encryption.
India
RBI and SEBI encryption requirements for financial data create demand for sovereign cloud encryption services among domestic banks and fintech startups. Data localization mandates under central bank guidelines force on-premises and managed service deployments. Mumbai and Bangalore financial technology corridors absorb the highest per-deployment expenditure for compliance-driven infrastructure.
United Kingdom
NCSC post-quantum migration guidance drives government agency demand for crypto-agility frameworks isolating asymmetric encryption vulnerabilities. Healthcare providers face GDPR Article 32 technical safeguard enforcement for patient record systems. London financial services and Cambridge technology clusters adopt policy-as-code encryption mandates through infrastructure orchestration platforms.
Japan
PMDA data integrity guidelines compel pharmaceutical companies to implement research dataset compartmentalization through file-level encryption. METI cybersecurity frameworks push manufacturing enterprises toward hardware security module-backed key management. Tokyo and Osaka pharmaceutical research corridors deploy column encryption for granular access control under sector-specific data governance.
Global Database Encryption Market Vendor Landscape
Technology leadership and cost leadership are held by different player archetypes across the database encryption market. Consolidation concentrates around cloud hyperscalers embedding encryption-by-default into managed database services, while specialized hardware security module vendors retain premium positioning in defense-grade deployments. Three archetypes dominate: mainframe-heritage systems integrators, cloud-native platform providers, and hardware security specialists. Competitive moves center on confidential computing convergence and post-quantum cryptography certification races.
Within the mainframe-heritage tier, IBM Corporation represents high-assurance deployment anchoring in regulated industries through quantum-safe cryptography research. Microsoft Corporation exemplifies cloud-native platform integration across hybrid cloud estates with native transparent data encryption capabilities. Thales Group occupies a position among hardware security module specialists sustaining premium government and defense vertical positioning through certified key management infrastructure.
| Leading Market Players |
|---|
| IBM Corporation |
| Microsoft Corporation |
| Oracle Corporation |
| Symantec Corporation |
| Thales Group |
| McAfee |
| Amazon Web Services |
| Cisco Systems |
| Trend Micro |
| Others |
Supply Flow & Price Mechanics
Cloud-native encryption services substituting for on-premises hardware security modules are redrawing procurement geography and compressing pricing premiums previously commanded by German and Swiss HSM manufacturers. This substitution simultaneously shifts value capture toward hyperscale cloud providers and erodes the installed-base pricing power of legacy encryption infrastructure vendors.
Pricing Analysis
Geographic price spreads between North American and European deployments exceed those within Asia-Pacific due to FedRAMP certification premiums and EU Cybersecurity Act evaluation costs. Three-tier pricing structure across premium, standard, and economy levels separates defense-grade HSM-backed deployments from commercial SaaS tiers and open-source implementations. Pricing pressure stems from AWS, Azure, and Google Cloud embedding encryption-by-default at no incremental cost. SMEs exhibit highest price sensitivity and gravitate toward consumption-based managed services; government agencies absorb premium pricing for certified configurations.
Supply Chain Analysis
HSM semiconductor fabrication chokepoints in Taiwan and South Korea constrain supply elasticity for defense-grade encryption deployments. Hardware security module production draws from specialized foundry capacity, precision analog components, and tamper-resistant packaging substrates. Single-source vulnerability concentrates in European HSM final assembly facilities. Distribution runs through systems integrators and direct hyperscaler marketplaces rather than traditional value-added resellers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Post-quantum cryptography standardization by NIST is accelerating enterprise procurement cycles and creating first-mover advantages for vendors with crypto-agility frameworks. This regulatory inflection compresses migration timelines and favors vendors with certified quantum-safe implementations.
For Market Incumbents: Consolidate around confidential computing integration and quantum-safe certification races to defend against cloud-native entrants. IBM Corporation and Thales Group should deepen backward integration into post-quantum algorithm R&D. Acquire specialist key management SaaS providers to offset middleware displacement by native cloud encryption.
For New Entrants and Emerging Players: Lead with sovereign cloud encryption services in India and Saudi Arabia where data localization mandates create compliance-driven demand. Target managed encryption services for healthcare SMEs facing HIPAA breach penalties. Deploy partner-led go-to-market through systems integrators serving federal agencies.
For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors crypto-agility platform providers over point-solution HSM vendors. Long-term viability hinges on post-quantum migration services revenue streams. Watch NIST PQC algorithm finalization as the signal for enterprise procurement acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Quantum-Safe Certification | NIST PQC algorithm validation enables FedRAMP authorization for federal database deployments. |
| Confidential Computing Integration | Intel SGX and AMD SEV enclaves extend TDE into memory-encrypted processing environments. |
| Sovereign Cloud Partnership | RBI-sanctioned data localization meets SEBI encryption requirements for Indian financial institutions. |
| Key Management SaaS Acquisition | Automated key rotation capabilities address cryptographer scarcity in enterprise implementations. |
| Homomorphic Encryption R&D | Privacy-preserving analytics enable pharmaceutical cross-institutional collaboration under PMDA guidelines. |
Methodological Framework
The analysis maps transparent data encryption, database column encryption, full disk encryption, and confidential computing architectures, each validated through chief information security officers, cloud infrastructure architects, federal procurement officers, and healthcare IT directors. Primary interviews with these stakeholders combined with secondary validation against SEC 10-K filings, FedRAMP authorization databases, and EU Cybersecurity Act certification registries. Bottom-up deployment estimates triangulated against top-down market sizing from hyperscaler capex disclosures.
Consistency checks validated volume and value outputs against external benchmarks across deployment model, organization size, vertical regulatory exposure, and regional data sovereignty requirements. CAGRs derived from segment-level growth rate reconciliation with macro technology adoption curves. Forecast inputs incorporated NIST post-quantum standardization timelines and cloud migration velocity indices.
Forecasts assume regulatory continuity in FedRAMP authorization regimes and EU GDPR enforcement; material policy shifts would require re-modeling. Specific risk factors include cryptographer talent availability, HSM supply chain constraints, and quantum computing advancement timelines. Practitioners should keep alternative scenarios live as NIST PQC standardization and data localization mandates evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Global Automated Breach and Attack Simulation (BAS) Market
Cybersecurity
CDN Security Market
Cybersecurity
Firewall-As-A-Service (Fwaas) Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Europe Web Application Firewall Market
Cybersecurity
Global Bug Bounty Platforms Market
Cybersecurity
Digital Immune System Market
Cybersecurity
Wireless Lan Security Market
Cybersecurity
Education Data Security Market
Cybersecurity
Asia Pacific IoT Security Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Global Breach and Attack Simulation Market