
 Cloud-Based IDS IPS Market | 2026-2036
Cloud-Based IDS IPS Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud-Based IDS IPS Market Outlook
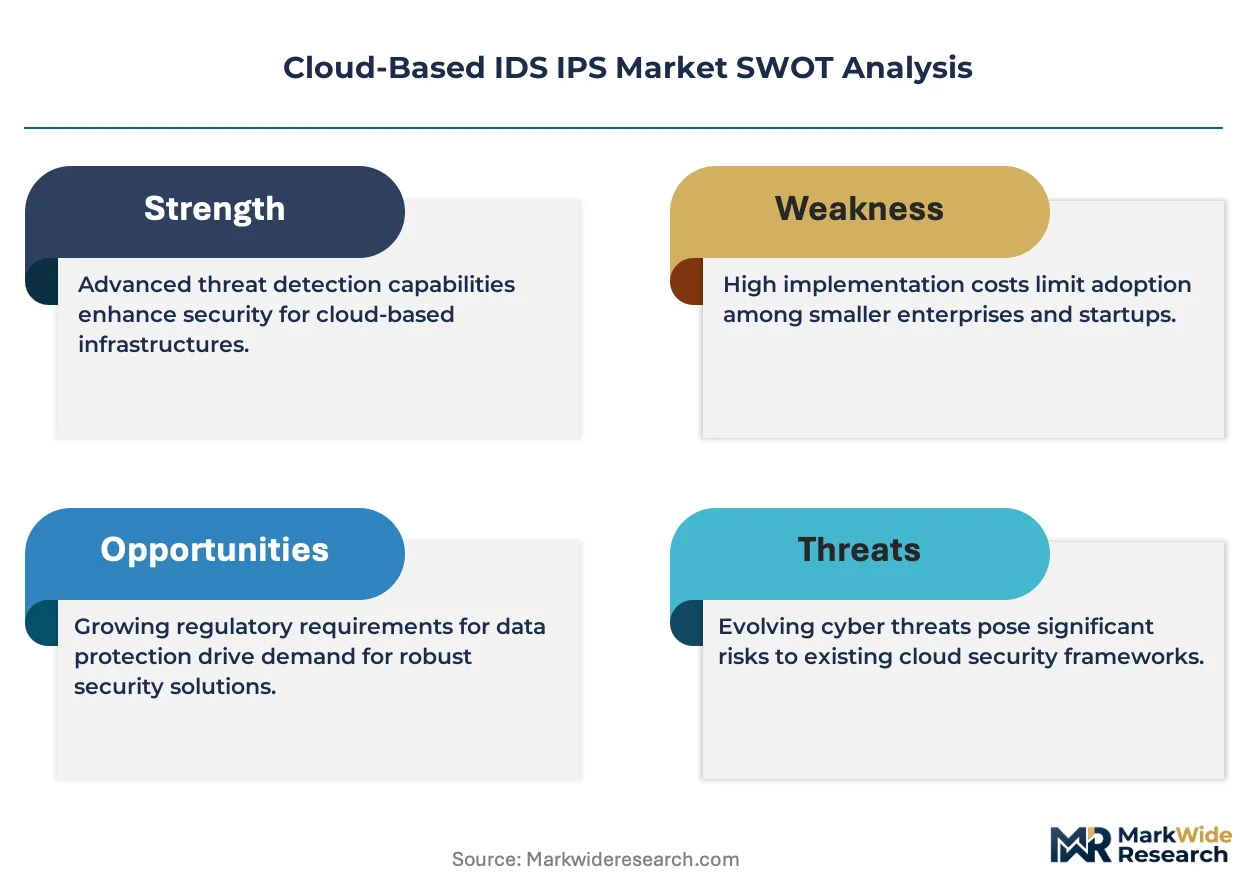
Enterprise-grade threat detection is rotating toward AI-augmented behavioral analysis as the baseline specification tier across cloud workloads. Palo Alto Networks leverages machine-learning inference pipelines to sustain differentiation in large enterprise accounts. Fortinet anchors its position through integrated firewall-IDS convergence and aggressive channel density. Cisco Systems dominates hybrid cloud deployments with native telemetry fabrics that span on-premises and multi-cloud estates.
Cloud-based intrusion detection and prevention systems monitor network traffic and system activities across distributed cloud infrastructures using real-time packet inspection, flow analysis, and automated response orchestration to identify and block malicious behavior before data exfiltration or service disruption occurs. The hybrid cloud deployment segment captures the largest addressable base as organizations retain sensitive workloads on private infrastructure while bursting analytics to public environments. Signature-based solutions still occupy the majority of installed instances, though anomaly-based detection is recording the fastest expansion as zero-day exploits render static rule libraries insufficient against polymorphic threats. Behavior-based analytics concentrates margin pools in government and regulated financial verticals where dwell-time reduction commands premium pricing.
NIST cybersecurity frameworks, the EU NIS2 Directive, and PCI DSS compliance mandates collectively shape procurement specifications by requiring continuous monitoring, automated incident response, and auditable detection logs for cloud-hosted payment and personal data. HIPAA security rules enforce comparable technical safeguards for healthcare cloud migrations, while GDPR Article 32 obligations drive European enterprises toward policy-based detection with documented data-breach notification triggers. Stakeholders must evaluate whether their current detection architectures can satisfy converging compliance requirements without fragmenting into jurisdiction-specific tool stacks.
Market Dynamics
Zero-day exploit proliferation is compressing dwell-time tolerance thresholds across cloud-hosted workloads, forcing detection architectures toward sub-second automated response loops that bypass human-in-the-middle approval chains.
Growth Catalysts
- NIS2 Directive:The EU mandate for continuous monitoring and incident reporting is compelling critical infrastructure operators to replace periodic audits with real-time detection fabrics.
- Behavioral analytics:Machine-learning inference pipelines trained on cloud-native telemetry streams are capturing budget allocations previously assigned to signature-based rule maintenance.
- Financial services:Payment card industry data security standards are driving tier-one banks toward unified cloud security platforms that consolidate detection, response, and compliance logging.
Market Restraints
- Skilled analyst scarcity:The talent pool for cloud-native security operations center staffing remains concentrated in Germany, Japan, and the United States, inflating deployment costs elsewhere.
- Encryption blind spots:Widespread TLS 1.3 adoption is degrading packet inspection visibility without corresponding investments in decryption proxy infrastructure.
- Alert fatigue:High false-positive rates from poorly tuned anomaly detection are driving operational teams toward alert suppression rather than investigation protocols.
Strategic Opportunities
- Sovereign cloud frameworks:Germany's Gaia-X initiative and comparable national data sovereignty programs are creating procurement pathways for EU-hosted detection infrastructure.
- Healthcare migration:HIPAA-covered entities moving electronic health records to cloud environments require specialized detection architectures with documented audit trails.
- Extended detection and response convergence:Integration of endpoint detection with network-level intrusion prevention is opening consolidated platform contracts previously split between vendors.
Industry Challenges
- Multi-cloud telemetry normalization:Security teams struggle to correlate alerts across AWS, Azure, and Google Cloud native logging formats without expensive middleware development.
- Compliance timeline compression:NIS2's 24-hour incident notification window is forcing organizations to rebuild detection-to-ticket workflows that previously allowed 72-hour assessment periods.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud-Based IDS IPS Market |
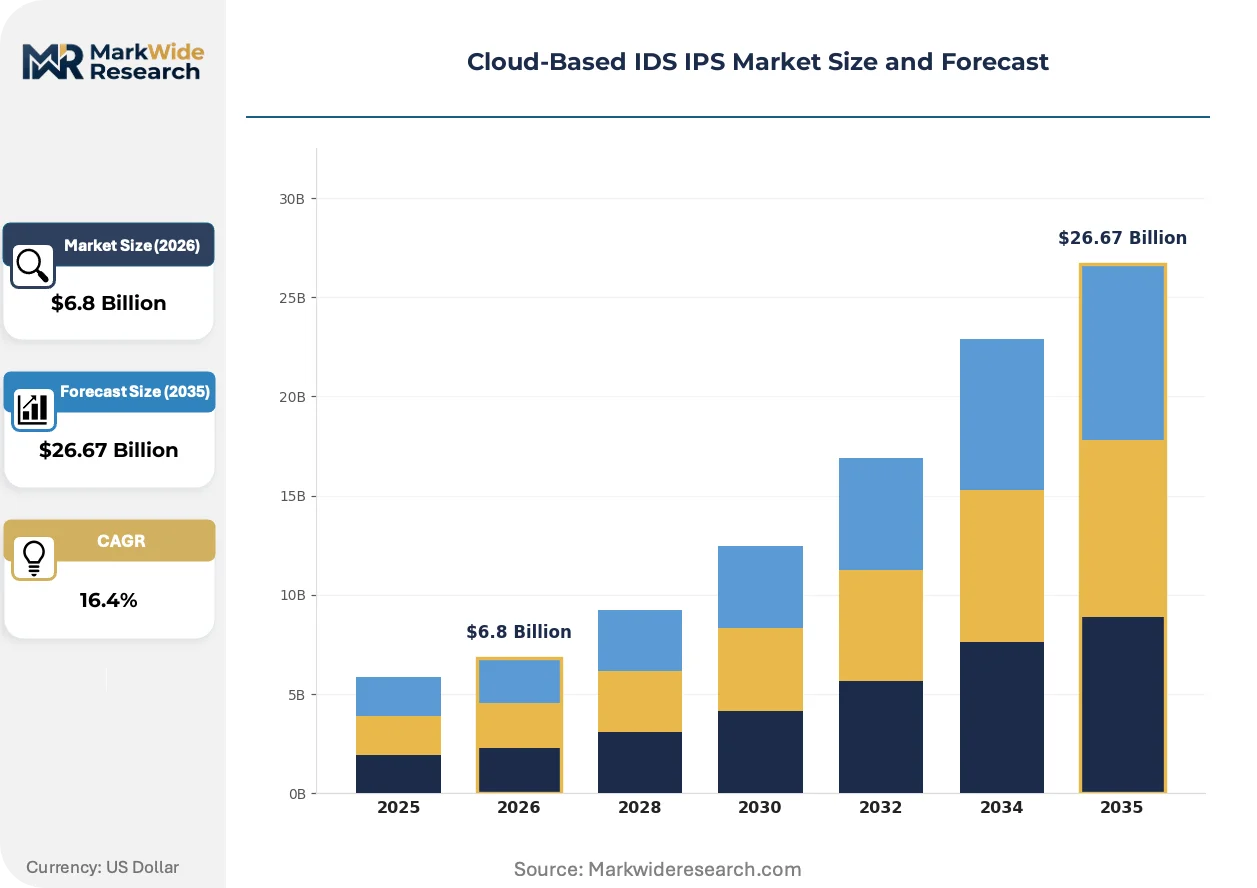
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $26.67 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud Solution: Signature-Based, Anomaly-Based, Behavior-Based, Policy-Based End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Organizations Compliance Standard: GDPR, HIPAA, PCI DSS, SOC 2 |
| Companies Covered | Cisco Systems, Palo Alto Networks, Fortinet, Trend Micro, Check Point Software Technologies, CrowdStrike, IBM Security, Sophos, Juniper Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud-Based IDS IPS Market Strategic Shifts
Detection architectures are abandoning perimeter-centric designs in favor of workload-embedded sensors that operate inside virtualized boundaries. This reconfiguration demands new integration patterns between cloud providers and security vendors.
Agentless cloud-native application protection platforms are displacing traditional virtual appliance deployments that required traffic hairpinning through inspection zones. Large enterprises with containerized microservices are adopting these platforms within 18-month refresh cycles. The shift is compressing margins for hardware-dependent detection vendors while elevating software-only providers with API-level cloud integrations.
The EU AI Act's risk classification framework for automated decision systems is mandating algorithmic transparency in security tools deployed across European critical infrastructure. Vendors must now document training data provenance and detection model drift metrics. Financial services and energy operators in Germany and France are requiring these disclosures as standard procurement terms, forcing product roadmap adjustments.
Security procurement committees are consolidating vendor relationships from point-solution portfolios toward platform contracts with unified billing and shared telemetry lakes. Managed security service providers are capturing this consolidation by offering detection infrastructure as operational expenditure rather than capital deployment. United States federal contractors and Japanese manufacturing conglomerates represent the most advanced adopters of this procurement model compression.
Cloud-Based IDS IPS Market Segmentation
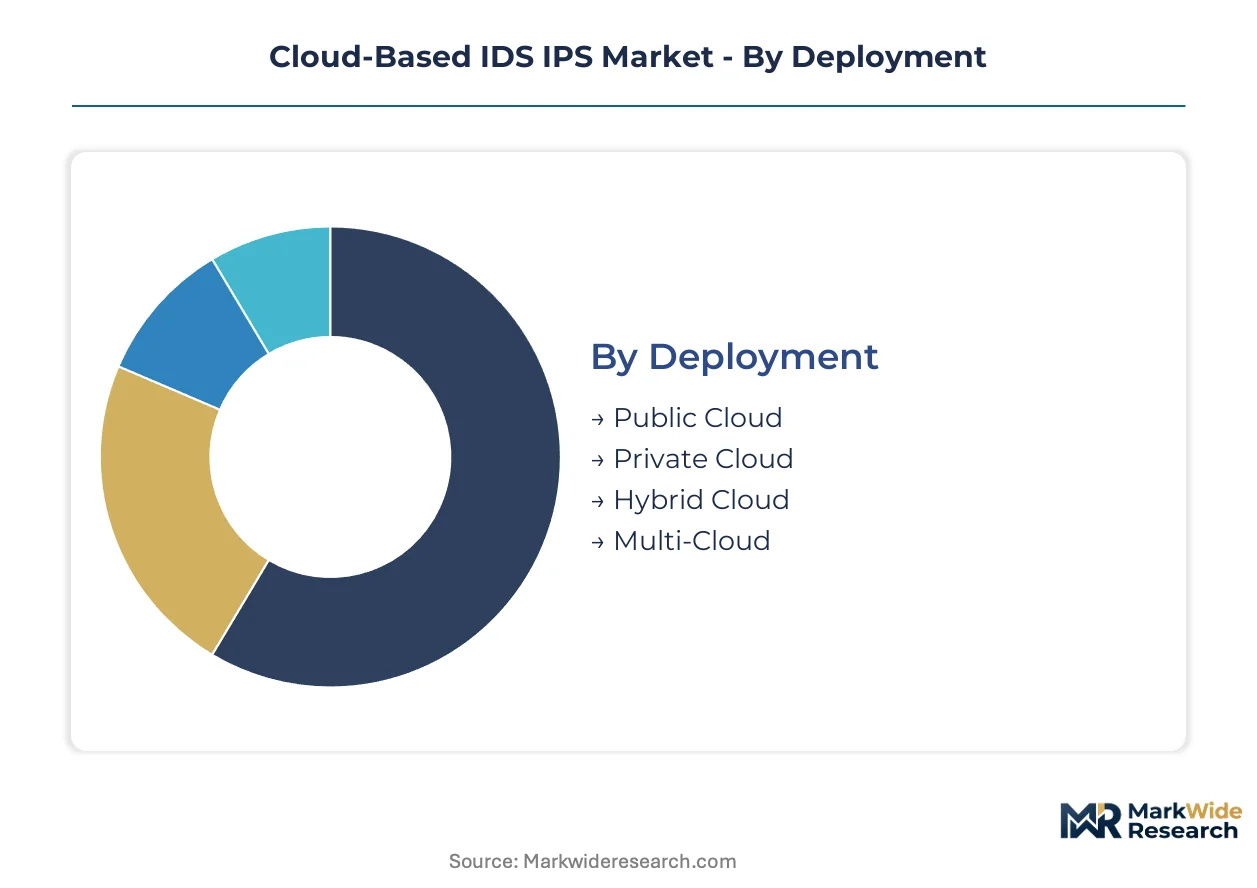
Cloud-based IDS IPS procurement channels diverge sharply across deployment architectures, with managed security service providers dominating public cloud subscriptions while direct vendor relationships persist in private infrastructure. Solution type determines margin structure, as behavioral analytics commands premium pricing against commoditized signature-based offerings. End-user scale and compliance mandates further stratify the addressable market into distinct buying centers with incompatible procurement workflows.
Deployment:
Channel economics vary dramatically by deployment model, with hybrid and multi-cloud configurations requiring systems integrator involvement while single-tenant private deployments flow through direct enterprise sales.
- Public Cloud:Native security service bundles from AWS, Azure, and Google Cloud displace third-party virtual appliances through consumption-based pricing. North American financial services firms represent the primary external vendor opportunity where shared responsibility gaps persist.
- Hybrid Cloud:Unified threat management platforms spanning on-premises data centers and burst capacity environments capture the largest procurement budgets. German automotive manufacturers and Japanese industrial conglomerates anchor demand for consistent policy enforcement across estate boundaries.
- Private Cloud:Dedicated virtual appliances and containerized sensors serve regulated workloads with data residency requirements. Banking regulators in Switzerland and healthcare authorities in Canada mandate this architecture for sensitive record repositories.
- Multi-Cloud:Abstraction layers normalizing telemetry across disparate provider environments attract cloud-native enterprises avoiding vendor lock-in. Technology sector adopters in the United States drive early traction for these orchestration platforms.
Hybrid Cloud dominates installed base. Multi-Cloud is where expansion concentrates.
Solution:
Cost tier stratification separates mature signature libraries from emerging AI-augmented detection, with pricing multiples expanding across the technology maturity curve.
- Signature-Based:Static rule libraries matching known threat indicators against packet contents and file hashes. Legacy installations across United States federal agencies and state-level government organizations perpetuate this lowest-cost tier despite coverage gaps.
- Anomaly-Based:Statistical deviation detection establishing baseline traffic patterns and flagging outliers for investigation. European critical infrastructure operators under NIS2 Directive pressure represent the fastest-climbing demand segment as zero-day tolerance collapses.
- Behavior-Based:Machine-learning models trained on entity behavior graphs to identify lateral movement and privilege escalation. United States healthcare systems migrating HIPAA-covered workloads to cloud environments pay substantial premiums for dwell-time reduction capabilities.
- Policy-Based:Explicit rule engines enforcing organizational security posture through automated remediation workflows. Financial services compliance teams in Germany and France require auditable detection triggers satisfying EU AI Act documentation standards.
Signature-Based retains the largest footprint. Behavior-Based is gaining share fastest.
End User:
Customer type determines contract structure, with large enterprises negotiating platform licenses while government organizations mandate FedRAMP or equivalent certification barriers.
- Small Enterprises:Managed detection and response services delivered through channel partners replace in-house security operations center investments. United Kingdom and Australian mid-market professional services firms represent concentrated uptake for outsourced monitoring.
- Medium Enterprises:Cloud-native application protection platforms with simplified deployment interfaces address staffing constraints. Regional healthcare networks across the United States select these solutions for HIPAA-aligned protection without dedicated security engineering.
- Large Enterprises:Custom-integrated detection fabrics spanning hybrid estates with dedicated threat intelligence feeds. Japanese manufacturing keiretsu and United States defense contractors anchor this highest-ACV segment with multi-year platform commitments.
- Government Organizations:Sovereign cloud deployments with classified processing requirements and domestic data residency mandates. Germany's Gaia-X initiative and comparable French national cloud programs structure procurement specifications.
Large Enterprises command the deepest vendor relationships. Government Organizations present the steepest expansion trajectory.
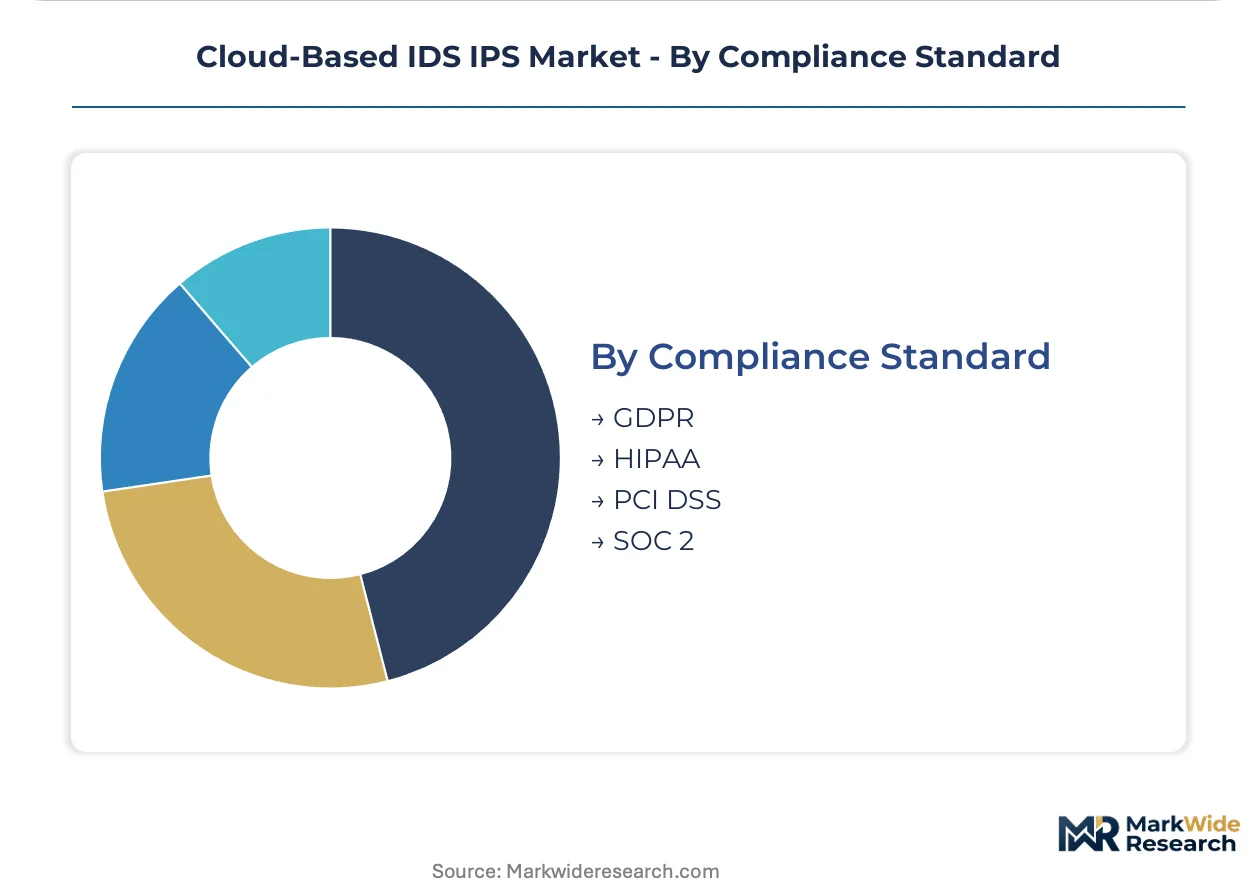
Compliance Standard:
Application context dictates mandatory control frameworks, with cross-border data flows requiring multi-jurisdictional certification stacking.
- GDPR:European data protection mandates requiring documented breach notification triggers and data processing impact assessments. French and Italian cloud migrations drive detection procurement with Article 32 technical safeguard specifications.
- HIPAA:United States healthcare security rules enforcing access controls and audit logging for electronic protected health information. Hospital systems in Texas and California represent concentrated demand as patient record digitization accelerates.
- PCI DSS:Payment card industry standards mandating continuous monitoring and intrusion detection for cardholder data environments. Tier-one banks and payment processors across Singapore and Hong Kong consolidate detection and compliance logging under unified platforms.
- SOC 2:Service organization control frameworks attesting to security availability and processing integrity for SaaS providers. United States software vendors pursuing enterprise sales require Type II reports with documented detection coverage.
PCI DSS anchors financial services procurement. GDPR is expanding fastest among cross-border enterprises.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Cloud security infrastructure investment concentrates where data sovereignty mandates intersect with financial services digitization. Germany, the United States, Japan, Singapore, and France collectively structure procurement specifications through divergent regulatory timelines and industrial cluster demands.
United States
Federal cloud migration and defense contractor requirements dominate procurement volumes. HIPAA enforcement by the Department of Health and Human Services accelerates healthcare system adoption of continuous monitoring architectures. Hospital networks across Texas and California are consolidating detection contracts under unified platform licenses.
Germany
Gaia-X sovereign cloud specifications and NIS2 Directive timelines compress deployment schedules for critical infrastructure operators. The EU AI Act mandates algorithmic transparency documentation for automated security tools. Automotive manufacturers in Bavaria and Baden-Württemberg anchor hybrid cloud demand for consistent policy enforcement.
Japan
Manufacturing keiretsu digitization and METI cybersecurity guidelines drive multi-year platform commitments. Financial services regulators in Tokyo mandate real-time incident reporting aligned with international standards. Industrial conglomerates in the Kansai and Chubu regions are standardizing detection fabrics across hybrid estates.
Singapore
Monetary Authority of Singapore cyber risk management guidelines compel tier-one banks toward unified detection and compliance logging. Payment processors and fintech clusters concentrate procurement in the central business district. Cross-border data flow requirements are stacking certification obligations for regional headquarters operations.
France
ANSSI critical infrastructure protection mandates and GDPR Article 32 enforcement shape technical safeguard specifications. Energy operators under NIS2 pressure represent accelerating demand for anomaly-based detection. Financial services compliance teams in Paris require auditable triggers satisfying EU AI Act documentation standards.
Cloud-Based IDS IPS Market Competitive Environment
Technology leadership and cost leadership are held by different player archetypes across the detection infrastructure market. Consolidation pressures favor platform providers with unified telemetry lakes over point-solution specialists. Three archetypes dominate: integrated firewall-IDS convergers, AI-augmented behavioral analytics providers, and agentless cloud-native protection platforms. M&A activity targets API-level cloud integration capabilities, while strategic partnerships focus on managed security service provider channel density.
Within the integrated security platform tier, Cisco Systems, Palo Alto Networks, and Fortinet exemplify divergent architectural bets. Cisco anchors hybrid cloud deployments with telemetry fabrics spanning estate boundaries. Palo Alto Networks occupies a position emphasizing machine-learning inference pipelines for large enterprise accounts. Fortinet represents cost-optimized convergence through channel-heavy distribution models.
| Leading Market Players |
|---|
| Cisco Systems |
| Palo Alto Networks |
| Fortinet |
| Trend Micro |
| Check Point Software Technologies |
| CrowdStrike |
| IBM Security |
| Sophos |
| Juniper Networks |
| Others |
Value Chain & Pricing Dynamics
Capacity reservation contracts with hyperscaler security bundles lock in multi-year supply access while flattening price visibility for enterprise buyers navigating NIS2 compliance timelines. German automotive manufacturers and Japanese industrial conglomerates anchor these arrangements, trading procurement flexibility for guaranteed detection infrastructure availability across hybrid estates.
Pricing Analysis
NIS2 Directive dictates the pricing tier structure by mandating continuous monitoring capabilities that stratify offerings across premium behavioral analytics, standard anomaly detection, and economy signature-based tiers. Certification grade under FedRAMP and EU sovereign cloud frameworks commands substantial premiums, while small enterprises in the United Kingdom and Australia exhibit acute price sensitivity toward outsourced managed detection services. Cost compression in the signature-based tier intensifies because AWS, Azure, and Google Cloud native bundles commoditize basic packet inspection, forcing independent vendors toward AI-augmented differentiation to sustain margins.
Supply Chain Analysis
Strategic stockpiling of decryption proxy infrastructure and machine-learning training pipelines dominates inventory strategy as TLS 1.3 adoption accelerates. Hardware component sourcing draws from Taiwan for specialized packet inspection ASICs, the United States for GPU acceleration modules, and Israel for behavioral analytics firmware. Single-source vulnerability concentrates in hyperscaler API dependencies that gate cloud-native sensor deployment. Distribution runs through managed security service providers who consolidate vendor relationships into operational expenditure contracts for United States federal contractors and Japanese manufacturing keiretsu.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Regulatory entrenchment constructs formidable defensive moats in this market, as NIS2 Directive timelines and FedRAMP certification barriers embed incumbent detection fabrics into critical infrastructure procurement specifications for years ahead.
For Market Incumbents: Fortify platform consolidation by acquiring API-level cloud integration specialists before agentless protection platforms displace virtual appliance revenue streams. Deepen backward integration into sovereign cloud infrastructure partnerships, particularly Germany's Gaia-X initiative, to preempt compliance-driven vendor switches. Channel control through managed security service provider density anchors renewal rates against emerging software-only competitors. For New Entrants and Emerging Players: Lead with healthcare system migrations in Texas and California, where HIPAA-covered workloads lack specialized detection architectures and procurement committees prioritize dwell-time reduction over brand recognition. Target regional healthcare networks with simplified cloud-native application protection platforms that bypass dedicated security engineering requirements. A direct-to-CISO SaaS deployment model bypasses entrenched systems integrator relationships that gate enterprise accounts. For Investors and Strategic Acquirers: Capital is best deployed toward agentless cloud-native protection platforms with demonstrated API integration velocity across AWS, Azure, and Google Cloud environments. Long-term viability hinges on algorithmic transparency documentation satisfying EU AI Act procurement terms now standard in French and German financial services. Watch NIS2 incident notification compliance rates as the inflection signal—operators missing 24-hour windows will accelerate detection fabric replacement cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint detection with network-level prevention for consolidated telemetry lakes demanded by Japanese manufacturing keiretsu. |
| Acquisition of Specialist Firm | Captures API-level cloud integration capabilities that compress deployment cycles for multi-cloud abstraction layers. |
| Strategic Partnership | Secures Gaia-X sovereign cloud certification pathways for German critical infrastructure operators under NIS2 pressure. |
| Product Launch | Introduces agentless sensors displacing virtual appliances within 18-month containerized microservices refresh cycles. |
| Geographic Expansion | Establishes healthcare-focused detection architectures for HIPAA-covered hospital systems in Texas and California. |
Study Parameters
Two parallel data streams informed the analysis: structured conversations with CISOs at United States defense contractors, cloud security architects at German automotive manufacturers, managed security service provider executives, and healthcare IT directors in Texas and California; alongside secondary validation through SEC 10-K filings, hyperscaler capex disclosures, NIST cybersecurity framework documentation, and EU NIS2 Directive implementation timelines. Bottom-up deployment estimates across public, hybrid, private, and multi-cloud configurations triangulated against top-down market sizing from vendor revenue disclosures and procurement database tracking.
Across the projection horizon, the analytical framework modeled segmentation dimensions spanning deployment architecture, solution type from signature-based through behavior-based analytics, end-user scale from small enterprises through government organizations, and compliance standard including GDPR, HIPAA, PCI DSS, and SOC 2. CAGRs derived from historical vendor growth rates, compliance mandate implementation schedules, and cloud migration velocity indicators specific to financial services and healthcare verticals.
The analysis sits within stated boundaries; outcomes outside sustained hyperscaler security bundle pricing aggression or accelerated TLS 1.3 adoption curves would require recalibration. Forecasts reflect assumptions regarding NIS2 enforcement consistency, sovereign cloud procurement pathway maturation, and machine-learning inference cost trajectories. Revision becomes warranted when agentless platform displacement velocity crosses thresholds that collapse virtual appliance refresh cycles below 24 months.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Bahrain Cybersecurity Market
Cybersecurity
Global Virtualization Security Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Europe Data Exfiltration Market
Cybersecurity
Global SSH Terminal Market
Cybersecurity
Cloud Firewalls Market
Cybersecurity
Asia Pacific IoT Security Market
Cybersecurity
Global Mobile Anti Malware Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Penetration Testing Market
Cybersecurity
Global Breach and Attack Simulation Market
Cybersecurity
Application-Level Encryption Market
Cybersecurity
Global Serverless Security Market
Cybersecurity
North America Software Defined Perimeter Market
Cybersecurity
IT and Telecom Cyber Security Market
Cybersecurity
Cloud Security in Banking Market