
 Global Container and Kubernetes Security Market | 2026-2036
Global Container and Kubernetes Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Container and Kubernetes Security Market Foresight
Subscription-based consumption models and usage-metered licensing are fragmenting procurement patterns across the container security landscape. Aqua Security leverages deep runtime protection capabilities to anchor enterprise accounts with complex microservice architectures. Palo Alto Networks sustains competitive pressure through integrated cloud-native application protection platforms that span network and workload layers. Sysdig specializes in open-source-derived monitoring pipelines that extend visibility into container forensics without proprietary agent lock-in.
Container and Kubernetes security encompasses policy enforcement, image integrity verification, runtime threat detection, and secrets management for orchestrated workloads operating across distributed infrastructure. The discipline centers on maintaining confidentiality, availability, and auditability of ephemeral compute units that spin up and terminate in seconds across heterogeneous clusters. Runtime security and image scanning dominate current spending as organizations prioritize vulnerability interception before deployment and anomalous behavior detection during execution. Hybrid cloud and multi-cloud deployment models are expanding fastest as regulated industries seek to avoid single-provider concentration risk while maintaining consistent security posture.
FDA cybersecurity guidance for cloud-based medical devices, EU GDPR data residency requirements, and NIST SP 800-190 container security standards collectively elevate baseline compliance costs for vendors and buyers alike. BSI Germany and ANSSI France impose additional national certification layers that filter market access for non-European suppliers. Enterprises must monitor evolving SBOM mandates and zero-trust architecture deadlines that will reshape procurement criteria and vendor qualification timelines.
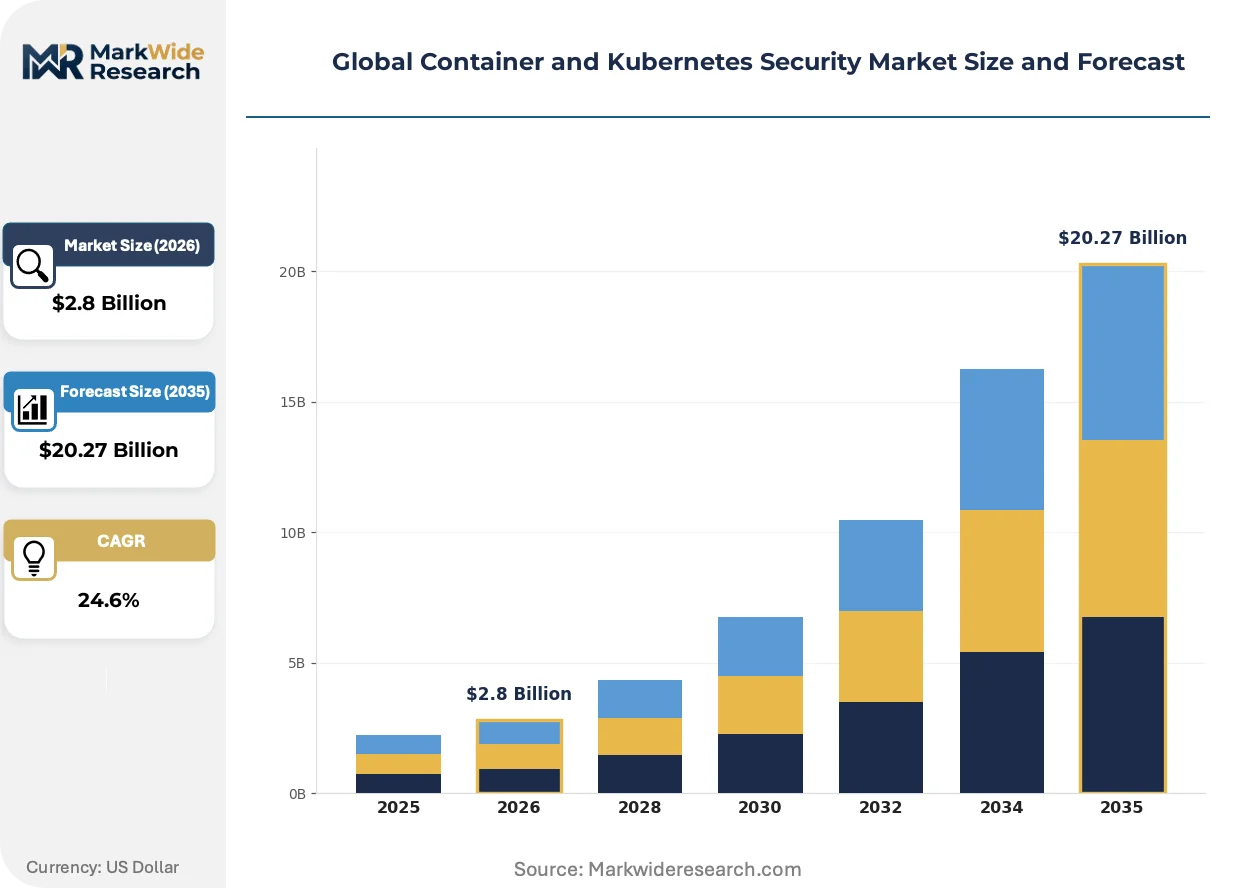
Market Dynamics
Runtime security platforms are fragmenting procurement patterns as financial services firms demand usage-metered licensing tied to actual container spin-up events rather than static seat counts. This shift from perpetual licenses to consumption-based models concentrates vendor selection power with procurement teams managing multi-cloud estates.
Growth Catalysts
- EU AI Act compliance mandates:European enterprises must harden Kubernetes governance frameworks for automated decision-making workloads, forcing security stack upgrades across Frankfurt, Paris, and Amsterdam data centers.
- Ephemeral compute visibility gaps:Containers that terminate in seconds leave forensic blind spots, driving demand for continuous runtime monitoring in healthcare and fintech verticals.
- BSI Germany certification requirements:Industrial technology companies operating dense multi-cloud container estates must meet strict federal cybersecurity standards, filtering vendor access and elevating procurement budgets.
Market Restraints
- Specialized talent scarcity:Shortage of engineers fluent in both Kubernetes orchestration and security operations limits enterprise deployment velocity and inflates implementation costs.
- Agent proliferation complexity:Each security vendor deploys proprietary monitoring agents, creating interoperability friction and observability data silos across hybrid infrastructure.
- Legacy identity system integration:Existing Active Directory and LDAP investments resist seamless mapping to container-native RBAC models, extending deployment timelines.
Strategic Opportunities
- Open-source monitoring convergence:eBPF-based kernel instrumentation combined with Falco rule engines enables vendor-neutral threat detection without proprietary agent lock-in.
- Medical device cloud migration:FDA cybersecurity guidance for cloud-based connected devices creates compliant-ready demand from diagnostic imaging and patient monitoring manufacturers.
- SBOM mandate preparation:Software bill of materials requirements across US federal procurement and EU critical infrastructure sectors position image-scanning vendors for embedded contract wins.
Industry Challenges
- Zero-trust architecture deadlines:Federal and defense contractor mandates for microsegmentation and identity verification compress vendor qualification timelines and certification backlogs.
- Secrets rotation at scale:Automated credential management across thousands of ephemeral pods requires architectural redesign of existing vault and certificate authority infrastructure.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Container and Kubernetes Security Market |
| Market Size in 2026 | $2.8 Billion |
| Market Size in 2035 | $20.27 Billion |
| CAGR (2026 – 2036) | 24.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Security Type: Runtime Security, Image Scanning, Network Security, Configuration Management, Vulnerability Assessment Deployment Model: On-Premise, Public Cloud, Hybrid Cloud, Multi-Cloud Application: Threat Detection, Compliance Monitoring, Access Control, Incident Response End User: Financial Services, Telecommunications Providers, Technology Companies, Government Agencies |
| Companies Covered | Aqua Security, Palo Alto Networks, Sysdig, Trend Micro, Red Hat, Qualys, Anchore, NeuVector, Capsule8, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Container and Kubernetes Security Market Shifts & Advancements
Security instrumentation is migrating from perimeter appliances to kernel-level observability, collapsing the distinction between monitoring and enforcement. This architectural shift rewards vendors with deep runtime telemetry capabilities over those relying on network-side inspection alone.
eBPF-powered kernel tracing is rendering obsolete traditional agent-based security models that require sidecar containers or host-level daemonsets. Financial services firms in London and Singapore are deploying these capabilities for sub-millisecond threat detection without container image modification. The technology is compressing vendor consolidation timelines as buyers prioritize unified platforms over point-product stitching.
GDPR data residency requirements are forcing European enterprises to deploy regional Kubernetes clusters with localized encryption key management and audit logging. This regulatory pressure is fragmenting cloud provider selection as AWS, Azure, and GCP compete on sovereign cloud certifications. German automotive and pharmaceutical manufacturers are driving demand for EU-only data processing architectures that complicate global workload portability.
Consumption-based licensing is displacing annual enterprise agreements as container security buyers demand usage-metered pricing aligned with actual workload density. Channel partners in North America and Western Europe are restructuring compensation models around monthly active container counts rather than upfront license bookings. Healthcare providers with seasonal patient volume spikes represent the most visible adopters of this flexible procurement approach.
Global Container and Kubernetes Security Market Segmentation
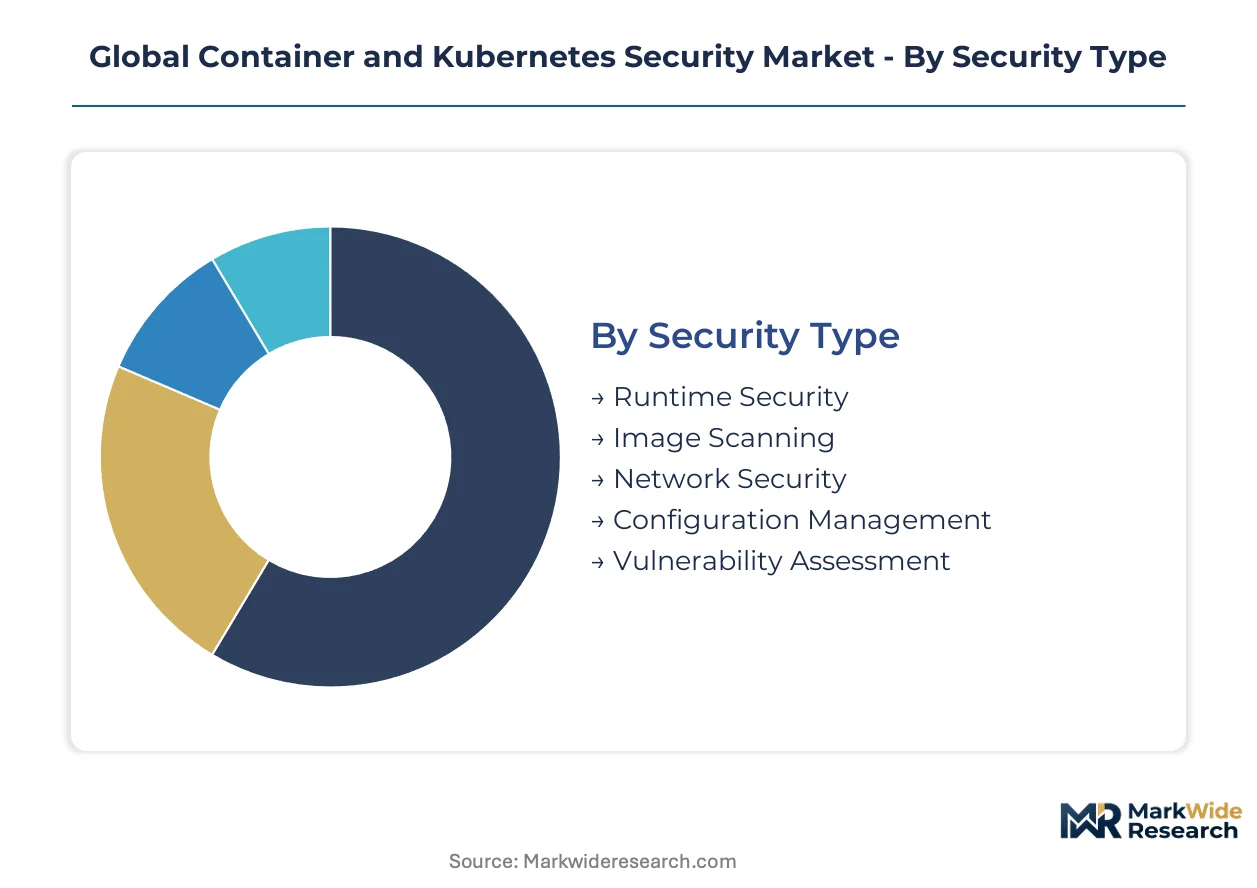
Container and Kubernetes security procurement fragments across security type, deployment model, application, and end user. Each dimension captures distinct budget authority, technical requirements, and compliance obligations. Understanding these boundaries clarifies where vendors compete for wallet share versus where specialization dominates.
Security Type:
Cost tier determines procurement sequencing, with enterprises prioritizing capabilities that intercept threats before production deployment versus those operating continuously in live environments.
- Runtime Security:Continuous behavioral monitoring of executing containers detects anomalous process execution, file system modifications, and network connections in real time. Financial services firms in London and Singapore deploy these capabilities for sub-millisecond threat detection without container image modification. Runtime platforms command premium pricing due to kernel-level instrumentation complexity and ephemeral workload visibility requirements.
- Image Scanning:Static analysis of container images before deployment identifies known vulnerabilities, malware signatures, and misconfigurations in base layers and application dependencies. Healthcare providers with seasonal patient volume spikes prioritize image scanning to satisfy FDA cybersecurity guidance for cloud-based medical devices before runtime deployment.
- Network Security:Microsegmentation and east-west traffic inspection between pods and services enforces zero-trust architecture mandates.
- Configuration Management:Policy-as-code enforcement prevents drift from secure Kubernetes manifests and RBAC definitions.
- Vulnerability Assessment:Continuous posture evaluation across cluster nodes and control plane components identifies patch gaps.
Runtime security commands the established base. The steepest expansion runs through image scanning.
Deployment Model:
Application context shapes infrastructure choices, with regulated industries avoiding single-provider concentration risk while maintaining consistent security posture.
- Multi-Cloud:Security orchestration across AWS, Azure, and GCP clusters with unified policy enforcement and centralized telemetry aggregation. German automotive manufacturers drive demand for multi-cloud runtime protection to satisfy BSI certification requirements while avoiding vendor lock-in.
- Hybrid Cloud:Consistent security controls spanning on-premise Kubernetes distributions and managed cloud services. French pharmaceutical companies deploy hybrid models to maintain GDPR data residency for patient records while bursting compute to public cloud.
- Public Cloud:Native integration with EKS, AKS, or GKE managed control planes and serverless container offerings.
- On-Premise:Self-managed OpenShift or Rancher clusters in air-gapped environments with offline vulnerability databases.
Multi-cloud deployments absorb the largest procurement budgets. Hybrid cloud is gaining share fastest among established enterprises.
Application:
Customer type dictates functional priority, with security operations teams selecting tools based on mean-time-to-detect versus compliance audit requirements.
- Threat Detection:Real-time identification of runtime exploits, cryptojacking, and lateral movement through behavioral analytics and machine learning classifiers. Telecommunications providers in Germany deploy threat detection for 5G network function virtualization workloads subject to BSI federal cybersecurity standards.
- Compliance Monitoring:Continuous evidence collection for GDPR, EU AI Act, and NIST SP 800-190 audit trails with automated control mapping. Technology companies in Amsterdam data centers harden Kubernetes governance frameworks for automated decision-making workloads under EU AI Act mandates.
- Access Control:Identity verification and least-privilege enforcement for human and service account interactions with cluster resources.
- Incident Response:Forensic capture and automated containment of compromised containers with evidence preservation for post-breach analysis.
Threat detection commands the established base. Compliance monitoring is climbing the fastest as regulatory deadlines compress.
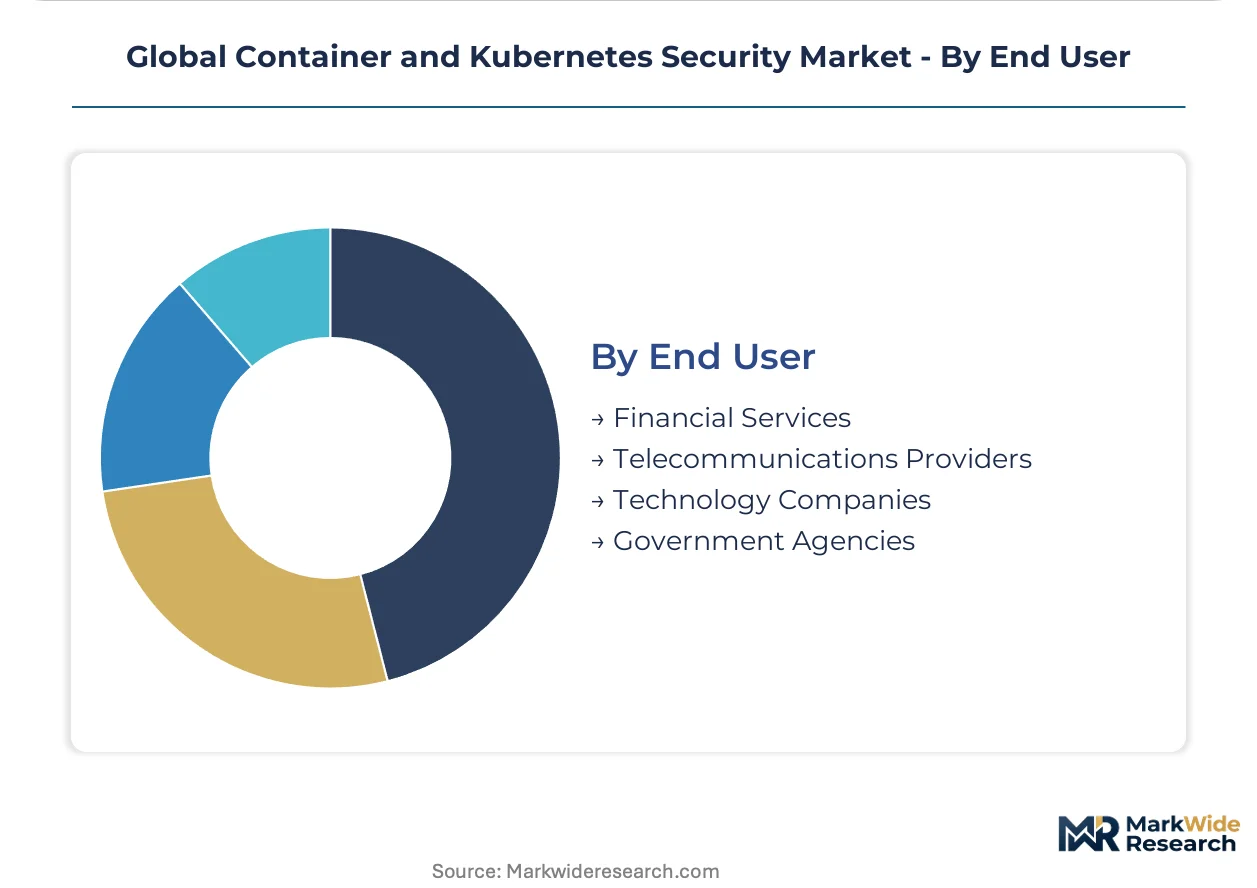
End User:
Volume concentration varies by sector maturity, with technology-forward industries absorbing advanced capabilities before regulated verticals complete procurement cycles.
- Financial Services:Banks, insurers, and payment processors with strict runtime security requirements for containerized trading platforms and fraud detection systems. Usage-metered licensing tied to actual container spin-up events is fragmenting procurement patterns as procurement teams manage multi-cloud estates.
- Technology Companies:SaaS providers and platform operators with dense microservice architectures requiring deep runtime protection and CI/CD pipeline integration. Industrial technology companies in Germany operate dense multi-cloud container estates subject to strict BSI cybersecurity requirements.
- Government Agencies:Federal and defense contractors with zero-trust architecture deadlines compressing vendor qualification timelines.
- Telecommunications Providers:Network operators virtualizing infrastructure with Kubernetes-based network functions and edge computing platforms.
Financial services commands the established base. Government agencies represent the steepest expansion trajectory as federal mandates activate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export-import dynamics in container security services flow predominantly from US and Israeli technology exporters toward European and Asian importers. Germany and France absorb the largest cross-border procurement volumes as domestic vendors lack comparable runtime protection depth.
United States
Financial services firms in New York and Chicago drive consumption of usage-metered runtime security platforms. FDA cybersecurity guidance for cloud-based medical devices elevates compliance spending for diagnostic imaging manufacturers in Boston and Minneapolis. Silicon Valley technology clusters anchor the densest microservice deployments, with SaaS providers demanding deep CI/CD pipeline integration.
Germany
Industrial technology companies in Munich and Stuttgart operate dense multi-cloud container estates subject to strict BSI federal cybersecurity standards. GDPR data residency requirements force Frankfurt data centers to deploy regional Kubernetes clusters with localized encryption key management. Automotive manufacturers in Wolfsburg and Ingolstadt prioritize multi-cloud runtime protection to satisfy certification requirements while avoiding vendor lock-in.
United Kingdom
London financial institutions deploy sub-millisecond threat detection for containerized trading platforms without container image modification. The UK Information Commissioner's Office enforces GDPR-aligned audit trails for automated decision-making workloads in Canary Wharf data centers. Telecommunications providers in Manchester virtualize 5G network functions with Kubernetes-based edge computing platforms subject to national security reviews.
France
ANSSI imposes additional national certification layers that filter market access for non-European security suppliers. Paris pharmaceutical companies deploy hybrid cloud models to maintain GDPR data residency for patient records while bursting compute to public cloud. Lyon-based industrial software vendors integrate policy-as-code enforcement to prevent drift from secure Kubernetes manifests.
Singapore
Monetary Authority of Singapore operational resilience guidelines compel banks to implement continuous runtime monitoring for ephemeral container workloads. The city-state's sovereign cloud certifications attract ASEAN regional headquarters deploying multi-cloud security orchestration. Fintech startups in one-north and Marina Bay demand consumption-based licensing aligned with seasonal transaction volume spikes.
Global Container and Kubernetes Security Market Competitive Landscape
Platform integrators command the system tier; component specialists sit upstream with narrower runtime telemetry or image scanning depth. The vendor base compresses toward unified platforms as procurement teams reject point-product stitching across hybrid estates. Three archetypes dominate: cloud-native application protection platforms, open-source-derived monitoring pipelines, and specialized runtime protection engines. Consolidation pressure intensifies through strategic partnerships bridging network security and workload layers, plus technology licensing deals embedding kernel-level instrumentation into broader portfolios.
Among Israel-anchored specialists, Aqua Security exemplifies the runtime protection archetype with kernel-level instrumentation capabilities. Palo Alto Networks, a US-incorporated platform integrator, occupies the unified cloud-native application protection tier spanning network and workload layers. Sysdig represents the open-source-derived monitoring pipeline segment, extending visibility through Falco rule engines without proprietary agent dependencies. These three anchors illustrate how geographic clustering around Tel Aviv, Silicon Valley, and San Francisco shapes competitive positioning.
| Leading Market Players |
|---|
| Aqua Security |
| Palo Alto Networks |
| Sysdig |
| Trend Micro |
| Red Hat |
| Qualys |
| Anchore |
| NeuVector |
| Capsule8 |
| Others |
Supply & Pricing Matrix
Overcapacity in Israeli kernel instrumentation talent pools compresses vendor margins while concentrating pricing power with platform integrators who bundle runtime protection into broader cloud-native portfolios. This utilization dynamic forces specialized engine providers toward consumption-based models that align revenue with actual container spin-up events rather than static licensing.
Pricing Analysis
Industrial OEM buyers anchor a three-tier pricing structure across premium, standard, and economy levels. Premium tiers bundle kernel-level instrumentation with dedicated threat response teams; standard tiers offer SaaS-delivered monitoring with shared support; economy tiers provide basic image scanning without runtime capabilities. Price differentiation rests on certification depth—BSI Germany and ANSSI France compliance tiers command substantial premiums—and deployment scale, with multi-cloud estates securing volume discounts. Pricing pressure stems from open-source Falco and eBPF alternatives eroding proprietary agent value. Healthcare providers with seasonal patient volume spikes exhibit highest price sensitivity; financial services firms in London and Singapore show lowest sensitivity due to regulatory penalty exposure.
Supply Chain Analysis
Upstream feedstock for container security platforms draws from three concentrated sources: Israeli runtime protection engineering clusters, US cloud-native platform development hubs, and European compliance certification bodies. Core components include eBPF kernel instrumentation libraries, threat intelligence feeds from financial services ISACs, and sovereign cloud infrastructure certified for GDPR data residency. Single-source vulnerability concentrates in Israeli specialist acquisition pipelines, where talent scarcity limits vendor scaling velocity. Distribution runs through hyperscaler marketplaces—AWS Marketplace, Azure Marketplace, and Google Cloud Marketplace—plus channel partners restructuring compensation around monthly active container counts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market sits at an inflection where eBPF-powered kernel instrumentation is collapsing the distinction between monitoring and enforcement, compressing timelines for vendor consolidation as buyers reject point-product stitching.
For Market Incumbents: Build switching-cost moats through deep CI/CD pipeline integration that embeds security gates into developer workflows before container deployment. Incumbents should acquire open-source monitoring pipeline specialists to neutralize the threat of vendor-neutral Falco-based alternatives; this represents the priority lever for platform integrators facing eBPF commoditization pressure. Certification investment in BSI Germany and ANSSI France compliance tiers creates channel control that filters non-European competitors from dense industrial technology accounts. For New Entrants and Emerging Players: Pursue white-space targets in medical device cloud migration, where FDA cybersecurity guidance for connected diagnostic imaging creates compliant-ready demand without entrenched incumbent relationships. The most penetrable segment comprises diagnostic imaging and patient monitoring manufacturers in Boston and Minneapolis seeking pre-runtime image scanning with embedded SBOM generation. A go-to-market angle anchored to FDA submission support and 510(k) cybersecurity documentation bundles differentiates against generic runtime platforms. For Investors and Strategic Acquirers: Long-term, this sits as a consolidation play because procurement teams managing multi-cloud estates are compressing vendor counts toward unified cloud-native application protection platforms over point-product stitching. Acquisition targets should display kernel-level telemetry depth combined with open-source community traction that deflects proprietary agent lock-in criticism. The signal to watch is hyperscaler marketplace revenue concentration—platforms deriving substantial bookings through AWS, Azure, and GCP channels indicate distribution scalability that commands premium multiples.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies network and workload layers for procurement teams rejecting point-product stitching across hybrid estates. |
| Acquisition of Specialist Firm | Captures kernel-level instrumentation depth from Israeli runtime protection clusters facing talent scarcity constraints. |
| Strategic Partnership | Bridges eBPF-based monitoring pipelines with Falco rule engines to neutralize open-source commoditization threats. |
| Geographic Expansion | Establishes Frankfurt and Paris data center presence to satisfy GDPR data residency and EU AI Act compliance mandates. |
| Product Launch | Introduces usage-metered licensing aligned with container spin-up events for healthcare providers with seasonal volume spikes. |
Research Methodology
A standing panel of CISOs at financial services firms, platform engineers managing multi-cloud Kubernetes estates, procurement officers at German industrial technology companies, and compliance leads at pharmaceutical manufacturers provided ongoing calibration. This primary input combined with secondary validation from SEC filings of publicly traded security vendors, hyperscaler capex disclosures revealing cloud infrastructure investment patterns, BSI Germany certification registries, and EU AI Act implementation guidance documents. Bottom-up container deployment estimates triangulated against top-down security software spending forecasts.
Scenario bracketing anchored projections across the analysis window through three regulatory adoption pathways: accelerated EU AI Act enforcement, delayed federal zero-trust architecture deadlines, and fragmented SBOM mandate implementation across US federal procurement. Segmentation dimensions modeled include security type, deployment model, application context, and end-user vertical, with CAGRs derived from elasticity analysis linking container density growth to security tooling attach rates. Industry-specific inputs encompassed BSI certification backlog timelines and FDA cybersecurity guidance revision cycles.
The forecast holds incumbent behavior within observed patterns; aggressive moves by open-source-derived monitoring pipeline specialists or hyperscaler native security suites would shift outcomes. Material shifts in eBPF kernel instrumentation standardization timelines or sovereign cloud certification reciprocity agreements between EU member states would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
M2M Network Security Market
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Network Traffic Analysis Solutions Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Home Wi-Fi Security Solutions Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Network Security Market
Cybersecurity
DNS Security Market
Cybersecurity
Austria Cybersecurity Market
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
Vietnam Cybersecurity Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Micro Segmentation Technology Market