
 Japan Ransomware Protection Market | 2026-2036
Japan Ransomware Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Japan Ransomware Protection Market Insights
Hardware-based encryption modules are decoupling ransomware protection from pure software economics, lowering total cost of ownership for mid-sized deployments. Trend Micro Japan leverages its domestic threat-intelligence feeds to anchor detection accuracy against Japan-specific attack patterns. NEC Corporation competes through integrated offerings that combine endpoint agents with network segmentation. Fujitsu sustains enterprise relationships by embedding protection within broader IT outsourcing contracts.
Japan Ransomware Protection encompasses technologies and services that prevent, detect, and recover from malicious encryption of digital assets, typically incorporating real-time behavioral analysis, immutable backup architectures, and automated incident-response orchestration with sub-minute containment targets. The primary purpose is preserving operational continuity for organizations facing financially motivated extortion campaigns. Endpoint Security dominates current spending as organizations retrofit legacy workstations with next-generation detection agents. Cloud-Based deployment is expanding fastest among mid-market firms seeking to avoid capital expenditure on security infrastructure. Managed Security services capture disproportionate margin pools by bundling 24/7 monitoring with guaranteed response-time commitments.
METI's cybersecurity framework and the Act on Protection of Personal Information jointly shape procurement standards, with the former mandating supply-chain risk assessments and the latter imposing penalties for delayed breach disclosure. PMDA guidelines for medical-device software security extend these requirements into healthcare delivery organizations. JIS standards for information security management systems further constrain vendor qualification, favoring providers with certified implementation methodologies. Stakeholders must weigh whether to consolidate protection under domestic integrators or diversify across specialized foreign platforms as attack sophistication escalates.
Market Dynamics
Japan's amended Act on Protection of Personal Information has compressed breach-notification timelines to 72 hours, forcing organizations to rebuild incident-response infrastructure rather than patch legacy workflows. This regulatory pressure is reallocating security budgets toward automated containment and immutable backup architectures.
Growth Catalysts
- Financial services digitization:Banks and insurers are deploying behavioral analytics platforms to meet METI cybersecurity framework mandates for real-time threat detection.
- Critical infrastructure clustering:The Greater Tokyo Area's concentration of utilities and transportation hubs creates concentrated demand for network segmentation solutions.
- PMDA medical device guidelines:Healthcare delivery organizations must secure connected diagnostic equipment, expanding endpoint protection procurement.
Market Restraints
- Specialized talent scarcity:Japan's domestic cybersecurity workforce lacks sufficient incident-response engineers to staff 24/7 security operations centers.
- Legacy system interdependence:Manufacturing and logistics firms operate on decades-old OT networks that resist modern agent-based protection.
- Hardware security module costs:Mid-sized enterprises face capital barriers to deploying FIPS-certified encryption appliances at scale.
Strategic Opportunities
- Osaka-Kobe industrial corridor:Western Japan's pharmaceutical and chemical clusters remain underpenetrated by managed detection and response services.
- Cloud-native mid-market:Sub-500 employee firms are bypassing on-premise infrastructure entirely, creating greenfield SaaS protection contracts.
- JIS Q 27001 certification convergence:Integrators bundling ransomware protection with compliance auditing capture higher-margin recurring revenue.
Industry Challenges
- Multi-vendor orchestration complexity:Enterprises stitching together endpoint, network, and backup tools struggle to achieve sub-minute containment targets.
- Supply chain attestation gaps:METI-mandated vendor risk assessments lack standardized methodologies, delaying procurement cycles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Japan Ransomware Protection Market |
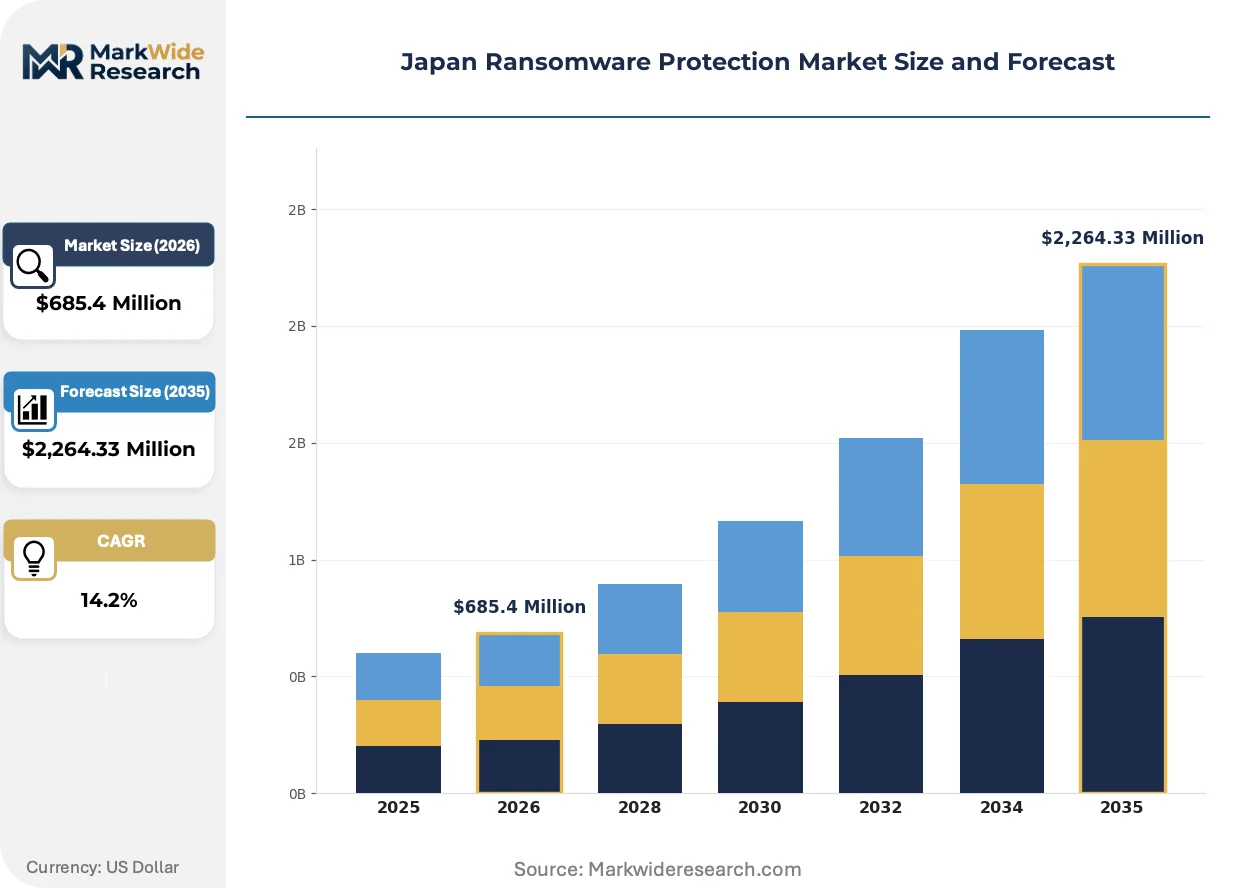
| Market Size in 2026 | $685.4 Million |
| Market Size in 2035 | $2,264.33 Million |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Endpoint Security, Network Security, Backup Solutions, Threat Intelligence Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Enterprise, Government, Healthcare, Education Service Type: Consulting, Managed Security, Incident Response, Training |
| Companies Covered | Fujitsu, Cybertrust Japan, Trend Micro Japan, Cisco Systems, IBM Japan, NEC Corporation, Hitachi Systems, Fortinet, NTT Security, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Japan Ransomware Protection Market Trends and Innovations
Hardware-based security modules are decoupling protection from software-only economics, while regulatory pressure accelerates automation investments. These forces are compressing deployment timelines and reshaping vendor competitive positioning.
Immutable backup architectures are expanding into financial services and healthcare as primary recovery mechanisms against encryption-based extortion. Regional banks with limited IT staff are adopting air-gapped storage appliances faster than large enterprises. This technology shift is expanding into mid-market procurement, lowering recovery-time-objective commitments from hours to minutes.
METI's cybersecurity framework now mandates supply-chain risk assessments for critical infrastructure operators, extending compliance obligations to third-party software vendors. Industrial control system suppliers must document security development lifecycles to maintain procurement eligibility. Manufacturing firms in automotive and electronics are responding by consolidating vendor panels and demanding certified implementation methodologies.
Security service unbundling is fragmenting traditional outsourcing relationships as enterprises separate monitoring from response functions. Large manufacturers are bringing detection engineering in-house while contracting guaranteed-response SLAs to specialized providers. This pattern is most visible among automotive and semiconductor firms in Aichi and Hiroshima prefectures seeking direct control over threat intelligence.
Japan Ransomware Protection Market Segmentation
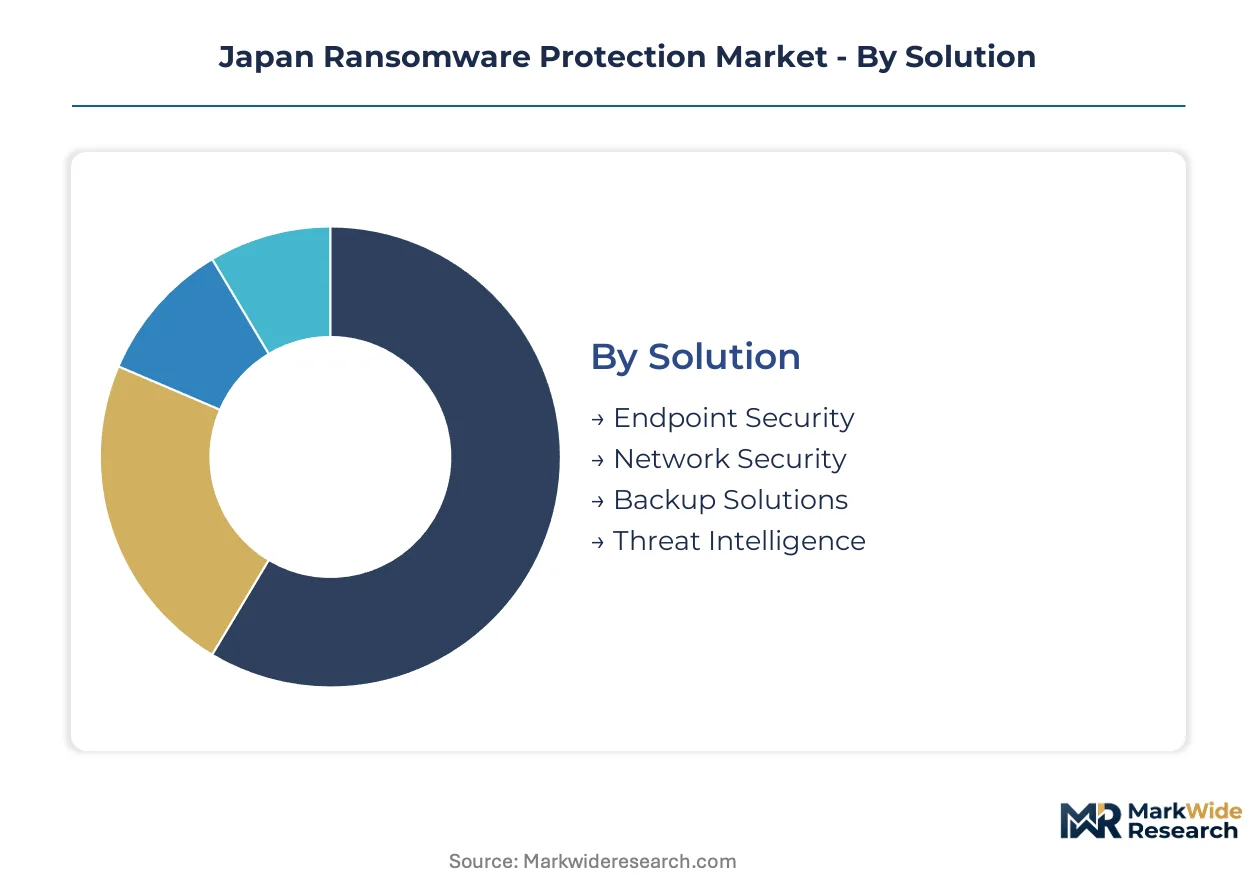
Segmentation reveals how procurement priorities diverge across Japan's ransomware protection landscape. Organizations balance legacy infrastructure constraints against regulatory pressure for automated response capabilities.
Solution:
Upgrade cycles vary sharply by protection layer, with endpoint refreshes outpacing network overhauls.
- Endpoint Security:Next-generation detection agents monitor workstation behavior in real time. Financial institutions in Tokyo's central business district dominate procurement as METI cybersecurity framework mandates tighten. Behavioral analytics integration drives replacement of signature-based antivirus.
- Network Security:Segmentation tools isolate lateral movement paths across flat corporate networks. Critical infrastructure operators in the Greater Tokyo Area prioritize these investments following supply-chain risk assessment requirements. Microsegmentation complexity limits deployment velocity.
- Backup Solutions:Immutable storage architectures with air-gapped recovery points gain traction among regional banks lacking dedicated security staff.
- Threat Intelligence:Domestic feed integration distinguishes Japan-specific attack patterns from global noise.
Endpoint Security sits at the top of the volume ranking, with Backup Solutions climbing the fastest.
Deployment:
Cost tier structures separate capital-intensive on-premise builds from operational expenditure models.
- On-Premises:Appliance-based protection requires dedicated data center footprint and internal engineering staff. Large manufacturers in Aichi Prefecture retain this model for operational technology network isolation. Hardware security module procurement faces budget friction at mid-market scale.
- Cloud-Based:SaaS delivery eliminates infrastructure ownership for sub-500 employee firms. Osaka-Kobe pharmaceutical clusters adopt fastest to bypass capital constraints. Native API integration with existing productivity suites accelerates deployment.
- Hybrid:Split architectures protect crown-jewel assets on-premise while offloading commodity workloads. Healthcare delivery organizations favor this balance for PMDA medical device guideline compliance.
- Managed Services:Twenty-four-hour monitoring with guaranteed response-time commitments addresses domestic talent scarcity. Margin pools concentrate here through bundled compliance auditing.
Managed Services commands premium pricing tiers, while Cloud-Based deployment expands most quickly among cost-constrained buyers.
End User:
Application maturity separates regulated sectors with mandated frameworks from discretionary adopters.
- Enterprise:Multi-layer orchestration across endpoint, network, and backup tools strains integration capabilities. Automotive and semiconductor firms bring detection engineering in-house while contracting response functions. Sub-minute containment targets drive automation investment.
- Government:National security classifications restrict vendor qualification to domestic integrators with certified implementation methodologies. Procurement cycles extend due to supply-chain attestation complexity.
- Healthcare:Connected diagnostic equipment security extends PMDA guidelines into delivery organizations. Immutable backup architectures spread fastest among regional hospitals with limited IT staff.
- Education:Distributed campus networks and bring-your-own-device policies complicate agent deployment. Budget constraints favor cloud-native protection over capital-intensive infrastructure.
Enterprise accounts anchor absolute spending volume, with Healthcare posting the steepest expansion trajectory amid regulatory deadline pressure.
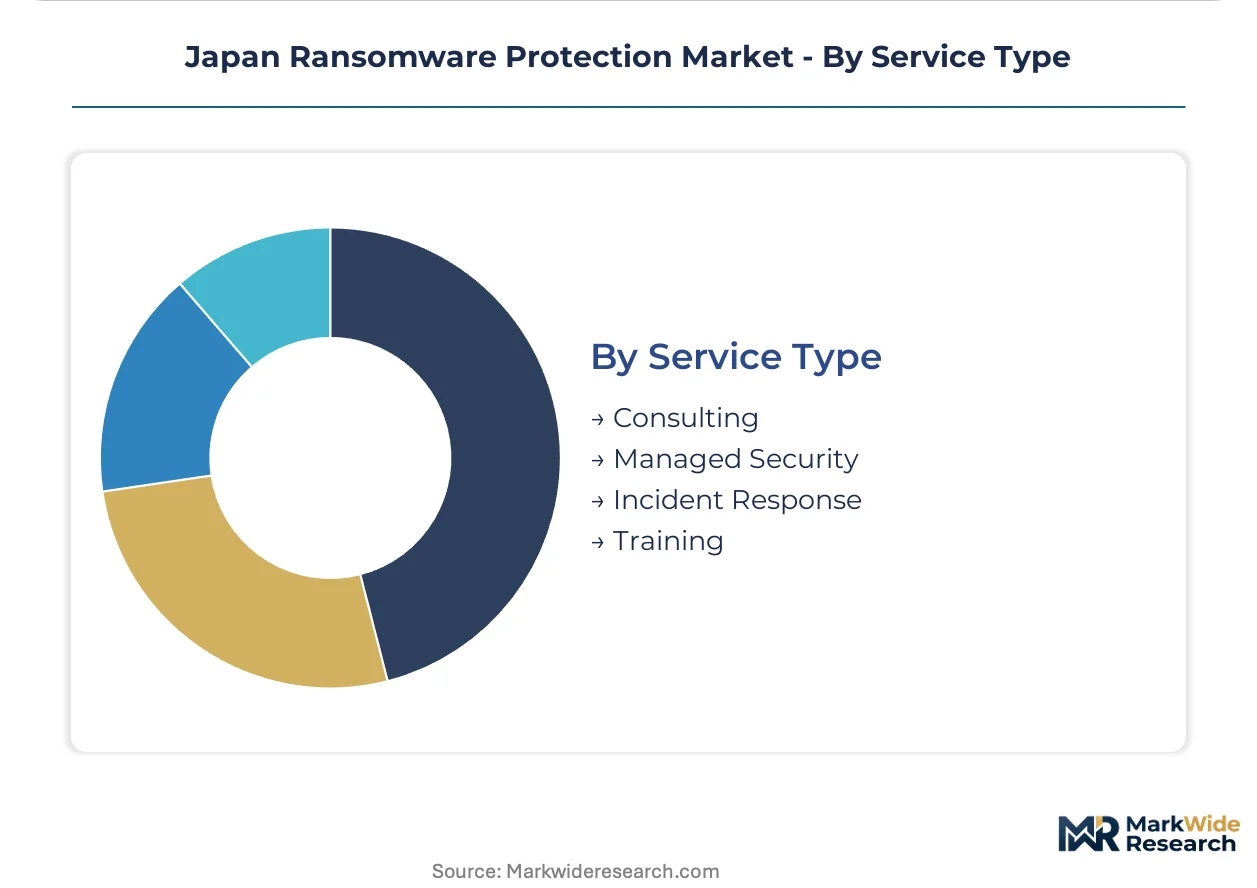
Service Type:
Customer sophistication determines whether organizations buy discrete capabilities or integrated transformation programs.
- Consulting:JIS Q 27001 certification readiness assessments bundle with ransomware protection architecture design. Manufacturing firms consolidate vendor panels to reduce coordination overhead.
- Managed Security:Continuous monitoring with automated escalation paths addresses the 72-hour breach notification mandate. Talent scarcity makes this the default choice for mid-market firms.
- Incident Response:Retainer-based emergency containment and recovery services command premium pricing. Regional banks adopt fastest following high-profile sector attacks.
- Training:Phishing simulation and security awareness programs reduce initial compromise vectors. Education sector procurement concentrates here due to limited technical control options.
Managed Security dominates recurring revenue pools, with Incident Response gaining share fastest as notification timelines compress.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Greater Tokyo Area anchors Japan's ransomware protection demand through its concentration of financial institutions, critical infrastructure operators, and corporate headquarters facing compressed breach-notification deadlines.
Kanto/Tokyo
Financial services digitization and critical infrastructure clustering drive procurement intensity across the capital region. METI's cybersecurity framework mandates real-time threat detection for banking and insurance sectors. Central Tokyo's dense financial district accelerates behavioral analytics platform deployment among institutions retrofitting legacy workstations.
Kansai/Osaka
Pharmaceutical and chemical manufacturing clusters generate specialized endpoint protection requirements for connected industrial systems. PMDA guidelines for medical-device software security extend compliance obligations into healthcare delivery organizations. The Osaka-Kobe industrial corridor remains underpenetrated by managed detection and response services, creating expansion opportunities for cloud-native providers.
Chubu/Nagoya
Automotive and semiconductor manufacturers dominate regional demand through operational technology network protection needs. Legacy system interdependence in manufacturing facilities complicates modern agent-based deployment. Aichi Prefecture's industrial concentration drives hybrid architecture adoption, with firms bringing detection engineering in-house while contracting response functions to specialized providers.
Kyushu
Renewable energy infrastructure and port logistics operations create distributed protection requirements across southwestern Japan. Regional utilities face supply-chain risk assessment mandates under METI frameworks. Fukuoka's emerging technology sector attracts mid-market firms bypassing on-premise infrastructure for SaaS-delivered protection.
Tohoku
Regional healthcare networks and agricultural processing facilities drive demand for immutable backup architectures with limited internal IT staffing. Post-disaster reconstruction investments have modernized telecommunications infrastructure, enabling cloud-based deployment models. Sendai's medical device manufacturers navigate PMDA security guidelines while securing connected diagnostic equipment.
Japan Ransomware Protection Market Competitive Landscape
Global majors compete with regional champions across integration depth and domestic threat-intelligence specialization. The market structure tilts toward consolidated procurement relationships where enterprise clients favor bundled compliance auditing over point solutions. Three archetypes dominate: domestic systems integrators with certified implementation methodologies, global cybersecurity platforms with localized threat feeds, and telecommunications carriers leveraging network infrastructure ownership. Competitive positioning hinges on vertical integration into managed security operations and JIS Q 27001 certification bundling.
Within the domestic integrator tier, Fujitsu and NEC Corporation occupy positions defined by embedded protection within broader IT outsourcing contracts. Trend Micro Japan exemplifies the global-platform-localized model through domestic threat-intelligence feed integration. These three anchors represent distinct competitive vectors: outsourcing consolidation, certified compliance bundling, and attack-pattern specialization.
| Leading Market Players |
|---|
| Fujitsu |
| Cybertrust Japan |
| Trend Micro Japan |
| Cisco Systems |
| IBM Japan |
| NEC Corporation |
| Hitachi Systems |
| Fortinet |
| NTT Security |
| Others |
Pricing and Supply Chain Analysis
Financial institutions in Tokyo's central business district concentrate procurement power, anchoring subscription-based SaaS pricing as the dominant commercial model across Japan's ransomware protection landscape.
Pricing Analysis
Input-cost pass-through from specialized cybersecurity talent and FIPS-certified hardware modules shapes pricing trajectories. Pricing stratifies across premium managed detection and response tiers, standard cloud-native endpoint packages, and economy self-service backup solutions. Cost compression in mid-market cloud deployments is intensifying because domestic talent scarcity forces premium labor arbitrage into vendor margins. Regional banks with limited IT staff exhibit highest price sensitivity, while central Tokyo financial institutions prioritize guaranteed response-time commitments over unit cost.
Supply Chain Analysis
Workforce availability constraints in Japan's domestic cybersecurity labor market and Taiwan's semiconductor manufacturing ecosystem anchor supply chain vulnerabilities. Hardware security module production draws from Taiwan, South Korea, and domestic Japanese foundries. Critical dependencies include cryptographic processors, specialized SOC engineering talent, and immutable storage media. Single-source vulnerability concentrates in FIPS-certified encryption appliance fabrication. Distribution runs through certified systems integrators with JIS Q 27001 implementation methodologies, bypassing direct vendor relationships for enterprise accounts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Japan's compressed 72-hour breach notification timeline creates a regulatory arbitrage opportunity against jurisdictions with longer disclosure windows, rewarding vendors with automated containment capabilities.
For Market Incumbents: Acquire specialized incident-response engineering teams to offset domestic talent scarcity. Integrate immutable backup architectures with JIS Q 27001 certification auditing to capture higher-margin recurring revenue. Consolidate vendor panels among manufacturing clients to reduce multi-vendor orchestration complexity threatening sub-minute containment targets. For New Entrants and Emerging Players: The premium-economy pricing gap in cloud-native mid-market protection creates entry opportunity. Target Osaka-Kobe pharmaceutical clusters with SaaS-delivered managed detection and response, bypassing capital constraints that slow on-premise adoption. Lead with native API integration against existing productivity suites to accelerate deployment velocity. For Investors and Strategic Acquirers: Domestic telecommunications carriers are the most active acquirer in this space, leveraging network infrastructure ownership for downstream security service bundling. Long-term viability hinges on vertical integration into managed security operations with compliance auditing capabilities. Monitor METI supply-chain risk assessment mandate expansion as inflection signal for vendor consolidation acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Managed Security Service Bundling | Telecommunications carriers leverage network ownership to capture 24/7 monitoring margins. |
| JIS Q 27001 Certification Integration | Systems integrators embed ransomware protection within compliance auditing contracts. |
| Cloud-Native Platform Launch | SaaS delivery bypasses capital constraints constraining mid-market on-premise adoption. |
| Domestic Threat Intelligence Feed Development | Localized attack-pattern detection distinguishes vendors against global platform competitors. |
| Immutable Backup Architecture Deployment | Air-gapped recovery appliances address regional bank talent scarcity with minimal staffing. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window. Primary engagement encompassed CISOs at financial institutions, healthcare delivery organization IT directors, manufacturing plant engineers, and managed security service provider operations leads. Secondary validation drew from METI cybersecurity framework disclosures, PMDA medical device software security guidelines, JIS standards documentation, and hyperscaler regional capex reports. Bottom-up deployment model adoption curves and top-down regulatory mandate timelines were triangulated for convergence.
Segment-weighting approaches anchored the analytical framework across the analysis window. Modeled dimensions included solution layer, deployment architecture, end-user vertical, and service type complexity. CAGRs were derived from segment-level growth rate reconciliation against aggregate market trajectory. Forecast inputs incorporated METI mandate compliance deadlines and PMDA guideline implementation phases without specific year anchoring.
Caveats apply where regulatory timeline acceleration or hardware security module supply disruption could materially shift the outlook. Forecasts reflect assumptions about domestic talent pipeline development and cloud migration velocity among mid-market firms. Material deviation in breach notification enforcement intensity or semiconductor foundry capacity warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
North America IoT Security Market
Cybersecurity
Europe Digital Forensics Market
Cybersecurity
Portugal Cybersecurity Market
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Global Digital Forensic Laboratory As a Service Market
Cybersecurity
Malaysia Cybersecurity Market
Cybersecurity
Global Network Forensics Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
Cryptojacking Solution Market
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Oman Cybersecurity Market