
 Operational Technology Security Market | 2026-2036
Operational Technology Security Market Size, Share, and Industry Trends Forecast 2026-2036
Operational Technology Security Market Outlook
The EU Cyber Resilience Act is realigning procurement criteria for connected industrial equipment across European manufacturing. Fortinet leverages integrated platform architecture to consolidate firewall and segmentation functions for plant operators. Dragos specializes in threat intelligence tailored to electric utilities and oil-and-gas infrastructure. Nozomi Networks anchors its position through passive network monitoring that maps industrial protocols without disrupting SCADA operations.
Operational technology security encompasses hardware and software defenses engineered to protect industrial control systems, distributed control networks, and supervisory data acquisition infrastructure from unauthorized access, malware injection, and process manipulation. These systems enforce deterministic latency thresholds below 10 milliseconds to avoid disrupting real-time manufacturing or energy dispatch cycles. Firewalls and intrusion detection systems command the largest installed base, though security information and event management platforms capture expanding budget share as facilities consolidate visibility across hybrid IT-OT environments. Cloud-based deployment options are gaining traction among mid-sized manufacturers seeking managed detection without on-site security engineering depth.
NIST SP 800-82r3 guidelines, IEC 62443 standards, and the EU Cyber Resilience Act collectively mandate baseline security capabilities for critical infrastructure operators and connected device manufacturers. IEC 62443 certification tiers now function as de facto market access requirements for European industrial automation vendors. Stakeholders must monitor evolving sector-specific mandates from the EPA and FERC in the United States, where water treatment and power generation face distinct incident reporting obligations.
Market Dynamics
The operational technology security market is experiencing structural compression as legacy SCADA networks converge with cloud-native monitoring platforms, forcing vendors to re-architect products for hybrid IT-OT environments without breaching deterministic latency thresholds.
Growth Catalysts
- NERC CIP enforcement:North American electric utilities face escalating penalty exposure for critical infrastructure protection violations, accelerating replacement of perimeter-only defenses with continuous monitoring architectures.
- Automotive manufacturing clusters:Germany's chemical and vehicle production corridors are deploying passive network monitoring after ransomware campaigns disrupted assembly line PLCs.
- IEC 62443 certification mandates:European industrial automation vendors now treat security certification tiers as market access requirements, embedding baseline capabilities into new control system shipments.
Market Restraints
- Specialized engineering talent scarcity:OT security operations require hybrid expertise spanning industrial protocols and enterprise cybersecurity, with qualified practitioners concentrated in Germany and the United States.
- Legacy system replacement cycles:Manufacturing facilities operate control hardware with 15-20 year lifespans, creating asynchronous upgrade timelines that fragment security architecture decisions.
- Segmentation complexity costs:Microsegmentation deployment in brownfield environments demands extensive network mapping and downtime windows that plant managers resist scheduling.
Strategic Opportunities
- Managed detection services:Mid-sized manufacturers without on-site security engineering depth are adopting cloud-based monitoring subscriptions to access threat intelligence and incident response capabilities.
- Water treatment infrastructure:EPA incident reporting obligations for municipal utilities are creating procurement urgency for intrusion detection systems that map Modbus and DNP3 traffic patterns.
- AI-driven anomaly detection:Machine learning models trained on industrial protocol behavior are reducing false positive rates that previously limited automated response deployment.
Industry Challenges
- IT-OT organizational silos:Enterprise security teams and plant engineering departments operate under conflicting performance metrics, complicating unified incident response workflows.
- Vendor certification bottlenecks:IEC 62443 assessment timelines extend 12-18 months for complex distributed control systems, delaying product launches and revenue recognition.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Operational Technology Security Market |
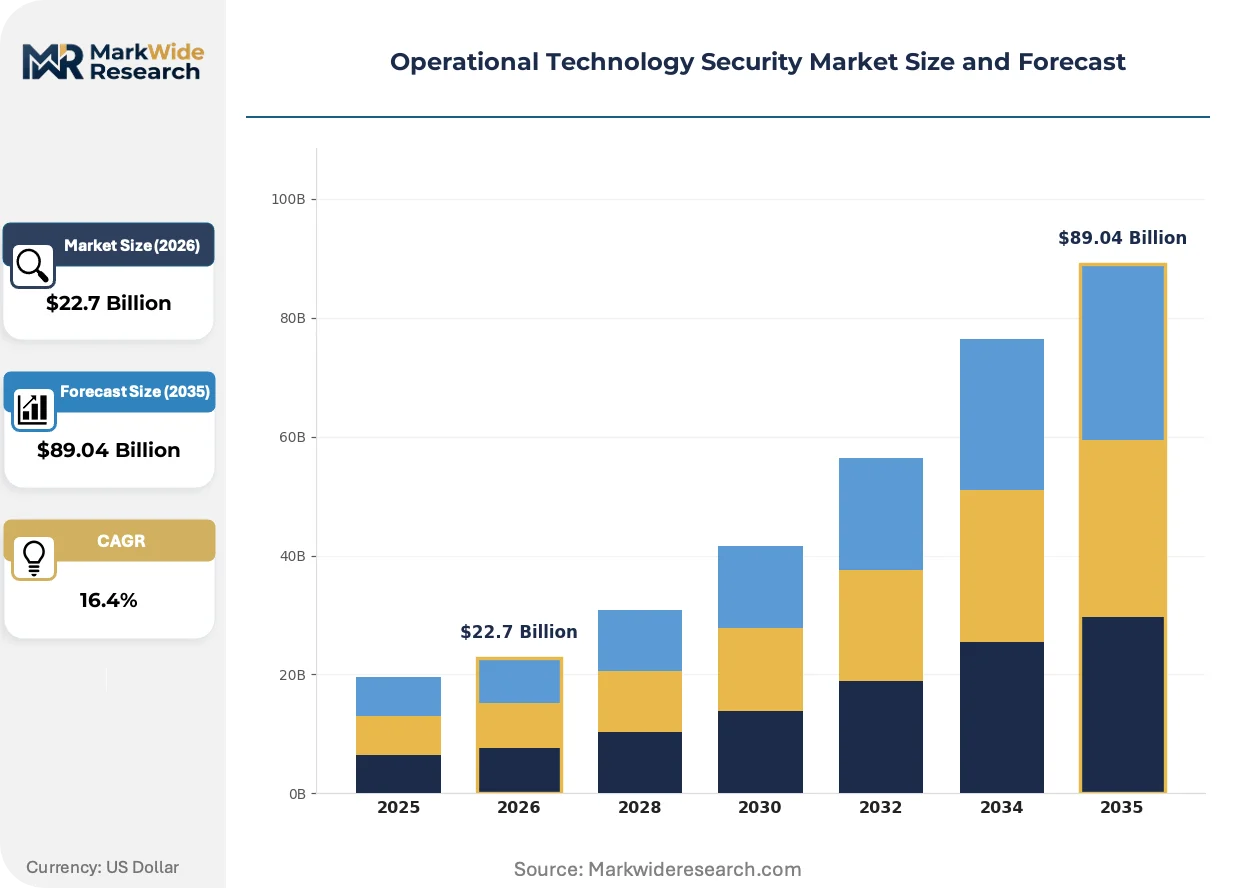
| Market Size in 2026 | $22.7 Billion |
| Market Size in 2035 | $89.04 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewalls, Intrusion Detection Systems, Antivirus Software, Security Information and Event Management End User: Manufacturing Facilities, Energy Sector, Transportation Industry, Healthcare Organizations Technology: Network Segmentation, Threat Intelligence, Endpoint Detection, Risk Assessment Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services |
| Companies Covered | Fortinet, Cisco Systems, Tenable, Forcepoint, Palo Alto Networks, Nozomi Networks, Dragos, Claroty, Microsoft, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Operational Technology Security Market Strategic Shifts
Platform consolidation is compressing vendor margins while expanding functional scope, as buyers reject point-product accumulation in favor of unified architectures spanning firewall, monitoring, and response orchestration.
Passive network monitoring technology is consolidating visibility across heterogeneous industrial environments without requiring agent installation on legacy controllers. Automotive and chemical manufacturers in Germany's industrial corridor are deploying these systems at accelerated pace to satisfy insurance underwriting requirements. The technology is consolidating previously separate network mapping, protocol analysis, and threat detection budgets into single procurement decisions.
The EU Cyber Resilience Act is mandating security-by-design requirements for connected industrial equipment placed on European markets. Manufacturers must embed update capabilities and vulnerability disclosure processes into product lifecycles or face market exclusion. Industrial automation vendors serving German automotive OEMs are restructuring supply chain contracts to pass compliance liability downstream to component suppliers.
Utility procurement departments are unbundling security software from control system hardware purchases, creating separate evaluation criteria and vendor shortlists. Electric utilities facing FERC and EPA reporting obligations are establishing dedicated OT security procurement functions independent from traditional SCADA engineering teams. This pattern is most visible among North American power generation operators accelerating post-incident security investments.
Operational Technology Security Market Segmentation
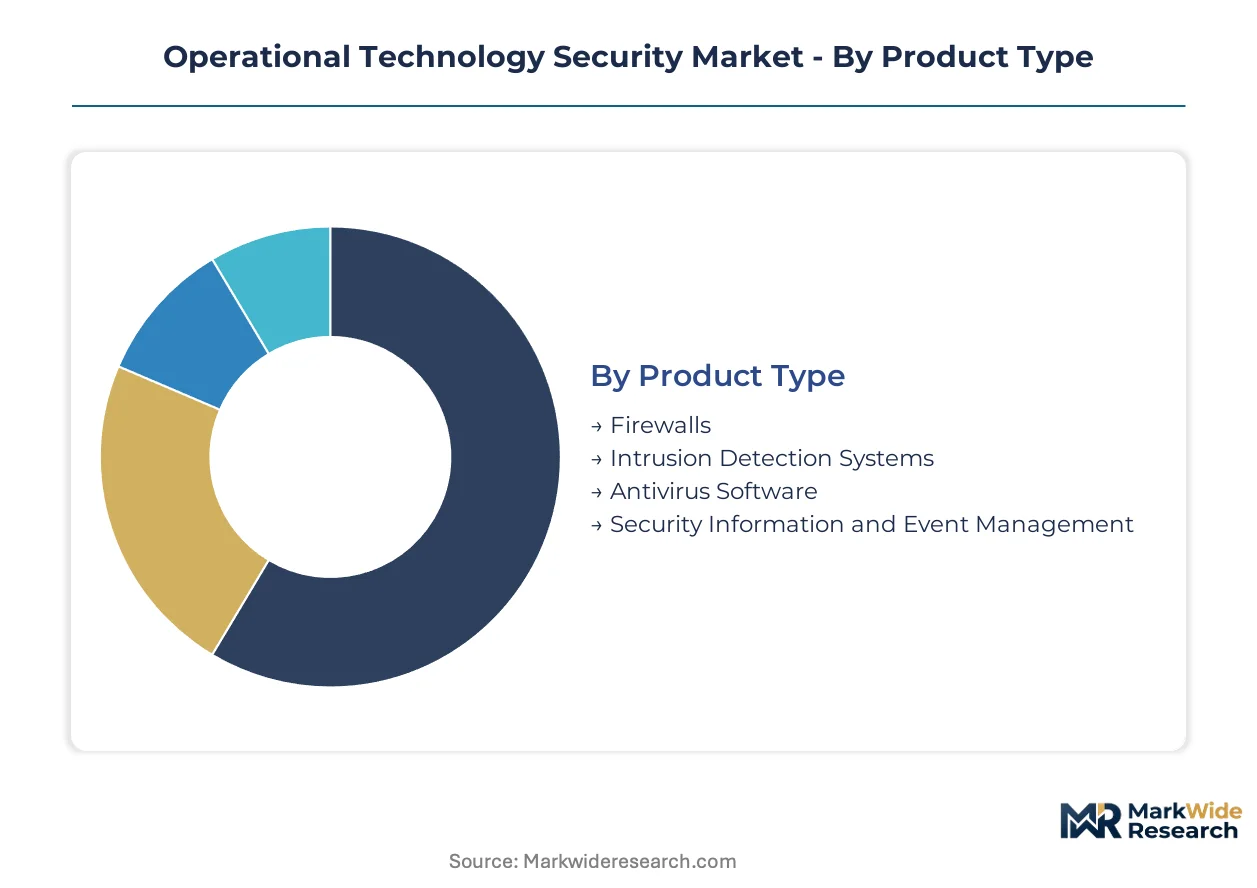
Operational technology security procurement diverges sharply across industrial contexts. Certification requirements, latency tolerances, and legacy infrastructure constraints reshape how buyers evaluate solutions within each segment category.
Product Type:
IEC 62443 certification tiers impose distinct validation burdens across product categories, with SL-3 and SL-4 compliance extending development timelines for critical infrastructure deployments.
- Firewalls:Industrial firewalls enforce protocol-aware filtering for Modbus, DNP3, and EtherNet/IP traffic while maintaining sub-10 millisecond latency thresholds. German automotive OEMs mandate these for supplier network segmentation following ransomware disruptions to assembly line PLCs. IEC 62443-4-2 certification now functions as a market access requirement for European deployments.
- Intrusion Detection Systems:Passive network sensors map industrial protocol behavior without agent installation on legacy controllers. North American electric utilities facing NERC CIP enforcement are accelerating procurement of these systems to satisfy continuous monitoring mandates. EPA incident reporting obligations for water treatment operators are expanding addressable demand.
- Antivirus Software:Signature-based and behavioral endpoint protection tailored for Windows-based HMIs and engineering workstations in manufacturing environments.
- Security Information and Event Management:Consolidated visibility platforms integrating IT-OT telemetry streams for hybrid environment correlation and response orchestration.
Leading the category by volume: Firewalls. Growing fastest: Security Information and Event Management.
End User:
Procurement authority and budget allocation patterns vary substantially across end-user verticals, with regulated utilities operating under distinct compliance-driven purchasing cycles compared to discretionary manufacturing investments.
- Manufacturing Facilities:Discrete and process manufacturers deploy passive monitoring and segmentation solutions to protect brownfield control systems with 15-20 year replacement cycles. Germany's chemical corridor represents concentrated demand following insurance underwriting requirement changes. Legacy PLC vulnerabilities and ransomware exposure are accelerating procurement urgency.
- Energy Sector:Electric utilities, oil-and-gas operators, and renewable generation facilities face the most stringent regulatory exposure. NERC CIP enforcement actions in the United States have created penalty-driven procurement cycles independent of capital planning timelines. FERC and EPA reporting obligations mandate specific detection and logging capabilities.
- Transportation Industry:Rail signaling, port automation, and pipeline control systems requiring safety-critical system protection with deterministic availability requirements.
- Healthcare Organizations:Medical device networks and building automation systems in hospital environments subject to HIPAA security rule compliance.
Dominating procurement volume: Energy Sector. Expanding most quickly: Manufacturing Facilities.
Technology:
Technology selection correlates directly with organizational maturity and in-house engineering depth, with advanced capabilities concentrated among large operators while mid-sized facilities favor managed alternatives.
- Network Segmentation:Microsegmentation and zone-based architectures enforce least-privilege communication paths between control system tiers. Brownfield deployment complexity and required downtime windows limit adoption among continuous-process manufacturers. German automotive clusters are deploying these at accelerated pace to satisfy OEM supplier security mandates.
- Threat Intelligence:Industrial-specific indicator feeds and adversary campaign tracking tailored to electric utility and oil-and-gas targeting patterns. Dragos and specialized vendors dominate this capability layer with sector-focused research teams.
- Endpoint Detection:Agent-based monitoring for Windows engineering workstations and HMIs with behavioral analysis for removable media and lateral movement detection.
- Risk Assessment:Asset inventory, vulnerability prioritization, and consequence-driven scoring methodologies for control system environments.
Capturing largest budget share: Network Segmentation. Climbing the fastest: Threat Intelligence.
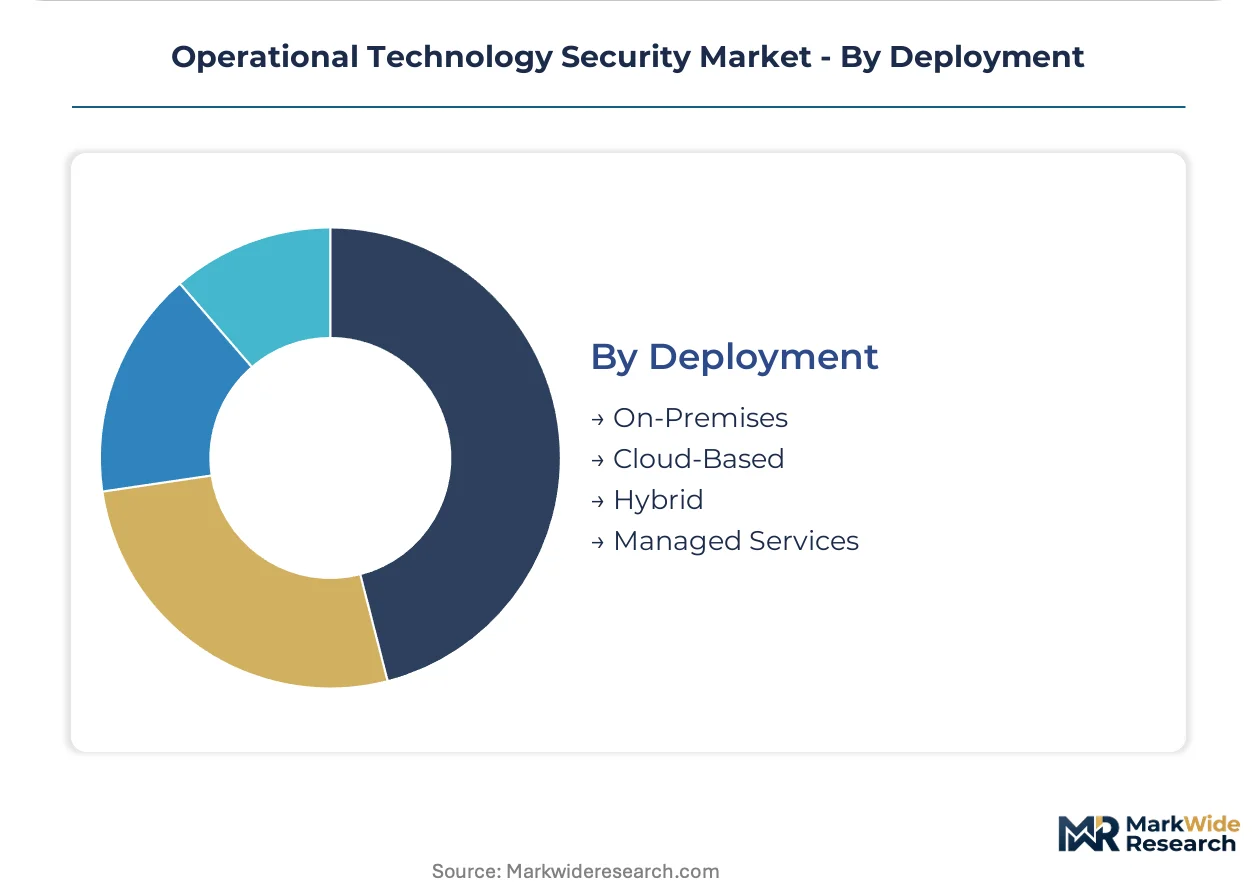
Deployment:
Deployment model selection reflects talent availability and capital preference, with cloud-native options gaining traction among mid-sized operators lacking on-site security engineering.
- On-Premises:Appliance-based and software deployments within facility data centers or control rooms requiring local engineering expertise for configuration and maintenance. Large electric utilities and chemical manufacturers prefer this model for air-gapped or high-assurance environments.
- Cloud-Based:SaaS-delivered monitoring and analytics platforms reducing upfront capital requirements and specialized staffing needs. Mid-sized manufacturers across Germany and the United States are adopting these subscriptions to access threat intelligence capabilities without building in-house SOC functions.
- Hybrid:Split architectures with on-premises sensors and cloud-based analytics planes balancing latency requirements with scalability.
- Managed Services:Fully outsourced detection, investigation, and response functions delivered by specialized OT security providers.
Highest installed base: On-Premises. Steepest expansion trajectory: Cloud-Based.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Production of OT security platforms concentrates in the United States and Germany, while consumption spreads across industrialized economies with legacy infrastructure exposure. Procurement patterns diverge sharply between penalty-driven utility markets and insurance-influenced manufacturing clusters.
United States
Electric utilities facing NERC CIP enforcement actions are accelerating security procurement independent of capital planning cycles. FERC and EPA reporting obligations mandate specific intrusion detection capabilities for power generation and water treatment operators. The Gulf Coast petrochemical corridor and Texas independent power producers represent concentrated demand for continuous monitoring architectures.
Germany
Automotive OEMs and chemical manufacturers in the industrial corridor are deploying passive network monitoring after ransomware disrupted assembly line PLCs. The EU Cyber Resilience Act and IEC 62443 certification tiers function as de facto market access requirements for control system vendors. Bavaria's automotive supplier networks and North Rhine-Westphalia's chemical complexes are restructuring procurement criteria to pass compliance liability downstream.
China
State-owned power generators and petrochemical operators are mandating domestic security platforms for critical infrastructure under MIIT guidance. GB standards and national cybersecurity law impose data localization requirements on foreign vendors. The Yangtze River Delta manufacturing belt and Shandong Peninsula energy complexes are consolidating IT-OT security budgets under state procurement frameworks.
Japan
Automotive and electronics manufacturers are extending supplier security mandates to tier-2 component vendors under METI industrial cybersecurity guidelines. JIS standards for control system security are tightening procurement specifications for domestic automation vendors. The Chubu region around Nagoya and Kansai industrial corridor are deploying hybrid cloud monitoring for brownfield facility upgrades.
United Kingdom
Water utilities and nuclear operators are implementing NIS2-aligned security frameworks ahead of enforcement deadlines. The national cybersecurity center is publishing sector-specific guidance for operational technology risk management. Scotland's offshore wind installations and England's water treatment networks are procuring managed detection services to address engineering talent scarcity.
Operational Technology Security Market Competitive Environment
The competitive structure tilts toward platform consolidation as buyers reject point-product accumulation in favor of unified architectures. Specialist vendors with industrial protocol expertise compete against diversified cybersecurity incumbents extending into OT environments. Two strategic archetypes dominate: integrated platform providers spanning firewall through response orchestration, and pure-play OT specialists with sector-specific threat intelligence. Competitive moves center on certification acceleration to satisfy IEC 62443 timelines and managed service packaging for mid-sized manufacturers lacking in-house security operations.
Within the integrated platform tier, Fortinet and Cisco Systems exemplify vendors consolidating firewall, segmentation, and monitoring functions into unified procurement decisions. Among pure-play specialists, Dragos and Nozomi Networks occupy positions defined by industrial-specific threat intelligence and passive network monitoring capabilities respectively. Claroty represents the archetype of OT-native vendors extending from visibility into risk assessment and response orchestration. Microsoft anchors the cloud-native entry vector, leveraging existing enterprise relationships to displace on-premises deployments among hybrid-environment manufacturers.
| Leading Market Players |
|---|
| Fortinet |
| Cisco Systems |
| Tenable |
| Forcepoint |
| Palo Alto Networks |
| Nozomi Networks |
| Dragos |
| Claroty |
| Microsoft |
| Others |
Value Chain & Pricing Dynamics
OT security engineering talent concentrated in Germany and the United States commands premium compensation that widens pricing-tier spreads between managed service bundles and self-deployed appliance configurations.
Pricing Analysis
Margin tightening in cloud-based monitoring tiers reflects talent arbitrage as mid-sized manufacturers substitute subscription fees for scarce in-house SOC staffing. Three-tier pricing structure across premium, standard, and economy levels differentiates by IEC 62443 certification grade and after-sales engineering support depth. Pricing pressure stems from platform consolidation as buyers reject point-product accumulation. Water treatment utilities facing EPA mandates show highest price sensitivity; electric utilities under NERC CIP enforcement demonstrate lowest sensitivity due to penalty avoidance calculus.
Supply Chain Analysis
Specialized semiconductor components for industrial firewalls rest on Taiwanese foundry capacity and German automotive-grade chip packaging facilities. Firmware development draws from Israeli cybersecurity research clusters and United States threat intelligence feeds. Single-source vulnerability concentrates in proprietary industrial protocol parsing engines. Distribution runs through certified system integrators with IEC 62443-2-4 credentials, bypassing traditional IT channel partners.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market rewards vertical-integration into managed detection services, with downstream service revenue now exceeding hardware margins for platform vendors.
For Market Incumbents: Anchor platform consolidation momentum by accelerating IEC 62443-4-2 certification timelines ahead of competitor product launches. Deepen threat intelligence differentiation against cloud-native entrants from enterprise IT security. Prioritize managed service packaging for mid-sized German automotive suppliers lacking captive security operations. For New Entrants and Emerging Players: Municipal water utilities represent an underserved buyer archetype with urgent EPA compliance deadlines and limited incumbent penetration. Target intrusion detection systems for Modbus and DNP3 protocol environments with simplified deployment requiring minimal downtime. Pursue channel partnerships with regional engineering firms holding existing SCADA maintenance contracts. For Investors and Strategic Acquirers: The window for entry favors pure-play OT specialists with sector-specific threat intelligence capabilities and established utility customer relationships. Long-term viability hinges on certification acceleration capacity and managed service attach rates. Monitor IEC 62443 assessment timeline compression as an inflection indicator for vendor competitive positioning.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies firewall, segmentation, and monitoring functions to displace point-product vendors in German automotive procurement. |
| Managed Detection Service Launch | Captures recurring revenue from mid-sized manufacturers lacking NERC CIP-mandated security engineering depth. |
| IEC 62443 Certification Acceleration | Shortens 12-18 month assessment timelines to match European market access requirements for control system vendors. |
| Threat Intelligence Partnership | Secures industrial-specific adversary tracking for electric utilities facing escalating ransomware targeting. |
| Geographic Expansion | Establishes local engineering presence in Texas Gulf Coast petrochemical corridor and Bavarian automotive supplier networks. |
Study Parameters
Document review covered NERC CIP enforcement records, EPA incident reporting guidelines, IEC 62443 certification databases, and EU Cyber Resilience Act implementation drafts, complemented by interviews with utility CISOs, plant engineering directors, OT security vendors, and industrial system integrators. Secondary validation drew from FERC filings, German automotive OEM supplier mandates, and customs data on industrial firewall imports. Bottom-up deployment estimates triangulated against top-down security spending surveys from energy and manufacturing trade associations.
Cross-referencing historical procurement patterns with panel input from utility procurement officers and manufacturing IT directors shaped the analytical framework across the analysis window. Segmentation dimensions modeled include product type, end-user vertical, deployment architecture, and regional regulatory cluster. CAGRs derived from vendor revenue disclosures and facility-level security budget allocations, with specific weighting for NERC CIP penalty exposure and insurance underwriting requirement changes in German industrial corridors.
Revisions become necessary when regulatory enforcement intensity shifts, certification timeline bottlenecks ease, or platform consolidation accelerates beyond current trajectories. Forecasts reflect documented assumptions about compliance-driven procurement cycles and talent availability constraints. A small set of triggers—EPA rulemaking expansion, IEC 62443 timeline compression, and cloud-native entrant pricing aggression—warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cyber Security Consulting Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Global Database Encryption Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
India Network Security and Cyber Risk Management Market
Cybersecurity
Japan Ransomware Protection Market
Cybersecurity
India Ransomware Protection Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
Global Email Encryption Market
Cybersecurity
V2X Cybersecurity Market
Cybersecurity
Egypt Cybersecurity Market
Cybersecurity
Cloud Access Security Broker Market
Cybersecurity
Europe Zero Trust Security Market