
 Content Delivery Network (CDN) Security Market | 2026-2036
Content Delivery Network (CDN) Security Market Size, Share, and Industry Trends Forecast 2026-2036
Content Delivery Network (CDN) Security Market Outlook
ISO 27001 certification is rotating as the baseline qualification for enterprise CDN security procurement, filtering vendors without audited information security management systems. Akamai Technologies leverages its globally distributed edge platform to sustain compliance-heavy contracts in financial services and government sectors. Cloudflare competes on developer-centric deployment velocity, while Amazon Web Services anchors large-scale integrations through native cloud ecosystem lock-in.
Content Delivery Network (CDN) Security encompasses distributed edge infrastructure designed to inspect, filter, and encrypt traffic at points of presence proximal to end users, typically operating with sub-50 millisecond latency requirements for real-time threat interception. Its primary commercial purpose is to prevent volumetric attacks, application-layer intrusions, and data exfiltration without degrading content delivery performance. DDoS Mitigation services within the Service Type dimension dominate current revenue pools due to their subscription-like renewal patterns and measurable downtime prevention value. Hybrid Cloud deployment models are expanding fastest as enterprises retain sensitive policy engines on-premises while bursting scrubbing capacity to public infrastructure.
FCC guidelines on communications infrastructure resilience and GDPR data-localization mandates from European regulators are elevating demand for regionally distributed encryption and access control functionality. NIST zero-trust architecture standards and SEC cybersecurity disclosure rules are further tightening procurement specifications for publicly traded enterprises in the United States. Stakeholders must monitor how quantum-resistant encryption requirements and evolving sovereign data laws reshape hardware and software refresh cycles across edge security stacks.
Market Dynamics
Zero-trust architecture mandates are compressing procurement cycles and forcing edge security stacks into continuous verification models, eliminating implicit trust zones across distributed infrastructure.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Publicly traded enterprises must report material security incidents within four business days, accelerating CDN security procurement to ensure real-time visibility and rapid incident containment.
- Financial Services Transaction Flows:Real-time payment networks and open banking APIs require sub-50 millisecond threat interception, driving edge-native security deployments at points of presence.
- Quantum-Resistant Cryptography:NIST post-quantum standards are forcing hardware refresh cycles, creating replacement demand for encryption modules across CDN edge nodes.
Market Restraints
- Hyperscaler Concentration Risk:Three cloud providers control the majority of global edge infrastructure, creating single-point-of-failure vulnerabilities and limiting vendor diversification options.
- Silicon Supply Volatility:Custom ASICs for traffic inspection face fabrication bottlenecks at Taiwan-based foundries, extending lead times for high-throughput edge appliances.
- Data Localization Friction:GDPR and emerging sovereign data laws fragment encryption key management, forcing redundant infrastructure deployments that inflate operational overhead.
Strategic Opportunities
- EU AI Act Compliance Layer:Automated content filtering and biometric data processing at the edge creates demand for policy enforcement engines integrated with CDN security stacks.
- India Digital Public Infrastructure:Unified Payments Interface expansion and government cloud mandates present untapped deployment opportunities for localized edge security.
- Confidential Computing Convergence:Trusted execution environments combined with CDN edge nodes enable privacy-preserving analytics for healthcare and financial data processing.
Industry Challenges
- Zero-Trust Architecture Integration:Legacy perimeter-based security tools require complete re-architecture, extending deployment timelines and demanding specialized systems integration expertise.
- ISO 27001 Certification Velocity:Vendor qualification cycles stretch 12-18 months, creating bottlenecks for enterprises with urgent compliance deadlines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Content Delivery Network (CDN) Security Market |
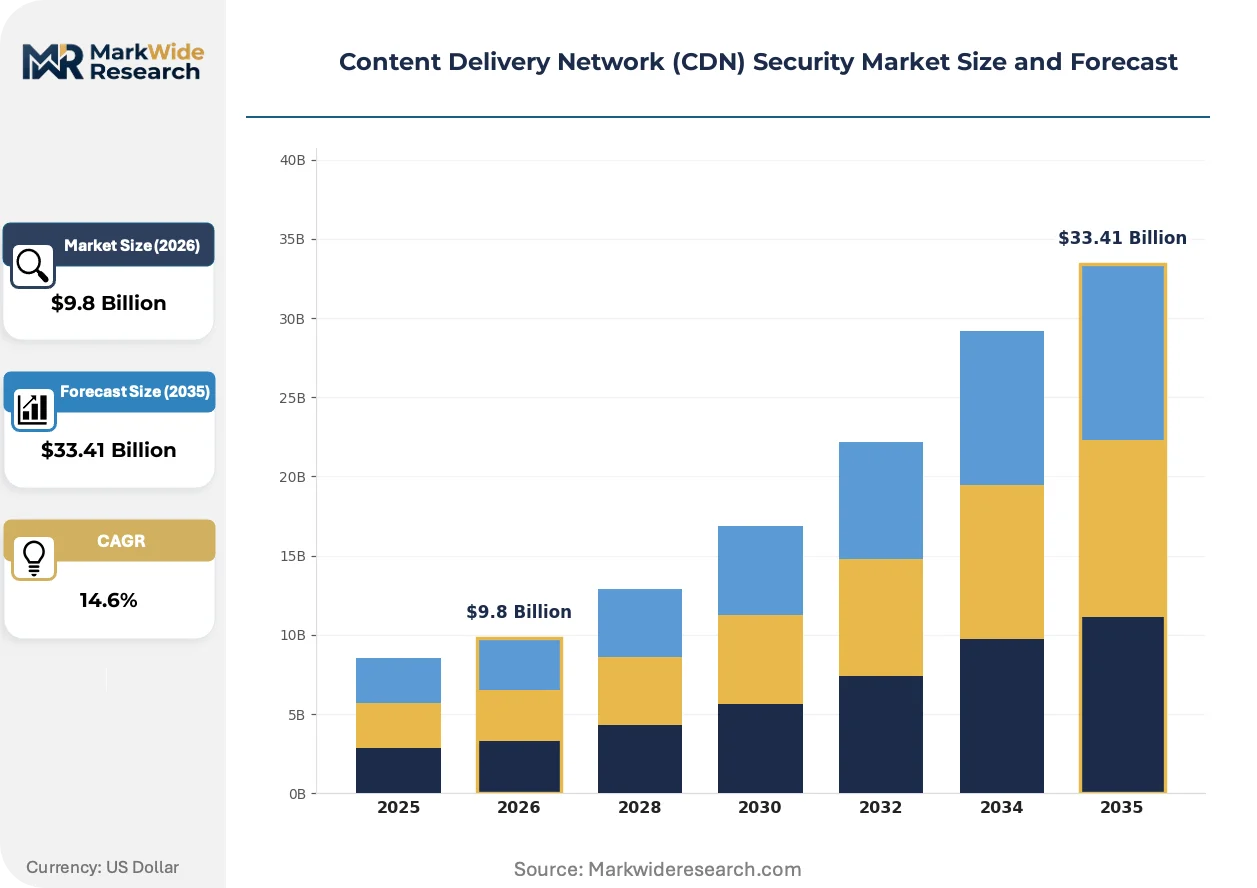
| Market Size in 2026 | $9.8 Billion |
| Market Size in 2035 | $33.41 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, On-Premises Service Type: DDoS Mitigation, Web Application Firewall, Secure Token, Video Delivery End User: E-commerce, Media & Entertainment, Financial Services, Government Functionality: Real-Time Protection, Traffic Monitoring, Data Encryption, Access Control |
| Companies Covered | Akamai Technologies, Cloudflare, Amazon Web Services, Google, Microsoft, Fastly, Imperva, Radware, F5, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Content Delivery Network (CDN) Security Market Strategic Shifts
Edge security architectures are fragmenting into composable microservices, enabling enterprises to mix vendor capabilities rather than accepting monolithic platform lock-in.
Web Application Firewall functionality is decomposing into discrete, API-callable inspection modules. Financial services firms are deploying these components as sidecar proxies within Kubernetes clusters. This modularization is compressing vendor switching costs and enabling best-of-breed assembly.
The EU AI Act's risk classification framework is mandating automated content moderation at network edges. High-risk AI deployments must maintain audit trails and human oversight capabilities. European media and fintech verticals are embedding policy engines directly into CDN points of presence to satisfy these requirements.
Enterprise buying committees are unbundling security and performance procurement decisions. Network operations teams now select CDN providers independently from security engineering groups selecting threat inspection tools. This bifurcation is most pronounced in United States federal contracting, where zero-trust mandates require separate evaluation of encryption, identity, and traffic management capabilities.
Content Delivery Network (CDN) Security Market Segmentation
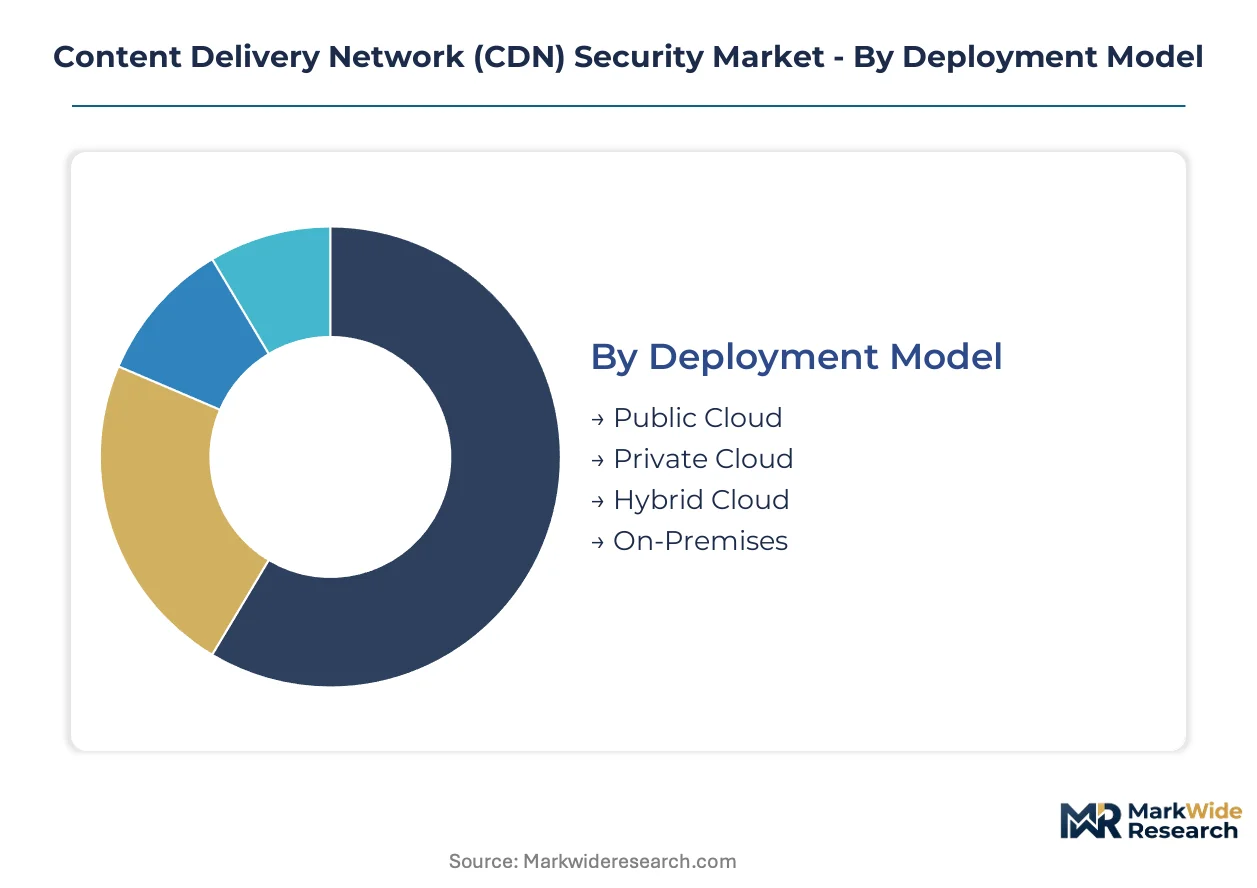
CDN security procurement splits across four distinct axes that determine architectural choices and vendor selection criteria. Deployment model dictates infrastructure ownership and compliance boundaries. Service type defines the threat surface covered. End user verticals impose sector-specific latency and regulatory requirements. Functionality segments separate preventive controls from detective and responsive capabilities.
Deployment Model:
Channel mix varies sharply by deployment topology: public cloud flows through hyperscaler marketplaces and direct enterprise sales, while hybrid and on-premises deployments route through systems integrators and value-added resellers with compliance expertise.
- Hybrid Cloud:Enterprises retain sensitive policy engines on-premises while bursting scrubbing capacity to public infrastructure during volumetric attacks. Financial services firms in the United States favor this model to satisfy SEC cybersecurity disclosure rules without sacrificing elastic response capacity.
- Public Cloud:Native integration with hyperscaler identity and networking stacks enables rapid provisioning through self-service portals. This segment concentrates among mid-market digital natives prioritizing developer velocity over custom compliance architectures.
- Private Cloud:Dedicated edge nodes within single-tenant environments serve defense contractors and classified government workloads. Procurement runs through specialized federal channel partners with security clearance requirements.
- On-Premises:Hardware appliances deployed in carrier-neutral facilities or enterprise data centers address data localization mandates. GDPR-sensitive European media organizations and sovereign cloud initiatives drive residual demand.
Public cloud dominates installed base. Hybrid cloud is where expansion concentrates.
Service Type:
Margin profiles diverge by service maturity: DDoS mitigation commands premium subscription pricing with measurable downtime prevention value, while video delivery and secure token services compete on volume throughput with thinner unit economics.
- DDoS Mitigation:Distributed scrubbing centers filter volumetric attacks before they reach origin infrastructure. Real-time payment networks and open banking APIs in the United States require sub-50 millisecond interception, anchoring demand at financial services edge nodes.
- Web Application Firewall:Layer 7 inspection blocks SQL injection, cross-site scripting, and API abuse. E-commerce platforms deploy these as sidecar proxies within Kubernetes clusters to protect checkout flows without adding origin latency.
- Secure Token:Cryptographic authentication validates content access rights for premium streaming and software distribution. Media and entertainment verticals embed these into DRM workflows.
- Video Delivery:Optimized caching and transport security for live and on-demand streaming. This segment faces commoditization pressure as performance and security procurement decisions unbundle.
DDoS mitigation anchors vendor revenue. Web Application Firewall is climbing the fastest.
End User:
Customer type determines sales cycle length and integration complexity: government and financial services stretch procurement to 12-18 months with ISO 27001 certification requirements, while e-commerce closes in 3-6 months on standardized cloud contracts.
- Financial Services:Real-time transaction flows and open banking APIs demand edge-native security with audit-grade logging. United States federal zero-trust mandates and SEC disclosure rules tighten procurement specifications.
- Government:Classified and civilian agencies require FedRAMP or equivalent authorization with regionally distributed encryption. NIST standards and FCC resilience guidelines shape technical requirements.
- E-commerce:Seasonal traffic spikes and checkout security drive demand for elastic DDoS protection and bot management. Peak provisioning occurs ahead of holiday shopping periods.
- Media & Entertainment:Live streaming and premium content distribution require low-latency token authentication and geo-fencing. EU AI Act content moderation mandates are embedding policy engines at network edges.
Financial services commands highest contract values. Government is gaining share fastest.
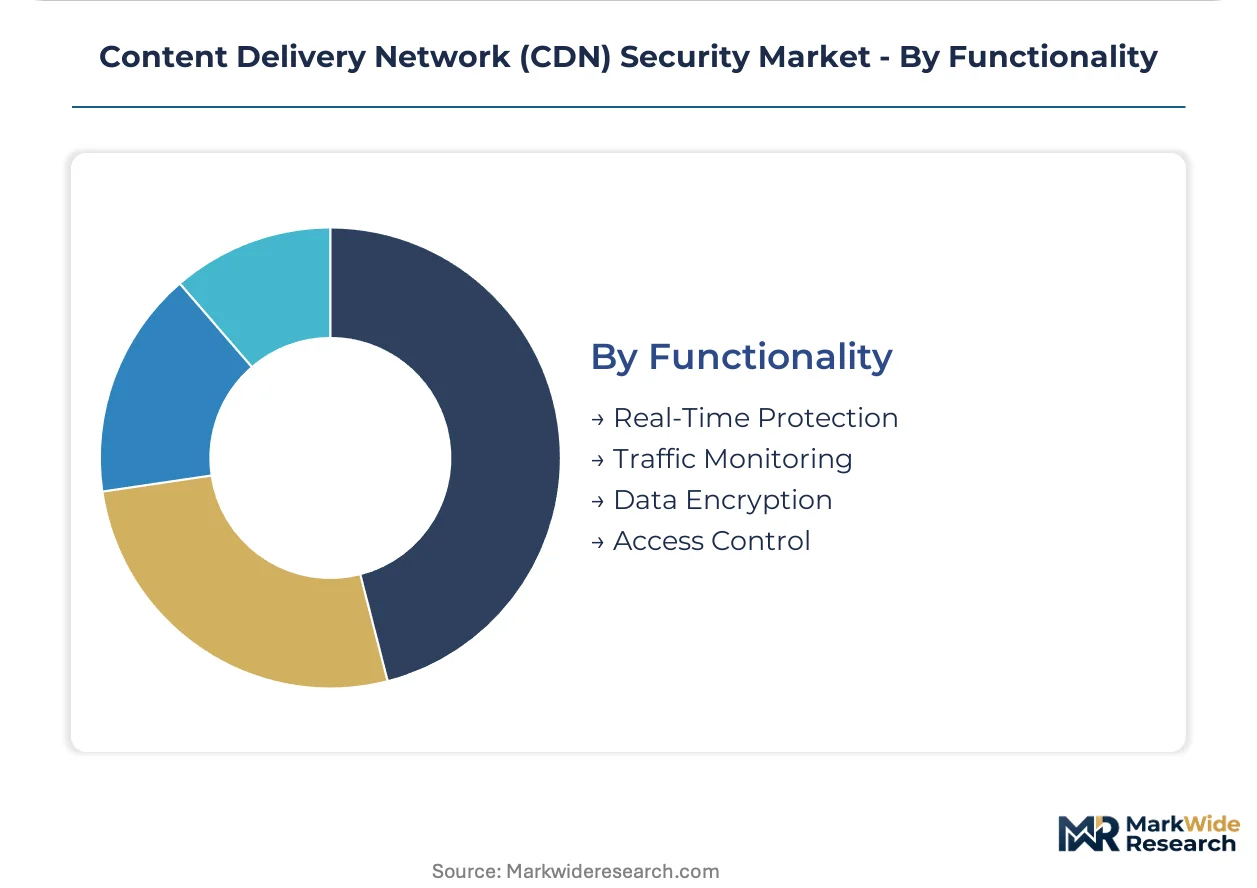
Functionality:
Technology maturity separates established capabilities from emerging differentiators: traffic monitoring and data encryption represent baseline table stakes, while real-time protection and access control incorporate newer zero-trust and confidential computing architectures.
- Real-Time Protection:Sub-50 millisecond threat interception at points of presence proximal to end users. Quantum-resistant cryptography upgrades are forcing hardware refresh cycles across edge nodes.
- Traffic Monitoring:Continuous flow analysis and anomaly detection with SIEM integration. This capability spans all deployment models as a foundational visibility layer.
- Data Encryption:TLS termination, field-level encryption, and key management at edge locations. GDPR and emerging sovereign data laws fragment key management architectures.
- Access Control:Identity-aware proxy and zero-trust network access enforcement. Confidential computing convergence with trusted execution environments enables privacy-preserving analytics.
Traffic monitoring saturates deployments. Real-time protection shows steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Zero-trust mandates and data localization requirements are redrawing CDN security procurement maps. Governments are weaponizing data sovereignty as industrial policy, forcing infrastructure fragmentation that vendors must architect around.
United States
SEC cybersecurity disclosure rules and NIST zero-trust standards compress procurement cycles for publicly traded enterprises. Federal mandates require continuous verification architectures across distributed edge nodes. Financial services clusters in New York and Chicago drive sub-50 millisecond threat interception deployments for real-time payment networks.
Germany
GDPR enforcement and the EU AI Act's risk classification framework elevate compliance-heavy contracts. Automotive and industrial manufacturing in Bavaria and Baden-Württemberg demand confidential computing integration for supply chain data processing. Frankfurt's carrier-neutral facilities anchor regional encryption key management infrastructure.
India
RBI guidelines on digital payments infrastructure and the Digital Personal Data Protection Act accelerate edge security deployments. Unified Payments Interface expansion creates localized scrubbing capacity requirements. Mumbai and Bangalore technology corridors concentrate demand from fintech and SaaS exporters serving global markets.
United Kingdom
Post-Brexit data adequacy negotiations and Financial Conduct Authority operational resilience rules reshape cross-border traffic inspection. London's financial services density sustains premium-tier DDoS mitigation contracts. Cambridge-Oxford technology clusters experiment with quantum-resistant cryptography pilots ahead of NIST standardization.
Japan
METI cybersecurity frameworks and critical infrastructure protection standards tighten procurement specifications for telecommunications and financial sectors. Tokyo-Osaka metropolitan corridors concentrate hyperscaler edge node deployments. Manufacturing supply chains in Aichi Prefecture drive demand for confidential computing at industrial IoT gateways.
Content Delivery Network (CDN) Security Market Competitive Environment
Player mix skews toward hyperscaler-anchored platforms with native cloud ecosystem integration. Three cloud providers control majority edge infrastructure capacity, creating tiered competitive dynamics between integrated suites and best-of-breed specialists. Strategic archetypes include: full-stack hyperscalers bundling security with compute primitives; edge-native specialists competing on developer velocity; and network-centric incumbents leveraging carrier relationships. Dominant competitive moves center on confidential computing convergence and quantum-resistant cryptography roadmap acceleration.
Within the hyperscaler tier, Amazon Web Services and Google exemplify cloud-native integration strategies that embed CDN security within broader infrastructure consumption. Akamai Technologies occupies a position representing network-centric incumbency, sustaining compliance-heavy contracts through globally distributed edge presence. Cloudflare sits within the developer-centric specialist archetype, competing on deployment velocity and API-first architectures that reduce switching costs for digital-native enterprises.
| Leading Market Players |
|---|
| Akamai Technologies |
| Cloudflare |
| Amazon Web Services |
| Microsoft |
| Fastly |
| Imperva |
| Radware |
| F5 |
| Others |
Value Chain & Pricing Dynamics
Subscription-based capacity reservation contracts lock in multi-year scrubbing commitments for financial services firms, anchoring price visibility while securing Taiwan-foundry ASIC allocation amid silicon fabrication bottlenecks. This structure concentrates procurement power among ISO 27001-certified vendors with proven hyperscaler integration, compressing margins for challengers lacking audited compliance credentials.
Pricing Analysis
Certification level creates the primary spread between premium-tier and economy-tier CDN security offerings. Three-tier pricing structure across FedRAMP-authorized, ISO 27001-compliant, and uncertified service levels anchors enterprise procurement decisions. Pricing pressure stems from hyperscaler bundling of security with compute primitives, forcing standalone vendors toward value-based differentiation. Mid-market digital natives exhibit highest price sensitivity, while government and financial services verticals prioritize compliance over unit cost.
Supply Chain Analysis
Container availability constraints across the Trans-Pacific trade lane extend lead times for custom traffic inspection appliances destined for carrier-neutral facilities. Hardware supply concentrates in Taiwan for ASIC fabrication, the United States for edge node assembly, and Germany for encryption module production. Custom silicon, FPGA substrates, and quantum-resistant cryptographic processors constitute critical input dependencies. Single-source vulnerability at Taiwan-based foundries threatens scrubbing capacity expansion timelines. Distribution runs through hyperscaler marketplaces for public cloud deployments and specialized systems integrators for hybrid and on-premises configurations.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
CDN security is approaching a platform-economics inflection where API-first interoperability and confidential computing convergence determine vendor survival. Ecosystem lock-in through native cloud identity and networking stacks is displacing standalone security procurement.
For Market Incumbents: Consolidate through backward integration into custom ASIC design to secure Taiwan-foundry allocation and reduce silicon supply volatility exposure. Deepen vertical integration by acquiring confidential computing specialists with trusted execution environment expertise. ISO 27001 certification velocity represents a critical defensive lever against emerging API-native challengers.
For New Entrants and Emerging Players: Lead with EU AI Act compliance automation as a wedge into European media and fintech verticals facing content moderation mandates. Target India's Digital Public Infrastructure expansion, where localized edge security demand outpaces incumbent footprint. Deploy Kubernetes-native sidecar proxy architectures to reduce switching costs for developer-centric buyers.
For Investors and Strategic Acquirers: Capital is best deployed toward edge-native specialists with quantum-resistant cryptography roadmaps and existing FedRAMP authorization. Long-term viability hinges on confidential computing convergence capabilities and hyperscaler partnership depth. Monitor NIST post-quantum standardization timelines as the primary inflection signal for hardware refresh cycle acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Integration | Trusted execution environments at CDN edge nodes enable privacy-preserving analytics for healthcare data processing under HIPAA. |
| Quantum-Resistant Cryptography Roadmap | NIST post-quantum standard alignment forces hardware refresh cycles across edge encryption modules. |
| EU AI Act Compliance Layer Development | Automated content filtering engines embedded at network edges satisfy risk classification mandates for European media verticals. |
| Hyperscaler Marketplace Expansion | Native AWS and Azure integration accelerates procurement velocity for mid-market digital-native enterprises. |
| India Digital Public Infrastructure Partnership | RBI-mandated localized scrubbing capacity addresses Unified Payments Interface security requirements. |
Study Parameters
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CDN security engineering leads, federal procurement officers, financial services CISOs, and hyperscaler platform architects. Secondary validation drew from SEC cybersecurity disclosure filings, NIST zero-trust architecture publications, EU AI Act regulatory texts, and hyperscaler capex deployment disclosures. Bottom-up segmentation modeling triangulated against top-down market sizing across deployment model, service type, end user vertical, and functionality dimensions.
Across the analysis window, projections incorporated elastic demand modeling for DDoS mitigation capacity, subscription renewal pattern analysis, and quantum-resistant hardware replacement cycle assumptions. Segmentation dimensions spanned hybrid versus public cloud deployment topology, DDoS mitigation versus Web Application Firewall service maturity, and financial services versus government versus e-commerce end user concentration. CAGR derivation rested on scrubbing center buildout rates, ISO 27001 certification velocity, and confidential computing adoption curves.
Forecasts assume regulatory continuity in SEC disclosure regimes and EU AI Act enforcement; material policy shifts would require re-modeling. Silicon supply volatility at Taiwan-based foundries and quantum standardization timeline delays constitute primary forecast revision risks. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Web Filtering Market
Cybersecurity
Middle East and Africa Cybersecurity Market
Cybersecurity
Server Security Market
Cybersecurity
Global Network Security Policy Management Market
Cybersecurity
Egypt Cybersecurity Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Application Security Market
Cybersecurity
AI in Cybersecurity Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Europe Zero Trust Security Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
Next-Gen Firewall Market
Cybersecurity
Taiwan Cybersecurity Market
Cybersecurity
United States Cybersecurity Market
Cybersecurity
Threat Intelligence Market
Cybersecurity
South Africa Cybersecurity Market