
 Russia Cybersecurity Market | 2026-2036
Russia Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Russia Cybersecurity Market Analytics
The gap between premium sovereign-grade platforms and commodity imported tools is expanding across Russian enterprise procurement. Kaspersky Lab leverages decades of antivirus R&D and state-trusted certifications to dominate high-assurance contracts. Positive Technologies sustains offensive security expertise that anchors its penetration testing and threat intelligence services. Group-IB competes through specialized fraud protection and incident response capabilities tied to financial sector clients.
Russia cybersecurity encompasses hardware, software, and services engineered to protect information systems from unauthorized access, disruption, or espionage through cryptographic protocols, intrusion detection algorithms, and access control frameworks operating at network perimeter and endpoint levels. The discipline secures critical infrastructure, commercial transactions, and state communications against evolving attack vectors. Threat detection solutions lead current procurement volumes as organizations prioritize real-time anomaly identification over reactive remediation. Cloud-based deployment models are gaining traction fastest among mid-market enterprises seeking elastic capacity without capital-intensive infrastructure buildouts. Government end users represent the most concentrated margin pool due to classified procurement requirements and long-term service contracts.
Russia's Federal Service for Technical and Export Control (FSTEC) certifies security products for classified systems, creating a compliance barrier that foreign vendors cannot cross. The Central Bank of Russia mandates granular cybersecurity standards for financial institutions through its information security regulations, driving recurring demand for audit and monitoring services. Stakeholders must monitor whether geopolitical technology restrictions harden into permanent architectural requirements that reshape vendor qualification criteria and procurement timelines.
Market Dynamics
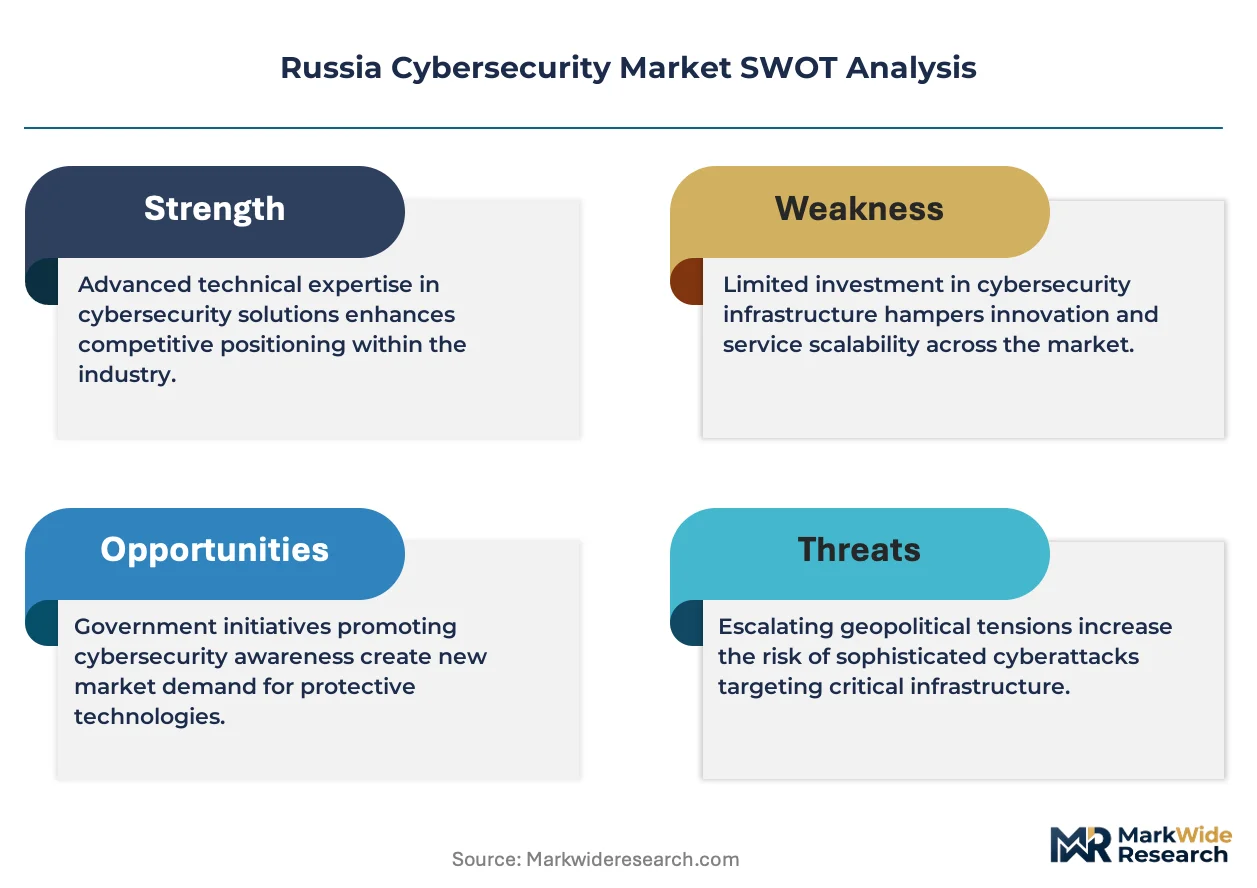
Federal Law No. 242-FZ mandates strict data localization, forcing domestic infrastructure buildouts and reshaping vendor qualification criteria across Russian enterprise procurement.
Growth Catalysts
- FSTEC Certification Requirements:The Federal Service for Technical and Export Control's security product approvals create exclusive access corridors for domestic vendors serving classified government systems.
- Financial Sector Mandates:Central Bank of Russia cybersecurity regulations impose granular audit and monitoring obligations on banks, generating recurring service contracts.
- Moscow Technology Corridor:Concentrated federal procurement and defense sector R&D spending in the capital region accelerates solution deployment cycles.
Market Restraints
- Semiconductor Import Dependencies:Restricted access to advanced chip fabrication limits hardware security module performance upgrades.
- Foreign Software Substitution Gaps:Legacy enterprise systems built on Western platforms face painful migration timelines without equivalent domestic alternatives.
- Geographic Vendor Concentration:Moscow-based solution providers dominate certified product pipelines, creating single-point-of-failure risks for nationwide deployment.
Strategic Opportunities
- Siberian Data Center Expansion:Cool climate and abundant energy resources position Novosibirsk and Irkutsk regions for hyperscale facility development.
- Industrial IoT Protection:Manufacturing and energy infrastructure digitization creates unmet demand for operational technology security integration.
- Sovereign Cloud Architecture:Federal requirements for state data processing on certified domestic platforms opens managed security service white space.
Industry Challenges
- Cryptographic Talent Scarcity:Shortage of engineers qualified in FSTEC-approved encryption protocols extends implementation timelines.
- Legacy System Integration Friction:Soviet-era industrial control systems lack native security interfaces, requiring expensive custom gateway development.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Russia Cybersecurity Market |
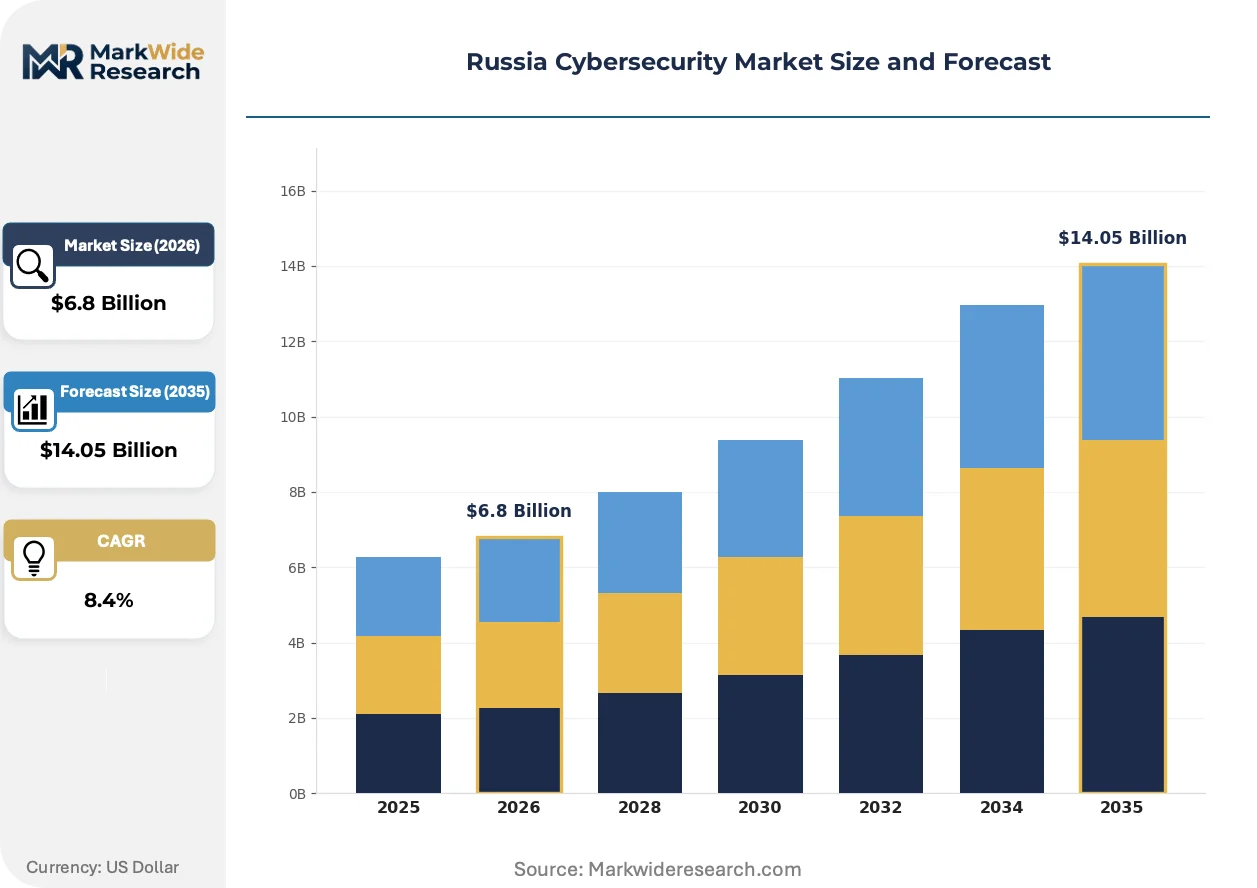
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $14.05 Billion |
| CAGR (2026 – 2036) | 8.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Threat Detection, Network Security, Endpoint Protection, Identity Management Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services Industry Segment: Finance, Healthcare, Retail, Telecommunications End User: SMEs, Large Enterprises, Government, Education |
| Companies Covered | Kaspersky Lab, Positive Technologies, Group-IB, Softline, Solar Security, Bi.Zone, Angara Technologies Group, InfoTeCS, Dr.Web, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Russia Cybersecurity Market Evolving Landscape
Threat detection architectures are fragmenting into composable components as buyers reject monolithic platforms. Sovereign compliance requirements and operational technology convergence are accelerating specialization.
Extended detection and response platforms are modularizing around API-first sensor networks. Mid-market enterprises in Saint Petersburg and Yekaterinburg adopt these architectures fastest, unbundling endpoint, network, and identity monitoring into vendor-agnostic layers. This modularity is compressing incumbent platform pricing power while elevating integration service margins.
Federal Law No. 187-FZ on critical information infrastructure imposes mandatory incident reporting and security audit frequencies on designated operators. Energy and transport sector entities face the steepest compliance curves, driving demand for automated governance documentation tools. Regional subsidiaries outside Moscow struggle with auditor availability, creating compliance backlogs.
Security service purchasing is consolidating under annual framework agreements rather than project-based contracting. Federal agencies and state corporations lead this transition, replacing discrete penetration tests with continuous validation subscriptions. This pattern is most visible in defense-adjacent procurement, where multi-year managed detection contracts now dominate vendor revenue mix.
Russia Cybersecurity Market Segmentation
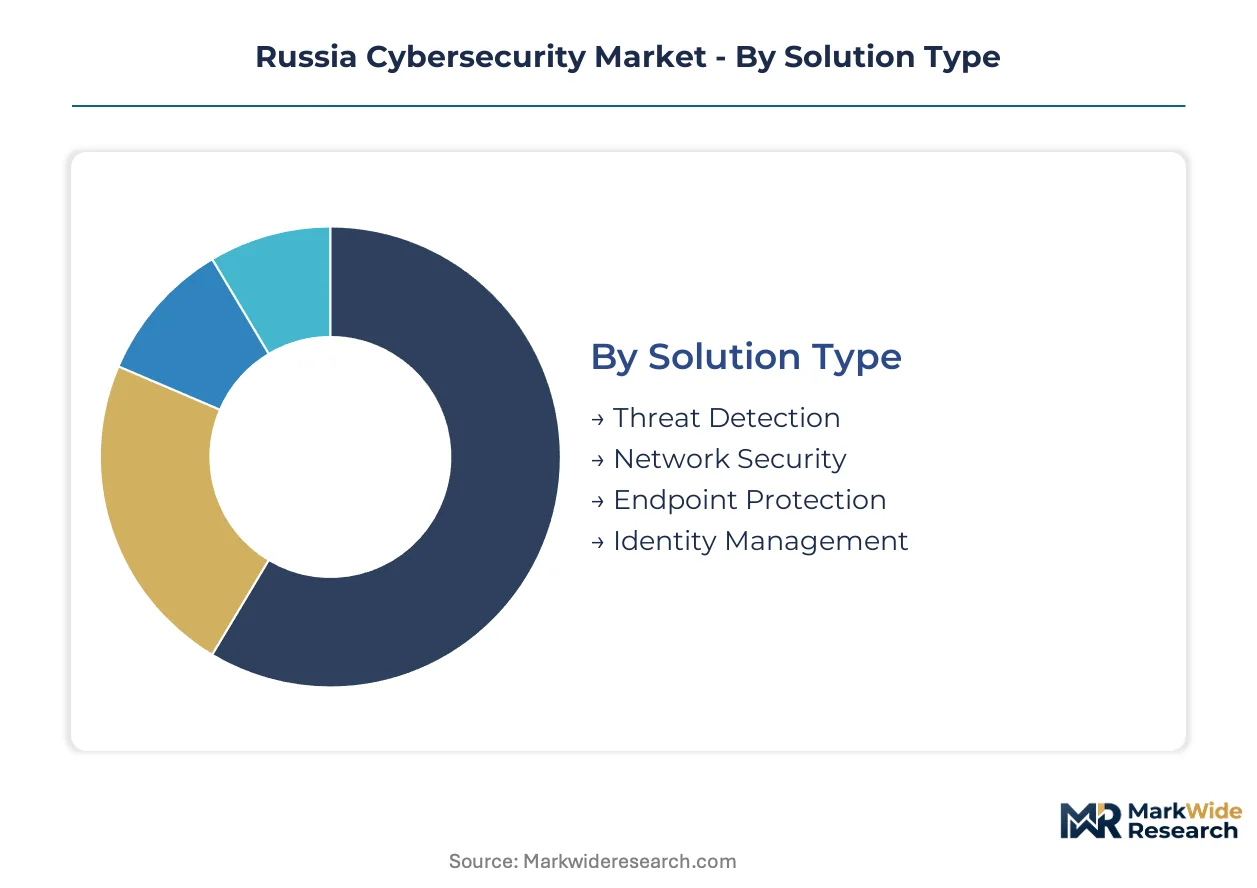
Russian cybersecurity procurement fragments across four intersecting dimensions. FSTEC certification requirements and Federal Law No. 242-FZ data localization rules reshape how buyers evaluate each category. Vendors must align segment-specific offerings with sovereign compliance thresholds.
Solution Type:
Customization intensity varies sharply—threat detection demands bespoke sensor tuning while endpoint protection standardizes faster.
- Threat Detection:Real-time anomaly identification systems process telemetry from network perimeters and endpoints through machine learning classifiers. Moscow-based defense contractors and federal agencies drive demand for sovereign-grade platforms with FSTEC-certified encryption modules.
- Network Security:Firewalls, intrusion prevention systems, and secure gateways enforce traffic segmentation at perimeter boundaries. Financial institutions in the capital region prioritize hardware appliances with domestic cryptographic processors to satisfy Central Bank audit requirements.
- Endpoint Protection:Antivirus and endpoint detection and response agents secure workstations and servers.
- Identity Management:Multi-factor authentication and privileged access control systems govern user credential lifecycles.
Most installed capacity flows through Network Security. Expansion is steepest in Threat Detection.
Deployment Model:
Capital intensity separates self-managed infrastructure from outsourced operations, with compliance liability clustering differently across each.
- On-Premises:Dedicated hardware and software installations within customer-controlled facilities. Government end users and defense sector entities mandate this model to maintain physical custody of classified data under FSTEC jurisdiction.
- Cloud-Based:Elastic compute and storage resources delivered from certified domestic providers. Mid-market enterprises in Saint Petersburg and Yekaterinburg adopt this fastest to avoid data center construction costs while meeting localization mandates.
- Hybrid:Mixed architectures spanning private infrastructure and sovereign cloud nodes.
- Managed Services:Continuous monitoring and incident response delivered under subscription contracts.
Government procurement concentrates in On-Premises. Cloud-Based deployment is gaining share fastest among commercial buyers.
Industry Segment:
Regulatory enforcement intensity creates tiered compliance obligations that reshape solution specifications.
- Finance:Banks, payment processors, and insurance carriers face granular Central Bank of Russia cybersecurity regulations. Mandatory penetration testing frequencies and incident reporting timelines generate recurring demand for audit automation platforms.
- Healthcare:Medical institutions and pharmaceutical distributors protect patient records and clinical systems. Regional hospital networks outside Moscow struggle with legacy system vulnerabilities and limited IT security staffing.
- Retail:E-commerce platforms and physical merchants secure payment card data and customer databases.
- Telecommunications:Network operators defend subscriber data and critical infrastructure under Federal Law No. 187-FZ designation.
Finance absorbs the highest compliance-driven spending. Healthcare shows the steepest expansion trajectory as digitization accelerates.
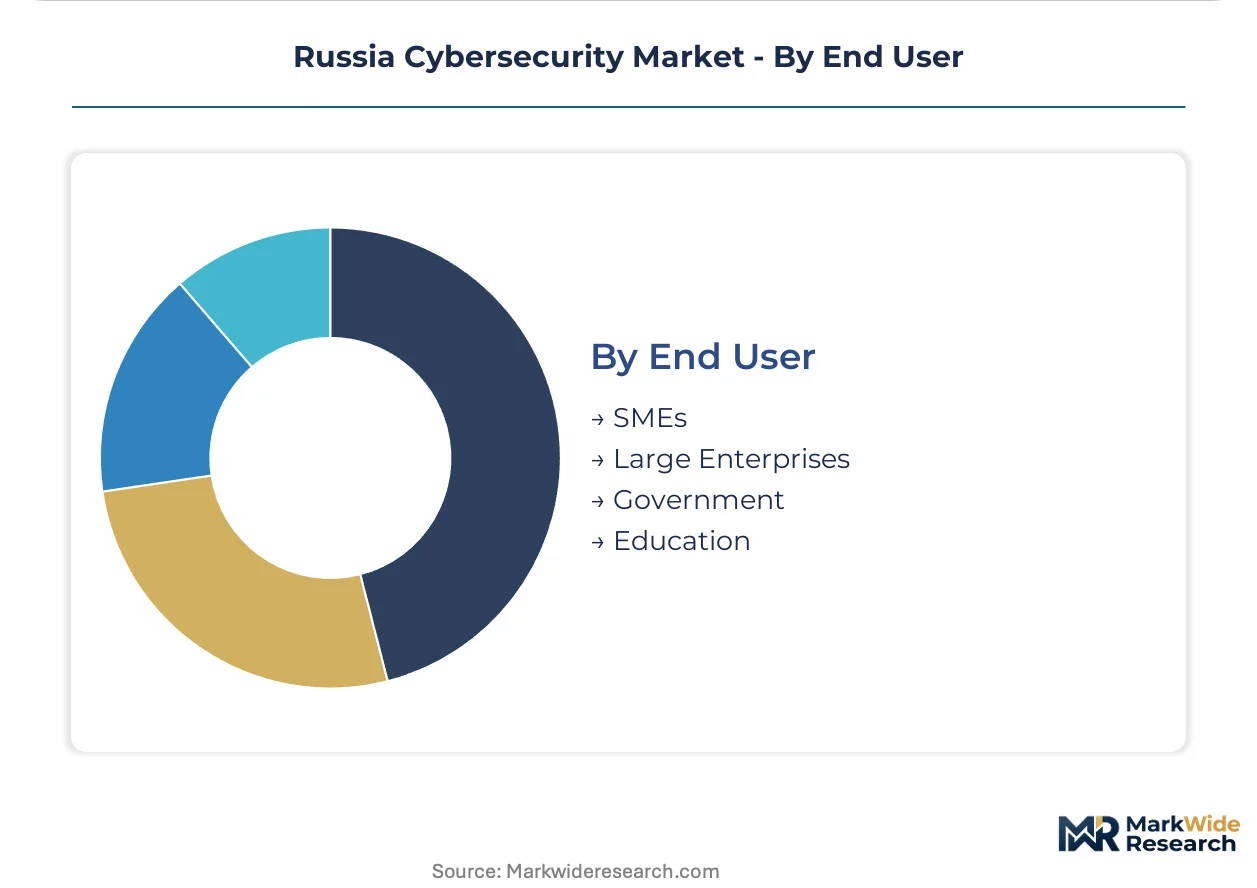
End User:
Procurement sophistication and contract scale diverge sharply across organizational size and sector.
- SMEs:Small and medium enterprises with limited internal security expertise. These buyers favor managed service bundles and cloud-delivered platforms to substitute for dedicated security operations centers.
- Large Enterprises:Major corporations with complex hybrid infrastructures and dedicated CISO functions. Energy and manufacturing conglomerates invest heavily in operational technology security integration for industrial control environments.
- Government:Federal agencies, state corporations, and military entities with classified procurement requirements. FSTEC certification gates restrict vendor pools to domestic providers with established security clearances.
- Education:Universities and research institutes protecting intellectual property and student records.
Government contracts command the highest margins. SME adoption is climbing the fastest as managed security services democratize access.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Moscow's concentration of cryptographic engineering talent anchors Russian cybersecurity development, with federal procurement corridors drawing specialists from Novosibirsk and Saint Petersburg research institutes.
Moscow and Central Federal District
Federal agency procurement and defense contractor R&D spending drive concentrated demand. FSTEC certification requirements restrict classified system vendors to domestic providers with security clearances. The Moscow Technology Corridor hosts Kaspersky Lab and Positive Technologies headquarters, anchoring high-assurance solution development.
Saint Petersburg and Northwestern Federal District
Mid-market enterprise adoption accelerates fastest in this region. Federal Law No. 242-FZ data localization mandates push commercial buyers toward certified domestic cloud providers. The city's financial services cluster generates recurring demand for audit automation and fraud protection platforms.
Novosibirsk and Siberian Federal District
Cool climate and abundant energy resources position this region for hyperscale data center expansion. Federal requirements for state data processing on certified domestic platforms drive infrastructure investment. The Akademgorodok research hub supplies cryptographic talent to nationwide security vendors.
Yekaterinburg and Ural Federal District
Industrial IoT digitization creates unmet demand for operational technology security integration. Federal Law No. 187-FZ critical infrastructure designations impose mandatory incident reporting on energy and transport entities. Manufacturing conglomerates invest heavily in custom gateway development for Soviet-era control systems.
Kazan and Volga Federal District
Regional bank networks and telecommunications operators anchor commercial cybersecurity procurement. Central Bank of Russia audit requirements generate service contract demand outside capital-based providers. The republic's IT park initiatives attract mid-tier managed security service operators.
Russia Cybersecurity Market Competitive Landscape
Capital-heavy infrastructure vendors compete with asset-light specialized service providers across Russian cybersecurity procurement. The vendor base clusters around three tiers: sovereign-grade platform developers with FSTEC certifications, mid-market cloud-native specialists, and regional managed service operators. Strategic differentiation centers on certification depth, vertical specialization, and geographic proximity to federal procurement corridors. Competitive moves concentrate on portfolio diversification into adjacent compliance services and strategic partnerships with state corporations.
Within the sovereign-grade tier, Kaspersky Lab and Positive Technologies occupy anchor positions representing decades of state-trusted development. Group-IB exemplifies the specialized fraud protection archetype, anchoring financial sector incident response capabilities. These Moscow-based entities sit within an exclusive vendor pool shaped by FSTEC jurisdiction and classified procurement requirements.
| Leading Market Players |
|---|
| Kaspersky Lab |
| Positive Technologies |
| Group-IB |
| Softline |
| Solar Security |
| Bi.Zone |
| Angara Technologies Group |
| InfoTeCS |
| Dr.Web |
| Others |
Value Network & Pricing Analysis
Captive cryptographic engineering clusters in Moscow anchor both supply security and pricing power for sovereign-grade platforms. Federal Law No. 242-FZ data localization mandates force domestic infrastructure buildouts that insulate certified vendors from commodity pricing pressure.
Pricing Analysis
The bundled-vs-unbundled service split separates government procurement from commercial adoption patterns. Three-tier pricing structure across premium, standard, and economy levels stratifies by FSTEC certification grade and customization depth. Cost compression in the mid-market tier is intensifying because cloud-native specialists unbundle endpoint, network, and identity monitoring into vendor-agnostic layers. SME buyers show highest price sensitivity while defense contractors accept premium positioning for classified system clearances.
Supply Chain Analysis
Dual-sourcing requirements for cryptographic processors mandate multi-supplier qualification across Taiwan, China, and South Korea fabrication facilities. Hardware security module production draws from advanced semiconductor lithography, domestic cryptographic chip foundries, and FSTEC-certified firmware development. Single-source vulnerability concentrates in Moscow-based certification pipelines. Distribution runs through federal procurement corridors and state corporation framework agreements.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Russia's cybersecurity market functions as a regulatory compounder where Federal Law No. 187-FZ critical infrastructure designations generate recurring compliance expenditure across energy and transport operators.
For Market Incumbents: Cement FSTEC certification depth as the primary defensive moat against emerging cloud-native specialists. Expand capacity in Novosibirsk cryptographic talent pools to offset Moscow concentration risk. Deepen backward integration into domestic hardware security module production to reduce semiconductor import exposure. For New Entrants and Emerging Players: API-first sensor networks offer the most penetrable wedge into Saint Petersburg and Yekaterinburg mid-market enterprises. Target operational technology security integration for manufacturing conglomerates struggling with Soviet-era control system vulnerabilities. Lead with managed detection subscriptions rather than perpetual license sales to align with federal framework agreement consolidation. For Investors and Strategic Acquirers: Roll-up economics work for regional managed security service operators because compliance backlogs outside Moscow create captive customer bases with high switching costs. The 5-10 year viability window favors platforms with sovereign cloud architecture capabilities. Watch Siberian data center buildout velocity as the signal for hyperscale infrastructure demand inflection.| Strategic Initiative | Industry Significance |
|---|---|
| FSTEC Certification Investment | Opens exclusive access corridors to classified government procurement pipelines. |
| Siberian Data Center Expansion | Captures Federal Law No. 242-FZ sovereign cloud requirements with cool climate advantages. |
| Operational Technology Security Integration | Addresses unmet demand from energy and manufacturing critical infrastructure operators. |
| Managed Detection Subscription Pivot | Aligns vendor revenue mix with federal framework agreement consolidation trends. |
| Cryptographic Talent Acquisition | Resolves implementation bottlenecks from FSTEC-approved encryption protocol scarcity. |
Research Methodology
Multiple input streams — primary interviews with CISOs, federal procurement officers, and FSTEC certification specialists; secondary validation through FSTEC registry filings, Central Bank of Russia regulatory circulars, and customs import data; plus hyperscaler capex disclosures — were reconciled through bottom-up and top-down triangulation.
Historical spending patterns were cross-referenced against panel input from defense contractors and financial institutions across the projection horizon. Segmentation dimensions modeled include deployment model, organization size, vertical regulatory intensity, FSTEC certification tier, and regional procurement corridor. CAGRs were derived from elasticity-adjusted adoption curves and compliance mandate enforcement timelines.
The model holds under stable geopolitical technology restriction regimes; deviation in semiconductor export control severity or cryptographic talent migration patterns would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Endpoint Security Market
Cybersecurity
Education Data Security Market
Cybersecurity
Israel Cybersecurity Market
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
Global Automated Breach and Attack Simulation (BAS) Market
Cybersecurity
Data Exfiltration Techniques Market
Cybersecurity
Industrial Cybersecurity Market
Cybersecurity
Latin America IoT Security Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
North America IoT Security Market
Cybersecurity
Network Traffic Analysis Solutions Market
Cybersecurity
Italy Cybersecurity Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Spain Cybersecurity Market
Cybersecurity
Europe SOC As a Service Market
Cybersecurity
Information Security Products and Services Market