
 CDN Security Market | 2026-2036
CDN Security Market Size, Share, and Industry Trends Forecast 2026-2036
CDN Security Market Analysis
Enterprise buyers are bifurcating between cloud-native startups and legacy financial institutions as the dominant procurement archetypes in CDN security. Akamai Technologies Inc. anchors its position through massive edge server footprint and deep carrier relationships. Cloudflare Inc. differentiates via developer-centric platform architecture and rapid feature velocity. Amazon Web Services Inc. competes by bundling CDN security into broader cloud consumption contracts, locking in enterprise spend.
CDN security encompasses distributed protection layers—web application firewalls, bot mitigation, and DDoS scrubbing—deployed across geographically dispersed edge nodes to intercept threats before they reach origin infrastructure. These systems operate at sub-50 millisecond latency thresholds to maintain application performance while filtering malicious traffic. DDoS Protection and Bot Management command the largest service type revenue pools, though CDN Security Analytics is expanding fastest as observability becomes a competitive requirement. Hybrid Cloud deployment is gaining share among regulated industries seeking data sovereignty controls, while Public Cloud remains the default for media and entertainment workloads.
The FCC enforces communications infrastructure resilience standards that shape CDN operator compliance investments in the United States. NIST zero-trust architecture guidelines and state-level data breach notification laws compound procurement complexity for domestic enterprises. ISO 27001 and IEC 62443 certifications increasingly function as market access prerequisites for vendor selection in regulated sectors. Stakeholders must weigh sovereign cloud requirements against the operational economics of hyperscaler edge networks when architecting multi-provider security stacks.
Market Dynamics
API traffic volumes in financial services are forcing edge infrastructure refresh cycles as latency-sensitive workloads migrate from centralized data centers to distributed scrubbing nodes.
Growth Catalysts
- Zero-trust mandates:NIST architecture guidelines in the United States are compelling federal contractors to replace perimeter-based security with identity-verified edge access controls.
- Bot-driven fraud:Financial services firms are deploying advanced mitigation layers as automated credential stuffing attacks surge against payment APIs.
- Edge server densification:Hyperscalers are expanding physical footprint within 50 kilometers of major metropolitan clusters to meet sub-20 millisecond latency requirements.
Market Restraints
- Specialized engineering scarcity:Talent capable of tuning WAF rules for low-latency environments commands premium compensation, compressing vendor margins.
- Certificate authority concentration:Dependence on a limited pool of root certificate providers creates systemic vulnerability for TLS termination at scale.
- Cross-border data friction:Divergent sovereignty requirements between the United States and European Union fragment unified security policy deployment.
Strategic Opportunities
- Sovereign cloud carve-outs:Regulated European industries are procuring EU-operated edge nodes to satisfy NIS2 Directive resilience mandates without US jurisdictional exposure.
- Observability convergence:Security analytics platforms that ingest telemetry from CDN, identity, and endpoint sources are capturing budget from standalone monitoring tools.
- Critical infrastructure designation:Communications infrastructure reclassification under FCC resilience standards is unlocking federal co-funding for operator hardening investments.
Industry Challenges
- Multi-cloud policy orchestration:Enterprises operating across AWS, Azure, and Google Cloud struggle to maintain consistent WAF rule sets without configuration drift.
- ISO 27001 audit compression:Certification timelines for edge facilities are extending as assessors lack standardized frameworks for distributed infrastructure validation.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | CDN Security Market |
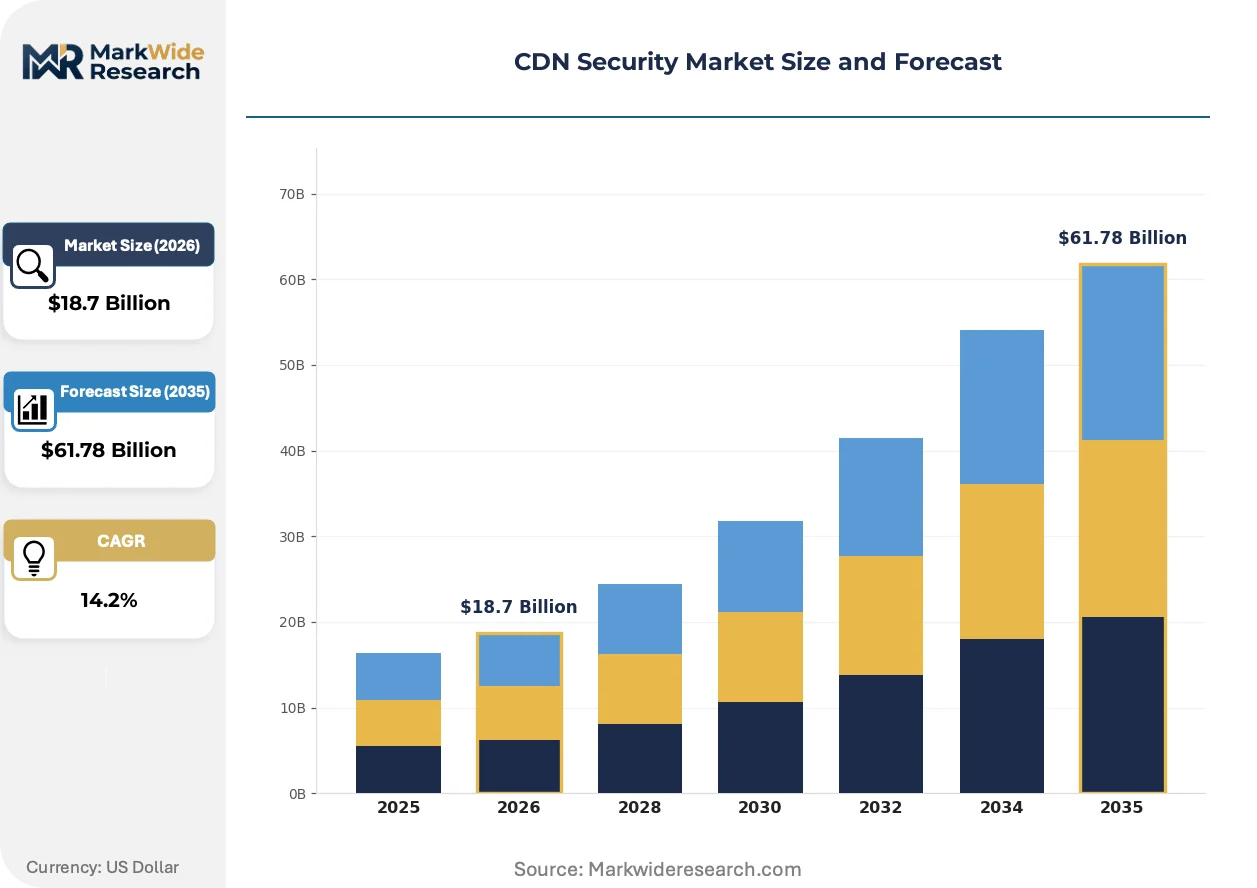
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $61.78 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Web Application Firewall, DDoS Protection, Bot Management, CDN Security Analytics Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, On-premises End User: Media & Entertainment, E-commerce, BFSI, Government Integration Level: API Integration, SDK Integration, Custom Integration, Out-of-the-box Integration |
| Companies Covered | Akamai Technologies Inc., Cloudflare Inc., Amazon Web Services Inc., Fastly Inc., Google LLC, Microsoft Corp., Imperva Inc., Edgio Inc., Radware Ltd., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
CDN Security Market Emerging Trajectories
Monolithic security stacks are fragmenting into composable components as buyers demand modular integration with existing cloud-native toolchains.
Web application firewall architectures are decomposing from hardware appliances into software-defined functions deployable as sidecar containers. Financial services institutions are piloting this shift for payment card industry compliance workloads. The technology is decomposing vendor lock-in by enabling rule portability across cloud provider edge networks.
EU AI Act risk classification requirements are mandating algorithmic transparency for automated threat detection systems. CDN operators must now document decision logic for bot scoring models deployed in European jurisdictions. Financial services and critical infrastructure providers face the steepest compliance burden as their traffic volumes trigger high-risk system designations.
Enterprise buyers are consolidating vendor relationships around platforms that bundle DDoS mitigation with identity-aware proxy functions. Media and entertainment firms are displacing standalone CDN contracts with integrated security-performance suites. This concentration is most pronounced in the United States where hyperscaler marketplaces simplify procurement through committed spend agreements.
CDN Security Market Segmentation
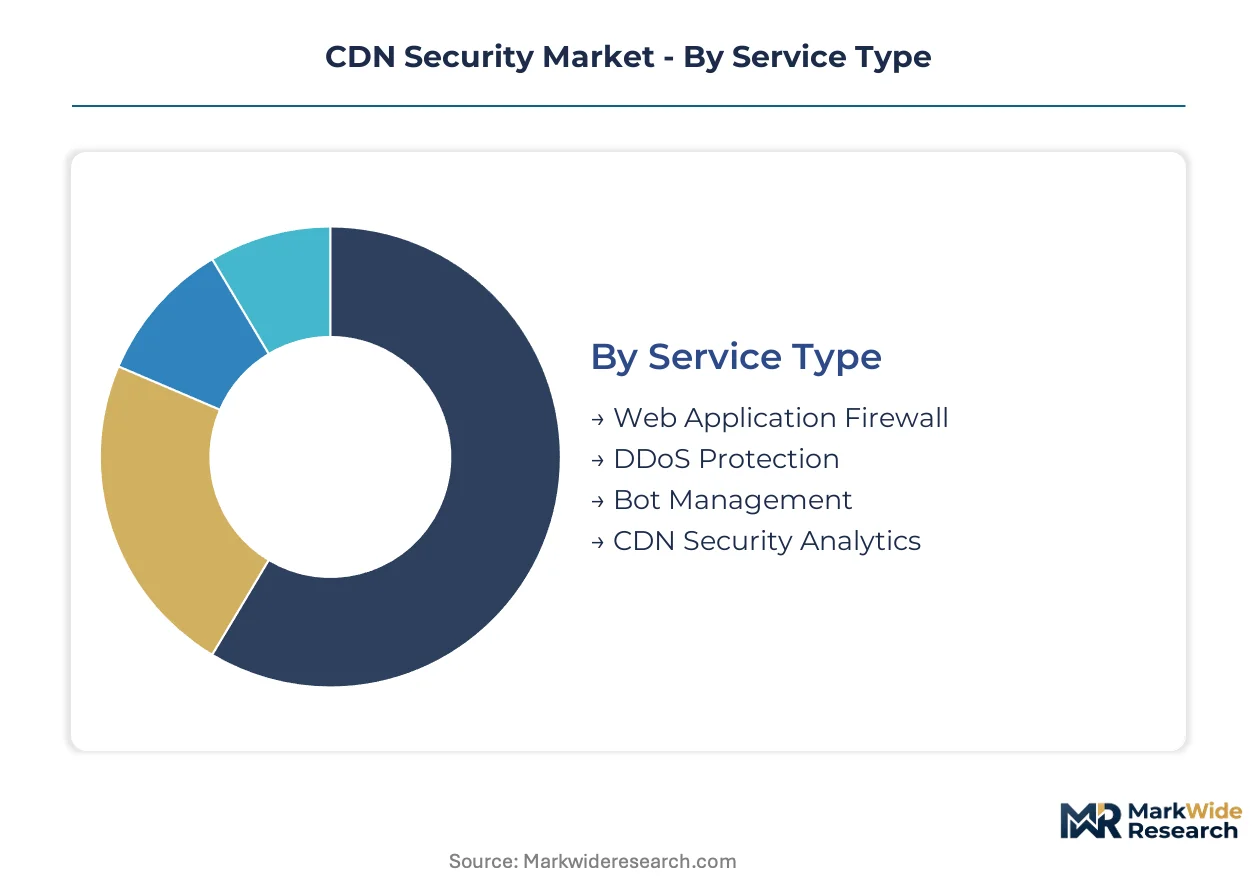
CDN security procurement patterns diverge sharply across service architectures and deployment topologies. Buyers prioritize latency-performance trade-offs and regulatory jurisdiction when selecting segment combinations. Vendor pricing and contract structures vary substantially across these boundaries.
Service Type:
DDoS Protection and Web Application Firewall face intensifying substitution pressure from integrated cloud-native security suites bundling multiple functions. Bot Management and CDN Security Analytics maintain stronger differentiation through specialized algorithmic requirements.
- DDoS Protection:Distributed traffic scrubbing operates across geographically dispersed edge nodes to absorb volumetric attacks before origin saturation. Financial services firms in the United States deploy this layer most aggressively as API traffic volumes surge against payment infrastructure.
- Web Application Firewall:Rule-based request inspection filters malicious payloads at sub-50 millisecond latency thresholds to preserve application performance. E-commerce platforms concentrate procurement here as automated credential stuffing attacks escalate against checkout flows.
- Bot Management:Behavioral scoring distinguishes automated traffic from legitimate sessions using device fingerprinting and request pattern analysis.
- CDN Security Analytics:Telemetry aggregation from edge nodes enables real-time threat visibility and compliance documentation for regulated industries.
DDoS Protection retains volume leadership; CDN Security Analytics holds the steepest expansion curve.
Deployment Model:
Cost tier stratification separates hyperscaler consumption from sovereign infrastructure investments. Public Cloud minimizes operational overhead while Hybrid Cloud and Private Cloud extract premiums for data residency controls.
- Public Cloud:Shared edge infrastructure delivers elastic capacity scaling without capital deployment. Media and entertainment workloads default to this model for cost efficiency during traffic spikes.
- Hybrid Cloud:Split architectures route sensitive traffic through sovereign nodes while bursting non-critical loads to hyperscaler edges. European BFSI institutions pilot this configuration to satisfy NIS2 Directive mandates without full infrastructure displacement.
- Private Cloud:Dedicated edge deployments satisfy stringent data sovereignty requirements in government and defense applications.
- On-premises:Captive hardware installations persist in legacy financial institutions with mainframe-dependent core systems.
Public Cloud dominates transaction volume; Hybrid Cloud is gaining share fastest among regulated verticals.
End User:
Application-specific latency requirements and compliance exposure shape procurement archetypes. Media streaming tolerates higher risk thresholds than financial transaction processing.
- BFSI:Payment API protection and fraud prevention drive multi-layer edge deployments with sub-20 millisecond latency requirements. United States institutions lead procurement intensity following federal zero-trust mandates.
- Media & Entertainment:Content delivery optimization prioritizes bandwidth efficiency over deep packet inspection. Streaming platforms concentrate in Public Cloud deployments for global distribution scale.
- E-commerce:Checkout flow protection and inventory bot mitigation dominate security spending.
- Government:Critical infrastructure designation under FCC resilience standards unlocks federal co-funding for hardened edge networks.
BFSI commands premium pricing; Government vertical is expanding most quickly through infrastructure reclassification.
Integration Level:
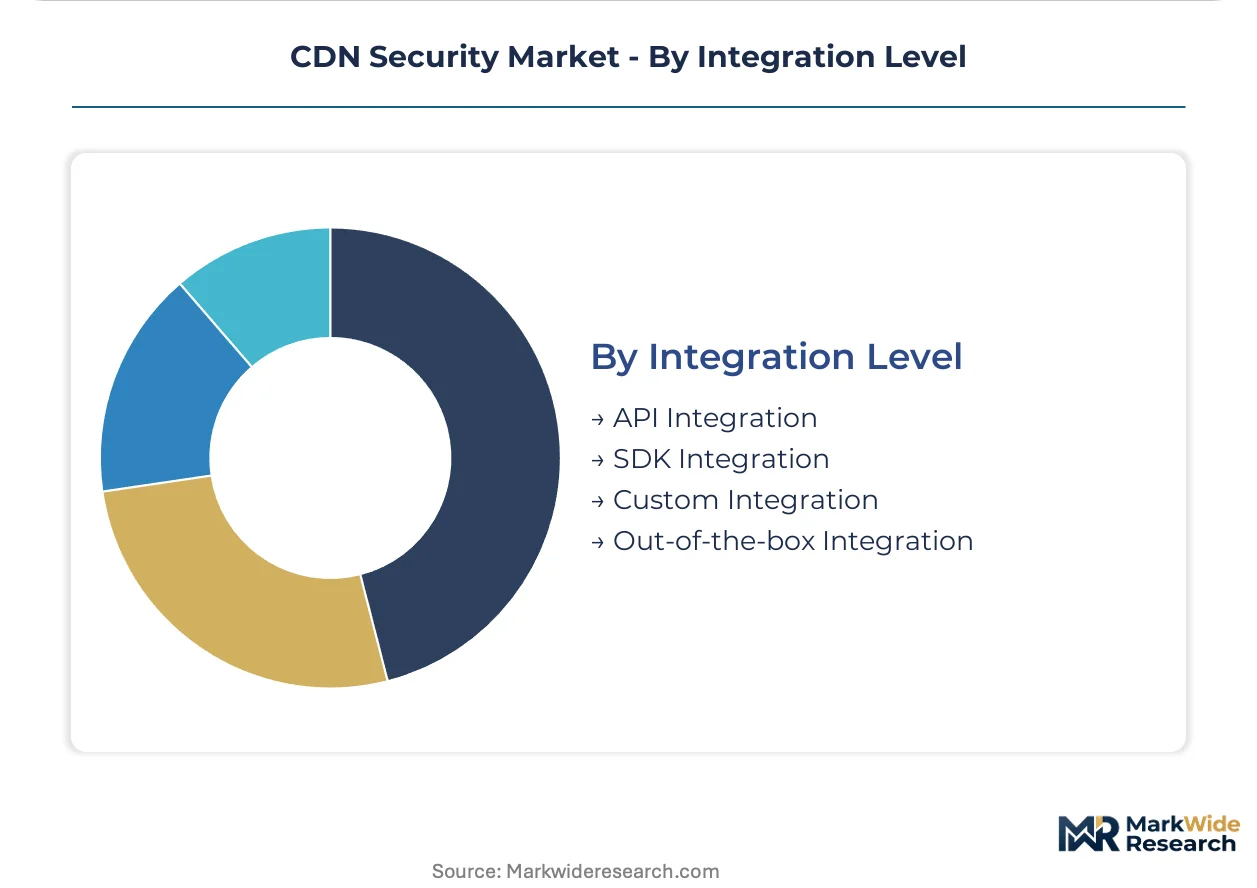
Technical maturity and in-house engineering capacity determine integration pathway selection. Developer-centric organizations favor API and SDK routes while legacy enterprises require pre-configured deployments.
- API Integration:Programmatic configuration enables dynamic rule deployment across multi-cloud edge networks. Technology-forward financial services institutions standardize on this approach for CI/CD pipeline integration.
- SDK Integration:Embedded client-side libraries provide granular device telemetry for bot scoring models. Mobile-first e-commerce platforms deploy this layer for native application protection.
- Custom Integration:Bespoke middleware development connects proprietary identity systems to edge security policies.
- Out-of-the-box Integration:Pre-configured connectors accelerate deployment for organizations lacking specialized security engineering.
API Integration leads adoption among cloud-native enterprises; SDK Integration is climbing fastest with mobile application proliferation.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Hyperscaler edge infrastructure concentrates most densely across five national markets where latency requirements and regulatory mandates intersect. Each geography presents distinct procurement patterns shaped by local compliance frameworks and industrial clustering.
United States
Federal zero-trust mandates and FCC resilience standards are accelerating enterprise refresh cycles across financial services and government verticals. NIST architecture guidelines compel contractors to replace perimeter-based security with identity-verified edge access controls. Northern Virginia's data center corridor hosts the densest concentration of scrubbing nodes, with hyperscalers expanding physical footprint within 50 kilometers of major metropolitan clusters.
Germany
EU AI Act risk classification requirements and NIS2 Directive resilience mandates are tightening procurement specifications for critical digital infrastructure providers. BSI federal cybersecurity guidance shapes vendor certification requirements for BFSI institutions. Frankfurt's financial hub drives sovereign cloud carve-outs as regulated industries seek EU-operated edge nodes without US jurisdictional exposure.
United Kingdom
Financial Conduct Authority operational resilience rules and Bank of England cyber stress testing protocols are forcing edge infrastructure upgrades across payment systems. NCSC cloud security principles influence vendor selection criteria for government contracts. London's fintech corridor concentrates demand for sub-20 millisecond latency protection against API-targeted credential stuffing attacks.
Japan
METI critical infrastructure protection guidelines and Financial Services Agency cybersecurity regulations are mandating distributed scrubbing architectures for banking and securities firms. JIS standards for information security management systems shape certification requirements. Tokyo-Osaka corridor enterprises are piloting hybrid cloud configurations to balance latency performance against data sovereignty controls.
Singapore
Monetary Authority of Singapore technology risk management guidelines and IMDA data protection trustmark requirements are driving multi-layer edge deployments across ASEAN financial hubs. Cyber Security Agency of Singapore national cybersecurity strategy unlocks public-private co-funding for operator hardening investments. Marina Bay's digital infrastructure cluster attracts hyperscaler expansion targeting sub-50 millisecond latency thresholds for regional payment networks.
CDN Security Market Vendor Landscape
Concentration sits with hyperscale cloud providers and specialized edge security platforms that command divergent procurement archetypes. The vendor base stratifies across three tiers: massive infrastructure operators leveraging carrier relationships, developer-centric platforms emphasizing feature velocity, and cloud-native entrants bundling security into consumption contracts. Strategic moves center on sovereign cloud carve-outs to satisfy data residency mandates and observability convergence capturing budget from standalone monitoring tools.
Within the infrastructure-heavy tier, Akamai Technologies Inc. anchors positioning through edge server footprint depth. Cloudflare Inc. exemplifies the developer-centric platform archetype with rapid deployment capabilities. Amazon Web Services Inc. occupies the bundling position within broader cloud consumption frameworks. These three representations capture the essential competitive vectors—physical presence, engineering accessibility, and ecosystem lock-in—that define procurement decision frameworks across regulated verticals.
| Leading Market Players |
|---|
| Akamai Technologies Inc. |
| Cloudflare Inc. |
| Amazon Web Services Inc. |
| Fastly Inc. |
| Google LLC |
| Microsoft Corp. |
| Imperva Inc. |
| Edgio Inc. |
| Radware Ltd. |
| Others |
Supply Flow & Price Mechanics
ISO 27001 certification gates both vendor qualification and price differentiation in CDN security procurement, forcing suppliers to absorb audit costs while buyers tier contracts around compliance tier. NIS2 Directive mandates in Europe compound this dynamic by requiring sovereign infrastructure investments that extract premiums from regulated BFSI institutions.
Pricing Analysis
NIST zero-trust architecture guidelines dictate the pricing tier structure across federal contractor segments in the United States, separating certified edge deployments from standard commercial offerings. Three-tier pricing structure across premium, standard, and economy levels reflects latency-performance guarantees and data residency controls. Cost compression in the economy tier is intensifying because hyperscaler bundling locks in volume discounts. Government verticals exhibit lowest price sensitivity; media and entertainment buyers concentrate procurement around standard tier elasticity.
Supply Chain Analysis
Port congestion across Asia-Pacific trade lanes elevates inbound logistics costs for edge server hardware deployments, compressing deployment timelines for scrubbing node expansion. Supply concentrates in Taiwan for semiconductor components, China for server assembly, and the United States for final edge facility integration. Raw material dependencies span advanced processors, TLS acceleration modules, and fiber optic interconnects. Single-source vulnerability sits with concentrated root certificate authority providers. Distribution runs through hyperscaler marketplace channels and direct enterprise sales teams.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Integrated cloud-native security suites threaten standalone CDN security contracts, forcing incumbents to defend substitution through platform bundling and developer ecosystem lock-in.
For Market Incumbents: Secure sovereign cloud carve-out capabilities to satisfy NIS2 Directive data residency mandates without hyperscaler jurisdictional exposure. Anchor positioning through captive edge server footprint expansion within 50 kilometers of metropolitan financial hubs. Certification investment in ISO 27001 and IEC 62443 functions as the priority defensive lever against cloud-native entrants. For New Entrants and Emerging Players: Lead with observability convergence plays that aggregate telemetry from distributed edge nodes into unified security analytics platforms. White-space concentrates in EU-operated sovereign nodes for regulated European BFSI institutions. SDK integration pathways for mobile-first e-commerce platforms offer the most penetrable go-to-market angle. For Investors and Strategic Acquirers: Capital-intensity ratios are inflecting upward across hybrid cloud deployment configurations as sovereign infrastructure requirements multiply facility costs. Long-term viability favors platforms with demonstrated multi-cloud orchestration capabilities and existing carrier relationships. Acquisition target archetype: developer-centric platforms with rapid feature velocity and established API integration ecosystems. Signal to watch: hyperscaler marketplace committed spend agreements displacing standalone procurement.| Strategic Initiative | Industry Significance |
|---|---|
| Sovereign Cloud Carve-Out | EU AI Act compliance unlocks regulated BFSI procurement without US jurisdictional exposure. |
| Observability Platform Integration | Telemetry aggregation from CDN, identity, and endpoint sources captures standalone monitoring budgets. |
| Edge Server Densification | Sub-20 millisecond latency requirements force physical footprint expansion near metropolitan clusters. |
| API-First Developer Ecosystem | Programmatic configuration enables CI/CD pipeline integration for cloud-native financial services. |
| Multi-Cloud Policy Orchestration | Consistent WAF rule deployment across AWS, Azure, and Google Cloud reduces configuration drift. |
Methodological Framework
Cross-validation between primary stakeholder interviews and secondary regulatory filings anchors the qualitative findings in this analysis. Primary fieldwork engaged CDN platform engineers, enterprise IT procurement officers, federal cybersecurity contractors, and carrier network architects. Secondary validation drew from FCC resilience standards documentation, NIST zero-trust architecture guidelines, EU AI Act regulatory texts, and hyperscaler capex disclosures. Bottom-up segment sizing triangulated against top-down market envelope estimates.
Sensitivity analysis tested forecast outputs across alternative adoption scenarios for hybrid cloud deployment and sovereign infrastructure investment. Segmentation dimensions modeled include service type, deployment topology, end-user vertical, and integration complexity tier. CAGRs derived from fitted growth curves applied to base-year estimates, with trajectory adjustments reflecting regulatory mandate timing and edge server densification capex cycles. Bot management algorithm development costs and TLS certificate authority concentration risk factored as industry-specific forecast inputs.
Forecasts assume regulatory continuity in NIST zero-trust mandates, EU AI Act risk classifications, and FCC critical infrastructure designations; material policy shifts would require re-modeling. Edge latency requirements below 10 milliseconds or sovereign cloud fragmentation beyond current NIS2 Directive scope would force forecast revision. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Bangladesh Cybersecurity Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
Open RAN Security Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Global Deep Packet Inspection (DPI) Market
Cybersecurity
Greece Cybersecurity Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Middle East Cybersecurity Market
Cybersecurity
Romania Cybersecurity Market
Cybersecurity
Cybersecurity in Gaming Market
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Global Quantum Cryptography Solutions Market
Cybersecurity
Thailand Cybersecurity Market
Cybersecurity
Network Traffic Analysis Solutions Market