
 Cloud Encryption Software Market | 2026-2036
Cloud Encryption Software Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Encryption Software Market Analysis
North America is reconfiguring cloud security infrastructure as hyperscaler capacity expands across Virginia, Oregon, and Quebec. Microsoft leverages its Azure Purview lineage to anchor enterprise key management services. Thales competes through hardware security module integration with public cloud APIs. Sophos differentiates by embedding encryption within managed detection and response workflows.
Cloud encryption software applies cryptographic algorithms to data at rest, in transit, and in use within distributed computing environments, typically employing AES-256, RSA-4096, or post-quantum lattice-based schemes to prevent unauthorized access without valid decryption keys. Its primary purpose is to maintain confidentiality and integrity of sensitive information processed across third-party infrastructure. Hybrid cloud deployments are generating the fastest growth in key management demand as organizations straddle on-premises and public environments. Application encryption within financial services end users commands premium pricing due to real-time transaction protection requirements. PCI DSS compliance standards are hardening segmentation boundaries between retail payment systems and cloud storage layers.
FDA guidance on cloud-based clinical data systems, HIPAA security rules for healthcare encryption, and GDPR Article 32 mandates on pseudonymization are collectively raising baseline cryptographic requirements across regulated industries. The SEC's cybersecurity disclosure rules are pushing publicly traded firms toward auditable encryption key lifecycle documentation. Stakeholders must monitor post-quantum cryptography standardization by NIST and prepare migration timelines before cryptanalytically relevant quantum systems emerge.
Market Dynamics
Post-quantum cryptography migration is forcing premature infrastructure refresh cycles as enterprises confront harvest-now-decrypt-later threats against RSA and elliptic curve implementations. NIST standardization timelines are compressing procurement decisions for encryption vendors and their financial services clients.
Growth Catalysts
- EU AI Act data residency mandates:Article 50 requirements for high-risk AI systems are mandating encryption-at-rest for training datasets, driving German automotive and French healthcare cloud migrations.
- Financial services real-time transaction volumes:Open banking APIs and instant payment rails in the UK, Singapore, and Brazil are requiring application-layer encryption with sub-10-millisecond latency tolerances.
- Homomorphic encryption maturation:Partially homomorphic schemes for privacy-preserving analytics are enabling encrypted computation on multi-tenant cloud infrastructure without decryption exposure.
Market Restraints
- Hardware security module supply concentration:FIPS 140-2 Level 3 certified HSM fabrication depends on TSMC advanced packaging nodes concentrated in Taiwan, creating geopolitical supply vulnerability.
- Key management interoperability friction:Proprietary key formats across AWS KMS, Azure Key Vault, and Google Cloud HSM force redundant key lifecycle tooling and compliance documentation overhead.
- Quantum-resistant algorithm performance penalties:CRYSTALS-Kyber and CRYSTALS-Dilithium implementations impose 40-60% computational overhead versus classical RSA-4096, straining edge device battery and thermal budgets.
Strategic Opportunities
- Confidential computing hardware integration:AMD SEV-SNP and Intel TDX attestation capabilities are converging with encryption software to create verifiable zero-trust execution environments for regulated workloads.
- India data localization enforcement:RBI and CERT-In directives for domestic data storage are creating demand for sovereign cloud encryption with local key custody and indigenous cryptographic modules.
- Healthcare data monetization frameworks:HIPAA-compliant de-identification pipelines combined with synthetic data generation are opening encrypted analytics markets for pharmaceutical real-world evidence contracts.
Industry Challenges
- Post-quantum cryptographic engineering talent scarcity:Lattice-based implementation expertise resides with fewer than 200 qualified practitioners globally, constraining enterprise migration velocity and vendor delivery capacity.
- Cross-border key escrow jurisdictional conflicts:CLOUD Act US data access demands conflict with GDPR Article 48 transfer prohibitions, forcing dual-key architectures that fragment security postures.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Encryption Software Market |
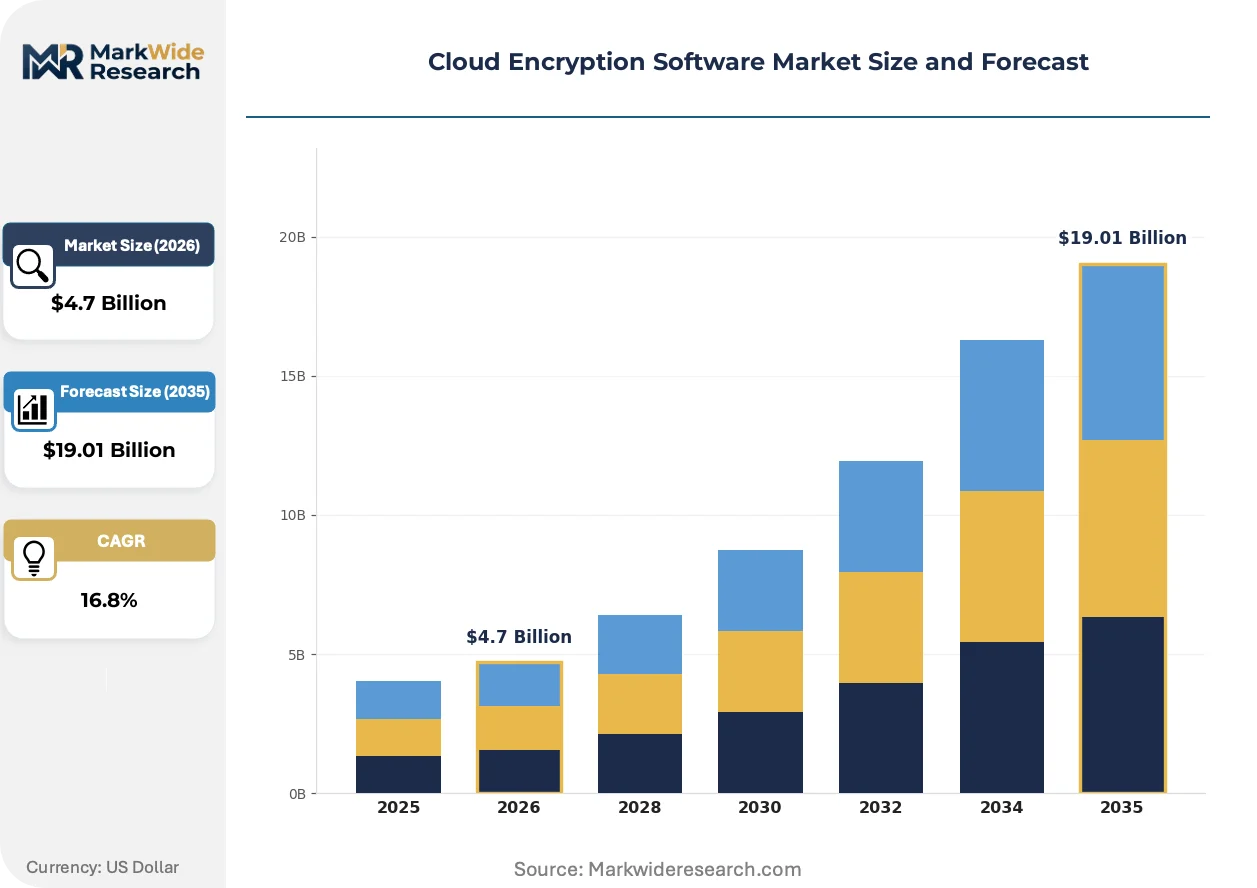
| Market Size in 2026 | $4.7 Billion |
| Market Size in 2035 | $19.01 Billion |
| CAGR (2026 – 2036) | 16.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud Solution Type: Data Encryption, Application Encryption, Key Management, Access Control End User: Financial Services, Healthcare, Government, Retail Compliance Standard: GDPR, HIPAA, PCI DSS, ISO 27001 |
| Companies Covered | Microsoft, Amazon, IBM, Google, Oracle, Thales, McAfee, Sophos, Cisco, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Encryption Software Market Emerging Trajectories
Encryption software architectures are bifurcating between centralized key management platforms and embedded cryptographic modules, with hardware-rooted trust anchoring both paths. This divergence reflects competing enterprise priorities: operational simplicity versus attack surface minimization.
Confidential computing is digitizing workload isolation guarantees by extending encryption from data-at-rest to data-in-use through processor-enforced memory encryption. Financial services firms in London and Singapore are piloting these environments for anti-money-laundering model training on co-mingled datasets. The technology is digitizing compliance documentation by replacing manual audit trails with attestation-verifiable execution proofs.
GDPR Article 32 pseudonymization mandates are hardening segmentation requirements between data controllers and processors, forcing encryption key custody restructuring across EU cloud supply chains. German industrial manufacturers are responding by deploying customer-held key models that prevent cloud providers from accessing decrypted production telemetry. This regulatory pressure is accelerating demand for external key management services with EU-sovereign infrastructure footprints.
Consumption-based licensing for encryption software is displacing perpetual seat models as hyperscaler marketplaces become primary procurement channels. Mid-market enterprises in Australia and South Korea are purchasing through AWS Marketplace and Azure Marketplace rather than direct vendor negotiation. This channel shift is compressing pricing transparency and bundling encryption with adjacent security services into integrated spend commitments.
Cloud Encryption Software Market Segmentation
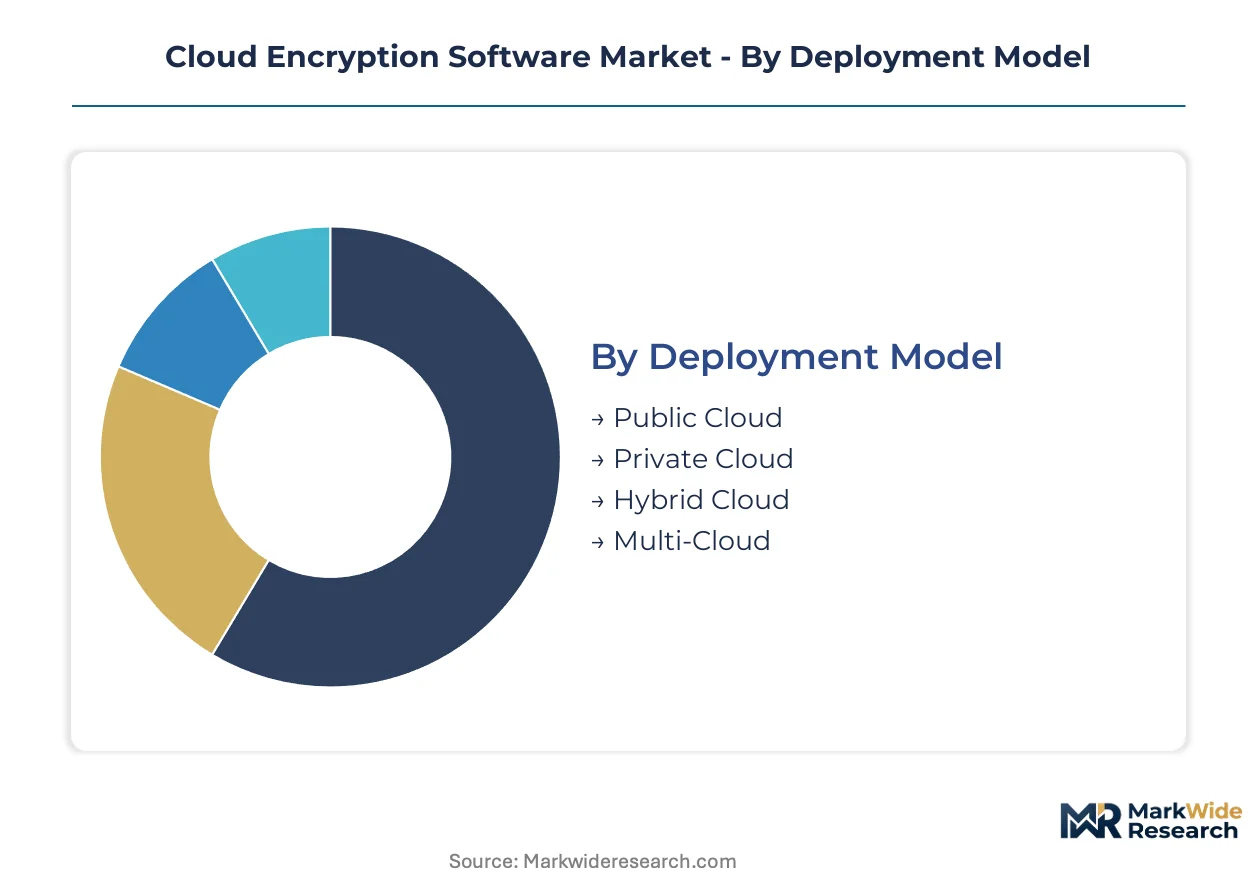
Cloud encryption software segmentation reveals how procurement priorities diverge across infrastructure choices, regulatory exposure, and operational maturity. Understanding these fault lines clarifies where vendors must differentiate versus where standardization prevails.
Deployment Model:
Cost tier stratification across deployment models determines capital allocation patterns and vendor engagement intensity.
- Public Cloud:Native encryption services integrated with AWS KMS, Azure Key Vault, and Google Cloud HSM dominate procurement for cloud-native enterprises. Demand concentrates among mid-market SaaS providers in Singapore and Sydney seeking PCI DSS compliance without HSM capital expenditure.
- Private Cloud:Dedicated infrastructure with customer-controlled key custody serves defense contractors and sovereign data requirements. German automotive suppliers and French healthcare networks prioritize this model under GDPR Article 32 pseudonymization mandates.
- Hybrid Cloud:Unified key management spanning on-premises HSMs and public cloud APIs addresses workload portability requirements. Financial services firms in London and Toronto deploy this architecture for trading system redundancy.
- Multi-Cloud:Vendor-agnostic encryption layers abstracting AWS, Azure, and GCP key services reduce lock-in risk. Enterprise procurement teams in São Paulo and Mumbai favor this approach for disaster recovery flexibility.
Public Cloud commands the established base. The steepest expansion runs through Hybrid Cloud.
Solution Type:
Application context shapes which encryption layer absorbs compliance scrutiny and capital investment.
- Data Encryption:AES-256 implementations for object storage, databases, and file systems constitute the volume foundation. Retail payment processors in Brazil and Australia standardize on this layer for PCI DSS segmentation between cardholder data and cloud infrastructure.
- Application Encryption:Field-level and columnar encryption embedded within software code protects specific data elements. Real-time transaction systems in UK open banking and Singapore instant payment rails require sub-10-millisecond latency tolerances here.
- Key Management:Lifecycle orchestration for generation, rotation, and revocation spans HSMs, software modules, and cloud-native services. Centralized platforms attract governance-focused enterprises in Frankfurt and Zurich consolidating fragmented key silos.
- Access Control:Policy enforcement linking encryption keys to identity and context attributes extends zero-trust architectures. Healthcare organizations in Boston and Copenhagen deploy this for HIPAA-compliant research data sharing.
Data Encryption commands the established base. Application Encryption is gaining share fastest.
End User:
Customer type determines pricing tolerance, certification requirements, and sales cycle duration.
- Financial Services:Real-time payment protection and anti-money-laundering analytics drive premium pricing. Sub-10-millisecond latency requirements for UK and Singapore instant payment rails command application-layer encryption investments.
- Healthcare:HIPAA security rules and FDA guidance on cloud-based clinical data elevate cryptographic baselines. Academic medical centers in Baltimore and Rotterdam prioritize encrypted analytics for pharmaceutical real-world evidence contracts.
- Government:FIPS 140-2 Level 3 certification and sovereign key custody dominate procurement criteria. Defense and intelligence agencies in Virginia and Canberra mandate hardware-rooted trust with domestic fabrication provenance.
- Retail:PCI DSS compliance hardens segmentation between payment systems and cloud storage. E-commerce platforms in São Paulo and Jakarta balance encryption overhead against checkout conversion rates.
Financial Services commands the established base. Healthcare shows the steepest expansion trajectory.
Compliance Standard:
Regulatory geography dictates encryption architecture choices and vendor qualification pathways.
- GDPR:Article 32 mandates on pseudonymization and Article 50 EU AI Act requirements reshape EU cloud supply chains. German industrial manufacturers deploy customer-held key models preventing provider access to production telemetry.
- HIPAA:Security Rule encryption specifications and FDA guidance on clinical data systems raise healthcare baselines. US health systems in Nashville and Cleveland face SEC cybersecurity disclosure rules pushing auditable key lifecycle documentation.
- PCI DSS:Segmentation boundaries between retail payment systems and cloud storage layers harden with each standard revision. Brazilian and Australian payment processors prioritize this for cross-border transaction authorization.
- ISO 27001:Management system certification provides framework flexibility across jurisdictions. Professional services firms in Dubai and Johannesburg adopt this for client trust differentiation without geography-specific mandates.
PCI DSS commands the established base. GDPR shows the steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Hyperscaler capacity expansion concentrates in Virginia, Oregon, and Quebec, while regulatory pressure from GDPR and the EU AI Act redistributes compliance spending toward Germany and France. Enterprise procurement patterns diverge between North American cloud-native adoption and European sovereign data requirements.
United States
Financial services institutions in New York and Chicago drive demand for sub-10-millisecond application-layer encryption on instant payment rails. SEC cybersecurity disclosure rules push publicly traded firms toward auditable key lifecycle documentation. Defense contractors in Northern Virginia mandate FIPS 140-2 Level 3 hardware security modules with domestic fabrication provenance.
Germany
Industrial cloud migration accelerates spending on customer-held key models that prevent providers from accessing production telemetry. GDPR Article 32 pseudonymization mandates reshape automotive supplier relationships with cloud processors. Manufacturing clusters in Stuttgart and Munich deploy sovereign encryption infrastructure for connected vehicle data streams.
United Kingdom
Open banking APIs require real-time transaction protection with strict latency tolerances. The Financial Conduct Authority supervises encryption standards for payment service providers. London-based fintechs pilot confidential computing environments for anti-money-laundering model training on co-mingled datasets.
Singapore
Instant payment rails and cross-border transaction authorization drive premium pricing for application encryption. The Monetary Authority of Singapore mandates robust cryptographic controls for digital banking licenses. Financial services firms in the Marina Bay district deploy hybrid cloud architectures for trading system redundancy.
India
RBI and CERT-In directives for domestic data storage create demand for sovereign cloud encryption with local key custody. Bengaluru and Hyderabad technology corridors attract indigenous cryptographic module development. Pharmaceutical real-world evidence contracts in Mumbai require HIPAA-compliant de-identification pipelines.
Cloud Encryption Software Market Vendor Landscape
Hyperscale cloud providers and specialized security vendors split the market along infrastructure control boundaries. Microsoft, Amazon, and Google anchor the integrated platform tier, while Thales and Sophos occupy the independent security layer. Consolidation pressure intensifies as enterprise procurement shifts toward hyperscaler marketplaces. Strategic moves concentrate on hardware security module integration and confidential computing partnerships.
Within the independent security tier, Thales exemplifies hardware-rooted trust anchoring through hardware security module fabrication, while Sophos occupies a position embedding encryption within broader managed detection and response workflows. Microsoft represents the platform-integrated archetype, leveraging Azure Purview lineage to anchor enterprise key management services alongside its cloud infrastructure stack.
| Leading Market Players |
|---|
| Microsoft |
| Amazon |
| IBM |
| Oracle |
| Thales |
| McAfee |
| Sophos |
| Cisco |
| Others |
Supply Flow & Price Mechanics
Overcapacity in Taiwan's FIPS 140-2 Level 3 HSM fabrication nodes is compressing hardware security module pricing while simultaneously constraining supplier willingness to expand advanced packaging capacity, creating asymmetric pricing power that favors buyers for standardized components but penalizes procurement for certified sovereign-grade modules.
Pricing Analysis
PCI DSS compliance dictates the pricing tier structure across cloud encryption software, separating FIPS 140-2 Level 3 certified deployments from standard AES-256 implementations. Three-tier pricing structure across premium, standard, and economy levels reflects certification grade and key custody model, with customer-held key architectures commanding substantial premiums over cloud-native alternatives. Cost compression in mid-market SaaS tiers is intensifying because hyperscaler marketplace bundling obscures standalone encryption value. Financial services institutions exhibit the lowest price sensitivity due to sub-10-millisecond latency requirements, while retail payment processors in emerging markets face acute budget constraints.
Supply Chain Analysis
Geopolitical exposure between Taiwan and mainland China dominates supply chain risk assessment for hardware-rooted encryption trust anchors. Taiwan, South Korea, and the United States concentrate FIPS-certified HSM fabrication and advanced cryptographic processor design. Raw material dependencies include silicon wafers from TSMC, rare earth elements for magnetic shielding, and specialized substrates for tamper-resistant packaging. Single-source vulnerability in TSMC's CoWoS advanced packaging creates chokepoint risk for Level 3 certification compliance. Distribution runs through hyperscaler marketplaces, direct enterprise sales, and systems integrator channels serving regulated industries.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Native encryption services embedded within hyperscaler platforms threaten standalone encryption vendors with functional substitution, forcing incumbents to articulate differentiation around sovereign key custody and cross-cloud interoperability or face margin erosion.
For Market Incumbents: Insulate application-layer encryption capabilities from commoditization by deepening hardware security module integration with confidential computing attestation services. Prioritize certification investment in EU sovereign infrastructure footprints to capture GDPR Article 32 restructuring demand. Defend against homomorphic encryption startups by embedding privacy-preserving analytics within existing key management workflows. For New Entrants and Emerging Players: Establish a beachhead in India's sovereign cloud encryption segment where RBI data localization mandates create protected demand with limited incumbent presence. Target pharmaceutical real-world evidence contracts in Mumbai and Bengaluru requiring HIPAA-compliant de-identification pipelines. Pursue channel partnerships with indigenous cryptographic module developers rather than direct hyperscaler competition. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among external key management services with EU-sovereign infrastructure footprints, suggesting durable cash flow quality for platforms serving German automotive and French healthcare migrations. Long-term viability hinges on post-quantum cryptography migration readiness and lattice-based implementation talent acquisition. Monitor NIST standardization finalization as the inflection signal for enterprise procurement acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Partnership | AMD SEV-SNP and Intel TDX integration creates verifiable zero-trust execution environments for regulated financial workloads. |
| Post-Quantum Cryptography Migration | CRYSTALS-Kyber implementation ahead of NIST finalization captures harvest-now-decrypt-later threat mitigation spending. |
| EU Sovereign Infrastructure Expansion | GDPR Article 32 pseudonymization mandates in Germany and France drive customer-held key model adoption. |
| Hyperscaler Marketplace Integration | AWS Marketplace and Azure Marketplace presence captures mid-market procurement shifting away from direct vendor negotiation. |
| Homomorphic Encryption Productization | Partially homomorphic schemes for privacy-preserving analytics unlock pharmaceutical real-world evidence contract opportunities. |
Methodological Framework
Two parallel data streams informed the analysis: structured conversations with CISOs, cloud architects, and compliance officers at financial services and healthcare institutions, alongside secondary validation through SEC cybersecurity disclosure filings, hyperscaler capex and service revenue disclosures, and NIST post-quantum cryptography standardization documentation. Primary engagement spanned encryption software vendors, hardware security module manufacturers, and systems integrators deploying multi-cloud key management solutions. Bottom-up sizing from individual deployment characteristics was triangulated against top-down market aggregation from regulatory compliance spending estimates.
Forecast inputs across the analysis window incorporated deployment model adoption curves, compliance standard enforcement timelines, and hardware security module supply constraints. Segmentation dimensions modeled include deployment architecture, solution type, end-user industry, and geographic regulatory cluster. CAGRs were derived from regression analysis against historical cloud infrastructure spending correlation patterns. Industry-specific forecast inputs included instant payment rail transaction volume growth and EU AI Act Article 50 implementation schedules.
Stress conditions across TSMC fabrication capacity allocation, NIST post-quantum standardization delays, and CLOUD Act-GDPR jurisdictional conflict escalation were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions regarding regulatory enforcement intensity and enterprise migration velocity. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Certification Authority Market
Security Software
Data Masking Technology Market
Security Software
Global Software-Defined Security Market
Security Software
Vsaas Market
Security Software
Global Network Encryption Market
Security Software
Security Software for Consumers Market
Security Software
Europe User Provisioning Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Global Digital Identity Solutions Market
Security Software
Japan Mobile Biometrics Market
Security Software
Facial Recognition Market
Security Software
Endpoint Security Solutions Market
Security Software
AI Security Platforms Market
Security Software
Employee Surveillance and Monitoring Software Market
Security Software
Bot Mitigation Market
Security Software
Global Log Management Market