
 Global Bug Bounty Platforms Market | 2026-2036
Global Bug Bounty Platforms Market Size, Share, and Industry Trends Forecast 2026-2036
Global Bug Bounty Platforms Market Foresight
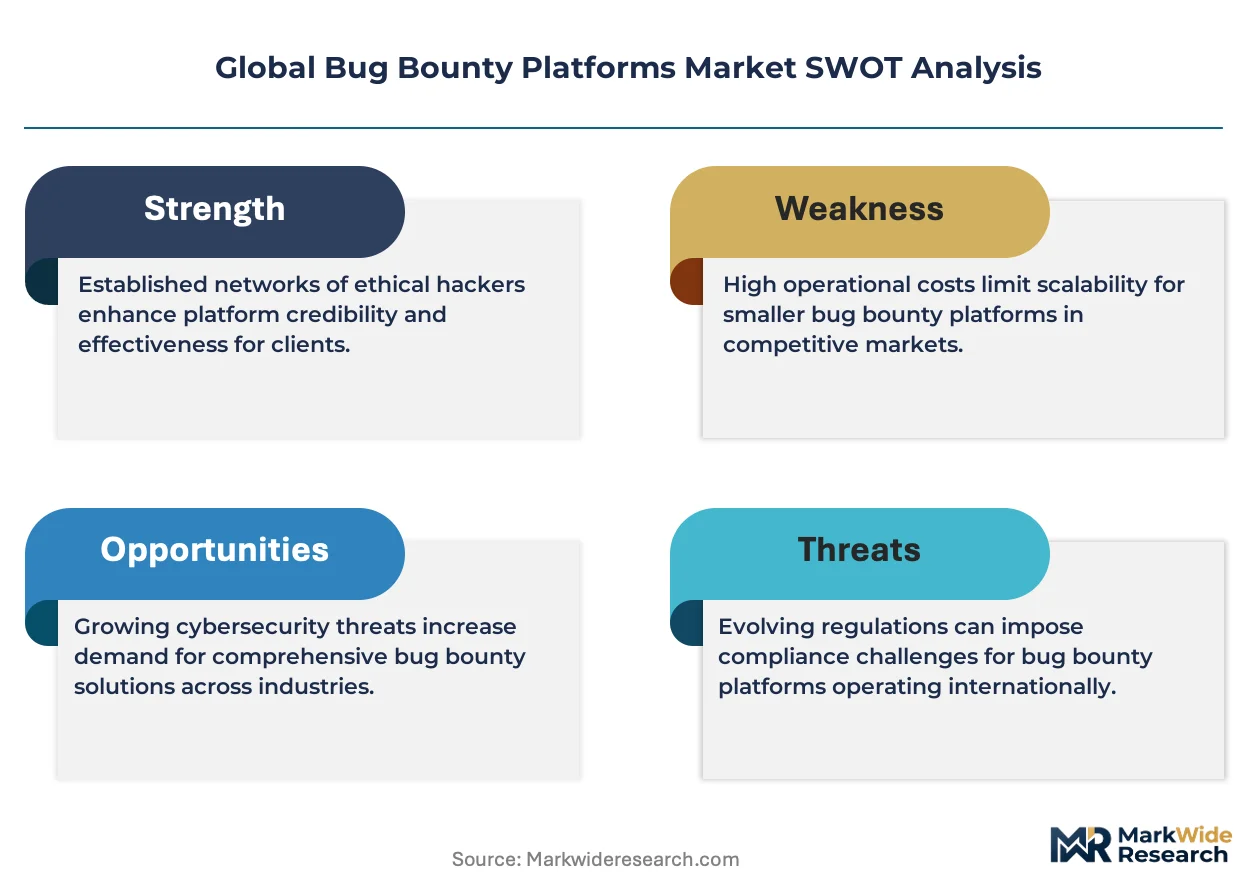
Automated scanning tools are realigning how enterprises allocate cybersecurity budgets toward human-validated findings. HackerOne leverages its researcher community to sustain enterprise-grade vulnerability triage at scale. Synack dominates government-facing contracts with its vetting-intensive model, while Bugcrowd competes across mid-market technology firms with flexible program structures.
Bug bounty platforms are crowdsourced security testing systems that connect organizations with independent researchers to identify and remediate software vulnerabilities before exploitation, typically operating through standardized submission portals with severity-based reward workflows. The platform type dimension spans private, public, managed, community, and hybrid configurations, with private programs commanding premium pricing due to controlled disclosure requirements and exclusive researcher access. Within service models, platform-as-a-service offerings lead current deployment while subscription-based arrangements are expanding fastest among Fortune 500 accounts seeking predictable security expenditure.
The EU AI Act, NIS2 Directive, and SEC cybersecurity disclosure rules in the United States collectively mandate systematic vulnerability management, directly expanding addressable demand for structured disclosure channels. ISO 29147 and ISO 30111 standards further codify coordinated vulnerability handling, elevating platform adoption where regulatory compliance carries enforcement risk. Stakeholders must weigh researcher community depth against regulatory certification breadth when selecting platform partners.
Market Dynamics
Automated vulnerability scanners are compressing triage timelines and forcing platforms to differentiate through human researcher curation rather than volume aggregation.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Publicly traded companies in the United States face mandatory incident reporting requirements. Structured bug bounty channels provide defensible documentation trails for regulatory filings.
- Critical Infrastructure Operators:Energy utilities and transportation authorities in Germany and Singapore are expanding crowdsourced testing programs. These sectors require specialized researcher pools with OT security expertise.
- EU AI Act:High-risk AI system deployers must maintain documented vulnerability management processes. Coordinated disclosure platforms satisfy audit requirements for foundation model providers.
Market Restraints
- Researcher Supply Concentration:Top-tier vulnerability discovery talent clusters in the United States, Israel, and Western Europe. Platform competition for proven researchers drives bounty inflation.
- Disclosure Policy Friction:Safe harbor provisions remain inconsistent across national jurisdictions. Researchers face legal exposure when testing systems without explicit authorization frameworks.
- False Positive Volume:Automated scanning submissions overwhelm triage teams at scale. Human validation costs erode platform margins on lower-tier programs.
Strategic Opportunities
- India's Digital Public Infrastructure:Aadhaar and UPI systems lack mature disclosure channels. Government procurement rules are evolving to permit crowdsourced security testing.
- Medical Device Convergence:Connected implantables and hospital IoT create attack surfaces requiring specialized researcher expertise. ISO 14971 risk management standards are expanding to cover coordinated disclosure.
- Automotive Software-Defined Vehicles:OTA update architectures expose new vulnerability classes. Tier-1 suppliers in Germany and Japan are piloting continuous testing programs.
Industry Challenges
- Credential Verification Bottlenecks:Government-facing contracts require security clearance-equivalent vetting. Background check timelines extend researcher onboarding to 8-12 weeks.
- Legacy SIEM Integration:Enterprise security operations centers demand API-native workflow connections. Custom integration development consumes platform engineering resources.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Bug Bounty Platforms Market |
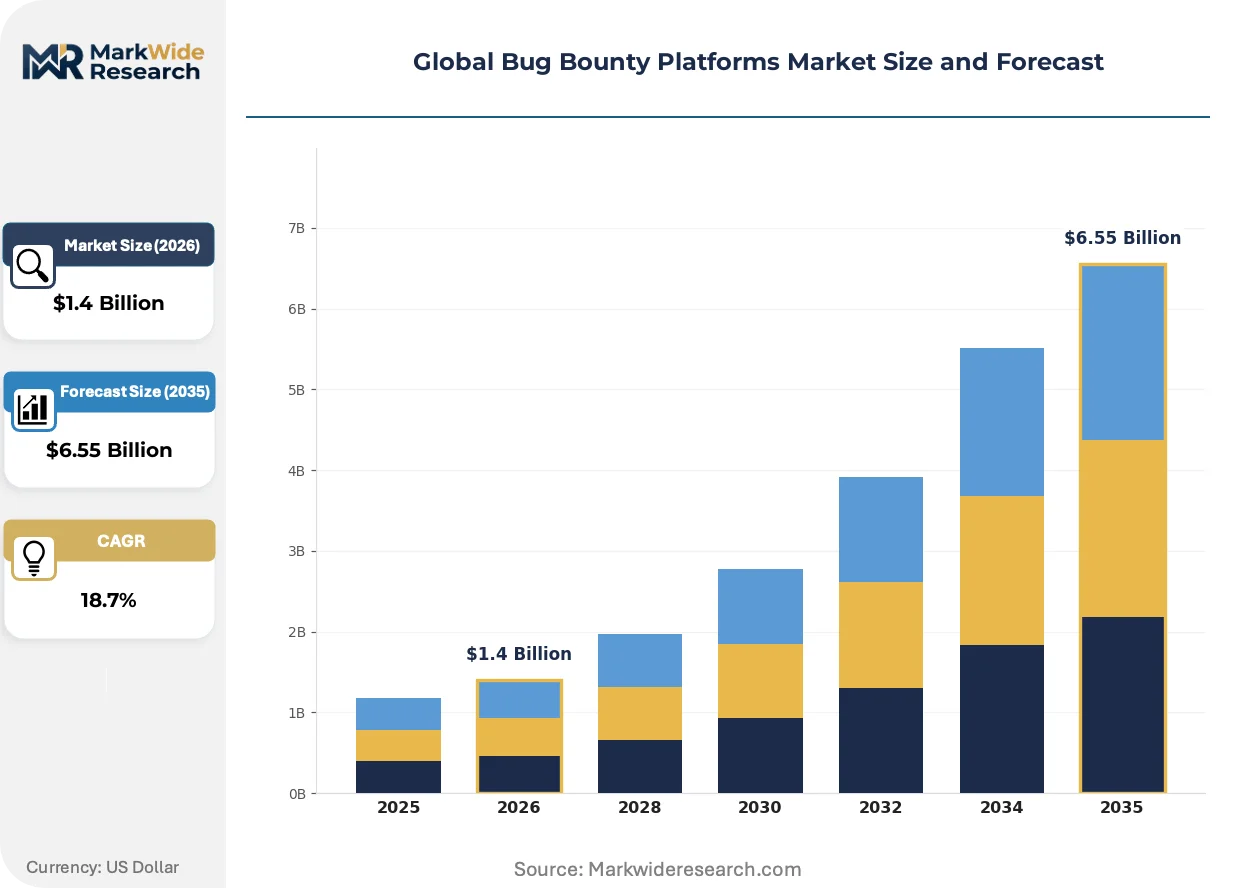
| Market Size in 2026 | $1.4 Billion |
| Market Size in 2035 | $6.55 Billion |
| CAGR (2026 – 2036) | 18.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Platform Type: Private, Public, Managed, Community, Hybrid Service Model: Platform as a Service, Software as a Service, Subscription-Based, Pay-Per-Bug, Enterprise License Target Industry: Information Technology, Telecommunications, Financial Services, E-Commerce, Media & Entertainment Reward Model: Monetary Compensation, Reputation Points, Swag & Merchandise, Hiring Opportunities, Certification, Exclusive Access |
| Companies Covered | Intigriti, Immunefi, HackerOne, Cobalt, HackenProof, Bugcrowd, Synack, Open Bug Bounty, YesWeHack, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Bug Bounty Platforms Market Shifts & Advancements
Artificial intelligence is reshaping how vulnerability reports are triaged, validated, and routed to remediation teams. Three convergent developments are compressing program operational costs while expanding addressable researcher pools.
Generative AI is integrating into submission preprocessing workflows. Large language models classify incoming reports by severity and duplicate probability before human analyst review. Fortune 500 security teams in the United States are deploying these systems to reduce triage backlog by 40-60 percent. The structural consequence is a shift of platform value toward researcher community quality rather than submission volume.
The EU NIS2 Directive is mandating systematic vulnerability handling across essential and important entities. Member state regulators are interpreting coordinated disclosure as a compliance mechanism for incident prevention obligations. Critical infrastructure operators in Germany, France, and the Netherlands are responding by migrating from informal researcher relationships to contracted platform programs with documented SLAs.
Retainer-based researcher engagement is displacing pure bounty competition in high-sensitivity sectors. Financial services and defense contractors in Singapore and the United Kingdom are securing dedicated researcher hours through prepaid arrangements. This procurement evolution reduces researcher income volatility while guaranteeing capacity for urgent testing windows.
Global Bug Bounty Platforms Market Segmentation
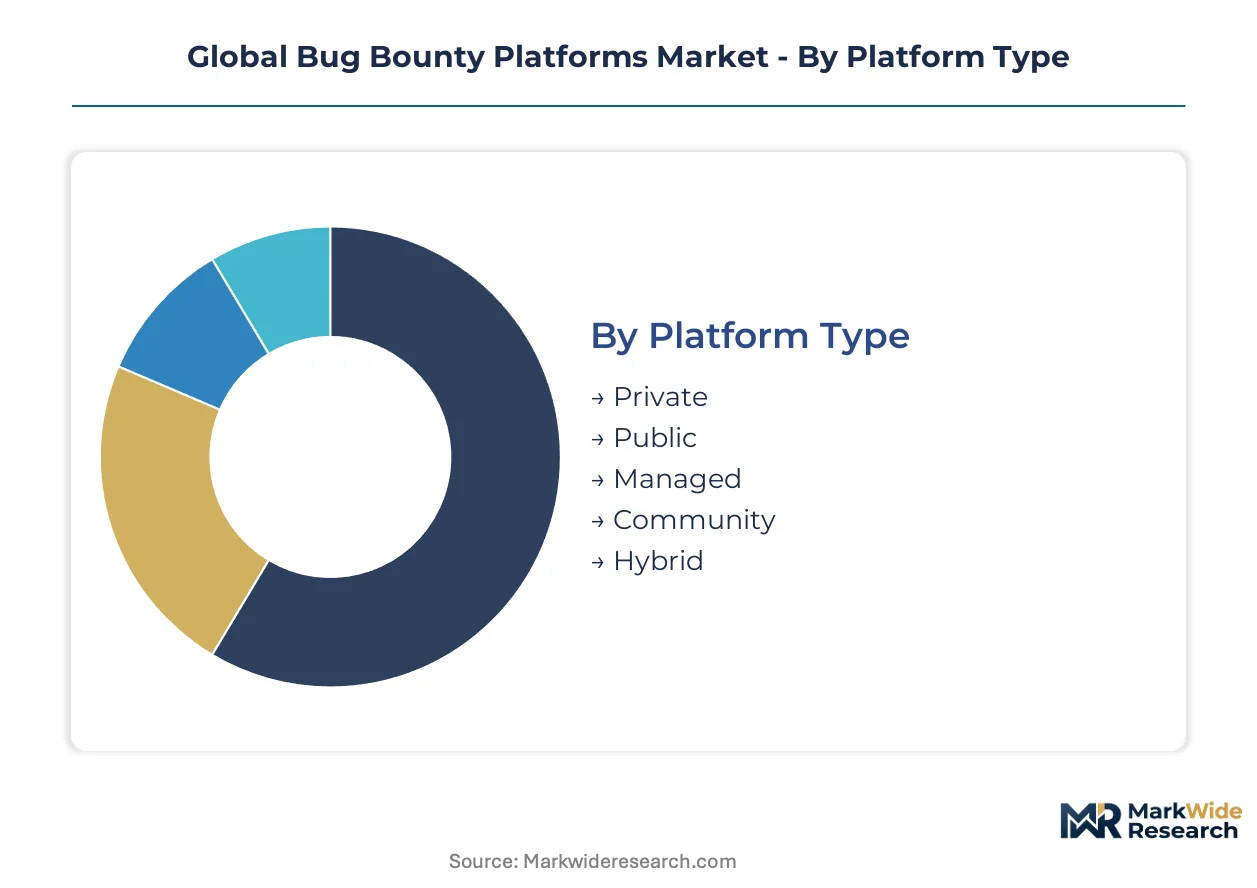
Bug bounty platforms segment across four dimensions that determine procurement priorities and operational design. Platform type and service model choices reflect organizational risk tolerance and budget predictability requirements. Target industry and reward model selections shape researcher community composition and vulnerability discovery velocity.
Platform Type:
Buyer differentiation in this category centers on disclosure control requirements and researcher access governance.
- Private:Invitation-only researcher pools with controlled disclosure timelines. Financial services firms in Singapore and Germany dominate demand here, driven by SEC disclosure rules and EU NIS2 Directive compliance documentation needs.
- Public:Open researcher participation with transparent disclosure policies. Technology companies in the United States and Israel concentrate procurement here, prioritizing vulnerability volume and community visibility over secrecy.
- Managed:Vendor-operated triage and remediation workflows. Mid-market enterprises lacking internal security operations centers favor this structure for operational offload.
- Community:Decentralized coordination without commercial platform intermediation. Academic institutions and open-source foundations in Western Europe sustain demand through grant-funded programs.
- Hybrid:Combined public and private program phases. Critical infrastructure operators in Germany deploy this model to balance broad testing with sensitive system protection.
Private programs lead volumes today; hybrid configurations are gaining share fastest.
Service Model:
Cost predictability separates buyers selecting fixed versus variable expenditure structures.
- Platform as a Service:Cloud-hosted submission portals with standardized workflows. This model concentrates among Fortune 500 accounts in the United States seeking rapid deployment without infrastructure investment.
- Software as a Service:Self-managed platform instances with vendor support. Large technology firms in Israel and the United Kingdom prefer this for customization control over triage automation.
- Subscription-Based:Fixed monthly fees for predictable researcher capacity. Financial services procurement teams in Singapore and the United States are expanding this model fastest for budget forecasting.
- Pay-Per-Bug:Variable costs tied to validated vulnerability submissions. Startups and growth-stage companies favor this for cash flow alignment.
- Enterprise License:Unlimited program scope with dedicated support tiers. Defense contractors and government agencies require this for classified system testing.
Platform as a Service dominates current deployment; subscription-based arrangements show the steepest expansion trajectory.
Target Industry:
Regulatory exposure and attack surface complexity drive industry-specific platform requirements.
- Information Technology:Cloud infrastructure and enterprise software vendors with continuous deployment pipelines. Demand clusters in the United States and Israel where researcher talent density supports rapid program scaling.
- Telecommunications:5G network operators and messaging platform providers. EU NIS2 Directive obligations are expanding procurement across Germany, France, and the Netherlands.
- Financial Services:Banks, payment processors, and cryptocurrency exchanges. SEC cybersecurity disclosure rules in the United States and Monetary Authority of Singapore guidelines mandate structured vulnerability channels.
- E-Commerce:Retail platforms with seasonal traffic spikes and payment integration. Mid-market penetration remains uneven due to margin constraints on security expenditure.
- Media & Entertainment:Streaming services and gaming platforms with user data monetization. Content protection requirements intersect with vulnerability management in this segment.
Information Technology anchors current volumes; financial services is climbing the fastest.
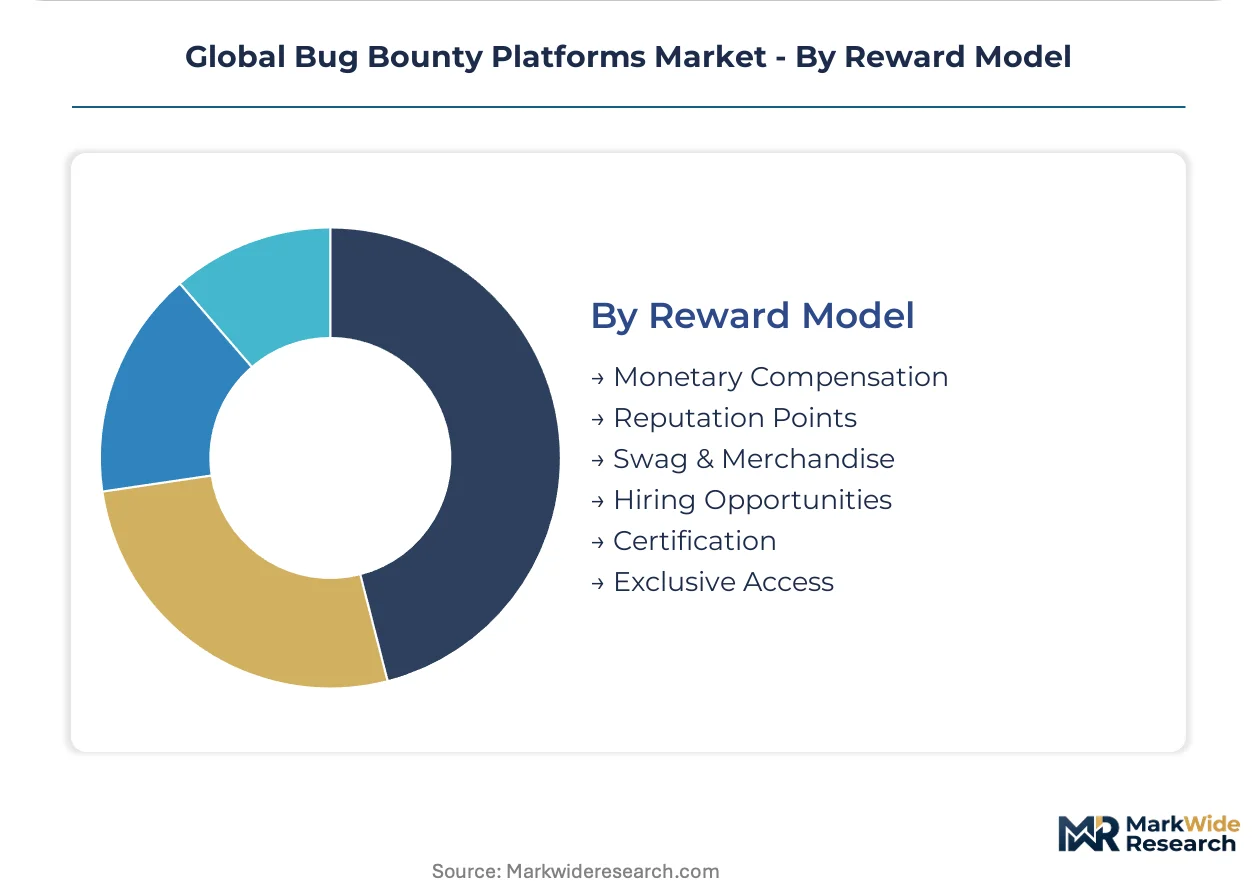
Reward Model:
Researcher motivation architecture determines community quality and retention outcomes.
- Monetary Compensation:Severity-scaled cash bounties with payment guarantees. This model dominates in the United States, Israel, and Western Europe where professional researcher populations expect income stability.
- Reputation Points:Platform-agnostic scoring systems building researcher credibility. Bugcrowd and HackerOne point economies enable cross-program recognition.
- Swag & Merchandise:Branded merchandise for low-severity findings. Community-focused programs use this for engagement without budget expansion.
- Hiring Opportunities:Direct recruitment pathways from researcher pools to security teams. Technology companies in the United States and Israel leverage this for talent pipeline development.
- Certification:Formal credentials validating vulnerability research skills. Emerging demand in India and Southeast Asia where traditional security education gaps persist.
- Exclusive Access:Early feature access or private program invitations for top performers. High-sensitivity sectors use this for researcher retention without bounty inflation.
Monetary compensation leads deployment today; hiring opportunities are expanding most quickly.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's cybersecurity ecosystem generates disproportionate platform innovation and researcher talent density. Regulatory mandates across multiple jurisdictions are accelerating procurement of structured vulnerability disclosure channels. Platform operators must navigate divergent safe harbor frameworks while scaling cross-border researcher communities.
United States
SEC cybersecurity disclosure rules and critical infrastructure designations drive enterprise adoption. The Securities and Exchange Commission mandates incident reporting with defensible documentation trails. San Francisco and New York City host the densest concentrations of platform headquarters and Fortune 500 security procurement teams.
Germany
Energy utilities and automotive Tier-1 suppliers expand crowdsourced testing for OT systems. The EU NIS2 Directive imposes systematic vulnerability management on essential entities. Munich and Stuttgart clusters lead deployment of hybrid public-private program structures for sensitive industrial systems.
Singapore
Financial services regulators mandate structured disclosure channels for banks and payment processors. The Monetary Authority of Singapore guidelines require documented vulnerability handling processes. The city-state's technology corridor attracts regional platform operations serving Southeast Asian markets.
Israel
Military intelligence veterans populate elite researcher pools serving global enterprise clients. The Israel National Cyber Directorate promotes coordinated disclosure frameworks for critical infrastructure. Tel Aviv's cybersecurity cluster exports vulnerability research expertise through platform partnerships.
United Kingdom
Defense contractors and fintech operators adopt retainer-based researcher engagement models. The National Cyber Security Centre provides safe harbor guidance for ethical hacking activities. London's financial district concentrates procurement of subscription-based platform arrangements for predictable security expenditure.
Global Bug Bounty Platforms Market Competitive Landscape
Global majors compete with regional champions across researcher community depth and regulatory certification breadth. The vendor landscape concentrates around three operational models: managed triage services, self-service platforms, and government-facing cleared programs. Strategic differentiation hinges on researcher vetting intensity, API-native SIEM integrations, and geographic compliance coverage. Consolidation pressure favors platforms with proven enterprise retention and multi-jurisdictional legal frameworks.
Within the managed service archetype, HackerOne and Bugcrowd occupy positions defined by researcher community scale and mid-market accessibility respectively. Synack exemplifies the cleared-researcher tier serving defense and intelligence sector contracts with vetting-intensive onboarding. These three entities anchor competitive dynamics around triage automation investment and geographic expansion into regulated European and Asia-Pacific markets.
| Leading Market Players |
|---|
| Intigriti |
| Immunefi |
| HackerOne |
| Cobalt |
| HackenProof |
| Bugcrowd |
| Synack |
| Open Bug Bounty |
| YesWeHack |
| Others |
Supply & Pricing Matrix
Researcher talent scarcity indices in Israel and the United States cascade through platform economics into differentiated service tiers, with premium private programs absorbing talent concentration premiums while mid-market subscriptions compress margins.
Pricing Analysis
Input-cost pass-through from elite researcher retention expenses shapes platform pricing architecture. Subscription-based arrangements dominate Fortune 500 procurement for budget predictability, while pay-per-bug models serve cash-constrained growth-stage firms. Price differentiation hinges on vetting intensity depth and API-native SIEM integration completeness. Pricing pressure intensifies as automated scanning tools commoditize volume aggregation, forcing platforms to invest in human curation layers. Financial services buyers in Singapore exhibit lowest price sensitivity due to regulatory compliance mandates; mid-market technology firms in Israel display highest sensitivity, prioritizing variable cost structures.
Supply Chain Analysis
Logistics and talent mobility costs concentrate researcher supply in Tel Aviv, San Francisco, and Berlin corridors. Platform operations draw from specialized cybersecurity labor pools, cloud infrastructure provisioning, and compliance certification services. Single-source vulnerability in elite researcher concentration creates bidding-war dynamics for proven talent. Distribution runs through direct enterprise sales teams for large accounts and self-service portals for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market compounds steadily as regulatory mandates across the United States, European Union, and Singapore institutionalize structured vulnerability disclosure as a compliance requirement rather than discretionary security expenditure.
For Market Incumbents: Extend researcher community depth through retainer-based engagement models that lock in elite talent pools before competitors replicate cleared-researcher vetting infrastructure. Invest in API-native SIEM integrations to defend against emerging platforms offering faster enterprise workflow embedding. Counter Synack's government-contract dominance by accelerating security-clearance-equivalent background check automation.
For New Entrants and Emerging Players: Enter via India's evolving Digital Public Infrastructure procurement rules, where Aadhaar and UPI systems lack mature disclosure channels and government rules are shifting to permit crowdsourced testing. Target medical device manufacturers in Germany and Japan facing ISO 14971 expansion into coordinated disclosure. Deploy certification-based researcher incentives to differentiate in Southeast Asian markets where formal security education gaps persist.
For Investors and Strategic Acquirers: Consolidation pressure builds where platforms lack multi-jurisdictional legal frameworks to navigate divergent safe harbor provisions across national boundaries. Long-term viability favors entities with proven enterprise retention and regulatory certification breadth. Watch for inflection signals in EU NIS2 Directive enforcement intensity across German and French critical infrastructure operators.
| Strategic Initiative | Industry Significance |
|---|---|
| Cleared-Researcher Vetting Automation | Compresses 8-12 week onboarding timelines to capture defense and intelligence contracts. |
| API-Native SIEM Integration | Meets enterprise SOC demands for workflow connectivity without custom engineering. |
| Retainer-Based Researcher Engagement | Reduces income volatility for talent while guaranteeing urgent testing capacity. |
| Multi-Jurisdictional Legal Framework Expansion | Enables safe harbor navigation across EU, US, and Singapore regulatory regimes. |
| Medical Device Specialized Program Launch | Captures ISO 14971-driven demand from connected implantable manufacturers. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window. Primary fieldwork engaged platform operators, CISOs at Fortune 500 financial services firms, government procurement officers in Germany and Singapore, and elite vulnerability researchers across Israel and the United States. Secondary validation drew from SEC cybersecurity disclosure filings, EU NIS2 Directive implementation guidance, Monetary Authority of Singapore regulatory circulars, and ISO 29147/30111 standards documentation. Bottom-up program deployment counts and top-down security expenditure estimates were triangulated against platform-reported researcher community metrics.
Segment-weighting approaches distributed value across platform type, service model, target industry, and reward model dimensions. Deployment patterns by organization size and regional regulatory cluster shaped volume assumptions. CAGRs were derived from regression analysis of historical program expansion rates and forward projection of compliance-driven procurement acceleration. Researcher talent supply constraints and automated tooling substitution effects informed growth ceiling parameters.
The model holds under stable regulatory enforcement intensity; deviation in EU NIS2 penalty implementation or SEC disclosure rule litigation thresholds would shift enterprise adoption timelines. Stakeholders should weight assumptions against their own operating context.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Mobile Encryption Market
Cybersecurity
Global Cloud Encryption Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
South Africa Cybersecurity Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Data Center Logical Security Market
Cybersecurity
Big Data Security Market
Cybersecurity
Asia Pacific IoT Security Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Server Security Market
Cybersecurity
Malaysia Cybersecurity Market
Cybersecurity
North America Cyber Security Market
Cybersecurity
Greece Cybersecurity Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
Austria Cybersecurity Market
Cybersecurity
Micro Segmentation Technology Market