
 Global Data Exfiltration Market | 2026-2036
Global Data Exfiltration Market Size, Share, and Industry Trends Forecast 2026-2036
Global Data Exfiltration Market Foresight
Israeli cybersecurity engineering talent is hardening the defensive perimeter against state-sponsored exfiltration campaigns. Palo Alto Networks leverages its Strata platform to anchor enterprise network security architectures across North American critical infrastructure. CrowdStrike Holdings sustains endpoint detection leadership through AI-native threat graph analytics that compress incident response timelines. Check Point Software Technologies dominates gateway security with unified threat prevention appliances deployed in tier-one banking environments.
Data exfiltration is the unauthorized transfer of sensitive information from organizational systems to external destinations, typically executed through encrypted channels, DNS tunneling, or cloud storage APIs with payload obfuscation techniques. The primary purpose is intelligence theft, financial fraud, or competitive sabotage targeting structured databases and unstructured document repositories. Cloud-based deployment modes are capturing the fastest expansion as distributed workforces dissolve traditional network perimeters and mandate zero-trust validation architectures. Banking and energy verticals concentrate the highest defensive spending where regulatory capital requirements and operational technology convergence amplify breach consequences. Insider threat vectors are maturing fastest as behavioral analytics platforms refine anomaly detection for privileged user sessions.
The U.S. SEC cybersecurity disclosure rules, the EU NIS2 Directive, and India's DPDP Act are collectively mandating incident reporting timelines and board-level accountability for data loss events. These frameworks reshape procurement priorities toward platforms with native compliance automation and forensic audit trails. Stakeholders must evaluate vendor architectures for sovereign data residency controls and cross-border transfer governance as jurisdictional fragmentation intensifies.
Market Dynamics
Zero-trust network architectures are dissolving perimeter-based security models and forcing organizations to rebuild data protection around continuous identity verification and micro-segmentation. This structural shift compresses procurement cycles for cloud-native exfiltration prevention platforms while elevating sovereign data residency requirements to board-level priority.
Growth Catalysts
- EU AI Act compliance deadlines:Automated data governance mandates are accelerating procurement of platforms with embedded audit trails and cross-border transfer controls.
- Critical infrastructure operators:Energy and utilities sectors are hardening operational technology networks against ransomware-to-exfiltration kill chains.
- DNS-over-HTTPS proliferation:Encrypted DNS traffic is masking command-and-control channels, forcing investment in deep packet inspection and behavioral analytics.
Market Restraints
- Specialized talent scarcity:Shortages of threat intelligence analysts and cloud security architects inflate implementation timelines and service costs.
- Legacy infrastructure debt:Mainframe and on-premise data warehouses resist API-based monitoring without expensive middleware layers.
- False positive fatigue:Over-alerting from signature-based detection erodes security team responsiveness and platform trust.
Strategic Opportunities
- India's DPDP Act implementation:Data localization mandates are creating demand for domestic-hosted exfiltration monitoring and incident response services.
- Extended detection and response convergence:XDR platforms integrating endpoint, network, and cloud telemetry are capturing budget from point solutions.
- Managed detection services:Mid-market enterprises are outsourcing 24/7 security operations to specialized providers rather than building in-house SOCs.
Industry Challenges
- Encrypted traffic inspection:TLS 1.3 and certificate pinning complicate payload analysis without performance-degrading decryption proxies.
- Shadow SaaS sprawl:Unsanctioned cloud application usage bypasses traditional data loss prevention controls and expands attack surfaces.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Data Exfiltration Market |
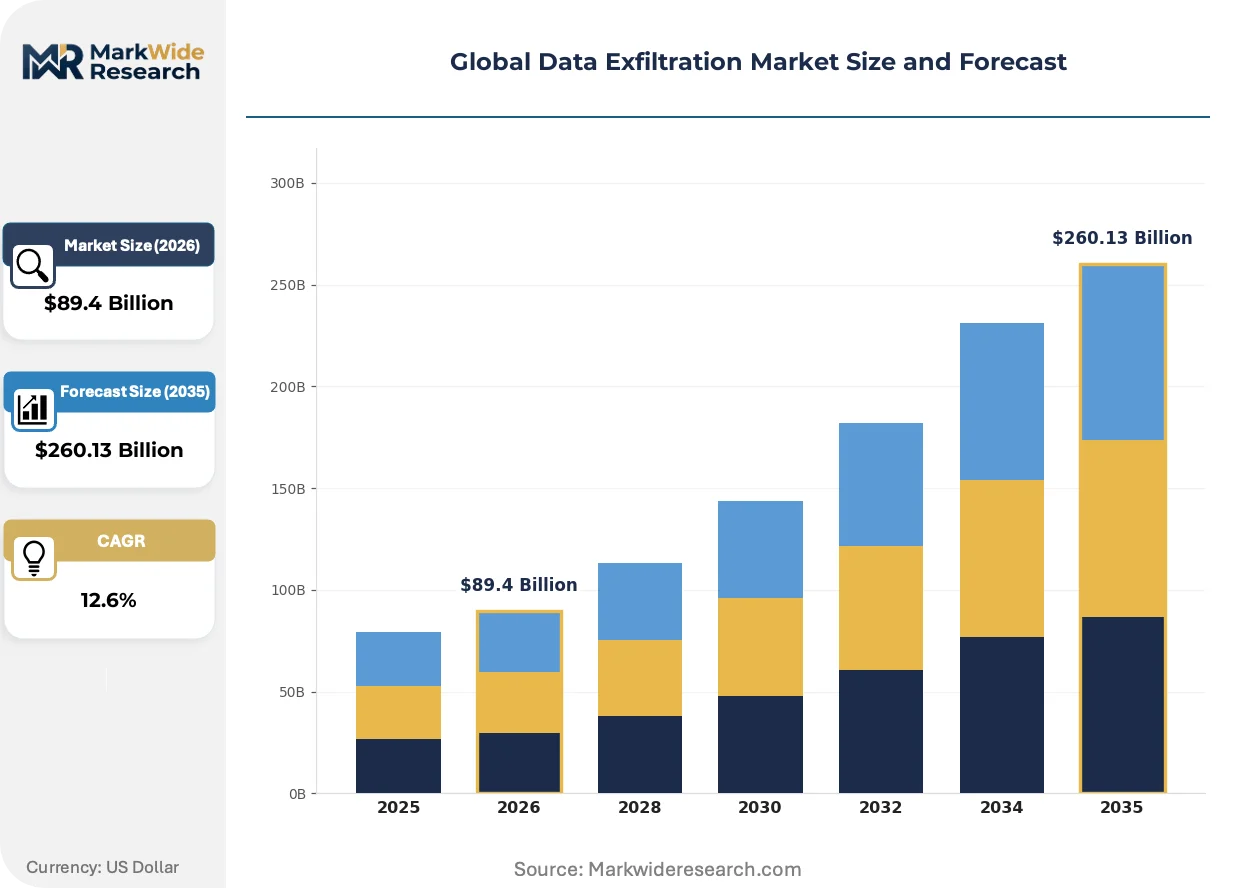
| Market Size in 2026 | $89.4 Billion |
| Market Size in 2035 | $260.13 Billion |
| CAGR (2026 – 2036) | 12.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Attack Vector: Phishing, Malware, Social Engineering, Insider Threats, Advanced Persistent Threats Industry Vertical: Banking, Telecommunication, Government, Education, Energy Deployment Mode: On-Premises, Cloud-Based, Hybrid, Managed Security Service Data Type Targeted: Personal Identifiable Information, Intellectual Property, Financial Data, Healthcare Records, Trade Secrets |
| Companies Covered | Palo Alto Networks, Cisco Systems, Check Point Software Technologies, Fortinet, Zscaler, CrowdStrike Holdings, Broadcom, Forcepoint, Trend Micro, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Data Exfiltration Market Shifts & Advancements
Artificial intelligence is compressing threat detection latency while regulatory fragmentation is fragmenting vendor architectures around jurisdictional data boundaries. These forces are reshaping how organizations architect defense-in-depth strategies.
User and entity behavior analytics is converging with large language model-powered natural language processing to identify anomalous data access patterns in unstructured document repositories. Financial institutions in Germany and the United States are deploying these hybrid systems to flag insider exfiltration before payload transfer completes. The technology is converging with zero-trust access brokers to enforce dynamic data masking based on real-time risk scoring.
The EU NIS2 Directive is mandating incident reporting within 24 hours for critical entities across energy, transport, and digital infrastructure sectors. This regulatory pressure is forcing vendors to embed automated compliance documentation and forensic chain-of-custody features directly into detection platforms. Banking consortia in France and the Netherlands are collectively negotiating standardized reporting formats to reduce administrative burden.
Security procurement committees are consolidating vendor relationships and demanding platform consolidation over best-of-breed point solutions. CISOs at Fortune 500 manufacturers are replacing three to four standalone tools with integrated suites that span endpoint, email, and cloud data protection. This preference shift is most pronounced in the United States and United Kingdom where board-level cybersecurity accountability has tightened following SEC disclosure rule enforcement.
Global Data Exfiltration Market Segmentation
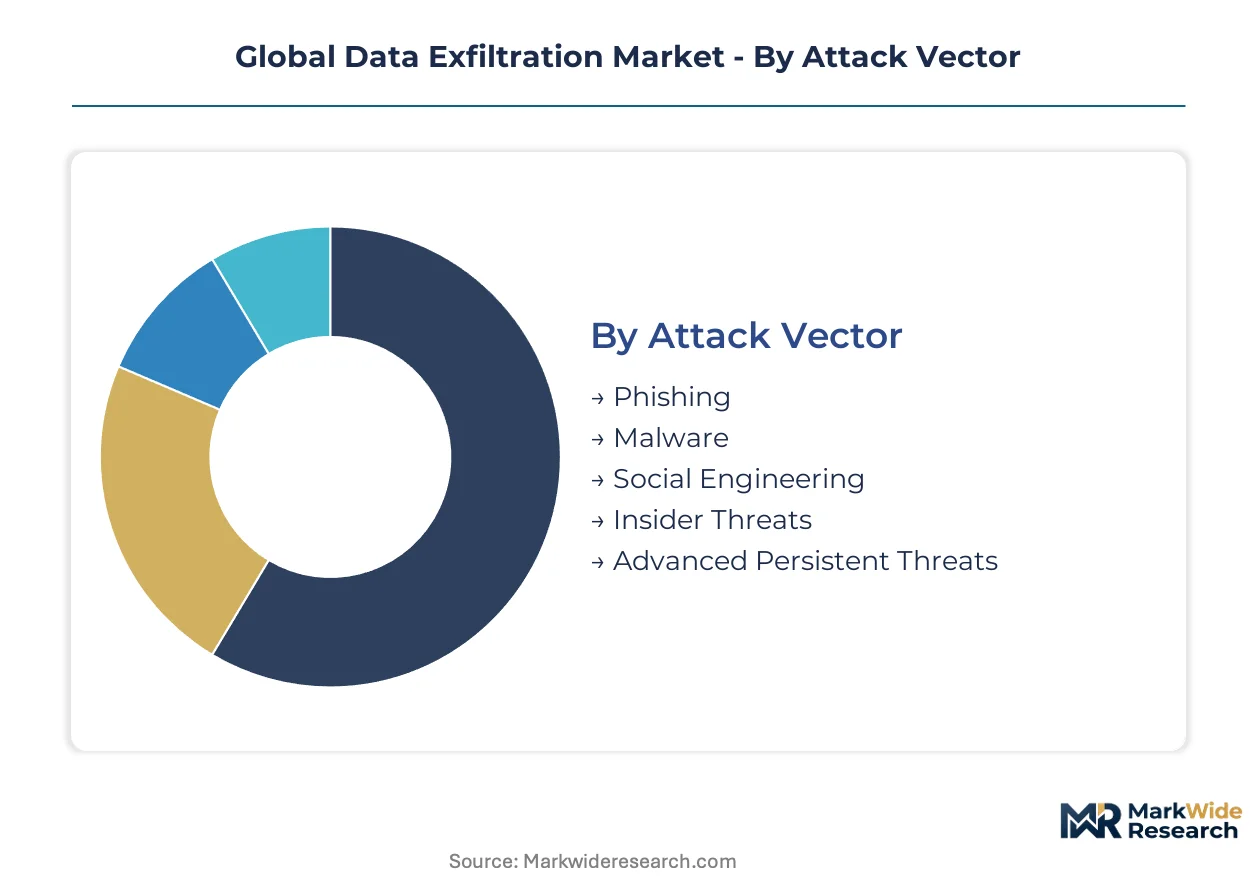
Attack sophistication and regulatory exposure vary sharply across exfiltration vectors, forcing vendors to architect modular platforms that span endpoint, network, and cloud telemetry. Segmentation reveals where procurement budgets concentrate and which defensive layers command premium pricing.
Attack Vector:
Customization intensity runs highest where human behavior intersects with technical exploit delivery, while standardized detection suffices for automated malware signatures.
- Phishing:Deceptive email and messaging campaigns leverage credential harvesting and malicious attachments to establish initial access. Financial institutions in Germany and the United States allocate disproportionate training budgets here due to SEC and BaFin disclosure accountability. Email gateway vendors embed natural language processing to flag social engineering before inbox delivery.
- Insider Threats:Authorized users abuse legitimate access privileges to extract structured databases or unstructured documents to personal cloud storage. Behavioral analytics platforms refine anomaly detection for privileged sessions in Indian IT services firms and U.S. defense contractors. User activity monitoring solutions command premium pricing where intellectual property concentration is highest.
- Malware:Automated payload delivery through trojans and infostealers targets endpoint vulnerabilities at scale.
- Social Engineering:Voice phishing and pretexting manipulate human trust rather than technical exploits.
- Advanced Persistent Threats:State-sponsored actors maintain long-dwell access for strategic intelligence collection.
Leading the category by volume: Phishing. Growing fastest: Insider Threats.
Industry Vertical:
Regulatory capital requirements and operational technology convergence amplify breach consequences unevenly across sectors.
- Banking:Tier-one institutions face Basel III operational risk capital charges alongside GDPR and SEC disclosure mandates. Fraud-to-exfiltration kill chains drive consolidation around integrated XDR platforms with native compliance automation. French and Dutch banking consortia negotiate standardized incident reporting formats to reduce administrative burden.
- Energy:Operational technology networks controlling generation and distribution infrastructure attract ransomware-to-exfiltration campaigns. The EU NIS2 Directive mandates 24-hour reporting for critical entities, forcing vendors to embed forensic chain-of-custody features. U.S. FERC and German BSI standards harden procurement specifications for SCADA-adjacent monitoring.
- Telecommunication:Subscriber metadata and lawful intercept systems create high-value targets for state actors.
- Government:Classified document repositories demand sovereign data residency controls and air-gapped architectures.
- Education:Research intellectual property and student financial aid data face lower defensive investment thresholds.
Banking captures the largest procurement value. Energy shows the steepest expansion trajectory.
Deployment Mode:
Cost tier stratification separates capital-intensive on-premise builds from operational expenditure cloud subscriptions.
- Cloud-Based:Distributed workforces dissolve traditional network perimeters and mandate zero-trust validation architectures. API-native data loss prevention integrates with SaaS productivity suites and cloud storage services. Indian enterprises adopting the DPDP Act favor domestic-hosted instances with data localization guarantees.
- Managed Security Service:Mid-market enterprises outsource 24/7 security operations rather than building in-house SOCs. Specialized providers in Israel and the United Kingdom deliver threat hunting and incident response as subscription services. Procurement committees favor outcome-based pricing tied to mean-time-to-containment metrics.
- On-Premises:Legacy mainframe environments and classified networks resist cloud migration.
- Hybrid:Segmented architectures protect crown-jewel assets on-premise while cloud-enabling general workloads.
Cloud-Based deployment holds the dominant share. Managed Security Service is climbing the fastest.
Data Type Targeted:
Margin concentration aligns with resale value and regulatory penalty severity rather than volume alone.
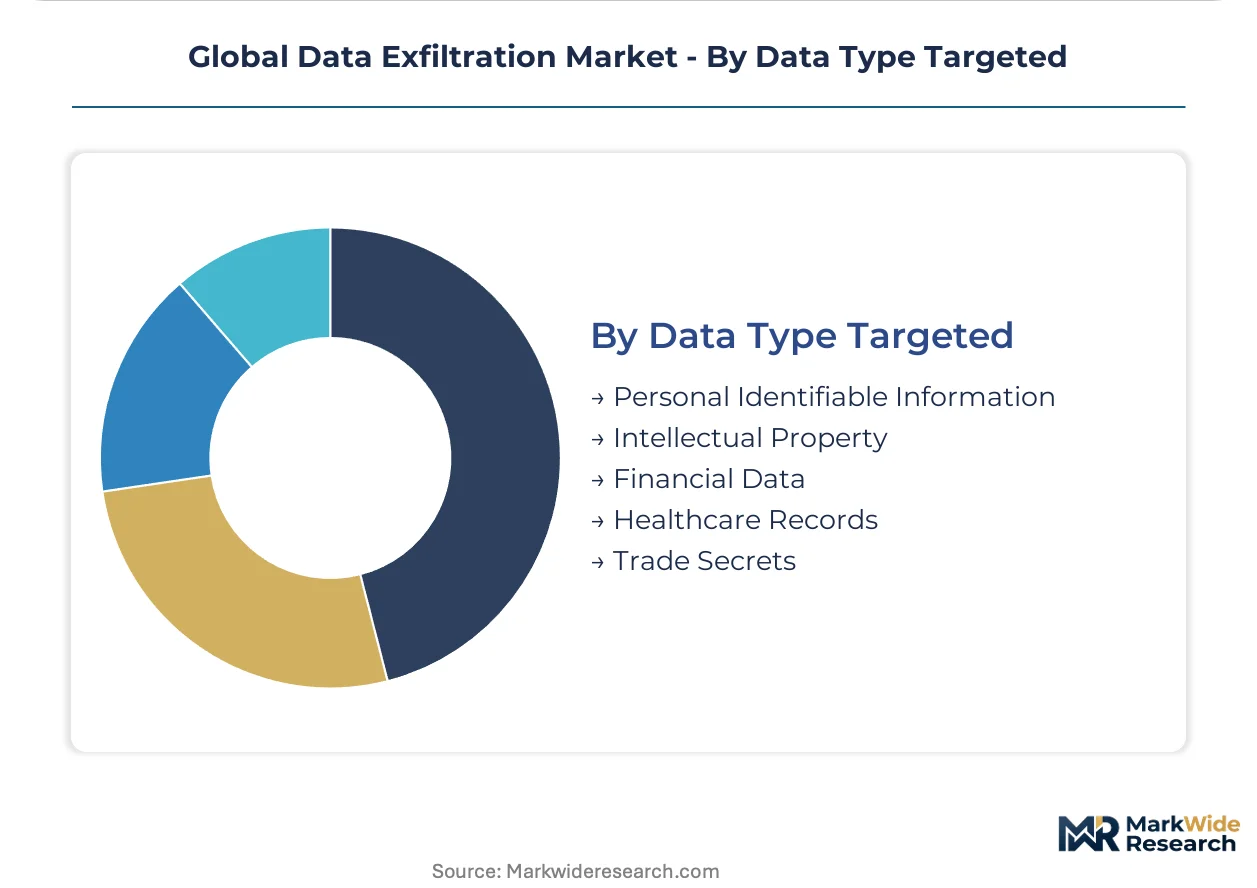
- Personal Identifiable Information:Structured identity attributes enable synthetic fraud and account takeover at scale. GDPR and India's DPDP Act impose penalty structures that elevate defensive spending above baseline IT budgets. Healthcare and financial services verticals deploy tokenization and dynamic data masking for database fields containing national identifiers.
- Intellectual Property:Unstructured document repositories containing source code, chemical formulas, and design specifications command targeted extraction efforts. German automotive and pharmaceutical manufacturers deploy UEBA-LLM hybrid systems to flag anomalous access before payload transfer. Trade secret litigation exposure in U.S. federal courts drives board-level visibility.
- Financial Data:Payment card and transaction records feed direct monetization through fraud networks.
- Healthcare Records:Medical histories support insurance fraud and prescription abuse schemes.
- Trade Secrets:Proprietary manufacturing processes and customer lists enable competitive sabotage.
Personal Identifiable Information leads by defensive budget allocation. Intellectual Property is gaining share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Israeli cybersecurity talent clusters anchor defensive engineering capabilities against state-sponsored exfiltration campaigns. Sovereign data protection frameworks in the United States, Germany, and India are reshaping procurement priorities and compliance architectures.
United States
SEC cybersecurity disclosure rules and FERC standards for critical infrastructure are tightening board-level accountability for data loss events. Palo Alto Networks anchors enterprise network security architectures across North American energy and financial sectors. Fortune 500 manufacturers in the Midwest and Southeast are consolidating vendor relationships around integrated XDR platforms.
Germany
BaFin disclosure mandates and BSI standards for operational technology networks are elevating defensive spending in banking and energy verticals. German automotive and pharmaceutical manufacturers in Bavaria and Baden-Württemberg deploy UEBA-LLM hybrid systems to flag insider exfiltration before payload transfer completes.
India
DPDP Act data localization requirements and RBI operational risk frameworks are creating demand for domestic-hosted exfiltration monitoring services. Indian IT services firms in Bangalore and Hyderabad are refining behavioral analytics for privileged user session anomaly detection. Mid-market enterprises in Maharashtra and Gujarat favor managed security service subscriptions over in-house SOC builds.
Israel
Specialized threat intelligence analyst talent scarcity inflates implementation timelines and service costs across the ecosystem. Israeli cybersecurity engineering clusters harden defensive perimeters against encrypted DNS tunneling and cloud storage API exploitation. Tel Aviv-based providers deliver threat hunting and incident response as subscription services to European and North American clients.
United Kingdom
Post-Brexit data governance fragmentation and NIS2 Directive alignment pressures are reshaping cross-border transfer controls. London financial services institutions face consolidated regulatory scrutiny from the FCA and PRA alongside GDPR residual obligations. Security procurement committees in the Southeast and Midlands are demanding platform consolidation over best-of-breed point solutions.
Global Data Exfiltration Market Competitive Landscape
Global majors compete with regional champions across cloud-native architecture and sovereign data residency capabilities. The vendor base stratifies into three tiers: integrated platform providers spanning endpoint, network, and cloud telemetry; specialized gateway security appliance manufacturers; and managed detection service operators serving mid-market outsourcing demand. Strategic archetypes include scale-driven suite consolidators, geography-bound compliance specialists, and AI-native threat graph analytics innovators. Dominant competitive moves center on XDR platform convergence capturing budget from point solutions, and outcome-based pricing tied to mean-time-to-containment metrics.
Within the integrated platform tier, Palo Alto Networks, CrowdStrike Holdings, and Check Point Software Technologies exemplify contrasting architectural approaches. Palo Alto Networks occupies a position anchoring enterprise network security through cloud-delivered zero-trust validation. CrowdStrike Holdings represents the AI-native endpoint detection archetype compressing incident response timelines through threat graph analytics. Check Point Software Technologies sits within the gateway security specialization dominating tier-one banking environments with unified threat prevention appliances.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Cisco Systems |
| Check Point Software Technologies |
| Fortinet |
| Zscaler |
| CrowdStrike Holdings |
| Broadcom |
| Forcepoint |
| Trend Micro |
| Others |
Supply & Pricing Matrix
Specialized cybersecurity talent salary indices in Israel and the United States cascade through vendor cost structures into three-tier pricing stratification across cloud-native platforms, managed detection services, and on-premise appliance tiers. Procurement committees in banking and energy verticals absorb premium pricing for sovereign data residency guarantees while mid-market buyers face compressed margins on standardized SaaS subscriptions.
Pricing Analysis
Managed detection and response service bundles with 24/7 threat hunting and incident response command 40-60% premiums over unmonitored platform licenses. Three-tier pricing structure across premium, standard, and economy levels separates Fortune 500 integrated XDR deployments from mid-market SaaS subscriptions and basic email gateway appliances. Pricing pressure stems from hyperscaler cloud security entrants compressing margins in the standard tier. Mid-market enterprises in India and Southeast Asia exhibit highest price sensitivity, while tier-one banks in Germany and the United States prioritize compliance automation over cost minimization.
Supply Chain Analysis
Direct-to-OEM channels handle hyperscale buyer demand from Fortune 500 manufacturers and critical infrastructure operators, while value-added resellers and managed security service providers serve fragmented mid-market demand. Engineering talent concentrates in Israel, the United States, and India, with threat intelligence analyst scarcity inflating implementation timelines. Semiconductor components for security appliances draw from Taiwan and South Korea, while cloud infrastructure rests on hyperscaler data center networks in Virginia, Frankfurt, and Mumbai. Single-source vulnerability in specialized encryption hardware creates supply chain risk. Distribution runs through channel partners with certified security architects in North America, Western Europe, and Asia-Pacific financial hubs.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Vertical integration into proprietary threat intelligence feeds and sovereign data center infrastructure anchors sustainable margin defense as jurisdictional fragmentation intensifies regulatory compliance costs.
For Market Incumbents: Deepen integration of behavioral analytics engines with zero-trust access brokers to lock in banking and energy verticals against CrowdStrike and Palo Alto Networks platform convergence. Acquire specialist UEBA-LLM hybrid technology providers in Germany and Israel to preempt insider threat vector commoditization. Prioritize embedded compliance automation for EU NIS2 Directive and India DPDP Act timelines.
For New Entrants and Emerging Players: Managed security service providers in the United Kingdom and Singapore represent the most penetrable channel partner type for mid-market outsourcing demand. Target India's DPDP Act implementation window with domestic-hosted exfiltration monitoring services before incumbent cloud providers establish data localization infrastructure. Pursue outcome-based pricing tied to mean-time-to-containment metrics to differentiate from established per-seat SaaS models.
For Investors and Strategic Acquirers: Distressed-cycle entries favor Israeli threat intelligence specialists with proprietary encrypted traffic inspection capabilities. Long-term viability across the analysis window hinges on AI-native detection latency compression and cross-border transfer governance automation. Monitor EU AI Act enforcement actions against non-compliant vendors as inflection indicator for consolidation timing.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | XDR convergence captures endpoint, network, and cloud telemetry budgets from point solutions. |
| Acquisition of Specialist Firm | UEBA-LLM hybrid technology providers in Germany command premium multiples from banking verticals. |
| Geographic Expansion | Domestic-hosted instances in India satisfy DPDP Act data localization mandates for mid-market demand. |
| Strategic Partnership | Banking consortia in France and Netherlands negotiate standardized incident reporting formats. |
| Product Launch | Native compliance automation for EU NIS2 Directive 24-hour reporting deadlines accelerates procurement cycles. |
Research Methodology
SEC cybersecurity disclosure filings, EU NIS2 Directive implementation guidance, and RBI operational risk frameworks formed the secondary backbone for regulatory timeline validation. Primary interviews with CISOs at Fortune 500 manufacturers, threat intelligence directors at Israeli cybersecurity firms, and procurement leads at tier-one European banks combined with customs data on security appliance trade flows and hyperscaler capex disclosures. Bottom-up triangulation across deployment mode, attack vector, and industry vertical segmentation validated top-down market sizing from banking and energy vertical IT budget benchmarks.
Bottom-up modeling of cloud-native platform subscriptions, managed detection service contracts, and on-premise appliance shipments anchored value projections across the analysis window. Segmentation dimensions spanned deployment mode, attack vector sophistication, industry vertical regulatory exposure, and data type targeted resale value. CAGRs derived from procurement cycle compression rates in critical infrastructure and banking verticals, adjusted for talent scarcity implementation delays. Forecast inputs incorporated EU AI Act compliance deadline acceleration and India's DPDP Act localization mandates.
Caveats apply where TLS 1.3 encryption standard adoption or quantum-resistant cryptography migration could materially shift deep packet inspection technology viability. Forecasts reflect assumptions on sovereign data residency enforcement intensity and hyperscaler cloud security service expansion. Periodic stress-testing of base assumptions is recommended against regulatory enforcement variance and state-sponsored exfiltration campaign escalation patterns.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
Global Distributed Denial of Service (Ddos) Protection Market
Cybersecurity
Industrial Cybersecurity Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Data Center Security Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Egypt Cybersecurity Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Malaysia Cybersecurity Market
Cybersecurity
Europe Mobile Security Market
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Digital Immune System Market
Cybersecurity
Saudi Arabia Cybersecurity Market
Cybersecurity
New Zealand Cybersecurity Market
Cybersecurity
Europe Software Defined Perimeter Market
Cybersecurity
Global Cyber Situational Awareness Market