
 Data Center Security Market | 2026-2036
Data Center Security Market Size, Share, and Industry Trends Forecast 2026-2036
Data Center Security Market Intelligence
Channel partnership structures for data center security are fragmenting as vendors bypass traditional VARs to sell directly to enterprise buyers. Palo Alto Networks leverages its platform consolidation strategy to capture multi-year enterprise commitments. CrowdStrike anchors its growth in endpoint detection workloads that extend into cloud-native data center environments. Check Point competes through perimeter firewall specialization while maintaining strong channel presence in regulated verticals.
Data center security encompasses the integrated hardware, software, and procedural safeguards protecting physical and digital infrastructure from unauthorized access, cyber intrusion, and operational disruption, with systems typically enforcing sub-millisecond latency thresholds for inline traffic inspection. Its primary purpose is maintaining confidentiality, integrity, and availability of mission-critical compute, storage, and network resources. Firewall and intrusion detection system deployments dominate solution spending as foundational layers, while encryption is gaining traction among financial institutions navigating data residency mandates. Cloud-based deployment is expanding fastest as organizations retire legacy on-premises security stacks, though hybrid configurations retain the largest margin pools due to integration complexity.
FCC guidelines on communications infrastructure resilience, SEC cybersecurity disclosure rules for publicly traded operators, and ISO 27001 certification requirements collectively elevate baseline security spending across US data center operators. GDPR and the EU AI Act impose additional compliance burdens on European facilities processing personal data or deploying automated threat response systems. Stakeholders must weigh sovereign cloud mandates against platform consolidation economics when architecting multi-jurisdiction security postures.
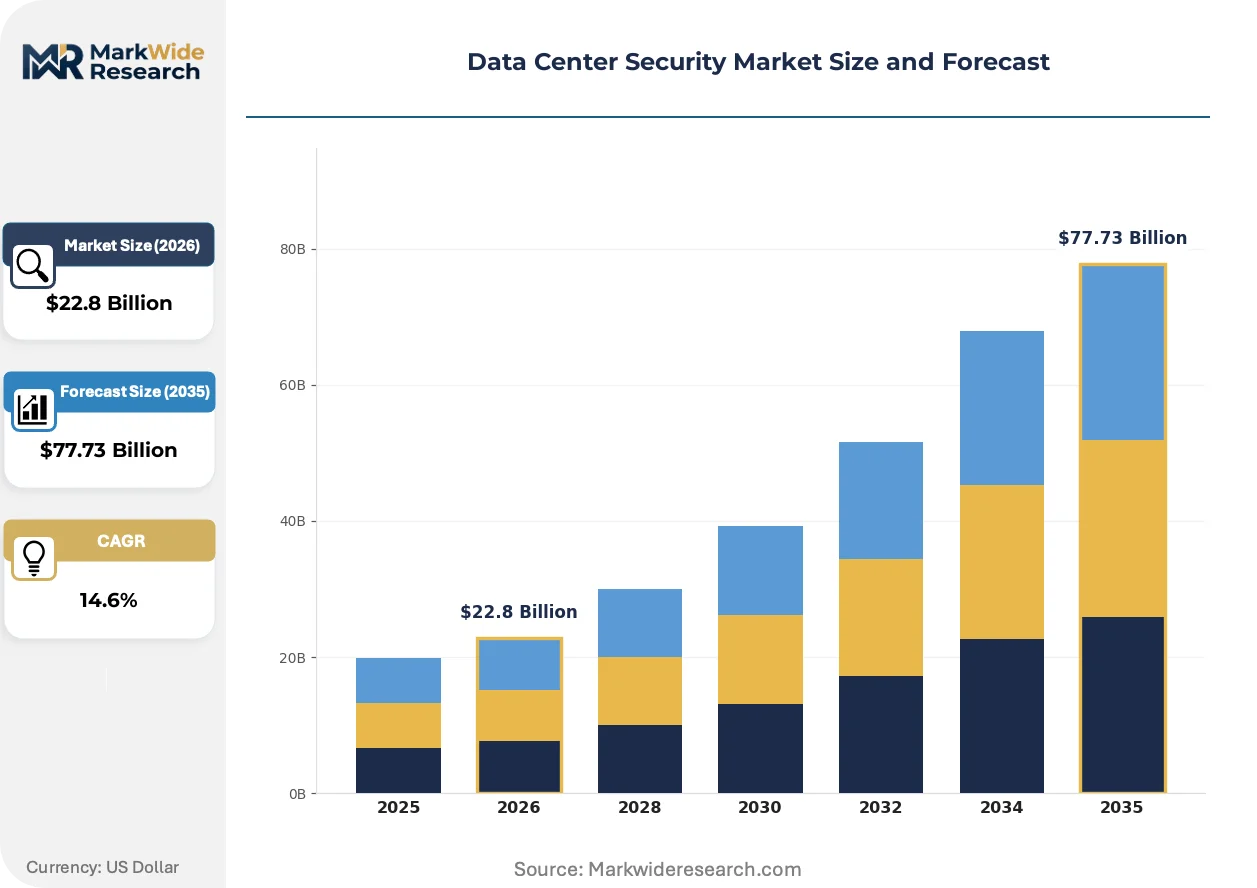
Market Dynamics
Zero-trust architecture migration is compressing procurement cycles and forcing vendors to consolidate previously discrete security functions into unified platforms, reshaping how enterprise buyers evaluate and deploy data center protection layers.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Mandated incident reporting and governance disclosures for publicly traded operators are accelerating security stack refresh cycles across US financial services and cloud infrastructure sectors.
- Hyperscaler Buildouts:Concentrated capital deployment by cloud providers in Germany, India, and the United States is generating sustained demand for high-throughput, low-latency inspection appliances.
- Confidential Computing:Hardware-based enclave technologies are expanding addressable security spend beyond traditional perimeter defenses into runtime data protection workloads.
Market Restraints
- Specialized Engineering Talent Scarcity:Shortages of professionals certified in zero-trust implementation and cloud-native security architecture are extending deployment timelines and inflating service costs.
- Silicon Supply Concentration:Dependence on advanced semiconductor fabrication concentrated in Taiwan and South Korea creates vulnerability for inline security appliance manufacturers facing capacity constraints.
- GDPR Compliance Friction:Cross-border data transfer restrictions and automated decision-making prohibitions complicate centralized security operations for multinational data center operators.
Strategic Opportunities
- India Sovereign Cloud Mandates:Data localization requirements under RBI and SEBI guidelines are compelling foreign cloud providers to establish India-domiciled security operations, opening greenfield deployment opportunities.
- AI-Driven Threat Detection:Convergence of machine learning inference with programmable data plane silicon is enabling real-time behavioral analysis without traffic hairpinning.
- Outcome-Based Security Contracts:Enterprise buyers in Germany's manufacturing sector are piloting performance-guaranteed service models that tie vendor compensation to measurable risk reduction metrics.
Industry Challenges
- ISO 27001 Certification Timelines:Extended audit backlogs and evolving control requirements are delaying market entry for new data center operators seeking enterprise credibility.
- Legacy Firewall Integration Complexity:Hybrid environments requiring seamless policy orchestration between on-premises hardware and cloud-native controls are multiplying implementation failure rates.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Data Center Security Market |
| Market Size in 2026 | $22.8 Billion |
| Market Size in 2035 | $77.73 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Firewall, Intrusion Detection System, Data Loss Prevention, Access Control, Security Information and Event Management, Encryption Deployment: On-Premises, Cloud-Based, Hybrid, Virtual Use Case: Threat Detection, Compliance Management, Physical Security, Network Segmentation, Identity Management End User: Telecommunications, Financial Institutions, Government Agencies, Technology Providers, Educational Organizations |
| Companies Covered | Zscaler, Check Point, Palo Alto Networks, IBM, Leidos, CrowdStrike, CyberArk, Cisco, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Data Center Security Market Strategic Shifts & Innovations
Security function consolidation and embedded intelligence are displacing point-product architectures, with vendors racing to own the policy enforcement layer across distributed compute footprints.
Confidential computing using trusted execution environments is digitizing how sensitive workloads isolate cryptographic operations from host operating systems. Financial institutions processing cardholder data are deploying these enclaves at scale to satisfy PCI-DSS segmentation requirements without physical network air gaps. The technology is digitizing trust boundaries, collapsing the distinction between perimeter security and runtime protection.
The EU AI Act's risk classification framework for automated threat response systems is compelling European data center operators to document algorithmic decision logic and maintain human oversight capabilities. Facilities deploying autonomous intrusion remediation must now implement kill-switch protocols and audit trails. German and French operators are most affected, with several hyperscalers pausing fully automated response rollouts pending legal clarity.
Enterprise security procurement is consolidating around platform vendors capable of unified policy management across on-premises, colocation, and public cloud footprints. Traditional value-added resellers are losing influence as hyperscalers and large enterprises negotiate direct multi-year commitments with Palo Alto Networks, CrowdStrike, and Check Point. This disintermediation is most pronounced in the United States, where Fortune 500 technology budgets now flow predominantly through vendor-managed service programs rather than channel partners.
Data Center Security Market Segmentation
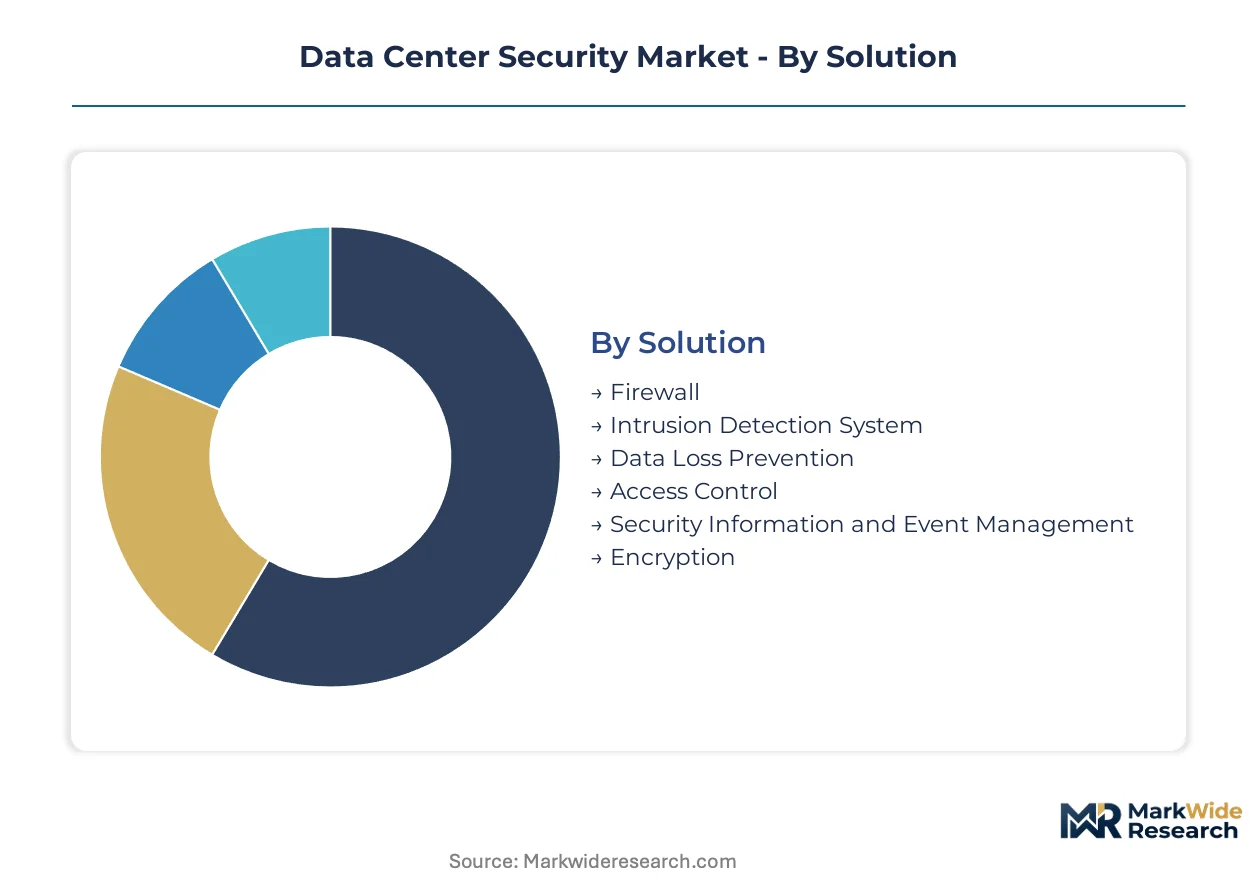
Data center security procurement cycles vary dramatically across solution types, with hardware refresh intervals stretching to five years while cloud-native controls update quarterly. Understanding these velocity differences helps vendors align R&D investment with actual replacement windows and margin capture opportunities.
Solution:
Firewall appliances turn over slowest due to capital-intensive deployment and certification requirements, while cloud-native encryption services refresh fastest as algorithms evolve and compliance mandates tighten.
- Firewall:Hardware appliances enforcing network traffic policies through deep packet inspection at sub-millisecond latency. Financial institutions in Germany and the United States dominate procurement as PCI-DSS and SEC rules mandate perimeter hardening, though silicon supply constraints extend lead times for high-throughput models.
- Intrusion Detection System:Network sensors and behavioral analytics engines identifying anomalous traffic patterns. Demand concentrates among hyperscalers building out capacity in India and the United States, driven by requirements for automated threat response without traffic hairpinning.
- Data Loss Prevention:Content inspection and egress monitoring tools preventing unauthorized data exfiltration.
- Access Control:Identity verification and privilege management systems governing physical and logical entry points.
- Security Information and Event Management:Centralized log aggregation and correlation platforms for forensic analysis.
- Encryption:Cryptographic key management and data-at-rest protection services.
Firewall dominates installed base. Encryption is where expansion concentrates.
Deployment:
Cost structures separate these modes sharply, with on-premises carrying heavy upfront capital burden while cloud-based shifts spending to operational budgets with usage-based scaling.
- On-Premises:Physical appliances housed within operator-controlled facilities. Government agencies and regulated financial institutions in Germany prefer this mode for data sovereignty compliance, despite higher total cost of ownership and extended procurement cycles.
- Cloud-Based:Vendor-managed security services delivered through API integration and agent deployment. Technology providers in the United States are retiring legacy stacks fastest here, attracted by zero-trust architecture alignment and reduced hardware maintenance overhead.
- Hybrid:Orchestrated policy enforcement across physical and cloud-native control planes.
- Virtual:Software-defined security functions deployed on commodity compute without dedicated hardware.
Hybrid configurations retain the largest margin pools due to integration complexity. Cloud-based deployment is climbing the fastest as organizations exit capital-intensive refresh cycles.
Use Case:
Application criticality determines investment priority, with threat detection commanding continuous funding while physical security sees episodic capital allocation tied to facility expansion.
- Threat Detection:Real-time identification of malware, intrusion attempts, and anomalous behavior through machine learning and signature analysis. Financial institutions facing SEC cybersecurity disclosure mandates are expanding budgets fastest here, particularly for AI-driven behavioral analytics.
- Compliance Management:Automated audit trails, control documentation, and certification maintenance workflows. European operators under GDPR and EU AI Act requirements are prioritizing this use case to satisfy algorithmic decision documentation and cross-border transfer restrictions.
- Physical Security:Biometric access, surveillance, and environmental monitoring for facility protection.
- Network Segmentation:Micro-segmentation and zero-trust zone isolation for lateral movement prevention.
- Identity Management:Multi-factor authentication and privileged access governance for human and machine identities.
Threat detection dominates installed base. Compliance management is gaining share fastest as regulatory frameworks proliferate.
End User:
Customer sophistication and procurement scale create distinct service tiers, with hyperscale technology providers demanding customized architectures while educational organizations prioritize cost-optimized standard packages.
- Telecommunications:Carriers securing multi-tenant infrastructure and edge compute nodes. Operators in India are expanding fastest here, compelled by RBI data localization mandates requiring sovereign cloud security operations.
- Financial Institutions:Banks, insurers, and payment processors protecting cardholder data and trading infrastructure. German and US institutions lead spending as PCI-DSS segmentation requirements and SEC disclosure rules force stack refreshes.
- Government Agencies:Federal, state, and municipal entities with classified or citizen data protection mandates.
- Technology Providers:Cloud hyperscalers and SaaS vendors securing distributed compute footprints.
- Educational Organizations:Universities and research institutions protecting intellectual property and student records.
Telecommunications dominates installed base. Financial institutions are where expansion concentrates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
SEC cybersecurity disclosure rules are accelerating security stack refreshes across United States financial services and cloud infrastructure sectors. Data center security demand concentrates in three sovereign jurisdictions with distinct regulatory drivers.
United States
Hyperscaler buildouts in Northern Virginia and Dallas-Fort Worth are generating sustained procurement of high-throughput inspection appliances. FCC guidelines on communications infrastructure resilience elevate baseline spending for multi-tenant facilities. Financial institutions in New York and Chicago are expanding zero-trust migration budgets to satisfy mandated incident reporting timelines.
Germany
Manufacturing enterprises in Bavaria and Baden-Württemberg are piloting outcome-based security contracts tied to measurable risk reduction. GDPR and the EU AI Act impose documentation burdens on automated threat response systems deployed in Frankfurt and Berlin data center clusters. Government agencies prefer on-premises deployment for data sovereignty compliance despite higher total cost of ownership.
India
RBI and SEBI data localization guidelines are compelling foreign cloud providers to establish sovereign security operations in Mumbai and Bangalore. Telecommunications carriers expanding multi-tenant edge infrastructure represent the fastest-growing end-user segment. Domestic hyperscaler buildouts in Hyderabad and Chennai are absorbing cloud-native security services at scale.
Data Center Security Market Key Industry Players
Platform consolidators and perimeter specialists split the market along architectural philosophy lines. Vendor-direct sales are displacing traditional channel structures as enterprise buyers negotiate multi-year commitments. Three archetypes dominate: unified platform vendors, firewall-centric perimeter defenders, and cloud-native workload protection specialists. Competitive intensity centers on strategic partnerships with hyperscalers and vertical integration into silicon-optimized appliances.
Within the platform consolidation tier, Palo Alto Networks and CrowdStrike exemplify the shift toward unified policy management across distributed footprints. Check Point occupies a position representing perimeter firewall specialization with maintained channel presence in regulated verticals. These three anchors illustrate how vendor strategies diverge between cloud-native extensibility and hardware-anchored inspection performance.
| Leading Market Players |
|---|
| Zscaler |
| Check Point |
| Palo Alto Networks |
| IBM |
| Leidos |
| CrowdStrike |
| CyberArk |
| Cisco |
| Fortinet |
| Others |
Cost & Logistics Intelligence
Advanced semiconductor fabrication concentrated in Taiwan and South Korea feeds directly into margin capture at the high-throughput appliance tier, where sub-millisecond inspection engines command premium positioning against commodity virtualized alternatives.
Pricing Analysis
United States buyers pay 15-25% premiums over Indian procurement for identical firewall appliances due to FCC resilience certification requirements and domestic support bundling. Pricing stratifies across premium hardware-anchored tiers, standard virtualized deployments, and economy cloud-native subscriptions differentiated by throughput ceiling and SLA guarantees. Cost compression in the standard tier is intensifying because hyperscalers are internalizing security functions and bypassing vendor licensing. Educational organizations and mid-market colocation operators exhibit highest price sensitivity, while financial institutions under SEC disclosure mandates show lowest elasticity due to compliance-driven refresh cycles.
Supply Chain Analysis
Export controls on advanced programmable silicon from the United States and allied jurisdictions restrict flows to Chinese equipment vendors, concentrating supply leverage with Taiwan Semiconductor Manufacturing and Samsung Foundry. Security appliance manufacturing draws from specialized ASIC design houses in Israel and the United States, advanced packaging facilities in Taiwan and South Korea, and rare earth magnet suppliers for cooling subsystems concentrated in China. Single-source vulnerability around 7nm and below fabrication nodes creates procurement risk for vendors competing on latency performance. Distribution runs through direct vendor-managed service programs displacing traditional VAR channels, particularly for Fortune 500 enterprise commitments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fragmentation opportunity exists as zero-trust architecture migration splinters procurement authority between CISO organizations, cloud platform teams, and compliance officers, creating specialist niches for vendors bridging these silos.
For Market Incumbents: Pre-empt channel disintermediation by embedding professional services capabilities that VARs cannot replicate, particularly around hybrid policy orchestration. Acquire cloud-native workload protection specialists in India and Germany before sovereign cloud mandates lock in local vendor relationships. Certification investment in ISO 27001 and EU AI Act compliance documentation represents the priority lever for defending enterprise renewal rates against platform consolidators. For New Entrants and Emerging Players: Build out sovereign cloud security operations in Mumbai and Bangalore to capture RBI and SEBI localization-driven procurement from foreign hyperscalers establishing India-domiciled infrastructure. Target telecommunications carriers expanding multi-tenant edge compute as the most penetrable end-user segment, with outcome-based pricing models piloted in German manufacturing as the referenceable go-to-market angle. For Investors and Strategic Acquirers: Secondary-cycle assets sit with PE-backed firewall-centric specialists lacking cloud-native extensibility, where sponsor exits face compressed multiples against platform consolidators. Five-to-ten year viability hinges on AI-driven threat detection capabilities converging with programmable data plane silicon. Watch hyperscaler capex allocation shifts toward confidential computing infrastructure as the signal indicating which security workload protection vendors will capture next-generation spend.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Palo Alto Networks and CrowdStrike consolidate previously discrete firewall, endpoint, and cloud-native controls into unified policy layers. |
| Strategic Partnership | Check Point maintains channel presence in German regulated verticals where direct sales models face procurement friction. |
| Acquisition of Specialist Firm | Confidential computing enclave vendors attract interest from financial institutions seeking PCI-DSS segmentation without physical air gaps. |
| Geographic Expansion | Foreign cloud providers establish sovereign security operations in India under RBI and SEBI data localization mandates. |
| Product Launch | Vendors race to deploy AI-driven behavioral analytics without traffic hairpinning, leveraging programmable silicon from NVIDIA and Intel. |
Research Approach
Cross-validation between primary interviews with data center operators, CISOs, and channel partners and secondary validation against hyperscaler capex disclosures, SEC cybersecurity disclosure filings, and RBI/SEBI regulatory circulars anchors the qualitative findings. Bottom-up triangulation aggregates procurement cycle data across firewall appliance, intrusion detection system, and encryption service categories, while top-down analysis calibrates against total security spending reported by Fortune 500 technology and financial services firms.
Calibration against historical replacement intervals—five-year hardware refresh cycles versus quarterly cloud-native control updates—shapes the projection framework across solution, deployment, and end-user segmentation dimensions. CAGRs derive from weighted capacity expansion announcements by cloud providers in Northern Virginia, Frankfurt, and Mumbai, layered against compliance-driven refresh mandates from SEC disclosure rules and EU AI Act documentation requirements. Confidential computing adoption curves and AI inference integration timelines feed scenario-weighted outputs throughout the forecast period.
Practitioners should monitor silicon supply constraints, sovereign cloud mandate enforcement intensity, and automated threat response regulatory clarity for early signals requiring model revision. Material shifts in export control regimes affecting programmable data plane silicon, or abrupt changes to GDPR cross-border transfer mechanisms, would force updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Benelux Cybersecurity Market
Cybersecurity
Global Automated Breach and Attack Simulation (BAS) Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
Oman Cybersecurity Market
Cybersecurity
South Korea Cybersecurity Market
Cybersecurity
India Ransomware Protection Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
Data Exfiltration Techniques Market
Cybersecurity
Web Filtering Market
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
Cloud Security Market
Cybersecurity
Thailand Cybersecurity Market
Cybersecurity
Belgium Cybersecurity Market